❌

Visualização normal

Antes de ontemCybersecurity News
  • ✇Cybersecurity News
  • GMO Internet Ransom Demand Slashed After Cloud Breach Do Son
    Hackers reduced the GMO Internet ransom demand from $50M to $1M and leaked victim files after the Japanese conglomerate ignored multiple bug warnings. Related Posts: UAT-11473 Deploys KeyDrift Malware on Cisco SD-WAN Controllers via CVE-2026-20127 Chained PHP2Shell Exploit Roots 25 Firewall Servers Including US Government Systems Hive Ransomware Affiliate Artem Stryzhak Sentenced to 70 Months in US Prison The post GMO Internet Ransom Demand Slashed After Cloud Breach appeared first on Daily C
     

US Ransomware Negotiator Suspected of Helping ShinyHunters Extort Victims

Federal investigators suspect a US ransomware negotiator helped ShinyHunters operate an extortion site used to pressure nearly 100 organisations.

MonsterCloud CEO Zohar Pinhasi Accused of Paying Hackers, Defrauding Victims

The DOJ accuses MonsterCloud CEO Zohar Pinhasi of secretly paying ransomware gangs for decryption keys while charging victims…
  • ✇Graham Cluley
  • N0n ransomware: what you need to know Graham Cluley
    N0n is a newly-emerged cyber extortion gang. The group was first spotted in the middle of September 2026, and within days it had published on its dark web leak site details of what it claimed to be around a dozen victims. Since then, the tally has continued to grow. Read more in my article on the Fortra blog.
     

N0n ransomware: what you need to know

3 de Outubro de 2026, 05:29
N0n is a newly-emerged cyber extortion gang. The group was first spotted in the middle of September 2026, and within days it had published on its dark web leak site details of what it claimed to be around a dozen victims. Since then, the tally has continued to grow. Read more in my article on the Fortra blog.
  • ✇Cybersecurity News
  • ShinyHunters Renews Oracle PeopleSoft Attacks With One-Character WAF Bypass Do Son
    ShinyHunters PeopleSoft attacks are back. A one-letter WAF bypass lets the group exploit CVE-2026-35273 and plant web shells on unpatched servers. Related Posts: Operation Master Turns GlobalProtect Breaches Into Brazilian Invoice Fraud Konni Launches Operation Conflict Compass Against Ukraine Kiteworks Mandates Global Precautionary Server Shutdown The post ShinyHunters Renews Oracle PeopleSoft Attacks With One-Character WAF Bypass appeared first on Daily CyberSecurity.
     

Exclusive: ShinyHunters Says FBI Data Won’t Be Leaked When Ultimatum Ends

ShinyHunters tells Hackread it never planned to publish or sell stolen FBI data and says its ultimatum was part of a marketing campaign to counter FBI claims.

Clop Ransomware Responds to ShinyHunters Amid Eight-Figure Demands

Clop responds to ShinyHunters after its leak site takeover as the group demands an eight-figure payment, interest and a public apology in their escalating feud.

ShinyHunters Hacks and Defaces Clop Ransomware Leak Site

ShinyHunters hacked and defaced Clop's ransomware leak site, replacing its content with ShinyHunters branding as its own onion site goes offline.
  • ✇Firewall Daily – The Cyber Express
  • Global Crackdown on West African Crime Networks Leads to 58 Arrests Samiksha Jain
    An eight-month international operation targeting West African organized crime groups has resulted in 58 arrests and the identification of 263 suspects across 22 countries, according to INTERPOL. Operation Jackal IV, conducted from November 2025 to June 2026, focused on disrupting criminal networks, tracing illicit funds, identifying high-value targets and supporting arrests and prosecutions. The operation brought together countries across six continents to tackle the growing global threat pos
     

Global Crackdown on West African Crime Networks Leads to 58 Arrests

26 de Agosto de 2026, 05:12

West African Organized Crime Groups

An eight-month international operation targeting West African organized crime groups has resulted in 58 arrests and the identification of 263 suspects across 22 countries, according to INTERPOL. Operation Jackal IV, conducted from November 2025 to June 2026, focused on disrupting criminal networks, tracing illicit funds, identifying high-value targets and supporting arrests and prosecutions. The operation brought together countries across six continents to tackle the growing global threat posed by West African criminal networks, including Black Axe and similar groups. These networks have been linked to a significant share of global cyber-enabled financial fraud, including romance scams, cryptocurrency and investment scams, and business email compromise fraud.

Operation Jackal IV Targets West African Organized Crime Groups

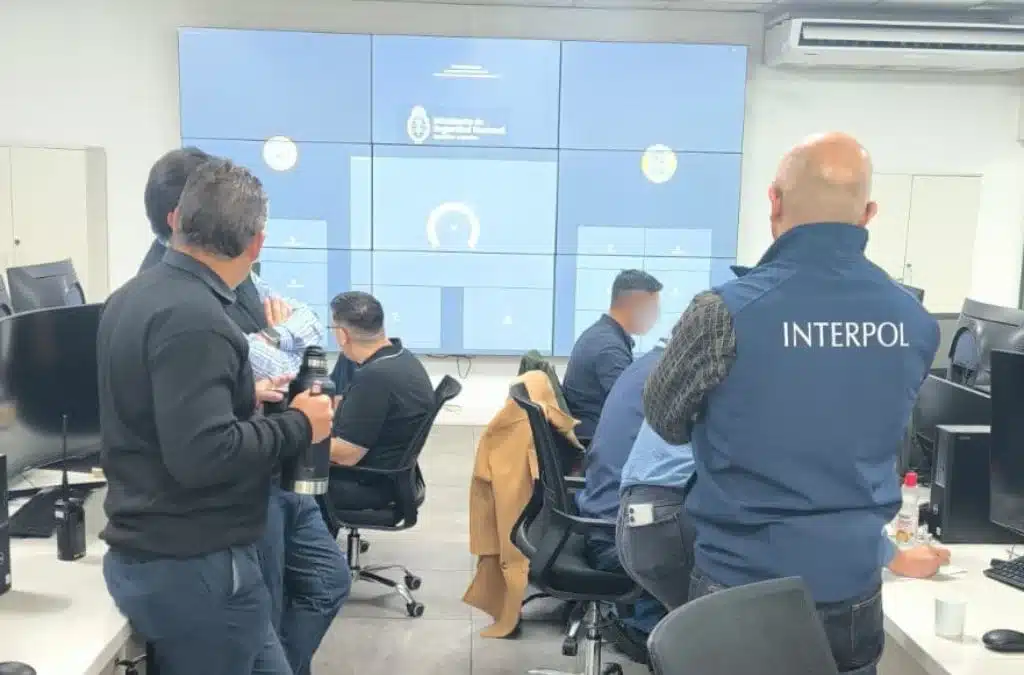
Operation Jackal IV also targeted money laundering activities used to move and conceal criminal proceeds across borders. INTERPOL coordinated cross-border intelligence sharing, analysis and operational support during the operation. It also provided specialized training to strengthen international investigations into financial crime. Tomonobu Kaya, Director of the INTERPOL Financial Crime and Anti-Corruption Centre, said the operation showed the importance of international cooperation in following illicit financial flows and disrupting criminal networks. [caption id="attachment_113806" align="aligncenter" width="600"]West African Organized Crime Groups Image Source: INTERPOL[/caption]

Major Arrests and Financial Crime Investigations

In Argentina, authorities identified 196 individuals linked to a major Crime-as-a-Service network suspected of providing website domains and money laundering support to West African organized crime groups. The investigation resulted in 17 arrests, with an INTERPOL Operational Support Team assisting with analysis of seized data and identification of suspects and criminal networks. South African authorities raided seven locations in Johannesburg linked to a syndicate involved in romance and investment scams targeting retirees in English-speaking countries. Investigators arrested 39 people, seized USD 2.67 million and blocked 257 bank accounts. In Italy, investigators identified an individual connected to a pan-European money laundering network that used shell companies, remittance services and cash withdrawals. One account processed EUR 845,000, or about USD 736,000, through 560 transactions involving 20 financial instruments. Romanian authorities dismantled a criminal group operating an investment scam through a call centre. The group promoted high returns from stocks and cryptocurrencies, with victims' money transferred to electronic wallets controlled by perpetrators. Authorities estimated that EUR 143 million had been stolen and laundered globally. Eleven people were arrested, while cash, cryptocurrency, six real estate properties and luxury watches were seized.

Sextortion and Crime-as-a-Service Emerge

Beyond individual investigations, the operation highlighted emerging threats involving sextortion and Crime-as-a-Service. INTERPOL identified an increase in West African organized crime groups using sextortion to target minors, including victims as young as 14. In these cases, offenders typically contacted minors through social media, established trust and persuaded them to share explicit images or videos. They then threatened to distribute the material to the victim's contacts unless a ransom was paid. Investigators also found that some criminal syndicates were procuring Crime-as-a-Service from external providers, including through the dark web. These services were used to outsource activities such as money laundering and other operational functions. While several cases from Operation Jackal IV remain under investigation, the preliminary results demonstrate the scale and international reach of the networks targeted during the eight-month operation. The participating countries were Austria, Argentina, Australia, Canada, Côte d'Ivoire, France, Germany, Indonesia, Ireland, Italy, Japan, Malaysia, the Netherlands, Nigeria, Portugal, South Africa, Spain, Sweden, Switzerland, the United Arab Emirates, the United Kingdom and the United States.

Prison for data analyst who tried to extort $2.5 million from his employer

19 de Agosto de 2026, 04:26
When Cameron Curry discovered that his contract as a data analyst wasn't going to be renewed, he could have updated his LinkedIn profile. He could have started sending out his resume. But what the 27-year-old from Charlotte, North Carolina, did instead was turn to extortion. Read more in my article on the Hot for Security blog.

LeakNet Claims 11TB of Data Stolen in NYC Health + Hospitals Breach

LeakNet claims it stole 11TB of NYC Health + Hospitals data containing sensitive medical, financial and biometric records linked to more than 12 million people.

ShinyHunters Claims Ernst & Young (EY) Data Breach, Threatens July 31 Leak

EY confirmed the theft of client tax documents from its third-party support platform. ShinyHunters claims responsibility and is threatening to publish the data.

Cybersecurity Negotiator Gets 70 Months for Helping BlackCat Extort Victims

Former ransomware negotiator Angelo Martino gets 70 months in prison for helping BlackCat extort US victims and misuse confidential client data in cyberattacks.
❌
❌