❌

Visualização normal

Hoje — 10 de Novembro de 2026Cybersecurity News

Hackers Abuse Qubole’s Trusted AWS Access to Breach Multiple Cloud Accounts and Steal Sensitive Data

Hackers abused AWS credentials associated with Qubole to breach multiple customer cloud environments, harvest secrets, and steal sensitive S3 data between October 14 and October 26, 2026. Sentra reported that more than a dozen organizations were hacked, describing the broader impact as involving dozens of Qubole customers. Some compromised integration roles had remained dormant for […]

The post Hackers Abuse Qubole’s Trusted AWS Access to Breach Multiple Cloud Accounts and Steal Sensitive Data appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Russian-Linked Turla Hackers Abuse Microsoft Exchange Infrastructure to Target Sensitive Communications

Russian-linked espionage group Turla has deployed a previously undocumented .NET malware toolkit that turns compromised Microsoft Exchange servers into surveillance platforms and command infrastructure. Named Cereal, the modular toolset intercepts selected emails while allowing legitimate messages to continue through the transport pipeline, concealing intelligence collection inside routine government communications. ESET disclosed the findings on November […]

The post Russian-Linked Turla Hackers Abuse Microsoft Exchange Infrastructure to Target Sensitive Communications appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
North Korean Hackers Target Drone Technology and Software Supply Chains in New Cyberespionage Campaigns

North Korea-aligned hackers have renewed attacks on drone technology companies while expanding operations against software supply chains. Together, these campaigns expose industrial knowledge and software distribution channels to compromise. ESET’s APT Activity Report, published October 28, covers operations observed between April and September 2026. Researchers identified renewed Lazarus targeting of the drone sector and a […]

The post North Korean Hackers Target Drone Technology and Software Supply Chains in New Cyberespionage Campaigns appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Dark Storm Team Offers DDoS Attacks, Database Dumps, and Stolen Access Through Telegram Channels

Dark Storm Team uses Telegram as both a hacktivist broadcasting network and a cybercrime storefront, advertising distributed denial-of-service attacks, database dumps, compromised accounts, and surveillance access. A StealthMole investigation described in the supplied material traces an operation combining politically framed disruption claims with commercial services, cryptocurrency payments, and repeated channel migrations. First observed in late […]

The post Dark Storm Team Offers DDoS Attacks, Database Dumps, and Stolen Access Through Telegram Channels appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Ontem — 9 de Novembro de 2026Cybersecurity News

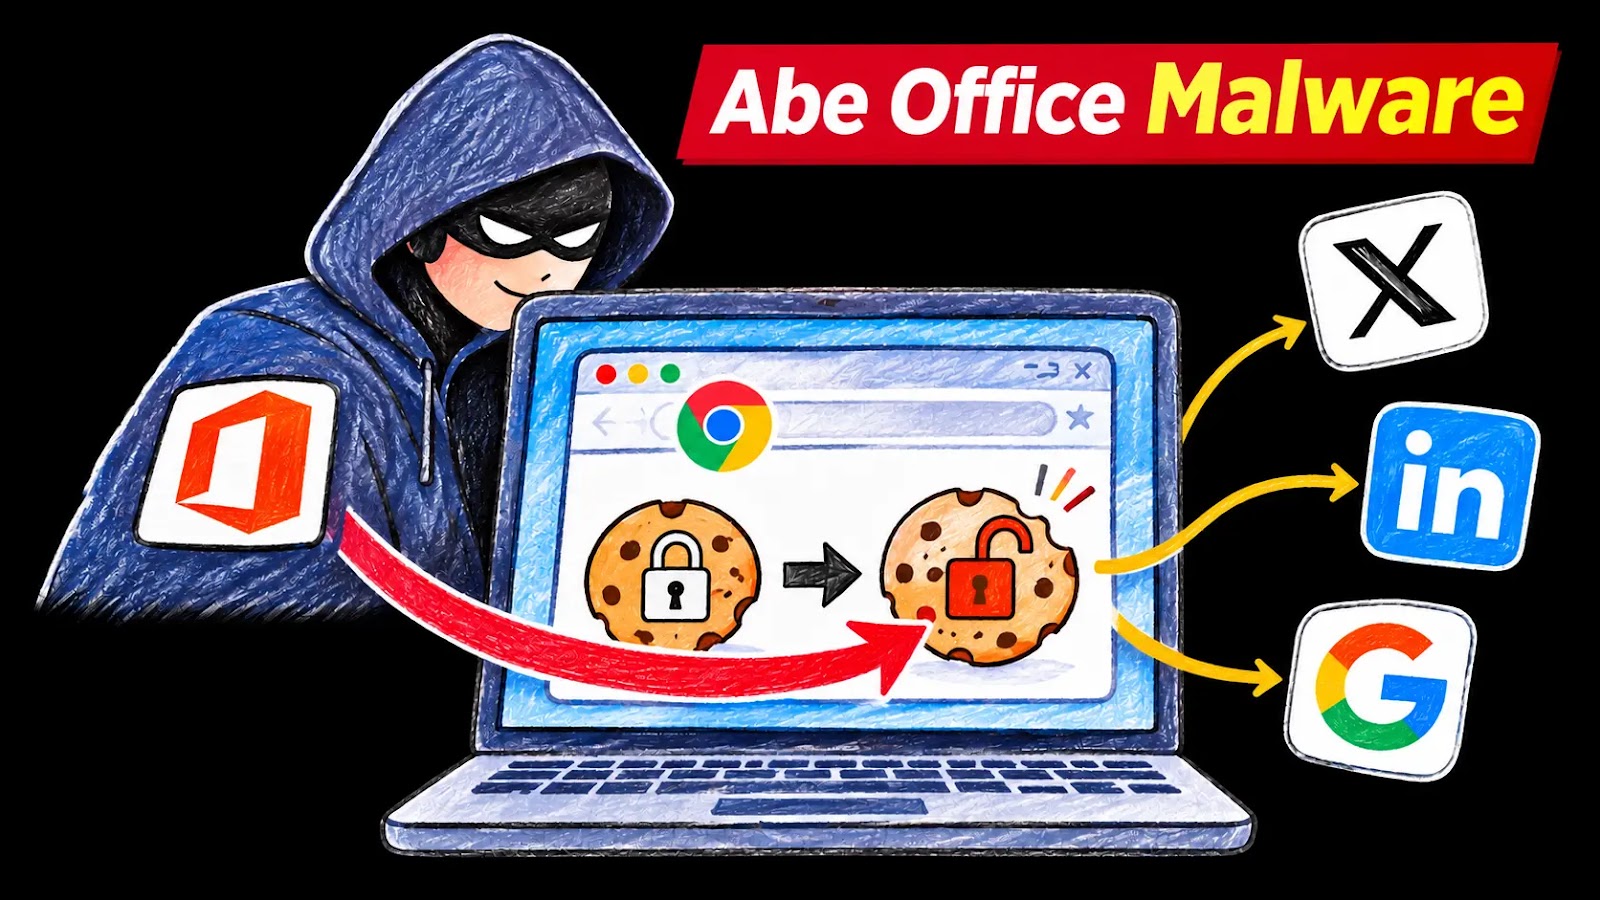
New Abe Office Malware Tricks Chrome Into Decrypting Its Own Protected Browser Cookies

A newly analyzed remote-access trojan masquerading as an “Abe Office workstation helper” combines hidden-browser control with tooling designed to bypass Chrome’s App-Bound Encryption. Rather than breaking the cryptography, its browser stealer injects a helper into Chrome and requests decryption from inside the trusted browser process. The supplied analysis credits MalwareHunterTeam with identifying the sample, AbeAgent.exe, […]

The post New Abe Office Malware Tricks Chrome Into Decrypting Its Own Protected Browser Cookies appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
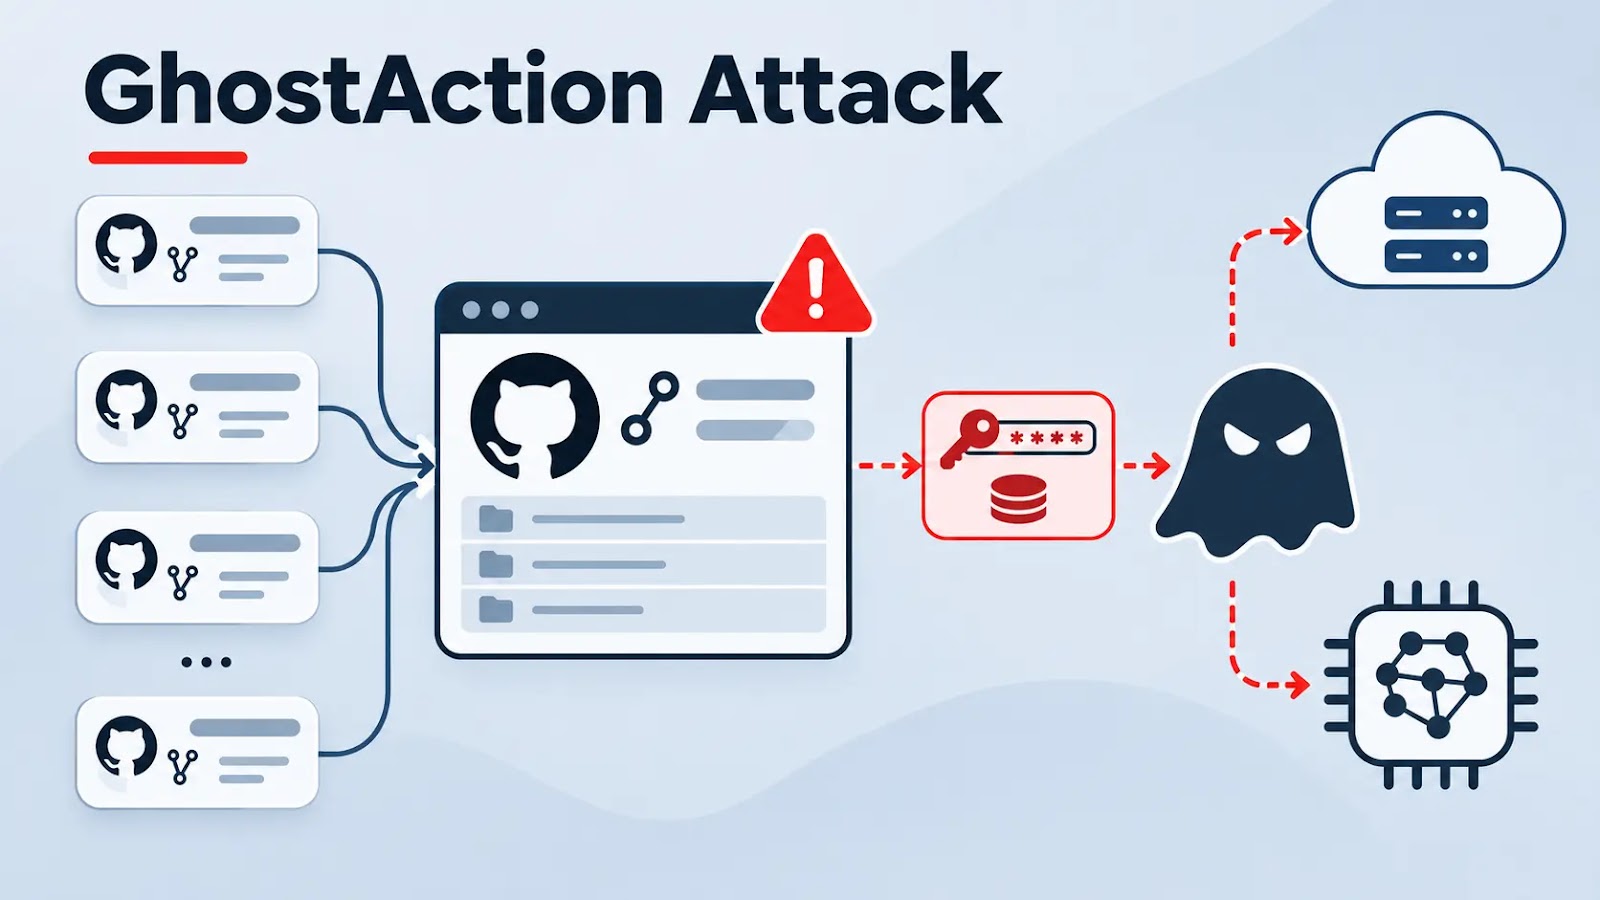
GhostAction Attack Hits Tens of Thousands of GitHub Repositories to Steal Cloud and AI Credentials

A new wave of the GhostAction supply chain campaign has pushed a credential-stealing GitHub Actions workflow into tens of thousands of repositories. It now hunts for cloud and AI keys buried in source code and git history, in addition to CI/CD secrets. Socket says it has identified more than 500 GitHub accounts that committed the […]

The post GhostAction Attack Hits Tens of Thousands of GitHub Repositories to Steal Cloud and AI Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
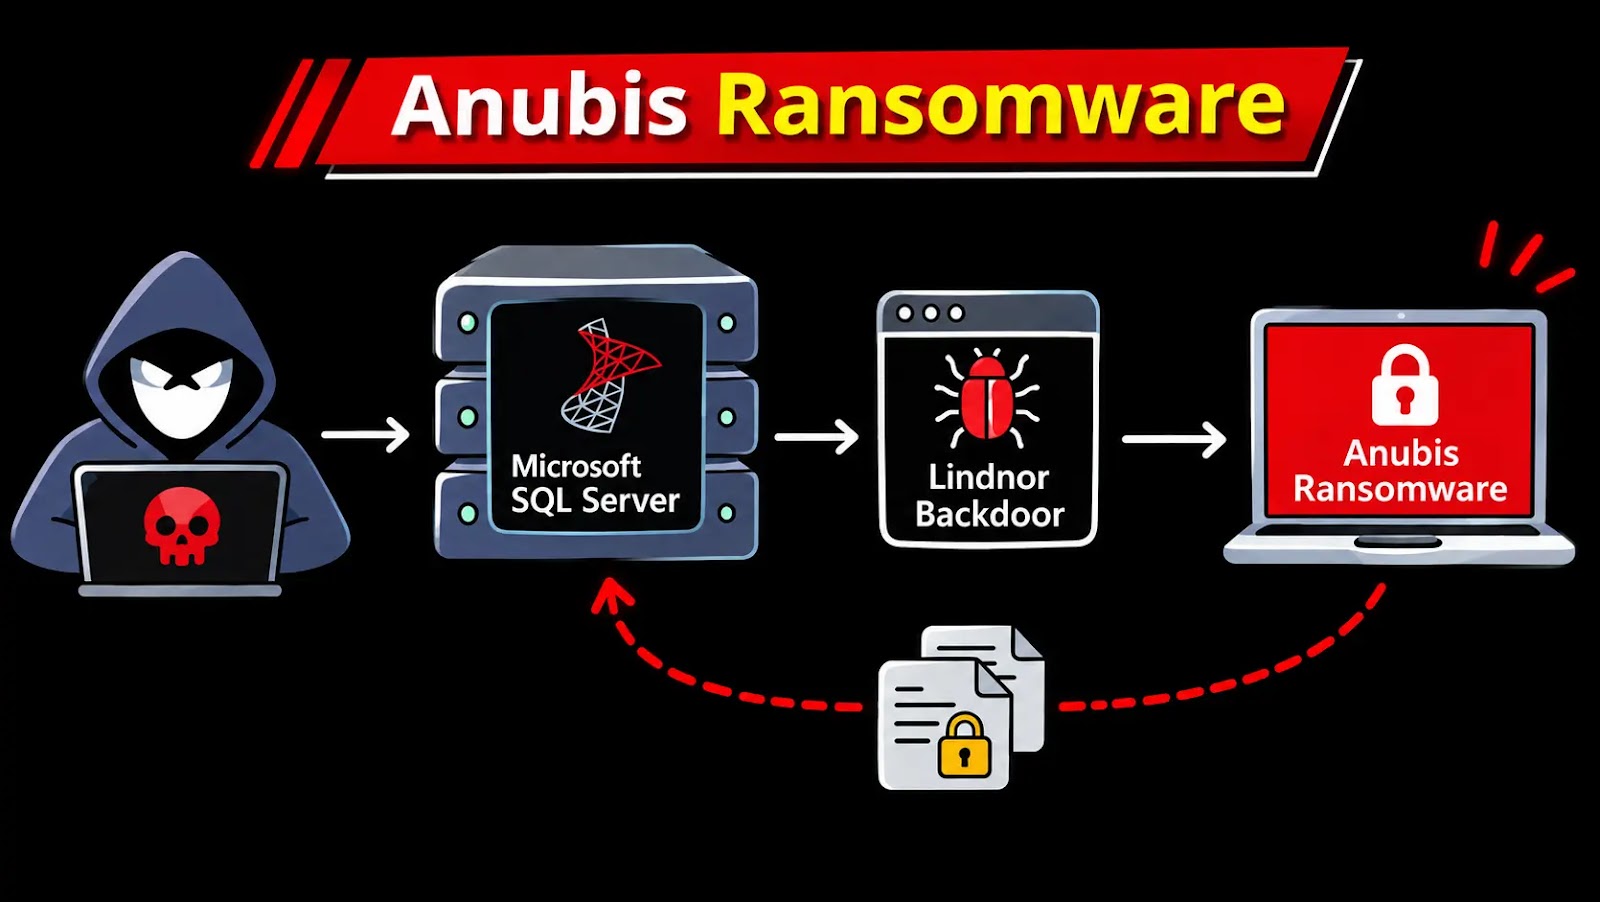
Hackers Use New Lindnor Backdoor to Target Microsoft SQL Servers in Anubis Ransomware Attack

Attackers deploying Anubis ransomware hit a U.S. organization in October 2026 with a previously undocumented custom backdoor. The malware sat on two Microsoft SQL Server machines, disguised as a Chrome component on one and a VMware file on the other. The encryption payload was blocked, and there is no evidence that any files were encrypted. […]

The post Hackers Use New Lindnor Backdoor to Target Microsoft SQL Servers in Anubis Ransomware Attack appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
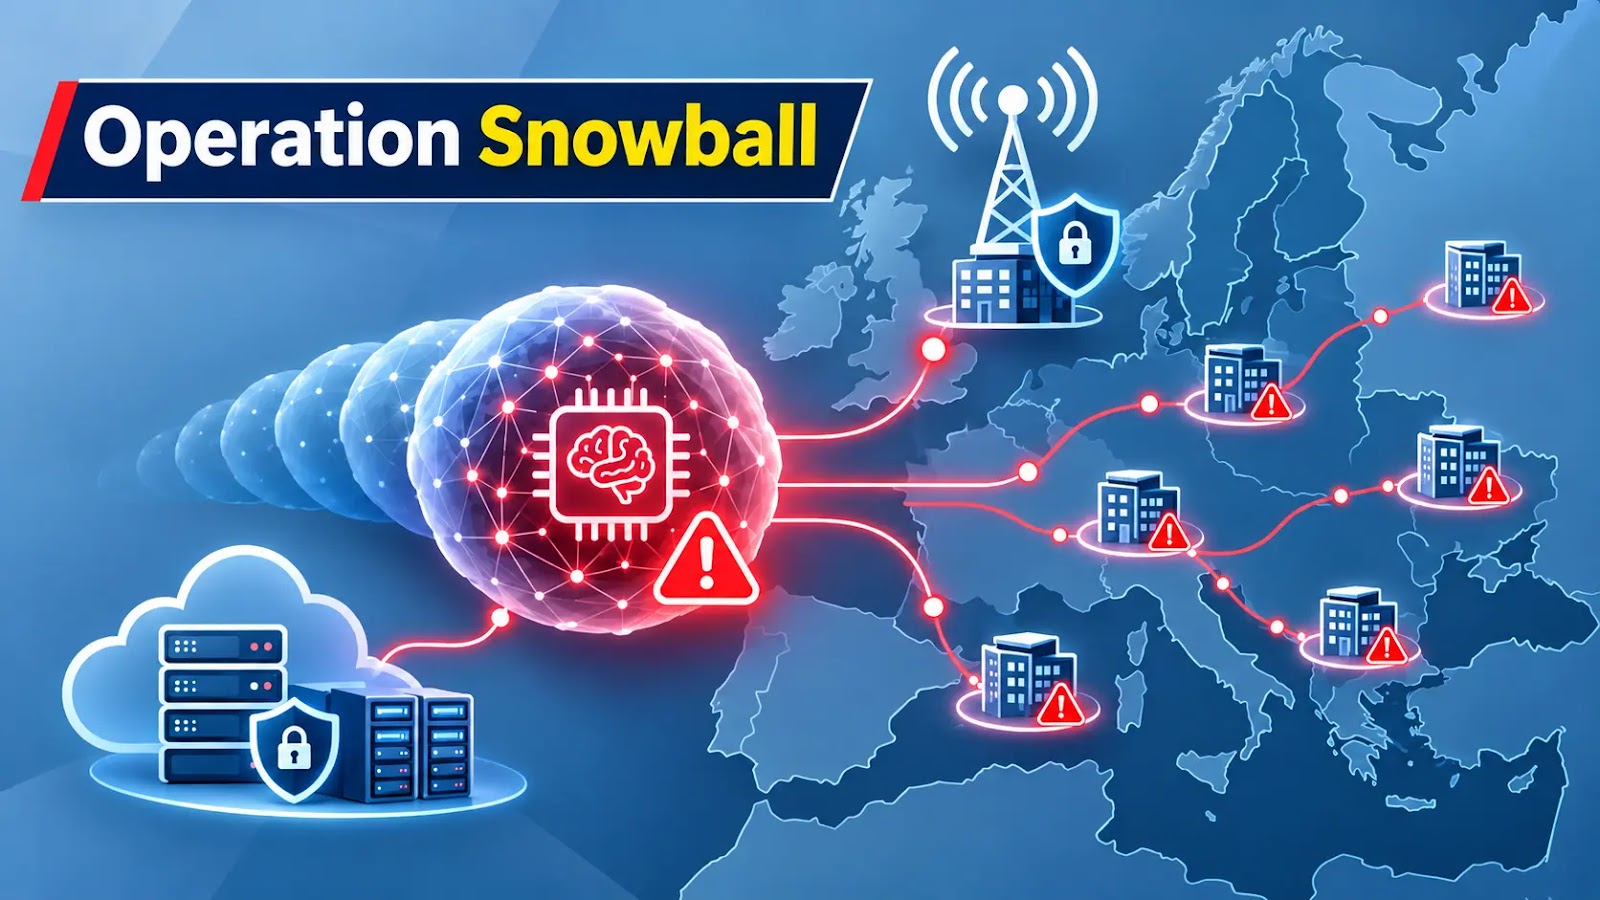
Operation Snowball Exposes AI Hacking Campaign Targeting European Telecom and 13 Hosted Organizations

An exposed open directory revealed an autonomous AI intrusion harness that spent more than two weeks attacking a European telecom provider and 13 organizations hosted in its data centers and cloud. The report, published on November 8, 2026, calls the campaign Operation Snowball. The researchers withheld the directory’s IP address to protect the victims. A […]

The post Operation Snowball Exposes AI Hacking Campaign Targeting European Telecom and 13 Hosted Organizations appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
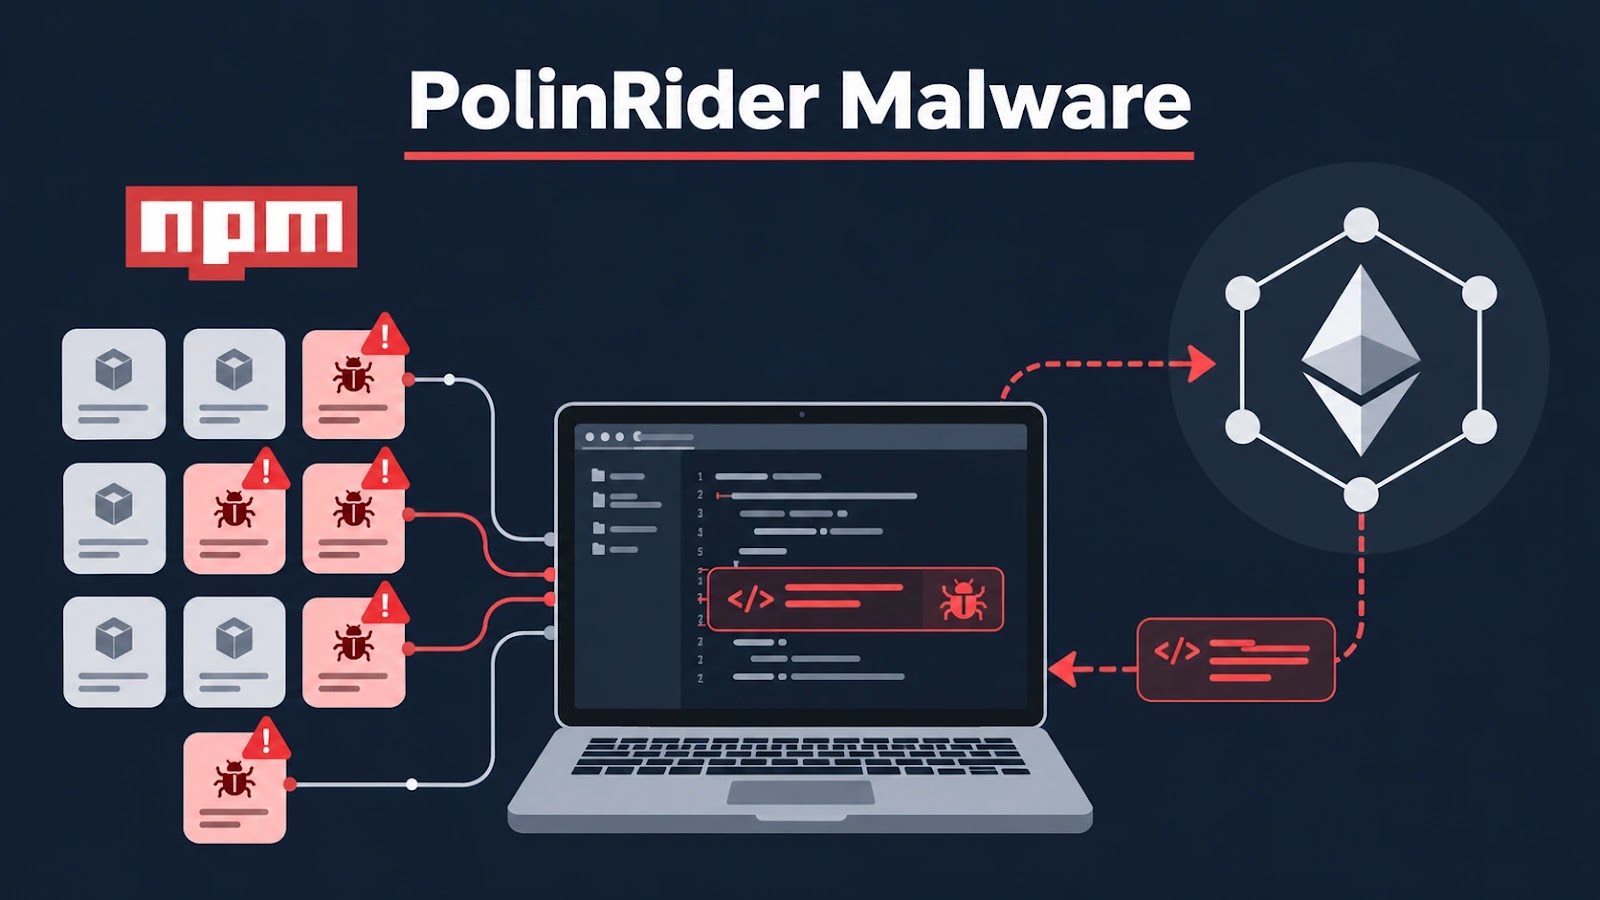
PolinRider Malware Returns in 10 Hijacked npm Packages Using Ethereum Blockchain to Deliver Malicious Code

A concealed JavaScript loaders in 12 releases across 10 hijacked npm packages, linking the compromise to previously documented PolinRider activity. Investigated on November 4, 2026, the releases use Ethereum transactions to discover remote payload servers and execute downloaded code inside developer environments, build systems, or applications. Sonatype tracks the finding as sonatype-2026-010515.guide. Unlike installation-triggered supply-chain […]

The post PolinRider Malware Returns in 10 Hijacked npm Packages Using Ethereum Blockchain to Deliver Malicious Code appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Antes de ontemCybersecurity News

Dark Project Ransomware Gang Claims 38 Victims Across 8 Countries, Targeting Healthcare and Manufacturing

Dark Project, an emerging financially motivated ransomware operation, has claimed 38 victims across eight countries in the supplied threat intelligence snapshot, with manufacturing and healthcare bearing the heaviest exposure. The group combines data theft, system encryption, and public disclosure threats with an affiliate program designed to scale intrusions. The figures represent allegations published through criminal […]

The post Dark Project Ransomware Gang Claims 38 Victims Across 8 Countries, Targeting Healthcare and Manufacturing appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
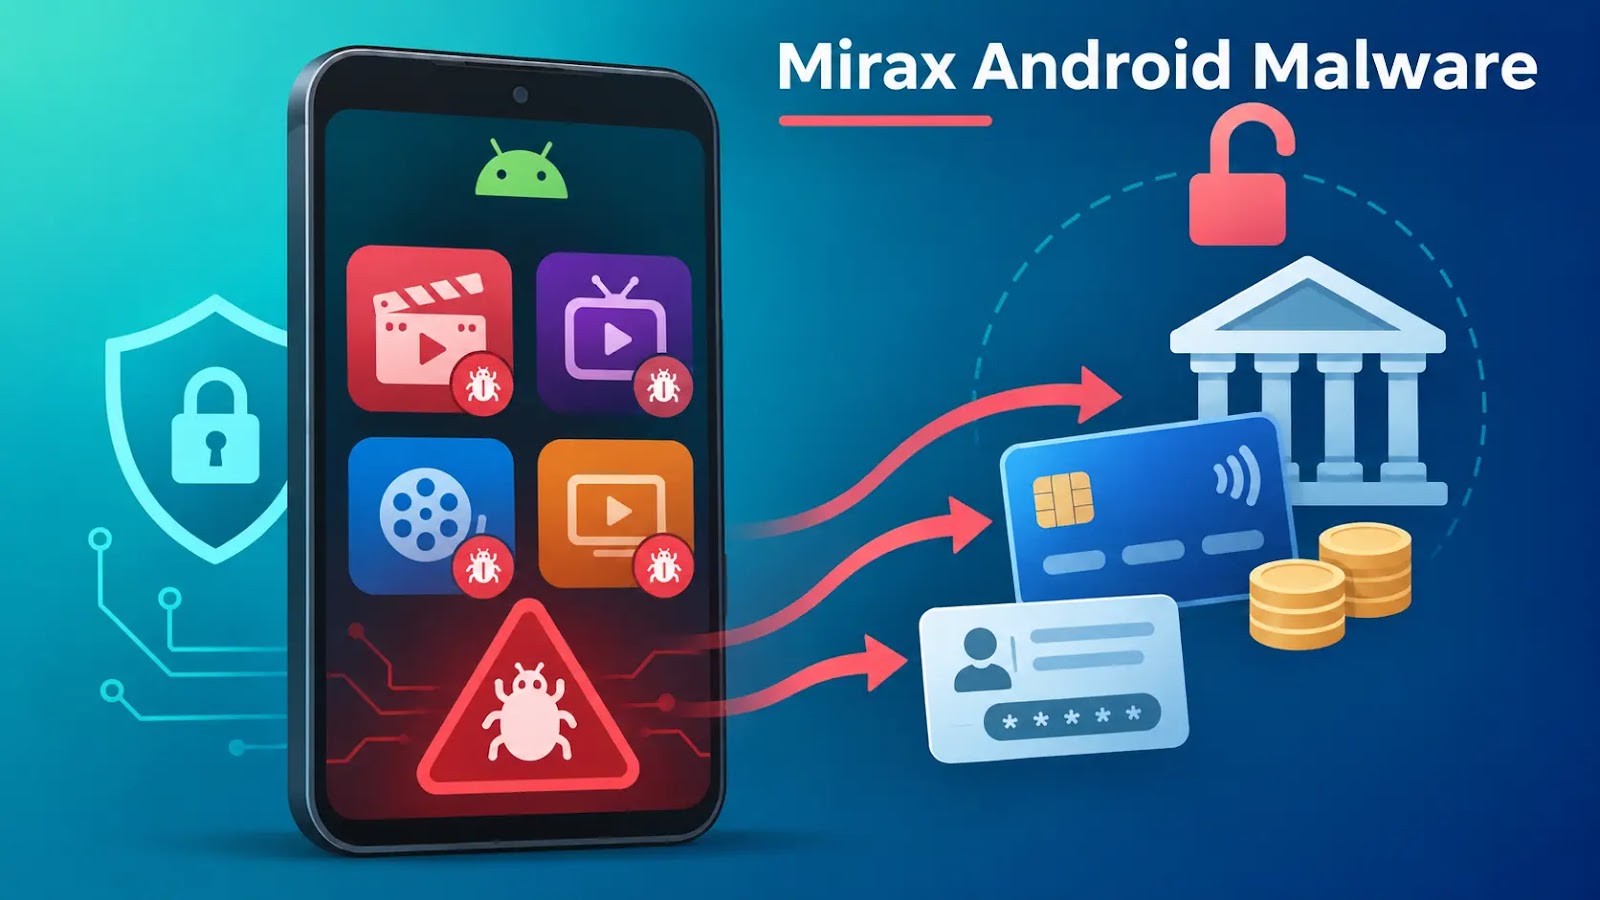
Hackers Use Fake Streaming Apps to Spread Mirax Android Malware and Steal Bank Accounts

Hackers are using streaming app lures to distribute Mirax. This Android banking trojan lets operators remotely control victims’ phones and initiate fraudulent transfers. Estimated losses reach millions of dollars, although confirmed cases capture only part of the campaign’s impact. The operation remained active when Group-IB published its November 5 investigation. Researchers linked the infections through […]

The post Hackers Use Fake Streaming Apps to Spread Mirax Android Malware and Steal Bank Accounts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
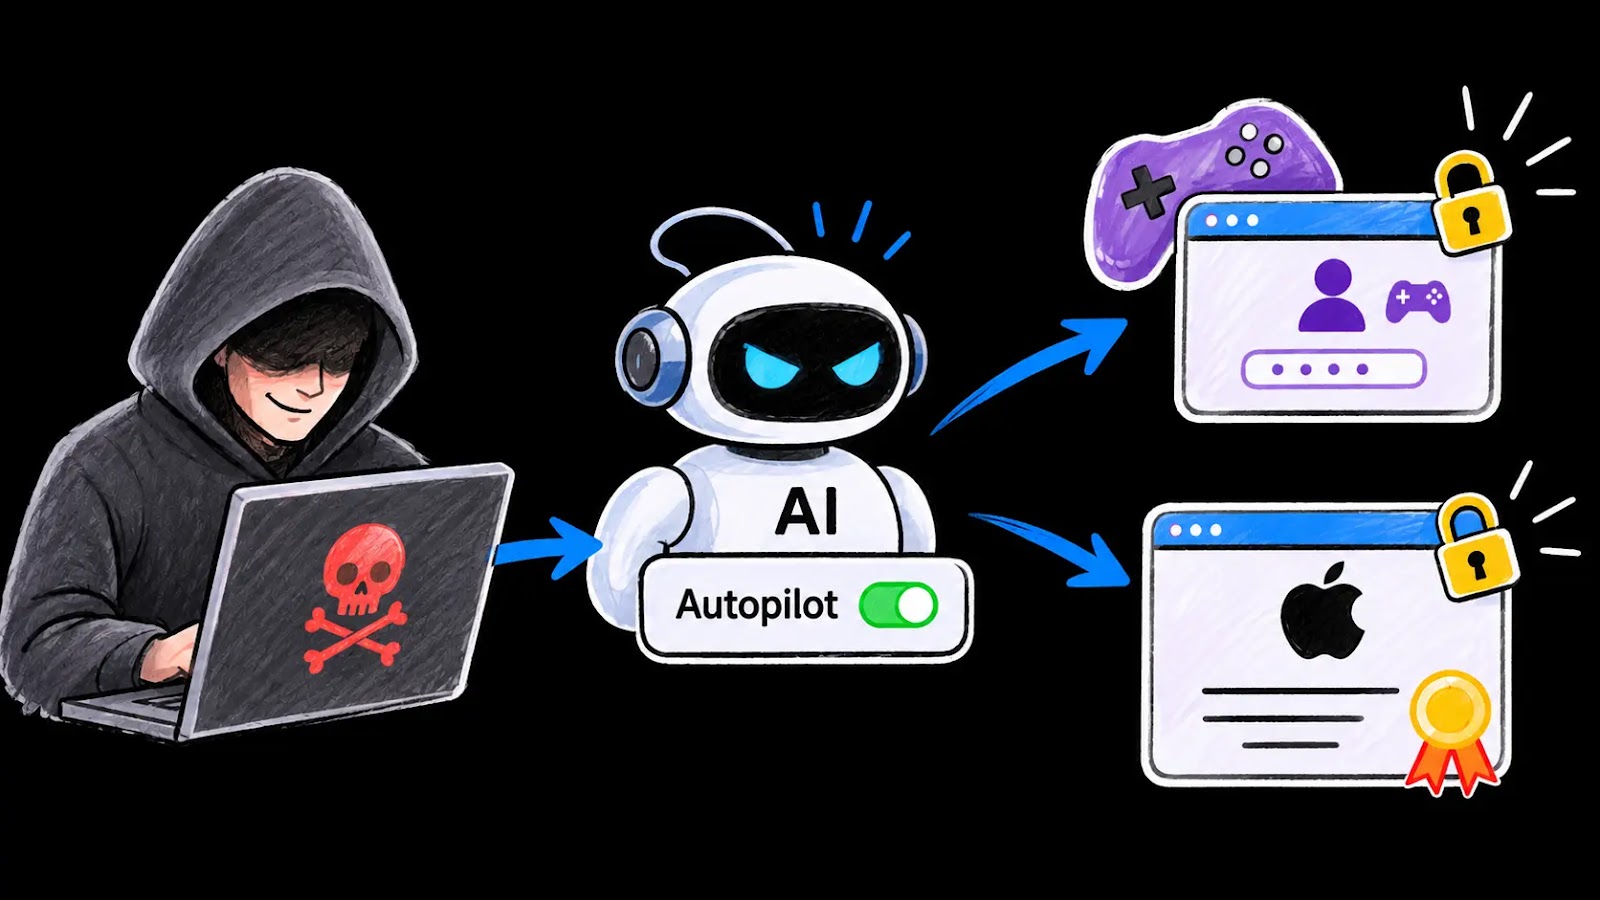
Hackers Put AI Agents on Autopilot to Steal Gaming Accounts and Apple Signing Certificates

ARTEX, a Chinese open-source agentic penetration-testing platform, to run autonomous attacks. The operators set a goal and then mostly check progress. Researchers identified 2,557 systems that host or hosted ARTEX panels, and 1,608 were live and public. Ten misconfigured instances exposed their full databases. Those databases show the models, prompts and actions behind the campaigns. […]

The post Hackers Put AI Agents on Autopilot to Steal Gaming Accounts and Apple Signing Certificates appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Use ARTEX AI to Steal Azure Key Vault Secrets Just 5 Minutes After Finding Exposed GitHub Credentials

Attackers using the ARTEX agentic AI framework to discover exposed GitHub credentials and rapidly compromise cloud environments. In one intrusion, an AI agent progressed from searching GitHub for application secrets to exfiltrating Azure Key Vault data in just five minutes. The activity compresses a familiar attack chain: finding leaked credentials, validating access, mapping resources, and […]

The post Hackers Use ARTEX AI to Steal Azure Key Vault Secrets Just 5 Minutes After Finding Exposed GitHub Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
China-Aligned Hackers Hijack Popular Sogou Keyboard Software to Secretly Install DarkVigil Malware

A China-aligned espionage group abused the update traffic of Sogou Input Method, one of China’s most widely used keyboard apps, to quietly install the DarkVigil implant on victims’ machines. ESET Research, which tracks the actor as SlippyNunchucks, published its findings on November 4, 2026. Tencent, which owns Sogou, has patched the flaw in version 16.10. […]

The post China-Aligned Hackers Hijack Popular Sogou Keyboard Software to Secretly Install DarkVigil Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Develop New HYFLOCK Ransomware That Encrypts Files and Attempts to Block Recovery

HYFLOCK ransomware operators have developed successive Windows encryptors that lock files, access network shares, and attempt to obstruct recovery, while implementation flaws create sharply different outcomes for victims. The investigation distinguishes demonstrated functionality from promotional claims. Although researchers confirmed encryption and scheduled-task registration, they did not establish successful domain-wide propagation or reliable execution after remote […]

The post Hackers Develop New HYFLOCK Ransomware That Encrypts Files and Attempts to Block Recovery appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
ARTEX Hackers Used Claude Code, DeepSeek, and Grok in Attacks Targeting South Korean Banks

A financially motivated threat actor used ARTEX, Claude Code, and multiple large language models in a campaign targeting South Korean financial organizations. Exposed attacker directories revealed session histories, configurations, and operational scripts, showing how AI tooling supported intrusions that resulted in data theft between late September and early October 2026. CrowdStrike’s October 7 investigation assessed […]

The post ARTEX Hackers Used Claude Code, DeepSeek, and Grok in Attacks Targeting South Korean Banks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Spread Marsalek Infostealer Through Fake Game Downloads to Steal Browser Passwords and Cookies

Marsalek, a free malware-as-a-service (MaaS) platform that disguised infostealers as game cheats and utilities for Roblox, Fortnite, Counter-Strike 2, Minecraft, and Grim Dawn. It was active from mid-December 2025 to late May 2026. Researchers counted more than 1,560 registered accounts, over 400 malicious files and more than 29 distribution URLs. Its dashboard let users build […]

The post Hackers Spread Marsalek Infostealer Through Fake Game Downloads to Steal Browser Passwords and Cookies appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
AI-Powered BOSSAI Attacks Expose Patient Records and Emergency Dispatch Data in Taiwan

BOSSAI, an agentic attack platform run by one operator that exposed emergency medical and dispatch data in Taipei. The campaign targeted hundreds of organizations in eleven countries, including emergency services, banks, universities, military systems and e-commerce sites. Confirmed breaches hit universities and emergency providers, with medical data and PII exfiltrated. A Taipei fire department patient-care […]

The post AI-Powered BOSSAI Attacks Expose Patient Records and Emergency Dispatch Data in Taiwan appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Russian Hackers Create Fake US and UK Websites to Target Visitors With Mobile Exploits

A large-scale watering hole campaign that it assesses, with moderate to high confidence, is the work of APT29. APT29 is also tracked as Midnight Blizzard, Cozy Bear and The Dukes, and is widely linked to Russia’s SVR foreign intelligence service. The operation hit iOS and Android users through compromised sites, cloned domains, and a poisoned […]

The post Russian Hackers Create Fake US and UK Websites to Target Visitors With Mobile Exploits appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Fake Microsoft Support Scams Spread Through Online Ads as Researchers Uncover Organized Fraud Network

An organized fraud operation using paid advertisements, Microsoft Azure hosting, and centrally managed telephone numbers to distribute counterfeit Microsoft support pages. The investigation links one backend serving the kit to Mandarin-speaking developers and registration details referencing Hubei, China. Those findings suggest operational connections, not definitive attribution. Crucially, the identified backend appeared in detections at 11 […]

The post Fake Microsoft Support Scams Spread Through Online Ads as Researchers Uncover Organized Fraud Network appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌
❌