U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds PHP flaws PHP2Shell to its Known Exploited Vulnerabilities catalog.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the PHP PHP2Shell vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog:
CVE-2026-109618 – PHP Memory Corruption Vulnerability
CVE-2026-109619 – PHP Stale Internal Request-State Vulnerability
On October 21, PHP released emergency patches for two critical vulnerab
CVE-2026-109619 – PHP Stale Internal Request-State Vulnerability
On October 21, PHP released emergency patches for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619 (CVSS score of 9.2). The flaws affect all PHP versions that handle web requests.
The vulnerable code dates back to PHP 5.4, released in 2012, and resides in the PHP engine itself rather than in individual applications. Attackers can exploit the flaws to execute code remotely by sending specially crafted HTTP requests, without authentication.
Exploitation attempts increased rapidly after the vulnerabilities became public. Cloudflare researchers reported tens of thousands of attempts within the first 45 minutes, hundreds of thousands in just two hours, and millions by October 22.
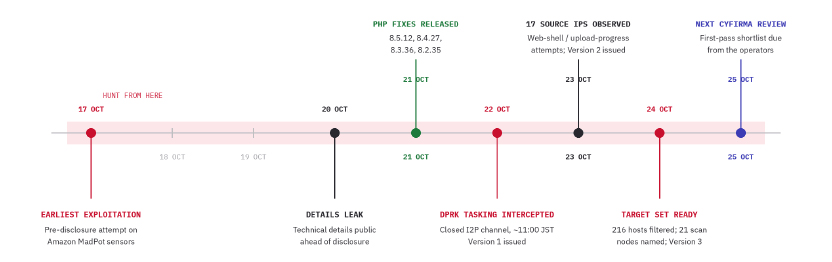
Cyfirma reported that a group of North Korea-linked group has identified 216 hosts that may still be vulnerable to PHP2Shell. The operators communicate through a private I2P channel that Cyfirma has monitored since October 22. On October 24, they reported that 216 hosts appeared to be unpatched or only partly protected, earlier than Cyfirma expected.
They are checking the systems from 21 compromised machines. At the time Cyfirma captured the conversation, the operators had already checked about one-third of the targets.
“Two handles active since March 2026, coordinating in a closed I2P channel; staging infrastructure shared in-channel.” states the cybersecurity firm. “Target set and scan nodes. “On 24 October the operators reported 216 unpatched or partially mitigated hosts and named 21 scan nodes; the same addresses were seen performing web-shell tooling and upload-progress session-poisoning attempts.”
The scanning is slow on purpose. Volume stays low, the machines rotate, and any node that shows filtering or rate limiting gets pulled and never reused. That’s why a rate-based alert will probably stay quiet.
Cyfirma links PHP2Shell scans of 216 vulnerable hosts to a suspected North Korean campaign using AI to rank public exploits.
On October 21, PHP released emergency patches for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on the CVSS scale. The flaws affect all PHP versions that handle web requests. The vulnerable code dates back to PHP 5.4, released in 2012, and resides in the PHP engine itself rather than in individual applications. Attackers can exploit
Cyfirma links PHP2Shell scans of 216 vulnerable hosts to a suspected North Korean campaign using AI to rank public exploits.
On October 21, PHP released emergency patches for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on the CVSS scale. The flaws affect all PHP versions that handle web requests. The vulnerable code dates back to PHP 5.4, released in 2012, and resides in the PHP engine itself rather than in individual applications. Attackers can exploit the flaws to execute code remotely by sending specially crafted HTTP requests, without authentication.
Exploitation attempts increased rapidly after the vulnerabilities became public. Cloudflare researchers reported tens of thousands of attempts within the first 45 minutes, hundreds of thousands in just two hours, and millions by October 22.
Cyfirma reported that a group of North Korea-linked group has identified 216 hosts that may still be vulnerable to PHP2Shell. The operators communicate through a private I2P channel that Cyfirma has monitored since October 22. On October 24, they reported that 216 hosts appeared to be unpatched or only partly protected, earlier than Cyfirma expected.
They are checking the systems from 21 compromised machines. At the time Cyfirma captured the conversation, the operators had already checked about one-third of the targets.
“Two handles active since March 2026, coordinating in a closed I2P channel; staging infrastructure shared in-channel.” states the cybersecurity firm. “Target set and scan nodes. “On 24 October the operators reported 216 unpatched or partially mitigated hosts and named 21 scan nodes; the same addresses were seen performing web-shell tooling and upload-progress session-poisoning attempts.”
The scanning is slow on purpose. Volume stays low, the machines rotate, and any node that shows filtering or rate limiting gets pulled and never reused. That’s why a rate-based alert will probably stay quiet.
Who’s behind it? Cyfirma assesses with moderate confidence a link to the Lazarus family of North Korean groups, based on language, operating style and old habits with PHP web shells and hijacked web servers. It has no shared malware or infrastructure to point to yet, and it admits that a Korean-speaking criminal crew without state backing would fit the same facts. Its confidence in the campaign itself is high.
Government agencies and banks come first. Next in line are logistics, ports, airports and aviation, manufacturing, and online transaction and trading platforms. The countries named are the US, Japan, South Korea, Thailand, Indonesia, Australia, Taiwan, India, Singapore, the UAE, Saudi Arabia and the EU.
Cyfirma has not named any victims or seen the full list of targeted systems. The operators have not announced when they plan to launch attacks, and the researchers have not confirmed that this group has compromised systems on a large scale. Cyfirma gives the campaign an imminence score of 78 out of 100. The operators plan to check all 216 hosts, select the most promising targets, and decide which publicly available exploits to adapt.
The group does not appear to be developing new exploits. Instead, its members use a local AI model to rank public exploit repositories, then test the results manually in a lab. Cyfirma believes this approach could help attackers turn newly disclosed vulnerabilities into working attacks more quickly. However, researchers warn that some proof-of-concept exploits shared online are fake and may contain malware, so downloading and running them can be dangerous.
Technical details leaked on October 20, ahead of coordinated disclosure, and the PHP project shipped fixes on October 21. Apache mod_php with default settings and prefork is the confirmed worst case for 109618, with full unauthenticated code execution. For 109619, PHP-FPM is validated through the upload-progress path.
One correction matters for your temporary controls. Early coverage tied the session upload-progress field to 109618, but PHP’s advisories put it under 109619 only. Disabling upload progress does nothing for 109618, so the two bugs need different stopgaps.
Triggering the bug is easy, but reliable code execution isn’t. The attacker has to land a follow-up request on the same worker and shape heap data into the freed space, otherwise the worker crashes or answers normally. VulnCheck reports working code execution on x86-64 with ASLR enabled against PHP 8.4.10 to 8.4.26, while ARM64 only leaks memory so far.
Short of code execution, attackers have already shown worker crashes, arbitrary file reads through OPcache and a leak of about 67 KB of process memory. The fixed releases are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. PHP 8.1, 8.0 and 7.4 get only minimal backports, and vendors such as cPanel EasyApache, CloudLinux, TuxCare and Plesk carry their own builds, so confirm coverage with yours.
Anything from PHP 5.4 to 7.3 has no fix, so migrate or isolate it. Restart every worker after patching, because a reload that keeps old workers alive leaves the stale state in place. Isolate anything internet-facing that you can’t patch within hours, starting with Apache mod_php.
If you suspect a host is compromised, capture memory and logs before you patch, since a restart destroys the CVE-2026-109619 state. Then rebuild the host from a trusted image and rotate every secret the PHP worker could reach. Hunt back to October 17, the earliest known exploitation, and use long time windows.
The strongest single signal is a PHP or web server process spawning something it never normally spawns. Application logs will usually show nothing, because the bug fires before application code runs. Look for odd multipart POSTs to endpoints that never take uploads, bursts of worker crashes and memory errors, new PHP files in web roots, and new cron jobs, local users or SSH keys.
Cyfirma includes Sigma, Splunk and YARA content, though it says the YARA set hasn’t been tested on real application code yet. It also lists 21 scan-node addresses, 17 source addresses from October 23 and 15 staging addresses, all defanged. Some scan nodes are described as compromised and may belong to victims, so hunt for prior contact before assuming who owns them.
If you can’t patch yet, the advisory suggests limits such as a low post_max_size and disabling session upload progress for 109619. Cyfirma is clear that none of it replaces patching. The operators’ own selection rule is the most useful detail in the whole advisory, because they dropped every host that showed a fixed version or sat behind heavy filtering. That makes a current version string a cheap filter against you, and for once being boring pays off.
“Hosts still bannering older PHP are the ones the operators kept.” Cyfirma states.
Pierluigi Paganini answers questions about the PHP2Shell vulnerability, early exploitation, AI-assisted attacks, and the risks to businesses, servers, and personal data.
1. Your latest report reveals that hackers began exploiting the PHP2Shell vulnerability four days before it was publicly disclosed. First, can you explain what PHP is, how widely it is used across the internet, and why this particular security flaw is so serious?
PHP is a programming language widely used to build websites
Pierluigi Paganini answers questions about the PHP2Shell vulnerability, early exploitation, AI-assisted attacks, and the risks to businesses, servers, and personal data.
1. Your latest report reveals that hackers began exploiting the PHP2Shell vulnerability four days before it was publicly disclosed. First, can you explain what PHP is, how widely it is used across the internet, and why this particular security flaw is so serious?
PHP is a programming language widely used to build websites and web applications. It powers a significant share of the web. PHP2Shell is serious because it can allow attackers to execute commands on a vulnerable server remotely. Depending on the configuration and the server’s privileges, this could give threat actors access to sensitive data, applications and other systems.
2. According to AWS researchers, attacks were already underway before the vulnerability became public. How did researchers uncover this early exploitation, and what does it tell us about the ability of hackers to identify security weaknesses before developers can fix them?
AWS researchers detected exploitation attempts against their honeypot network four days before public disclosure and the release of patches. This shows that attackers can discover or weaponize vulnerabilities before defenders have time to respond. AI-assisted analysis may accelerate this process, helping attackers turn technical information into working exploits in hours rather than days. However, detected attempts do not automatically mean successful compromises.
3. The vulnerability could potentially allow attackers to execute malicious commands on affected servers. What does that mean in practical terms, and what risks does it pose to websites, businesses and the personal information of their users?
Remote command execution means an attacker may be able to make a server run commands without authorization. Depending on the attacker’s access, they could steal data, install malware, change website content, or use the compromised server to attack other systems. Businesses could face service disruption, financial losses and reputational damage. Users may also be exposed if their personal information is stored on an affected system. The actual impact depends on the server’s configuration and security controls.
4. The latest findings raise concerns about the gap between discovering a vulnerability and protecting systems against it. How quickly can attackers exploit these weaknesses, and are businesses adequately prepared to respond when critical security flaws emerge?
The window can be extremely short. In some cases, attackers can develop or adapt an exploit within hours, leaving organizations little time to react. Many businesses still rely on patching schedules that are too slow for internet-facing systems. Organizations need continuous monitoring, rapid patching, tested incident response plans and clear visibility into exposed assets. They should also investigate suspicious activity dating back to before a vulnerability was publicly disclosed, because attacks may already be underway.
5. With PHP powering a significant portion of the internet, could we see further attacks exploiting this vulnerability? What should website operators do immediately to protect their systems, and should ordinary internet users be concerned about their data?
Further attacks are possible, particularly against systems that remain unpatched or exposed. Website operators should apply the relevant security updates, check whether their PHP applications are vulnerable, and review logs for suspicious activity dating back to October 17. They should also restrict access and investigate signs of compromise. Ordinary users do not need to panic, but they should keep their accounts protected with unique passwords and multi-factor authentication where available. Whether personal data is at risk depends on which services they use and whether those systems were compromised.
AI-assisted tools are increasingly being used to analyze code and identify vulnerabilities. How much of a role could artificial intelligence play in helping attackers discover and exploit flaws like PHP2Shell, and can defenders use the same technology to their advantage?
AI can help analyze code, identify suspicious patterns and speed up the process of turning a vulnerability into a working exploit. This lowers some of the technical barriers for attackers and may shorten the time between discovering a flaw and exploiting it. However, AI is not the only factor, and we should not assume that every attack is AI-driven. Defenders can use the same capabilities to review code, prioritize vulnerabilities, analyze logs and detect suspicious behavior. The real advantage comes from combining AI with reliable data, skilled security teams and effective response processes.
This case shows that attackers may exploit a vulnerability before a patch is available. Does this mean traditional vulnerability management is no longer enough, and how should organizations rethink their security strategy?
Traditional vulnerability management remains essential, but patching alone is not enough when attackers may act before a fix becomes available. Organizations need to know which internet-facing systems they operate, understand their exposure and have additional controls in place. These include limiting access to vulnerable services, monitoring suspicious activity, applying temporary mitigations and preparing incident response procedures. They should also investigate whether systems were targeted before the vulnerability was disclosed. The goal is to reduce the opportunity for exploitation and detect attacks quickly, even when a patch is not yet available.
Below is another interview I gave to TRT World discussing critical PHP vulnerabilities, the risks they pose to web servers, and the growing number of exploitation attempts. I explain why rapid patching and effective security measures are essential to minimize potential damage.
PHP warns of a new, unlikely code execution flaw, CVE-2026-115560, and advises disabling session upload progress until a fix is released.
PHP has warned of a new code execution vulnerability, tracked as CVE-2026-115560, just two days after releasing emergency patches for the critical PHP2Shell flaws.
The vulnerability affects only a specific PHP configuration that PHP says is unlikely to be used in practice. An application must meet several conditions: it must configure session.serialize
PHP warns of a new, unlikely code execution flaw, CVE-2026-115560, and advises disabling session upload progress until a fix is released.
PHP has warned of a new code execution vulnerability, tracked as CVE-2026-115560, just two days after releasing emergency patches for the critical PHP2Shell flaws.
The vulnerability affects only a specific PHP configuration that PHP says is unlikely to be used in practice. An application must meet several conditions: it must configure session.serialize_handler as php_binary or php_serialize, change it to php at runtime using ini_set(), and make this change before calling session_start(). Session upload progress must also remain enabled.
In an advisory published on October 23, the project recommended disabling session upload progress until a fix becomes available in a regular release. The vulnerability is separate from PHP2Shell and is not fixed by the October 21 updates for PHP versions 8.2.35, 8.3.36, 8.4.27 and 8.5.12.
“The issue can only occur under an unusual combination of configuration and application code. An application must set session.serialize_handler to php_binary or php_serialize in its configuration and then switch it to php at runtime with ini_set() before calling session_start(). Session upload progress must also still be enabled.” reads the advisory. “Applications that never change the serialize handler at runtime can keep the feature enabled. Since this setup is unlikely in practice, we are handling it in the regular release cycle and will publish a full advisory for CVE-2026-115560 with the next release.”
Applications that do not change the serialization handler while running are not exposed through this attack path, even if session upload progress is enabled.
PHP recommends a simple temporary fix: set session.upload_progress.enabled=0 until the next routine bugfix release. This is the same mitigation already recommended in the October 21 advisory for CVE-2026-109619. Administrators who applied this setting and have kept it in place do not need to take further action for this issue.
Session upload progress is enabled by default and allows applications to track the progress of file uploads. Disabling it reduces exposure to this specific vulnerability path.
PHP will fix CVE-2026-115560 through its regular release cycle because the vulnerable setup is uncommon. It plans to publish a full advisory with the next release. PHP has not yet identified affected versions, confirmed when the fix will arrive, assigned a severity score, or explained whether the flaw shares a root cause with CVE-2026-109619. No attacks targeting this new issue have been reported.
On October 21, PHP released emergency patches for two critical vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS score of 9.2), affecting every PHP version that handles web requests. The bug code dates back to PHP 5.4 from 2012, lives in the PHP engine itself rather than in any application, and allows unauthenticated remote code execution via crafted HTTP requests.
Cloudflare researchers observed tens of thousands of exploit attempts within 45 minutes of public disclosure, hundreds of thousands within two hours, and millions by October 22.
PHP2Shell attacks have surged into the millions, but no successful exploitation is confirmed. Patch it immediately.
On October 21, PHP released emergency patches for two critical vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS score of 9.2), affecting every PHP version that handles web requests. The bug code dates back to PHP 5.4 from 2012, lives in the PHP engine itself rather than in any application, and allows unauthenticated remote code execution via crafted HTTP req
PHP2Shell attacks have surged into the millions, but no successful exploitation is confirmed. Patch it immediately.
On October 21, PHP released emergency patches for two critical vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS score of 9.2), affecting every PHP version that handles web requests. The bug code dates back to PHP 5.4 from 2012, lives in the PHP engine itself rather than in any application, and allows unauthenticated remote code execution via crafted HTTP requests.
Cloudflare researchers observed tens of thousands of exploit attempts within 45 minutes of public disclosure, hundreds of thousands within two hours, and millions by October 22.
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
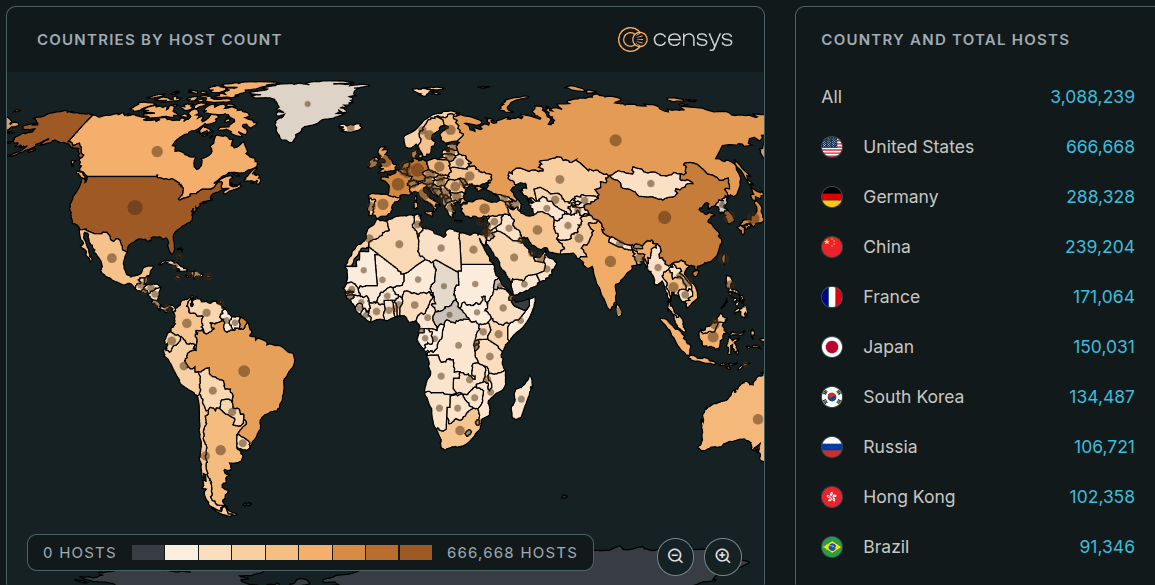
As of October 23, Censys counts over 34.4 million PHP services still running vulnerable versions. Governments, hospitals, and schools across Asia, Europe, and North America have preemptively taken services offline rather than wait.
Below is an image showing the hosts potentially vulnerable to CVE-2026-109618 and/or CVE-2026-109619.
Security firms using honeypots report the same pattern: attackers are scanning many servers and trying to exploit the PHP flaws, but no successful remote code execution has been confirmed in real-world attacks. Sophos says this suggests that attackers are also struggling to exploit the vulnerabilities. Even its own security team needed more effort than expected, despite using AI, to develop a working exploit.
However, the risk is growing. VulnCheck researchers have developed an exploit that bypasses ASLR, a security feature that randomizes where code is stored in memory. By combining both vulnerabilities, they can use a memory leak to bypass this protection and run code on the target system. The exploit works, even though there is no evidence of widespread use yet.
The attempts that have been caught so far are mostly scanning, fingerprinting, and botnet delivery attempts. Cowrai’s analysis of PHP2Shell traffic in the wild found connections to a Mirai variant called Potassium, which contacts a C2 server, checks for an HTTP 200 response, then downloads a Linux executable as a follow-on payload.
“The payload, a likely Mirai botnet variant known as Potassium, was not delivered since the exploitation attempt was unsuccessful due to being blocked by Sophos countermeasures.” states the report published by Sophos. “However, analysis of the sample revealed that is an updated and significantly expanded version of the Mirai-derived botnet variant identified in early 2026.”
The malware can download additional files and disrupt networks. It contacts a hard-coded command-and-control server, checks that the server responds successfully, and downloads a file designed to run on Linux. If normal address lookup fails, it can use public DNS servers such as Google DNS and Cloudflare DNS. Like other Mirai malware, it can also launch distributed denial-of-service (DDoS) attacks.
Arctic Wolf found that both malware samples had Ethereum Name Service (ENS) resolution disabled, meaning the feature was available but not active.
“ENS resolution was disabled in both samples, indicating that the capability was present but inactive.” states Arctic Wolf. “If enabled in future variants, it could complicate disruption by reducing reliance on registrars and DNS providers, requiring defenders to block the ENS names, RPC infrastructure, and resolved command-and-control addresses.”
The botnet’s developers have already added the ability to use ENS to find command-and-control (C2) servers. This could help them keep their infrastructure online and make it harder for authorities to take down their domains, but the feature has not yet been enabled.
Sophos blocked the attempted Potassium delivery before it succeeded. But analysis of the sample itself showed it’s a significantly expanded version of the Mirai variant spotted earlier in 2026, with added DDoS capabilities and fallback DNS resolution using public servers like 8.8.8.8 and 1.1.1.1 hardcoded as backup.
PHP2Shell is being compared to Log4Shell because it affects a huge number of systems. The flaw is in PHP itself, so it can affect websites, content management systems and shared hosting services. Even a basic WordPress site with no extra plugins is at risk if it uses a vulnerable PHP version.
Fixes are available in PHP versions 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Older versions, including 7.4, 8.0 and 8.1, need fixes provided by their software distributors or an upgrade to a supported version.
Cisco Talos notes that scanning for flaws and using public exploit code is easier than building attacks into custom tools. Advanced attackers may still be developing those tools, so administrators should use this time to patch vulnerable systems.
“The true impact of this vulnerability will take time to evaluate.” concludes Talos. “These types of vulnerabilities that impact core technologies tend to cascade into other platforms and applications as they evaluate impact and provide associated patching, harkening back to the waves of exploitation that we saw after Log4J.”
AWS detected PHP2Shell exploit attempts four days before disclosure, highlighting the risk of attackers exploiting critical flaws before patches arrive.
Attackers attempted to exploit two critical PHP vulnerabilities four days before the flaws became public, according to Amazon Threat Intelligence.
“Amazon Threat Intelligence identified a PHP2Shell exploitation attempt dating to Oct. 17, 2026, in MadPot telemetry, four days before public disclosure of CVE-2026-109618 and CVE-2026-109619.
AWS detected PHP2Shell exploit attempts four days before disclosure, highlighting the risk of attackers exploiting critical flaws before patches arrive.
Attackers attempted to exploit two critical PHP vulnerabilities four days before the flaws became public, according to Amazon Threat Intelligence.
“Amazon Threat Intelligence identified a PHP2Shell exploitation attempt dating to Oct. 17, 2026, in MadPot telemetry, four days before public disclosure of CVE-2026-109618 and CVE-2026-109619.” reads the report published by Amazon team.”The exploit attempt originated from an IP address associated with a commercial anonymization network. While the vulnerability was under embargo, the targeting of a honeypot from an anonymized IP address suggests the activity was conducted by a threat actor, though it remains unclear how the actor acquired exploit information prior to disclosure.”
The activity began on October 17, 2026, and appeared in telemetry from MadPot, AWS’s network of honeypots designed to attract and study malicious activity. The company said the first attempt targeted a honeypot from an IP address linked to a commercial anonymization network. The vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, were still under embargo at the time.
AWS believes the use of anonymized infrastructure suggests a threat actor was behind the activity. However, the company hasn’t established how the attacker obtained information about the vulnerabilities before their public disclosure, nor has it confirmed that the early attempts would have succeeded against real-world systems.
The first attempt wasn’t an isolated event. AWS detected multiple proof-of-concept exploits on October 21, with the earliest appearing at around 02:00 UTC, roughly 12 hours before the scheduled public release and patch at 14:00 UTC.
Between 02:00 and 08:00 UTC that day, AWS observed further attempts against MadPot from additional anonymized infrastructure. The payloads and anonymization services varied, leading the company to suspect that multiple actors were involved.
After the embargo ended and PHP released the fixes, more proof-of-concept exploits appeared within hours. AWS reported that attackers used them against its sensors almost immediately, describing PHP2Shell as being broadly exploited in the wild.
The findings show why the date of a public security advisory can’t always serve as the starting point for an incident investigation. In this case, defenders had to account for activity that began before they could publicly identify the vulnerabilities.
“The actual payloads and choices in anonymization infrastructure varied, suggesting these were multiple actors.” continues the report. “Technical analysis is ongoing, and it’s unclear if any of these attempts would have succeeded in real-world systems.”
PHP2Shell refers to two critical flaws in the PHP runtime that can allow unauthenticated remote code execution. An attacker may be able to send a specially crafted web request and run commands on a vulnerable server without first logging in.
PHP published fixes on October 21. The corrected releases are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, according to the official PHP security notice.
The vulnerabilities affect PHP itself, rather than a specific website application. As a result, updating WordPress, Drupal or another application won’t fix the underlying problem if the server continues to run a vulnerable PHP runtime.
AWS says there is no configuration-only workaround that fully addresses both flaws. Organizations should install the fixed PHP version as soon as possible and check whether their hosting provider, operating system vendor or container image has supplied the necessary update.
For systems that can’t be patched immediately, AWS suggests considering whether blocking multipart file uploads is practical. Administrators should assess the impact on their applications before applying that restriction, and they shouldn’t treat it as a replacement for installing the fixes.
AWS recommends reviewing web server logs for suspicious requests, particularly POST requests containing the PHP_SESSION_UPLOAD_PROGRESS string in multipart form data. Security teams should also look for unexpected processes launched by PHP and unexplained changes to files on web application servers.
These checks matter because an attack may leave evidence beyond the original HTTP request. Unexpected command interpreters, newly created files or unusual process activity can help investigators determine whether an attacker progressed beyond probing a vulnerable endpoint.
AWS also published six IP addresses associated with observed activity:
103.216.220.92, observed on October 17
31.223.184.166, observed on October 21
37.19.200.5, observed on October 21
134.209.159.64, observed on October 21
103.114.163.188, observed on October 21
95.217.98.37, observed on October 21
These addresses require careful handling. AWS warns that some belong to shared anonymization infrastructure and aren’t exclusive to PHP2Shell activity, so organizations should investigate matching events rather than automatically blocking every address.
The Cloudflare analysis of PHP2Shell provides additional context. Cloudflare said it had deployed web application firewall protections before public disclosure and had already observed attack traffic targeting its customers, including attempts to change payloads to evade those protections.
A web application firewall can help reduce exposure, but it doesn’t replace patching. Defenders should combine updated software with log analysis, process monitoring and checks for suspicious file changes.
AWS draws a broader lesson from the incident: organizations shouldn’t assume that exploitation begins only after a vulnerability becomes public. The October 17 activity shows that attackers may obtain or develop exploit information while a flaw is still under coordinated disclosure.
Attackers are using AI to develop exploits faster, sometimes within hours of a patch being released. Security teams need to patch critical systems quickly and investigate attacks from the earliest known date. For PHP2Shell, AWS recommends checking logs and activity from October 17 onward, including suspicious behavior that detection tools may not yet recognize.
PHP will release emergency fixes for two critical RCE flaws rated 9.2, as researchers warn of potential risks to exposed and unsupported systems.
PHP is preparing an emergency security release for two critical vulnerabilities that could let attackers execute code remotely on affected servers. The update is scheduled for today, October 21 at 14:00 UTC, after details of the flaws leaked online ahead of their planned disclosure.
I have successfully recreated & lab/field tested CVE-2026-
PHP will release emergency fixes for two critical RCE flaws rated 9.2, as researchers warn of potential risks to exposed and unsupported systems.
PHP is preparing an emergency security release for two critical vulnerabilities that could let attackers execute code remotely on affected servers. The update is scheduled for today, October 21 at 14:00 UTC, after details of the flaws leaked online ahead of their planned disclosure.
I have successfully recreated & lab/field tested CVE-2026-109618 / CVE-2026-109619
The PHP security team confirmed both vulnerabilities carry a CVSS v4.0 score of 9.2. It hasn’t yet published their technical details, confirmed the affected versions, or identified the releases that will fix them. The official PHP announcement says the full information will accompany the security updates.
“The PHP security team would like to give advance notice of an upcoming security release. It is scheduled for Wednesday, 21 October 2026 at 14:00 UTC. It addresses two critical vulnerabilities, both rated CVSS v4.0 9.2.” states the announcement.
“All PHP users are encouraged to prepare now so they can upgrade as soon as the release is available. We reserve the right to release earlier should details of either vulnerability become public, or should evidence of active exploitation appear in the wild. Full details, affected versions, and the fixed versions will be published with the release.”
Researchers dubbed the vulnerabilities as php2shell, using the identifiers CVE-2026-109618 and CVE-2026-109619. The identifiers and the claim that the flaws allow remote code execution come from reports outside PHP’s initial advisory, rather than from a published technical analysis by the project.
According to the Hacker News, the two critical PHP vulnerabilities would be disclosed on October 22. The post described them as remote code execution flaws with CVSS scores of 10.0 and said they affected versions dating back to PHP 5.
Researchers at watchTowr subsequently confirmed that the vulnerabilities were real and said the information had leaked before the agreed disclosure date. The company also reported that it had reproduced one of the flaws, CVE-2026-109618, but withheld technical details while patches remained unavailable.
PHP published its advance security notice later that day, setting the release for Wednesday, October 21, one day before the date reported in the leak. The team also reserved the right to release the fixes earlier if technical details became public or it found evidence of active exploitation.
The difference between the reported severity scores matters. The leaked information cited CVSS 10.0, while PHP officially rated both vulnerabilities 9.2 under CVSS version 4.0. Until the vendor publishes its technical advisory, the official score is the one administrators should use when describing PHP’s assessment.
The main concern is the possibility that the flaws affect a wide range of PHP installations. Reports have suggested that versions from PHP 5 onward could be vulnerable, but watchTowr’s FAQ explicitly notes that the scope hasn’t been confirmed by an official vendor advisory.
“The report claims the vulnerability affects every PHP version from PHP 5 onward, though this scope has not been confirmed by an official vendor advisory. No specific configuration or feature requirement has been described in the available report.” states watchTowr.
“Until PHP publishes an official advisory, security teams cannot determine which specific deployments face the greatest exposure; every organization running PHP in production should prepare to act quickly once a fix is confirmed.”
Administrators also don’t yet know which PHP components are involved or whether exploitation depends on a particular configuration or deployment mode. Those details will determine how attackers could reach the vulnerable code and which systems need the most urgent attention.
PHP’s supported versions policy adds another complication. The project currently supports four release branches, PHP 8.2 through 8.5, while older branches no longer receive security updates from the PHP project.
The anticipated fixes are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, according to tracking by Mallory. These version numbers were predictions ahead of the release, not confirmed package versions in PHP’s advance notice.
If the vulnerabilities affect older releases, organizations running PHP 8.1, 8.0, 7.x or 5.x may not receive an upstream fix. They may need to upgrade to a supported branch, apply any security updates provided by their operating system vendor, or restrict access to affected systems until they can remediate them.
Research by Mallory highlights the scale of the potential problem. Using Shodan data collected on October 20, the company identified about 884,000 internet-facing hosts reporting PHP 8.1 or an older version, representing roughly 59% of the 1.5 million hosts that disclosed a PHP version in their HTTP banners.
These figures don’t establish that every host is vulnerable. The count identifies systems running older PHP versions that may not receive a direct fix from the PHP project if the reported scope is confirmed. Another 740,000 hosts reported PHP without revealing a version, making it harder to assess the full exposure.
The numbers also count hosts, not individual websites or organizations. Shared hosting can place many websites on the same server, while software vendors and hosting providers may bundle PHP into products that administrators don’t recognize as PHP installations.
That makes asset discovery an important first step. Security teams should check web servers, Windows systems, vendor appliances, hosting control panels such as cPanel and Plesk, and applications that include their own PHP runtime.
PHP hasn’t published a workaround in its advance notice. Until the fixes become available, organizations should identify their PHP installations and prepare to install the correct update as soon as the vendor publishes it.
Internet-facing systems should take priority, particularly servers running business-critical applications or processing sensitive information. Administrators should also check with their Linux distribution and hosting provider, since vendors sometimes backport security fixes without changing the upstream version number in the way expected.
For installations running end-of-life PHP, the options are less comfortable. Organizations should plan an upgrade or reduce exposure by taking vulnerable services offline, restricting access through a VPN or IP allowlist, or placing them behind a web application firewall while a longer-term fix is prepared.
CERT-EU’s security advisory recommends considering the isolation of internet-facing applications from public networks when immediate patching isn’t possible.
“CERT-EU strongly recommends identifying PHP-based applications and preparing to patch as soon as fixed versions become available.”states CERT-EU. “Where immediate remediation is not feasible, organisations should consider isolating internet-facing applications from public networks until a fix can be applied.”
This is a precautionary measure, not a confirmed workaround for either PHP vulnerability.
Monitoring process activity can also help identify suspicious behavior. On Linux, security teams should investigate PHP-related processes such as php-fpm, php-cgi, httpd or apache2 launching unexpected shells, interpreters or download utilities, including sh, bash, python, curl and wget.
Florian Roth’s open-source process-watcher can log programs launched by PHP processes and record their command lines. It provides visibility into process activity, but it doesn’t block an exploit or prevent a malicious command from running.
If an investigation uncovers suspicious activity, teams should isolate the affected server, preserve PHP and web server logs, and check for newly created files in web roots, web shells, unexpected scheduled tasks, cron jobs and user accounts. Those steps can help determine whether an attacker has already gained access, rather than simply whether a server was exposed.
As of October 21, Huntress said it hadn’t observed exploitation in attacks against its partner environments and hadn’t developed or reproduced a proof of concept. watchTowr’s FAQ also listed no reported exploitation and no vendor patch at the time of its update.
That doesn’t mean administrators can safely wait to assess their exposure. Once technical details and fixes become public, attackers may be able to develop working exploits more quickly, particularly if the vulnerabilities affect widely deployed versions of PHP.
A previous PHP flaw illustrates how quickly the situation can change. When CVE-2024-4577, which affected PHP running in CGI mode on Windows, became public in June 2024, Akamai reported exploit attempts against its honeypot servers within 24 hours.
The scheduled release should answer the questions administrators still face: which versions are affected, which components contain the flaws, whether exploitation requires a particular configuration, and which updates fix each issue. Until then, the priority is straightforward: know where PHP runs, prepare the updates, and avoid leaving internet-facing systems on unsupported versions without additional protection.

 Entrar



 (@eastdakota)