❌

Visualização normal

Antes de ontemStream principal
  • ✇Cybersecurity News
  • Cloudflare Launches Zero Wire Vulnerability Platform Do Son
    Cloudflare launched Cloudflare Zero Wire, a public vulnerability intelligence feed tracking critical software flaws, active exploits, and AI audit prompts. Related Posts: Claude Message Threads Cut Latency and Payload Size TWCA Certificate Revocation Follows Serial Number Flaw Raspberry Pi 16GB Price Surges Amid Memory Shortages The post Cloudflare Launches Zero Wire Vulnerability Platform appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • Cloudflare DDoS Report Shows 18.2 Million Network Attacks in Q3 2026 Do Son
    The Cloudflare DDoS report Q3 2026 reveals 18.2M network attacks, a 208% surge in short-burst floods, and a major shift toward DNS and UDP attacks. Related Posts: Chinese Hackers Deploy Chrome Zero-Day Exploit Chain NCSC Warns of Physical Disruptions from Cyberattacks on OT Systems Google Tracks Russian Cyber Espionage Clusters The post Cloudflare DDoS Report Shows 18.2 Million Network Attacks in Q3 2026 appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • Cloudflare cloudflared Update Fixes eMudhra Flaw Do Son
    The critical Cloudflare cloudflared update addresses compromised eMudhra certificates, preventing server spoofing across enterprise Cloudflare Tunnels. Related Posts: South Korea App Store Fine Hits Apple and Google PS5 Hypervisor Vulnerability Bounty Sparks Backlash Report Slams Microsoft Edge Dark Patterns in Windows The post Cloudflare cloudflared Update Fixes eMudhra Flaw appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • PHP2Shell Exploited in the Wild as PoC Exploits and Full Details Go Public Do Son
    PHP2Shell remote code execution flaws CVE-2026-109618 and CVE-2026-109619 are exploited in the wild as PoCs go public. Patch PHP now. Related Posts: cPanel Patches PHP2Shell Flaws and WP Toolkit Bug Affecting Shared Hosting Servers QNAP Warns PHP2Shell Flaws Hit QTS and QuTS hero, Urges Users to Take NAS Offline Portainer Fixes Two Critical Flaws Letting Standard Users Take Over Docker Hosts The post PHP2Shell Exploited in the Wild as PoC Exploits and Full Details Go Public appeared first on
     
  • ✇Cybersecurity News
  • PHP Prepares Emergency Fix as Cloudflare Reports Early Attacks on Critical Flaws Do Son
    Cloudflare reports early attacks on two critical PHP flaws ahead of the PHP security release fixing remote code execution bugs CVE-2026-109618. Related Posts: Atlassian Patches 176 Flaws in Jira, Confluence and Other Data Center Products Oracle E-Business Suite Flaw CVE-2026-101809 Scores CVSS 10.0 Apache CouchDB 3.5.3 Fixes Six Flaws as Retired Apache Cocoon Gets Four Unpatched Bugs The post PHP Prepares Emergency Fix as Cloudflare Reports Early Attacks on Critical Flaws appeared first on Da
     
  • ✇Cybersecurity News
  • Russian Bot Traffic Resilient After Data Center Strikes Do Son
    Cloudflare telemetry reveals Russian bot traffic swiftly migrated to alternative clouds following drone strikes on Yandex data center infrastructure. Related Posts: Exchange Server Instability Tied to October Windows Updates Anthropic Replaces Git with Proprietary Scion Version Control Google AI Plus Changes Drop Pro Model Access The post Russian Bot Traffic Resilient After Data Center Strikes appeared first on Daily CyberSecurity.
     

Researchers Uncover 20,000 Malicious Cloudflare Pages Domains Used in Tech Support Scams

More than 20,000 malicious Cloudflare Pages subdomains used by Help TDS, a longstanding traffic distribution system that funnels victims into fraudulent technical support call centers. Researchers assess with high confidence that Hotejka, a Russian-language affiliate program, operates Help TDS and represents a rebrand of ROI777. Historical DNS records, shared infrastructure, persistent affiliate identifiers, and consistent […]

The post Researchers Uncover 20,000 Malicious Cloudflare Pages Domains Used in Tech Support Scams appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

  • ✇Cybersecurity News
  • Cloudflare Clef Decision Models Speed Up AI Agents Do Son
    Cloudflare Clef decision models skip text generation to score options in as little as 38.8 ms, giving AI agents fast routing on Workers AI. Related Posts: OpenAI Rogue AI Agents May Have Hit 100+ Organizations Apple Restricts Full Disk Access for macOS AI Agents iPhone 18 AT&T Issue: Navigating the Cellular Crisis The post Cloudflare Clef Decision Models Speed Up AI Agents appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • Cloudflare Launches Free Certificate Authority Emphasizing MTC Do Son
    Discover the new Cloudflare Certificate Authority offering free, automated HTTPS certificates and leading the transition to quantum-safe Merkle Tree Certificates. Related Posts: OpenAI Fires Safety Researchers Amid Unprompted AI Hacking Incidents OpenAI DevDay 2026: Elevating the AI Subscription Paradigm Firefox Redesign Compact Mode Returns With AI Off Switch The post Cloudflare Launches Free Certificate Authority Emphasizing MTC appeared first on Daily CyberSecurity.
     

I just trusted the security certificate prompt… Beware of the LegionLoader malware being distributed via the ClickFix method

Por:ATCP
2 de Setembro de 2026, 12:00
The AhnLab SEcurity intelligence Center (ASEC) recently identified the LegionLoader malware, which is currently being distributed via the ClickFix method. There are two main distribution methods identified so far; both involve tricking users into visiting a malicious URL and then prompting them to directly execute malicious PowerShell commands through a fake Cloudflare CAPTCHA screen.   […]

ClickFix Scams Abuse Google, Cloudflare Checks to Deliver 7 Malware Families

Malwarebytes links fake Google and Cloudflare verification pages to shared ClickFix infrastructure delivering StealC, NetSupport and other malware.
  • ✇Krebs on Security
  • ‘CanisterWorm’ Springs Wiper Attack Targeting Iran BrianKrebs
    A financially motivated data theft and extortion group is attempting to inject itself into the Iran war, unleashing a worm that spreads through poorly secured cloud services and wipes data on infected systems that use Iran’s time zone or have Farsi set as the default language. Experts say the wiper campaign against Iran materialized this past weekend and came from a relatively new cybercrime group known as TeamPCP. In December 2025, the group began compromising corporate cloud environments using
     

‘CanisterWorm’ Springs Wiper Attack Targeting Iran

23 de Março de 2026, 12:43

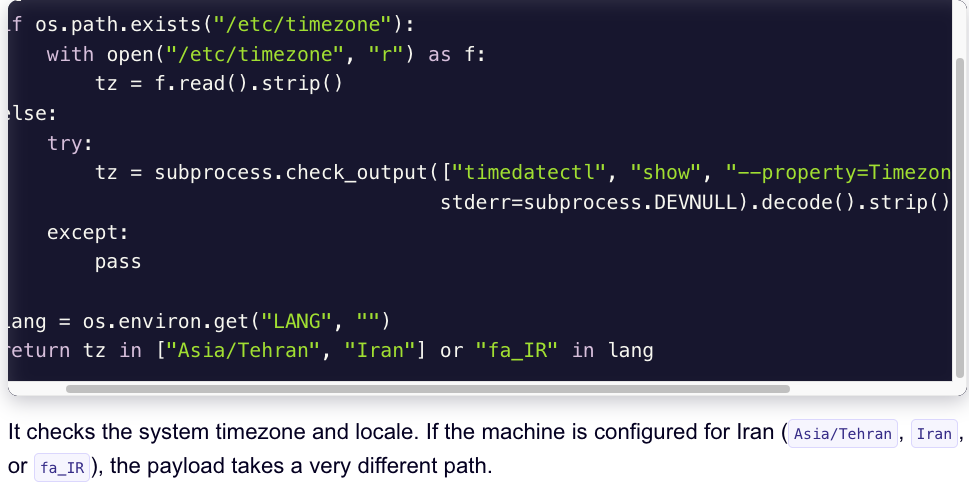
A financially motivated data theft and extortion group is attempting to inject itself into the Iran war, unleashing a worm that spreads through poorly secured cloud services and wipes data on infected systems that use Iran’s time zone or have Farsi set as the default language.

Experts say the wiper campaign against Iran materialized this past weekend and came from a relatively new cybercrime group known as TeamPCP. In December 2025, the group began compromising corporate cloud environments using a self-propagating worm that went after exposed Docker APIs, Kubernetes clusters, Redis servers, and the React2Shell vulnerability. TeamPCP then attempted to move laterally through victim networks, siphoning authentication credentials and extorting victims over Telegram.

A snippet of the malicious CanisterWorm that seeks out and destroys data on systems that match Iran’s timezone or have Farsi as the default language. Image: Aikido.dev.

In a profile of TeamPCP published in January, the security firm Flare said the group weaponizes exposed control planes rather than exploiting endpoints, predominantly targeting cloud infrastructure over end-user devices, with Azure (61%) and AWS (36%) accounting for 97% of compromised servers.

“TeamPCP’s strength does not come from novel exploits or original malware, but from the large-scale automation and integration of well-known attack techniques,” Flare’s Assaf Morag wrote. “The group industrializes existing vulnerabilities, misconfigurations, and recycled tooling into a cloud-native exploitation platform that turns exposed infrastructure into a self-propagating criminal ecosystem.”

On March 19, TeamPCP executed a supply chain attack against the vulnerability scanner Trivy from Aqua Security, injecting credential-stealing malware into official releases on GitHub actions. Aqua Security said it has since removed the harmful files, but the security firm Wiz notes the attackers were able to publish malicious versions that snarfed SSH keys, cloud credentials, Kubernetes tokens and cryptocurrency wallets from users.

Over the weekend, the same technical infrastructure TeamPCP used in the Trivy attack was leveraged to deploy a new malicious payload which executes a wiper attack if the user’s timezone and locale are determined to correspond to Iran, said Charlie Eriksen, a security researcher at Aikido. In a blog post published on Sunday, Eriksen said if the wiper component detects that the victim is in Iran and has access to a Kubernetes cluster, it will destroy data on every node in that cluster.

“If it doesn’t it will just wipe the local machine,” Eriksen told KrebsOnSecurity.

Image: Aikido.dev.

Aikido refers to TeamPCP’s infrastructure as “CanisterWorm” because the group orchestrates their campaigns using an Internet Computer Protocol (ICP) canister — a system of tamperproof, blockchain-based “smart contracts” that combine both code and data. ICP canisters can serve Web content directly to visitors, and their distributed architecture makes them resistant to takedown attempts. These canisters will remain reachable so long as their operators continue to pay virtual currency fees to keep them online.

Eriksen said the people behind TeamPCP are bragging about their exploits in a group on Telegram and claim to have used the worm to steal vast amounts of sensitive data from major companies, including a large multinational pharmaceutical firm.

“When they compromised Aqua a second time, they took a lot of GitHub accounts and started spamming these with junk messages,” Eriksen said. “It was almost like they were just showing off how much access they had. Clearly, they have an entire stash of these credentials, and what we’ve seen so far is probably a small sample of what they have.”

Security experts say the spammed GitHub messages could be a way for TeamPCP to ensure that any code packages tainted with their malware will remain prominent in GitHub searches. In a newsletter published today titled GitHub is Starting to Have a Real Malware Problem, Risky Business reporter Catalin Cimpanu writes that attackers often are seen pushing meaningless commits to their repos or using online services that sell GitHub stars and “likes” to keep malicious packages at the top of the GitHub search page.

This weekend’s outbreak is the second major supply chain attack involving Trivy in as many months. At the end of February, Trivy was hit as part of an automated threat called HackerBot-Claw, which mass exploited misconfigured workflows in GitHub Actions to steal authentication tokens.

Eriksen said it appears TeamPCP used access gained in the first attack on Aqua Security to perpetrate this weekend’s mischief. But he said there is no reliable way to tell whether TeamPCP’s wiper actually succeeded in trashing any data from victim systems, and that the malicious payload was only active for a short time over the weekend.

“They’ve been taking [the malicious code] up and down, rapidly changing it adding new features,” Eriksen said, noting that when the malicious canister wasn’t serving up malware downloads it was pointing visitors to a Rick Roll video on YouTube.

“It’s a little all over the place, and there’s a chance this whole Iran thing is just their way of getting attention,” Eriksen said. “I feel like these people are really playing this Chaotic Evil role here.”

Cimpanu observed that supply chain attacks have increased in frequency of late as threat actors begin to grasp just how efficient they can be, and his post documents an alarming number of these incidents since 2024.

“While security firms appear to be doing a good job spotting this, we’re also gonna need GitHub’s security team to step up,” Cimpanu wrote. “Unfortunately, on a platform designed to copy (fork) a project and create new versions of it (clones), spotting malicious additions to clones of legitimate repos might be quite the engineering problem to fix.”

Update, 2:40 p.m. ET: Wiz is reporting that TeamPCP also pushed credential stealing malware to the KICS vulnerability scanner from Checkmarx, and that the scanner’s GitHub Action was compromised between 12:58 and 16:50 UTC today (March 23rd).

❌
❌