❌

Visualização normal

Antes de ontemStream principal
  • ✇Security Affairs
  • North Korean IT Workers Used Stolen US Identities to Earn $3 Million Pierluigi Paganini
    The FBI raided 40 Texas homes over a North Korean scheme that used fake IT workers to target 70 US companies and generate $3 million. The Justice Department (DoJ) announced coordinated enforcement actions this week targeting North Korea’s long-running scheme to place fake IT workers inside American companies. Two US nationals were arrested, 14 people charged across two separate indictments, and the FBI searched more than 40 residences in Texas, seizing approximately 187 laptops and KVM switc
     

North Korean IT Workers Used Stolen US Identities to Earn $3 Million

17 de Outubro de 2026, 13:29

The FBI raided 40 Texas homes over a North Korean scheme that used fake IT workers to target 70 US companies and generate $3 million.

The Justice Department (DoJ) announced coordinated enforcement actions this week targeting North Korea’s long-running scheme to place fake IT workers inside American companies. Two US nationals were arrested, 14 people charged across two separate indictments, and the FBI searched more than 40 residences in Texas, seizing approximately 187 laptops and KVM switch devices.

The Texas operation, called Operation Lonestar Roundup, ran between September 21 and 25. The seized devices are the same laptops American companies shipped to their newly hired remote employees, not knowing those IT workers were North Korean intelligence agents using stolen US identities.

“Today the Department of Justice announced coordinated actions against the Democratic People’s Republic of North Korea (DPRK) government’s schemes to fund its regime through remote information technology (IT) work for U.S. companies.” states DoJ. “These actions include an indictment, two arrests, searches of multiple known or suspected “laptop farms” in Texas pursuant to “Operation Lonestar Roundup,” and the seizure of approximately 187 computer devices used by DPRK IT workers.”

The scheme was simple. North Korean IT workers applied for remote jobs using stolen or fake identities. They used VPNs and proxy servers to make it look like they were working from the United States. American helpers received the laptops provided by employers and installed remote access software so the North Korean workers could use them. These helpers were paid for their role, while the money earned from the jobs was sent back to North Korea through accounts controlled by the regime.

According to an indictment from the Northern District of Ohio, the scheme ran from 2019 to mid-2025 and targeted more than 70 US companies across 17 states. The companies operated in sectors including healthcare, communications, cybersecurity support, retail, and manufacturing.

“In total, the scheme impacted more than 70 U.S. company employers and generated approximately $3 million in revenue for IT workers.” SoJ states.”The revenue is believed to have been sent to sanctioned entities controlled by the DPRK. Victim employers included companies in the health care, communications, cyber support, retail, and manufacturing sectors across Ohio, sixteen additional states, and the District of Columbia.”

The North Korean IT workers earned about $3 million, which prosecutors believe was sent to North Korean entities subject to international sanctions.

The authorities warn the scheme is evolving in response to better detection.

“Increasingly, North Korean IT workers are turning to recruiting American facilitators to counter improved private sector detections and law enforcement actions.” states DoJ. “These workers are hiring facilitators to complete a wider variety of tasks, and in some cases subcontracting entire jobs to third-party foreign nationals. “

That’s not just using Americans as props. It’s actively outsourcing parts of the operation to people inside the US, which makes attribution harder and interception more complicated.

Some IT workers are now subcontracting entire jobs to third-party foreign nationals. Others are hiring facilitators to handle a wider range of tasks beyond just managing the laptops. CrowdStrike, which helped the FBI investigate, tracks the group behind this operation as Famous Chollima and describes the laptop farm infrastructure as vital to overcoming the physical and legal barriers of operating from outside the US.

“These laptop farms enabled FAMOUS CHOLLIMA operatives to pose as legitimate remote workers and siphon illicit wages back to their regime while maintaining persistent access to victim organizations. Working alongside the FBI, CrowdStrike’s threat intelligence into the adversary and their operations, and technical analysis helped make these disruptions possible.” states CrowdStrike.

“This operation marks the beginning of a broader U.S. law enforcement effort to dismantle FAMOUS CHOLLIMA’s U.S. infrastructure. CrowdStrike’s Counter Adversary Operations team intends to remain an integral part of that effort.”

The FBI’s separate public service announcement puts the operation in broader context: “thousands of North Korean state-controlled IT workers” are currently embedded at Western companies, posing what the agency calls a significant national security and intellectual property theft insider threat. North Korean IT workers have individually earned up to $300,000 per year under these schemes, and the collective revenue is measured in hundreds of millions annually, flowing directly to designated entities including the North Korean Ministry of Defense.

This is the fifth round of enforcement actions announced since June 2025 under the DOJ’s DPRK RevGen Domestic Enabler Initiative (June 2025, November 2025, April 2026, and May 2026). The initiative targets people in the United States who help North Korean IT workers carry out these schemes.

According to CrowdStrike, North Korean hackers were responsible for about half of all documented hands-on cyber intrusions over the past year. The regime is also targeting cryptocurrency exchanges and open-source software projects. In 2025 alone, North Korean attackers stole at least $2 billion in cryptocurrency.

The DOJ released a list of email addresses used in these operations, including accounts like randyryang@gmail.com and dev.jerryyang@gmail.com, which companies can add to their screening indicators. The FBI’s public service announcement includes detailed mitigation guidance on spotting DPRK IT worker applications. The red flags are consistent: inconsistencies in work history, reluctance to appear on video, requests to redirect laptop deliveries, and payment accounts that route through intermediaries.

“Threats posed by nation-states like North Korea are a stark reminder that our adversaries will go to great measures to exploit our nation’s economic strength to further and fuel their own nefarious agendas,” said U.S. Attorney David M. Toepfer for the Northern District of Ohio. “We are thankful to FBI Cleveland for their incredible work and persistence to put a stop to these bad actors. These charges serve as an urgent alert to all U.S. companies to remain vigilant in their hiring practices.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, IT workers)

  • ✇Firewall Daily – The Cyber Express
  • Death Threats, Laptop Farms, Stolen IDs: Inside North Korea’s Job Scam Samiksha Jain
    North Korean IT workers are paying Americans to help them get and keep remote jobs at U.S. companies, the FBI said in an updated FBI public service announcement. At the same time, the Justice Department announced charges, two arrests, and the seizure of about 187 computer devices linked to the scheme. The FBI said these workers use stolen identities, extort victims, and threaten physical violence to demand payments. North Korea's government receives an estimated 85 to 90 percent of the revenu
     

Death Threats, Laptop Farms, Stolen IDs: Inside North Korea’s Job Scam

14 de Outubro de 2026, 04:49

North Korean IT workers

North Korean IT workers are paying Americans to help them get and keep remote jobs at U.S. companies, the FBI said in an updated FBI public service announcement. At the same time, the Justice Department announced charges, two arrests, and the seizure of about 187 computer devices linked to the scheme. The FBI said these workers use stolen identities, extort victims, and threaten physical violence to demand payments. North Korea's government receives an estimated 85 to 90 percent of the revenue they generate, money that helps fund its nuclear weapons and other military programs.

How North Korean IT Workers Use American Facilitators

According to the FBI, North Korean IT workers are hiring Americans for a growing list of tasks. These include appearing on camera, sitting for job interviews, verifying fake identities, lending social media or professional networking accounts, shipping packages, completing urinalysis tests or fingerprint submissions, and keeping work laptops online from their homes. [caption id="attachment_114769" align="aligncenter" width="600"]North Korean IT workers Image Source: FBI Cyber Division[/caption] The FBI said some workers deliberately target people under financial stress, looking for those more likely to follow instructions without questions if paid. Taking part in these activities is illegal. Home setups that host company laptops, known as laptop farms, have helped the workers hide their locations for years. The FBI said they now run more laptop farms with fewer laptops at each to avoid single points of failure. Some also land remote IT jobs and then subcontract the work to freelancers in Pakistan, India, Nigeria, or nearby countries for a fraction of the salary.

Extortion, Threats, and Identity Theft

Identity theft sits at the center of the scheme. Most names and addresses given to employers come from stolen identities, and workers often buy accounts from identity verification providers to check that stolen details will pass background checks. The FBI said that after being fired, some workers made death threats against former managers and their families to collect more money. Others threatened to leak sensitive corporate data unless paid large lump sums. Some hired U.S.-based facilitators to show up in person at victim companies to intimidate staff. The workers also target jobs requiring U.S. government security clearances, positions with cleared defense contractors, and active-duty U.S. military members to host laptops.

Justice Department Charges Linked to North Korean IT Workers

In Ohio, a four-count indictment charges a scheme that ran from 2019 to around July 2025. U.S. nationals Michael James Bostelle of Pennsylvania and Juan Cecilio Pena Carrillo of Texas were arrested. Ten China-based individuals were also charged, and two more defendants remain under seal. Prosecutors say the scheme affected more than 70 U.S. employers and generated about $3 million, believed to have gone to sanctioned DPRK-controlled entities. Victims included health care, communications, cyber support, retail, and manufacturing firms across Ohio, 16 other states, and the District of Columbia. Under Operation Lonestar Roundup, the FBI carried out searches and other actions at more than 40 Texas residences between Sept. 21 and Sept. 25. Agents seized about 187 laptops and KVM devices. Cybersecurity firm CrowdStrike tracks the group as "Famous Chollima. FBI Cyber Division Assistant Director Brett Leatherman said 14 individuals have been charged and called close coordination with the private sector central to the operation.

What Companies Should Know About North Korean IT Workers

The FBI said no single red flag reliably identifies North Korean IT workers. It recommends an "identity in depth" approach, using layered checks throughout employment. Warning signs include remote desktop tools such as AnyDesk and TeamViewer, KVM over IP devices like TinyPilot and PiKVM, unrelated software on work devices, and frequent changes in bank accounts or addresses. Using E-Verify, requiring a U.S. passport, and live identity checks can add friction, the FBI said, while relying only on name ban lists may block real applicants. Individuals who receive threats should call 911. Victims or anyone approached can contact a local FBI field office and file a complaint at www.ic3.gov. The State Department has offered rewards of up to $5 million for information that disrupts North Korea's illicit financial activities.
  • ✇Security Affairs
  • Contagious Interview: 30,000 devices infected by a fake job interview Pierluigi Paganini
    North Korea-linked WaterPlum runs the Contagious Interview campaign, infecting over 30,000 devices using a fake job interview. On September 18, Japan’s National Police Agency, the FBI, the US Department of Defense’s Cyber Crime Center, and intelligence agencies from Australia and Germany published a joint advisory about a group called WaterPlum, better known as Contagious Interview. The name says it all. The job interview is the infection vector. The numbers in the advisory are hard to sh
     

Contagious Interview: 30,000 devices infected by a fake job interview

22 de Setembro de 2026, 03:44

North Korea-linked WaterPlum runs the Contagious Interview campaign, infecting over 30,000 devices using a fake job interview.

On September 18, Japan’s National Police Agency, the FBI, the US Department of Defense’s Cyber Crime Center, and intelligence agencies from Australia and Germany published a joint advisory about a group called WaterPlum, better known as Contagious Interview. The name says it all. The job interview is the infection vector.

The numbers in the advisory are hard to shrug off. At least 30,000 devices infected across more than 100 countries, funds or credentials stolen from over 7,000 cryptocurrency wallets, and a total of 1.7 billion yen, roughly $10.71 million, funneled back to North Korea. The victims are almost always the same type: freelance developers and specialists in blockchain and Web3 work.

Japan’s NPA and the FBI assess that both WaterPlum operators and some North Korean IT workers report to the same place, the 313 General Bureau of the Munitions Industry Department, under the Workers’ Party’s Central Committee. That’s not a loose affiliation. It’s an org chart.

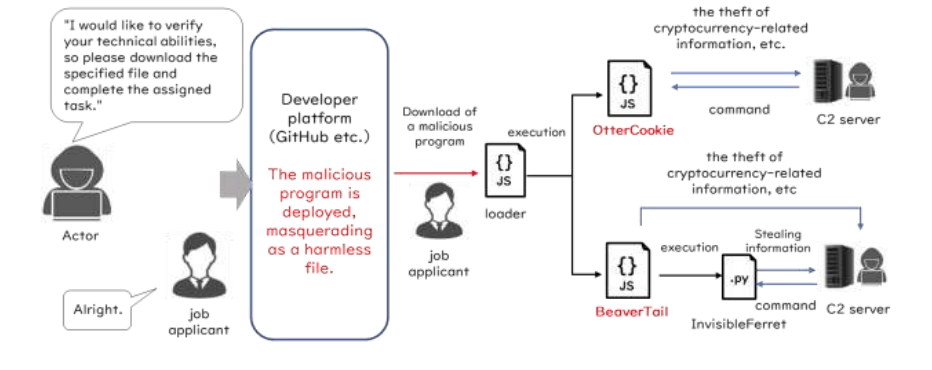
The trap itself is almost embarrassingly simple. WaterPlum actors pose as recruiters or hiring managers, often impersonating real AI, crypto, or NFT companies, and reach out on social media, job boards, and freelance platforms. Candidates get invited to a technical interview, then told to download a file to complete a coding test or fix a supposed bug on the video call.

“WaterPlum actors pose as prospective employers to target software developers and IT professionals worldwide under the pretext of attractive job opportunities. They often impersonate legitimate Artificial Intelligence (AI), cryptocurrency, or Non-Fungible Token (NFT) companies and have also used recruiting services.” reads the joint advisory. “WaterPlum actors have infected at least 30,000 devices in more than 100 countries and exfiltrated funds or account credentials from over 7,000 cryptocurrency wallets. WaterPlum actors have transferred 1.7 billion Japanese yen (JPY) (equivalent to 10.71 million USD) of cryptocurrency assets to the Democratic People’s Republic of Korea (DPRK).”

That file is never what it claims to be. The advisory names five malware families riding inside these downloads, BeaverTail, InvisibleFerret, OtterCookie, OtterCandy, and StoatWaffle, each doing its own piece of the job: one steals browser credentials, another opens a backdoor, another sets up a remote access trojan to move deeper into the machine. Once inside, the goal is straightforward: drain the wallet, then look for whatever else might be worth stealing.

What happens next goes beyond one stolen wallet. The report notes that a successful infection can give WaterPlum a way into the victim’s employer, opening the door to espionage, stolen source code, and further movement inside a company’s systems. Stolen ID photos get reused too, letting North Korean IT workers impersonate the victim to land more paying contracts elsewhere.

That last part connects to a separate but related scheme covered in the same advisory: North Korean IT workers using so-called “laptop farms.” These are physical locations, often just someone’s house, where a local facilitator plugs in company-issued laptops and lets a North Korean worker operate them remotely over VPN. The worker gets a Western-looking identity and a legitimate-sounding job. The facilitator gets a cut.

“Beyond immediate credential theft, successful infections provide WaterPlum actors opportunities to infiltrate organizations employing targeted developers, enabling espionage, intellectual property theft, and additional lateral movement in corporate environments. Stolen ID images can also be used by North Korean IT workers to impersonate victims and generate foreign currency.” continues the report. “Other sensitive data targeted for exfiltration includes:

  • Authentication data stored in web browsers (ID, password, etc.);
  • Clipboard information, key-logs (recorded keystrokes), screenshots;
  • Cryptocurrency-wallet data (private key, seed phrase, etc.); and
  • Any files or data of interest to the actors on a PC or in shared folders (ID pictures of driver’s licenses, passports, etc.)”

Here’s a simpler and more natural version, while keeping the same details:

Japan says this is no longer just a theoretical threat. Authorities have already shut down the country’s first known “laptop farm,” run by a local facilitator who had moved several hundred million yen in cryptocurrency out of Japan. In the US, the FBI says it continues to prosecute people who help North Korean IT workers operate this way, across several states and under different charges.

The advisory also describes a case involving a Japanese crypto exchange that spotted one of these applicants in May 2025. His resume listed an unusually wide range of skills across more than a dozen technologies. He claimed to be Malaysian, raised in Finland, and fluent in Malay and Chinese, but struggled with basic English questions that did not fit his claimed background. The company rejected him, avoiding any damage.

Other red flags recruiters have picked up on read like a checklist for a bad Zoom call: the applicant glancing sideways as if reading a script, background voices that shouldn’t be there, video that keeps freezing at convenient moments, a firm preference for getting paid in crypto, sometimes to someone else’s account entirely.

Not every North Korean IT worker sticks to quiet fraud, either. One extorted a client over a payment dispute and leaked the company’s proprietary code online out of spite. Another, hired for basic website maintenance, defaced the site and knocked it offline instead. Petty, but the effect on the client was anything but.

The advisory draws one more thread together: WaterPlum’s cyberattack operators and North Korea’s IT worker network aren’t running in parallel. They’ve been caught using the same IP addresses to access laptop farms, register on freelance platforms, and apply for that same crypto exchange job. Same infrastructure, two revenue streams, one regime cashing the checks.

“The techniques described in this advisory are only examples; actors continuously evolve and refine their methods.” concludes the advisory. “Stay informed by monitoring alerts from domestic and international security agencies and by reviewing reports published by security vendors.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – Contagious Interview, WaterPlum)

  • ✇Firewall Daily – The Cyber Express
  • WaterPlum Hackers Steal $10.7M in Crypto From IT Workers Samiksha Jain
    A North Korean cyber actor group known as WaterPlum, also referred to as "Contagious Interview," has infected at least 30,000 devices across more than 100 countries. The group has been stealing cryptocurrency from IT professionals worldwide. A joint advisory was issued on September 18, 2026, by Japan's National Police Agency and National Cybersecurity Office, the US FBI and Department of Defense Cyber Crime Center, Australia's Signals Directorate, and Germany's Federal Intelligence Service an
     

WaterPlum Hackers Steal $10.7M in Crypto From IT Workers

21 de Setembro de 2026, 03:52

WaterPlum

A North Korean cyber actor group known as WaterPlum, also referred to as "Contagious Interview," has infected at least 30,000 devices across more than 100 countries. The group has been stealing cryptocurrency from IT professionals worldwide. A joint advisory was issued on September 18, 2026, by Japan's National Police Agency and National Cybersecurity Office, the US FBI and Department of Defense Cyber Crime Center, Australia's Signals Directorate, and Germany's Federal Intelligence Service and Federal Office for the Protection of the Constitution.

How WaterPlum Hackers Operate

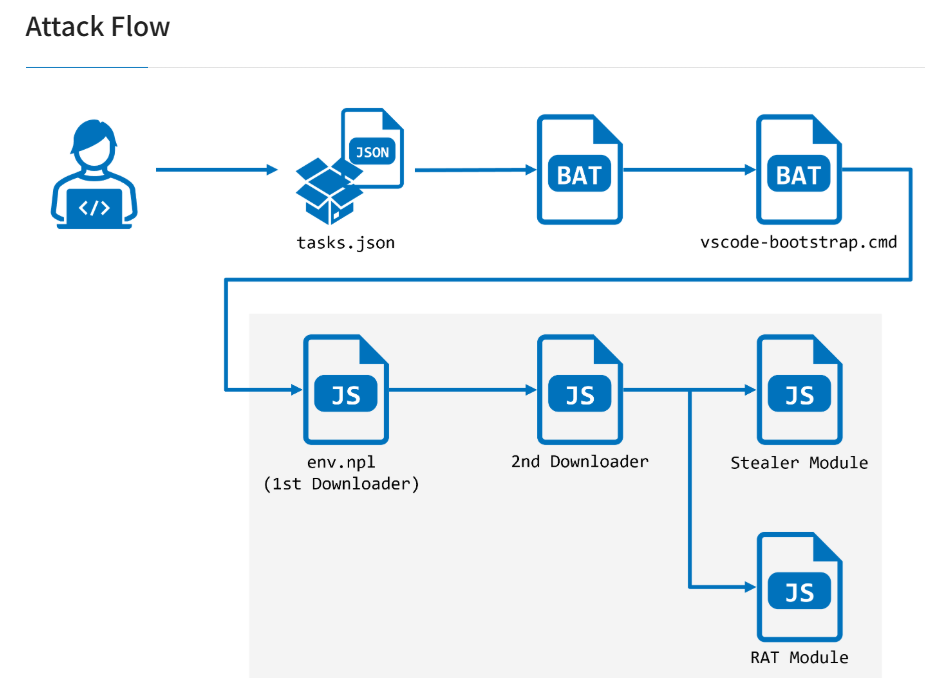
The agencies assess that WaterPlum actors and certain North Korean IT workers operate under the 313 General Bureau of the Munitions Industry Department, part of the Workers' Party of Korea's Central Committee. The group poses as prospective employers, targeting software developers and IT professionals by impersonating artificial intelligence, cryptocurrency, or non-fungible token companies, and by using recruiting services. During fake technical interviews, victims are instructed to download files to complete coding assignments or fix errors on video calls. These files carry malicious Node Package Manager packages embedded with BeaverTail malware, InvisibleFerret, OtterCookie, OtterCandy, or StoatWaffle. Once installed, the malware grants backdoor access, allowing Remote Access Trojans to maintain persistence while infostealers exfiltrate wallet credentials, browser passwords, clipboard data, keystrokes, and identification documents to command-and-control servers.

Scale of the Cryptocurrency Theft

Between December 2025 and July 2026, WaterPlum exfiltrated funds or credentials from over 7,000 cryptocurrency wallets, transferring 1.7 billion Japanese yen, equivalent to 10.71 million USD, to North Korea. Primary targets included web designers, engineers, and specialists in blockchain and Web3 technologies.

Role of Laptop Farms

The advisory also details how North Korean IT workers generate foreign currency through "laptop farms," locations, often an enabler's residence, where employment computers are remotely controlled by workers based in North Korea, China, Russia, and occasionally Africa or Southeast Asia. Enablers supply identification images, bank accounts, and internet connections, then forward payments to the workers after taking a cut. Japanese authorities dismantled a laptop farm for the first time domestically, uncovering evidence of several hundred million yen transferred abroad in cryptocurrency. A related case involved a suspected North Korean applicant at a Japanese cryptocurrency exchange in May 2025, who submitted a forged resume, accessed the recruitment portal via VPN, and displayed mismatched language skills during a video interview. The company declined to hire the applicant, and no damage occurred.

Warning Signs and Recommended Countermeasures

The agencies list red flags including refusal of in-person meetings, requests for cryptocurrency payment, background voices during calls, and repeated video freezes. Recommended defenses include avoiding execution of untrusted code outside a sandbox, treating VSCode projects with caution using "Restricted Mode," deploying Endpoint Detection and Response tools, and immediately disconnecting compromised devices from the internet. Victims are advised to assume wallet data has been exposed, create new wallets on separate devices, and perform full operating system resets.

International Cooperation Continues

The FBI stated it continues to prosecute US-based facilitators who assist North Korean IT workers, while Japanese and American authorities pledged ongoing cooperation to expose revenue-generation schemes benefiting the Kim regime. The advisory noted that WaterPlum and North Korean IT worker operations shared overlapping IP addresses across laptop farms, crowdsourcing platforms, and job applications, indicating coordinated infrastructure. Companies and individual IT professionals are urged to review the tactics outlined in the advisory and strengthen hiring verification processes to prevent further infiltration.
❌
❌