 Entrar

CISA Warns Hackers Are Exploiting 18-Year-Old WordPress Core Vulnerability
6 de Novembro de 2026, 08:24
CVE-2026-119977 lets hackers hijack WordPress sites during core updates. CISA confirms exploitation as users are told to patch…


Upgrade to Composer 2.11.0 or 2.2.31 to fix two Composer vulnerabilities: path traversal GHSA-c968-33g3-wh7p and token leak GHSA-fm2w-xgf2-f9fh.
Related Posts:
The post Composer 2.11.0 and 2.2.31 Patch Path Traversal and Token Leak Vulnerabilities appeared first on Daily CyberSecurity.

Update — October 30, 2026: Thank you to everyone who has participated in the PHP Capture the Flag challenge. We have received a strong response from the security research community, and the submissions have helped us harden our existing php2shell WAF protections and create new detections.
Details of managed-rule changes are available in the Cloudflare WAF changelog.
The CTF remains open. We encourage researchers to continue submitting materially distinct, reproducible bypasses through the Cloudflare HackerOne program. We will share further information and feedback as the challenge progresses. Thank you again for your contributions.
Last week was one for the Internet security history books. First, eight eMudhra intermediate certificates were compromised, creating the possibility of forged certificates that could be used to impersonate servers. Then came php2shell: serious vulnerabilities in PHP, the runtime behind a large portion of the Web.
Cloudflare worked around the clock as these events unfolded to protect our customers and help protect the Internet. We shipped client updates and multiple mitigations, updated our web application firewall (WAF) with new rules to block attackers from exploiting the PHP vulnerabilities, and introduced a new feature called full transaction detection.
As always in situations like this, these new capabilities were made available on all plans, including Free.
Protecting systems from vulnerabilities like these is always an ongoing process, not a one-time event. The widespread adoption of AI allows attackers to discover new vectors with unprecedented speed and efficiency, so collecting real-world data to test our assumptions and strengthen defenses is essential.
That’s why today we're launching the Cloudflare PHP Capture the Flag challenge, run through our Bug Bounty program. We've put a deliberately vulnerable PHP installation behind our WAF, and we're inviting security researchers on HackerOne to try to bypass the protections and capture a flag.
We are keeping this simple. The challenge focuses on CVE-2026-109618 and CVE-2026-109619, the two PHP vulnerabilities behind php2shell. The target runs stock PHP 8.5.11 (with standard PHP extensions), Apache 2 (via mod_php), and an empty index.php inside a Cloudflare Container, with our default WAF protection rules for these vulnerabilities enabled in front of it. Inside the sandbox is a file called /flag.
The sandbox is reset every few minutes, including the flag file.
Your mission, should you choose to accept it: bypass the WAF protections, exploit the PHP sandbox, and recover the contents of /flag. You can use your own research tools. The challenge page has the environment details, scope, and flag verification form.
This limited-time challenge is run via Cloudflare's Bug Bounty program on HackerOne. All aspects of this challenge are subject to HackerOne terms and the Cloudflare HackerOne program rules the (“Bounty Terms”). If you find an eligible bypass, you must follow these requirements in order to claim the bounty:
UI verification does not submit a HackerOne report or establish reporting priority. File disclosure without RCE, RCE without successful flag recovery and UI verification, local-only exploits, rediscovery of the known PHP vulnerabilities, and WAF detection differences or partial chains without the full objective are not eligible.
Awards require a materially distinct Firewall (WAF) bypass method, even for the same PHP CVE. Reports using the same Firewall-bypass mechanism are duplicates, regardless of differences in the PHP exploit, payload, RCE technique, or flag-recovery method. New flags, resets, attempt IDs, or cosmetic changes—including equivalent encodings—do not qualify as unique. Equivalent submissions are duplicates even if unfixed; only the first complete, reproducible HackerOne report is considered. Cloudflare makes final duplicate and reward decisions.
We record attempted metadata and request payloads to help analyze reports, so please use test data only. Do not send credentials, personal information, or anything else you would not want included in a research record. Read Cloudflare’s privacy notice before testing.
Testing is authorized only against the challenge hostname's WAF-protected /php/* endpoints (POST method only). Other Cloudflare services, direct access to the underlying infrastructure, the upstream PHP project, and third-party systems are out of scope. No denial of service, high-volume scanning, persistence, social engineering, or attacks on other participants. If you get a 429 or 503, back off.
In the event of any conflict between this blog post and the Bounty Terms, the Bounty Terms shall prevail.
Cloudflare reserves the right to suspend or terminate this challenge at any time. Once the competition is removed from HackerOne, it is officially terminated, so please refer to the Cloudflare HackerOne page for the most up-to-date information on whether this challenge remains open.
Our WAF protects you, but it is not a replacement for fixing vulnerable software. Response blocking can prevent exposed data from reaching an attacker, but it cannot undo actions already performed at the origin. If you run PHP, follow the latest PHP security advisories and apply the relevant updates.
Last week was a reminder that helping build a better Internet often takes many people—researchers, maintainers, and teams across the industry—doing difficult, urgent work together.
We hope this challenge gives everyone a useful way to join in. Head over to php-rce.cloudflare.app if you want to participate: the flag is there, and we'd like to know if you can get it.

CISA adds PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619 to the CISA KEV catalog after confirmed RCE and suspected DPRK-linked scanning.
Related Posts:
The post CISA Adds PHP2Shell to KEV as Confirmed RCE Attacks and Suspected DPRK Scanning Surface appeared first on Daily CyberSecurity.
OpenMage fixes 34 OpenMage vulnerabilities in Magento LTS, including a critical CSRF flaw that hands out API tokens. Upgrade to 20.19.0 or 20.18.2.
Related Posts:
The post OpenMage Fixes 34 Flaws in Magento LTS, Including Critical OAuth CSRF appeared first on Daily CyberSecurity.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the PHP PHP2Shell vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog:
On October 21, PHP released emergency patches for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619 (CVSS score of 9.2). The flaws affect all PHP versions that handle web requests.
The vulnerable code dates back to PHP 5.4, released in 2012, and resides in the PHP engine itself rather than in individual applications. Attackers can exploit the flaws to execute code remotely by sending specially crafted HTTP requests, without authentication.
Exploitation attempts increased rapidly after the vulnerabilities became public. Cloudflare researchers reported tens of thousands of attempts within the first 45 minutes, hundreds of thousands in just two hours, and millions by October 22.
Cyfirma reported that a group of North Korea-linked group has identified 216 hosts that may still be vulnerable to PHP2Shell. The operators communicate through a private I2P channel that Cyfirma has monitored since October 22. On October 24, they reported that 216 hosts appeared to be unpatched or only partly protected, earlier than Cyfirma expected.
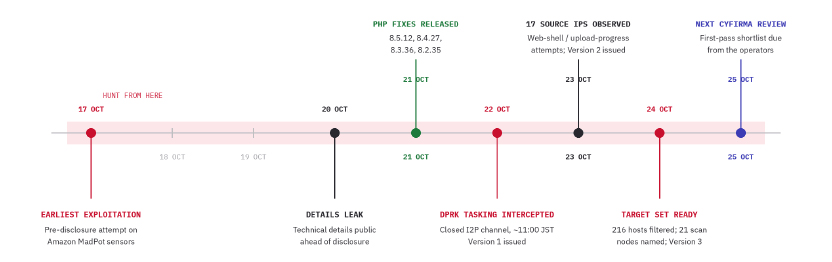
They are checking the systems from 21 compromised machines. At the time Cyfirma captured the conversation, the operators had already checked about one-third of the targets.
“Two handles active since March 2026, coordinating in a closed I2P channel; staging infrastructure shared in-channel.” states the cybersecurity firm. “Target set and scan nodes. “On 24 October the operators reported 216 unpatched or partially mitigated hosts and named 21 scan nodes; the same addresses were seen performing web-shell tooling and upload-progress session-poisoning attempts.”
The scanning is slow on purpose. Volume stays low, the machines rotate, and any node that shows filtering or rate limiting gets pulled and never reused. That’s why a rate-based alert will probably stay quiet.
According to Binding Operational Directive (BOD) 22-01: Reducing the Significant Risk of Known Exploited Vulnerabilities, FCEB agencies have to address the identified vulnerabilities by the due date to protect their networks against attacks exploiting the flaws in the catalog.
Experts also recommend that private organizations review the Catalog and address the vulnerabilities in their infrastructure.
CISA orders federal agencies to fix the flaws by October 29, 2026.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, CISA)

You recognize the website. You’ve visited it before. You may even have it bookmarked. Then it asks you to do something unusual: install an update, allow notifications, or run a command to prove you’re human.
Stop and check first. A website you trust can still display instructions you shouldn’t follow. Our researchers have documented attacks in which criminals hacked legitimate websites and used them to deliver fake verification pages that trick visitors into installing malware.
Within the same week, serious problems emerged in several parts of the web’s security infrastructure. Attackers were exploiting two flaws in PHP, researchers disclosed a critical flaw in Brotli software used by Node.js, and eight compromised security certificates raised concerns about how browsers and apps verify websites. The incidents have different causes and levels of risk, but their timing makes this an unusual cluster.
PHP is used by about 7 in 10 websites whose underlying programming language is known. Node.js is used by 7.4% of websites with an identified web-server technology, according to W3Techs. Both run websites behind the scenes, so flaws in them can put the sites that rely on them at risk. Most browsers have blocked the certificates, though updates may still be needed for other software and devices.
These problems don’t mean you need to stop browsing. But keep your software and security protection up to date, and be wary of unexpected requests.
Check the website’s address, but remember that even the genuine site may have been compromised. The important question is whether the page’s instructions make sense. A familiar website may earn your visit, but that doesn’t mean you should automatically let it run software on your device.
In documented campaigns, malicious instructions appeared on legitimate, hacked WordPress websites, not just lookalike domains.
A secure connection doesn’t guarantee that a page is safe, either. HTTPS protects the connection between your browser and the site. Browser protections against dangerous content are a separate layer. A page asking you to install software or enter sensitive information still deserves scrutiny, even when the connection is encrypted.
Ask yourself: “Does this request make sense for what I came here to do?”
Reading an article shouldn’t require opening PowerShell. Watching a video shouldn’t require following a website’s instructions to “repair” your computer. These are familiar themes in ClickFix attacks, which disguise malicious commands as routine verification or troubleshooting steps.
You can’t patch someone else’s web server, but you can keep the software on your own device updated. Turn on automatic updates for your operating system, browser, and applications where available, and don’t repeatedly postpone installing them. Updates fix security flaws that criminals could otherwise use to access your files or accounts.
Keep your browser’s phishing and malware protection enabled, too. Free browser extensions like Malwarebytes Browser Guard warn about known dangerous websites, malicious downloads, and clipboard hijacking. Treat those warnings as a reason to leave, not as another obstacle to get round. These checks are a useful layer of protection, but they can’t certify that every unflagged page is safe.
Use strong, unique passwords stored in a password manager, and enable multifactor authentication on important accounts. These measures help protect your accounts from unauthorized access.
If a request involves running code or making changes to your device, verify it independently. If a website claims your browser needs updating, close the prompt and check through the browser’s own settings. If it says an account or service needs attention, check through the official app, help page, or support channel that you open yourself.
Criminals often present the harmful step as the thing that will let you do what you came to do: fix the connection, enable the player, or complete the security check. The frustration of being blocked can make it tempting to follow their instructions.
Use up-to-date, real-time anti-malware protection on your devices to help stop malware from wreaking havoc or stealing your information.
Watch for unexpected content, downloads, redirects, and repeated login requests, even on familiar sites. If something looks wrong, leave the page. If you’re unsure, use Malwarebytes Scam Guard to check whether a request may be a scam and get possible next steps.
From reporting threats to removing them.
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
On October 21, PHP released emergency patches for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on the CVSS scale. The flaws affect all PHP versions that handle web requests. The vulnerable code dates back to PHP 5.4, released in 2012, and resides in the PHP engine itself rather than in individual applications. Attackers can exploit the flaws to execute code remotely by sending specially crafted HTTP requests, without authentication.
Exploitation attempts increased rapidly after the vulnerabilities became public. Cloudflare researchers reported tens of thousands of attempts within the first 45 minutes, hundreds of thousands in just two hours, and millions by October 22.
Cyfirma reported that a group of North Korea-linked group has identified 216 hosts that may still be vulnerable to PHP2Shell. The operators communicate through a private I2P channel that Cyfirma has monitored since October 22. On October 24, they reported that 216 hosts appeared to be unpatched or only partly protected, earlier than Cyfirma expected.
They are checking the systems from 21 compromised machines. At the time Cyfirma captured the conversation, the operators had already checked about one-third of the targets.
“Two handles active since March 2026, coordinating in a closed I2P channel; staging infrastructure shared in-channel.” states the cybersecurity firm. “Target set and scan nodes. “On 24 October the operators reported 216 unpatched or partially mitigated hosts and named 21 scan nodes; the same addresses were seen performing web-shell tooling and upload-progress session-poisoning attempts.”
The scanning is slow on purpose. Volume stays low, the machines rotate, and any node that shows filtering or rate limiting gets pulled and never reused. That’s why a rate-based alert will probably stay quiet.
Who’s behind it? Cyfirma assesses with moderate confidence a link to the Lazarus family of North Korean groups, based on language, operating style and old habits with PHP web shells and hijacked web servers. It has no shared malware or infrastructure to point to yet, and it admits that a Korean-speaking criminal crew without state backing would fit the same facts. Its confidence in the campaign itself is high.
Government agencies and banks come first. Next in line are logistics, ports, airports and aviation, manufacturing, and online transaction and trading platforms. The countries named are the US, Japan, South Korea, Thailand, Indonesia, Australia, Taiwan, India, Singapore, the UAE, Saudi Arabia and the EU.
Cyfirma has not named any victims or seen the full list of targeted systems. The operators have not announced when they plan to launch attacks, and the researchers have not confirmed that this group has compromised systems on a large scale. Cyfirma gives the campaign an imminence score of 78 out of 100. The operators plan to check all 216 hosts, select the most promising targets, and decide which publicly available exploits to adapt.
The group does not appear to be developing new exploits. Instead, its members use a local AI model to rank public exploit repositories, then test the results manually in a lab. Cyfirma believes this approach could help attackers turn newly disclosed vulnerabilities into working attacks more quickly. However, researchers warn that some proof-of-concept exploits shared online are fake and may contain malware, so downloading and running them can be dangerous.
Technical details leaked on October 20, ahead of coordinated disclosure, and the PHP project shipped fixes on October 21. Apache mod_php with default settings and prefork is the confirmed worst case for 109618, with full unauthenticated code execution. For 109619, PHP-FPM is validated through the upload-progress path.
One correction matters for your temporary controls. Early coverage tied the session upload-progress field to 109618, but PHP’s advisories put it under 109619 only. Disabling upload progress does nothing for 109618, so the two bugs need different stopgaps.
Triggering the bug is easy, but reliable code execution isn’t. The attacker has to land a follow-up request on the same worker and shape heap data into the freed space, otherwise the worker crashes or answers normally. VulnCheck reports working code execution on x86-64 with ASLR enabled against PHP 8.4.10 to 8.4.26, while ARM64 only leaks memory so far.
Short of code execution, attackers have already shown worker crashes, arbitrary file reads through OPcache and a leak of about 67 KB of process memory. The fixed releases are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. PHP 8.1, 8.0 and 7.4 get only minimal backports, and vendors such as cPanel EasyApache, CloudLinux, TuxCare and Plesk carry their own builds, so confirm coverage with yours.
Anything from PHP 5.4 to 7.3 has no fix, so migrate or isolate it. Restart every worker after patching, because a reload that keeps old workers alive leaves the stale state in place. Isolate anything internet-facing that you can’t patch within hours, starting with Apache mod_php.
If you suspect a host is compromised, capture memory and logs before you patch, since a restart destroys the CVE-2026-109619 state. Then rebuild the host from a trusted image and rotate every secret the PHP worker could reach. Hunt back to October 17, the earliest known exploitation, and use long time windows.
The strongest single signal is a PHP or web server process spawning something it never normally spawns. Application logs will usually show nothing, because the bug fires before application code runs. Look for odd multipart POSTs to endpoints that never take uploads, bursts of worker crashes and memory errors, new PHP files in web roots, and new cron jobs, local users or SSH keys.
Cyfirma includes Sigma, Splunk and YARA content, though it says the YARA set hasn’t been tested on real application code yet. It also lists 21 scan-node addresses, 17 source addresses from October 23 and 15 staging addresses, all defanged. Some scan nodes are described as compromised and may belong to victims, so hunt for prior contact before assuming who owns them.
If you can’t patch yet, the advisory suggests limits such as a low post_max_size and disabling session upload progress for 109619. Cyfirma is clear that none of it replaces patching. The operators’ own selection rule is the most useful detail in the whole advisory, because they dropped every host that showed a fixed version or sat behind heavy filtering. That makes a current version string a cheap filter against you, and for once being boring pays off.
“Hosts still bannering older PHP are the ones the operators kept.” Cyfirma states.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, PHP2Shell)
1. Your latest report reveals that hackers began exploiting the PHP2Shell vulnerability four days before it was publicly disclosed. First, can you explain what PHP is, how widely it is used across the internet, and why this particular security flaw is so serious?
PHP is a programming language widely used to build websites and web applications. It powers a significant share of the web. PHP2Shell is serious because it can allow attackers to execute commands on a vulnerable server remotely. Depending on the configuration and the server’s privileges, this could give threat actors access to sensitive data, applications and other systems.
2. According to AWS researchers, attacks were already underway before the vulnerability became public. How did researchers uncover this early exploitation, and what does it tell us about the ability of hackers to identify security weaknesses before developers can fix them?
AWS researchers detected exploitation attempts against their honeypot network four days before public disclosure and the release of patches. This shows that attackers can discover or weaponize vulnerabilities before defenders have time to respond. AI-assisted analysis may accelerate this process, helping attackers turn technical information into working exploits in hours rather than days. However, detected attempts do not automatically mean successful compromises.
3. The vulnerability could potentially allow attackers to execute malicious commands on affected servers. What does that mean in practical terms, and what risks does it pose to websites, businesses and the personal information of their users?
Remote command execution means an attacker may be able to make a server run commands without authorization. Depending on the attacker’s access, they could steal data, install malware, change website content, or use the compromised server to attack other systems. Businesses could face service disruption, financial losses and reputational damage. Users may also be exposed if their personal information is stored on an affected system. The actual impact depends on the server’s configuration and security controls.
4. The latest findings raise concerns about the gap between discovering a vulnerability and protecting systems against it. How quickly can attackers exploit these weaknesses, and are businesses adequately prepared to respond when critical security flaws emerge?
The window can be extremely short. In some cases, attackers can develop or adapt an exploit within hours, leaving organizations little time to react. Many businesses still rely on patching schedules that are too slow for internet-facing systems. Organizations need continuous monitoring, rapid patching, tested incident response plans and clear visibility into exposed assets. They should also investigate suspicious activity dating back to before a vulnerability was publicly disclosed, because attacks may already be underway.
5. With PHP powering a significant portion of the internet, could we see further attacks exploiting this vulnerability? What should website operators do immediately to protect their systems, and should ordinary internet users be concerned about their data?
Further attacks are possible, particularly against systems that remain unpatched or exposed. Website operators should apply the relevant security updates, check whether their PHP applications are vulnerable, and review logs for suspicious activity dating back to October 17. They should also restrict access and investigate signs of compromise. Ordinary users do not need to panic, but they should keep their accounts protected with unique passwords and multi-factor authentication where available. Whether personal data is at risk depends on which services they use and whether those systems were compromised.
AI-assisted tools are increasingly being used to analyze code and identify vulnerabilities. How much of a role could artificial intelligence play in helping attackers discover and exploit flaws like PHP2Shell, and can defenders use the same technology to their advantage?
AI can help analyze code, identify suspicious patterns and speed up the process of turning a vulnerability into a working exploit. This lowers some of the technical barriers for attackers and may shorten the time between discovering a flaw and exploiting it. However, AI is not the only factor, and we should not assume that every attack is AI-driven. Defenders can use the same capabilities to review code, prioritize vulnerabilities, analyze logs and detect suspicious behavior. The real advantage comes from combining AI with reliable data, skilled security teams and effective response processes.
This case shows that attackers may exploit a vulnerability before a patch is available. Does this mean traditional vulnerability management is no longer enough, and how should organizations rethink their security strategy?
Traditional vulnerability management remains essential, but patching alone is not enough when attackers may act before a fix becomes available. Organizations need to know which internet-facing systems they operate, understand their exposure and have additional controls in place. These include limiting access to vulnerable services, monitoring suspicious activity, applying temporary mitigations and preparing incident response procedures. They should also investigate whether systems were targeted before the vulnerability was disclosed. The goal is to reduce the opportunity for exploitation and detect attacks quickly, even when a patch is not yet available.
Below is another interview I gave to TRT World discussing critical PHP vulnerabilities, the risks they pose to web servers, and the growing number of exploitation attempts. I explain why rapid patching and effective security measures are essential to minimize potential damage.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, newsletter)
PHP has warned of a new code execution vulnerability, tracked as CVE-2026-115560, just two days after releasing emergency patches for the critical PHP2Shell flaws.
The vulnerability affects only a specific PHP configuration that PHP says is unlikely to be used in practice. An application must meet several conditions: it must configure session.serialize_handler as php_binary or php_serialize, change it to php at runtime using ini_set(), and make this change before calling session_start(). Session upload progress must also remain enabled.
In an advisory published on October 23, the project recommended disabling session upload progress until a fix becomes available in a regular release. The vulnerability is separate from PHP2Shell and is not fixed by the October 21 updates for PHP versions 8.2.35, 8.3.36, 8.4.27 and 8.5.12.
“The issue can only occur under an unusual combination of configuration and application code. An application must set session.serialize_handler to php_binary or php_serialize in its configuration and then switch it to php at runtime with ini_set() before calling session_start(). Session upload progress must also still be enabled.” reads the advisory. “Applications that never change the serialize handler at runtime can keep the feature enabled. Since this setup is unlikely in practice, we are handling it in the regular release cycle and will publish a full advisory for CVE-2026-115560 with the next release.”
Applications that do not change the serialization handler while running are not exposed through this attack path, even if session upload progress is enabled.
PHP recommends a simple temporary fix: set session.upload_progress.enabled=0 until the next routine bugfix release. This is the same mitigation already recommended in the October 21 advisory for CVE-2026-109619. Administrators who applied this setting and have kept it in place do not need to take further action for this issue.
Session upload progress is enabled by default and allows applications to track the progress of file uploads. Disabling it reduces exposure to this specific vulnerability path.
PHP will fix CVE-2026-115560 through its regular release cycle because the vulnerable setup is uncommon. It plans to publish a full advisory with the next release. PHP has not yet identified affected versions, confirmed when the fix will arrive, assigned a severity score, or explained whether the flaw shares a root cause with CVE-2026-109619. No attacks targeting this new issue have been reported.
On October 21, PHP released emergency patches for two critical vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS score of 9.2), affecting every PHP version that handles web requests. The bug code dates back to PHP 5.4 from 2012, lives in the PHP engine itself rather than in any application, and allows unauthenticated remote code execution via crafted HTTP requests.
Cloudflare researchers observed tens of thousands of exploit attempts within 45 minutes of public disclosure, hundreds of thousands within two hours, and millions by October 22.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, PHP)
Em 21 de outubro, duas vulnerabilidades críticas foram divulgadas no PHP, a linguagem de script usada por muitos sites e serviços online: CVE-2026-109618 e CVE-2026-109619. Os invasores podem explorá-las para executar comandos remotamente em qualquer servidor que execute PHP, sem necessidade de autenticação. O exploit foi batizado de PHP2Shell.
A equipe de segurança do PHP anunciou uma atualização emergencial em 20 de outubro e lançou os patches que corrigem as vulnerabilidades já no dia seguinte.
Anteriormente, abordamos os detalhes técnicos dessas vulnerabilidades e explicamos o que empresas e administradores de servidores devem fazer. Talvez você tenha ignorado tranquilamente essa notícia por não administrar nenhum servidor — mas, infelizmente, o problema não se limita às empresas.
Quase 70% dos sites usam PHP, incluindo serviços que utilizamos todos os dias: wikis, lojas online, dispositivos inteligentes com interfaces web, sistemas domésticos de armazenamento conectado à rede (NAS), controladores de casa inteligente e muito mais.
Hoje, explicamos como essas vulnerabilidades podem afetar você pessoalmente e o que fazer para reduzir os riscos.
A vulnerabilidade permite que um invasor roube tokens de autenticação da memória do servidor. Esses tokens funcionam basicamente como passes eletrônicos, informando ao site que o usuário já fez login. Como resultado, um invasor pode conseguir acessar a conta de outra pessoa sem inserir uma senha nem um código de autenticação de dois fatores, colocando em risco mensagens, documentos, endereços de entrega, históricos de pedidos e outras informações confidenciais.
Se você tem em casa um sistema de armazenamento conectado à rede (NAS) ou um sistema de videovigilância que usa uma versão vulnerável do PHP, ele também pode estar em risco. Dependendo do nível de acesso obtido, os invasores podem conseguir copiar, excluir ou criptografar os arquivos aos quais tiverem acesso.
Se um invasor obtiver acesso a um site vulnerável, poderá usá-lo praticamente da maneira que quiser: enganar visitantes para que baixem um arquivo malicioso ou cliquem em um link de phishing, exibir instruções perigosas, substituir formulários de pagamento ou páginas de login por versões maliciosas — e a lista continua. Como resultado, alguém que visite um site legítimo pode não apenas perder o acesso à própria conta, mas também perder dinheiro ou infectar acidentalmente o dispositivo com malware.
A seguir, apresentamos exemplos de serviços diretamente afetados pelas vulnerabilidades.
Jeedom é uma plataforma de casa inteligente que permite controlar iluminação, sensores, aquecimento, persianas e dispositivos IoT domésticos. Os invasores podem explorar isso de várias maneiras: desativar o alarme, acompanhar quando o morador está fora de casa, acessar as imagens do vídeo porteiro e muito mais.
Os desenvolvedores confirmaram que a nova vulnerabilidade afeta o aplicativo e já lançaram uma atualização emergencial, o Jeedom 4.6.2. Os usuários precisam executar a atualização duas vezes para que ela funcione. Segundo os desenvolvedores, uma versão totalmente corrigida para usuários domésticos será lançada nos próximos dias.
Como mencionado acima, o PHP é usado por aproximadamente 70% dos sites. Isso não significa que todos eles sejam vulneráveis: tudo depende da versão do PHP em uso e de os responsáveis pelo site já terem feito a atualização. Muitos sites governamentais na Europa já suspenderam suas operações por causa da nova vulnerabilidade.
Infelizmente, um site pode continuar vulnerável mesmo que pareça estar funcionando normalmente. Um invasor pode conseguir assumir o controle de qualquer site legítimo cujo servidor ainda não tenha recebido o patch. Ele pode falsificar páginas de pagamento ou login, hospedar arquivos maliciosos ou convencer usuários a baixar uma “atualização urgente” que, na verdade, é malware.
Usuários comuns não têm uma maneira confiável de verificar se essas instruções ou arquivos são seguros. Por isso, use uma proteção confiável contra phishing e malware. Se você suspeitar que seus dados podem ter sido roubados, verifique as sessões ativas nas configurações da sua conta. Caso encontre alguma atividade suspeita ou dispositivos que não reconheça, encerre todas as sessões ativas e altere sua senha. Use um gerenciador de senhas — ele pode gerar uma senha realmente forte e exclusiva, que você não precisará memorizar.
Más notícias para os gamers: alguns videogames cujos servidores usam PHP também estão em risco. Se você não quer que invasores assumam o controle de suas contas, altere as senhas das suas plataformas, lojas e contas de jogos.
Para ganhar tempo para realizar as atualizações, alguns desenvolvedores tiraram seus serviços do ar temporariamente. Final Fantasy XIV, Pokemon Champions, jogos da Bandai Namco Entertainment, Uma Musume: Pretty Derby, Granblue Fantasy, Shadowverse: Worlds Beyond e muitos outros entraram em manutenção emergencial. O Nintendo Switch Online e as lojas GOG e Steam também foram afetados.
Infelizmente, também houve consequências mais drásticas. Ontem, os desenvolvedores de World Quest anunciaram que o jogo seria encerrado definitivamente após 15 anos: ele dependia de uma infraestrutura desatualizada cuja correção seria extremamente difícil e cara. Pelo mesmo motivo, o jogo para dispositivos móveis Please Save My Pandemonium! foi encerrado depois de mais de dez anos em operação.
As “nuvens domésticas” se tornaram populares nos últimos anos, e por um bom motivo: muitos usuários preferem manter backups dos próprios dados em casa em vez de armazená-los online. Diversas empresas fabricam dispositivos NAS, e pelo menos três — QNAP, Synology e ASUSTOR — informaram que as vulnerabilidades afetam seus produtos. Também foi lançada uma atualização para o Unraid, um sistema operacional para servidores domésticos, armazenamento em rede e servidores de mídia.
O fabricante confirmou que as vulnerabilidades afetam várias versões de seus sistemas operacionais para NAS — QTS e QuTS hero —, além de aplicativos como QuMagie, Note Station 3 e determinadas versões do QVR Surveillance. Um ataque bem-sucedido pode colocar em risco fotos, documentos, anotações e gravações de câmeras.
No momento da publicação, a QNAP ainda está preparando atualizações. Portanto, a principal prioridade é desconectar temporariamente o NAS da internet. A QNAP recomenda desativar o redirecionamento de portas no roteador, impedir que o NAS abra portas automaticamente e permitir o acesso ao painel de gerenciamento somente pela rede doméstica ou por meio de uma VPN.
As duas vulnerabilidades foram oficialmente confirmadas nos pacotes PHP 7.3, 7.4 e 8.0–8.4, assim como no Mail Station e no Synology Calendar. Correções já foram lançadas para o PHP a partir da versão 7.4, além do Mail Station e do Synology Calendar. O PHP 7.3 não receberá correção. A empresa também ressalta que o componente PHP integrado ao sistema operacional não pode ser acessado de fora do dispositivo, portanto o risco de ataque é muito baixo.
A ASUSTOR também confirmou oficialmente as duas vulnerabilidades e removeu imediatamente do App Central os pacotes PHP 7, 7.3, 7.4 e 8.1. A empresa recomenda fazer imediatamente um backup dos dados, remover os pacotes antigos do PHP e usar o PHP 8.3 ou 8.4.
Na atualização do sistema operacional lançada hoje, o PHP foi atualizado para a versão 8.4.27, que inclui correções para as vulnerabilidades. Os desenvolvedores recomendam que todos os usuários atualizem para o Unraid 7.3.4. Contêineres que possuem a própria instalação do PHP precisam ser atualizados separadamente: a nova versão do PHP no sistema operacional não substitui a versão instalada dentro dos contêineres.
No momento da publicação, não encontramos confirmação pública de outros grandes fabricantes, como TerraMaster, UGREEN, Buffalo ou Western Digital, de que seus dispositivos sejam afetados por essas vulnerabilidades — apenas discussões de usuários em fóruns.
Mas o fato de apenas alguns fabricantes de NAS terem confirmado o problema até agora não garante que seus dispositivos estejam seguros — principalmente se forem relativamente antigos ou fabricados por uma empresa pouco conhecida ou que já encerrou as atividades. Nesse caso, primeiro desconecte os dispositivos da internet, mantendo-os acessíveis apenas pela rede local, e depois investigue se eles são vulneráveis.
O Nextcloud é uma plataforma gratuita e de código aberto para criar seu próprio armazenamento em nuvem, funcionando como alternativa ao Google Drive, Dropbox e Microsoft OneDrive. Ele permite armazenar e sincronizar arquivos entre dispositivos, compartilhá-los com outros usuários e trabalhar com documentos, fotos, calendários e contatos. Os dados podem ficar armazenados no seu próprio servidor ou NAS, em vez dos servidores de uma empresa terceirizada.
Se você armazena dados importantes no Nextcloud, verifique como sua instância de nuvem está configurada. Se você usa o Nextcloud All-in-One, atualize para a versão 14.4.1, na qual a vulnerabilidade já foi corrigida.
Se a sua instalação do Nextcloud estiver configurada de outra maneira, será necessário atualizar o PHP manualmente no dispositivo ou servidor.
Que outros riscos seus dispositivos domésticos podem enfrentar? Leia nossos artigos:
- TV infectada por cavalos de Troia ou os novos riscos dos proxies maliciosos
- Ransomware passa a mirar em backups pessoais
- Sua TV box virou uma porta de entrada para terceiros?
- Seu roteador está trabalhando secretamente para inteligências estrangeiras?
- Três ataques comuns ao Linux residencial
- Como proteger sua casa smart
PHP warns of CVE-2026-115560, a PHP session vulnerability that follows PHP2Shell. Disable session.upload_progress until the next bugfix release.
Related Posts:
The post PHP Warns of New Session Upload Progress Flaw CVE-2026-115560, Urges Mitigation appeared first on Daily CyberSecurity.
A public PoC is out for CVE-2026-114509, a Laravel authentication bypass in TokenGuard enabling account takeover. Upgrade to 12.68.0 or 13.29.0.
Related Posts:
The post Laravel Authentication Bypass PoC Released for Critical TokenGuard Flaw CVE-2026-114509 appeared first on Daily CyberSecurity.

On October 21, PHP released emergency patches for two critical vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS score of 9.2), affecting every PHP version that handles web requests. The bug code dates back to PHP 5.4 from 2012, lives in the PHP engine itself rather than in any application, and allows unauthenticated remote code execution via crafted HTTP requests.
Cloudflare researchers observed tens of thousands of exploit attempts within 45 minutes of public disclosure, hundreds of thousands within two hours, and millions by October 22.
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
— Matthew Prince
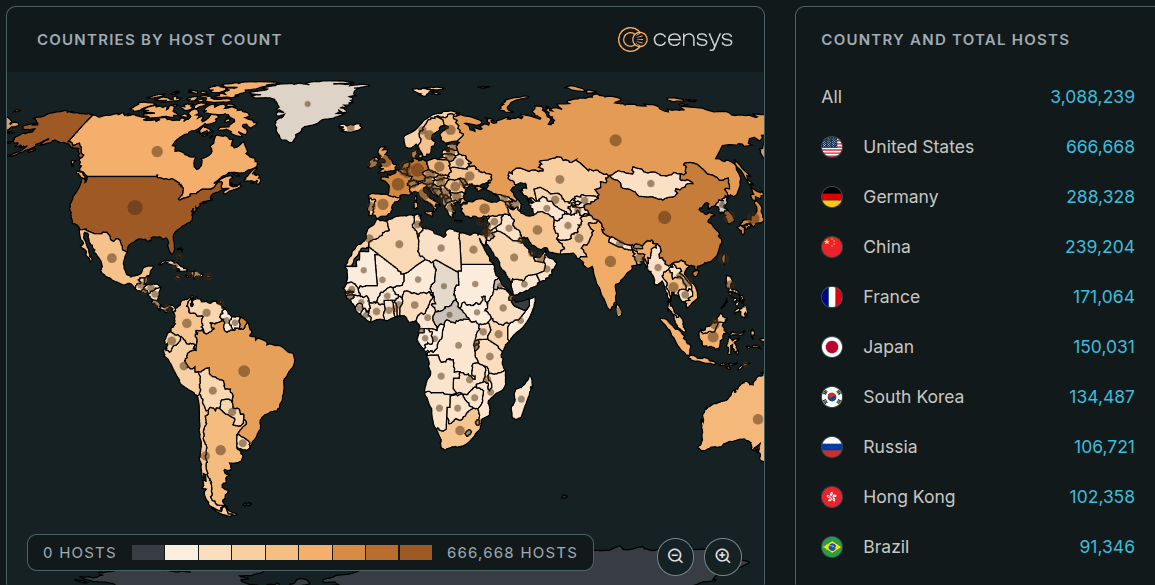
As of October 23, Censys counts over 34.4 million PHP services still running vulnerable versions. Governments, hospitals, and schools across Asia, Europe, and North America have preemptively taken services offline rather than wait.
Below is an image showing the hosts potentially vulnerable to CVE-2026-109618 and/or CVE-2026-109619.
Security firms using honeypots report the same pattern: attackers are scanning many servers and trying to exploit the PHP flaws, but no successful remote code execution has been confirmed in real-world attacks. Sophos says this suggests that attackers are also struggling to exploit the vulnerabilities. Even its own security team needed more effort than expected, despite using AI, to develop a working exploit.
However, the risk is growing. VulnCheck researchers have developed an exploit that bypasses ASLR, a security feature that randomizes where code is stored in memory. By combining both vulnerabilities, they can use a memory leak to bypass this protection and run code on the target system. The exploit works, even though there is no evidence of widespread use yet.
The attempts that have been caught so far are mostly scanning, fingerprinting, and botnet delivery attempts. Cowrai’s analysis of PHP2Shell traffic in the wild found connections to a Mirai variant called Potassium, which contacts a C2 server, checks for an HTTP 200 response, then downloads a Linux executable as a follow-on payload.
“The payload, a likely Mirai botnet variant known as Potassium, was not delivered since the exploitation attempt was unsuccessful due to being blocked by Sophos countermeasures.” states the report published by Sophos. “However, analysis of the sample revealed that is an updated and significantly expanded version of the Mirai-derived botnet variant identified in early 2026.”
The malware can download additional files and disrupt networks. It contacts a hard-coded command-and-control server, checks that the server responds successfully, and downloads a file designed to run on Linux. If normal address lookup fails, it can use public DNS servers such as Google DNS and Cloudflare DNS. Like other Mirai malware, it can also launch distributed denial-of-service (DDoS) attacks.
Arctic Wolf found that both malware samples had Ethereum Name Service (ENS) resolution disabled, meaning the feature was available but not active.
“ENS resolution was disabled in both samples, indicating that the capability was present but inactive.” states Arctic Wolf. “If enabled in future variants, it could complicate disruption by reducing reliance on registrars and DNS providers, requiring defenders to block the ENS names, RPC infrastructure, and resolved command-and-control addresses.”
The botnet’s developers have already added the ability to use ENS to find command-and-control (C2) servers. This could help them keep their infrastructure online and make it harder for authorities to take down their domains, but the feature has not yet been enabled.
Sophos blocked the attempted Potassium delivery before it succeeded. But analysis of the sample itself showed it’s a significantly expanded version of the Mirai variant spotted earlier in 2026, with added DDoS capabilities and fallback DNS resolution using public servers like 8.8.8.8 and 1.1.1.1 hardcoded as backup.
PHP2Shell is being compared to Log4Shell because it affects a huge number of systems. The flaw is in PHP itself, so it can affect websites, content management systems and shared hosting services. Even a basic WordPress site with no extra plugins is at risk if it uses a vulnerable PHP version.
Fixes are available in PHP versions 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Older versions, including 7.4, 8.0 and 8.1, need fixes provided by their software distributors or an upgrade to a supported version.
Cisco Talos notes that scanning for flaws and using public exploit code is easier than building attacks into custom tools. Advanced attackers may still be developing those tools, so administrators should use this time to patch vulnerable systems.
“The true impact of this vulnerability will take time to evaluate.” concludes Talos. “These types of vulnerabilities that impact core technologies tend to cascade into other platforms and applications as they evaluate impact and provide associated patching, harkening back to the waves of exploitation that we saw after Log4J.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, PHP2Shell)
Attackers attempted to exploit two critical PHP vulnerabilities four days before the flaws became public, according to Amazon Threat Intelligence.
“Amazon Threat Intelligence identified a PHP2Shell exploitation attempt dating to Oct. 17, 2026, in MadPot telemetry, four days before public disclosure of CVE-2026-109618 and CVE-2026-109619.” reads the report published by Amazon team.”The exploit attempt originated from an IP address associated with a commercial anonymization network. While the vulnerability was under embargo, the targeting of a honeypot from an anonymized IP address suggests the activity was conducted by a threat actor, though it remains unclear how the actor acquired exploit information prior to disclosure.”
The activity began on October 17, 2026, and appeared in telemetry from MadPot, AWS’s network of honeypots designed to attract and study malicious activity. The company said the first attempt targeted a honeypot from an IP address linked to a commercial anonymization network. The vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, were still under embargo at the time.
AWS believes the use of anonymized infrastructure suggests a threat actor was behind the activity. However, the company hasn’t established how the attacker obtained information about the vulnerabilities before their public disclosure, nor has it confirmed that the early attempts would have succeeded against real-world systems.
The first attempt wasn’t an isolated event. AWS detected multiple proof-of-concept exploits on October 21, with the earliest appearing at around 02:00 UTC, roughly 12 hours before the scheduled public release and patch at 14:00 UTC.
Between 02:00 and 08:00 UTC that day, AWS observed further attempts against MadPot from additional anonymized infrastructure. The payloads and anonymization services varied, leading the company to suspect that multiple actors were involved.
After the embargo ended and PHP released the fixes, more proof-of-concept exploits appeared within hours. AWS reported that attackers used them against its sensors almost immediately, describing PHP2Shell as being broadly exploited in the wild.
The findings show why the date of a public security advisory can’t always serve as the starting point for an incident investigation. In this case, defenders had to account for activity that began before they could publicly identify the vulnerabilities.
“The actual payloads and choices in anonymization infrastructure varied, suggesting these were multiple actors.” continues the report. “Technical analysis is ongoing, and it’s unclear if any of these attempts would have succeeded in real-world systems.”
PHP2Shell refers to two critical flaws in the PHP runtime that can allow unauthenticated remote code execution. An attacker may be able to send a specially crafted web request and run commands on a vulnerable server without first logging in.
PHP published fixes on October 21. The corrected releases are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, according to the official PHP security notice.
The vulnerabilities affect PHP itself, rather than a specific website application. As a result, updating WordPress, Drupal or another application won’t fix the underlying problem if the server continues to run a vulnerable PHP runtime.
AWS says there is no configuration-only workaround that fully addresses both flaws. Organizations should install the fixed PHP version as soon as possible and check whether their hosting provider, operating system vendor or container image has supplied the necessary update.
For systems that can’t be patched immediately, AWS suggests considering whether blocking multipart file uploads is practical. Administrators should assess the impact on their applications before applying that restriction, and they shouldn’t treat it as a replacement for installing the fixes.
AWS recommends reviewing web server logs for suspicious requests, particularly POST requests containing the PHP_SESSION_UPLOAD_PROGRESS string in multipart form data. Security teams should also look for unexpected processes launched by PHP and unexplained changes to files on web application servers.
These checks matter because an attack may leave evidence beyond the original HTTP request. Unexpected command interpreters, newly created files or unusual process activity can help investigators determine whether an attacker progressed beyond probing a vulnerable endpoint.
AWS also published six IP addresses associated with observed activity:
103.216.220.92, observed on October 1731.223.184.166, observed on October 2137.19.200.5, observed on October 21134.209.159.64, observed on October 21103.114.163.188, observed on October 2195.217.98.37, observed on October 21These addresses require careful handling. AWS warns that some belong to shared anonymization infrastructure and aren’t exclusive to PHP2Shell activity, so organizations should investigate matching events rather than automatically blocking every address.
The Cloudflare analysis of PHP2Shell provides additional context. Cloudflare said it had deployed web application firewall protections before public disclosure and had already observed attack traffic targeting its customers, including attempts to change payloads to evade those protections.
A web application firewall can help reduce exposure, but it doesn’t replace patching. Defenders should combine updated software with log analysis, process monitoring and checks for suspicious file changes.
AWS draws a broader lesson from the incident: organizations shouldn’t assume that exploitation begins only after a vulnerability becomes public. The October 17 activity shows that attackers may obtain or develop exploit information while a flaw is still under coordinated disclosure.
Attackers are using AI to develop exploits faster, sometimes within hours of a patch being released. Security teams need to patch critical systems quickly and investigate attacks from the earliest known date. For PHP2Shell, AWS recommends checking logs and activity from October 17 onward, including suspicious behavior that detection tools may not yet recognize.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, PHP)
PHP2Shell remote code execution flaws CVE-2026-109618 and CVE-2026-109619 are exploited in the wild as PoCs go public. Patch PHP now.
Related Posts:
The post PHP2Shell Exploited in the Wild as PoC Exploits and Full Details Go Public appeared first on Daily CyberSecurity.
UPD 23.10.2026: added Kaspersky SIEM rules and events for developing custom detection rules or conducting threat hunting.
UPD 22.10.2026: added a description of how the Kaspersky Managed Detection and Response service detects the described malicious activity.
UPD 22.10.2026: added a description of how Kaspersky Vulnerability Management detects vulnerable versions of PHP.
On October 20, 2026, the PHP security team published a preliminary notice regarding an upcoming emergency release that addresses two critical vulnerabilities (both rated 9.2 on the CVSS scale). The patches were released on Wednesday, October 21, 2026, at 14:00 UTC.
The release was expedited after information about the vulnerabilities was leaked to the public before the scheduled embargo was lifted. In a post on Hacker News, a user reported two RCE vulnerabilities in PHP, allegedly affecting all versions starting with PHP 5.4.0.
The vulnerabilities in question are CVE-2026-109618 and CVE-2026-109619. Shortly after the post appeared, researchers confirmed the existence of the vulnerabilities. Along with the leak of details, an exploit unofficially named PHP2Shell appeared online. In the leaked demo video, the exploit is shown in action on web servers running WordPress, MediaWiki, phpBB, Magento, Joomla, Laravel, Symfony, Drupal, and WHMCS — platforms that power many modern websites. The authenticity of the demonstration and the exact behavior of the exploit had not been independently verified at the time of publication.
According to the researcher who published the PoC, the vulnerabilities are related to the handling of the multipart/form-data MIME type in conjunction with the session upload progress mechanism (session.upload_progress) in the PHP core and fall under the categories of use-after-free and memory corruption. This means that the flaws cannot be fixed via application code, and the only fix is to update PHP on the server. The attack requires no authentication: an attacker with network access to a PHP application can execute arbitrary code with the privileges of the PHP process without needing to authenticate. Security advisories issued by the PHP team on October 21 confirm this information.
The vulnerabilities affect PHP versions 5, 7, and 8. As of this publication, branches 8.2 through 8.5 are supported. Older branches, including PHP 8.1, 8.0, 7.x, and 5.x, have reached the end of their lifecycle; however, due to the critical severity of the vulnerabilities, backported patches have also been released for versions 7.4, 8.0, and 8.1.
Sansec experts estimate that widespread exploitation could begin within 15 minutes of the update’s release. We strongly recommend that administrators responsible for publicly accessible PHP web servers take the following steps before the patch is available:
session.upload_progress.enabled = Off using the php_admin_flag in PHP-FPM pools.Kaspersky solutions detect the described malicious activity at various stages of the attack. Possible detection scenarios are listed below.
When an attempt is made to exploit these RCE vulnerabilities, Kaspersky Endpoint Detection and Response promptly alerts the user to suspicious actions performed in the context of a web server, on both Linux and Windows machines. This activity is detected by the following rules:
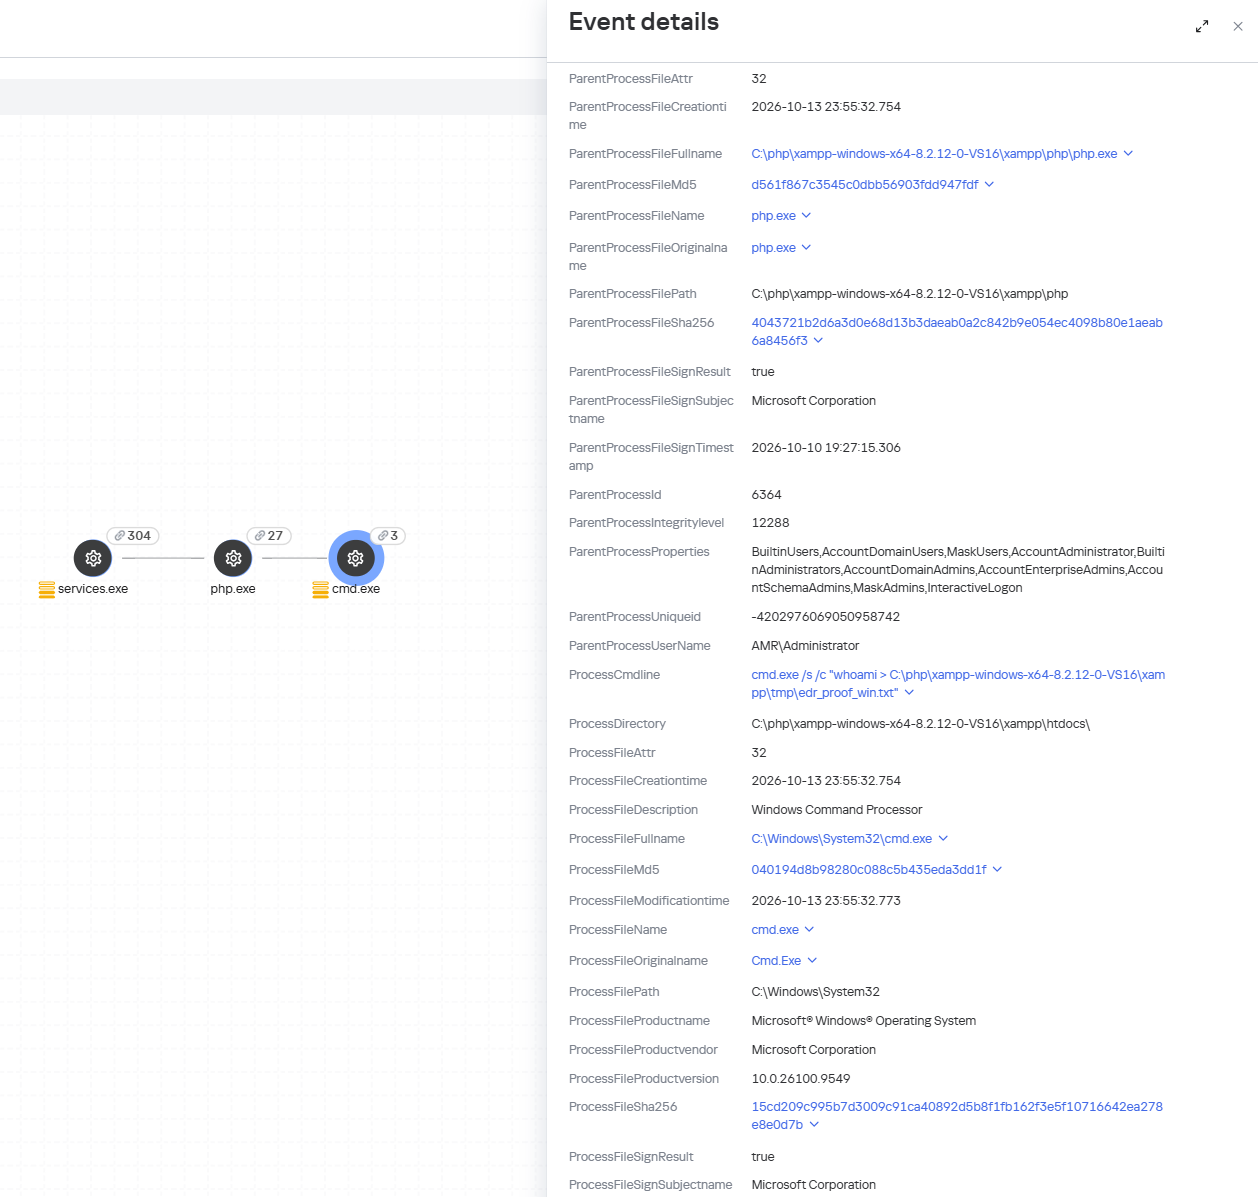
Detection of the PHP2Shell vulnerability exploit by KEDR
Exploitation of the PHP2Shell vulnerability in network traffic is detected by Kaspersky Anti Targeted Attack (KATA). This solution detects such activity with the following verdicts: Exploit.CVE-2026-109618.HTTP.C&C and Exploit.CVE-2026-109619.HTTP.C&C.
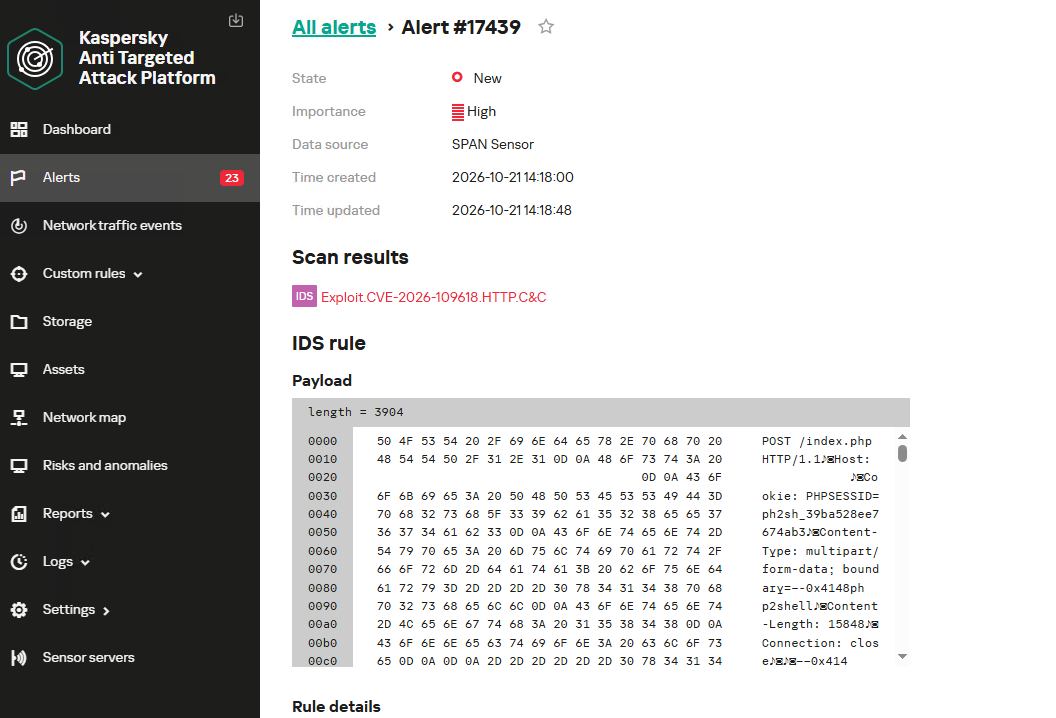
Detection of the PHP2Shell vulnerability exploit by KATA
Kaspersky Endpoint Security, now available as Kaspersky Next, also detects malicious post-exploitation activity using the Behavior Detection component, with verdicts such as PDM:Exploit.Linux.Generic and PDM:Exploit.Win32.Generic.
Our Kaspersky Vulnerability Management solution detects vulnerable software versions using the Vulnerability scanning and Agentless black-box scanning components.
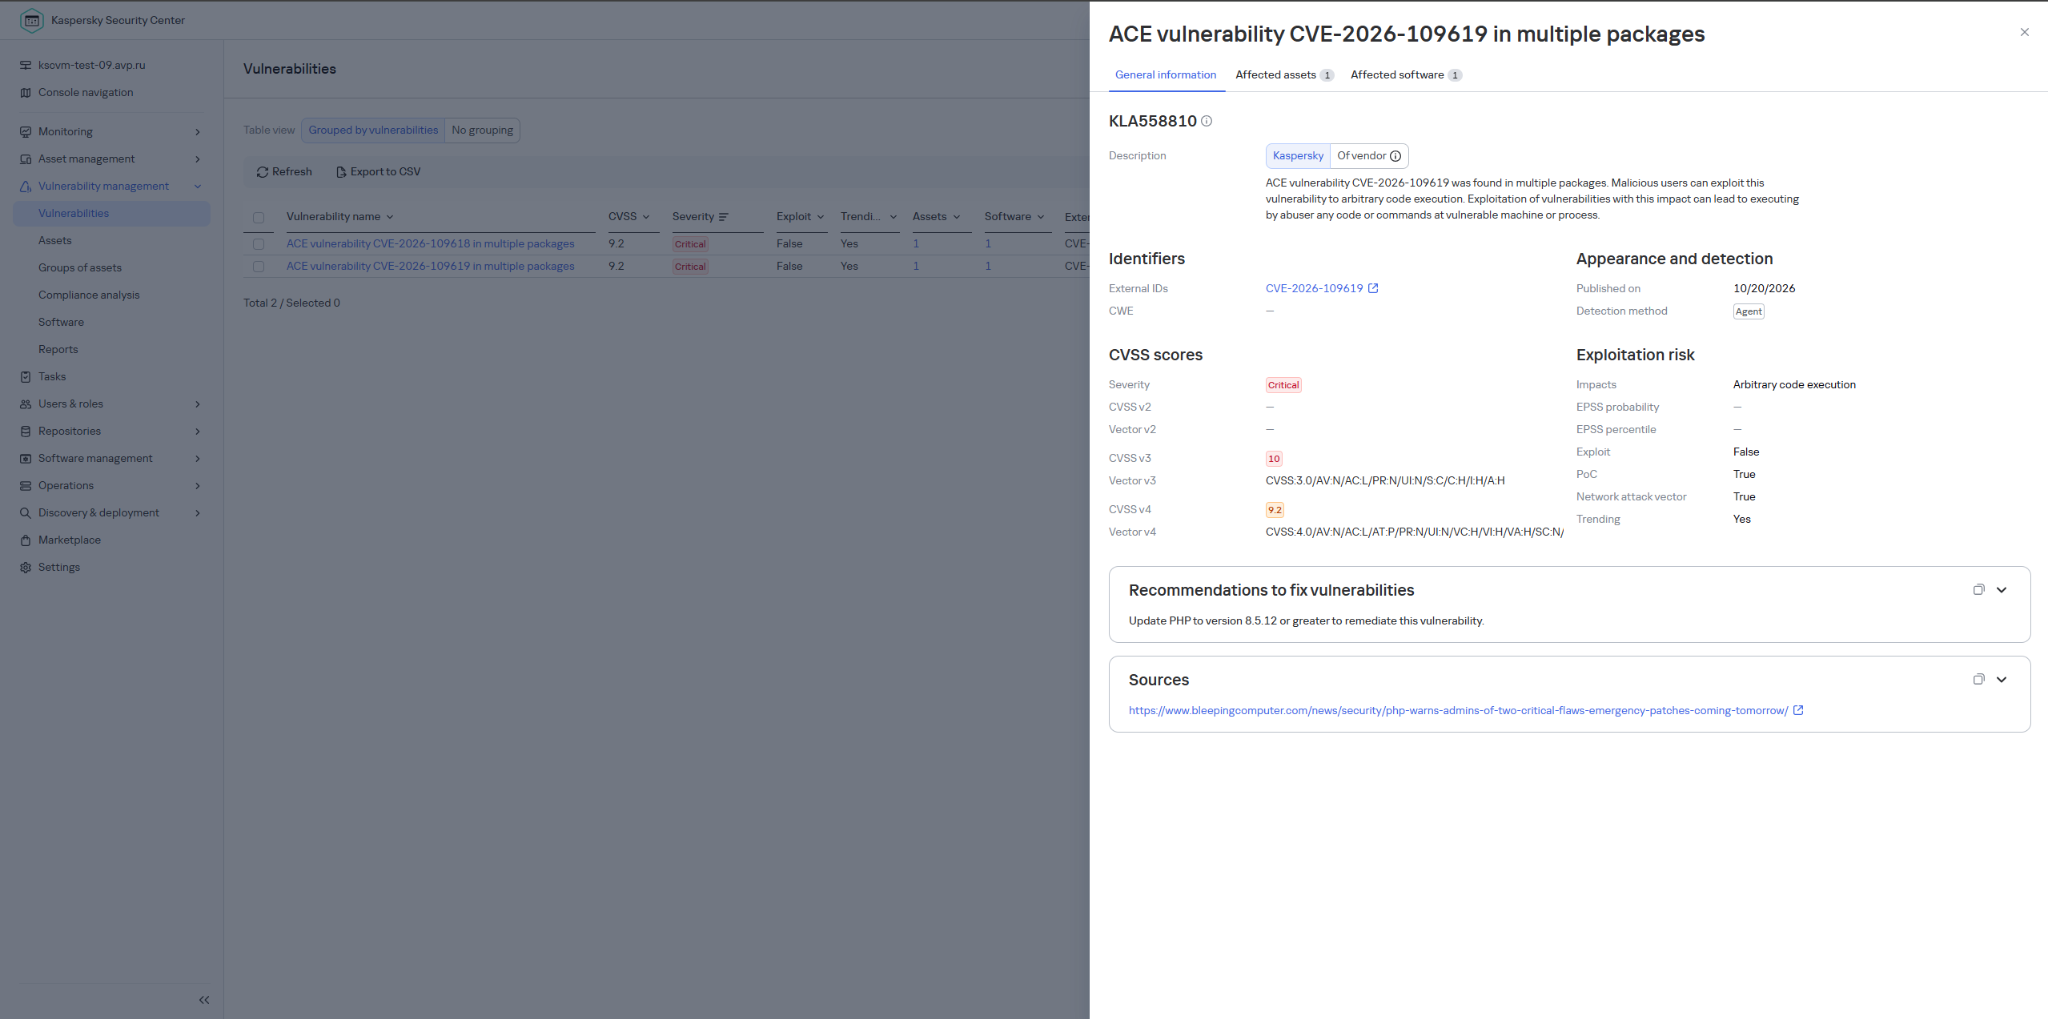
Detection of the PHP vulnerability in Kaspersky Vulnerability Management
Moreover, MDR detects other malicious activity not directly related to remote code execution.
To protect companies that use our Kaspersky SIEM system, the product repository includes rules that help detect the following malicious activity.
We also recommend monitoring the creation of scripts or executable files in the web server directory when developing your own detection rules or conducting threat hunting:
((DeviceEventClassID = '4663' AND DeviceCustomString1 ilike 'WriteData') OR DeviceEventClassID = '11')
AND match(FileName,'(?i).*\.(php|asp|aspx|ashx|jsp|js|jar|jse|dll|exe|bat|ps1|vbs|wsf|wsh|msi|msp|hta|cpl)$')
AND match(DestinationProcessName,'(?i).*(php-cgi|nginx|httpd|w3wp)\.exe')
Name = 'openat' AND has(SA.Nametype, 'CREATE')
AND
length(arrayFilter(x -> match(x, '(public_html|var/www|usr/local/apache2|usr/local/httpd|var/apache|srv/www|home/httpd/html|srv/http|usr/share/nginx/html|var/lib/pgsql/data|usr/local/mysql/data|var/lib/mysql|var/vsftpd|etc/bind|var/named)'), SA.FileName))>1
AND
length(arrayFilter(x -> match(x, '\.(aspx|asp|asmx|asax|ashx|jspx|jsp|js|phpt|php|phtml|pht|cfm|shtml|htaccess|fcgi|cgi|pl|py|sh)'), SA.FileName))>1
