❌

Visualização normal

Antes de ontemStream principal
  • ✇Security | CIO
  • Quantum without the hype: The CIO’s next architecture challenge
    The most expensive quantum mistake a CIO could make today may not be investing too early. It may be investing in the wrong capabilities, for the wrong reasons, without understanding the architectural and economic consequences. Over decades of leading enterprise technology, architecture, modernization, and innovation in complex, highly regulated environments, I have seen a recurring pattern: technological enthusiasm advances faster than institutional readiness. Capital g
     

Quantum without the hype: The CIO’s next architecture challenge

5 de Novembro de 2026, 06:00

The most expensive quantum mistake a CIO could make today may not be investing too early. It may be investing in the wrong capabilities, for the wrong reasons, without understanding the architectural and economic consequences.

Over decades of leading enterprise technology, architecture, modernization, and innovation in complex, highly regulated environments, I have seen a recurring pattern: technological enthusiasm advances faster than institutional readiness. Capital gets committed. Platforms become entrenched. Dependencies multiply. Business value remains difficult to demonstrate.

Quantum computing risks repeating that pattern, but with an important distinction: The cybersecurity consequences demand action today, while the timing and economics of broader commercial quantum advantage remain uncertain.

That is the strategic tension CIOs must resolve.

Quantum readiness and preparedness is not a race to acquire qubits. It is a discipline of protecting enterprise trust, preserving strategic options and directing scarce capital toward demonstrable value.

The fundamental question is no longer whether quantum computing deserves executive attention. It is whether CIOs and enterprises can distinguish what must be protected now, what deserves experimentation and what should remain an option rather than a financial commitment.

Two quantum clocks. One enterprise balance sheet

Quantum presents two fundamentally different timelines to a CIO.

The first is the security clock.

In August 2024, the National Institute of Standards and Technology (NIST) published its first three finalized post-quantum cryptography standards, establishing practical mechanisms for protecting information against anticipated quantum-enabled threats.

This is critical because cryptography is not an isolated cybersecurity component. It underpins identities, financial transactions, digital signatures, software integrity, communications, connected infrastructure and trusted business relationships.

A sufficiently capable future quantum computer could compromise certain widely deployed public-key cryptographic methods.

The October 2026 U.S. Government Accountability Office (GAO) report, Quantum Computing: Federal Actions Needed to Prepare for Emerging Cyber Threat, reinforces the urgency. None of the 24 federal agencies examined had fully addressed all three assessed preparatory practices for migrating vulnerable cryptography.

The lesson extends beyond government: you cannot migrate cryptographic dependencies you have not discovered.

The second is the commercial advantage clock.

Quantum computing may eventually offer meaningful advantages in selected areas of chemistry, materials science, simulation and optimization. But promising research does not automatically translate into repeatable enterprise economics.

IBM’s published quantum technology roadmap targets a fault-tolerant quantum system in 2029. That is an important technological ambition, not a guaranteed date for widespread commercial advantage.

These two clocks should not share the same investment assumptions.

Security readiness is justified by exposure and risk tolerance. Commercial adoption must be justified by demonstrated advantage and economic returns.

Confusing the two creates either dangerous underinvestment or speculative overspending for the CIOs.

Architecture before acquisition

The enterprise architecture challenge is more consequential than the quantum procurement question.

For CIOs, post-quantum preparation begins with initial understanding of where vulnerable cryptography exists across their enterprise, how it supports critical business services and whether those dependencies can be changed without destabilizing operations.

For example, consider a globally distributed financial institution.

Cryptographic dependencies may span payment platforms, customer identities, authentication services, certificates, mainframes, cloud environments, third-party APIs and decades of retained information.

Replacing an algorithm is not necessarily equivalent to replacing a library.

Some changes affect protocols, hardware security modules, certificate lifecycles, application compatibility, vendor contracts and operational resilience.

This demands cryptographic agility: the ability to replace or adapt cryptographic mechanisms without rebuilding the enterprise.

The same architectural discipline applies to future quantum workloads.

Enterprises should favor modular integration, well-defined interfaces, workload portability and interoperability across classical computing, high-performance computing, AI and emerging quantum services.

Quantum will not make classical computing obsolete. The more credible architectural direction is selective integration where a quantum capability demonstrably improves a specific computational outcome.

The architectural objective therefore is not quantum dependence. It is quantum optionality.

An enterprise should be able to adopt a useful breakthrough without surrendering control of its technology economics or becoming captive to a single provider.

The missing equation: Quantum workload economics

The quantum conversation becomes strategically meaningful when CIOs stop asking what a quantum computer can theoretically perform and start asking what business outcome it can improve.

The OECD’s 2026 research, Building Business Readiness for Quantum Computing, identifies barriers including technological immaturity, uncertainty surrounding business applications, access and training costs, and shortages of specialized expertise.

These are not simply engineering obstacles. They are capital allocation constraints. This means that a quantum experiment may demonstrate technical progress while failing to establish commercial value.

For example, a proposed optimization workload should be evaluated against competitive classical algorithms, realistic datasets, operational constraints and the full cost of execution.

The comparison must include more than processing time. It should consider problem preparation, data movement, orchestration, error mitigation or correction, integration, specialized talent, assurance and recurring operating expenses.

Even an impressive laboratory result may offer little economic benefit if the end-to-end enterprise workflow becomes slower, costlier or less dependable.

I would therefore introduce a more demanding investment metric: Cost per Trusted Quantum-Enabled Business Outcome.

This proposed measure evaluates the total attributable cost of achieving a validated business result, including the controls necessary to make that result operationally acceptable.

The denominator is not the number of quantum circuits executed. It is the number of useful, verified business outcomes delivered.

Where no defensible quantum advantage exists, the responsible decision may be to continue using classical computing.

That is not technological conservatism. It is capital discipline.

Introducing the quantum capital discipline framework

I propose a six-dimensional executive framework for separating quantum preparedness from quantum speculation.

  1. Exposure: What must we protect? Identify vulnerable cryptographic dependencies, long-lived sensitive information, critical services and contractual or regulatory obligations. Prioritize remediation by business consequence, not technology fashion.
  2. Relevance: What problem warrants quantum? Establish a specific business problem whose computational characteristics plausibly justify quantum investigation. Scientific curiosity alone is not an enterprise investment thesis.
  3. Advantage: What evidence proves improvement? Demand reproducible comparisons against strong classical alternatives. Evaluate solution quality, performance, operational constraints and independent validation.
  4. Architecture: Can we adapt without lock-in? Assess portability, integration complexity, vendor concentration, reversibility and the ability to change technology choices as the market evolves.
  5. Economics: What is the full cost of value? Measure total lifecycle costs, opportunity costs, talent requirements and credible returns. Distinguish research expenditure from production investment.
  6. Authority: Who decides to advance, defer or stop? Assign accountable decision makers, measurable milestones, investment thresholds and explicit exit criteria. Together, these dimensions form the Quantum Capital Discipline Framework.

Its governing principle is straightforward:

Capital follows evidence. Architecture preserves options. Governance owns consequences.

Importantly, this framework does not subject essential cryptographic remediation to the same commercial-return requirements as speculative quantum workloads. Security obligations and innovation opportunities require different investment justifications.

What boards should demand from their CIOs

Quantum strategy should enter Board discussions through enterprise risk, capital allocation, resilience and competitive positioning — not promotional demonstrations.

I would encourage directors and executive committees to demand answers to five key questions:

  1. Which critical business services and information assets face material quantum-related cryptographic exposure?
  2. Can we modernize vulnerable dependencies without unacceptable operational disruption?
  3. Which proposed quantum applications outperform credible classical alternatives?
  4. What evidence would justify expanding, delaying or terminating quantum investments?
  5. Who is accountable for the financial, security and architectural consequences?

These five questions create a practical governance boundary between preparedness and speculation. They also expose a broader institutional weakness: enterprises often approve emerging technology investments without establishing the conditions under which those investments should be reconsidered.

Quantum requires a different approach.

Investment decisions should be revisited when technical capabilities, benchmark results, standards, security exposure or business economics materially change.

Boards should insist on measurable progress but avoid manufacturing artificial deadlines for breakthroughs nobody can reliably predict.

The CIO’s next mandate: Preserve the freedom to act

Quantum computing will not transform every industry simultaneously, deliver equal advantage across workloads or reward every early investor.

Some enterprises may eventually realize significant value from specialized quantum applications. Others may encounter quantum’s most immediate consequences through cryptographic modernization, technology dependencies and the protection of long-lived information.

Both outcomes demand leadership today.

The CIO’s responsibility is not to predict which quantum architecture will prevail or which vendor will dominate. It is to ensure that today’s decisions do not compromise tomorrow’s ability to compete, adapt and protect enterprise trust.

That requires investment discipline, architectural foresight, credible experimentation and accountable governance.

The next quantum advantage may belong not to the enterprise that invests first or spends the most, but to the one that knows precisely when to act, where to invest and when to walk away.

Quantum readiness is not measured by the technology an enterprise owns. It is measured by the strategic freedom it retains, the risks it responsibly reduces and the business value it can demonstrably create.

That is the difference between quantum enthusiasm and quantum leadership.

Quantum leadership is not about predicting when the future arrives. It is about architecting the freedom to embrace it, exercising the discipline to invest in it and preserving the authority to walk away when promise fails to become value.

  • ✇Security | CIO
  • Practical quantum computers are over a decade away, says NEC
    A practical, commercial quantum computer is over a decade away, executives at Japanese IT services company NEC are reported as saying. That’s why, according to Japanese news publication The Mainichi, company has pulled the plug on its plans to develop a quantum computer — although it will still continue research into quantum technology. NEC sources told The Mainichi that it would take at least a decade to build a quantum computing that could be put to practical use,
     

Practical quantum computers are over a decade away, says NEC

18 de Setembro de 2026, 13:44

A practical, commercial quantum computer is over a decade away, executives at Japanese IT services company NEC are reported as saying.

That’s why, according to Japanese news publication The Mainichi, company has pulled the plug on its plans to develop a quantum computer — although it will still continue research into quantum technology.

NEC sources told The Mainichi that it would take at least a decade to build a quantum computing that could be put to practical use, and it would be difficult to monetize the technology.

This is quite a turnaround for NEC which three years ago was talking about its advances in quantum and its plans to accelerate investment in the technology.  The company is certainly bucking the trend as quantum computing is seen as being very much at the cutting edge of research. Pioneers in the field were awarded the Nobel Prize in Physics last year, while companies such as Nvidia and IBM are keen to boost their quantum credentials.

Despite its early successes in the quantum field, The Mainichi reports that NEC is lagging its Japanese competitors such as Fujitsu and Hitachi when it comes to the latest advances.

There is also the level of investment required. According to The Mainichi, Japan is set to commit just 10 trillion yen ($65.3 billion) to quantum computing by 2040, far lower than the sums invested by the US and China.

We’re talking about a long game. Quantum technology has been talked about for some time, but we’re still a long way from seeing the technology in the mainstream. NEC may not be the only company to decide the cost of investment is not worth it.

  • ✇Security | CIO
  • Quantum computing takes aim at AI
    As quantum computing inches closer to mainstream enterprise reality, a key question is arising: Could the technology shake up how IT leaders make use of AI? Much has been made about the problems quantum computing will create for traditional encryption methods, but experts say the technology could also take some pressure off the compute of large AI workloads, with quantum chips augmenting the GPUs and CPUs used today. The timeframe for availability of general-purpose,
     

Quantum computing takes aim at AI

15 de Setembro de 2026, 06:30

As quantum computing inches closer to mainstream enterprise reality, a key question is arising: Could the technology shake up how IT leaders make use of AI?

Much has been made about the problems quantum computing will create for traditional encryption methods, but experts say the technology could also take some pressure off the compute of large AI workloads, with quantum chips augmenting the GPUs and CPUs used today.

The timeframe for availability of general-purpose, error-corrected, or fault-tolerant quantum computers remains up for debate, but some quantum-focused companies have roadmaps for quantum systems to hit the market in the next two to four years.

For example, QuEra has projected that cloud access to a fault-tolerant 256-qubit system will be available in 2028, and IBM plans to release its 200-qubit Starling system in 2029. Some critics question those product roadmaps, however.

Still, Australian company Silicon Quantum Computing (SQC) is already selling quantum-based chips — called QPUs or quantum machine learning processors — trained to handle specific machine learning applications in industries such as finance, pharmaceuticals, energy, and defense.

Quantum-based chips can already speed up the training of AI models significantly, and quantum computers have the potential to run AI workloads more efficiently than traditional GPUs and CPUs, says Matthew Bradley, SQC’s vice president of corporate development.

“Given the increasing costs of AI, and if one is concerned about the broader power consumption and resource intensity of AI, that’s a really material result,” he explains. “It’s not quite as simple as drawing a straight line — if you do X, you can save Y — but it’s possible you can save a certain amount of model time that is resource-beneficial, both in terms of costs of running the model, but also sort of time and efficiency within the organization.”

Other industry insiders see the same potential. In some cases, quantum computers are already being used alongside AI to significantly improve results, notes Murray Thom, vice president of quantum technology evangelism at quantum provider D-Wave Systems.

For example, Japanese pharmaceutical company Shionogi has used D-Wave’s quantum computing technology and AI in the drug discovery process, resulting in a 10-fold increase in the number of desirable molecules uncovered, he says.

“We see early research and proof-of-concept projects indicating great potential for quantum computers to handle certain elements of AI workloads more efficiently than CPUs and GPUs,” Thom adds. “The opportunity is not for quantum computers to replace CPUs and GPUs, but to complement them by handling parts of AI workflows where quantum approaches may offer advantages in performance, solution quality, or energy efficiency.”

Outsiders also see benefits

As representatives of the quantum industry, Bradley and Thom certainly have strong motivations to tout the benefits of the technology, but other experts also see potential.

Most of the focus so far on the benefits of quantum AI has been on so-called quantum speed-up, when quantum systems process information faster than traditional computers, enabling enterprises to more readily tackle complex calculations and large data sets.

Quantum computers could also explore multiple solutions at the same time, allowing for accelerated decision-making.

Experts say quantum computers won’t replace traditional hardware in the foreseeable future, but running a hybrid architecture combining QPUs, CPUs, and GPUs could accelerate AI workloads and create some energy and compute efficiencies.

“GPUs and CPUs will continue to support AI workloads, and they will keep getting more capable,” says John Licata, futures director and enterprise quantum lead at ServiceNow. “QPUs come in alongside them, on the specific problems where classical compute runs into limits of scale, time, or scope.”

But operators of AI systems need to think creatively about how to use quantum computing alongside AI to get the full benefits, he adds. IT leaders must envision future AI workloads to find a place for quantum AI, he suggests.

“There is real strategic advantage in simulating multiple future pathways to see where GPUs come under stress, especially with billions of agents coming online in the next few years, greater needs for governance and regulatory compliance, and new ways to deliver autonomous decision-making with more confidence,” he says. “The door that opens is hybrid workloads where GPUs, CPUs, and QPUs each do what they do best.”

Quantum challenges

Quantum solutions still have some disadvantages, however, that make them unlikely replacements for GPUs in AI tasks, other experts say. GPUs are well suited to the dense matrix operations that dominate current machine learning problems, whereas many proposed quantum algorithms come with significant data-loading, measurement, and error-correction challenges, says Arjun Kudinoor, quantum security advisor at cybersecurity vendor Protegrity.

“Quantum computers could eventually accelerate some AI workloads, but I would not expect them to broadly replace GPUs,” he adds. “Quantum computers still need major advances in error correction, and any benefits will probably be limited to specific subroutines of larger AI workloads.”

Adnan Masood, chief AI architect at IT services vendor UST, also sees significant potential for quantum computing in the coming years but agrees that there are major technical hurdles ahead for the technology to replace GPUs and CPUs for AI tasks.

Still, he expects hybrid quantum and traditional architecture to arrive in the 2030s, with GPU clusters offloading structured workloads to QPUs and ingesting the output back.

Instead of focusing on the potential for QPUs to replace GPUs or cut energy consumption, IT leaders should focus on the impact on encryption and on quantum-inspired classical algorithms that run on GPUs, such as tensor network compression, Masood says.

Post-quantum cryptography is a non-speculative approach to quantum computing, he adds. “The threat is ‘harvest now, decrypt later’ — an adversary captures encrypted archives and traffic today and decrypts them once a cryptographically relevant machine exists,” he says.

Masood doesn’t recommend that IT leaders start to hire quantum machine learning teams. Every quantum AI vendor pitch should examine whether they provide real hardware or a simulator, whether they deal with classical data or quantum-native data, and what exactly their product is compared to.

IT leaders should also look for evidence of quantum advances, he says, including peer-reviewed end-to-end quantum ML advantages on classical data, and quantum product timelines delivered on schedule.

“Set your escalation triggers now, so you react to evidence rather than press releases,” he adds.

Protegrity’s Kudinoor, also a doctoral student in MIT’s Center for Theoretical Physics, agrees on the encryption threat, with the potential for quantum computers to break RSA- and ECC-based encryption.

Meanwhile, IT leaders should start to pay attention to the quantum AI space, he suggests. “CIOs and other IT leaders should watch the quantum and AI space with cautious optimism, relying on trusted subject matter experts and avoiding hype-driven investments,” he says.

  • ✇Firewall Daily – The Cyber Express
  • G7, CISA Urge Urgent Shift to Post-Quantum Cryptography Samiksha Jain
    Some of the world's leading democracies are pushing governments and companies to start preparing for post-quantum cryptography before quantum computers become powerful enough to break the encryption systems that protect global digital infrastructure today. In a joint advisory released Thursday, the G7 Cybersecurity Working Group and the U.S. Cybersecurity and Infrastructure Security Agency (CISA) said organizations should begin their transition to post-quantum cryptography now, rather than wait
     

G7, CISA Urge Urgent Shift to Post-Quantum Cryptography

7 de Setembro de 2026, 03:51

post-quantum cryptography

Some of the world's leading democracies are pushing governments and companies to start preparing for post-quantum cryptography before quantum computers become powerful enough to break the encryption systems that protect global digital infrastructure today.

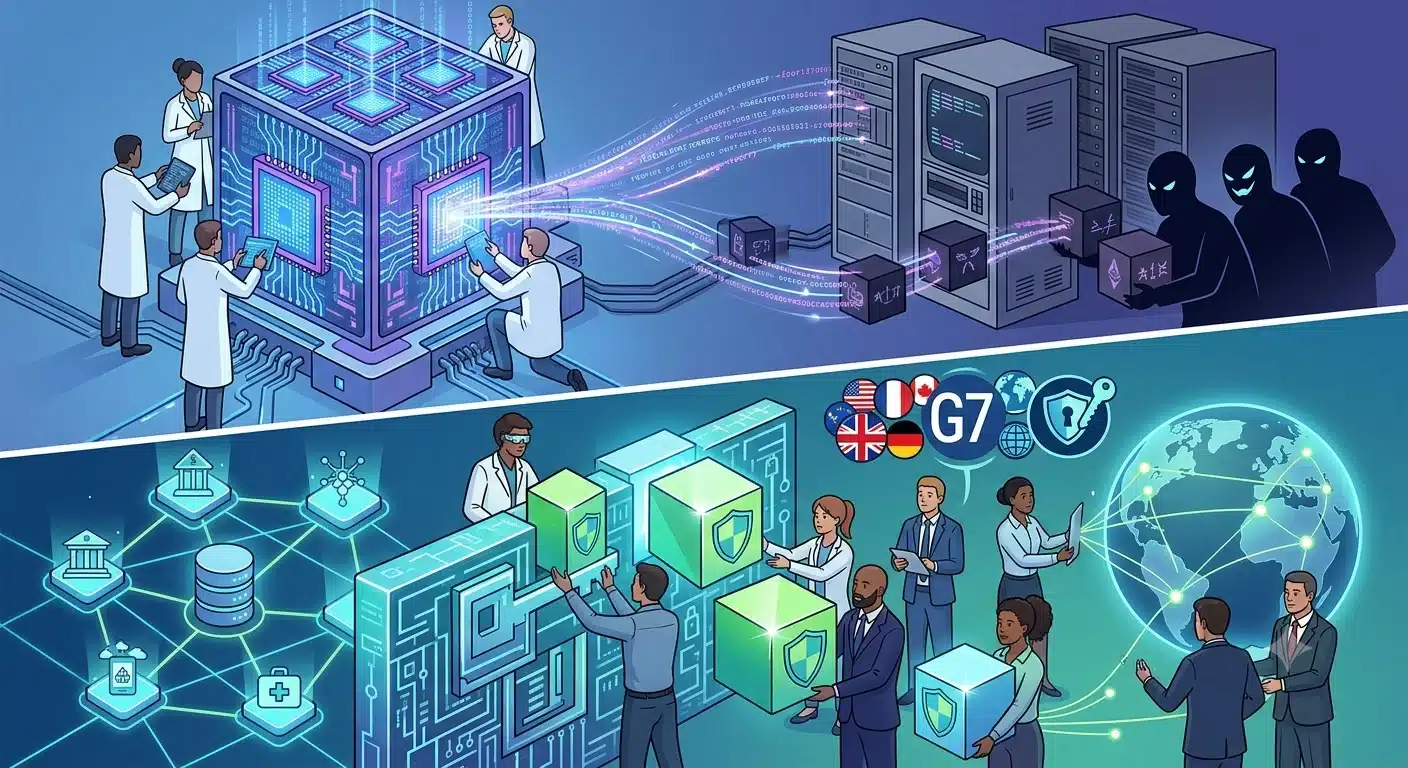
In a joint advisory released Thursday, the G7 Cybersecurity Working Group and the U.S. Cybersecurity and Infrastructure Security Agency (CISA) said organizations should begin their transition to post-quantum cryptography now, rather than waiting until cryptographically relevant quantum computers (CRQCs) are available to threat actors.

Why the Post-Quantum Cryptography Shift Cannot Wait

The publication, titled "Preparing for the Post-Quantum Era: A Call to Action," warns that the quantum computing threat is no longer a distant concern. While the exact timeline for CRQC development remains uncertain, the working group said recent technological advances suggest such machines could emerge sooner than expected, putting widely used public-key cryptography mechanisms at risk.

One of the most immediate dangers is a tactic known as "harvest now, decrypt later," where malicious actors intercept and store encrypted data today with the intention of decrypting it once a CRQC becomes available. This poses a serious risk to governmental records, sensitive personal data, and trade or business secrets that require long-term confidentiality.

The advisory also cautions that CRQCs could eventually be used to target authentication mechanisms, allowing bad actors to impersonate trusted entities, forge data, or compromise equipment. Because supply chain vulnerabilities can cascade, a single organization's delay in adopting post-quantum cryptography could expose entire sectors to compromise.

According to the report, organizations that fail to act may also face business consequences beyond security risk, including exclusion from public procurement contracts and loss of competitive advantage.

Five Priorities for the PQC Transition

The G7 Cybersecurity Working Group outlined five priority areas to guide the global shift toward post-quantum cryptography:

  1. Raising awareness — Many organizations still view the quantum threat as a distant or purely technical issue. The group called for awareness campaigns, technical guidance, and workforce upskilling to reframe it as an economic and business risk.
  2. Developing national strategies — Countries are encouraged to build strategies that ensure an adequate supply of quantum-safe hardware and software while encouraging adoption, integrating the effort into broader digital privacy and security policies.
  3. Advancing research and development — Governments should fund research programs and support pilot projects and testbeds to help organizations test and refine their transition to post-quantum cryptography.
  4. Building public-private partnerships — Collaboration between government, industry, and academia is seen as key to developing domestic expertise, lowering transition costs, and sharing playbooks and case studies across sectors.
  5. Integrating PQC into cybersecurity requirements — The group recommends treating post-quantum cryptography adoption as a natural evolution of cryptographic best practice, and embedding requirements into public procurement to push both vendors and organizations toward quantum-safe systems.

The advisory emphasizes that the shift to post-quantum cryptography cannot be solved by individual organizations in isolation. Instead, it calls for early engagement, coordinated planning, and informed decision-making across public and private sectors worldwide.

Tackling the risks that the impending quantum computing era poses to current cryptographic systems... requires a coordinated global effort to transition to PQC," the report states, adding that public and private organizations must act now to safeguard confidential data, supply chains, and critical systems.

The document was jointly published by cybersecurity authorities from Canada, Germany, Italy, Japan, the United Kingdom, the United States, and France's ANSSI, with participation from the European Commission and support from the EU Agency for Cybersecurity (ENISA).

  • ✇Schneier on Security
  • Python Now Has a Post-Quantum Encryption Library Bruce Schneier
    This is good: Post-quantum cryptography is now one pip-install away for the entire Python ecosystem. With funding from the Sovereign Tech Agency, we implemented support for ML-KEM, the NIST-standard key-establishment primitive, and ML-DSA, the NIST-standard digital-signature primitive, in pyca/cryptography. Remember, the reason to do this now is because there’s no emergency. And because you will make your systems crypto agile, which is always a good idea.
     

Python Now Has a Post-Quantum Encryption Library

10 de Agosto de 2026, 08:02

This is good:

Post-quantum cryptography is now one pip-install away for the entire Python ecosystem. With funding from the Sovereign Tech Agency, we implemented support for ML-KEM, the NIST-standard key-establishment primitive, and ML-DSA, the NIST-standard digital-signature primitive, in pyca/cryptography.

Remember, the reason to do this now is because there’s no emergency. And because you will make your systems crypto agile, which is always a good idea.

  • ✇Security Boulevard
  • Inventors of Quantum Cryptography Win Turing Award Bruce Schneier
    Charles Bennett and Gilles Brassard have won the 2026 Turing Award for inventing quantum cryptography. I am incredibly pleased to see them get this recognition. I have always thought the technology to be fantastic, even though I think it’s largely unnecessary. I wrote up my thoughts back in 2008, in an <a href+https://www.schneier.com/essays/archives/2008/10/quantum_cryptography.html”>essay titled “Quantum Cryptography: As Awesome As It Is Pointless.” Back then, I wrote: While I like the
     

Inventors of Quantum Cryptography Win Turing Award

31 de Março de 2026, 08:05

Charles Bennett and Gilles Brassard have won the 2026 Turing Award for inventing quantum cryptography.

I am incredibly pleased to see them get this recognition. I have always thought the technology to be fantastic, even though I think it’s largely unnecessary. I wrote up my thoughts back in 2008, in an <a href+https://www.schneier.com/essays/archives/2008/10/quantum_cryptography.html”>essay titled “Quantum Cryptography: As Awesome As It Is Pointless.”

Back then, I wrote:

While I like the science of quantum cryptography—my undergraduate degree was in physics—I don’t see any commercial value in it. I don’t believe it solves any security problem that needs solving. I don’t believe that it’s worth paying for, and I can’t imagine anyone but a few technophiles buying and deploying it. Systems that use it don’t magically become unbreakable, because the quantum part doesn’t address the weak points of the system...

The post Inventors of Quantum Cryptography Win Turing Award appeared first on Security Boulevard.

  • ✇Security Boulevard
  • Will Your Organization Take the Quantum Leap in 2026? Read This First David McNeely
    Explore how organizations can prepare for the quantum age by developing quantum security intelligence, establishing governance plans, and prioritizing system updates. Learn strategies for building resilience without exorbitant investments as quantum computing technology advances The post Will Your Organization Take the Quantum Leap in 2026? Read This First appeared first on Security Boulevard.
     
  • ✇Security Intelligence
  • 2024 trends: Were they accurate? Jennifer Gregory
    The new year always kicks off with a flood of prediction articles; then, 12 months later, our newsfeed is filled with wrap-up articles. But we are often left to wonder if experts got it right in January about how the year would unfold. As we close out 2024, let’s take a moment to go back and see if the crystal balls were working about how the year would play out in cybersecurity. Here are five trends that were often predicted for 2024. 1. The use of artificial intelligence in cybersecurity will
     

2024 trends: Were they accurate?

23 de Dezembro de 2024, 14:00

The new year always kicks off with a flood of prediction articles; then, 12 months later, our newsfeed is filled with wrap-up articles. But we are often left to wonder if experts got it right in January about how the year would unfold. As we close out 2024, let’s take a moment to go back and see if the crystal balls were working about how the year would play out in cybersecurity.

Here are five trends that were often predicted for 2024.

1. The use of artificial intelligence in cybersecurity will increase

As the year began, there was no doubt that artificial intelligence (AI) would be a main character in the year’s events — and that was right on the money. Many organizations began to use or continue using AI in their cybersecurity operations in a wide range of ways. For example, Microsoft’s internal response teams use a large language model to manage requests and tickets based on how they were handled previously, saving 20 hours per person each week.

As the world turned its attention over the summer to the Paris Olympics, the team responsible for keeping the Paris Olympics data, apps, systems and even physical buildings protected turned to AI. While 140 cyberattacks were linked to the Olympics, the teams’ efforts resulted in no disruption of the competitions.

Throughout the entire life cycle of the games, from before the opening ceremony to after the torch left Paris, cybersecurity teams used AI to secure critical information systems, protect sensitive data and raise awareness within the games’ ecosystem. Additionally, algorithmic video surveillance based in AI scanned video to detect abandoned bags, the presence of weapons, unusual crowd movements and fires.

2. Organizations will see more AI-based threats and attacks

Unfortunately, experts were right about cyber criminals also turning to AI technology to more effectively conduct attacks. Threat actors are using AI in a wide range of ways for data breaches and cyberattacks, including improved reconnaissance, better target profiling and lowering expertise required for conducting an attack. Because AI can automate many processes required for an attack, such as vulnerability scanning, exploitation and data exfiltration processes, more cyber criminals now have the skills for even more damaging attacks.

“Since the release of gen AI, attackers are increasingly employing tools along with large language models to carry out large-scale social engineering attacks, and Gartner predicts that by 2027, 17% of total cyberattacks/data leaks will involve generative AI,” wrote Gartner in an August 2024 press release.

IBM distinguished engineer Jeff Crume has no doubt that the trend of cyber criminals using AI for attacks will continue in 2025. He says that cyber professionals do a better job of authentication because attackers are finding it easier to log in than to hack in. While looking for bad grammar and spelling errors now works to spot phishing attacks, he expects that this will no longer work as AI-based phishing attacks hit mass distribution.

Explore cybersecurity services

3. An increase in deepfakes and deceptions

While experts correctly predicted that deepfakes would become more of a threat in 2024, it’s likely no one expected the scale of arguably the most shocking deepfake story of the year. At the beginning of 2024, attackers created a deepfake video call that led to an employee giving the cyber criminals $25 million, which showed the power and damage that deepfakes can cause. But the World Economic Forum expects that the trend will only increase, even declaring that over the next two years, AI-fueled disinformation will be the number one threat in the world.

Throughout the year, other deepfake incidents made headlines. Quantum AI, an AI company, was suspected by the Securities and Exchange Commission of using AI to generate deepfakes on social media to deceive the public that Elon Musk developed the company’s technology. Even the well-received Paris Olympics were not immune to deepfakes, with Russian Group Storm-1679 suspected of creating AI content to discredit the International Olympic Committee. As the year closed out, German citizens saw an increase in AI-based propaganda regarding the upcoming German elections in 2025, including text, images and video.

4. A growing impact of quantum computing on cybersecurity

Ray Harishankar, IBM Fellow, IBM Quantum Safe, predicted that in 2024, “harvest now, decrypt later” attacks would become more common. As the year moved forward, quantum computing became an increasingly top concern, especially the harvest-now attacks. In July, the Office of Management and Budget released the Report on Post-Quantum Cryptography, which urged organizations to prepare their systems and processes for advancements in quantum computing.

During the fall of 2024, the predictions of the quantum’s impact became even more urgent, as symmetric cryptography would be unsafe by 2029, with even asymmetric cryptography fully breakable by quantum technology by 2034.

“That does not mean, however, that the risks are five years away. The prospect of harvest-now, decrypt-later attacks is already a concern, making the post-quantum cryptography transition an urgent priority,” wrote Gartner.

 5. Recession of ransomware attacks

John Dwyer, former Head of Research at IBM X-Force, predicted we might face a ransomware recession as more companies pledged not to pay the ransom. While we wish we could declare this came true, the jury is still out, and likely, we won’t know for sure until all the data is collected from 2024.

However, Wired declared in the summer of 2024 that “ransomware showed no signs of slowing down in 2024 — despite increasing police crackdowns.” In December, Heather Wishart-Smith wrote in her Forbes article The Persistent Ransomware Threat: 2024 Trends and High-Profile Attacks about the increasing dual extortion technique of cyber criminals as an increasing trend in 2024.

All in all, the experts were largely on target with their 2024 predictions. And in the next few weeks, we will start the prediction game all over again as we wonder what’s in the cards for cybersecurity in 2025.

The post 2024 trends: Were they accurate? appeared first on Security Intelligence.

❌
❌