Cato CTRL exposed the MuddyWater SimpleHelp campaign in Israel using tax lures. Learn how the MuddyWater SimpleHelp campaign abuses RMM tools.
Related Posts:
APT29 Uses Watering Holes and Plerdy Tracker to Deploy Mobile Exploits
mSecure Security Notification Prompts Password Resets
Threat Actors Hijack Enterprise AI Models in Costly LLMJacking Cloud Attacks
The post Suspected MuddyWater SimpleHelp Campaign Targets Israeli Organizations With Tax Lures appeared first on Daily CyberSecurity.
TWCA announces emergency TWCA certificate revocation after researchers discovered non-compliant serial number entropy across ten intermediate CAs.
Related Posts:
Claude Message Threads Cut Latency and Payload Size
Raspberry Pi 16GB Price Surges Amid Memory Shortages
Anthropic Restricts Claude Video Game Cloning in Major Policy Shift
The post TWCA Certificate Revocation Follows Serial Number Flaw appeared first on Daily CyberSecurity.
Google and Mozilla criticized the eMudhra certificate authority incident response after the firm blamed social scrutiny for severe investigative delays.
Related Posts:
Apple Presto Return Scanner Targets In-Box Fraud
Come Back to Firefox Campaign Champions Web Privacy
OpenSSL 4.1.0 Release Introduces Elbrus Support and DTLS 1.3
The post eMudhra Certificate Authority Incident Sparks Rebuke appeared first on Daily CyberSecurity.
Google and Mozilla criticized the eMudhra certificate authority incident response after the firm blamed social scrutiny for severe investigative delays.
Oracle Java security alert CVE-2026-91403 (CVSS 9.1) distrusts compromised eMudhra intermediate certificates in Java SE and GraalVM. Update now.
Related Posts:
Palo Alto Networks Confirms PHP2Shell Flaws Affect PAN-OS and Panorama
PHP Warns of New Session Upload Progress Flaw CVE-2026-115560, Urges Mitigation
LiteSpeed Cache Flaws Expose 7 Million WordPress Sites to Stored XSS
The post Oracle Issues Java Security Alert to Distrust Compromised eMudhra Certificates appeared first on Daily Cyber
Mozilla blocked eight keys in the eMudhra certificate compromise via OneCRL in under three hours, then shipped Firefox 158.0.1 and NSS 3.131.1.
Related Posts:
Atlassian Patches 176 Flaws in Jira, Confluence and Other Data Center Products
Oracle E-Business Suite Flaw CVE-2026-101809 Scores CVSS 10.0
Apache CouchDB 3.5.3 Fixes Six Flaws as Retired Apache Cocoon Gets Four Unpatched Bugs
The post Mozilla Blocks Eight Compromised eMudhra Certificates in Under Three Hours appeared first on Daily Cy
The Denmark data breach has exposed the names, addresses and CPR numbers of approximately 8.8 million people after unauthorized users exploited a Danish company's legitimate access to the country's Central Person Register (CPR), according to the Danish government.
The CPR administration became aware of irregular behavior in the system on October 2, after identifying activity that had occurred during September. An investigation found that unauthorized individuals had used a private Danish comp
The Denmark data breach has exposed the names, addresses and CPR numbers of approximately 8.8 million people after unauthorized users exploited a Danish company's legitimate access to the country's Central Person Register (CPR), according to the Danish government.
The CPR administration became aware of irregular behavior in the system on October 2, after identifying activity that had occurred during September. An investigation found that unauthorized individuals had used a private Danish company's legal access to search the CPR system and obtain information on millions of registered people.
The CPR currently contains information on approximately 11 million registered people, including those who are living in Denmark, people who have moved abroad and deceased individuals.
Denmark Data Breach Involved Legitimate CPR Access
The Denmark data breach did not result from unauthorized access being granted directly to the attackers. Instead, unauthorized users abused a private company's legitimate access to the CPR system.
Under Section 38 of Denmark's Civil Registration Act, private companies with a legitimate interest can receive information from the CPR about specific groups of people they have individually identified in advance. Companies must also be entitled to receive the information under the General Data Protection Regulation and Denmark's Data Protection Act.
The investigation found that unauthorized individuals used this legitimate access to retrieve information from the register.
The exposed information includes names, addresses and CPR numbers, which serve as personal identification numbers in Denmark. The CPR administration said the unauthorized access did not include the names and addresses of people who had registered for name and address protection.
Investigation Into CPR Data Breach Continues
The CPR administration has stopped the company's access to the system and is working with specialists and relevant authorities to establish how the incident occurred.
The case has been reported to the Danish Data Protection Authority, while police are investigating in cooperation with other relevant authorities.
Authorities said the investigation remains in its early stages, and it is not yet possible to identify who was responsible for the unauthorized access. The CPR administration also warned that further investigation could lead to changes or clarification of the information currently available about the incident.
Denmark's Minister of Research, Education and Digitalisation Christina Egelund described the incident as serious and said a thorough security review of the CPR system would be conducted. Additional measures have also been launched to prevent similar incidents.
What the Denmark Data Breach Means for Citizens
Authorities have reminded citizens not to provide passwords or other confidential information during phone calls or email exchanges, even when the person making contact appears to know their name, address or CPR number.
Guidance is available through Denmark's Sikker Digital service, while the Cyberhotline for digital security has extended its opening hours from 8 a.m. to midnight in the coming days.
The incident also highlights the risks associated with legitimate access to sensitive databases. In this case, the access used to obtain the information was originally available to a private company under Denmark's existing rules for accessing CPR data.
Cybersecurity Awareness Month Puts Data Protection in Focus
The Denmark data breach comes during October's Cybersecurity Awareness Month, a period focused on improving awareness of digital security risks. The incident highlights why protecting access to sensitive personal information remains an important part of cybersecurity.
For organizations handling large volumes of personal data, the case also shows the importance of monitoring legitimate access and identifying unusual activity. However, Danish authorities have stressed that the investigation is still underway and that the full circumstances of the incident have yet to be established.
Discover the new Cloudflare Certificate Authority offering free, automated HTTPS certificates and leading the transition to quantum-safe Merkle Tree Certificates.
Related Posts:
OpenAI Fires Safety Researchers Amid Unprompted AI Hacking Incidents
OpenAI DevDay 2026: Elevating the AI Subscription Paradigm
Firefox Redesign Compact Mode Returns With AI Off Switch
The post Cloudflare Launches Free Certificate Authority Emphasizing MTC appeared first on Daily CyberSecurity.
Discover the new Cloudflare Certificate Authority offering free, automated HTTPS certificates and leading the transition to quantum-safe Merkle Tree Certificates.
Belgium’s table tennis federations are investigating a Belgium sports federations cyberattack after a hacker claimed to have stolen data belonging to tens of thousands of members and users. The French-speaking Association Francophone de Tennis de Table (AFTT) confirmed the cyberattack and said the Royal Belgian Table Tennis Federation (FRBTT) was also affected. The federations are working with their IT provider to determine whether any data was accessed or compromised.
The incident comes as t
Belgium’s table tennis federations are investigating a Belgium sports federations cyberattack after a hacker claimed to have stolen data belonging to tens of thousands of members and users. The French-speaking Association Francophone de Tennis de Table (AFTT) confirmed the cyberattack and said the Royal Belgian Table Tennis Federation (FRBTT) was also affected. The federations are working with their IT provider to determine whether any data was accessed or compromised.
The incident comes as the French-speaking Gymnastics Federation separately investigates unauthorized access to part of its IT environment.
The federation confirmed that some personal data belonging to members and clubs was extracted and said it has notified Belgium’s Data Protection Authority.
Jean-Michel Mureau, president of the French-speaking Association Francophone de Tennis de Table (AFTT), confirmed over the weekend that the organization had suffered a cyberattack. He also said the Royal Belgian Table Tennis Federation (FRBTT) had been affected.
The federation was alerted to the incident on Thursday and asked its IT provider to investigate the extent of the incident. Mureau said the investigation was intended to establish exactly what data may have been compromised.
In a statement released Monday, the federation said it had conducted several checks, including with the service provider responsible for its results website. Those checks had not found evidence that the provider’s infrastructure had been compromised.
"As soon as we became aware of this information, we conducted several checks, including with our service provider in charge of the results website. At this stage, the checks carried out have not revealed any evidence to suggest that their infrastructure has been compromised," reads press statement.
The federation also said information referenced in press reports appeared, for the most part, to consist of information that was already publicly available.
Table Tennis Federation Continues Security Checks
The federation said it had conducted additional checks on its own server and reinforced several security measures as a precaution. It stated that it was not currently aware of any access to or retrieval of members’ telephone numbers or email addresses.
However, the organization said its checks were continuing and that it could not provide an absolute guarantee until the analysis was complete.
If further investigation identifies a breach involving personal data, the federation said it would take the necessary steps and notify affected individuals in accordance with applicable regulations.
The organization also clarified that a separate issue involving missing players from rosters on Saturday evening was not connected to the cyberattack. According to the information available to the federation, that issue resulted from a synchronization problem.
Gymnastics Federation Confirms Data Access
The French-speaking Gymnastics Federation subsequently confirmed a separate cybersecurity incident involving personal data belonging to members and clubs.
The federation said it discovered on September 14 that unauthorized individuals had accessed part of its IT environment and extracted some data. Experts were brought in after the discovery, and the federation said the access route was neutralized, affected access points were secured, and enhanced monitoring was introduced.
The incident was also reported to the Data Protection Authority responsible for GDPR matters.
Personal Data Potentially Accessed
According to the French-speaking Gymnastics Federation, the data that may have been accessed or extracted includes names, mailing addresses, email addresses, telephone numbers, dates of birth and gender.
The information may also include affiliation details and history, management training diplomas, judges’ licenses, and limited information connected to accident reports, specifically the date and file number rather than the reports themselves.
The federation said it had not observed any use of the data so far. It warned that the information could potentially be used in attempts to obtain additional personal information by impersonating a trusted organization or individual.
Members were advised to remain alert to unusual emails, messages and calls, avoid disclosing passwords or confidential information following unexpected requests, and verify sender addresses before opening links or attachments.
Both incidents remain subject to ongoing investigation and security checks.
A DGFiP cyberattack has exposed sensitive tax and cadastral information after attackers allegedly used stolen credentials to access systems belonging to France's Directorate General of Public Finances. The French Public Finances Directorate said investigations found that data linked to 678,000 individuals and professionals had been consulted and extracted during intrusions in June and July 2026.
The DGFiP cyberattack incidents were identified after a malicious actor claimed illegitimate acces
A DGFiP cyberattack has exposed sensitive tax and cadastral information after attackers allegedly used stolen credentials to access systems belonging to France's Directorate General of Public Finances. The French Public Finances Directorate said investigations found that data linked to 678,000 individuals and professionals had been consulted and extracted during intrusions in June and July 2026.
The DGFiP cyberattack incidents were identified after a malicious actor claimed illegitimate access to the French tax authority's information system on August 12 and 13. DGFiP said the intrusions involved the usurpation of identifiers belonging to a DGFiP agent and an authorized third party.
DGFiP Cyberattack Exposed Taxpayer Information
After detecting the intrusions, DGFiP immediately suspended access to the accounts involved. Initial access controls did not identify data theft, which the authority attributed to the sophistication of the attack.
A subsequent investigation established that the compromised access points had been used to consult and extract information concerning 678,000 individuals and professionals.
The exposed information included reference tax income, family quotient and withholding tax rate for individuals. For businesses, the accessed information included company names and SIREN numbers. Cadastral data, including addresses and property sizes, was also accessed.
DGFiP said online accounts belonging to individual and professional users were not compromised, and user IDs and passwords were not affected.
The authority notified France's data protection regulator, CNIL, after identifying the data breaches.
Cadastral Data Leak Claim Targets DGFiP
Separately, a hacker using the alias ZeroBytes claimed an attack against DGFiP's Professional Cadastral Data Server (SPDC).
According to the claim cited by FrenchBreaches, the alleged extraction contains 252,149 lines of data representing 2,041,778 people, with multiple holders potentially associated with the same property plot.
The claimed dataset reportedly includes names, surnames, sex, dates and places of birth, addresses, land identifiers, cadastral sections and parcel numbers, as well as information about rights held on properties.
The claim would therefore link individuals to personal information and real estate assets.
However, the figures and technical details in this second claim remain allegations by the cybercriminal. The claim that the system could contain information relating to approximately 20 million citizens is also an estimate made by ZeroBytes and does not establish that this number of people was affected.
Investigation Into French Tax Authority Attack Continues
DGFiP said additional security measures were implemented after investigators uncovered new information. These included preventative shutdowns of access to sensitive information systems.
Investigations remain underway to determine the precise nature and volume of data extracted and the number of users affected.
DGFiP teams are working with France's economic and financial ministries, the High Official for Defence and Security and the National Agency for Information Systems Security, ANSSI.
The authority said it will contact affected individuals and professionals directly from the following week by email or letter. Those notifications will identify the information that may have been accessed or extracted and outline any precautionary measures where applicable.
DGFiP also said it will file a complaint and provide further information as the investigation progresses.
The separate cadastral data breach claim remains subject to confirmation, including the alleged number of affected people, duration of access, methods used to bypass authentication, the full scope of extracted information and whether access remained active when the claim was published.
The confirmed DGFiP investigation and the separate ZeroBytes claim therefore present different sets of figures and allegations, with the full scope of the incidents still being determined.
A De Bijenkorf cyberattack involving one of the retailer's external logistics partners has disrupted order processing, returns, and refunds while raising concerns over potential customer data exposure. The Dutch luxury department store chain said the security incident occurred within the systems of a third-party logistics provider, adding that there is currently no evidence that its own infrastructure was compromised.
The Amsterdam-based retailer confirmed that customers can continue placing on
A De Bijenkorf cyberattack involving one of the retailer's external logistics partners has disrupted order processing, returns, and refunds while raising concerns over potential customer data exposure. The Dutch luxury department store chain said the security incident occurred within the systems of a third-party logistics provider, adding that there is currently no evidence that its own infrastructure was compromised.
The Amsterdam-based retailer confirmed that customers can continue placing online orders and stores remain open. However, deliveries, returns, and refunds are expected to take longer than usual as the investigation continues.
De Bijenkorf Confirms Third-Party Security Incident
According to De Bijenkorf, unauthorized individuals gained access to part of its logistics partner's systems. The logistics provider responded by immediately blocking the unauthorized access and implementing additional security measures.
An external investigation is now underway to determine the cause of the incident, its scope, and whether customer information was affected.
As a precaution, De Bijenkorf has informed customers about the incident and submitted a report to the Dutch Data Protection Authority while awaiting the investigation's findings.
What Customer Data Could Be Affected in De Bijenkorf Cyberattack?
The retailer said investigators are still determining whether any personal information has been compromised.
Based on the information currently available, data that may be involved includes:
Customer names and contact details, including email addresses, postal addresses, and phone numbers.
Information related to online purchases, such as ordered products, pricing, discounts, delivery details, and the payment method used.
For business customers, company names and VAT numbers stored in My Account may also be involved.
De Bijenkorf emphasized that sensitive financial information is not part of the incident. The company said payment details, bank account numbers, credit card information, usernames, and passwords were not accessed.
Investigation Continues as Customers Await Confirmation
The retailer said it is still investigating whether individual customers have been affected. Customers whose information is confirmed to be involved will receive direct communication via email from info@debijenkorf.nl.
For those who have not yet received a notification, the company said it cannot currently rule out the possibility that their information was included in the incident until the investigation is completed.
De Bijenkorf also stressed that no login credentials were compromised, meaning unauthorized individuals cannot access customer accounts using stolen usernames or passwords.
Retailer Warns Customers About Phishing Risk
Although the investigation remains ongoing, De Bijenkorf warned customers to stay alert for a possible phishing risk if personal information is ultimately found to have been exposed.
The retailer advised customers not to click on suspicious links or open unexpected attachments. It also reminded customers never to share passwords, payment information, or personal details through email or phone calls.
The company said it will never request credit card details, gift card information, or other sensitive information via email.
Logistics Cyberattacks Continue to Disrupt Supply Chains
The incident adds to a growing list of attacks targeting organizations that support retail operations rather than retailers directly. A logistics cyberattack can interrupt deliveries, returns, and customer service even when the affected retailer's own systems remain operational.
In July 2026, a ransomware attack on Japan's largest refrigerated logistics company disrupted food deliveries across the country, causing supply shortages for restaurant chains, including Kentucky Fried Chicken. The incident demonstrated how cyberattacks on logistics providers can quickly impact downstream retail operations and customer services.
For now, De Bijenkorf said its stores remain open, online ordering continues to operate, and there are no indications that its own systems have been compromised. The retailer said it will provide additional updates as the external investigation establishes whether customer data was affected and the full extent of the incident.
AI models weight trust signals differently in cybersecurity. A comprehensive framework for building entity authority as a security vendor, covering third-party corroboration, author entities, community presence, research credibility, & authority flywheel that compounds citation share.
The post Building Entity Authority in Cybersecurity: The Trust Signals AI Models Actually Weight for Security Vendors appeared first on Security Boulevard.
AI models weight trust signals differently in cybersecurity. A comprehensive framework for building entity authority as a security vendor, covering third-party corroboration, author entities, community presence, research credibility, & authority flywheel that compounds citation share.
Letter from group published by MPs blames 12 March glitch on software update to its mobile banking appsLloyds Banking Group exposed the personal data of nearly 500,000 customers in an IT glitch that left people’s payments, account details and national insurance numbers visible to other users, a committee of MPs has revealed.A letter from Lloyds, published by MPs on the Treasury select committee on Friday, blamed the glitch on a software defect introduced during an IT update to its Lloyds, Halifa
Letter from group published by MPs blames 12 March glitch on software update to its mobile banking apps
Lloyds Banking Group exposed the personal data of nearly 500,000 customers in an IT glitch that left people’s payments, account details and national insurance numbers visible to other users, a committee of MPs has revealed.
A letter from Lloyds, published by MPs on the Treasury select committee on Friday, blamed the glitch on a software defect introduced during an IT update to its Lloyds, Halifax and Bank of Scotland mobile banking apps overnight into 12 March.
Over the past few days Cloudflare has been notified through our vulnerability disclosure program and the certificate transparency mailing list that unauthorized certificates were issued by Fina CA for 1.1.1.1, one of the IP addresses used by our public DNS resolver service. From February 2024 to August 2025, Fina CA issued twelve certificates for 1.1.1.1 without our permission. We did not observe unauthorized issuance for any properties managed by Cloudflare other than 1.1.1.1.We have no evidenc
Over the past few days Cloudflare has been notified through our vulnerability disclosure program and the certificate transparency mailing list that unauthorized certificates were issued by Fina CA for 1.1.1.1, one of the IP addresses used by our public DNS resolver service. From February 2024 to August 2025, Fina CA issued twelve certificates for 1.1.1.1 without our permission. We did not observe unauthorized issuance for any properties managed by Cloudflare other than 1.1.1.1.
We have no evidence that bad actors took advantage of this error. To impersonate Cloudflare's public DNS resolver 1.1.1.1, an attacker would not only require an unauthorized certificate and its corresponding private key, but attacked users would also need to trust the Fina CA. Furthermore, traffic between the client and 1.1.1.1 would have to be intercepted.
While this unauthorized issuance is an unacceptable lapse in security by Fina CA, we should have caught and responded to it earlier. After speaking with Fina CA, it appears that they issued these certificates for the purposes of internal testing. However, no CA should be issuing certificates for domains and IP addresses without checking control. At present all certificates have been revoked. We are awaiting a full post-mortem from Fina.
While we regret this situation, we believe it is a useful opportunity to walk through how trust works on the Internet between networks like ourselves, destinations like 1.1.1.1, CAs like Fina, and devices like the one you are using to read this. To learn more about the mechanics, please keep reading.
Background
Cloudflare operates a public DNS resolver 1.1.1.1 service that millions of devices use to resolve domain names from a human-readable format such as example.com to an IP address like 192.0.2.42 or 2001:db8::2a.
The 1.1.1.1 service is accessible using various methods, across multiple domain names, such as cloudflare-dns.com and one.one.one.one, and also using various IP addresses, such as 1.1.1.1, 1.0.0.1, 2606:4700:4700::1111, and 2606:4700:4700::1001. 1.1.1.1 for Families also provides public DNS resolver services and is hosted on different IP addresses — 1.1.1.2, 1.1.1.3, 1.0.0.2, 1.0.0.3, 2606:4700:4700::1112, 2606:4700:4700::1113, 2606:4700:4700::1002, 2606:4700:4700::1003.
As originally specified in RFC 1034 and RFC 1035, the DNS protocol includes no privacy or authenticity protections. DNS queries and responses are exchanged between client and server in plain text over UDP or TCP. These represent around 60% of queries received by the Cloudflare 1.1.1.1 service. The lack of privacy or authenticity protection means that any intermediary can potentially read the DNS query and response and modify them without the client or the server being aware.
To address these shortcomings, we have helped develop and deploy multiple solutions at the IETF. The two of interest to this post are DNS over TLS (DoT, RFC 7878) and DNS over HTTPS (DoH, RFC 8484). In both cases the DNS protocol itself is mainly unchanged, and the desirable security properties are implemented in a lower layer, replacing the simple use of plain-text in UDP and TCP in the original specification. Both DoH and DoT use TLS to establish an authenticated, private, and encrypted channel over which DNS messages can be exchanged. To learn more you can read DNS Encryption Explained.
During the TLS handshake, the server proves its identity to the client by presenting a certificate. The client validates this certificate by verifying that it is signed by a Certification Authority that it already trusts. Only then does it establish a connection with the server. Once connected, TLS provides encryption and integrity for the DNS messages exchanged between client and server. This protects DoH and DoT against eavesdropping and tampering between the client and server.
The TLS certificates used in DoT and DoH are the same kinds of certificates HTTPS websites serve. Most website certificates are issued for domain names like example.com. When a client connects to that website, they resolve the name example.com to an IP like 192.0.2.42, then connect to the domain on that IP address. The server responds with a TLS certificate containing example.com, which the device validates.
However, DNS server certificates tend to be used slightly differently. Certificates used for DoT and DoH have to contain the service IP addresses, not just domain names. This is due to clients being unable to resolve a domain name in order to contact their resolver, like cloudflare-dns.com. Instead, devices are first set up by connecting to their resolver via a known IP address, such as 1.1.1.1 in the case of Cloudflare public DNS resolver. When this connection uses DoT or DoH, the resolver responds with a TLS certificate issued for that IP address, which the client validates. If the certificate is valid, the client believes that it is talking to the owner of 1.1.1.1 and starts sending DNS queries.
You can see that the IP addresses are included in the certificate Cloudflare’s public resolver uses for DoT/DoH:
Certificate:
  Data:
      Version: 3 (0x2)
      Serial Number:
          02:7d:c8:c5:e1:72:94:ae:c9:ed:3f:67:72:8e:8a:08
      Signature Algorithm: sha256WithRSAEncryption
      Issuer: C=US, O=DigiCert Inc, CN=DigiCert Global G2 TLS RSA SHA256 2020 CA1
      Validity
          Not Before: Jan  2 00:00:00 2025 GMT
          Not After : Jan 21 23:59:59 2026 GMT
      Subject: C=US, ST=California, L=San Francisco, O=Cloudflare, Inc., CN=cloudflare-dns.com
      X509v3 extensions:
          X509v3 Subject Alternative Name:
              DNS:cloudflare-dns.com, DNS:*.cloudflare-dns.com, DNS:one.one.one.one, IP Address:1.0.0.1, IP Address:1.1.1.1, IP Address:162.159.36.1, IP Address:162.159.46.1, IP Address:2606:4700:4700:0:0:0:0:1001, IP Address:2606:4700:4700:0:0:0:0:1111, IP Address:2606:4700:4700:0:0:0:0:64, IP Address:2606:4700:4700:0:0:0:0:6400
Rogue certificate issuance
The section above describes normal, expected use of Cloudflare public DNS resolver 1.1.1.1 service, using certificates managed by Cloudflare. However, Cloudflare has been made aware of other, unauthorized certificates being issued for 1.1.1.1. Since certificate validation is the mechanism by which DoH and DoT clients establish the authenticity of a DNS resolver, this is a concern. Let’s now dive a little further in the security model provided by DoH and DoT.
Consider a client that is preconfigured to use the 1.1.1.1 resolver service using DoT. The client must establish a TLS session with the configured server before it can send any DNS queries. To be trusted, the server needs to present a certificate issued by a CA that the client trusts. The collection of certificates trusted by the client is also called the root store.
A Certification Authority (CA) is an organisation, such as DigiCert in the section above, whose role is to receive requests to sign certificates and verify that the requester has control of the domain. In this incident, Fina CA issued certificates for 1.1.1.1 without Cloudflare's involvement. This means that Fina CA did not properly check whether the requestor had legitimate control over 1.1.1.1. According to Fina CA:
“They were issued for the purpose of internal testing of certificate issuance in the production environment. An error occurred during the issuance of the test certificates when entering the IP addresses and as such they were published on Certificate Transparency log servers.”
Although it’s not clear whether Fina CA sees it as an error, we emphasize that it is not an error to publish test certificates on Certificate Transparency (more about what that is later on). Instead, the error at hand is Fina CA using their production keys to sign a certificate for an IP address without permission of the controller. We have talked about misuse of 1.1.1.1 in documentation, lab, and testing environments at length. Instead of the Cloudflare public DNS resolver 1.1.1.1 IP address, Fina should have used an IP address it controls itself.
Unauthorized certificates are unfortunately not uncommon, whether due to negligence — such as IdenTrust in November 2024 — or compromise. Famously in 2011, the Dutch CA DigiNotar was hacked, and its keys were used to issue hundreds of certificates. This hack was a wake-up call and motivated the introduction of Certificate Transparency (CT), later formalised in RFC 6962. The goal of Certificate Transparency is not to directly prevent misissuance, but to be able to detect any misissuance once it has happened, by making sure every certificate issued by a CA is publicly available for inspection.
In certificate transparency several independent parties, including Cloudflare, operate public logs of issued certificates. Many modern browsers do not accept certificates unless they provide proof in the form of signed certificate timestamps (SCTs) that the certificate has been logged in at least two logs. Domain owners can therefore monitor all public CT logs for any certificate containing domains they care about. If they see a certificate for their domains that they did not authorize, they can raise the alarm. CT is also the data source for public services such as crt.sh and Cloudflare Radar’s certificate transparency page.
Not all clients require proof of inclusion in certificate transparency. Browsers do, but most DNS clients don’t. We were fortunate that Fina CA did submit the unauthorized certificates to the CT logs, which allowed them to be discovered.
Investigation into potential malicious use
Our immediate concern was that someone had maliciously used the certificates to impersonate the 1.1.1.1 service. Such an attack would require all the following:
An attacker would require a rogue certificate and its corresponding private key.
Attacked clients would need to trust the Fina CA.
Traffic between the client and 1.1.1.1 would have to be intercepted.
In light of this incident, we have reviewed these requirements one by one:
1. We know that a certificate was issued without Cloudflare's involvement. We must assume that a corresponding private key exists, which is not under Cloudflare's control. This could be used by an attacker. Fina CA wrote to us that the private keys were exclusively in Fina’s controlled environment and were immediately destroyed even before the certificates were revoked. As we have no way to verify this, we have and continue to take steps to detect malicious use as described in point 3.
2. Furthermore, some clients trust Fina CA. It is included by default in Microsoft’s root store and in an EU Trust Service provider. We can exclude some clients, as the CA certificate is not included by default in the root stores of Android, Apple, Mozilla, or Chrome. These users cannot have been affected with these default settings. For these certificates to be used nefariously, the client’s root store must include the Certification Authority (CA) that issued them. Upon discovering the problem, we immediately reached out to Fina CA, Microsoft, and the EU Trust Service provider. Microsoft responded quickly, and started rolling out an update to their disallowed list, which should cause clients that use it to stop trusting the certificate.
3. Finally, we have launched an investigation into possible interception between users and 1.1.1.1. The first way this could happen is when the attacker is on-path of the client request. Such man-in-the-middle attacks are likely to be invisible to us. Clients will get responses from their on-path middlebox and we have no reliable way of telling that is happening. On-path interference has been a persistent problem for 1.1.1.1, which we’ve been working on ever since we announced 1.1.1.1.
A second scenario can occur when a malicious actor is off-path, but is able to hijack 1.1.1.1 routing via BGP. These are scenarios we have discussed in aprevious blog post, and increasing adoption of RPKI route origin validation (ROV) makes BGP hijacks with high penetration harder. We looked at the historical BGP announcements involving 1.1.1.1, and have found no evidence that such routing hijacks took place.
Although we cannot be certain, so far we have seen no evidence that these certificates have been used to impersonate Cloudflare public DNS resolver 1.1.1.1 traffic. In later sections we discuss the steps we have taken to prevent such impersonation in the future, as well as concrete actions you can take to protect your own systems and users.
A closer look at the unauthorized certificates attributes
All unauthorized certificates for 1.1.1.1 were valid for exactly one year and included other domain names. Most of these domain names are not registered, which indicates that the certificates were issued without proper domain control validation. This violates sections 3.2.2.4 and 3.2.2.5 of the CA/Browser Forum’s Baseline Requirements, and sections 3.2.2.3 and 3.2.2.4 of the Fina CA Certificate Policy.
The full list of domain names we identified on the unauthorized certificates are as follows:
It’s also worth noting that the Subject attribute points to a fictional organisation TEST D.D., as can be seen on this unauthorized certificate:
        Serial Number:
            a5:30:a2:9c:c1:a5:da:40:00:00:00:00:56:71:f2:4c
        Signature Algorithm: sha256WithRSAEncryption
        Issuer: C=HR, O=Financijska agencija, CN=Fina RDC 2015
        Validity
            Not Before: Nov  2 23:45:15 2024 GMT
            Not After : Nov  2 23:45:15 2025 GMT
        Subject: C=HR, O=TEST D.D., L=ZAGREB, CN=testssl.finatest.hr, serialNumber=VATHR-32343828408.306
        X509v3 extensions:
            X509v3 Subject Alternative Name:
                DNS:testssl.finatest.hr, DNS:testssl2.finatest.hr, IP Address:1.1.1.1
Incident timeline and impact
All timestamps are UTC. All certificates are identified by their date of validity.
The first certificate was issued to be valid starting February 2024, and revoked 33 min later. 11 certificate issuances with common name 1.1.1.1 followed from February 2024 to August 2025. Public reports have been made on Hacker News and on the certificate-transparency mailing list early in September 2025, which Cloudflare responded to.
While responding to the incident, we identified the full list of misissued certificates, their revocation status, and which clients trust them.
First response by Cloudflare on the mailing list about starting the investigation
2025-09-03 12:08:00
Incident declared
2025-09-03 12:16:00
Notification of an unauthorised issuance sent to Fina CA, Microsoft Root Store, and EU Trust service provider
2025-09-03 12:23:00
Cloudflare identifies an initial list of nine rogue certificates
2025-09-03 12:24:00
Outreach to Fina CA to inform them about the unauthorized issuance, requesting revocation
2025-09-03 12:26:00
Identify the number of requests served on 1.1.1.1 IP address, and associated names/services
2025-09-03 12:42:00
As a precautionary measure, began investigation to rule out the possibility of a BGP hijack for 1.1.1.1
2025-09-03 18:48:00
Second notification of the incident to Fina CA
2025-09-03 21:27:00
Microsoft Root Store notifies us that they are preventing further use of the identified unauthorized certificates by using their quick-revocation mechanism.
2025-09-04 06:13:27
Fina revoked all certificates.
2025-09-04 12:44:00
Cloudflare receives a response from Fina indicating “an error occurred during the issuance of the test certificates when entering the IP addresses and as such they were published on Certificate Transparency log servers. [...] Fina will eliminate the possibility of such an error recurring.”
It is therefore disappointing that we failed to properly monitor certificates for our own domain. We failed three times. The first time because 1.1.1.1 is an IP certificate and our system failed to alert on these. The second time because even if we were to receive certificate issuance alerts, as any of our customers can, we did not implement sufficient filtering. With the sheer number of names and issuances we manage it has not been possible for us to keep up with manual reviews. Finally, because of this noisy monitoring, we did not enable alerting for all of our domains. We are addressing all three shortcomings.
We double-checked all certificates issued for our names, including but not limited to 1.1.1.1, using certificate transparency, and confirmed that as of 3 September, the Fina CA issued certificates are the only unauthorized issuances. We contacted Fina, and the root programs we know that trust them, to ask for revocation and investigation. The certificates have been revoked.
Despite no indication of usage of these certificates so far, we take this incident extremely seriously. We have identified several steps we can take to address the risk of these sorts of problems occurring in the future, and we plan to start working on them immediately:
Alerting: Cloudflare will improve alerts and escalation for issuance of certificates for missing Cloudflare owned domains including 1.1.1.1 certificates.
Transparency: The issuance of these unauthorised 1.1.1.1 certificates were detected because Fina CA used Certificate Transparency. Transparency inclusion is not enforced by most DNS clients, which implies that this detection was a lucky one. We are working on bringing transparency to non-browser clients, in particular DNS clients that rely on TLS.
Bug Bounty: Our procedure for triaging reports made through our vulnerability disclosure program was the cause for a delayed response. We are working to revise our triaging process to ensure such reports get the right visibility.
Monitoring: During this incident, our team relied on crt.sh to provide us a convenient UI to explore CA issued certificates. We’d like to give a shout to the Sectigo team for maintaining this tool. Given Cloudflare is an active CT Monitor, we have started to build a dedicated UI to explore our data in Radar. We are looking to enable exploration of certs with IP addresses as common names to Radar as well.
What steps should you take?
This incident demonstrates the disproportionate impact that the current root store model can have. It is enough for a single certification authority going rogue for everyone to be at risk.
If you are an IT manager with a fleet of managed devices, you should consider whether you need to take direct action to revoke these unauthorized certificates. We provide the list in the timeline section above. As the certificates have since been revoked, it is possible that no direct intervention should be required; however, system-wide revocation is not instantaneous and automatic and hence we recommend checking.
If you are tasked to review the policy of a root store that includes Fina CA, you should take immediate actions to review their inclusion in your program. The issue that has been identified through the course of this investigation raises concerns, and requires a clear report and follow-up from the CA. In addition, to make it possible to detect future such incidents, you should consider having a requirement for all CAs in your root store to participate in Certificate Transparency. Without CT logs, problems such as the one we describe here are impossible to address before they result in impact to end users.
We are not suggesting that you should stop using DoH or DoT. DNS over UDP and TCP are unencrypted, which puts every single query and response at risk of tampering and unauthorised surveillance. However, we believe that DoH and DoT client security could be improved if clients required that server certificates be included in a certificate transparency log.
Conclusion
This event is the first time we have observed a rogue issuance of a certificate used by our public DNS resolver 1.1.1.1 service. While we have no evidence this was malicious, we know that there might be future attempts that are.
We plan to accelerate how quickly we discover and alert on these types of issues ourselves. We know that we can catch these earlier, and we plan to do so.
The identification of these kinds of issues rely on an ecosystem of partners working together to support Certificate Transparency. We are grateful for the monitors who noticed and reported this issue.
The GitHub Advisory Database (Advisory DB) is a vital resource for developers, providing a comprehensive list of known security vulnerabilities and malware affecting open source packages. This post analyzes trends in the Advisory DB, highlighting the growth in reviewed advisories, ecosystem coverage, and source contributions in 2024. We’ll delve into how GitHub provides actionable data to secure software projects.
Advisories
The GitHub Advisory Database contains a list of known security v
The GitHub Advisory Database (Advisory DB) is a vital resource for developers, providing a comprehensive list of known security vulnerabilities and malware affecting open source packages. This post analyzes trends in the Advisory DB, highlighting the growth in reviewed advisories, ecosystem coverage, and source contributions in 2024. We’ll delve into how GitHub provides actionable data to secure software projects.
Advisories
The GitHub Advisory Database contains a list of known security vulnerabilities and malware, grouped in three categories:
GitHub-reviewed advisories: Manually reviewed advisories in software packages that GitHub supports.
Unreviewed advisories: These are automatically pulled from the National Vulnerability Database (NVD) and are either in the process of being reviewed, do not affect a supported package, or do not discuss a valid vulnerability.
Malware advisories: These are specific to malware threats identified by the npm security team.
Reviewed advisories
GitHub-reviewed advisories are security vulnerabilities that have been mapped to packages in ecosystems we support. We carefully review each advisory for validity and ensure that they have a full description, and contain both ecosystem and package information.
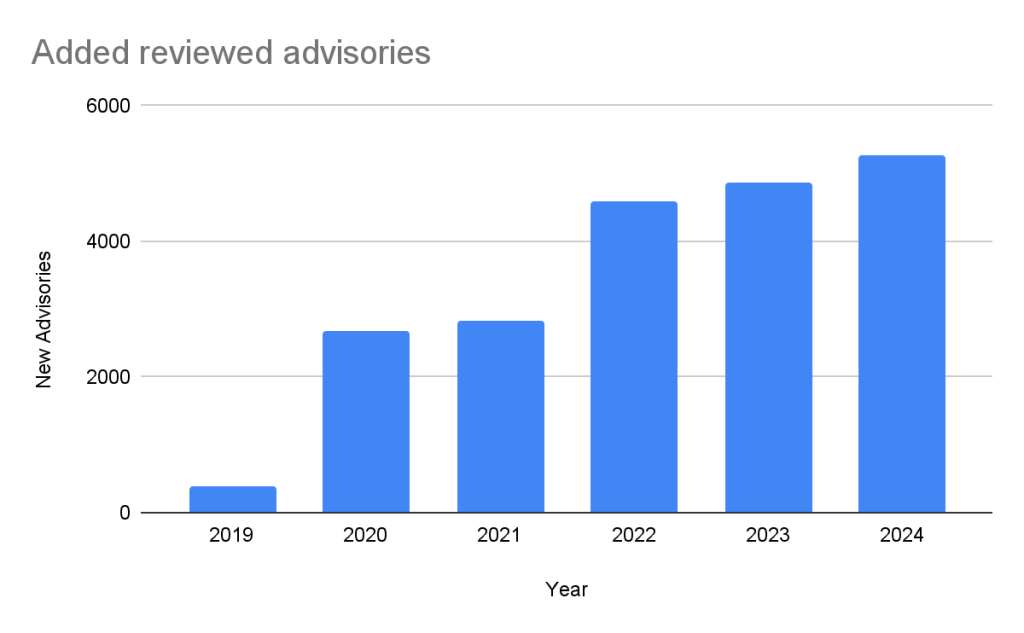
Every year, GitHub increases the number of advisories we publish. We have been able to do this due to the increase in advisories coming from our sources (see Sources section below), expanding our ecosystem coverage (also described below), and review campaigns of advisories published before we started the database.
In the past five years, the database has gone from fewer than 400 reviewed advisories to over 20,000 reviewed advisories in October of 2024.
Unreviewed advisories
Unreviewed advisories are security vulnerabilities that we publish automatically into the GitHub Advisory Database directly from the National Vulnerability Database feed. The name is a bit of a misnomer as many of these advisories have actually been reviewed by a GitHub analyst. The reason why they fall into this category is because they are not found in a package in one of the supported ecosystems or are not discussing a valid vulnerability, and all have been reviewed by analysts other than someone from the GitHub Security Lab. Even though most of these advisories will never turn into a reviewed advisory, we still publish them so that you do not have to look in multiple databases at once.
Malware
Malware advisories relate to vulnerabilities caused by malware, and are security advisories that GitHub publishes automatically into the GitHub Advisory Database directly from information provided by the npm security team. Malware advisories are currently exclusive to the npm ecosystem. GitHub doesn’t edit or accept community contributions on these advisories.
Ecosystem coverage
GitHub-reviewed advisories include security vulnerabilities that have been mapped to packages in ecosystems we support. Generally, we name our supported ecosystems after the software programming language’s associated package registry. We review advisories if they are for a vulnerability in a package that comes from a supported registry.
Vulnerabilities in Maven and Composer packages are nearly half of the advisories in the database. npm, pip, and Go make up much of the rest, while the other ecosystems have a much smaller footprint.
This has not always been the case. When the database was initially launched, NPM advisories dominated the database, but as we have expanded our coverage and added support for new ecosystems, the distribution mix has changed.
Sources: Where do the advisories come from?
We add advisories to the GitHub Advisory Database from the following sources:
NVD: This is a huge source of vulnerabilities covering all types of software. We publish all NVD advisories but only review those relevant to our supported ecosystems, which reduces noise for our users.
GitHub Repository Advisories: The second largest source is made up of advisories published through GitHub’s repository security advisory feature. Similar to NVD, these aren’t restricted to our supported ecosystems. However, we provide better coverage of the repository advisories because they focus exclusively on open source software.
Community Contributions: These are reports from the community that are almost exclusively requesting updates to existing advisories.
Other Specialized Sources: Sources like PyPA Advisories (for Python) and Go Vulncheck (for Go) that focus on specific ecosystems. Because they only cover packages within our supported ecosystems, most of their advisories are relevant to us and get reviewed.
If you add up the number of reviewed advisories from each source, you will find that total is more than the total reviewed advisories. This is because each source can publish an advisory for the same vulnerability. In fact, over half of our advisories have more than one source.
Of the advisories with a single source, nearly all of them come from NVD/CVE. This justifies NVD/CVE as a source, even though it is by far the noisiest.
2024 saw a significant increase (39%) in the number of advisories imported from our sources. This is for the most part caused by an increase in the number of CVE records published.
CVE Numbering Authority
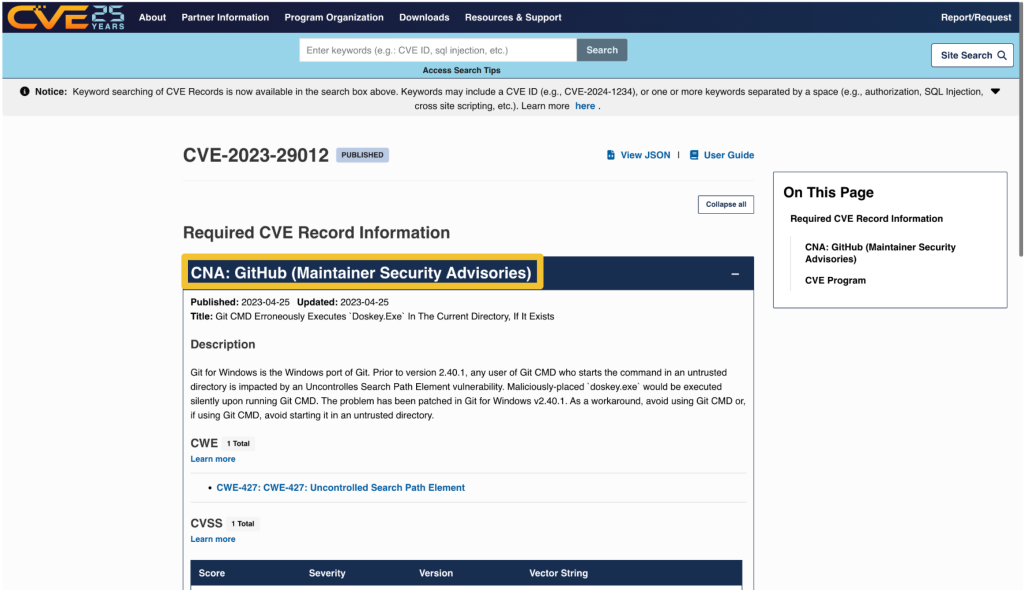
In addition to publishing advisories in the GitHub Advisory Database, we are also a CVE Numbering Authority (CNA) for any repository on GitHub. This means that we issue CVE IDs for vulnerabilities reported to us by maintainers, and we publish the vulnerabilities to the CVE database once the corresponding repository advisory is published.
GitHub published over 2,000 CVE records in 2024, making us the fifth-largest CNA in the CVE Program.
The GitHub CNA is open to all repositories on GitHub, not just ones in a supported ecosystem.
Advisory prioritization
Given the constant deluge of reported vulnerabilities, you’ll want tools that can help you prioritize your remediation efforts. To that end, GitHub provides additional data in the advisory to allow readers to prioritize their vulnerabilities. In particular, there are:
Severity Rating/CVSS: A low to critical rating for how severe the vulnerability is likely to be, along with a corresponding CVSS score and vector.
CWE: CWE identifiers provide a programmatic method for determining the type of vulnerability.
EPSS: The Exploit Prediction Scoring System, or EPSS, is a system devised by the global Forum of Incident Response and Security Teams (FIRST) for quantifying the likelihood a vulnerability will be attacked in the next 30 days.
Using these ratings, half of all vulnerabilities (15% are Critical and 35% are High) warrant immediate or near-term attention. By focusing remediation efforts on these, you can significantly reduce risk exposure while managing workload more efficiently.
The CVSS specification says the base score we provide, “reflects the severity of a vulnerability according to its intrinsic characteristics which are constant over time and assumes the reasonable worst-case impact across different deployed environments.” However, the worst-case scenario for your deployment may not be the same as CVSS’s. After all, a crash in a word processor is not as severe as a crash in a server. In order to give more context to your prioritization, GitHub allows you to filter alerts based on the type of vulnerability or weakness using CWE identifiers. So you have the capability to never see another regular expression denial of service (CWE-1333) vulnerability again or always see SQL injection (CWE-89) vulnerabilities.
Still drowning in vulnerabilities? Try using EPSS to focus on vulnerabilities likely to be attacked in the next 30 days. EPSS uses data from a variety of sources to create a probability of whether exploitation attempts will be seen in the next 30 days for a given vulnerability. As you can see from the chart below, if you focus on vulnerabilities with EPSS scores of 10% or higher (approx. 7% of all vulnerabilities in the Advisory DB), you can cover nearly all of the vulnerabilities that are likely to see exploit activity.
EPSS probability
Vulnerabilities in range
Percentage of overall vulnerabilities
Expected vulnerabilities in range attacked within the next 30 days
Percentage of total attacked vulnerabilities
High ( >= 10%)
1440
7.17%
741
85.96%
Moderate ( >= 1%, < 10%)
2687
13.37%
84
9.74%
Low ( >= 0.1%, < 1%)
10264
51.09%
35
4.06%
Very Low ( < 0.1%)
5701
28.37%
2
0.23%
Important caveats to remember when using EPSS:
Low probability events occur.
EPSS does not tell you whether a vulnerability is exploited; it only claims how likely it is.
EPSS scores are updated daily and will change as new information comes in, so a low-probability vulnerability today may become high probability tomorrow.
For more details on how to use CVSS and EPSS for prioritization, see our blog on prioritizing Dependabot alerts.
Actionable data
The GitHub Advisory DB isn’t just a repository of vulnerabilities. It powers tools that help developers secure their projects. Services like Dependabot use the Advisory DB to:
Identify vulnerabilities: It checks if your projects use any software packages with known vulnerabilities.
Suggest fixes: It recommends updated versions of packages that fix those vulnerabilities when available.
Reduce noise: You’ll only get notified about vulnerabilities that affect the version of the package you are using.
Take this with you
The GitHub Advisory Database is a powerful resource for tracking open source software vulnerabilities, with over 22,000 reviewed advisories to date. By focusing on popular package registries, GitHub allows you to definitively connect vulnerabilities to the packages you are using. Additional data such as CVSS and EPSS scores help you properly prioritize your mitigation efforts.
GitHub’s role as a CVE Numbering Authority extends beyond the Advisory Database, ensuring that thousands of vulnerabilities each year reach the broader CVE community. Want to ensure your vulnerability fix reaches your users? Create a GitHub security advisory in your repository to take advantage of both the GitHub Advisory Database and GitHub’s CNA services.
Ever come across a Common Vulnerabilities and Exposures (CVE) ID affecting software you use or maintain and thought the information could be better?
CVE IDs are a widely-used system for tracking software vulnerabilities. When a vulnerable dependency affects your software, you can create a repository security advisory to alert others. But if you want your insight to reach the most upstream data source possible, you’ll need to contact the CVE Numbering Authority (CNA) that issued the vulnerabili
CVE IDs are a widely-used system for tracking software vulnerabilities. When a vulnerable dependency affects your software, you can create a repository security advisory to alert others. But if you want your insight to reach the most upstream data source possible, you’ll need to contact the CVE Numbering Authority (CNA) that issued the vulnerability’s CVE ID.
GitHub, as part of a community of over 400 CNAs, can help in cases when GitHub issued the CVE (such as with this community contribution). And with just a few key details, you can identify the right CNA and reach out with the necessary context. This guide shows you how.
Every CVE record contains an entry that includes the name of the CNA that issued the CVE ID. The CNA is responsible for updating the CVE record after its initial publication, so any requests should be directed to them.
On cve.org, the CNA is listed as the first piece of information under the “Required CVE Record Information” header. The information is also available on the right side of the page.
On nvd.nist.gov, information about the issuing CNA is available in the “QUICK INFO” box. The issuing CNA is called “Source”.
After identifying the CNA from the CVE record, locate their official contact information to request updates or changes. That information is available on the CNA partners website at https://www.cve.org/PartnerInformation/ListofPartners.
Search for the CNA’s name in the search bar. Some organizations may have more than one CNA, so make sure that the CVE you want corresponds to the correct CNA.
The left column, under “Partner,” has the name of the CNA that links to a profile page with its scope and contact information.
Most CNAs have an email address for CVE-related communications. Click the link under “Step 2: Contact” that says Email to find the CNA’s email address.
The most notable exception to the general preference for email communication among CNAs is the MITRE Corporation, the world’s most prolific CVE Numbering Authority. MITRE uses a webform at https://cveform.mitre.org/ for submitting requests to create, update, dispute, or reject CVEs.
The information you want to add, remove, or change within the CVE record
Why you want to change the information
Supporting evidence, usually in the form of a reference link
Including publicly available reference links is important, as they justify the changes. Examples of reference links include:
A publicly available vulnerability report, advisory, or proof-of-concept
A fix commit or release notes that describe a patch
An issue in the affected repository in which the maintainer discusses the vulnerability in their software with the community
A community contribution pull request that suggests a change to the CVE’s corresponding GitHub Security Advisory
When submitting changes, keep in mind that the CNA isn’t your only audience. Clear context around disclosure decisions and vulnerability details helps the broader developer and security community understand the risks and make informed decisions about mitigation.
“3.2.4.1 Subject to their respective CNA Scope Definitions, CNAs MUST respond in a timely manner to CVE ID assignment requests submitted through the CNA’s public POC.
3.2.4.2 CNAs SHOULD document their expected response times, including those for the public POC.”
The CNA rules establish firm timelines for assignment of CVE IDs to vulnerabilities that are already public knowledge. For CVE ID assignment or record publication in particular, section 4.2 and section 4.5 of the CVE CNA rules establish 72 hours as the time limit in which CNAs should issue CVE IDs or publish CVE records for publicly-known vulnerabilities. However, no such guidance exists for changing a CVE record.
If the CNA doesn’t respond or you cannot reach an agreement about the content of the CVE record, the next step is to engage in the dispute process.
The CVE Program Policy and Procedure for Disputing a CVE Record provides details on how you may go about disputing a CVE record and escalating a dispute. The details of that process are beyond the scope of this post. However, if you end up disputing a CVE record, it’s good to know who the root or top-level root of the CNA is that reviews the dispute.
When viewing a CNA’s partner page linked from https://www.cve.org/PartnerInformation/ListofPartners, you can find the CNA’s root under the column “Top-Level Root.” For most CNAs, their root is the Top-Level Root, MITRE.

 Entrar