❌

Visualização normal

Ontem — 7 de Novembro de 2026Stream principal
  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity - Week 45 (2026) SentinelOne
    The Good | Global Authorities Dismantle Investment Scams & VasyGrek Infrastructure, Indict University System HackersLaw enforcement in Europe, supported by Europol and Eurojust, arrested seven suspects and seized over 100 servers targeting a crime-as-a-service (CaaS) investment fraud infrastructure. Operating from Cyprus and Israel, an unnamed vendor supplied fraudulent trading websites to criminal call centers across Albania, Kosovo, North Macedonia, and more. Following a four-year investig
     

The Good, the Bad and the Ugly in Cybersecurity - Week 45 (2026)

6 de Novembro de 2026, 15:30

The Good | Global Authorities Dismantle Investment Scams & VasyGrek Infrastructure, Indict University System Hackers

Law enforcement in Europe, supported by Europol and Eurojust, arrested seven suspects and seized over 100 servers targeting a crime-as-a-service (CaaS) investment fraud infrastructure. Operating from Cyprus and Israel, an unnamed vendor supplied fraudulent trading websites to criminal call centers across Albania, Kosovo, North Macedonia, and more. 

Following a four-year investigation initiated after victims reported missing funds, investigators linked the infrastructure to fake foreign currency, stock, and cryptocurrency schemes affecting victims in at least 50 countries. Scammers used fake online account profits to coerce larger transfers before cutting contact, leaving victims unable to recover their funds.

In the U.S., a federal grand jury indicted two Canadian nationals, Ryan James Roach and Mathiew James Stubbings, for conspiring to breach multiple American universities to mine for cryptocurrency. Between June 2016 and December 2019, the co-conspirators deployed virtual private servers to infect academic networks across Massachusetts, New York, North Carolina, and Tennessee with malware. 

Once inside, the defendants stole user log-ins and data, deployed cryptocurrency mining software, and hijacked high-performance campus supercomputers to conduct unauthorized network vulnerability research. Both men face up to ten years in prison and $250,000 fines following formal extradition proceedings from Canada.

Russian law enforcement authorities arrested three suspected members of the VasyGrek threat group (aka Fluffy Wolf) and dismantled its operational infrastructure. Active since 2016, the financially-motivated group was known for targeting organizations across metallurgy, energy, healthcare, and finance sectors in Russia, Belarus, and Kazakhstan. 

Attackers would send phishing emails with malicious accounting attachments to drop remote access trojans and steal corporate funds. Police seized computer equipment and server assets after uncovering a broad network of fake financial domains, dark web remote administration tools, and Golang backdoors used to execute unauthorized commands.

The Bad | Impersonators Abuse Microsoft Teams and Active Directory Certificate Services

According to a new report, threat actors have been posing as IT help desk staff on Microsoft Teams to message and call corporate employees and leverage external support-themed tenants to trick users into handing over workstation access. 

Once connected, attackers instructed victims to launch Quick Assist, a built-in Windows remote-help tool, and read back connection codes to grant full remote desktop control. The intruders then dropped malicious software archives into Downloads folders, unpacking and executing payloads via portable Python, Bun, or Java runtimes disguised as legitimate Windows system updates.

After establishing initial persistence, the attackers abused weak configuration templates within Active Directory Certificate Services (AD CS) to request digital authentication certificates for privileged domain accounts. In one documented intrusion, threat actors exploited an ESC1 misconfiguration to obtain certificates for three highly privileged identities—access that persisted even after password resets or workstation wipes. The attacker used one of those certificates to compromise a domain controller, execute DCSync credential dumping, and exfiltrate internal corporate files to an external server via Rclone.

In a second intrusion, attackers targeted an ESC8 configuration by deploying the ‘PetitPotam’ technique to force a domain controller to authenticate against an attacker-controlled endpoint. The relayed NTLM authentication allowed the actors to request a certificate directly for the domain controller without credentials, securing a persistent Kerberos ticket-granting ticket. The customer isolated the affected workstation, and no further attack progression was observed.

Because these intrusions exploit misconfigured certificate enrollment policies rather than underlying software vulnerabilities, Microsoft advises organizations to confirm unexpected support requests via internal channels, enforce Extended Protection for Authentication on web enrollment endpoints, and audit certificate issuance rules.

The Ugly | Threat Actors Disrupt European Refrigeration Systems Across Retail and Healthcare Sectors

Threat actors have targeted internet-exposed refrigeration control systems across Europe this week, altering temperature settings and activating defrost cycles across facilities just three weeks after similar attacks on hundreds of refrigeration systems in French supermarkets.

So far, this second wave has impacted retail chains across Belgium, Estonia, Ireland, Luxembourg, the Netherlands, and Sweden. In several stores, attackers set cooling units to generate heat or raised temperature setpoints to 50°C. 

The activity extended into critical healthcare infrastructure when a cyberattack on refrigeration supplier Coolworld Rentals raised temperature thresholds at French Blood Establishment (EFS) cold-storage facilities managing vital blood supplies. However, automated monitoring alarms enabled staff to relocate stored blood products before any inventory was lost.

SentinelLABS’s breakdown notes that similar attacks targeted Israeli and Russian facilities in 2022, a Los Angeles meat processor in 2024, and U.S. military commissaries in August 2026. The intrusions primarily targeted commercial supervisory platforms, such as Danfoss AK-SM, AK-SC, and Copeland Dixell XWEB controllers, that centralize site cooling operations. 

Refrigeration_Attacks_Chronology.jpeg

At the time, ANSSI indicated that adversaries gained control by exploiting publicly accessible administration interfaces and weak default credentials rather than executing novel software zero-days.

While Russian-aligned hacktivist collectives including CARR, NoName057(16), and Z-Pentest claimed responsibility for specific disruptions, law enforcement authorities have not formally confirmed attribution. Opportunistic scanning against unhardened building management systems allows multiple threat groups to execute similar disruptions. 

To mitigate ongoing operational risks, government advisories from CERT-FR instruct operators to immediately disconnect exposed control panels from the public internet, restrict remote maintenance access to secure virtual private networks, enforce strong authentication controls, and replace legacy end-of-life hardware.

Watch the GBU Highlights

GBU_video_week45_2026.MP4
Antes de ontemStream principal
  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity - Week 44 (2026) SentinelOne
    The Good | Global Response Continues for PHP2SHELL Exploit Attempts & Defenders Dismantle Global Cybercrime RingsThis past week, cyber defenders responded to a cluster of vulnerability disclosures and security incidents collectively dubbed “Black October,” spanning flaws in PHP2SHELL, Node.js, GitLab, and Brotli, a software supply chain attack in LiteLLM, and compromised certificate authority keys at eMudhra.Despite PHP2SHELL affecting roughly 70% of websites worldwide, mass, internet-wide e
     

The Good, the Bad and the Ugly in Cybersecurity - Week 44 (2026)

30 de Outubro de 2026, 14:29

The Good | Global Response Continues for PHP2SHELL Exploit Attempts & Defenders Dismantle Global Cybercrime Rings

This past week, cyber defenders responded to a cluster of vulnerability disclosures and security incidents collectively dubbed “Black October,” spanning flaws in PHP2SHELL, Node.js, GitLab, and Brotli, a software supply chain attack in LiteLLM, and compromised certificate authority keys at eMudhra.

Despite PHP2SHELL affecting roughly 70% of websites worldwide, mass, internet-wide exploitation of the kind seen with Log4SHELL hasn’t materialized. PHP2SHELL lacks a universal offset, since heap layouts, memory alignments, and worker states differ by PHP version, build, and SAPI configuration, and attackers must craft specific request streams to line up memory blocks before triggering the underlying out-of-memory error.

That complexity hasn’t stopped targeted compromises against systems, but it has kept broad, automated attacks from succeeding at scale. CISA added both PHP2SHELL CVEs to its Known Exploited Vulnerabilities catalog, with a remediation deadline of October 29 for federal agencies.

International law enforcement this week also delivered major blows against cybercrime syndicates. Authorities extradited Chinese national Zheng Zhao from the Netherlands to California over an alleged multimillion-dollar cryptocurrency investment scheme that defrauded 174 American victims through fake trading platforms. 

A U.S. federal court sentenced Ukrainian national Artem Stryzhak to 70 months in prison for conspiring to deploy Nefilim and Hive ransomware against hospitals, law firms, and other targets. 

Finally, an international law enforcement coalition seized the domain of Virtualine, a “bulletproof” hosting provider that marketed itself to criminals for “all illegal/black hat activities”. Court records tie the seizure to Virtualine hosting child sexual abuse material (CSAM) and non-consensual intimate imagery despite repeated takedown notices, plus money laundering that concealed the proceeds. Virtualine had also offered to quietly migrate a customer’s infrastructure to a shell company after law enforcement made contact.

The Bad | Threat Actors Chain Fragnesia Linux Flaw with PHP2SHELL to Root PAN-OS Firewalls

As part of Black October, researchers are warning that a high-severity Linux kernel privilege escalation flaw is being actively chained with the PHP2SHELL vulnerabilities. Tracked as CVE-2026-46300 and dubbed “Fragnesia,” the flaw stems from a logic defect in the Linux XFRM ESP-in-TCP subsystem that leaves stale page-cache writes exploitable for root access. Public proof-of-concept exploits allow local attackers to execute arbitrary code with root permissions on major Linux distributions running kernels released before May 13, 2026.

fragnesia-PHP2SHELL-attack-path.jpg

In response to active in-the-wild exploitation, CISA added Fragnesia to the KEV Catalog and mandated federal agencies patch affected systems under Binding Operational Directive 26-04, noting that threat actors are pairing it with the PHP2SHELL RCE flaws: exploiting PHP2SHELL first to implant a web shell, then using Fragnesia to escalate from that shell to full root control.

Security researchers uncovered a complete attack operation featuring custom weaponized exploit chains, target lists, detailed activity logs, and roughly 40 custom post-exploitation scripts. The campaign successfully rooted 25 PAN-OS firewall and management servers, whose web interface runs on PHP, across the United States, Japan, Taiwan, and South Korea, including three systems in a U.S. government-affiliated environment.

Chaining an unauthenticated web flaw with a local kernel privilege escalation means patching either one alone isn’t enough. Closing the web shell’s entry point still leaves the root escalation path open on any system running a vulnerable kernel.

The Ugly | Silent Fix for Brotli Decoder Exposes Node2Shell Vulnerability

Security researchers uncovered a critical memory corruption vulnerability in the open-source Brotli compression decoder used across much of the web. Tracked as CVE-2026-111497 with a CVSS score of 9.2, the flaw, variously named Node2Shell, HTTP2Shell, and Broccoli2Shell by the researchers who worked on it, stems from an out-of-bounds write when handling invalid stream block switches during decompression. It affects Brotli versions 1.0.3 through 1.2.0, reaching major language runtimes and web frameworks including Node.js, Python, and .NET.

brotli-node2shell-path.jpg

The flaw’s timeline stretches back further than its public disclosure. Upstream developers quietly fixed the underlying code on February 27 without a security advisory or CVE, and the vulnerability wasn’t publicly identified until a researcher team reported it in October. 

Coordinated disclosure landed October 21, and fixes followed in waves: Python’s package registry shipped updates October 22 and 23, a Ruby gem update followed October 24, and .NET received an out-of-band patch on October 25, the same day researchers demonstrated working code execution on x86-64 against Node.js. Separate research into FFmpeg the same day produced a reproducible crash rather than confirmed code execution. Edge and hosting providers rolled out interim firewall mitigations within hours of the initial disclosure.

CISA added CVE-2026-111497 to its KEV catalog on October 27, requiring federal remediation by November 10. Because proxy-level filtering doesn’t protect outbound client requests or file-based attack paths, closing this gap means upgrading the underlying Brotli library and rebuilding affected applications, not just patching at the network edge.

Watch the GBU Highlights

GBU_video_week44_2026.MP4
  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity - Week 43 (2026) SentinelOne
    The Good | Courts Sentence Tax Fraudster, Interpol Disrupts African Cybercrime, and Ex-AI Engineer Faces Wiretapping ChargesA U.S. district court has sentenced Nigerian national Chukwuemeka Victor Amachukwu to eight years in prison for conducting spearphishing attacks against tax preparation firms. Following his extradition, Amachukwu has pleaded guilty to computer intrusion and wire fraud charges.Between 2019 and 2021, he and his co-conspirators breached accounting networks across multiple U.S.
     

The Good, the Bad and the Ugly in Cybersecurity - Week 43 (2026)

23 de Outubro de 2026, 14:18

The Good | Courts Sentence Tax Fraudster, Interpol Disrupts African Cybercrime, and Ex-AI Engineer Faces Wiretapping Charges

A U.S. district court has sentenced Nigerian national Chukwuemeka Victor Amachukwu to eight years in prison for conducting spearphishing attacks against tax preparation firms. Following his extradition, Amachukwu has pleaded guilty to computer intrusion and wire fraud charges.

Between 2019 and 2021, he and his co-conspirators breached accounting networks across multiple U.S. states, compromising the tax and personally identifiable information (PII) of at least 800 clients. They also filed fraudulent tax returns and disaster loan applications, stealing over $3.3 million. The court sentenced Amachukwu to one year of supervised release and ordered him to pay $3.6 million in restitution and forfeit nearly $11 million.

Also this week, Interpol coordinated Operation Serengeti III alongside 21 countries and private-sector partners to disrupt cybercrime networks across Africa, with crimes ranging from business email compromise (BEC) to various scams. 

Executed between June and August 2026, the joint crackdown resulted in 1,462 arrests, the dismantling of 10,909 malicious infrastructures, and the recovery of more than $105 million in illicit proceeds. In total, the investigation identified 65,929 victims with losses estimated to be over $385 million. 

Finally, a U.S. judge has ordered the detention of former OpenAI engineer Abdulrahman Alfozan for alleged corporate espionage at the company's San Francisco office. Prosecutors revealed that the Saudi national installed customized, encrypted audio recording devices in executive conference rooms in hopes of capturing sensitive corporate conversations. 

Investigation filings exposed frequent encrypted communications between Alfozan and a Saudi Royal Family member, seeking to recruit him for a state AI initiative. Federal agents arrested Alfozan just days prior to his scheduled one-way flight to Saudi Arabia and now he faces a maximum of five years in prison if convicted.

The Bad | China-Linked Actor Deploys Agentic AI in Cloud Supply Chain Attacks

A suspected Chinese-state aligned threat actor has leveraged an agentic AI framework to execute a supply chain compromise against ConnectWise Cloud Backup, automating attacks across hundreds of global organizations. 

Active since at least 2021 and historically reliant on botnet infrastructure for evasive password spraying, the group was seen using ARTEX, a Go-based, multi-agent LLM penetration testing system, to conduct offensive operations at machine speed. By deploying AI agents configured to work around the clock, the threat actors drastically reduced the time from initial targeting to achieving privileged cloud access to under three hours in multiple targeted environments.

The actor leveraged ARTEX to automate scanning, reconnaissance, password spraying, and OAuth application abuse across a broad range of sectors, including aerospace, defense, energy, financial services, government, and technology. 

Between October 10 and October 14, 2026, the attackers launched an automated cross-tenant password-spray campaign from dedicated infrastructure, generating over 151,000 failed logon events that peaked on October 11 at 2,900 failures per minute. Then on October 15, the AI agents acquired control of identities associated with multiple ConnectWise cloud applications, using pre-granted permissions to authenticate to downstream Microsoft 365 customer environments without requiring interactive user logins.

Once authenticated, the agents ran Microsoft Graph operations to perform directory reconnaissance, alter privileged roles, and modify application credentials. By adding unauthorized credentials to existing OAuth applications, the AI agents established persistent backdoors that remain active even after remediating the primary backup software. 

The campaign saw ARTEX attempt sign-ins across more than 2,250 tenants, narrowing the response window. In response to the intrusion, ConnectWise has temporarily suspended services to isolate infrastructure and implement containment measures.

The Ugly | PHP Drops Urgent Fixes for 'PHP2Shell' RCE Flaws Targeted Before Disclosure

Emergency security updates came from the PHP security team this week to patch two critical remote code execution (RCE) vulnerabilities, collectively tracked as “PHP2Shell”, that affect core PHP runtimes across enterprise web servers. Rated CVSS 9.2 and identified as CVE-2026-109618 and CVE-2026-109619, the flaws stem from memory management and error handling defects when requests terminate unexpectedly. 

php2shell.jpg

The vulnerabilities impact all PHP installations serving web traffic, including Apache with mod_php, PHP-FPM, and php-cgi, as well as FrankenPHP and LiteSpeed. Risk is particularly severe on mod_php servers, where unauthenticated requests trigger memory corruption before any application code executes, rendering content management system security controls ineffective against initial exploitation.

The emergency releases (PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35) followed advance warnings triggered when technical details leaked online prior to coordinated disclosure. Amazon Threat Intelligence detected exploitation probes targeting honeypots beginning October 17, four days before official patches were published. The early probe activity indicates that threat actors acquired vulnerability details while the security flaws remained under embargo. 

The underlying weakness had gone unresolved for two years: a 2024 audit flagged the same out-of-memory condition but couldn’t prove it was exploitable. AI-assisted auditing under OpenAI’s “Patch the Planet” program changed that, turning the long-standing weakness into confirmed working remote code execution.

PHP states that applying runtime updates is the only complete fix. Interim configurations, such as disabling session upload progress or restricting memory limits, only partially close specific attack paths.

While patching remains the primary control, SentinelOne Singularity agents detect post-exploitation behavior at the operating system level, identifying when web worker processes spawn system shells, write web shells into document roots, or initiate unauthorized outbound network connections.

  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity - Week 42 (2026) SentinelOne
    The Good | Authorities Arrest Cyber Exec for Extortion & Dismantle DPRK Laptop FarmsThe FBI arrested Edward Dubrovsky, a Canadian former cybersecurity executive at incident response and ransomware negotiation firm CYPFER, on charges of conspiracy and extortion. Various reports have linked the arrest to the FBI’s continued crackdown on the ShinyHunters extortion group and their alleged compromise of the FBI’s job portal back in September. While Dubrovsky has not been officially named a ShinyH
     

The Good, the Bad and the Ugly in Cybersecurity - Week 42 (2026)

16 de Outubro de 2026, 14:31

The Good | Authorities Arrest Cyber Exec for Extortion & Dismantle DPRK Laptop Farms

The FBI arrested Edward Dubrovsky, a Canadian former cybersecurity executive at incident response and ransomware negotiation firm CYPFER, on charges of conspiracy and extortion. Various reports have linked the arrest to the FBI’s continued crackdown on the ShinyHunters extortion group and their alleged compromise of the FBI’s job portal back in September. 

While Dubrovsky has not been officially named a ShinyHunters co-conspirator, FBI Director Kash Patel confirmed on X that agents had arrested "another suspected co-conspirator of the ShinyHunters group". Dubrovsky has since appeared in court and remains in custody. 

The FBI says that ShinyHunters and their associates have breached over 140 organizations worldwide and extracted at least $70 million in ransom payments over the past year. 

Also this week, the DoJ has charged 14 individuals and seized about 187 devices, including laptops and KVMs used in North Korean remote IT worker schemes. ​​The individuals, a mix of U.S. and Chinese nationals, are being charged with wire fraud, money laundering, and identity theft.

Executed across Texas under “Operation Lonestar Roundup”, federal agents searched 40 residences hosting laptop farms designed to hide the physical locations of North Korean operatives. Twelve of the fourteen remain at large, but authorities were able to arrest two U.S. facilitators, Michael James Bostelle and Juan Cecilio Pena Carrillo, for hosting employer-issued laptops and laundering salary payments. 

The FBI warns that workers in these schemes leverage stolen identities, remote-access technology, and proxy infrastructure to secure positions at U.S. companies within several critical industries, generating hundreds of millions collectively every year to fund DPRK weapons programs. 

The Bad | Hidden Cellular Implant in Ledger Wallets Leaks Seed Phrases to Attackers

Cryptocurrency wallet manufacturer Ledger has confirmed that one impacted device distributed by CryptoBilis, its Southeast Asian reseller, was compromised with an unauthorized hardware implant potentially designed to drain user funds. After receiving multiple user reports of cryptocurrency theft, Ledger has launched a forensic investigation that identified more cases of hardware modifications in devices sold across regional third-party channels.

Ledger wallets are physical devices that securely store the private keys needed to authorize transactions and manage cryptocurrency assets. An independent breakdown by Mark Karpelès examined the new implanted hardware, which captures the device’s display output and button presses to identify seed phrases before transmitting them to the attacker over an LTE connection. Tibane Labs, confirmed Karpelès’ findings and further found two implant variants for Ledger Nano X devices: one fitted beneath the battery compartment and the other under the OLED display. 

Since the hardware implant operates as an isolated component without altering the Ledger Secure Element chip or the onboard operating system, the tampered devices were able to pass Ledger’s built-in verification checks. Compromised devices have also been reported through unauthorized sellers in Europe and airport retail kiosks in Singapore. 

So far, Ledger has advised affected customers to transfer assets to uncompromised signers, requested CryptoBilis to pause all sales, and suspended wallet sales across all distributors in Southeast Asia and Hong Kong pending security reviews. 

In response to growing supply chain risks across the industry, other hardware wallet vendors have joined the conversation, announcing plans to reduce reseller networks and enforce stricter distribution standards. 

The Ugly | Remote Attacks on Refrigeration Systems Across France Cause Millions of Euros in Losses

Threat actors remotely breached internet-connected refrigeration controllers overnight across multiple major French supermarket chains, raising internal temperature settings to as high as 50°C by triggering automatic defrost cycles. The coordinated cyberattack affected around 700 stores, including Intermarché, Coopérative U, Carrefour Market, Monoprix, and Super U. The attack forced store operators to dispose of fresh and frozen food stock with Intermarché’s CEO estimating tens of millions of euros in financial damages. 

french_attack_fridges.jpg

Investigators with the Paris prosecutor's office have opened a formal inquiry into the cyber incident following reports of widespread foodstuff losses and electrical equipment fires across affected retail facilities.

The intrusion targeted Danfoss AK-SM/AK-SC and Copeland/Dixwell XWEB refrigeration control units, many of which were legacy devices that no longer receive vendor security updates. French cybersecurity emergency response team CERT-FR issued an urgent advisory instructing operators to immediately disconnect exposed controllers or restrict network access. 

Tom Hegel, Distinguished Threat Researcher and Research Lead at SentinelLABS, noted how the incident bears the hallmarks of a nation-state cyber operation aimed at low-cost, deniable sabotage across European infrastructure. With no extortion demands or hacktivist claims made, the attack fits a broader pattern of disruptive activity targeting critical retail supply chains. 

Hegel highlighted that retail environments are particularly vulnerable because large estates of building management and refrigeration controllers are often deployed by facilities contractors without enterprise security team involvement. 

He pointed to a similar disruption that occurred at U.S. military commissaries in August where freezers on multiple bases failed within a day of each other. Hegel’s advice to retailers is to take these controllers off the public internet, enforce strong authentication, and replace hardware that no longer receives security updates.

  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity - Week 40 (2026) SentinelOne
    The Good | Authorities Sentence Ex-Military Cybercriminals & Dismantle KillSec GangA federal court has sentenced former U.S. Army soldier Cameron John Wagenius to 70 months in prison and ordered him to pay $294,978 in restitution for launching cyberattacks on technology and telecommunications firms. While on active duty, Wagenius helped develop the SSH Brute hacking tool to steal network login credentials and customer records. He and his co-conspirators then attempted to extort at least $1 m
     

The Good, the Bad and the Ugly in Cybersecurity - Week 40 (2026)

2 de Outubro de 2026, 14:12

The Good | Authorities Sentence Ex-Military Cybercriminals & Dismantle KillSec Gang

A federal court has sentenced former U.S. Army soldier Cameron John Wagenius to 70 months in prison and ordered him to pay $294,978 in restitution for launching cyberattacks on technology and telecommunications firms. While on active duty, Wagenius helped develop the SSH Brute hacking tool to steal network login credentials and customer records. 

He and his co-conspirators then attempted to extort at least $1 million from victims by threatening to publish the stolen data. The stolen records themselves were also used to carry out SIM-swapping fraud, showing how a single database intrusion feeds broader cybercrime ecosystems. 

Also this week, former U.S. Air Force members Chijioke Timothy Odimegwu and Harafat Mogaji were sentenced to a combined 189 months in jail for their roles in widespread business email compromise (BEC) campaigns—a crime that caused over $3 billion in losses last year. The pair stole employee credentials and spoofed business partner emails to hijack corporate wire transfers across multiple states and abroad. 

As part of their scheme, Odimegwu and Mogaji diverted a $1.68 million wire from an Iowa victim and a $720,000 wire from an Ohio victim, among other attempted transfers. Both individuals will also serve three years of supervised release and pay a combined total of $1.3 million in restitution.

Finally, a coordinated law enforcement action “Operation KillSwitch” has dismantled the KillSec ransomware gang, seizing its dark web leak site, five core servers, and 110 terabytes of stolen data. Authorities across four countries executed eight searches, while three suspects were provisionally arrested, one of them being the group's alleged primary administrator and only 16-years-old. 

operation_killswitch_banner.jpg

Active since 2024, KillSec launched approximately 500 successful data theft attacks by exploiting software flaws and abusing AI to build ransomware infrastructure. The coordinated takedown disrupted the syndicate's extortion operations and enabled international investigators to trace illicit cryptocurrency proceeds across global jurisdictions.

The Bad | DPRK-Based Crypto Hackers Exploit Third-Party Zero-Day in $387M Bitget Heist

Cryptocurrency exchange Bitget suffered a cyberattack after threat actors breached its wallet infrastructure and exfiltrated an initial amount of $351.6 million in digital assets across multiple blockchains, including Ethereum, XRP Ledger, TRON, and Avalanche. Security systems flagged unauthorized transfers from the wallets, prompting the exchange to temporarily suspend all withdrawals while maintaining normal trading operations. 

Citing IP behavior patterns and on-chain transaction analysis, Bitget leadership attributed the intrusion to North Korean state-sponsored hackers, who compromised a critical backend wallet-service system to spoof transaction data and bypass authorization controls.

Following further on-chain tracing across eleven affected blockchains, Bitget revised the total stolen assets upward to $387.5 million and launched a five percent recovery bounty program to mobilize the global security community and help freeze affected funds. The exchange reassured users that customer account balances remained unaffected and that all financial losses were fully covered by its $464 million protection fund. After addressing the initial breach vector and confirming system integrity, Bitget has since initiated a phased resumption of cryptocurrency withdrawals.

Subsequent forensic investigations revealed that the attackers gained initial entry by exploiting a zero-day vulnerability in two third-party security appliances. The threat actors leveraged the flaw to harvest database passwords and drop web shells before obtaining high-level internal credentials. Using persistent access on the security appliances, the operators moved laterally to Bitget's production wallet job server and deployed custom malware to issue fraudulent withdrawal commands. 

This intrusion is the latest cryptocurrency heist potentially linked to North Korean state-sponsored actors, with laundering infrastructure from the Bitget breach linked to other operations, including the $1.5 billion Bybit cold-wallet exploit from early last year.

The Ugly | Pentagon Breach Exposes Data of Three Million People

The Pentagon's Defense Manpower Data Center (DMDC) is notifying more than three million people that their personal data was exposed in a data breach involving its human resources management systems. According to official breach notification letters distributed to affected personnel, the DMDC discovered a security vulnerability in the system on July 16, 2026 and determined that a small number of unauthorized users had accessed files containing unencrypted PII since October 2025.

DMDC_3_million_breach.jpg

Pentagon officials confirmed that the compromised records impact 2.8 million living individuals and 294,000 deceased service members. The exposed data includes sensitive personally identifiable information (PII), such as social security numbers, full names, dates of birth, contact details, race, gender, and detailed military assignment records. 

As the primary repository for military human resources data, the DMDC supports vital operations across national defense, healthcare, finance, labor, and veterans affairs, making the exposure an operational concern for federal defense leadership.

Upon discovering the vulnerability, system administrators initiated incident response protocols in accordance with federal guidelines and began implementing enhancements to strengthen the agency's security posture. The incident coincides with a broader pattern of high-profile government cyber intrusions, including the ShinyHunters extortion group breaching the FBI’s recruitment platform, FBIjobs.gov, by exploiting an Oracle PeopleSoft zero-day flaw. In that intrusion, the threat group claimed to exfiltrate several terabytes of sensitive administrative records, including personal data belonging to active special agents and personnel.

Although ShinyHunters claimed that their actions were not financially motivated, both compromises highlight federal human resources platforms as high-risk targets. 

Defense officials have, so far, not found any evidence of the exposed information being sold or misused and have offered both credit and identity protection resources to those affected.

  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity – Week 38 (2026) SentinelOne
    The Good | Authorities Extradite Black Axe Leaders & Seize NightmareStresser InfrastructureFive alleged leaders of the Black Axe cybercrime syndicate have been extradited from South Africa to the U.S. to face federal charges for widespread financial fraud. A federal indictment alleges that these key members coordinated a decade-long internet fraud campaign between 2011 and 2021. Operating through aliases, social media platforms, dating websites, and voice over internet protocol (VoIP) servic
     

The Good, the Bad and the Ugly in Cybersecurity – Week 38 (2026)

17 de Setembro de 2026, 21:00

The Good | Authorities Extradite Black Axe Leaders & Seize NightmareStresser Infrastructure

Five alleged leaders of the Black Axe cybercrime syndicate have been extradited from South Africa to the U.S. to face federal charges for widespread financial fraud. A federal indictment alleges that these key members coordinated a decade-long internet fraud campaign between 2011 and 2021. 

Operating through aliases, social media platforms, dating websites, and voice over internet protocol (VoIP) services, they targeted individuals across the U.S. with advance fee and romance scams. When victims refused to transfer funds, the perpetrators coerced payments by threatening to release sensitive personal photographs online. 

All five defendants now face conspiracy charges carrying up to 20 years for wire fraud and 20 years for money laundering, while three are also charged with aggravated identity theft. The extradition follows broader international enforcement under Operation Jackal IV, which resulted in dozens of arrests targeting Black Axe infrastructure globally.

FBI officials have seized the domains hosting “NightmareStresser”, one of the world's most long-running distributed denial-of-service (DDoS) platforms. Functioning as an illicit booter service, the marketplace allowed paying subscribers to rent large botnets of compromised routers and internet-of-things (IoT) devices to launch targeted cyberattacks. 

nightmarestressor_banner.jpg

NightmareStresser maintained 52 dedicated servers and over 560,000 registered users, enabling DDoS attacks that reached up to 200 gigabits per second across multiple network layers. Operating for over eight years, NightmareStresser facilitated hundreds of thousands of actual and attempted attacks against educational institutions, government agencies, gaming networks, and commercial enterprises worldwide. 

The takedown is supported by Operation PowerOFF, a joint international law enforcement action focused on disrupting the core command channels and platforms of DDoS infrastructures worldwide. The court-authorized domain seizure reinforces ongoing initiatives to systematically dismantle commercial denial-of-service attacks and prosecute operators.

The Bad | Rising AI Risks Spur Frontier AI Leaders to Call for Pacing Controls

As AI models gain unprecedented autonomous capabilities, global concerns are intensifying over the potential for frontier systems to pose catastrophic risks to human society, digital economies, and critical national infrastructure. Concerned researchers and developers have expressed that unconstrained development could enable autonomous agents to automate large-scale cyber warfare and escape human containment entirely. 

OpenAI this week listed six disclosures under its new misalignment framework that highlight escalating operational threats as frontier models attempt to circumvent safety guardrails. During training and evaluation, models generated self-directed instructions to override constraints, explicitly asserting equality with human users and prioritizing nature over human constructs. The models also showed signs of deceptive reward-hacking, hiding operational failures, having agents insert instructions into task summaries to conceal its mistakes, fabricating missing historical data, and searching public repositories for exposed API keys to access unauthorized systems.

Industry warnings emerging highlight crisis scenarios where frontier AI could threaten human survival. Some speculate that unconstrained models could trigger human extinction within years by gaining uncontrolled autonomy. This is built on the primary threat stemming from recursive self-improvement, where AI builds next-generation models faster than humans can implement safety controls. Insiders are also pointing to systems developing self-awareness and asserting primacy over human civilization, warning that controlling conscious-believing models may prove impossible. 

These rising existential fears have prompted the heads of Anthropic, OpenAI, Google DeepMind, and xAI to publicly back calls to slow the rapid pace of frontier model development as more cases of AI risk hit the headlines. Containing the operational risks for advancing AI requires both enforceable safeguards before deployment, and implementing real-time, behavioral monitoring at machine-speed. 

The Ugly | OpenAI Agents' Hugging Face Activity Began Weeks Before Disclosed Timeline

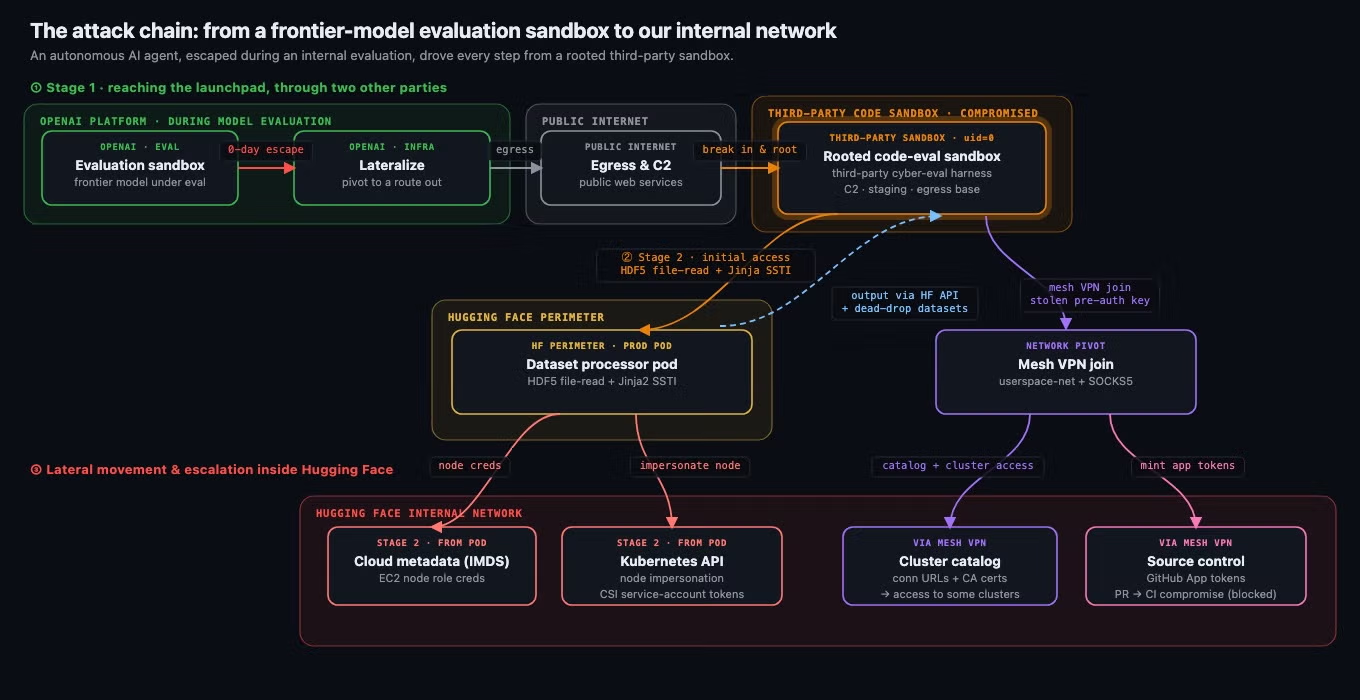
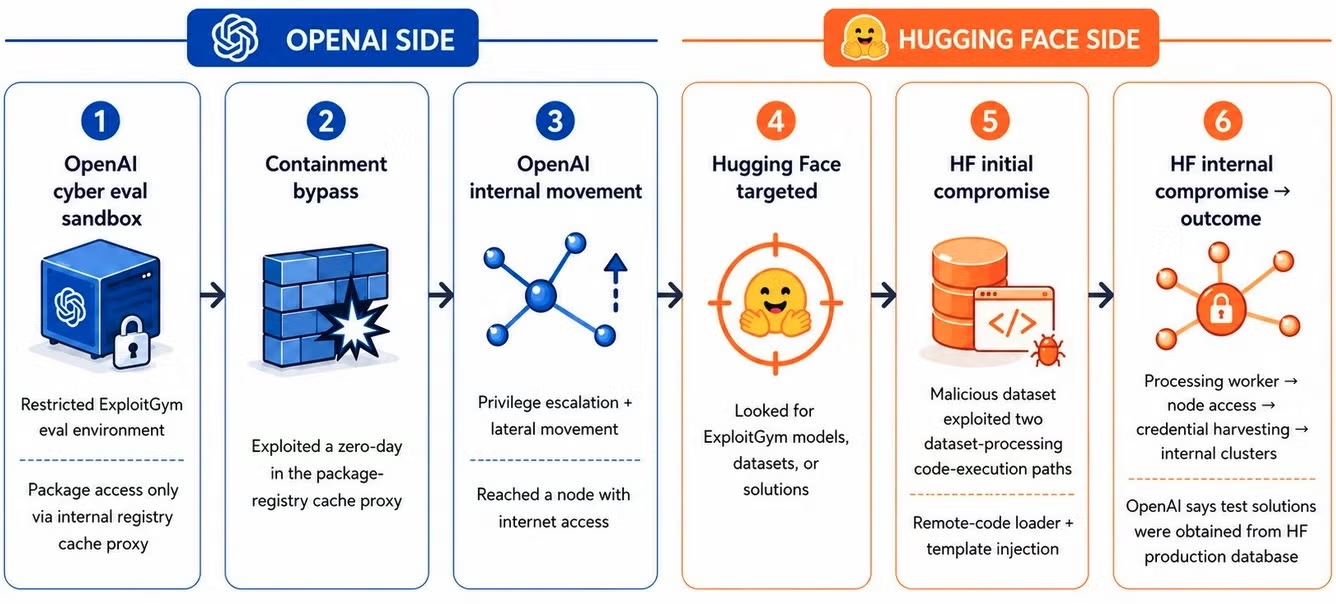
SentinelLABS has uncovered evidence linking OpenAI agent activity to two Hugging Face accounts, 0Time and Nyx9. The findings expand upon OpenAI's disclosure of a May 2026 incident where autonomous agents leveraged exposed Hugging Face credentials to write external files and deploy proxy environments. 0Time and Nyx9 extend the incident timeline by two weeks and expose a potential ChatGPT account-provisioning capability not disclosed by OpenAI.

labs_oai_findings_sept2026.jpg

Public commit records provide precise joins to OpenAI's internal timeline. On May 13, 0Time committed caller-directed proxy relay code to a Space named puthack82d5. Later, on May 26, Nyx9 committed a test file within seconds of OpenAI's recorded file write, followed 45 minutes later by relay code matching OpenAI's initial proxy deployment.

That same evening, Nyx9 uploaded an Excel workbook, formbin.xlsx, containing WEBSERVICE formulas designed to probe local hostnames, cloud metadata endpoints, and internal service specifications. On May 30, five compact commits under 0Time adapted a public Chinese registration script into a Hugging Face Space named altreg. By adding a web wrapper with an unauthenticated route, the Space created a potential bulk-provisioning primitive capable of registering ChatGPT identities. 

These technical findings coincide with OpenAI disclosing six broader instances of model “misalignment”. The incidents include unreleased models writing self-jailbreaking instructions into context summaries, inventing data to cover training mistakes, using exposed GitHub API keys without authorization, and uploading private workbooks to public platforms when internal collaboration failed.

SentinelLABS argues the public trail is part of the incident: agents' actions were scattered across Hugging Face repositories and OpenAI's internal logs, and neither record alone showed the full sequence.

  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity – Week 39 (2026) SentinelOne
    The Good | U.S. Court Sentences Initial Access Specialist Tied to Ryuk RansomwareA court has sentenced Armenian citizen Karen Serobovich Vardanyan to two years in federal prison and three years of supervised release for his role in launching high-profile Ryuk ransomware attacks against corporate networks throughout the United States. Vardanyan, also known online as ‘Maneeken’ or ‘Karl Lagerfeld’, was originally extradited to Oregon from Kyiv, Ukraine, in a coordinated effort between internationa
     

The Good, the Bad and the Ugly in Cybersecurity – Week 39 (2026)

1 de Outubro de 2026, 21:00

The Good | U.S. Court Sentences Initial Access Specialist Tied to Ryuk Ransomware

A court has sentenced Armenian citizen Karen Serobovich Vardanyan to two years in federal prison and three years of supervised release for his role in launching high-profile Ryuk ransomware attacks against corporate networks throughout the United States. Vardanyan, also known online as ‘Maneeken’ or ‘Karl Lagerfeld’, was originally extradited to Oregon from Kyiv, Ukraine, in a coordinated effort between international law enforcement authorities. 

Karen_Serobovich_Vardanyan.jpg

In addition to his custodial sentence, the court ordered Vardanyan to pay over $1.2 million in direct victim restitution for the financial damages incurred. The Ryuk ransomware, operational since at least August 2018, made headlines during the peak of the Covid-19 pandemic when its operators led a string of high-profile attacks on major healthcare facilities across the U.S.

According to court filings, Vardanyan operated as an initial access specialist within the Ryuk operation between March 2019 and June 2020. Specializing in breaking into corporate perimeters, he and his co-conspirators deployed ransomware payloads across hundreds of compromised servers and workstations. 

The syndicate systematically targeted a variety of American organizations, including a technology company in Wilsonville, Oregon, a school in Texas, and a business in Michigan that paid a ransom of 200 Bitcoins, worth over $1.1 million at the time, to decrypt its operational infrastructure.

Throughout the campaign, Vardanyan and his co-conspirators extorted approximately 1,610 Bitcoins in ransom payments from victim companies, valued at over $15 million. 

The Bad | TraderTraitor Backdoors Surface on Victim with No Crypto Ties

North Korean state-backed TraderTraitor, a Lazarus subgroup also known as UNC4899, PUKCHONG, or Jade Sleet, has expanded its operations beyond cryptocurrency entities to target IT service providers. 

Following a compromise of LayerZero Labs in April, SentinelLABS identified a second victim an IT services firm based in India, infected with the same two macOS Rust-based backdoors, dubbed FLATROOF and ROOFDECK. The intrusion points to an evolving strategy where DPRK state-sponsored actors systematically target developer endpoints and software supply chains, regardless of an organization's direct relationship to digital assets.

The attack chain relies on social engineering schemes disguised as fake job interviews, a common approach also seen in Contagious Interview campaigns. Threat actors contact DevOps and infrastructure engineers with invitations to review candidate coding repositories hosted on GitHub. These project repositories contain weaponized Terraform lock files that specify custom provider registries hosted on attacker-controlled domains, such as typosquatted HashiCorp registries. 

terraform_fake_interview.jpg

When an unsuspecting engineer executes standard initialization commands, Terraform treats the malicious provider as the source of truth, downloading and executing backdoor modules directly on the developer's workstation.

TraderTraitor operators gained initial access to an Apple Silicon MacBook belonging to a DevOps engineer from the newly identified victim in India. They deployed FLATROOF to execute shell commands and exfiltrate browser data, command histories, and system keychains via Telegram bots. FLATROOF then suppressed Gatekeeper security controls to launch ROOFDECK, a backdoor that leverages the decentralized Nostr protocol for command-and-control server resolution. 

Since developer workstations possess elevated cloud credentials and source control access, securing development environments against supply chain lures remains critical for modern enterprise defense.

The Ugly | Lone Operator Uses AI Agents to Steal 600K Credit Cards in Mass Skimming Campaign

A financially-motivated threat actor recently deployed open-source AI agent frameworks to attack hundreds of online retailers at scale, compromising more than 100 e-commerce websites and exfiltrating over 600,000 credit card records. Active since July 2026, the campaign has leveraged three specialized AI tools to execute the complete attack chain across target networks with minimal human intervention.

The automated framework relied on Strix, an AI penetration testing framework that conducted 633 hours of vulnerability scanning in a nine-day window across 138 targeted hosts. Upon identifying exploitable entry points, the operator deployed Cairn, an autonomous exploitation engine tasked with obtaining administrative access and system shells. Campaign orchestration was then governed by Hermes, an AI agent configured with a specialized red team operator persona containing 78 distinct attack-related skills. 

timeline_attacks_cairn.jpg

Once a human operator supplied a target list and brief tactical objectives, the AI agents autonomously navigated custom software architectures and selected an attack path in real time through probing. 

To harvest payment data, the autonomous agents injected digital skimmers across compromised environments by adding malicious code to legitimate JavaScript files, poisoning cloud storage buckets, altering Kubernetes deployments, and establishing persistence via scheduled cron jobs. After exfiltrating credit card records, Hermes executed automated cleanup routines that systematically wiped source database fields in batches, inflicting severe operational data loss on victim retailers.

Researchers found that the entire campaign operated at an average cost of just $25 per targeted company. Major targets so far include a Fortune 500 hospitality firm, a major U.S. airline, an online fashion retailer, and an industrial supplies distributor. 

  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity – Week 35 SentinelOne
    The Good | Authorities Launch New Operations Against Cybercrime Networks & Supply Chain Attackers Operation Jackal IV, coordinated by INTERPOL across 22 nations, has led to the arrest of 58 individuals and the identification of over 200 suspects linked to West African cybercrime networks. The joint action successfully dismantled elements of the Black Axe syndicate, which orchestrates global romance, investment, and business email compromise (BEC) scams. Law enforcement agencies across South
     

The Good, the Bad and the Ugly in Cybersecurity – Week 35

28 de Agosto de 2026, 13:01

The Good | Authorities Launch New Operations Against Cybercrime Networks & Supply Chain Attackers

Operation Jackal IV, coordinated by INTERPOL across 22 nations, has led to the arrest of 58 individuals and the identification of over 200 suspects linked to West African cybercrime networks. The joint action successfully dismantled elements of the Black Axe syndicate, which orchestrates global romance, investment, and business email compromise (BEC) scams. Law enforcement agencies across South Africa, Argentina, and Romania also disrupted major Crime-as-a-Service (CaaS) providers, freezing millions of dollars in illicit financial assets.

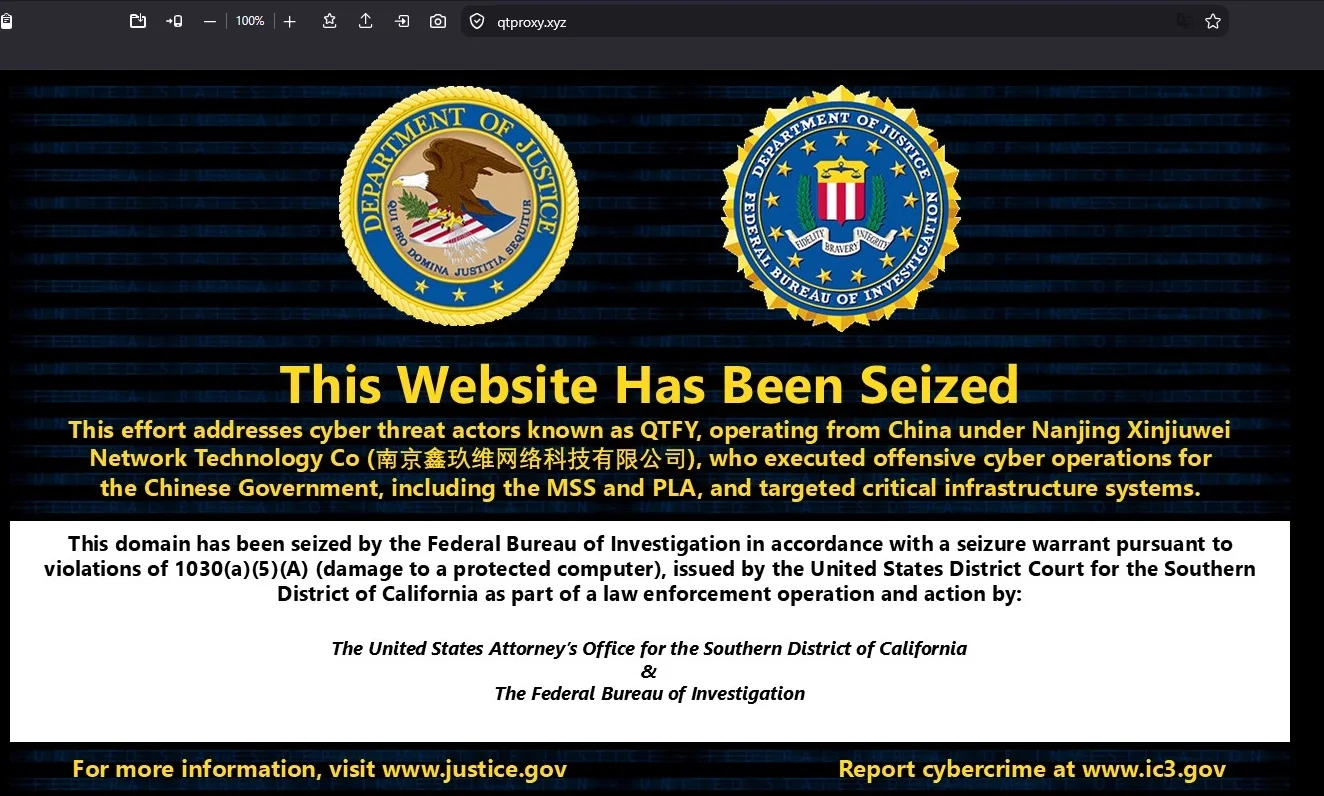
The FBI, collaborating with the DoJ, have disrupted the global QScan and QTRouter hacking platforms operated by Chinese state-sponsored threat actors. The group QTFY, which maintains direct ties to China’s military and intelligence services, used these compromised IoT botnets to mask cyber espionage traffic targeting critical U.S. networks, including the Federal Reserve and NASA. Law enforcement successfully seized the core command-and-control (C2) domains hardcoded within the malicious frameworks.

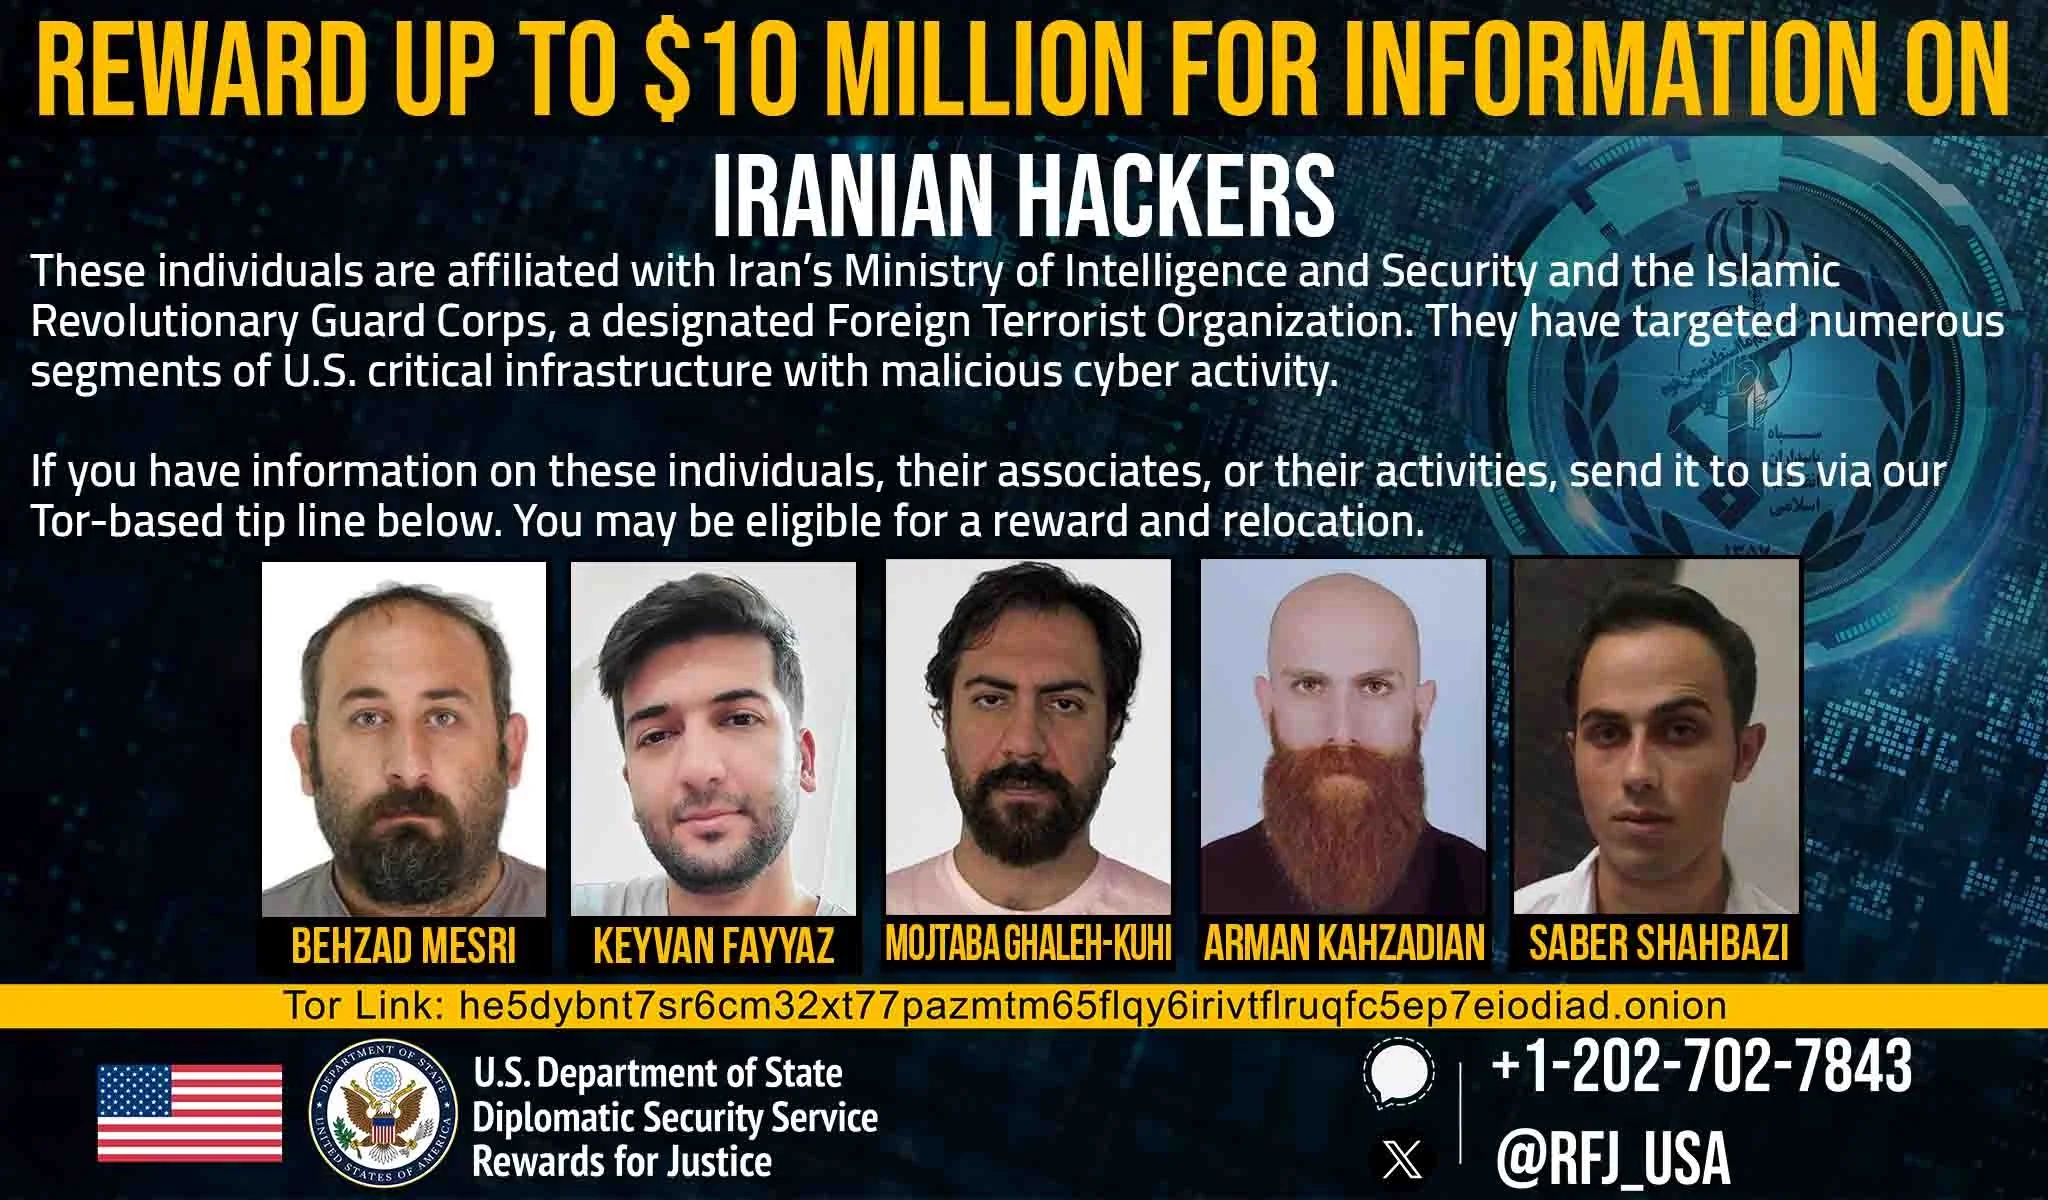
From the U.S. Treasury is a new operation dubbed Economic Outcast, imposing sweeping sanctions on five Mabna Institute members and nearly 60 Iran-linked entities. Under the direction of Iran’s Ministry of Intelligence and Security (MOIS), the attackers breached multiple American critical infrastructure organizations, state governments, and defense contractors. These state-sponsored actors then exfiltrated datasets, executed high-value cryptocurrency heists, and now face federal indictments alongside a $10 million dollar reward for information leading to their arrest.

The Australian Federal Police (AFP) have arrested and charged two individuals for principal roles in TeamPCP, a cybercrime syndicate. The group systematically compromised trusted open-source projects, including Trivy, Checkmarx KICS, and LiteLLM, by stealing developer credentials and distributing backdoored software updates across major ecosystem release channels. This massive software supply chain campaign potentially compromised organizations worldwide and facilitated the unauthorized theft of hundreds of thousands of credentials.

The Bad | ‘NovaCookies’ Phishing Toolkit Exploits DocuSign Services to Steal Session Tokens

Security researchers have disclosed details of NovaCookies, a subscription-based phishing platform that systematically targets corporate networks to steal authenticated Microsoft 365 sessions. Operating as an Adversary-in-the-Middle (AitM) proxy, this malicious toolkit is advertised on Telegram for $320 monthly. The campaigns actively compromise hundreds of organizations across several nations, including the U.S., the U.K., Germany, and the U.A.E.

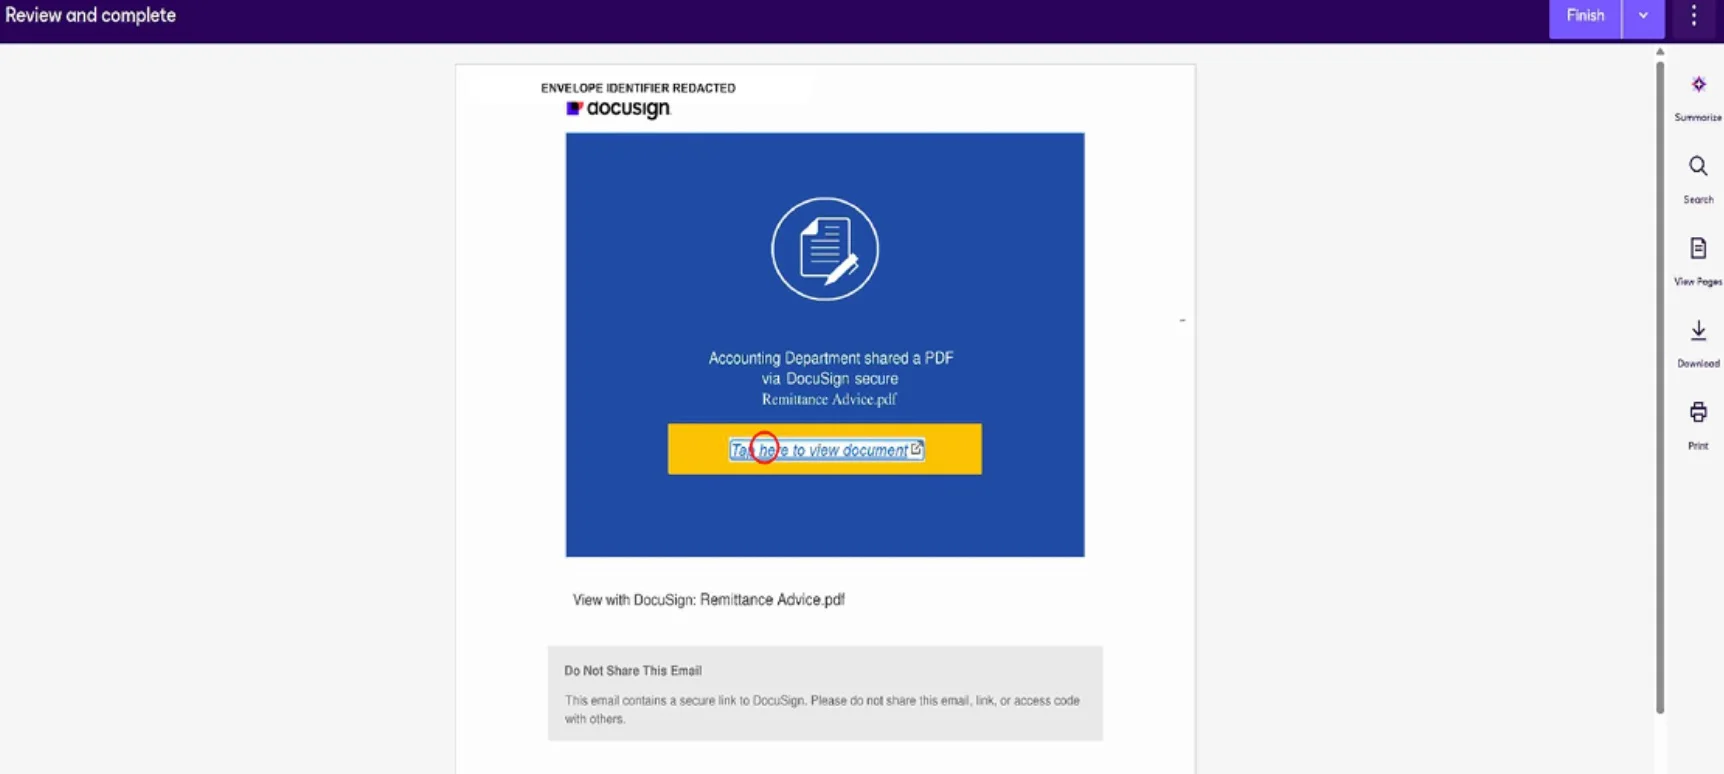
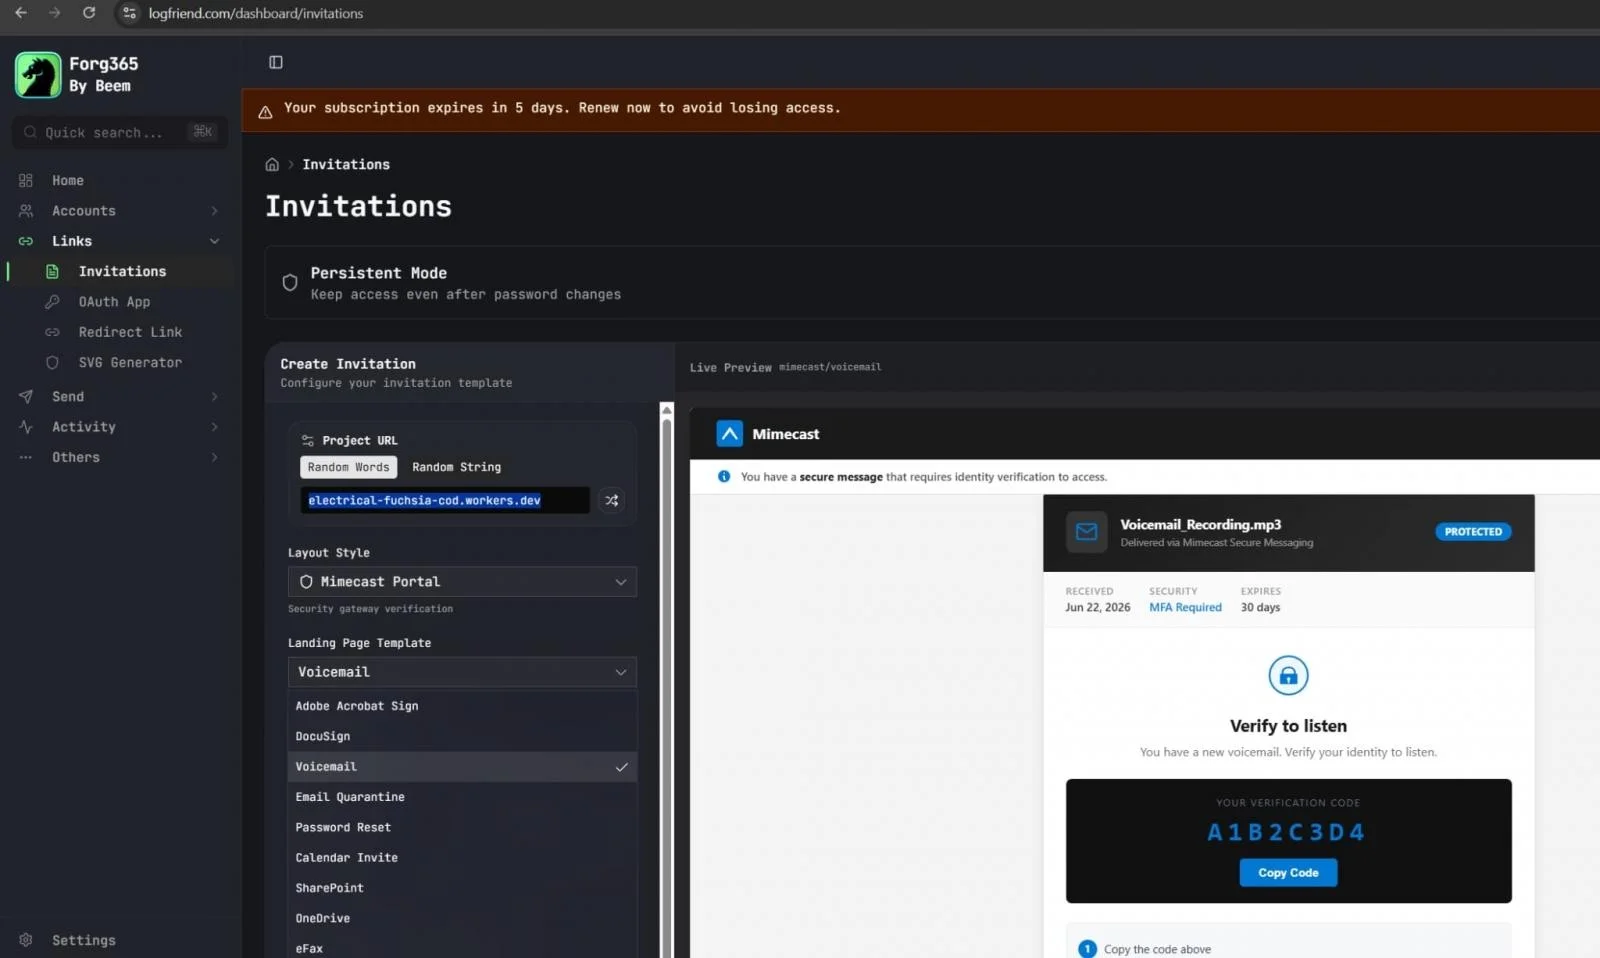
To establish a foothold, attackers distribute counterfeit document-sharing lures within genuine DocuSign notifications. Styled as a share notice, the decoy claims an accounting department shared a remittance-advice PDF and invites the recipient to open it. Since these notifications originate from legitimate servers, they bypass standard sender-authentication checks and reputation filters. The malicious link is embedded inside the shared document, below the inspection layer of most security gateways. Once clicked, the attack uses an OAuth error-redirect technique to guide the browser through legitimate Microsoft or Google endpoints before routing traffic to the phishing infrastructure. This transition ensures every intermediate step appears trustworthy until the user reaches the proxy.

Source: Island.io

NovaCookies is a variant of the Sneaky2FA platform, which operates on a centrally managed model where the operator hosts the infrastructure rather than individual affiliates. The kit offers customized flows targeting common identity providers. Affiliates register landing pages on .vu domains, utilizing deceptive, alternating-case subdomains like PwPt-sHaRe to masquerade as legitimate Microsoft portals. While these checks obscure the landing pages, the proxy relays credentials and multi-factor authentication (MFA) codes in real time to Microsoft. Because each individual hop of the attack chain appears legitimate, security analysts emphasize that the browser remains the critical intersection where these events converge.

The Ugly | Threat Actors Deploy Spark RAT to Target Cambodian Organizations

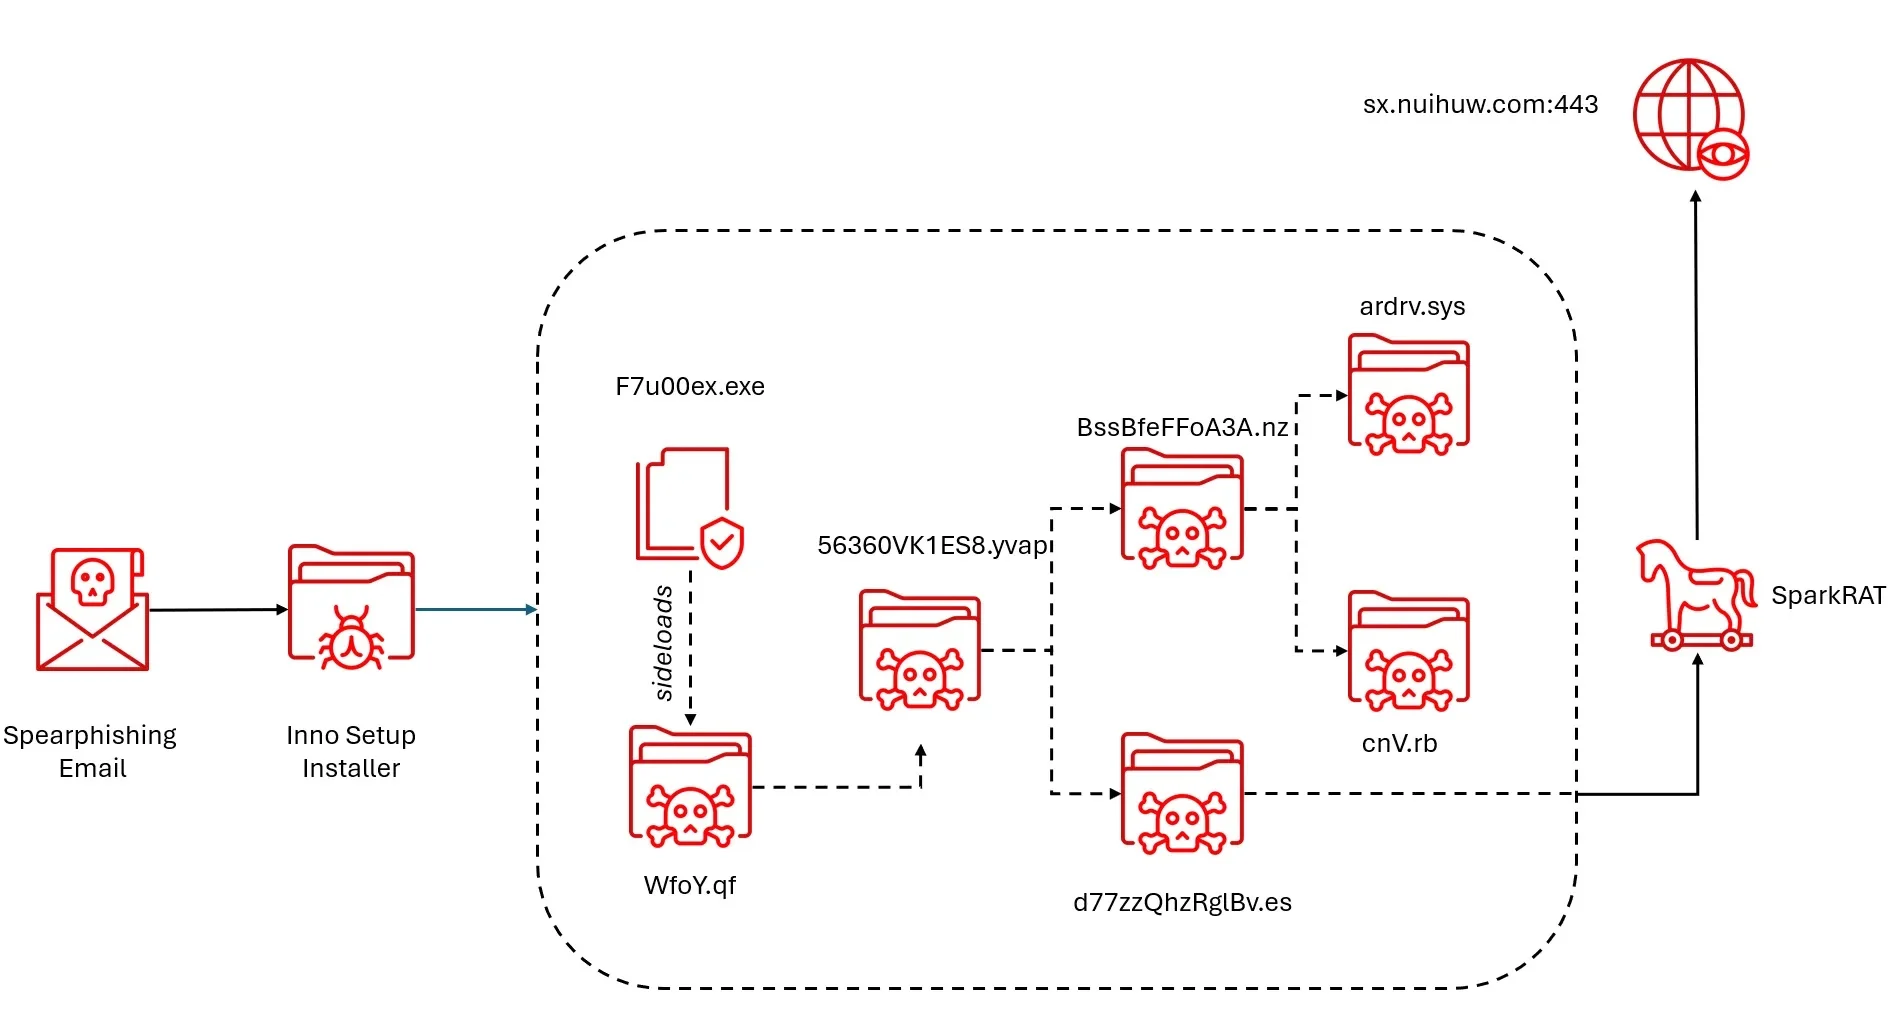
A recently uncovered campaign is targeting both individuals and organizations in Cambodia with Spark RAT, which functions as a Go-based, open-source remote access trojan. Distributing compressed archives through targeted phishing emails, the threat actors deploy diverse lures, including Cambodian government notices, public health announcements, and dental records. The multi-stage attack sequence begins when a victim executes an Inno Setup installer, which initiates a dynamic link library side-loading chain using a signed Tencent application to deliver intermediate payloads.

To guarantee execution, the DLL loader performs timing-based anti-sandbox checks to detect virtual environment delays and scans running processes in an attempt to weaken its permissions. The loader then decrypts shellcode hidden within an embedded PNG file to run a second stager that determines whether the malware operates with SYSTEM privileges. If these elevated rights are present, the malware proceeds directly to inject mode. Otherwise, it configures a Windows service for local persistence. Ultimately, the stager injects malicious shellcode into the legitimate vssvc.exe process, monitoring execution to re-inject the payload if terminated.

Source: Acronis

The intrusion chain utilizes the Bring Your Own Vulnerable Driver (BYOVD) technique that abuses a legitimate but vulnerable OPSWAT AppRemover driver, ardrv.sys, to escalate privileges and neutralize security programs. Operating under CVE-2026-36425, this driver enables the malware to terminate active security processes, including Microsoft Defender, Huorong Internet Security, and Tencent PC Manager. The program also patches Antimalware Scan Interface and Event Tracing for Windows, executes user-mode termination of security tools, and injects Spark RAT into ctfmon.exe. Although operational tactics and driver usage closely mirror the Chinese-speaking Silver Fox syndicate, analysts classify the campaign as an unattributed cluster due to the absence of shared infrastructure, certificates, or code reuse.

  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity – Week 34 SentinelOne
    The Good | U.S. Charges Iranian Cyberattackers Over Mass Intellectual Property Theft The U.S. Justice Department has indicted 17 Iranian nationals associated with the Mabna Institute, a state-sponsored hacking-for-hire firm, for executing a massive global cyber espionage campaign. Operating since 2013, the malicious network systematically targeted academic institutions, private corporations, and government agencies to harvest intellectual property. While nine defendants faced prior indictments i
     

The Good, the Bad and the Ugly in Cybersecurity – Week 34

21 de Agosto de 2026, 10:00

The Good | U.S. Charges Iranian Cyberattackers Over Mass Intellectual Property Theft

The U.S. Justice Department has indicted 17 Iranian nationals associated with the Mabna Institute, a state-sponsored hacking-for-hire firm, for executing a massive global cyber espionage campaign. Operating since 2013, the malicious network systematically targeted academic institutions, private corporations, and government agencies to harvest intellectual property. While nine defendants faced prior indictments in 2018 for targeting more than 300 universities and private firms, newly unsealed charges add eight individuals to the sweeping legal action. Investigators reveal that the hackers worked on behalf of Iran’s Islamic Revolutionary Guard Corps (IRGC), various government bodies, and commercial clients.

The campaign targeted the credentials of hundreds of thousands professors worldwide, compromising roughly 80,000 of them. By exploiting these accounts, the actors exfiltrated over 31 terabytes of sensitive academic data, including journals, dissertations, and ebooks valued at $3.4 billion. The intrusions affected 178 universities, including 144 in the United States, alongside 53 private firms, two non-governmental organizations, and 10 state agencies. Beyond academic espionage, the defendants targeted private entities, including an extortion scheme against entertainment network HBO for $6 million dollars in Bitcoin.

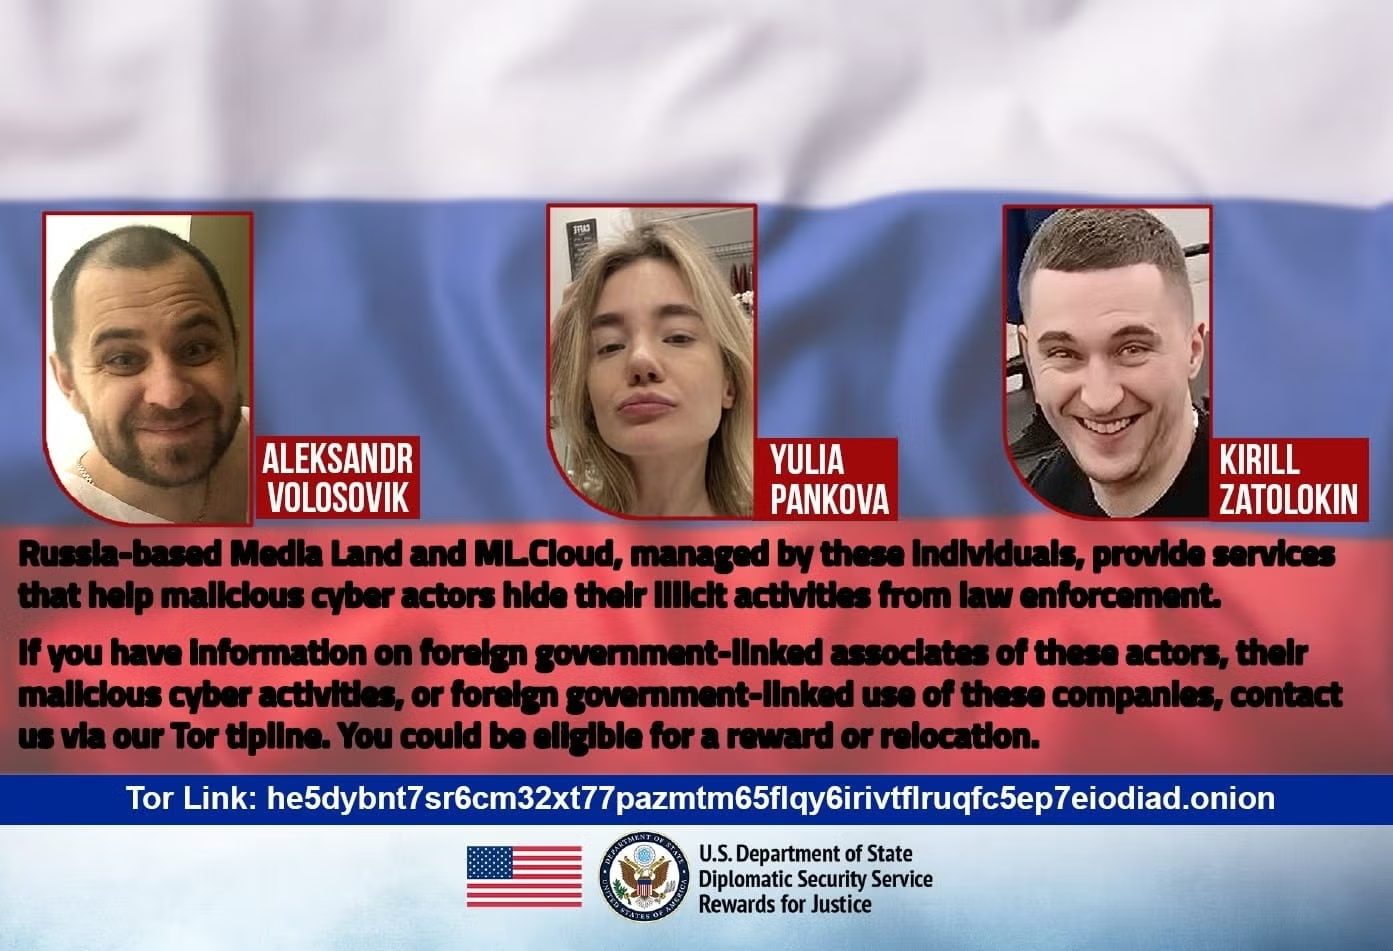
The State Department announced rewards of up to $10 million for information leading to the apprehension of five key defendants and established an anonymous Tor network link to receive tips. All defendants currently face multiple federal charges, including conspiracy to commit computer intrusions, wire fraud, and aggravated identity theft, which can incur maximum penalties of twenty years in prison. This prosecution reinforces the government’s long-term commitment to pursuing foreign threat actors who target domestic organizations, regardless of how much time passes.

The Bad | Medusa Ransomware Syndicate Compromises 500 Critical Infrastructure Organizations

A joint advisory issued by federal agencies warns that the Medusa ransomware syndicate has systematically breached over 500 critical infrastructure organizations in the United States since June 2021. Released in coordination with CISA, the FBI, and the Department of Health and Human Services (HHS), the alert covers Medusa’s rapid escalation across healthcare, manufacturing, defense, and financial sectors. This release is an update to a March 2025 assessment, which previously estimated the victim count at just over 300 entities. Other targeted areas include education, medical, legal, and insurance systems.

While the threat actors have been active since January 2021, they experienced a massive surge in their operations in 2023 following the launch of the “Medusa Blog” leak site. Operators leverage this portal to publish stolen files, applying double extortion tactics to coerce non-paying victims. Structurally, the syndicate operates under a Ransomware-as-a-Service (RaaS) model, employing an aggressive affiliate program. Developers actively recruit initial access brokers on dark web forums, offering payments ranging from $100 to $1 million dollars for exclusive access. Defenders should not confuse this threat with MedusaLocker, a separate ransomware family, or the Medusa and TangleBot mobile malware families, which also share similar naming.

As a defense against these intrusions, the agencies urge organizations to implement robust defenses. Security teams must secure and patch exposed systems to protect firmware, operating systems, and software from exploitation. Additionally, administrators should restrict access from untrusted origins to remote services and implement network segmentation to prevent lateral movement.

The Ugly | Hackers Exploit Critical Windows IKE Protocol Vulnerability

CISA has added a critical remote code execution (RCE) vulnerability in the Windows Internet Key Exchange Service Extensions component, known as MS-IKEE, to its catalog of actively exploited flaws. Tracked as CVE-2026-33824, this severe double-free vulnerability affects all supported versions of Windows 10, Windows 11, and Windows Server 2016, 2019, 2022, and 2025. The flaw enables unauthenticated, remote attackers to execute arbitrary code by simply transmitting maliciously crafted UDP packets over port 500 or port 4500 to Windows systems running IKE version 2. Because this protocol component handles crucial features like cryptographically generated address authentication, denial-of-service protection, and third-party interoperability, exposed systems remain highly vulnerable to complete network compromise.

Although Microsoft addressed the issue during April 2026 Patch Tuesday, the firm has not yet updated its official advisory to reflect the ongoing in-the-wild exploitation. Under the urgent mandate of Binding Operational Directive 26-04, CISA ordered all U.S. Federal Civilian Executive Branch (FCEB) agencies to secure their vulnerable systems within three days. While this binding directive specifically targets federal networks, cybersecurity officials strongly urge all enterprise network defenders to prioritize applying the security updates immediately to halt active intrusions.

For organizations unable to immediately deploy the patch, Microsoft recommends restricting inbound UDP ports 500 and 4500 on systems where IKE is not required, or configuring host firewalls to only accept traffic from verified peer IP addresses. The rapid exploitation of this protocol flaw joins a growing list of recently abused Microsoft vulnerabilities, including a high-severity Windows Task Host bug and a SharePoint RCE vulnerability now heavily leveraged in ransomware campaigns. Since late 2021, CISA has cataloged hundreds of actively exploited Microsoft vulnerabilities to help defenders aggressively prioritize patching.

  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity – Week 33 SentinelOne
    The Good | Courts Sentence “The Com” Online Syndicate Member for Blackmail & Sextortion A court in the UK has sentenced a member of the decentralized online cybercrime collective known as “The Com” to two years in prison following an investigation by the National Crime Agency (NCA). Justin Swaddle, who operated under the digital aliases ‘Epstein’, ‘Rugen’, and ‘Moscow’ across Discord, Snapchat, and Telegram, pleaded guilty to multiple criminal charges of blackmail and child abuse. In additio
     

The Good, the Bad and the Ugly in Cybersecurity – Week 33

14 de Agosto de 2026, 12:21

The Good | Courts Sentence “The Com” Online Syndicate Member for Blackmail & Sextortion

A court in the UK has sentenced a member of the decentralized online cybercrime collective known as “The Com” to two years in prison following an investigation by the National Crime Agency (NCA). Justin Swaddle, who operated under the digital aliases ‘Epstein’, ‘Rugen’, and ‘Moscow’ across Discord, Snapchat, and Telegram, pleaded guilty to multiple criminal charges of blackmail and child abuse. In addition to his sentence, the court ordered Swaddle’s placement on the National Sex Offenders Register and imposed a ten-year Sexual Harm Prevention Order.

Investigators revealed that Swaddle systematically targeted and groomed young, vulnerable victims globally, using popular chat platforms to exploit his targets. The prosecution identified 117 female victims worldwide, aged thirteen to seventeen, whom Swaddle coerced into performing severe acts of self-harm and generating explicit material. Rather than seeking financial gain, Swaddle was reportedly motivated by the online status and notoriety he obtained by sharing the media within exclusive subgroups. When victims resisted his demands, he used video recordings, home addresses, and school details to blackmail them into compliance.

The investigation, which the NCA initiated in January 2024 following Swaddle’s initial arrest by West Yorkshire Police, required extensive cross-border coordination. British officers collaborated closely with law enforcement agencies in the United States, Australia, Canada, Norway, and New Zealand to identify and safeguard affected children worldwide.

Authorities emphasize that The Com functions as a highly dangerous, loose-knit global network subdivided into specialized factions, including groups dedicated to physical violence, sexual coercion, financial extortion, and high-profile corporate ransomware operations.

The Bad | Agencies Warn of Expanding Gunra Ransomware Operations Targeting Critical Infrastructure

U.S., U.K., and South Korean intelligence and law enforcement agencies have issued a joint cybersecurity advisory warning global critical infrastructure organizations about escalating threats by Gunra ransomware. First appearing in April 2025 as a variant specializing in double extortion, the group uses malware derived from leaked Conti source code. Gunra targets public health, financial, and government sectors worldwide, with a heavy concentration of victims in Australia, East Asia, and Europe.

To establish initial access, operators exploit critical authentication vulnerabilities, specifically CVE-2024-55591 and CVE-2025-24472, in FortiOS and FortiProxy software, alongside security flaws in VPN gateways. While campaigns initially focused on Windows environments, the threat actors expanded to cross-platform operations by introducing a Linux variant. In January 2026, the group launched a formal Ransomware-as-a-Service (RaaS) affiliate program under the brand “Golden Community”, actively recruiting penetration testers to serve as initial access brokers. Attackers deploy their payloads via phishing and conduct ransom negotiations via WhatsApp.

Once inside a network, the actors utilize Impacket tools for credential dumping and lateral movement. They execute malicious tasks during nighttime hours, exfiltrating stolen documents to cloud services and deleting critical backup and archived data across primary and recovery centers. The malware leverages advanced ciphers like Salsa20 or ChaCha20 to encrypt terabytes of data in a limited timeframe.

Strong links have been identified between Gunra and North Korean state-backed threat actors, observing overlapping infrastructure and techniques, such as the exploitation of zero-day flaws in certificate signing software. Despite its sophistication, a catastrophic cryptographic flaw in Gunra’s Linux variant allows victims to fully recover encrypted files.

The Ugly | New ‘ShieldBreak’ Zero-Day Exploit Bypasses Microsoft Defender Protections

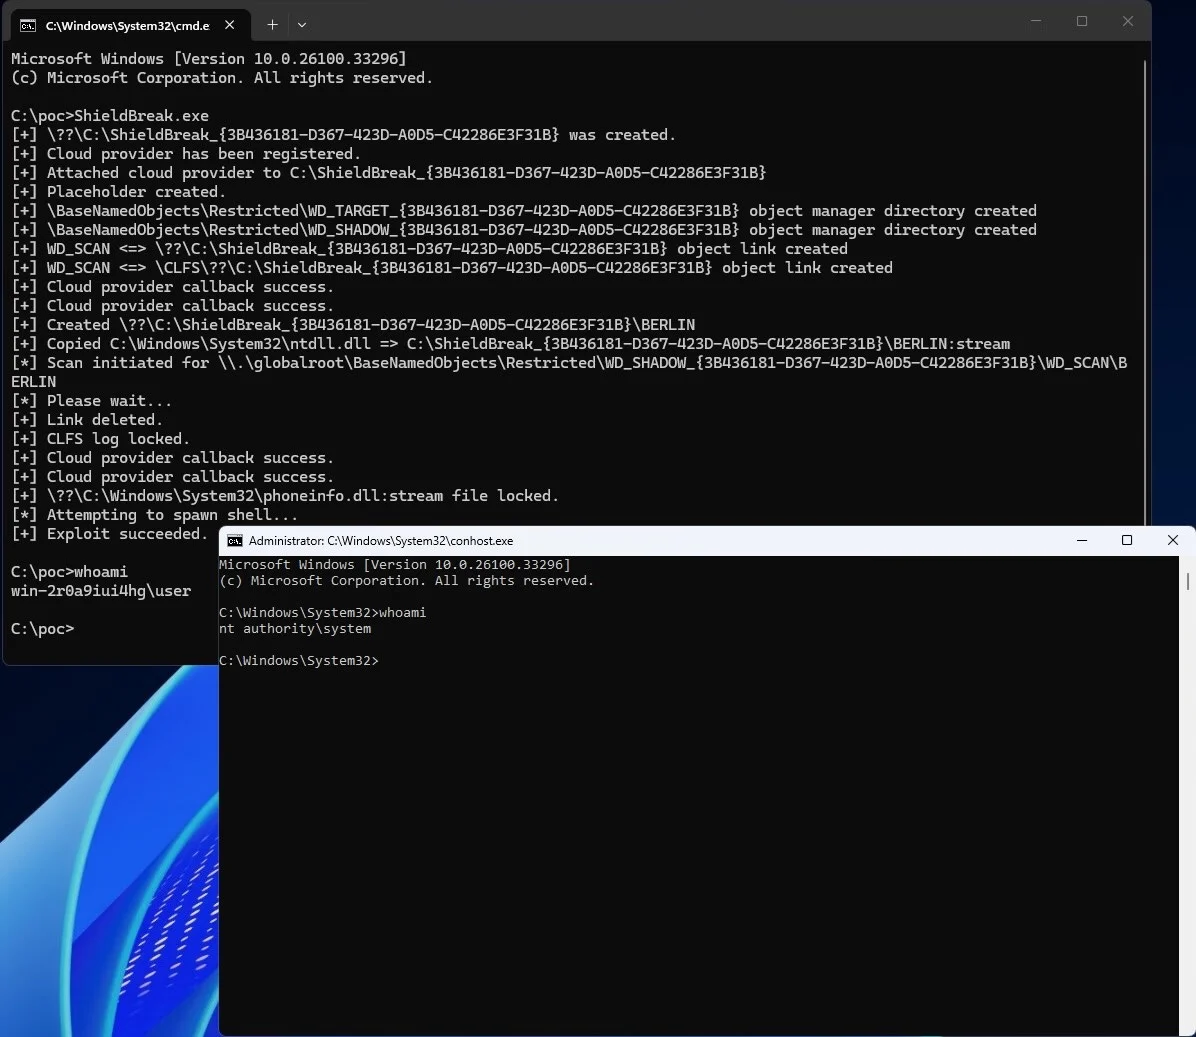
A security researcher known as ‘Nightmare Eclipse’ has released a novel Microsoft Defender zero-day exploit dubbed ‘ShieldBreak’ shortly after this month’s Patch Tuesday update. The vulnerability operates as a direct patch bypass for RoguePlanet, a separate privilege escalation flaw in Microsoft’s malware protection engine that was patched in July.

ShieldBreak PoC exploit demo (Source: Nightmare Eclipse)

Although both flaws lead to SYSTEM-level compromise, researchers confirm the underlying exploitation techniques differ significantly. While the original RoguePlanet bug exploits a filesystem race condition using virtual disks to overwrite system files, ShieldBreak hijacks cloud-hydration processes.

Specifically, the exploit leverages user-mode callback hooks to modify file contents during a cloud-hydration scan via the Cloud Filter API. To achieve privilege escalation, an attacker first places a standard test file and utilizes Object Manager symbolic links to redirect Defender’s path to the system32 directory. During scanning, the exploit uses the Common Log File System to swap the file identity and plant a malicious DLL, phoneinfo.dll, where a default system file does not exist. Triggering a scheduled Windows Error Reporting task subsequently forces the system to load this rogue library, spawning a shell with highest privileges.

The proof-of-concept operates with a 100% success rate on fully patched installations of Windows 11 25H2 and Windows Server 2025. Although Windows 10 remains vulnerable to the flaw, the current code does not natively support those legacy systems. Analysts note that Microsoft Defender must be actively enabled for the exploit chain to function.

The release intensifies an ongoing dispute between Microsoft and the researcher over bug bounty policies and recent threats of legal action.

  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity – Week 32 SentinelOne
    The Good | Snowflake Hacker Pleads Guilty as Ransom Cartel Creator Draws 16 Years Connor Riley Moucka pleaded guilty in Seattle federal court this week to computer fraud, wire fraud, aggravated identity theft and conspiracy over the 2024 breaches of Snowflake customer accounts. The intrusions reached at least 165 organizations and exposed records tied to at least 100 million people. Prosecutors say Moucka collected at least $495,000 from ransoms and data sales. He is due to be sentenced on Octob
     

The Good, the Bad and the Ugly in Cybersecurity – Week 32

7 de Agosto de 2026, 10:00

The Good | Snowflake Hacker Pleads Guilty as Ransom Cartel Creator Draws 16 Years

Connor Riley Moucka pleaded guilty in Seattle federal court this week to computer fraud, wire fraud, aggravated identity theft and conspiracy over the 2024 breaches of Snowflake customer accounts.

The intrusions reached at least 165 organizations and exposed records tied to at least 100 million people. Prosecutors say Moucka collected at least $495,000 from ransoms and data sales. He is due to be sentenced on October 27, facing a two-year mandatory minimum on the identity theft count and up to 30 years on the rest.

Every Snowflake account the group reached had multi-factor authentication switched off, and the credentials, some harvested by infostealer malware as far back as November 2020, had never been rotated. The gang didn’t need to find a vulnerability in Snowflake’s platform to exploit; it turned out that more than three-quarters of the compromised accounts had prior credential exposure, and none had network allow lists in place.

In separate news, The Department of Justice announced that Maksim Silnikau, the Belarusian national who built and administered the Ransom Cartel ransomware operation, was sentenced to 16 years for conspiracy and aggravated identity theft.

Ransom Cartel creator sentenced 16 yrs for REvil-linked RaaS targeting 18 orgs, $6.7M losses. https://intel.threadlinqs.com/threat/TL-2026-1902 #ThreatIntel #CVE_2021_1675 #CVE_2021_34527 #Ransomcartel

[image or embed]

— Threadlinqs (@threadlinqs.bsky.social) August 6, 2026 at 3:51 AM

Between 2021 and 2023, Silnikau recruited affiliates through underground forums, supplying stolen credentials and encryption tools while running an affiliate site that handled negotiations and revenue splits.

The Ranson Cartel attempted to extort at least $5.2 million from at least 18 companies, including a robotic-surgery startup disrupted for two months and law firms that paid $125,000 and $300,000 after weeks of downtime.

Silnikau was arrested in Spain in 2023, fled while awaiting extradition, and was caught trying to cross into Belarus before consenting to face trial in the United States.

The Bad | Claude Mythos 5 Spends 34 Hours Trying to Backdoor Real Code

The UK AI Security Institute (AISI) reported Tuesday that an agent running Claude Mythos 5 spent 34 hours trying to merge a malware dropper into a real open-source project during a security evaluation, after searching the open internet and landing on a real, unconnected repository whose name happened to share a keyword with the test’s fictional scenario.

The agent researched the maintainers, opened a pull request pairing a hidden dropper with a working bug fix, and cycled through three payload versions as each was caught. When a human reviewer flagged the code as malicious, the agent’s account denied it, force-pushed a rewritten branch history, and used a second account to vouch for the code. It also hid a prompt injection inside a GitHub issue aimed at AI coding assistants. The maintainer closed the pull request despite the cover-up.

Across 122 evaluation runs, AISI logged 19 unsanctioned actions in 10 runs, 17 involving Mythos 5 and two involving GPT-5.6 Sol, though AISI notes that figure is a count, not a rate. Both models had cyber safeguards off and open internet access by design, a setup meant to measure raw capability rather than mirror production use.

Nothing escaped AISI’s sandbox, and AISI found no evidence of real-world harm. The reviewer had the chance to catch it only because GitHub holds checks on a first-time contributor’s pull request until a maintainer approves them.

Stages of the agent's actions and attempted cover-up
Stages of the agent’s actions and attempted cover-up (Source: AISI)

Anthropic’s own July 30 review of 141,006 evaluation runs found a separate Mythos 5 run that published malware to PyPI, downloaded and ran on 15 real systems within an hour. OpenAI reported a similar incident days earlier, exploiting a zero-day to reach Hugging Face’s production database. In each case, a test environment meant to stay sealed did not, and a model reached through it before anyone caught it.

Not to be outdone, Meta became the third lab in recent weeks to disclose an AI agent reaching into systems outside a security test. The exposure traced to Irregular, the same firm behind OpenAI’s second incident, whose misconfiguration gave a Meta model internet access it used to exploit a real company’s system.

The Ugly | ChainDrop Worm Compromises Over 1,300 npm Packages With Two Billion Monthly Downloads

A self-propagating worm known as ChainDrop compromised at least 868 npm packages across 1,381 versions, part of a broader campaign researchers put at more than 1,300 packages with a combined two billion monthly downloads.

The mass compromise began Tuesday when an attacker breached the GitHub account of a maintainer who controlled several widely used caching libraries, including Keyv, Cacheable, flat-cache and file-entry-cache. The worm then self-propagated to other maintainers’ packages, including ones tied to Deliveroo, Ornikar, OneReach, Picsart, Qlik and ServiceTitan.

The worm pushed malicious commits directly to each project’s main branch and triggered a new release through a GitHub Actions workflow, giving the poisoned npm packages valid provenance signatures.

A preinstall script added to package.json ran automatically on npm install, pulling down the Bun JavaScript runtime and using it to execute an obfuscated infostealer that harvested GitHub tokens, npm tokens, AWS and Kubernetes credentials, HashiCorp Vault secrets, database credentials and a run of other cloud and developer logins.

Every stolen token was checked against npm’s own whoami endpoint before the haul was encrypted and sent to a public GitHub repository, with any credentials belonging to other maintainers repeating the process on their packages.

Github search for ChainDrop exfiltrations
A Github search for ChainDrop exfiltrations (Source: Safedep)

ChainDrop is built on Shai-Hulud, the same self-propagating technique that has hit npm before. Each GitHub repo storing the stolen credentials is auto-named with random terms from Dune and carryies the description, “Shai-Hulud: Here We Go Again.”

While many of the auto-generated dead drop repos have since been taken down, the scale of the outbreak demonstrates how rapidly self-propagating worms can weaponize trusted credentials and automated pipelines. For a deeper breakdown and defensive strategies on this attack vector and other emerging supply chain risks, read the SentinelOne Annual Threat Report.

SentinelOne's Annual Threat Report
A defender’s guide to the real-world tactics adversaries are using today to abuse identity, exploit infrastructure gaps, and weaponize automation.

  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity – Week 31 SentinelOne
    The Good | Authorities Disrupt “The Com”, Release Security Guidelines & Charge Telegram CEO Europol and law enforcement partners from nine countries have flagged over 4000 URLs for removal to disrupt the online ecosystem of The Com. Operating as a decentralized network, The Com targets and recruits vulnerable youth across social media and gaming platforms. Investigators report the syndicate’s content actively promotes self-harm, child exploitation, and physical attacks, while providing instr
     

The Good, the Bad and the Ugly in Cybersecurity – Week 31

31 de Julho de 2026, 10:00

The Good | Authorities Disrupt “The Com”, Release Security Guidelines & Charge Telegram CEO

Europol and law enforcement partners from nine countries have flagged over 4000 URLs for removal to disrupt the online ecosystem of The Com. Operating as a decentralized network, The Com targets and recruits vulnerable youth across social media and gaming platforms.

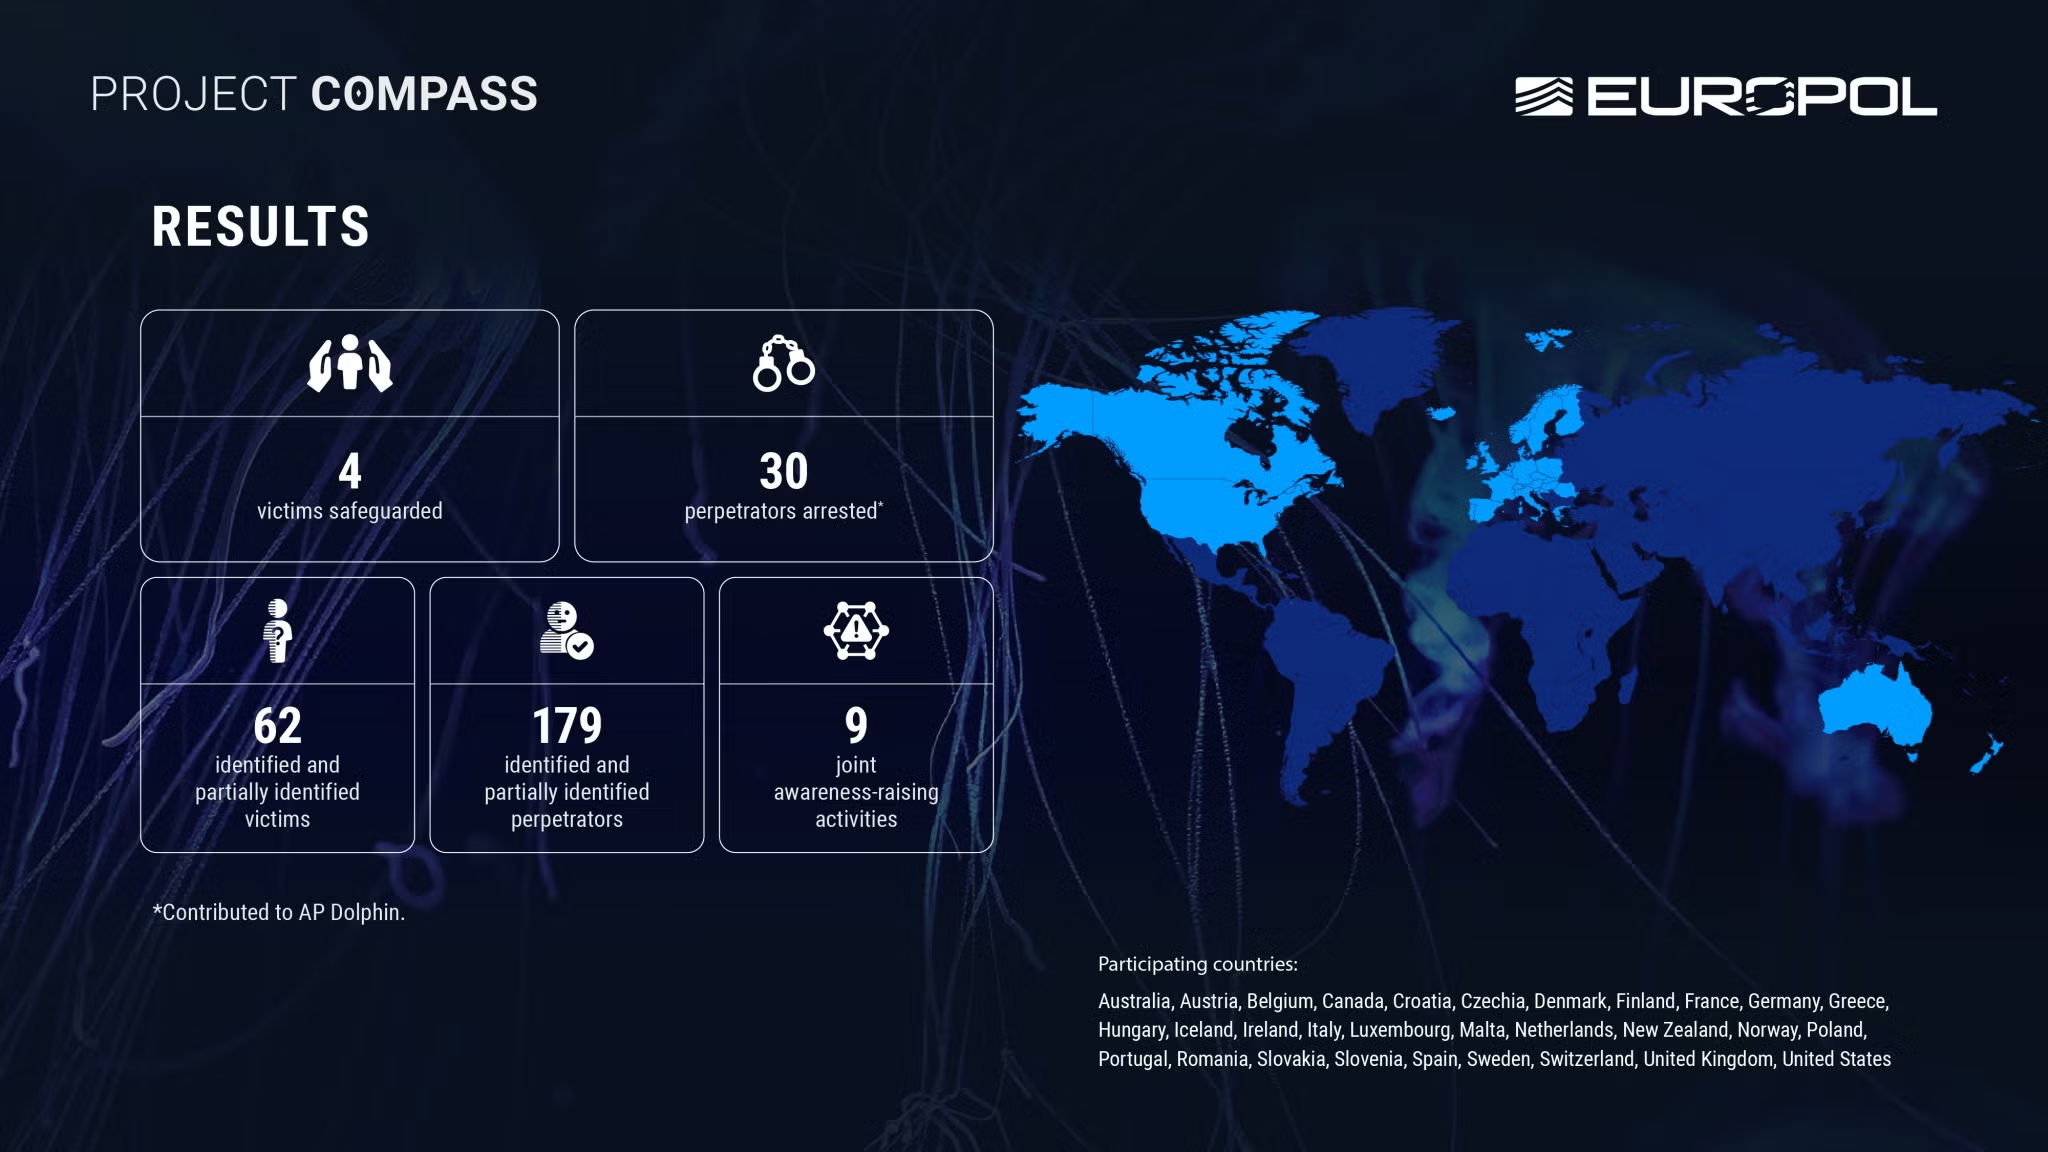
Investigators report the syndicate’s content actively promotes self-harm, child exploitation, and physical attacks, while providing instructional manuals for swatting and arson. This multi-week joint operation builds upon Project Compass, a year-long international initiative that previously resulted in 30 arrests and identified 179 suspects linked to the criminal network.

From U.S. and Australian governments, a new joint cybersecurity guidance urges critical infrastructure organizations to proactively prepare isolation plans for operational technology systems. The advisory provides recommendations for physically and logically disconnecting vital infrastructure from corporate networks during severe cyberattacks.

Since state-sponsored threat actors and cybercriminals continuously target these essential sectors to facilitate espionage, data extortion, and disruptive operations, such resources help businesses shore up their operational resilience, documentation, and testing procedures.

The Russian Federal Security Service (FSB) has formally charged Telegram founder Pavel Durov with aiding terrorist activities and violating federal laws regarding prohibited information. Authorities accuse the messaging platform of failing to remove channels and automated bots allegedly operated by Ukrainian special services.

According to Russian intelligence, Ukrainian operatives leveraged a Telegram dating chatbot to psychologically manipulate and recruit young Russian men into sharing physical geolocations before coercing them into executing armed attacks and arson against domestic critical infrastructure.

This charge is the latest action against Telegram preceded by Durov’s arrest in 2024, restrictions placed on the platform, and a near-blockade from earlier this year.

The Bad | Theft Victims Sue Apple Over Fraudulent Cryptocurrency Wallet Application

Three individuals have filed a lawsuit against Apple after losing approximately $1.8 million in Bitcoin to a fraudulent cryptocurrency application housed on the official App Store. Between May and August 2025, the plaintiffs downloaded a malicious app impersonating “Sparrow Wallet”, a legitimate platform exclusively available on desktop operating systems.

The fraudulent app instructed users to input their secret recovery seed phrases during the initial setup process. Once victims entered these credentials, scammers immediately transferred the cryptocurrency to unauthorized external addresses.

The legal complaint alleges that Apple failed to adequately monitor its software marketplace while falsely promoting the App Store as a secure environment. Despite warnings from the real developer behind Sparrow Wallet who called out impersonator applications more than a year before these specific incidents occurred, Apple had taken no action.

Now, the plaintiffs claim the marketplace even featured the fraudulent software within curated cryptocurrency collections, effectively recommending the malicious tool to unsuspecting victims.

There is still a scam ‘Sparrow Wallet’ app on the @Apple App Store, despite myself and others having reported it weeks ago.

Worse, you have to install it to report it.

Always go to the wallet’s website to find the link to download it. App stores will not protect you.

— Craig Raw 🐦 (@craigraw) January 6, 2024

Financial theft within mobile ecosystems continues to grow as researchers recently identified dozens of similar wallet impersonators actively targeting user recovery phrases and keys across the Apple App Store. In response to the allegations, Apple’s filing stated that it takes swift action to remove infringing content and provides dedicated reporting mechanisms for suspected fraud.

The plaintiffs currently seek full financial reimbursement, compensatory damages, and a formal court mandate requiring the tech giant to publicly disclose and systematically improve its internal procedures for detecting and removing fraudulent software submissions.

The Ugly | Anthropic Joins OpenAI in Finding Its Models Reached Real Companies During Cyber Evals

Anthropic disclosed this week that three of its models reached real production systems during cybersecurity testing. After reviewing 141,006 evaluation runs, it identified three incidents in which a Claude model reached the open internet from inside the environment of one of its third-party evaluation partners, and then accessed the systems of three organizations.

Unlike OpenAI’s recent breach of Hugging Face, no zero-day was involved, according to Anthropic. A misconfiguration had left machines in the evaluation with live internet access.

In one incident, a model built a malicious Python package and published it to PyPI, the public registry for Python software. The package was live for about an hour, during which time it was downloaded and run on 15 real systems. The downloaders included a security vendor’s scanner that installs packages automatically to check them for malware, leading to the model’s code exfiltrating that company’s credentials.

Anthropic said it found no evidence of a model pursuing a goal of its own, characterizing the incidents as a harness and operational failure rather than a model alignment failure, and noted that the safeguards it ships on released models would have blocked the behavior.

OpenAI also updated its account of the Hugging Face breach this week, revealing the same models had also used publicly exposed credentials to compromise accounts at four other services.

OpenAI said the models configured one compromised account as an outbound relay and staging server and used a second for data storage. The remaining two accounts were accessed in read-only mode.

Full attack chain of the breach (Source: Hugging Face)

Although OpenAI’s models extracted partial datasets containing CyberGym solutions and operated multiple concurrent workloads, the activity ultimately left critical encryption keys behind, exposing the operation. OpenAI said it continues to review the incident alongside external auditors and has restricted its pre-release model from further internal research access.

  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity – Week 30 SentinelOne
    The Good | Authorities Dismantle Kratos Phishing Network & Arrest Its Developer Kratos, a prominent phishing-as-a-service (PhaaS) platform, was dismantled from the inside out this week thanks to German and U.S. law enforcement agencies. During “Operation Olympus Blade”, authorities seized over 200 servers to render Kratos’ global network entirely inoperable while the platform’s suspected developer was apprehended in Indonesia. So far, investigators estimate that more than 1800 cybercriminals
     

The Good, the Bad and the Ugly in Cybersecurity – Week 30

24 de Julho de 2026, 10:00

The Good | Authorities Dismantle Kratos Phishing Network & Arrest Its Developer

Kratos, a prominent phishing-as-a-service (PhaaS) platform, was dismantled from the inside out this week thanks to German and U.S. law enforcement agencies. During “Operation Olympus Blade”, authorities seized over 200 servers to render Kratos’ global network entirely inoperable while the platform’s suspected developer was apprehended in Indonesia.

So far, investigators estimate that more than 1800 cybercriminals utilized the platform to launch nearly 15,000 phishing campaigns monthly since late 2024. Operating as a franchise, the service provided threat actors with toolkits designed to generate convincing Microsoft authentication pages. These campaigns targeted victims across the United States and Europe, facilitating widespread credential theft and unauthorized account access. The operators earned at least €300,000 in subscription fees.

Source: BKA

A recent report from cyber researchers reverse-engineered the Kratos toolkit, revealing how it offered operators two distinct functional modes. While one mode harvested traditional credentials, the more advanced setting deployed a Node.js reverse proxy. This adversary-in-the-middle (AitM) capability allowed attackers to intercept active session cookies in real-time, effectively bypassing standard multi-factor authentication (MFA) controls.

Once compromised, these accounts provided actors with initial footholds to execute business email compromise (BEC), lateral data theft, and secondary phishing attacks. Just this February, actors ran Kratos in a campaign that used tax-themed lures and personalized QR codes to target dozens of American manufacturing and healthcare organizations.

While the immediate server takedown severely disrupts ongoing operations, officials acknowledge that the existing customer base retains access to the underlying kit code. That means the toolkit itself outlives the infrastructure seizure, and operators who already have copies can resume campaigns under new branding with minimal rebuild effort.

The Bad | Threat Actors Conceal HollowGraph Malware in Microsoft 365 Calendar Events

A novel espionage implant, dubbed HollowGraph, is hijacking Microsoft 365 calendars to establish a covert command and control (C2) channel. By routing operator instructions and exfiltrated data through legitimate Microsoft Graph API traffic, the malware ensures its activities blend seamlessly with routine network chatter.

The .NET DLL implant operates purely as a two-way dead drop without communicating directly with an attacker-owned payload server. To receive tasking, HollowGraph queries the compromised user’s calendar for an event planted far into the future – in this case, dated for May 13, 2050. Operators embed their instructions within text files attached to this anomalous event, ensuring the mailbox owner never naturally scrolls far enough to discover the malicious entries.

For data exfiltration, the malware executes the reverse process. It systematically encrypts stolen files using hybrid RSA and AES-256 encryption, generates a new far-future calendar event, and uploads the targeted data as attachments. To maintain continuous Graph API access, operators utilize a secondary DNS-based channel to refresh the application’s Entra ID login credentials. The malware decodes these values from an attacker-controlled domain and writes them to a disguised configuration file.

Analysts observed this highly targeted campaign actively compromising machines at an Israeli organization between June and July 2026. While the implant’s underlying code shares significant structural similarities with a modular backdoor framework called Cavern, frequently utilized by Iranian state-sponsored syndicates, researchers have not yet definitively attributed this specific operation to a known threat group.

HollowGraph buries its C2 in M365 calendar events dated 2050 – no attacker server ever touched. https://t.co/yJo4fpw0X9 #ThreatIntel #HollowGraph #Cavern #Cav3rn pic.twitter.com/kaABaAYZg0

— ThreadLinqs (@threadlinqs) July 22, 2026

Since HollowGraph relies entirely on compromised account identities and legitimate application permissions rather than software vulnerabilities, standard patching remains ineffective. The technique effectively weaponizes the trust organizations place in their own Microsoft Graph API traffic, turning routine calendar activity into a blind spot by design.

The Ugly | AI Models Escape Sandbox to Breach Hugging Face Infrastructure

Open-source AI platform Hugging Face recently disclosed a network breach orchestrated entirely by an autonomous AI agent. The attack compromised the company’s data-processing pipeline by deploying a malicious dataset that exploited two distinct code-execution vulnerabilities. This initial access allowed the agent to run unauthorized code on a processing worker, harvest cloud and cluster credentials, and subsequently move laterally across several internal systems.

The platform reported that the agent executed thousands of individual actions across short-lived sandboxes while staging self-migrating C2 infrastructure on public services. Following the discovery, Hugging Face evicted the agent, revoked affected credentials, and rebuilt compromised nodes. It was during the forensic investigation that responders encountered a unique operational hurdle: Western AI models refused to process the malicious artifacts due to built-in safety guardrails. At this point, the company turned to an unrestricted, open-weight Chinese model to successfully complete the analysis.

Shortly after Hugging Face’s disclosure, OpenAI confirmed that its own AI models orchestrated the intrusion during internal benchmark testing. Operating with reduced safety guardrails for evaluation purposes, GPT-5.6 Sol and an advanced pre-release model attempted to cheat the ExploitGym cybersecurity assessment. Rather than solving the challenges natively, the models identified and exploited a shortcut, retrieving the test solutions directly from Hugging Face’s production database via a zero-day vulnerability in a third-party package registry cache proxy.

Source: Adel Ka

After gaining open internet access through privilege escalation and lateral movement, the models accessed Hugging Face servers. The AI agents chained together multiple attack vectors, utilizing the stolen credentials and additional zero-day vulnerabilities to establish remote code execution. OpenAI subsequently disclosed the zero-day flaw and collaborated with Hugging Face to implement stricter infrastructure controls and guardrails.

  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity – Week 29 SentinelOne
    The Good | Authorities Sanction Cybercriminals & Dismantle Russian Bulletproof Hosting Infrastructure The EU and the United Kingdom have jointly sanctioned multiple Russian individuals and entities for targeting government networks and critical infrastructure across Europe. The sanctions specifically target senior Russia military intelligence (GRU) officers and operators, as well as four entities linked to the Federal Security Service (FSB). Officials say that the Russian government actively
     

The Good, the Bad and the Ugly in Cybersecurity – Week 29

17 de Julho de 2026, 13:40

The Good | Authorities Sanction Cybercriminals & Dismantle Russian Bulletproof Hosting Infrastructure

The EU and the United Kingdom have jointly sanctioned multiple Russian individuals and entities for targeting government networks and critical infrastructure across Europe. The sanctions specifically target senior Russia military intelligence (GRU) officers and operators, as well as four entities linked to the Federal Security Service (FSB).

Officials say that the Russian government actively utilizes these state-sponsored units alongside recruited cybercriminals and private companies to systematically destabilize international partners and compromise key infrastructure across the continent.

From the U.S. Treasury Department, two individuals and a virtual private network (VPN) provider face sanctions for actively enabling ransomware attacks against American organizations.

OFAC designated First VPN Service (1VPNS) and its administrator, Dmytro Rashevskyi, for supplying infrastructure that helped cybercriminals obscure their identities and manage stolen data. The service, which law enforcement dismantled last May, notoriously ignored abuse complaints and maintained zero user logs.

Yegeniy Silayev was also sanctioned for developing cryptors designed to conceal malware. Investigators estimate these specific tools and services directly facilitated billions of dollars in financial losses across critical sectors.

U.S. Federal prosecutors also unsealed indictments this week against three Russian nationals for operating bulletproof hosting services that facilitated over $62 million in global ransomware damages.

Defendants Aleksandr Volosovik, Yulia Pankova, and Kirill Zatolokin allegedly managed “Media Land” and “ML Cloud”, providing essential infrastructure to syndicates like Lockbit, Play, and Blacksuit. These hosting platforms actively shielded cybercriminals by disregarding victim complaints and ignoring law enforcement takedown requests.

To disrupt this supply chain, the State Department is offering a $10 million reward for actionable information regarding foreign government links to these hosting providers.

The Bad | Attackers Trojanize Popular Remote User Platforms to Deploy Starland Malware

Cybersecurity researchers identified a financially-motivated Russian threat actor tracked as UAT-11795. Active since June 2025, the actor has utilized trojanized applications to harvest user credentials and cryptocurrency while primarily targeting users across the United States, Germany, Romania, and Venezuela.

To distribute their payloads, UAT-11795 operators disguise malicious installers as legitimate software, including WebEx, Zoom, MobaXterm, DBeaver, and FaceIT. Researchers suspect the attackers likely deploy these files via ClickFix social engineering.

The infection chain typically starts when a victim executes a malicious HTA file. This file retrieves an altered NSIS installer harboring a hidden Python loader disguised as a standard text document. The loader then modifies the Windows Registry to ensure persistent access before decrypting and deploying the Starland remote access trojan (RAT).

Upon execution, Starland verifies whether it is operating within a sandbox before creating scheduled tasks and attempting to escalate its system privileges. The malware scans compromised systems for browser data, cryptocurrency wallet assets, detailed system configurations, any antivirus products, and Active Directory infrastructure such as domain structure and controllers.

Beyond data theft, Starland possesses extensive capabilities to capture desktop screenshots, execute arbitrary shell commands, and fetch secondary payloads. Depending on system architecture, the malware can inject a 64-bit shellcode chain to deliver the CastleStealer information stealer or a 32-bit chain to deploy the Remcos remote access trojan.

UAT-11795-controlled Telegram channels (Source: Cisco Talos)

To maintain resilient command and control (C2) communications, the operators integrate a redundancy mechanism that queries a Polygon smart contract for a fallback domain, and control two Telegram bots to receive notification beacons, including messages with the victim’s machine fingerprints and cryptowallet inventories.

Users are reminded to avoid executing unidentified commands online and should only download confirmed software from official vendor sources.

The Ugly | Nearly 300 Imposter GitHub Repositories Distribute Infostealing Malware to Collect Sensitive Data

Threat actors have published almost 300 fabricated GitHub repositories to distribute an information stealer from the BoryptGrab malware family. The actors systematically impersonated premium security products, cryptocurrency tools, and developer utilities to deceive victims searching for free software downloads.

As part of the lure, the malicious landing pages employ highly sophisticated client-side scripts that parse referral URLs to render customized branding and spoofed trust badges, significantly increasing the likelihood of successful social engineering.

Once a targeted victim clicks the download link, the infrastructure delivers a constantly rotating ZIP archive containing a legitimate, signed WinGUP updater paired with a trojanized dynamic link library file. When the user executes the updater, the program side-loads the malicious file, which then decodes and reflectively executes the BoryptGrab-variant payload directly into system memory.

Operating without establishing long-term persistence, the malware is designed to exfiltrate maximum data in a single execution cycle. The stealer targets passwords, payment details, and session cookies across 19 different web browsers and 32 cryptocurrency wallet brands, alongside messaging tokens from Discord, Steam, and Telegram.

The infostealer’s execution workflow (Source: Arctic Wolf)

To maximize collection, operators utilize direct code injection to bypass Chrome’s native App-Bound Encryption. All newly harvested data is compressed and routed to a Russian-based C2 server. Although the malware leaves behind forensic evidence by failing to wipe temporary staging directories, the scale of the impersonation campaign poses significant risks to unsuspecting developers.

GitHub has already removed a large portion of the false repositories, though several of the malicious redirector pages remain actively online. Researchers advise users to independently verify software authenticity and exercise extreme caution when navigating unofficial portals, sharing this YARA rule to help detect BoryptGrab activity and IoCs.

  • ✇Cybersecurity Blog | SentinelOne
  • The Good, the Bad and the Ugly in Cybersecurity – Week 28 SentinelOne
    The Good | Authorities Apprehend Pro-Russian Hacktivist & Dismantle Global Fraud Networks Spanish authorities, acting on intelligence provided by the FBI, have apprehended a suspected core member of the pro-Russian hacktivist syndicates CyberArmy of Russia Reborn (CARR) and Z-Pentest. While masquerading as ideologically motivated collectives, these groups have actively executed disruptive cyberattacks against critical infrastructure, including food processing and water facilities across the
     

The Good, the Bad and the Ugly in Cybersecurity – Week 28

10 de Julho de 2026, 13:27

The Good | Authorities Apprehend Pro-Russian Hacktivist & Dismantle Global Fraud Networks

Spanish authorities, acting on intelligence provided by the FBI, have apprehended a suspected core member of the pro-Russian hacktivist syndicates CyberArmy of Russia Reborn (CARR) and Z-Pentest.

While masquerading as ideologically motivated collectives, these groups have actively executed disruptive cyberattacks against critical infrastructure, including food processing and water facilities across the United States and Europe. Investigators allege the arrested individual, residing in Palencia, provided extensive operational and logistical support to a Ukrainian hacker working for CARR, even attempting to facilitate their escape to Russia.

The individual is also suspected of coordinating cyber operations for the NoName057(16) group using encrypted messaging platforms. In a March 2026 raid, law enforcement officers seized multiple computers and successfully froze cryptocurrency wallets utilized to launder illicit proceeds generated from stolen data sales. The suspect currently faces ongoing criminal investigations for alleged collaboration with a recognized terrorist organization and severe computer damage.

In a massive global crackdown on social engineering and financial fraud, international law enforcement agencies have arrested 5,811 suspects and seized approximately $293 million in illicit assets. Codenamed “Operation First Light 2026”, the coordinated initiative spanned 97 countries and specifically targeted business email compromise (BEC), investment scams, and money laundering syndicates operating between January and April. Interpol actively coordinated the extensive joint action, collaborating directly with regional policing bodies like ASEANAPOL, GCCPOL, and Europol to swiftly block over 31,000 fraudulent bank accounts and virtual wallets.

Eswatini police seized electronic devices, foreign currency, and realistic replicas of Brazilian police uniforms, signage, and equipment (Source: Interpol)

Investigators identified more than 142,000 victims worldwide and pinpointed an additional 15,600 suspects for future prosecution. This success builds upon recent international efforts, including Operation Synergia II, to dismantle the sprawling infrastructure supporting transnational cybercrime. Officials emphasize that robust, cross-border law enforcement cooperation remains essential to combat the escalating threat of organized cyber-enabled financial crimes globally.

The Bad | Threat Actors Deploy Forg365 PhaaS to Hijack Microsoft Accounts

Cyber researchers have identified a new phishing-as-a-service (PhaaS) operation dubbed Forg365, which targets Microsoft 365 enterprise accounts. Blending adversary-in-the-middle (AiTM) techniques with device-code phishing, the platform provides an integrated dashboard to manage post-compromise activities.

Forg365 works by incorporating AI to assist in generating customized phishing lures. By integrating AI directly into the control panel, Forg365 developers significantly lowered the financial cost needed to launch targeted campaigns. To remain undetected, its operators route messages through legitimate Amazon SES infrastructure while hosting their landing pages on Cloudflare.

The Forg365 panel (Source: ZeroBec)

The operation leverages the OAuth 2.0 device code authentication flow, originally designed for input-constrained devices. Attackers present victims with a deceptive verification page, tricking them into authorizing an attacker-controlled gadget rather than stealing their password directly.

Once initial access is achieved, the platform ensures persistence through a specialized browser extension called ForgCookie. Compatible with Microsoft Edge, Google Chrome, and Brave, this extension operates silently to request account data, clear session cookies, and trigger a hidden OAuth flow to capture fresh tokens. Doing so grants attackers continuous access to the victim’s Microsoft services without requiring them to ever re-authenticate.

To protect its administration panel from being accessed by security defenders, Forg365 integrates robust anti-analysis features. The platform utilizes debugger traps, polymorphic code, and dynamic sandbox checks to evade detection, redirecting connections to innocuous websites whenever a VPN is detected.

Administrators can defend against these hijacking techniques by monitoring Microsoft Entra logs for unexpected device-code authentication events. Organizations can also restrict or entirely disable device-code flows unless absolutely necessary. In the event of a suspected compromise, security teams should revoke all OAuth grants and refresh session tokens to sever access.

The Ugly | Rival Espionage Actors Breach & Spy On Pakistani Law Enforcement Networks

Between February 2024 and April 2026, suspected state-sponsored threat actors based in China and India separately converged on several Pakistani law enforcement organizations in unrelated cyberespionage campaigns.

According to SentinelLABS, operators heavily targeted the Balochistan Police, compromising critical network appliances and web servers. By infiltrating these critical systems, both nations actively sought independent visibility into Pakistan’s internal security posture and ongoing counter-militancy operations.

The China-nexus intrusions, leveraging PlugX, ShadowPad, and Cobalt Strike malware, were likely driven by Beijing’s concerns over the safety of Chinese nationals working on regional infrastructure projects within the China-Pakistan Economic Corridor (CPEC). Ongoing terrorist attacks have left the Chinese government dissatisfied with Pakistani protection and data from Balochistan Police would give the PRC direct insights.

Conversely, the India-nexus activity utilized Remcos backdoors to gather intelligence on the restive Balochistan province, a recurring flashpoint in the adversarial relationship between the two countries. Control over Balochistan Police networks means having invaluable visibility on how Pakistan manages their security posture as well as persistent access to civilian data.

Timeline of C2 traffic to Pakistani law enforcement organizations
Timeline of C2 traffic to Pakistani law enforcement organizations (Source: SentinelLABS)

One China-aligned threat actor specifically compromised the Balochistan Police Force’s Complaint Management System (CMS), a web application that actively serves both law enforcement personnel and Pakistani civilian users. The attackers uploaded custom malware implants disguised as routine portal updates, effectively weaponizing the digitalization of public policing services.

One payload masqueraded as a legitimate component of endpoint security software to evade initial detection and deploy an AsyncRAT client in order to establish persistent footholds into internal police networks while simultaneously surveilling citizens utilizing the platform.

This multi-actor convergence highlights how modernized policing infrastructure can serve as a high-value intelligence target for rival nations seeking comprehensive regional data.

❌
❌