Statistics on Malware Distributed to the Financial Sector In Attack Stage 1, phishing (attacks that trick users into revealing information) had the highest rate at 2.1, Up from 1.8 The previous month. In Attack Stage 2, “Dropper/Downloader” (a type that downloads additional malware) was the most common at 1.1, Though this was a decrease from […]
At just 17 years old, Jordan DeMay was murdered by strangers online.
That’s how Jordan’s father, John DeMay, described what happened to his son four years ago. At home in Michigan, Jordan was readying for a weekend trip when he received a friend request on Instagram. The invite was sent by a user named “dani.robertts” whose profile showed an attractive young woman. After accepting the request, Jordan and the account chatted about nothing in particular—teenage matters, getting to know one another—before “dani” became flirtatious, eventually sending Jordan what she claimed was a nude photograph of herself.
Jordan responded in kind with an explicit photograph of himself.
But here, a trap was revealed.
“Dani Robertts” was not a young, friendly, interested woman. Dani Robertts was several men, sending messages from thousands of miles away in Lagos, Nigeria, who had followed a script to pressure young men into handing over their money. This was not the first time these men had run this scam. But with a great deal of investigative work, it hopefully has become the last.
What happened to Jordan can happen to anyone—and it has happened to far too many young men and women today. It is a type of attack commonly referred to as “sextortion.”
Today, on the Lock and Code podcast with host David Ruiz, we speak with John DeMay about his son Jordan, his family’s relationship with social media, and what parents should know.
In May 2026, we discovered a new cyber-espionage campaign by the Armored Likho group, also known as Eagle Werewolf, that targets private individuals and organizations across various industries in Russia, including major corporations, the public sector, IT, and education. The attackers used a fake app as bait that mimics a service for donations. However, the most interesting part of this campaign isn’t the initial infection method – it’s the malicious implants the attackers use for cyber-espionage.
We’ve written previously about recent Armored Likho attacks, but our analysis shows that the campaign discussed below has more in common with the group’s activity from February. That said, the attackers have significantly expanded their arsenal.
During our research, we found a new cyber-espionage toolkit written in Rust: the Still Toolkit. One of its components, Still Sync, steals Telegram session data to gain ongoing access to the victim’s account. With this stolen data, attackers can leverage the Telegram API to automatically pull chat logs, media files, and other information from the account.
The second component, Still Audio, is an implant for covert audio surveillance. It analyzes the incoming audio stream, automatically detects speech, records conversations, and sends the recordings to a command-and-control server.
In this article, we’ll look at the initial infection method, how the new Still Toolkit components are built, and the technical details of how they operate.
Kaspersky products detect this threat as Trojan.Win64.Agent.* and HEUR:Backdoor.Win32.Generic.
Background
Armored Likho’s malicious activity has been documented several times before: in November 2024, and in February and July 2026. The current campaign shows significant overlap with the November and February campaigns, which used malicious droppers disguised as documents and applications related to Starlink activation or fundraising efforts as the initial infection vector. This campaign also uses fundraising as its lure. At the same time, our research uncovered a number of new tools that point to the attackers expanding their capabilities.
Initial infection
The infection chain starts with an app that mimics a donation service. As of this writing, the app distribution method remains unknown. During our research, however, we obtained several samples posing as apps from different Russian foundations.
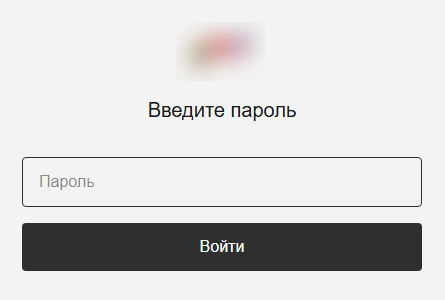
In reality, the app is a dropper. Its developers wrote it in Rust on top of the popular Tauri framework, and it has a graphical interface designed to deceive the user. After launch, it displays a login form that asks for a password, presumably one the attackers supplied.
The login form
After the user enters a valid password, they see a catalog of donatable items. The app pulls item and category information from orderapiserver[.]info through the public/categories and public/products endpoints. A clickable catalog makes the app look legitimate. While the user browses the items, the dropper quietly decrypts and launches the payload for the next stage in the background.
Our analysis shows that the mechanism for decrypting the payload and launching subsequent stages hasn’t changed since the February campaign. However, we found a new cyber-espionage toolkit – the Still Toolkit – made up of two components: Still Sync and Still Audio.
Still Sync
Still Sync is a stealer written in Rust that steals Telegram session data. However, its capabilities don’t stop there. With this stolen data, Sync can log in to the victim’s account and pull messages and media files through the Telegram API.
Architecturally, Sync is an asynchronous application based on the Tokio library. It talks to the server over gRPC and serializes messages with FlatBuffers. It supports both HTTP and HTTPS as transport protocols; the URL of the command-and-control server determines which one it uses.
How it works
When Sync launches, the attackers set several environment variables. Before starting any malicious activity, the implant pulls configuration parameters from these:
STILL_SYNC_ADDR: the address of the command-and-control server. By default, this is https://tg4service[.]com:443.
STILL_SEND_PATH: the path to the tdata
STILL_TELEGRAM_PASSCODE: the password for decrypting the tdata folder, if Telegram data encryption is enabled on the victim’s device.
Sync also supports several command-line arguments:
--console: runs as a console application. If this parameter is absent, the implant creates a TReload service to keep running in the background.
--version: prints version information and exits.
--firefly: launches a trace thread that monitors the program’s operation. It writes error messages to a hidden file, bin, located in the same folder as the main executable.
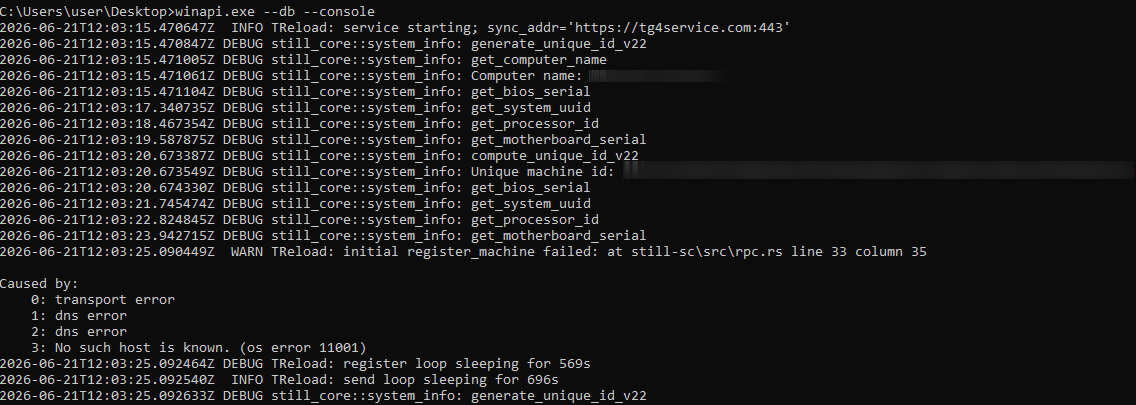
--db: turns on debug mode with detailed logging.
Example Still Sync logs
Once it launches, the malware begins registering the device with the C2 server. To do this, Sync collects the following information about the victim’s system:
Motherboard serial number
CPU ID
System UUID
BIOS serial number
Computer domain name
The malware combines the collected data into a single string with a colon as the separator. It then hashes that string with SHA-256 and stores the resulting hash under the key sysmarker. Worth noting: other Armored Likho tools, AquilaRAT included, use this same hashing algorithm.
Sync then serializes a package containing all the collected information and the agent version, and sends it in a POST request to /still.rpc.Sync/RegisterMachine. The response contains a machine_id value, which Sync uses to identify itself in subsequent requests.
Once registration succeeds, Sync sends a POST request with the machine_id parameter to /still.rpc.Sync/GetMachineSettings. The server responds with the following settings:
enabled: triggers malicious activity on the infected device.
scan_portable: turns on extended scanning when searching for the tdata We’ll cover this feature in more detail below.
fetch_telegram: if this parameter is on, Sync attempts to log in to Telegram and extract data. We’ll cover this feature in more detail below.
download_channels: if this parameter is off, Sync skips channel dialogs when exfiltrating Telegram data.
These parameters have no default values, so Sync doesn’t perform any malicious actions until the registration and settings-retrieval processes both complete successfully.
Telegram data collection
Before stealing a Telegram session, Sync searches for the tdata folder, unless the STILL_SEND_PATH variable is already set. The list of search paths includes both standard and nonstandard directories, if the scan_portable option is turned on:
C:\Users\<username>\AppData\Roaming\Telegram Desktop\: the standard Telegram Desktop installation directory.
C:\Users\<username>\AppData\Local\Packages\<package_folder>\LocalCache\Roaming\: the installation directory for the Microsoft Store version. Sync identifies the package folder by a name that contains the string TelegramMessenge.
C:\: used for the extended search (if the scan_portable option is on).
Sync then sends a POST request with a list of files from the tdata folder to the /still.rpc.Sync/CheckFiles endpoint. The server responds with the following values:
snapshot_id: an identifier the server assigns to the current data snapshot.
present: a list of file paths that are already present on the server.
This lets the C2 server avoid re-receiving files it already has. In addition, if Sync can’t access files on disk through standard methods, it falls back on three mechanisms that abuse the SeBackupPrivilege privilege:
Opening files with the CreateFileW function using the FILE_FLAG_BACKUP_SEMANTICS parameter
Creating a backup copy through the Shadow Copy service and reading files from there
If the previous methods all fail, attempting to copy the file using the Robocopy utility in backup mode
Beyond stealing Telegram session data, Sync can carry out full-scale collection of user information from the messaging app. When the fetch_telegram option is on, it launches a separate thread that authenticates to the chat app using the previously obtained tdata. Once authentication succeeds, Sync gains access to the account data and sends the following collected information to the server:
User details, such as username, phone number, first and last name
Information about private chats, groups, or channels, such as chat name and ID, the member list, and so on
Dialogs from private chats, groups, and channels (if the download_channels option is on)
Media files under 250MB: photos, documents, stickers, and contacts
Still Audio
Still Audio is an audio surveillance implant written in Rust. Its main job is to analyze the incoming audio stream and start recording voice when certain conditions are met – we’ll cover those in the next section. Architecturally, Still Audio largely mirrors Sync and uses the same mechanisms for communicating with the C2 server.
On launch, Still Audio performs a sequence of actions:
It extracts libmp3lame.dll, a file stored inside the executable. This is a library used to encode audio data.
If the --console command-line argument is absent, the implant creates a service named auxhost, connects to it, and continues running in the background.
While running in the background, it creates a file, logfile.log, to write logs to.
Next, Still Audio retrieves the C2 server address. As with Sync, it stores the URL in an environment variable – in this case, STILL_AUDIO_SYNC_ADDR. If that variable isn’t set, it falls back to STILL_SYNC_ADDR, which shows the two modules are compatible with each other. If neither variable is set, it uses the default URL, https://srwinservice[.]com.
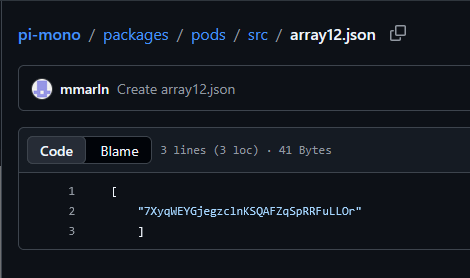
Still Audio also uses the Dead Drop Resolver technique as a fallback mechanism for obtaining the C2 address. If the current server stays unreachable for three days, the tool tries to pull the current C2 URL from a GitHub repository. In the sample under analysis, we found the following URL for the page containing C2 information: hxxps://raw.githubusercontent[.]com/mmarln/pi-mono/refs/heads/main/packages/pods/src/array12.json
Encrypted C2 address inside the GitHub repository
The repository, a fork of a popular project, contains the server URL Base64-encoded and encrypted with the Blowfish algorithm in ECB mode, using the key 5c8e153228edd3c6cbf75684 (lowercase string). Older AquilaRAT samples use this exact same algorithm and key.
Once it obtains the current C2 address, the Audio module starts a registration process similar to Sync’s, but through a different endpoint:
/still.rpc.Audio/RegisterAudioMachine. Also, unlike Sync, Audio sends a list of available audio input devices along with the system information.
The server responds with settings for the implant:
machine_id: a unique identifier for the current device.
vad_threshold: the threshold value for the VAD (Voice Activity Detection) algorithm. Expressed as a decimal fraction, it represents a proportion of the maximum sound level the input device can pick up. Sound above this threshold counts as voice activity. The default vad_threshold is 02.
max_silence_duration: the number of audio samples with a VAD value below the set threshold after which the implant considers the recording finished.
max_buffer_size: the maximum buffer size for recorded audio data.
active_device: the name of the input device selected for recording, from the list of available devices.
The eavesdropping process
Still Audio works with raw audio samples it captures directly from the input device. To detect voice activity, it implements an algorithm based on Root Mean Square (RMS), a lightweight signal-processing method that distinguishes speech from silence by measuring the audio signal’s average power over time. The implant doesn’t rely on any third-party libraries here; it implements all the calculations itself.
The implant compares the calculated RMS value against the vad_threshold parameter. If RMS meets or exceeds this threshold, recording starts. To avoid losing the beginning of the recording, Still Audio uses a pre-buffer, a size-limited buffer that stores samples from just before the current recording moment. A sequence of max_silence_duration samples (320 by default) with RMS values below the threshold signals the end of the recording. For example, with a standard headset running at a 44.1kHz sampling rate, recording stops after roughly 7ms of silence.
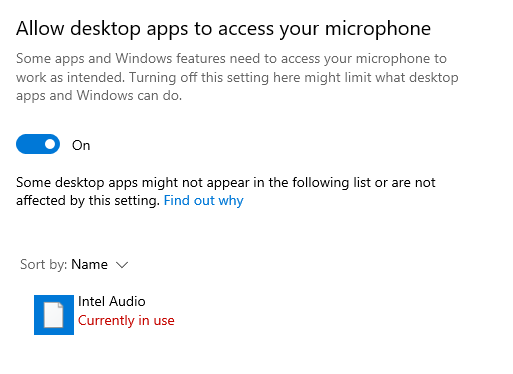
Interestingly, the Audio module makes no attempt to hide its use of the microphone: its name shows up in Windows settings. In the sample we examined, the file was saved to disk as IntAudio.exe, and it appeared in the list of apps using the microphone as “Intel Audio”:
The malicious module in the list of apps using the microphone
Before sending recordings to the server, the implant uses the libmp3lame library to encode the raw audio samples. It sends the recording files via a POST request to /tgfrg, adding a Client-Id header containing the machine_id obtained during registration to identify the device.
Infrastructure
This campaign draws on a broad set of hosting providers and domains registered at different points in time, which suggests the attackers are trying to make their infrastructure harder to detect. We found no direct overlap in domains or IP addresses with the February campaign. Even so, the two infrastructures share some similarities:
They use the same hosting providers, with the ASNs 149440, 202448, and 215311.
Their domain names follow similar naming patterns that mimic Windows system services and update mechanisms.
Domain
IP address
Registration date
ASN
orderapiserver[.]info
187.127.153[.]38
April 18, 2026
47583
tg4service[.]com
159.198.37[.]74
October 4, 2025
22612
srwinservice[.]com
213.252.244[.]123
March 19, 2026
61272
screenserv[.]com
23.26.237[.]250
February 13, 2026
149440
windowserv[.]net
23.27.24[.]30
February 10, 2026
149440
managementapiservice[.]com
188.212.124[.]178
May 1, 2026
202448
service8date[.]com
145.223.69[.]143
January 13, 2026
215311
updateservs[.]com
145.223.68[.]66
December 23, 2025
215311
Victims
In this campaign, we’ve determined that the attackers’ primary targets are users in Russia. Most victims are private individuals, though the corporate sector, government organizations, IT companies, and educational institutions are also affected.
Attribution
This campaign has been using both new tools and malware families documented in BI.ZONE’s February report. While some components turned up for the first time, they show significant code-level overlap with malicious tools seen in earlier Armored Likho campaigns. Based on these overlaps, along with additional technical artifacts, we’re highly confident the Armored Likho group is behind the campaign. The overlaps we identified include:
Identical dropper architecture in the February and current campaigns, which includes the use of the Tauri library to build the graphical interface, a similar user-input handler, a payload with the ICRYPTMP header, and the same multi-part encryption format.
The same encryption algorithm and key used in AquilaRAT from the previous campaign and in the Still Audio module from the current campaign, both implementing the Dead Drop Resolver technique.
Identical logic for generating the sysmarker value in older AquilaRAT samples and in the Still toolkit from the current campaign. The algorithms match down to the PowerShell commands used to collect system information.
Substantial infrastructure overlap, which includes the hosting providers and domain-naming patterns described in the Infrastructure section.
Takeaways
The campaign described in this post shows Armored Likho’s toolkit evolving, with the group steadily expanding its cyber-espionage capabilities. Beyond the components we already knew about, the attackers rolled out new modules that let them not only access Telegram data but also conduct audio surveillance on victims. Together, these capabilities significantly widen the range of information attackers can collect in a single compromise.
One point deserves particular attention: the new tools form a cohesive set, sharing similar architecture, C2 communication mechanisms, and common implementation elements. This points to the group building out its own tool ecosystem, designed for long-term use and further expansion.
The emergence of new, specialized modules shows the attackers aren’t just trying to preserve their existing capabilities – they’re working to make intelligence-gathering more effective by controlling multiple communication channels at once.
Analysis of the Aeternum botnet loader, a threat leveraging Polygon blockchain smart contracts for decentralized C2 infrastructure and payload execution.
Young people use AI for everything. From schoolwork to interview prep, relationship advice to shopping decisions, the technology has become part of how young people live. For the most digitally fluent generation ever, AI is a competitive edge, a creative partner, and an always-on assistant.
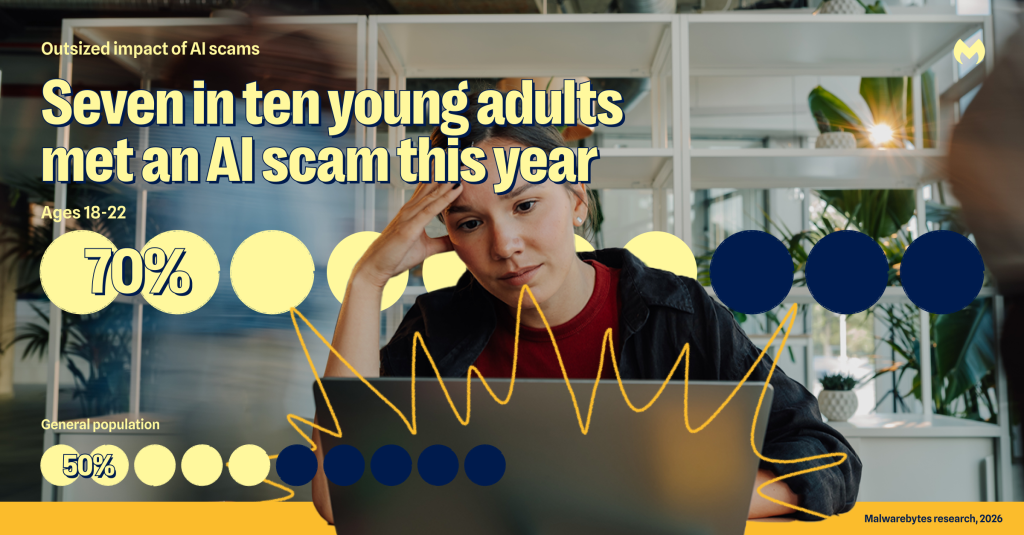
But the same technology making young people’s lives easier is also making the internet harder to navigate. AI is making scams more convincing, identities easier to manipulate, and online content harder to trust. Seven in ten (70%) 18-to-22-year-olds have experienced an AI-related scam in the last year, compared to half of the general population. And nearly every young person worries AI will be used against them.
This isn’t happening because young people are reckless. It’s happening because the online platforms they rely on for everyday life now double as entry points for AI threats: social feeds where manipulated content and real content sit side by side, online marketplaces filled with fake storefronts and reviews, messaging channels where threats can be personalized, and AI tools that can make false information feel like the truth.
That creates a new kind of safety burden. Young people are being asked to use AI, judge its output, protect their identities, and avoid increasingly personalized scams all at once. The result is a digital life that feels more powerful, but also more vulnerable to abuse.
The internet is getting harder for young people to trust
The internet young people grew up with isn’t the same one they’re facing today. AI has changed the landscape, making it harder for even these digital natives to know what information is credible and safe. Half of 18-to-22-year-olds strongly agree that it’s becoming harder to tell what content is genuinely human or real.
Young people have had a front row seat to how AI can bend the truth. Nearly half have seen AI provide information they knew or later found out was wrong or misleading (44% versus 30% of the general population). Nearly one in four (23%) have suffered negative consequences because of AI advice, compared with 16% of the general population, and 18% say they have suffered emotionally from AI advice, compared with 12% of the general population. For a generation using AI in every corner of their lives, bad information can have lasting effects on their credibility, reputation, and relationships.
Many young people have changed how they engage online as a result:
47% of young people say AI has changed how much they trust reviews or content, compared with 37% of the general population
35% say AI has changed how they shop online, compared with 26%
32% say AI has changed how they present themselves professionally, compared with 20%
19% say AI has changed how they date or communicate romantically, compared with 10%
As one young person said about online dating:
“Dating isn’t an option for me online anymore. You just never know what is or isn’t AI, and I don’t want to spend a lot of time on someone fake.”
AI is making it easier for scams to reach young people
The harder it becomes to tell what is real, the easier it becomes for scams to work. For young people, AI is fueling a wave of scams that are more personal and invasive than ever before.
Nearly one in four young people have been a victim of an extortion scam of some kind (24% versus 17% of the general population).
Nearly one in five have been a victim of a deepfake or virtual kidnapping scam (19% versus 8%).
Nearly one in ten have been a victim of sextortion (8% versus 7%).
More than one in ten have been a victim of an impersonation scam (14% versus 10%).
More than one in ten have been a victim of a romance scam (12% versus 10%).
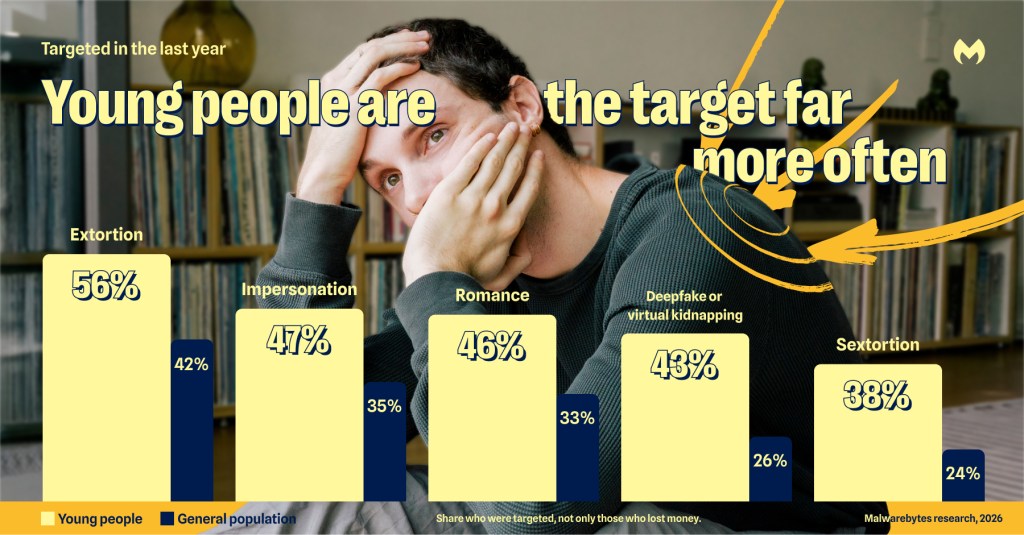
What’s striking isn’t just how many young people have been victimized—it’s how many have been targeted:
More than half have been the target of an extortion scam (56% versus 42% of the general population).
47% have encountered an impersonation scam (versus 35%)
46% have encountered a romance scam (versus 33%).
More than four in ten have been targeted by a deepfake or virtual kidnapping scam (43% versus 26%).
Nearly four in ten have encountered sextortion (38% versus 24%).
These scams may look different on the surface, but they all work the same way: they exploit fear, trust, shame, and intimacy. The more often young people encounter them, the more chances scammers have to find exactly which emotional triggers work.
This exposure isn’t random. Young people are on social platforms at rates up to three times those of the general population: 89% use Instagram (versus 55% of the general population), 78% use TikTok (versus 38%), 68% use Snapchat (versus 26%), and 49% use Pinterest (versus 25%). Scammers can use these platforms to get everything they need to make their threats more convincing: public photos, friend networks, school affiliations, relationship clues, and everyday posts containing personal information. With AI, scammers can use that content to create explicit images, clone voices, impersonate profiles, and create threats personalized with details that are hard to ignore.
One young person shared their experience:
“I had someone make fake nudes of me using AI on my photos from my social media and threaten to post them on Facebook after I realized that they had scammed me. I decided to be more careful with my personal information.”
Young people fear AI will steal what money cannot replace: identity, reputation, and sense of self
AI-fueled scams aren’t just scams in the traditional sense. They are forms of identity abuse. This is different from traditional identity theft. For young people, the risk isn’t only that someone steals a password or money. It’s that scammers can use AI to make them appear to say, do, or share something they never did, with consequences that can follow them in their personal and professional lives.
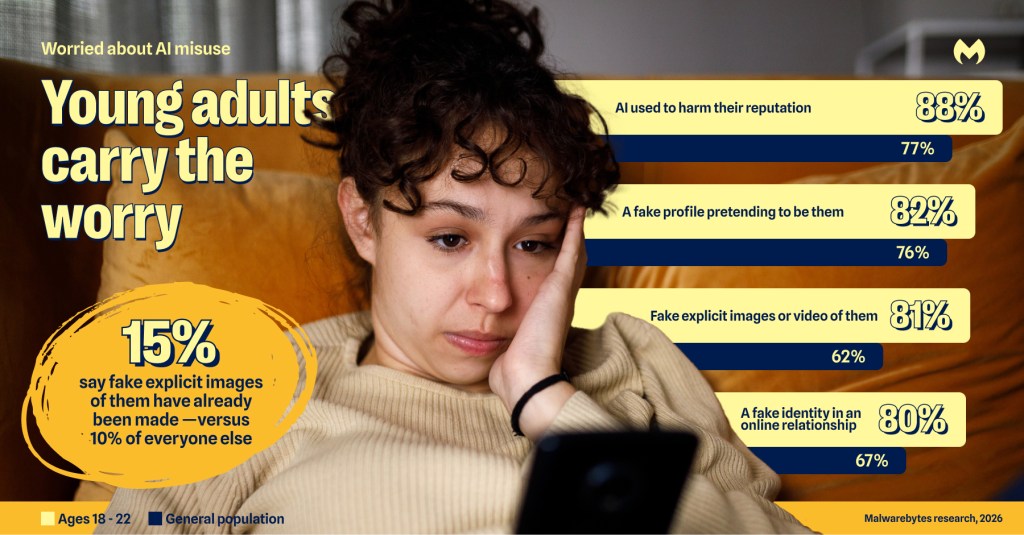
That’s why young people are so concerned about AI being used against them. The fears that hit hardest:
88% worry about AI being used to harm their professional or personal reputation versus 77% of the general population
82% worry about someone creating a fake profile pretending to be them versus 76%
81% worry about someone creating fake nude or sexually explicit photos or videos of them versus 62%; 15% say it’s happened to them already (versus 10%)
80% worry about being deceived by someone using AI to fake their identity in an online relationship versus 67%
These threats are especially powerful at a life stage where young people are still building their personal and professional reputations. A fake profile, manipulated image, or AI-generated explicit video can affect how everyone from classmates and professors to potential employers and romantic partners see them for years to come.
Young people are pulling back online, but protection is still too manual
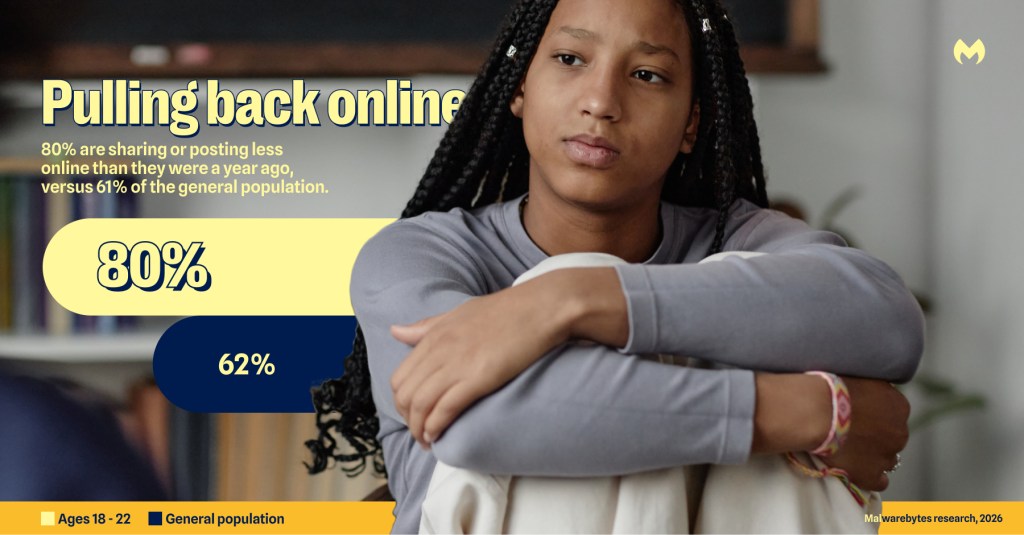
Many young people are responding by retreating. 80% are sharing or posting less online than they were a year ago, versus 61% of the general population. Compared to the general population, more 18–22-year-olds have also taken AI-related protective measures like tightening privacy settings, removing unknown followers, using reverse image search to verify content, requesting data removal, and watermarking their own photos and videos.
Those actions matter, but they also show how much responsibility has been pushed onto individuals. Staying safer online now means constantly reviewing settings, checking sources, questioning content, and so much more. That’s a lot to ask of anyone, and the fatigue is showing: 42% of young people say they receive so many warnings they have stopped paying attention, compared with 36% of the general population. It’s hard to sustain vigilance when new risks are always emerging.
At the same time, completely opting out isn’t realistic. Young people remain deeply embedded in digital life, and they’re still some of AI’s most enthusiastic adopters: 74% say AI has had a positive impact on their lives, compared with 57% of the general population. They aren’t rejecting AI or the internet, but they are carrying more of the safety burden than they should have to.
What young people can do to help decrease their risk right now
Know the scams targeting you. Extortion, sextortion, deepfakes, and romance scams disproportionately target young people. If someone contacts you with threats of any kind, do not pay. Report it to the platform and to authorities.
Button up your social media. Everything you post publicly is available to anyone, including scammers. Tighten privacy settings on the platforms you use most and review your followers regularly.
Don’t trust product images alone. Before buying from an unfamiliar retailer, use reverse image search on product photos and look for independent reviews off the retailer’s own site.
Create a family code word. Make sure you agree on this word in person, not online. If you receive a panicked call from someone you know asking for money or information, verify they are who they say they are with the code word.
Don’t reuse passwords. If one password gets stolen in a data breach, it will likely get tried on all other accounts you might have. Use a different password for every account to keep your accounts locked down.
Turn on two-factor authentication on all your important accounts. Only 30% of young people have done this. It is one of the highest-impact protections available and takes under five minutes to set up.
Protect your devices. Use security software on all your devices, and keep all your software up to date to make sure you’re patched against all known security holes.
Malwarebytes Student Protection Program
If you’re a student or work at a university, Malwarebytes Student Protection Program provides two years of free Premium Security for three devices for all US college or university students, staff and faculty.
This includes Malwarebytes device protection for laptops, tablets, and mobile phones with built-in scam protection. It protects against creepy trackers and ads, and blocks malware, ransomware, and cybercriminals themselves.
The research in this article is based on a March 2026 survey about AI, identity, and the collapse of digital trust and was conducted among 1,500 respondents in the United States, United Kingdom, Germany, Austria, and Switzerland. This article focuses on student-aged adults, defined as respondents ages 18 to 22, compared with the general population.
Additional context comes from Malwarebytes’ 2025 research Tap, Swipe, Scam: How Everyday Mobile Habits Carry Real Risk, which looked at mobile scams and scam-related behaviors across the same markets. Both research studies were prepared by an independent research consultant and distributed via Forsta.
There is a lot going on right now regarding the safety of kids online.
In the United States, the majority of state legislatures have passed age verification laws requiring a variety of websites to more rigorously verify the age of their visitors. In the United Kingdom, Canada, Norway, Spain, and Germany, lawmakers are considering bans on social media access for anyone under the age of 16—Australia passed its ban in 2025. In schools across the world, smartphones have been removed from classrooms, hallways, and cafeterias. And online, some of the most popular apps and video games with children, such as Discord and Roblox, have implemented default restrictions on what young users can find and who they reach.
Today, on the Lock and Code podcast with host David Ruiz, we bring back Anna Brading, editor-in-chief of Malwarebytes Labs and director of content and, perhaps most importantly, mother of three. With a long career in cybersecurity—and an equally long time spent reading, writing, and assigning some of the cybersecurity world’s most pressing headlines—Brading has a unique perspective on what is most dangerous to her children online.
Brading’s list of priorities is long, and includes improper image use, “online nastiness,” and Roblox, but she has a few rules and guidelines to help. She sets a one-hour-a-day video game limit on the weekends, restricts YouTube to a communal and monitored activity, and requests that no one share photos of her children online without her express permission. Importantly, she also reminds parents to trust their guts.
“If the norm now is mental health issues or online grooming or non-consensual porn or constant comparison, then I’m okay without my kids fitting in. I would say be radical, buck the trend, don’t do what everybody else is doing. Say no to things you don’t feel comfortable with.”
Every consumer app has a settings menu that lets you make decisions about things like notifications or dark mode. Meta has just decided that anyone can generate AI images of you from your public Instagram account by typing your Instagram handle into a prompt.
On July 7, Meta launched its AI image generation model, Muse Image. It integrates with public Instagram accounts. Now, all someone has to do is tag your account in a prompt, and they can use Meta AI to generate an image using your likeness. According to Meta’s own policy, you won’t be notified if someone does this, making it difficult to know when or how your likeness has been used.
Meta says Muse Image is meant to make AI image generation more personal by letting people reference public Instagram accounts in their prompts. That may sound fun when you’re creating images of yourself. It’s less appealing when anyone else can do the same with your account.
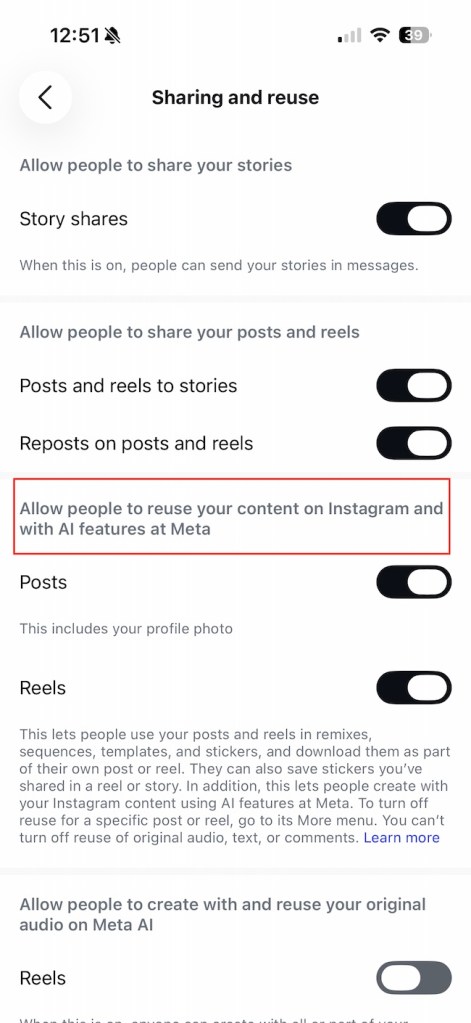
Meta lets you opt out, although finding the setting is its own adventure. On Instagram, open Profile > Menu > Sharing and reuse. Under “Allow people to reuse your content on Instagram and with AI features at Meta,” turn off the Posts and Reels toggles. Depending on your app version, the wording may vary, and the feature is still rolling out, starting in the US, so you may not see the setting yet.
You’d hope that Meta would tell you up front with a big, bold “Turn this off if you don’t want it” message when you open Instagram, but no such luck. You’d also hope that the company would retroactively remove any images that someone made of you before you opted out, but that’s not happening either.
Opting out only prevents future image generation. Any AI images that someone created before you switched the setting off still remain in circulation.
The only mechanism that comes close to comprehensive protection is switching your account to private.
What’s the risk?
There are privacy and security implications here. Anyone can now generate AI images based on your public Instagram profile without your knowledge, and Meta won’t notify you when it happens. Public Instagram photos were already being harvested by attackers to create deepfakes for identity verification fraud. Giving people an official way to generate AI images based on public profiles lowers the barrier to creating synthetic images that could be used for impersonation, scams, or other abuse.
Cybercriminals are already combining generative AI with automated tools to scale phishing and fraud. Muse Image makes it even easier to generate convincing images based on public identities.
Meta’s AI has introduced other security issues, too. Earlier this year, researchers disclosed a “confused deputy” flaw in Meta’s AI support chatbot that let it make account changes—including changing email addresses and resetting passwords—without adequately verifying who it was talking to. Enabling multi-factor authentication (MFA) appeared to mitigate that issue.
Meta also uses an opt-out approach when training its AI on European user data. The company relies on GDPR’s “legitimate interests” legal basis to process European users’ data for AI purposes, a position that privacy group NOYB has challenged.
Protect yourself
If your Instagram account is public, open Profile > Menu. Under “How others can interact with you” tap Sharing and reuse, then turn off the Posts and Reels reuse settings under “Allow people to reuse your content on Instagram and with AI features at Meta.” Turning off these reuse settings only prevents future AI image generation and reuse. It won’t remove AI-generated content or remixes that already exist.
Turn on MFA for all your Meta accounts. It’s one of the simplest ways to protect your account if your password is compromised.
If you want the strongest protection Meta currently offers, switch your Instagram account to private. It’s a blunt solution, but it prevents strangers from using your public profile as source material.
Meta’s own Oversight Board has already said the company needs stronger detection tools and better labeling of AI-generated content. When Meta’s own governance body says the defenses aren’t enough, consumers should take notice.
Update July 11: After widespread criticism over privacy and consent, Meta announced yesterday it has removed the Muse Image feature that allowed people to generate AI images by referencing public Instagram accounts. The company said the feature “missed the mark” and is no longer available.
Scammers don’t need to hack you. They just need you to click once.
1. Overview First identified in 2018, Vidar operates under a Malware-as-a-Service (MaaS) model and continues to be distributed through various attack cases to this day. AhnLab SEcurity intelligence Center (ASEC) has been monitoring cases of Vidar distribution targeting Korea, and this report summarizes the Vidar distribution cases identified in the first half of 2026. […]
SentinelLABS and Beazley Security discovered and analyzed a rapidly evolving series of infostealer campaigns delivering the Python-based PXA Stealer.
This discovery showcases a leap in tradecraft, incorporating more nuanced anti-analysis techniques, non-malicious decoy content, and a hardened command-and-control pipeline that frustrates triage and attempts to delay detection.
We identified more than 4,000 unique victim IP addresses in exfiltrated logs, with infected systems spanning at least 62 countries, most notably South Korea, the United States, the Netherlands, Hungary, and Austria.
The stolen data includes over 200,000 unique passwords, hundreds of credit card records, and more than 4 million harvested browser cookies, giving actors ample access to victims’ accounts and financial lives.
The threat actors behind these campaigns are linked to Vietnamese-speaking cybercriminal circles who monetize the stolen data through a subscription-based underground ecosystem that efficiently automates resale and reuse through the Telegram platform’s API.
Overview
In close partnership, Beazley Security and SentinelLABS have uncovered a large-scale, ongoing infostealer campaign built around the Python-based PXA Stealer. Initially surfacing in late 2024, this threat has since matured into a highly evasive, multi-stage operation driven by Vietnamese-speaking actors with apparent ties to an organized cybercriminal Telegram-based marketplace that sells stolen victim data.
Throughout 2025, these actors have continuously refined their delivery mechanisms and evasion strategies. Most notably, they’ve adopted novel sideloading techniques involving legitimate signed software (such as Haihaisoft PDF Reader and Microsoft Word 2013), concealed malicious DLLs, and embedded archives disguised as common file types. These campaigns use elaborate staging layers that obscure their purpose and delay detection by endpoint tools and human analysts alike.
The final payload, PXA Stealer, exfiltrates a broad spectrum of high-value data–which includes passwords, browser autofill data, cryptocurrency wallet and FinTech app data, and more–to Telegram channels via automated bot networks. Our telemetry and analysis uncovered over 4,000 unique victims across more than 60 countries, suggesting a widespread and financially motivated operation that feeds into criminal platforms such as Sherlock. This data is then monetized and sold to downstream cybercriminals, enabling actors who engage in cryptocurrency theft or buy access to infiltrate organizations for other purposes.
This campaign exemplifies a growing trend in which legitimate infrastructure (e.g., Telegram, Cloudflare Workers, Dropbox) is weaponized at scale to both execute and monetize information theft, while simultaneously reducing the cost and technical overhead for attackers. As stealer campaigns become increasingly automated and supply-chain integrated, defenders must adjust to an adversary landscape defined not just by malware, but by infrastructure, automation, and real-time monetization.
SentinelLABS would like to extend sincere thanks to our partners at Beazley Security for their instrumental collaboration and openness in sharing critical insights throughout this investigation.
Background and Haihaisoft Sideloading
This cluster of PXA Stealer activity has been ongoing and active since late 2024, with some BotIDs being created as early as October, 2024. The general delivery mechanisms and TTPs have not changed. However the actors behind this cluster have continually pivoted to new sideloading mechanisms, along with updated Telegram C2 infrastructure.
During a wave of attacks occurring in April 2025, users were phished or otherwise lured into downloading a compressed archive containing a signed copy of the Haihaisoft PDF Reader freeware application along with the malicious DLL to be sideloaded. This component of the attack is responsible for establishing persistence on the target host via the Windows Registry, and retrieving additional malicious components, including Windows executable payloads hosted remotely on Dropbox. Various infostealers were delivered in this initial campaign, including LummaC2 and Rhadamanthys Stealer.
It was during the first wave that we also observed a change in TTPs: the threat actors shifted to updated Python-based payloads instead of Windows executables.
Attacks leveraging the updated Python-based payloads are initiated in the same manner: delivery of a large archive containing the signed copy of Haihaisoft PDF Reader, alongside the malicious DLL to be loaded.
Upon execution, the malicious DLL creates a .CMD script Evidence.cmd in the current directory, which orchestrates all subsequent steps in the attack chain. The .CMD script utilizes certutil to extract an encrypted RAR archive embedded inside a malformed PDF.
This command leads the Edge browser to open the PDF file, though this results in an error message as the file is not a valid PDF. Subsequently, the packaged WinRAR utility–masquerading as images.png–extracts an embedded RAR archive using decoded command lines. This process took several minutes and caused sandbox analysis to time out in several cases, which led to false negative results.
images.png x -pS8SKXaOudHX78CnCmjawuXJAXwNAzVeK -inul -y LX8bzeZTzF5XSONpDC.rar C:\Users\Public\LX8bzeZTzF5XSONpDC
This extracts several Python dependencies, including a legitimate Python 3.10 interpreter renamed svchost.exe and a malicious Python script named Photos, which are then executed. This step sets a Registry Run key to ensure the payload will run each time the computer starts.
In July 2025, our partners at Beazley Security’s MDR shared initial indications of a new campaign closely mirroring the infection chain and TTPs we’d observed. This iteration notably improves their operational maturity and additional functionality.
The large archive attached to the phishing lure contained:
A legitimate, signed Microsoft Word 2013 executable
A malicious DLL, msvcr100.dll, that is sideloaded by the Microsoft Word 2013 executable
Additional files and later-stage payloads within a supporting directory named “_”.
While similar to the April campaign, the July wave introduces more sophisticated file naming to increase evasion and leverages non-malicious decoy documents opened to ensure the user remains unsuspecting.
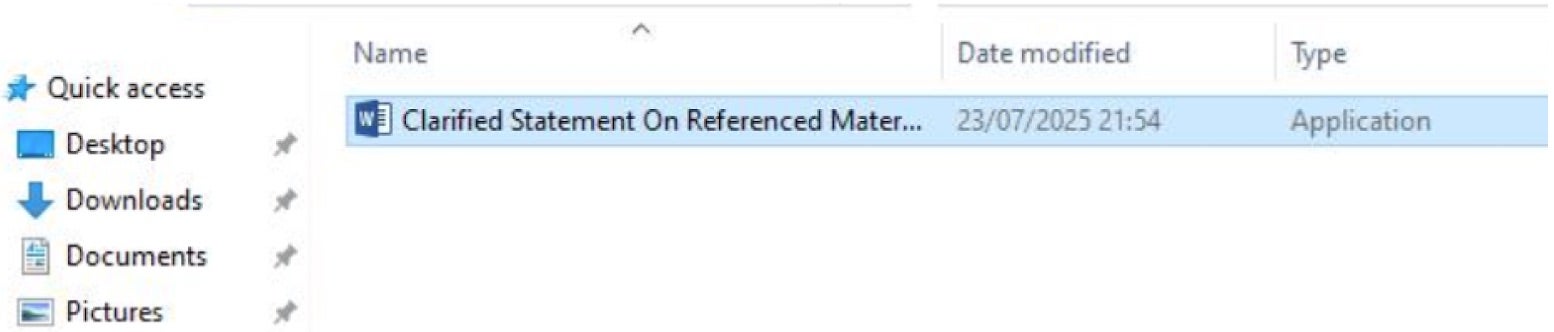
The Microsoft Word 2013 binary is renamed to appear to the user as a Word document:
Screenshot of renamed Word 2013 executable to lure the user
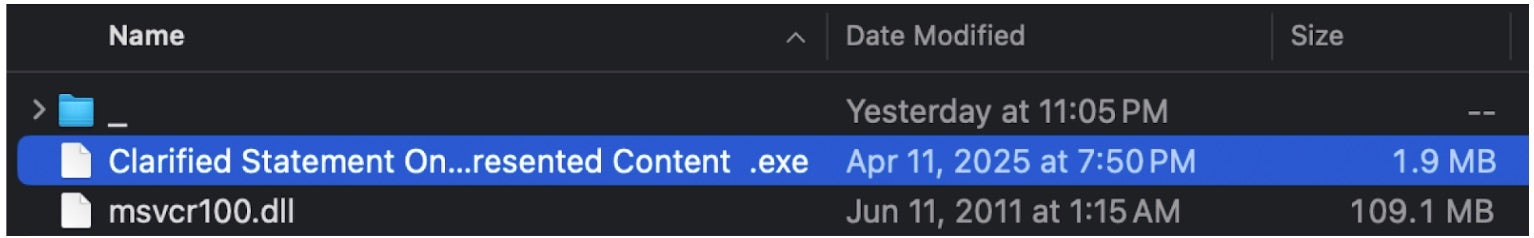
The other files extracted from the archive are hidden from the user in Windows Explorer but shown below:
Extracted contents of the archive, including hidden files
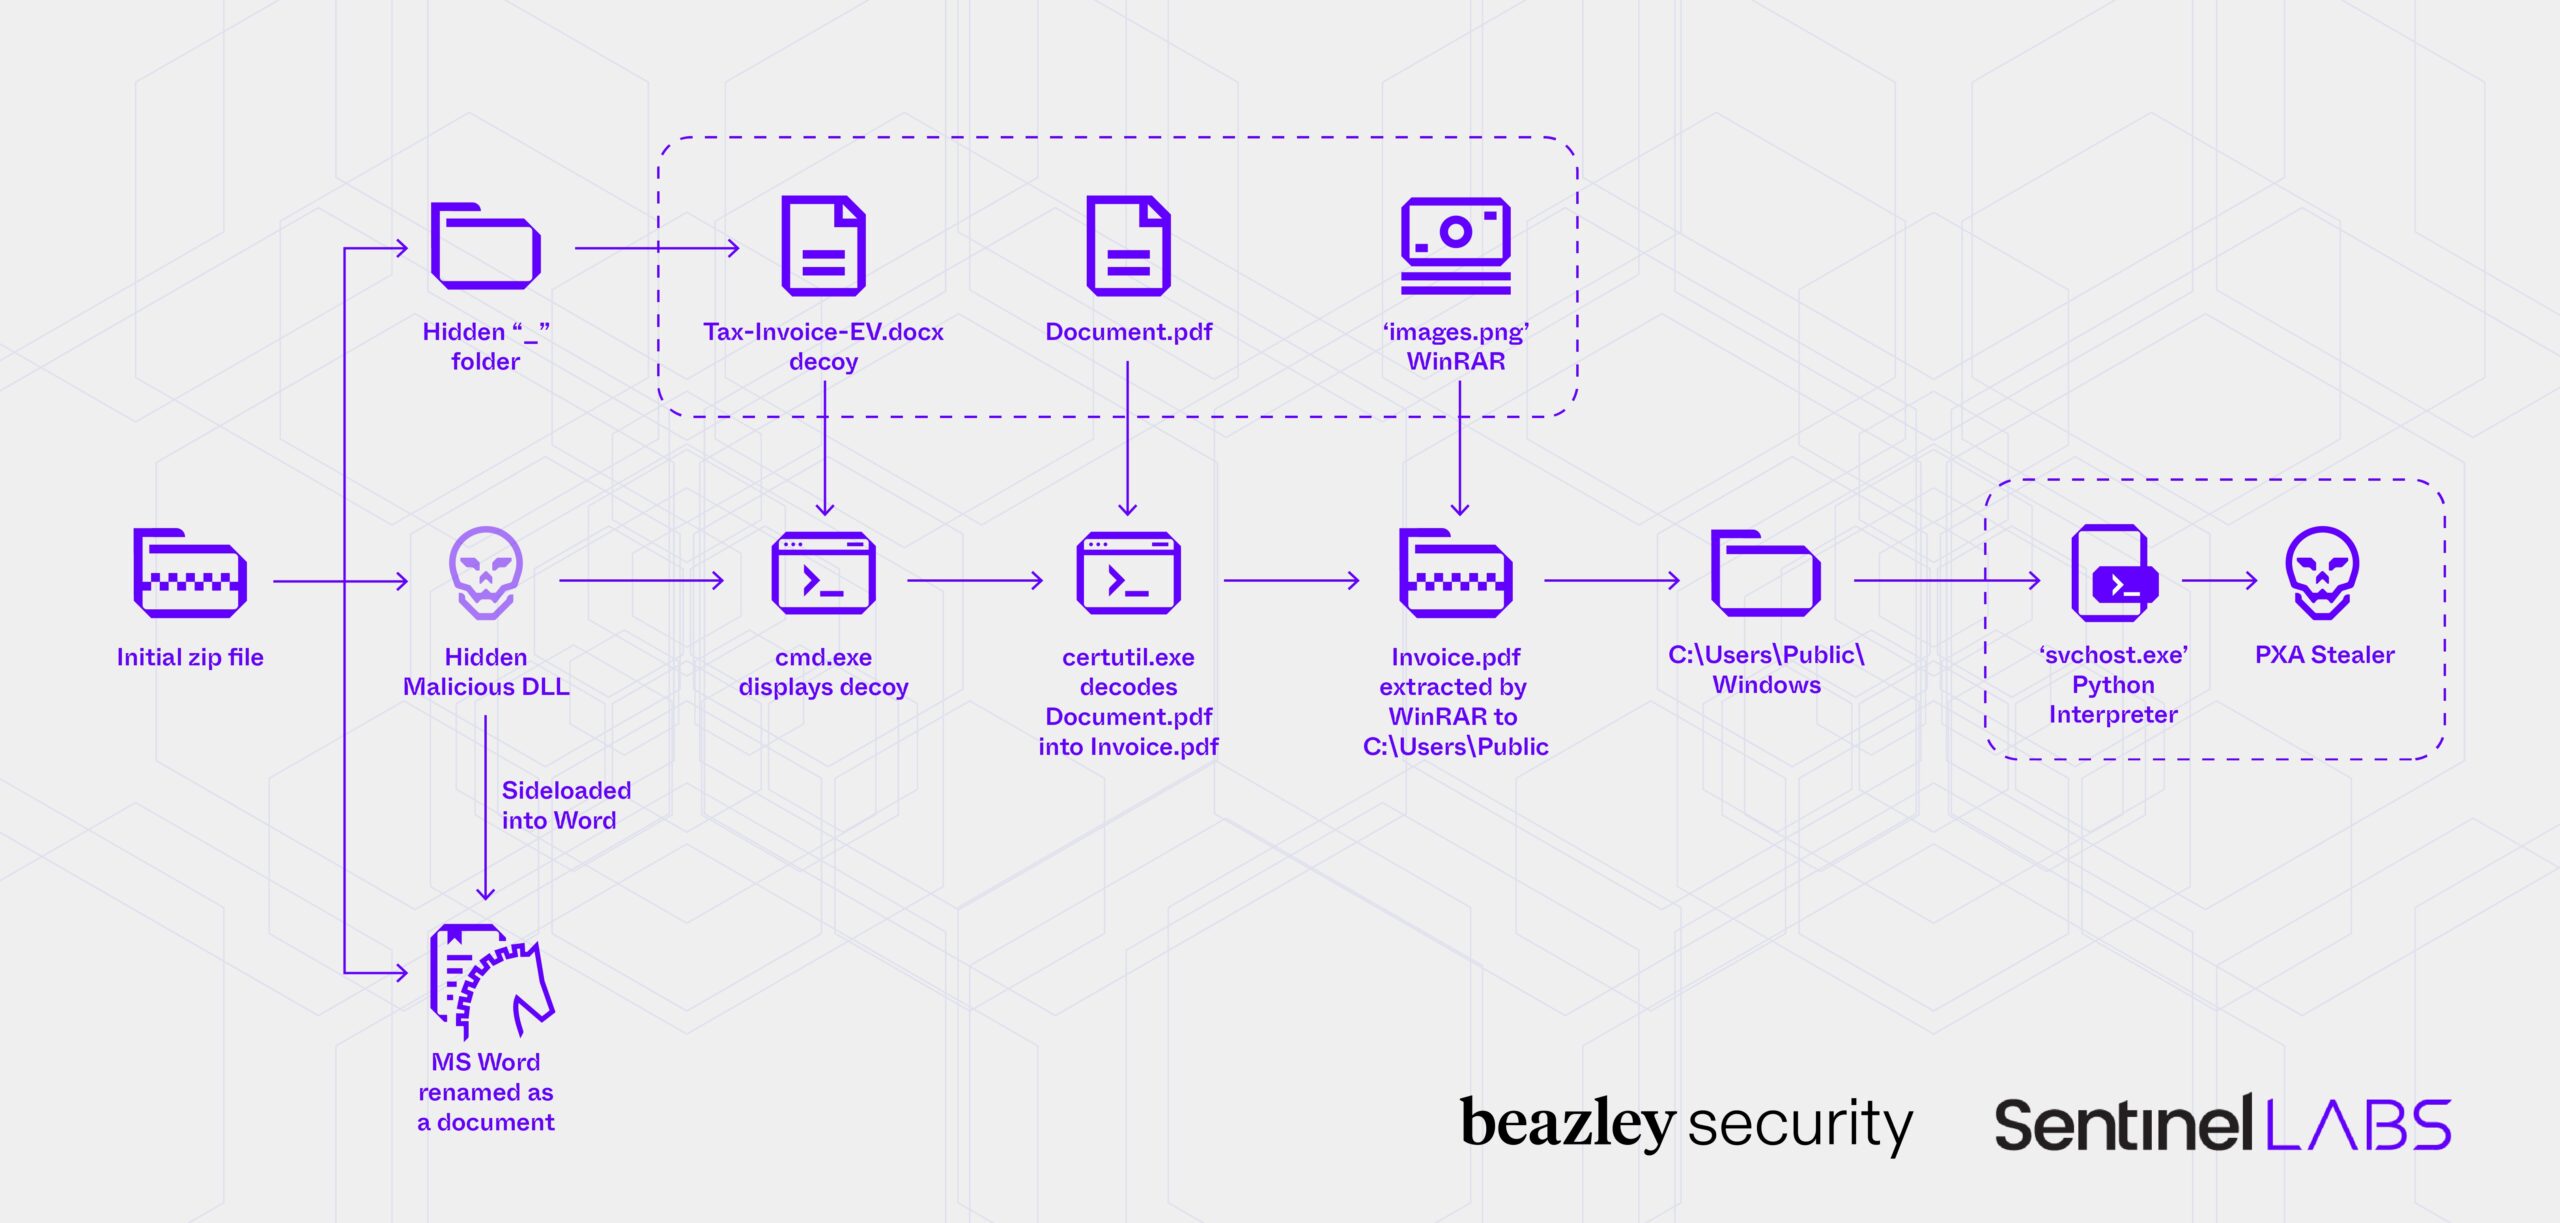
When the victim opens the Word executable, Windows loads the malicious msvcr100.dll since the OS searches for the filename in the local directory before system directories. The sideloaded DLL then launches a hidden instance of Command Prompt and begins a multi-stage chain of activity:
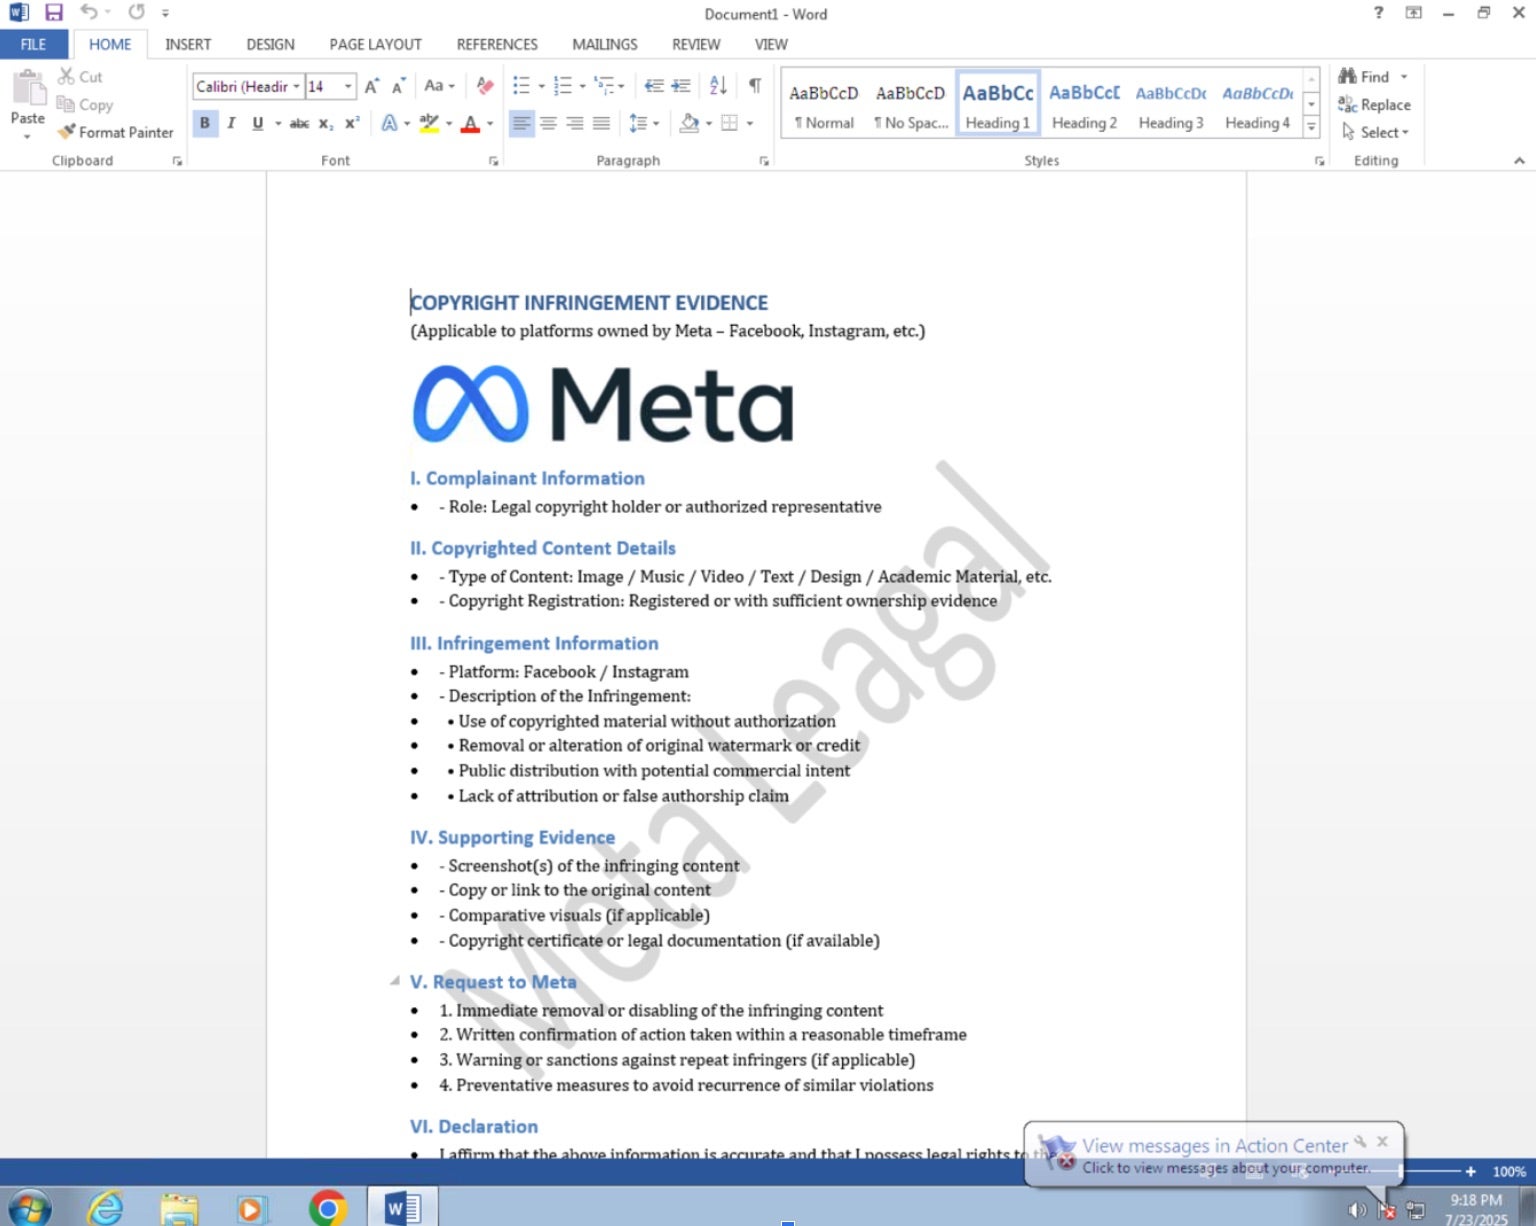
First, Word launches a benign decoy document named Tax-Invoice-EV.docx, which displays a fake copyright infringement notice to the victim. We believe this document doubles as an anti-analysis feature by introducing a non-malicious file into the attack chain, which potentially wastes security analysts’ time. The document lacks macros or other scriptable objects.
Screenshot of the non-malicious decoy document
Next, like the previous activity, certutil is used to decode a file from the “-“ folder into a new encrypted zip archive that is deceptively named with a PDF file extension, Document.pdf for example:
certutil -decode Document.pdf Invoice.pdf
Then, a legitimate WinRar executable also hosted in the “-“ folder renamed images.png is used to unpack the archive:
images.png x -ibck -y -poX3ff7b6Bfi76keXy3xmSWnX0uqsFYur Invoice.pdf C:\\Users\\Public
The second archive contains a portable Windows Python interpreter, several Python libraries, and a malicious Python script. The Python interpreter is renamed to svchost.exe and launches a heavily obfuscated Python script again disguised as images.png, followed by the $BOT_ID argument.
The final payload is an updated version of PXA Stealer. PXA Stealer is a Python-based infostealer which first emerged in 2024. PXA is primarily seen in Vietnamese-speaking threat actor circles. The malware targets sensitive information including credentials, financial data, browser data and cookies, and cryptocurrency wallet details. As detailed below, a wide variety of applications and data types within these categories are supported by PXA Stealer. PXA Stealer is capable of exfiltrating data via Telegram, as has been observed in prior campaigns.
Similar to prior campaigns, the newly observed PXA Stealer payloads are capable of identifying, packaging, and exfiltrating data from an extensive list of applications and interfaces on infected systems. Exfiltration continues to be handled via Telegram, with specific Telegram BOT IDs and Tokens identified as tied to these more recent campaigns.
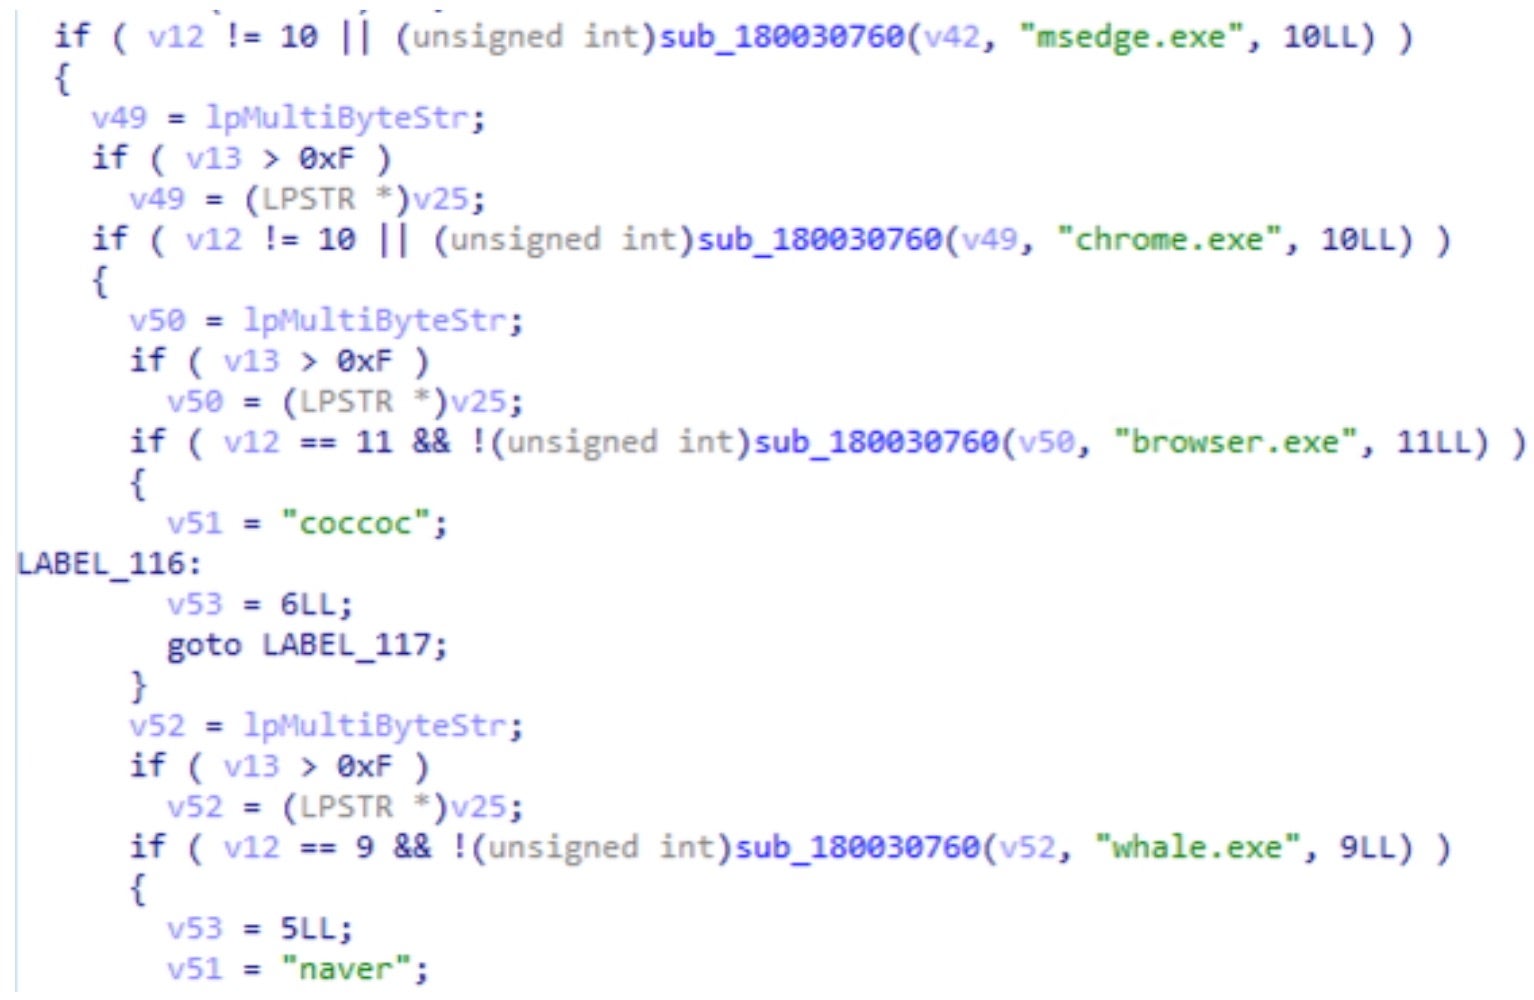
The new variant of PXA Stealer will enumerate Chromium/Gecko browsers, decrypt any saved passwords, cookies, stored personally identifiable information (PII), autofill data, and any authentication tokens. The infostealer will also attempt to inject a DLL into running instances of browsers such as Chrome, targeting Chrome’s App-Bound Encryption Key to defeat the internal encryption schemes within Chrome. The DLL injected during the July campaign targets MSEdge, Chrome, Whale, and CocCoc browsers.
Browsers targeted by the injected DLL from the July campaign
The infostealer also grabs files from dozens of desktop cryptocurrency wallets, VPN clients, Cloud-CLI utilities, connected fileshares, as well as applications such as Discord, and much more.
The collected data is packaged into ZIP archives then exfiltrated to a specific Telegram bot via Cloudflare Worker relays. There are also conditions where the malware will reach out to external sources for additional Python payloads, such as 0x0[.]st, a Pastebin-like temporary file hosting resource. Other analyzed PXA Stealer payloads support stealing data from the following browsers:
360Browser
Chromium
Opera Crypto
360 Extreme Browser
CocCoc
Opera GX
Aloha
CryptoTab
QQBrowser
Amigo
Dragon
Sidekick
Arc
Edge
Slimjet
Avast
Epic
Sogou
AVG
Ghost
Speed360
Brave
Iridium
SRWare
Brave Nightly
Liebao
Thorium
CCleaner
Liebao AI
UR Browser
Cent
Maxthon
Vivaldi
Chedot
Naver
Wavebox
Chrome
Opera
Yandex
The malware targets the following list of cryptocurrency wallet related browser extensions:
Ambire
ExodusWeb3
SafePal Wallet
Aptos Wallet
Frame
Station Wallet
Argent X
Keystone Wallet
Sui Wallet
Atomic Wallet
Leather Bitcoin Wallet
Talisman Wallet
Backpack Wallet
Ledger Live
Tonkeeper Wallet
Bitapp
Leo Wallet
TON Wallet
Bitget Wallet
Magic Eden Wallet
Uniswap Wallet
Bitski Wallet
MathWallet
Wallet Guard
Cosmostation Wallet
MyTonWallet
Zeal
Crocobit
OpenMask Wallet
Zeeve Wallet
Crypto.com
Portal DEX Wallet
Zerion
Edge Wallet
Pulse Wallet Chromium
Equal
Quai Wallet
User databases and configuration files for the following applications are targeted, many of which house sensitive data or cryptocurrency assets:
Armory
Dogecoin
Ledger Live
Atomic
Electron Cash
Litecoinwallets
Azure
Electrum
Monero
Binance
ElectrumLTC
Multidoge
Bitcoin Core
Ethereum
MyMonero
Blockstream Green
Exodus
OpenVPN
bytecoin
FileZilla
ProtonVPN
Chia Wallet
Guarda Desktop
Raven Core
Coinomi
Jaxx Desktop
Telegram
Daedalus Mainnet
KeePass
Wasabi Wallet
DashCorewallets
Komodo Wallet
Zcash
The infostealer is also capable of targeting website-specific data. The malware includes the following list of sites, for which the stealer will attempt to discover and collect credentials, cookies and session tokens. The targeted sites are primarily financial, such as FinTech services or cryptocurrency exchanges:
ads.google.com
coinomi.co.nl
korbit.co.kr
adsmanager.facebook.com
coinone.co.kr
kraken.com
binance.com
coinplug.ng
kucoin.com
bingx.com
crypto.com
lbank.com
bitfinex.com
electrum.org
mexc.com
bitget.com
exodus.com
nami.exchange
bitgo.com
gate.com
okx.com
bitmart.com
gemini.com
paypal.com
bitunix.com
gopax.co.kr
probit.com
business.facebook.com
htx.com
upbit.com
bybit.com
huobi.com
whitebit.com
coinbase.com
hyperliquid.xyz
xt.com
The specific Telegram Bot Token, and associated Chat ID, identified in the samples from July are:
Data is exfiltrated to Telegram via connection via Cloudflare workers. The specific Cloudflare DNS address is:
Lp2tpju9yrz2fklj.lone-none-1807.workers[.]dev
We reported this abuse of Cloudflare Workers to Cloudflare, and we thank their team for taking immediate action to disrupt this malicious infrastructure.
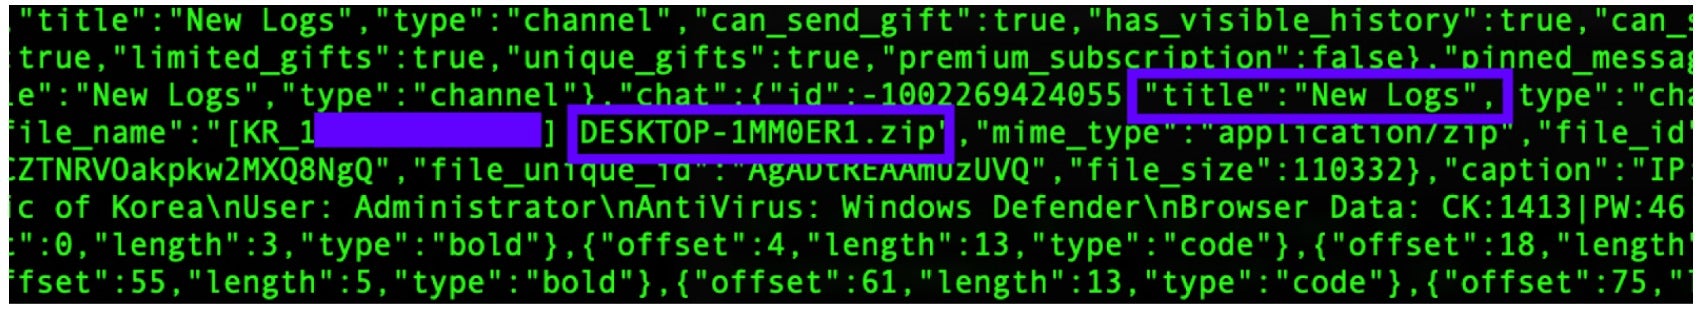
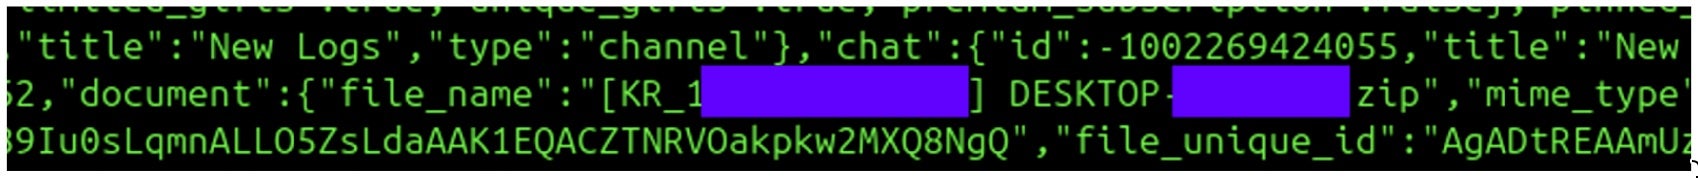
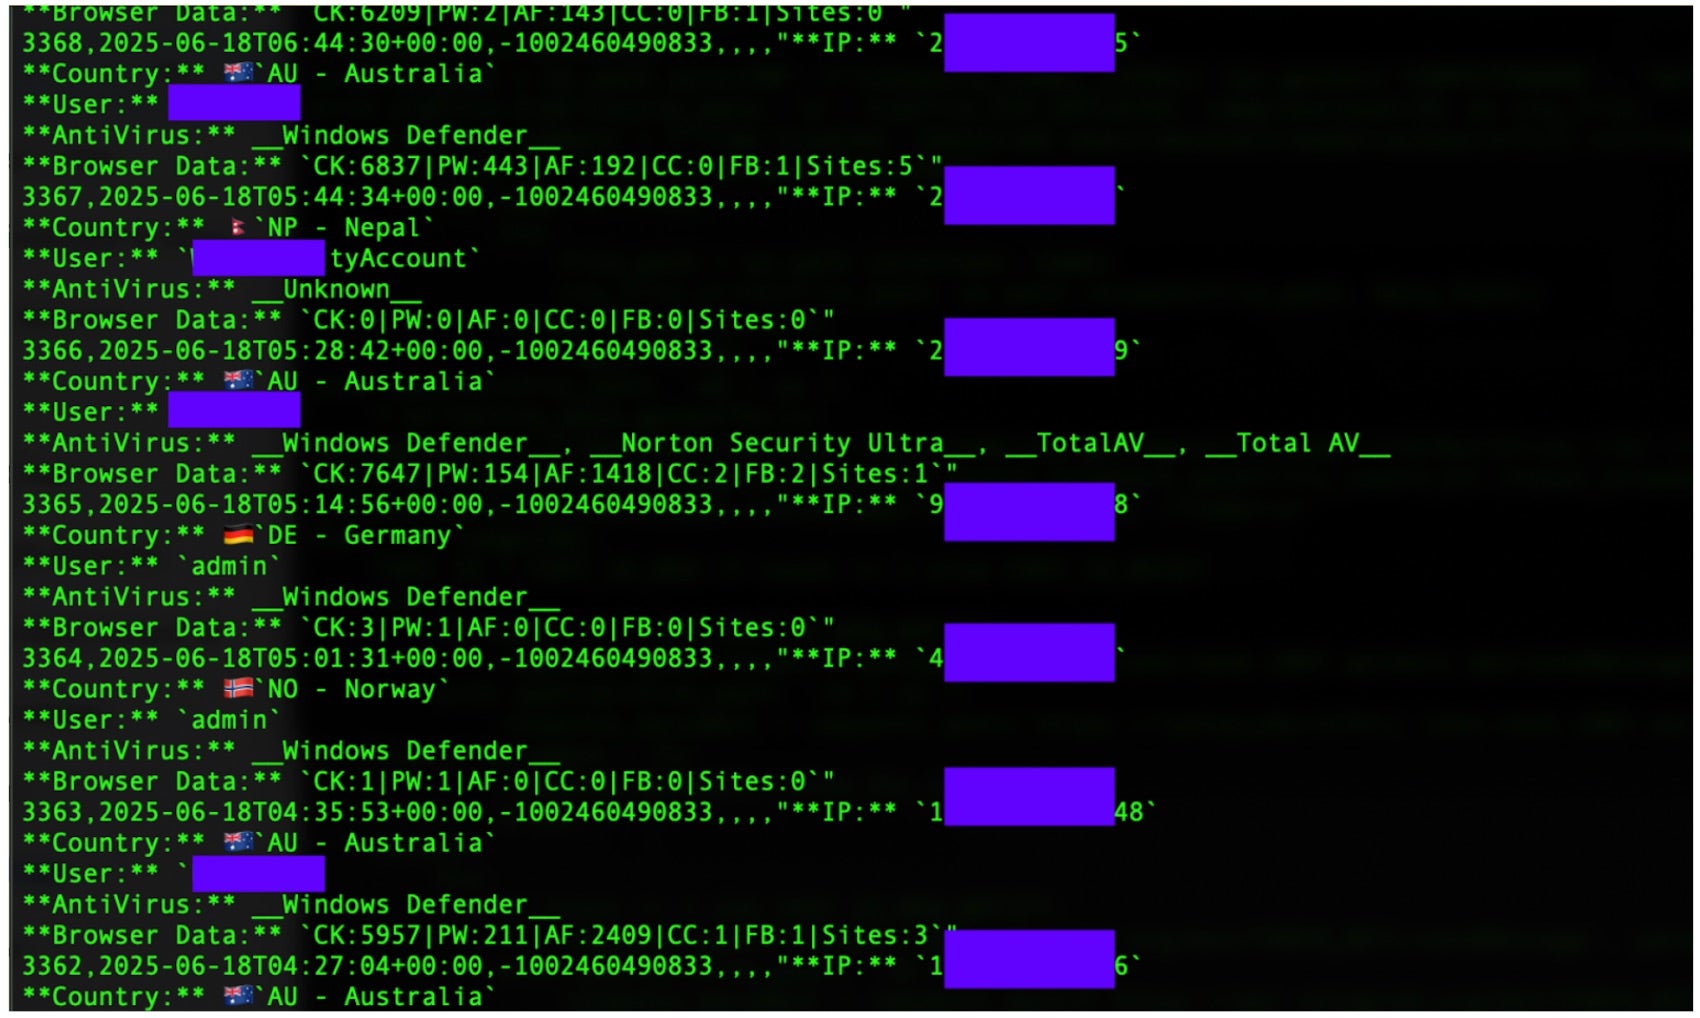
Each of the final PXA Stealer payloads corresponds to a Telegram Bot Token and ChatID combination. Each variant we analyzed is associated with the same Telegram Bot Token (7414494371:AAHsrQDkPrEVyz9z0RoiRS5fJKI-ihKJpzQ) although the ChatIDs vary. Additionally, there can be multiple ChatIDs, which correspond to a Telegram channel, tied to each payload. Each bot is tied to as many as 3 Telegram channels. One channel, typically denoted with the New Logs string, receives exfiltrated data contained in zip archives uploaded from victims’ machines, along with log/ledger style data for each victims’ exfiltrated data set. Specific entries also indicate the victim’s geographic location, IP address and other contextual data.
PXA Stealer log entries show counts for the types of data within: CK:2868|PW:482|AF:606|CC:0|FB:1|Sites:4|Wallets:0|Apps:1
The stealer data types include:
CK = Cookies
PW = Passwords
AF = AutoFill data
CC = Credit Card data
FB = Facebook Cookies
TK = Authentication Tokens
Sites = Domains / Site specific data
Wallets = Crypto Wallet data
Apps = Application specific data (ex: private messenger chat history and keys)
Exfiltrated Victim Data from MRB_NEW_VER_BOT via PXA Stealer
Each bot will also have an associated ‘Reset’ and ‘Notifications’ channel as well. The ‘Notification’ channels appear to allow operators to automate their communications process when new victim logs are uploaded or otherwise obtained. The ‘Reset’ channels appear to be used in similar manner to the ‘New Logs’ channels, storing newly exfiltrated victim data.
While all analyzed variants share the same Bot Token ID, we have observed multiple ChatIDs across the New Log/Reset/Notification combinations across this stealer’s ecosystem. The observed Bots-to-ID sets include:
The firstname field on this bot decodes to a string of Cyrillic text “ВИДЕО С ЛАЙКА”. This roughly translates to ‘Video for/with/of Laika,” though the significance of this string is unclear.
Telegram Abuse and Attribution
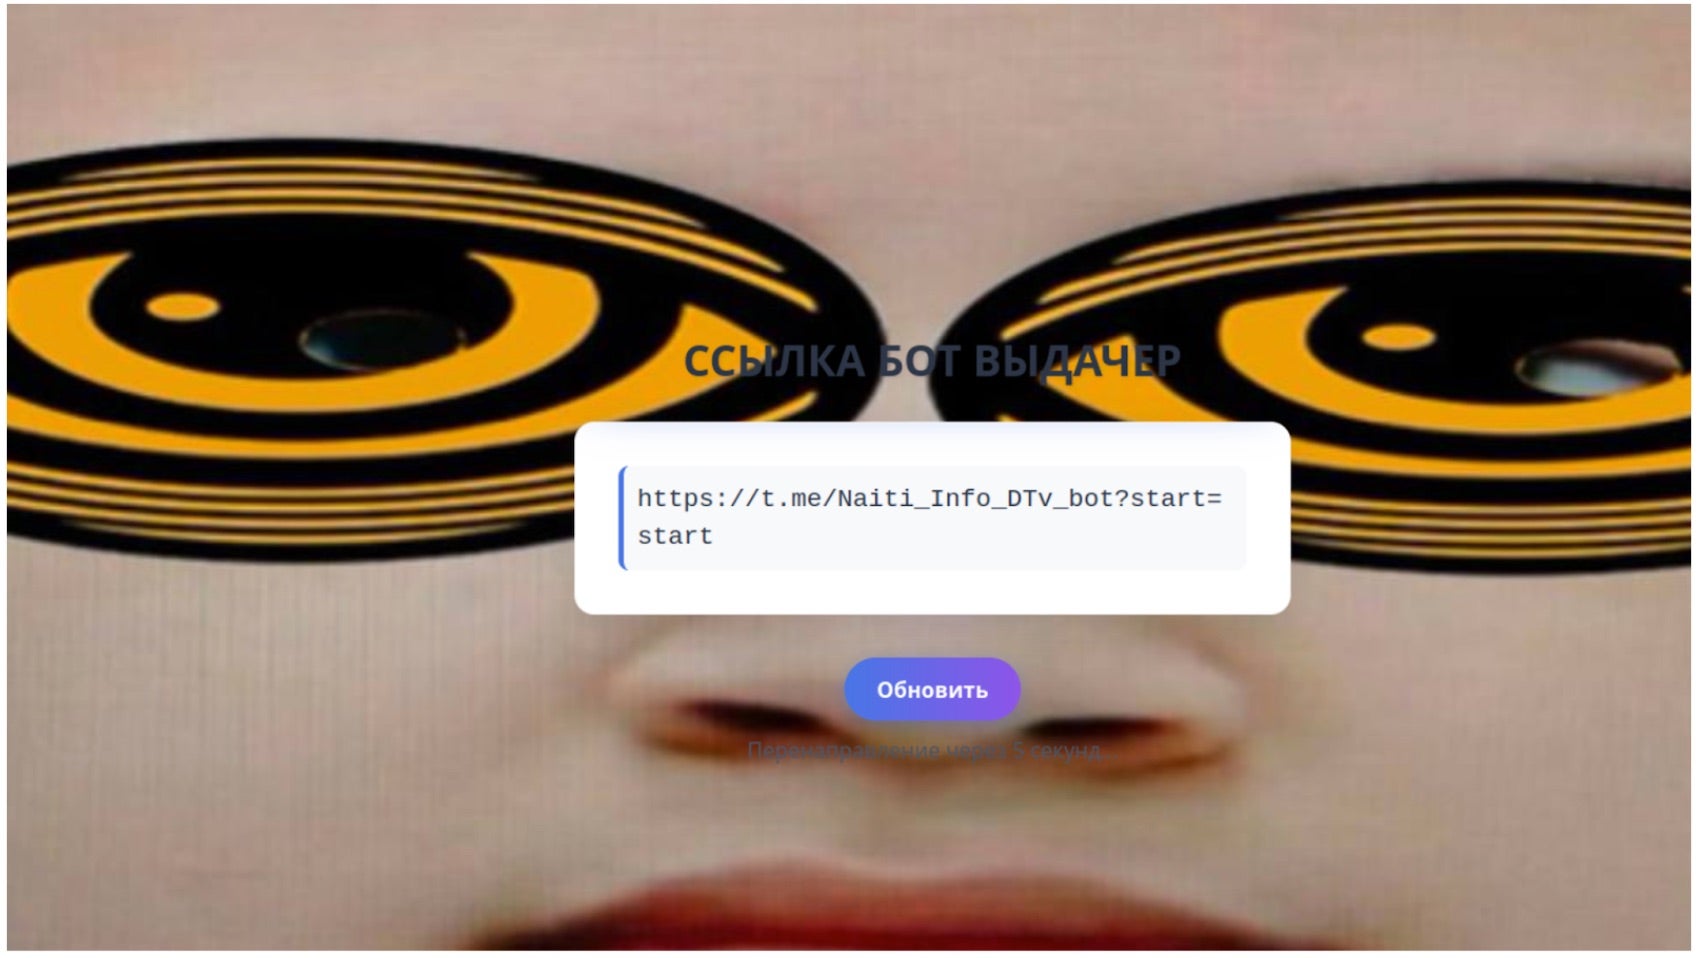
The later-stage dropper component is responsible for parsing target Telegram URLs based on a string gathered from a prescribed Telegram ChatID. This string is then combined with the base URL for either paste[.]rs or 0x0[.]st to retrieve the next batch of obfuscated Python code.
Multiple identifiers were observed across the multitude of analyzed samples. The most prominent we observed are:
ADN_2_NEW_VER_BOT
DA_NEW_VER_BOT
JAMES_NEW_VER_BOT
JND_NEW_VER_BOT
MR_P_NEW_VER_BOT
MR_Q_NEW_VER_BOT
KBL_NEW_VER_BOT
MRB_NEW_VER_BOT
These identifiers are visible within the commands launched by the side-loaded DLL described above.
cmd /c cd _ && start Tax-Invoice-EV.docx && certutil -decode Document.pdf Invoice.pdf && images.png x -ibck -y -poX3ff7b6Bfi76keXy3xmSWnX0uqsFYur Invoice.pdf C:\\Users\\Public && start C:\\Users\\Public\\Windows\\svchost.exe C:\\Users\\Public\\Windows\\Lib\\images.png MR_Q_NEW_VER_BOT && del /s /q Document.pdf && del /s /q Invoice.pdf && exit && exit)
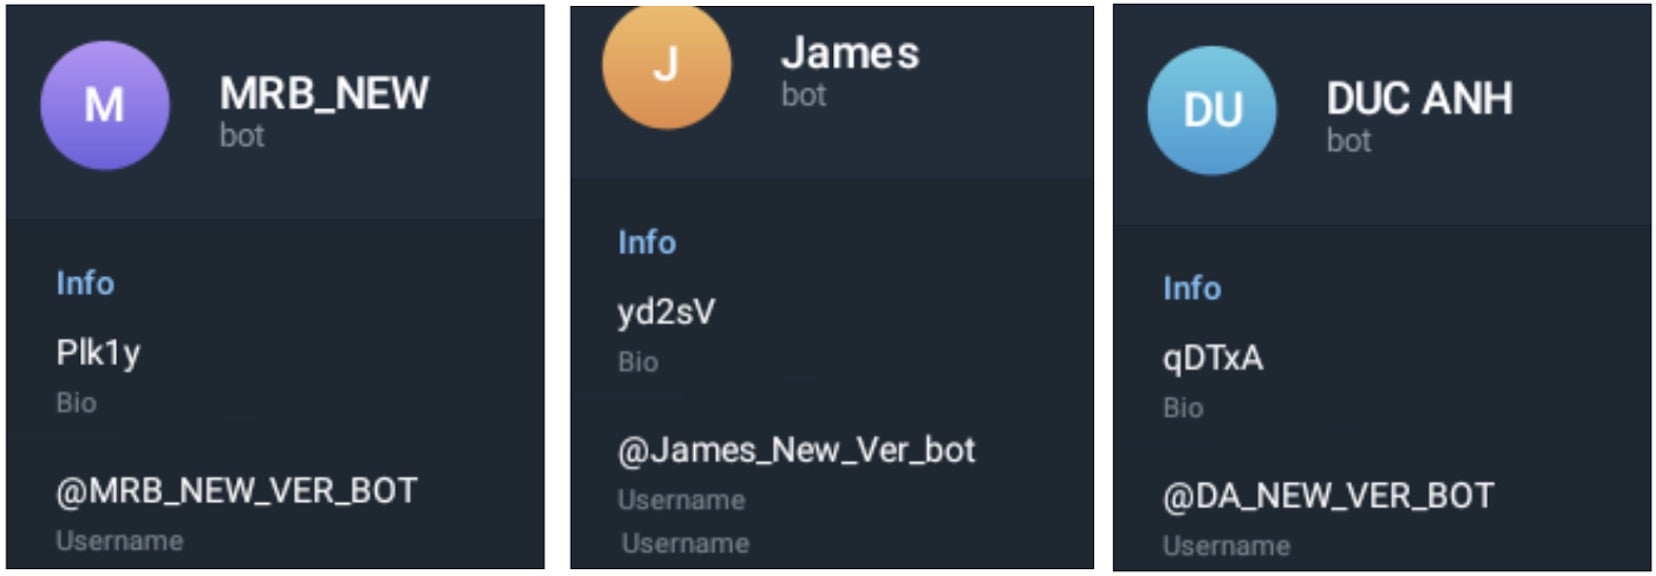
Each of these _NEW_VER_BOT identifiers corresponds to a Telegram User ID. The profile names resemble a bot, but are actually user accounts:
Bio and Info fields from Telegram profiles masquerading as bots
When retrieving files from paste[.]rs, the corresponding strings are concatenated with the hxxps://paste[.]rs or hxxps://0x0[.]st prefix, which constructs the full download URL hosting another payload.
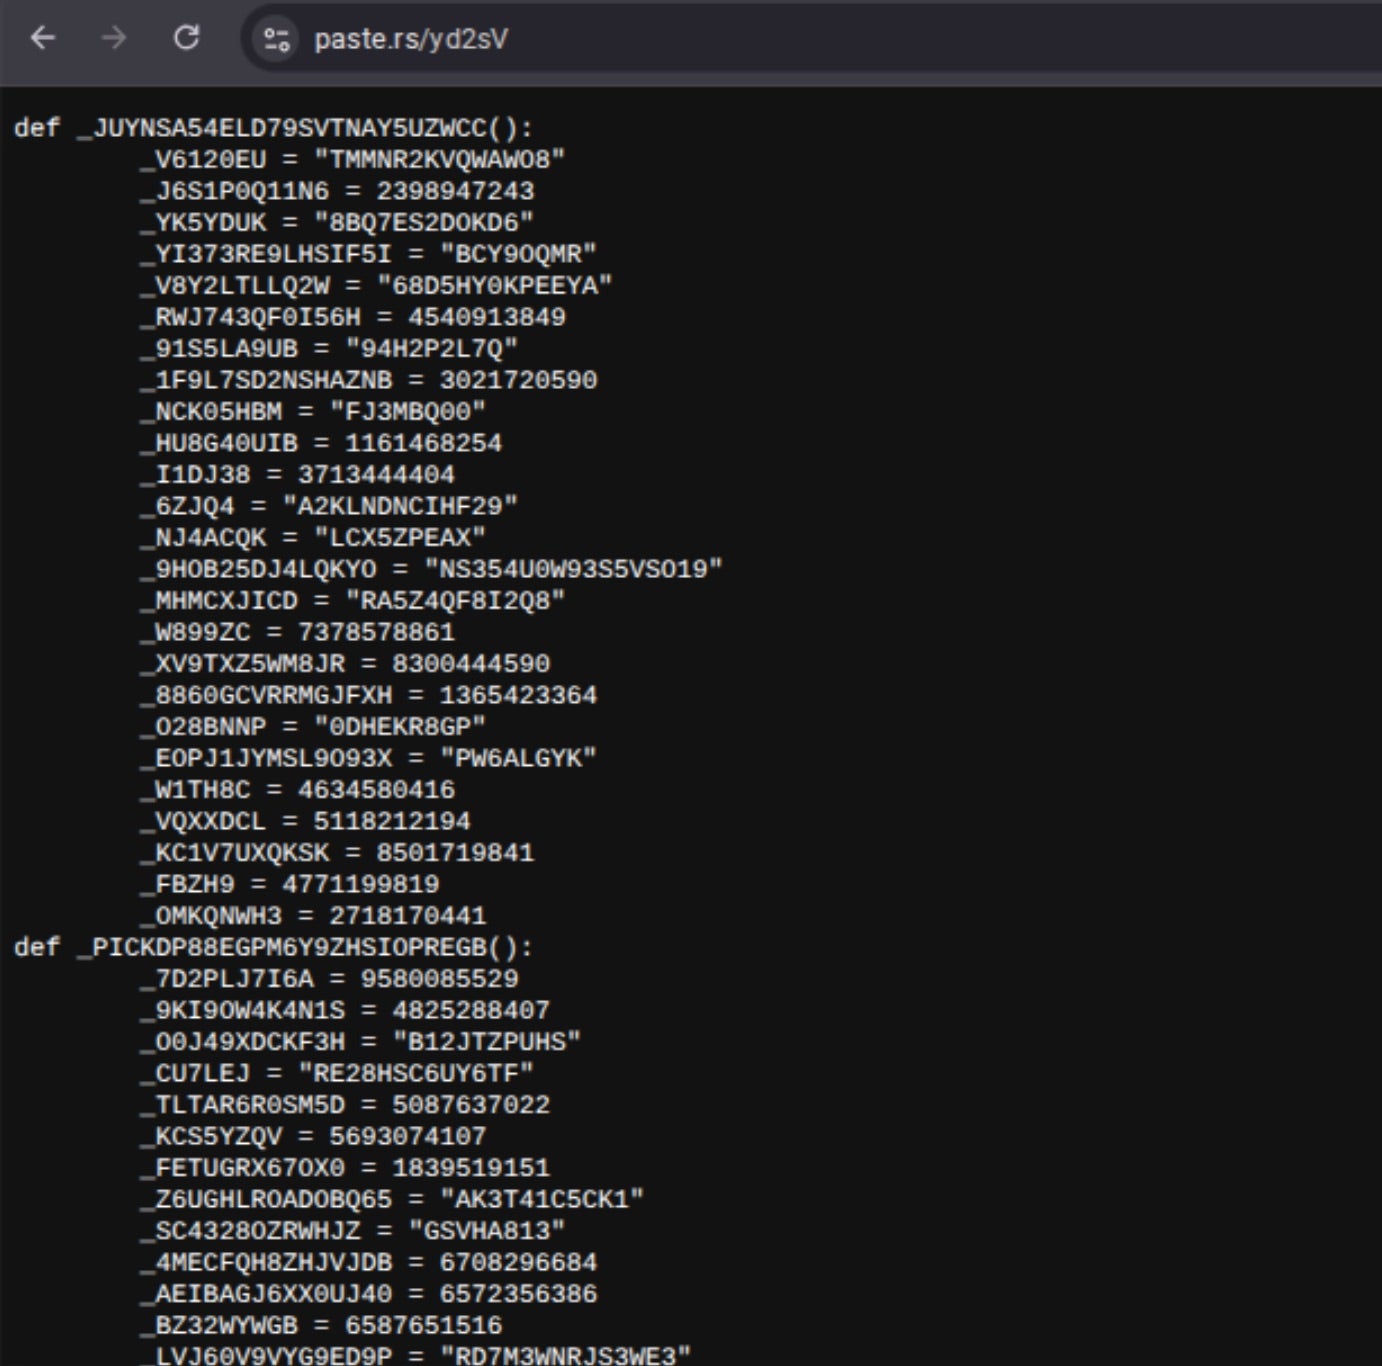
Obfuscated Python code hosted on Paste[.]rsOnce downloaded, the obfuscated Python code is decoded and executed, delivering the Infostealer component of the attack.
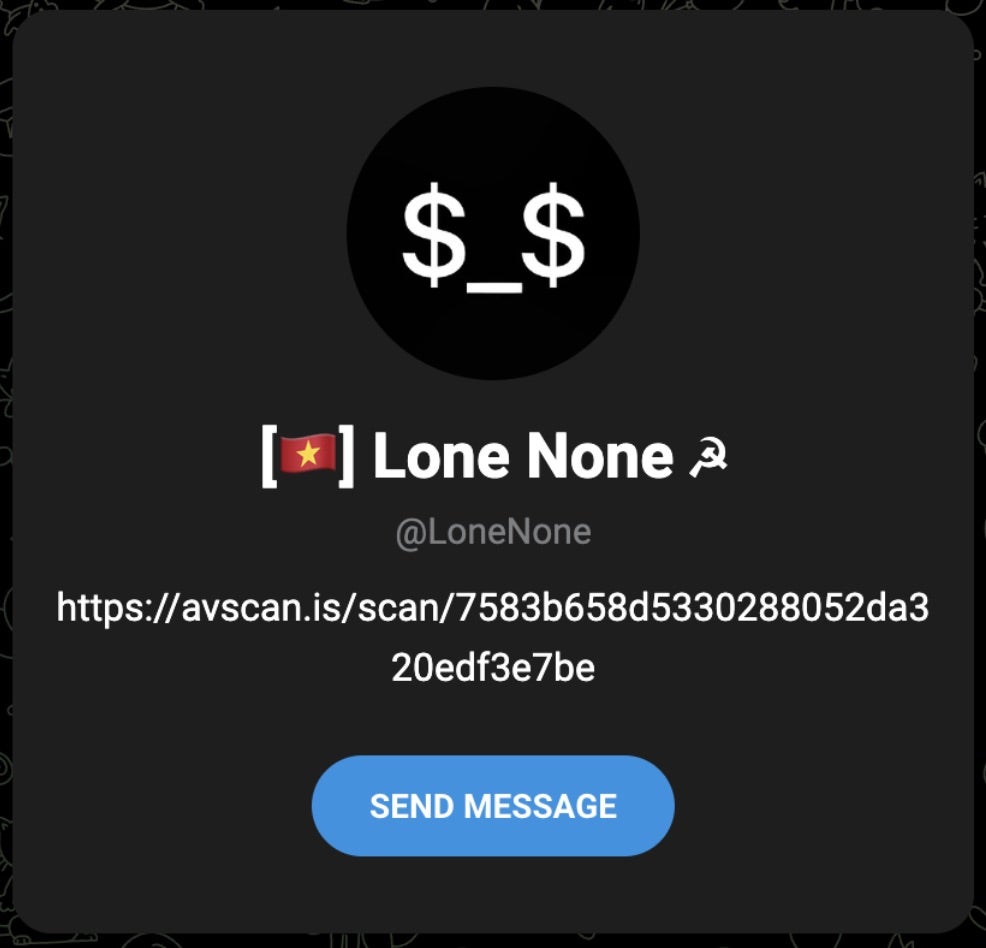
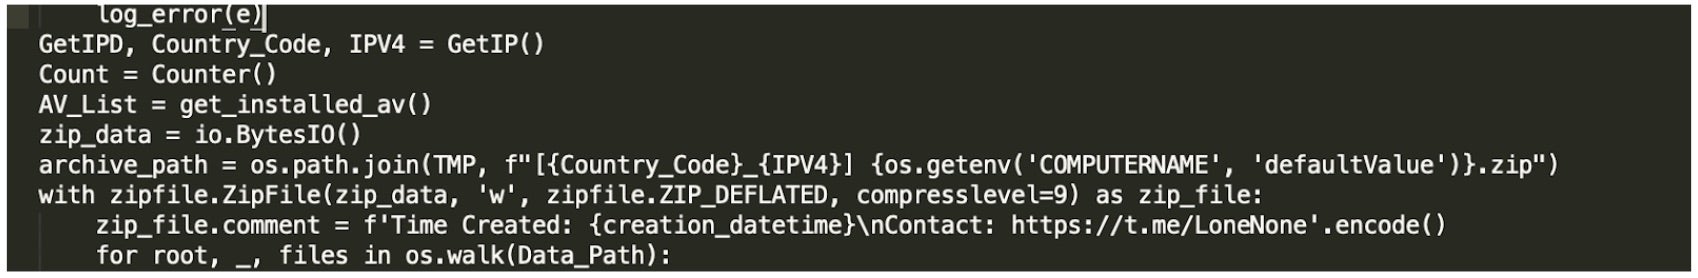
The Telegram ChatID associated with the infostealer component of this attack is “@Lonenone.” The “Lonenone” theme is also present in the Cloudflare Worker hostname lp2tpju9yrz2fklj[.]lone-none-1807[.]workers[.]dev. The profile display name contains an emoji of the Vietnam flag.
Lone None Telegram ChatIDReference to LoneNone TG channel in decoded (July) infostealer
This Telegram ChatID/Account is associated with the same threat actor using PXA Stealer as previously described by Cisco Talos. It is worth noting that there are a number of other Vietnamese-language artifacts present in these stages of the malware. For example, the aforementioned Telegram BOT IDs show ‘Duc Anh’…aka “đức anh” as display names, which loosely translates to “brother”.
PXA Stealer uses the BotIDs (stored as TOKEN_BOT) to establish the link between the main bot and the various ChatID (stored as CHAT_ID). The ChatIDs are Telegram channels with various properties, but they primarily serve to host exfiltrated data and provide updates and notifications to the operators.
PXA Stealer transmits data via HTTP POST requests to the Telegram API. Everything is handled via HTTPS, thus there is no visible Telegram process or self-contained client producing the traffic. This is one of PXA stealer’s methods of hiding exfiltration traffic from potential analysis or detection.
Prior to transferring the exfiltrated data, the stealer packages stage data into an archive using the following naming convention where CC=Country Code:
Probiv[.]gg contains a redirect to the Sherlock Telegram Bot Service, which provides a search interface for data culled from infostealers.
Telegram redirect on probiv[.]ggThe redirect leads to the Telegram landing page for SherLock1u_BOT, a provider of stolen data, and the automated services to search for specific data types or sets.
SherLock1u_BOT
We also tracked activity from the bots since April indicating targeting of victims in South Korea. The following image shows details of exfiltrated data from one Korea-based victim by the MRB_NEW_VER_BOT ID.
South Korea victim data uploaded to Telegram via PXA Stealer
Victimology
Our analysis uncovered details around victimology for several active BotIDs associated with the ongoing PXA Stealer campaign. Some of these Bots have been active since at least October 2024, and they continue to receive data from infected hosts to date.
Adonis (ADN_2_NEW_BOT) victim records
The PXA Stealer logs contain victim IP addresses that indicate there are potentially more than 4,000 unique victims from 62 countries. The top targeted countries in the analyzed set are:
Republic of Korea (KR)
United States (US)
Netherlands (NL)
Hungary (HU)
Austria (AT)
Some appear to favor specific locations, for example Adonis (ADN_2_NEW_VER_BOT) most heavily targets hosts in Israel and Taiwan, followed by South Korea and the United States.
Conclusion
The evolving tradecraft in these recent campaigns demonstrates that these adversaries have meticulously refined their deployment chains, making them increasingly more challenging to detect and analyze. The July 2025 attack chain in particular illustrates a highly tailored approach engineered to bypass traditional antivirus solutions, delay execution in sandboxes, and mislead SOC analysts who review process trees or EDR data by using byzantine delivery and installation methods.
This campaign’s medley of legitimate applications and non-malicious decoy documents is designed to mislead users and SOC analysts alike. The actors reinforce this facade by naming a user-space folder to mimic the system directory Windows and disguising a Python interpreter as svchost.exe to blend into typical system activity. In parallel, they use files with familiar extensions, such as PNG and PDF, to conceal embedded WinRAR executables and ZIP archives, layering their evasion techniques to mislead users, investigators, and traditional detection technologies.
PXA Stealer, and the threat actors behind it, continue to feed the greater infostealer ecosystem. It is also important to note that PXA, along with similar stealers like Redline, Lumma, and Vidar, each produce data that can be neatly ingested into data monetization ecosystems. The sales-oriented services like Sherlock, such as Daisy Cloud and Moon Cloud, take data harvested by these stealers directly from the bots. The more mature services then normalize the sets of exfilterated data to make it ‘sales-ready’. The idea behind leveraging the legitimate Telegram infrastructure is driven by the desire to automate exfiltration and streamline the sales process, which enables actors to deliver data more efficiently to downstream criminals. The developer-friendly nature of Telegram–combined with the company’s laissez-faire attitude towards cybercrime–underscores the crucial role that Telegram plays in the holistic cybercriminal ecosystem.

 Entrar