❌

Visualização de leitura

GitHub Launches Copilot Fusion to Automatically Select and Combine AI Models for Coding

GitHub has launched Copilot Fusion, a runtime model router and orchestrator that automatically selects AI models and execution patterns for coding tasks. Instead of requiring developers to choose a model for each step, Fusion coordinates reasoning, code generation, debugging, and review, ultimately providing a single cohesive response. The feature is available across all Copilot plans. […]

The post GitHub Launches Copilot Fusion to Automatically Select and Combine AI Models for Coding appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Compromise OVHcloud GitHub Repository to Distribute Secret-Stealing Malware

OVHcloud has reported a supply-chain attack involving its command-line interface (CLI) repository. An attacker exploited a developer’s GitHub account to distribute a malicious binary designed to steal sensitive information from users’ disks. CEO Octave Klaba confirmed the incident on October 19, 2026, after a customer reported it. The company identified the compromised release at 14:47 […]

The post Hackers Compromise OVHcloud GitHub Repository to Distribute Secret-Stealing Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Meta GitHub Repositories Compromised, Exposing Software Code and Employee Personal Data

Meta has revealed a breach of a GitHub repository that exposed software code and personal information belonging to about 1,500 individuals, most of whom are U.S. employees. The company began notifying affected individuals on October 13, after discovering the intrusion several weeks earlier, which involved the theft of an employee’s credentials. According to Meta’s statement […]

The post Meta GitHub Repositories Compromised, Exposing Software Code and Employee Personal Data appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Researchers Find 543,699 Active Credentials Leaked in Public GitHub Repos

Security researchers have identified 543,699 unique credentials that remain valid despite being exposed in public GitHub repositories. This highlights a persistent failure to revoke secrets once they enter source code. These credentials were verified as active in July 2026, even though many had been publicly accessible for years. Researchers at Truffle Security examined The Stack […]

The post Researchers Find 543,699 Active Credentials Leaked in Public GitHub Repos appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
GitHub AI Agent Uncovers 24 Android App Vulnerabilities

GitHub Security Lab has disclosed 24 vulnerabilities in Android applications discovered through its open-source AI security agent and specialized audit taskflows. The findings highlight issues that could enable covert location tracking in the OsmAnd navigation app and account takeover attacks against Wikipedia users on Android. Kevin Stubbings, a researcher at GitHub Security Lab, developed targeted […]

The post GitHub AI Agent Uncovers 24 Android App Vulnerabilities appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
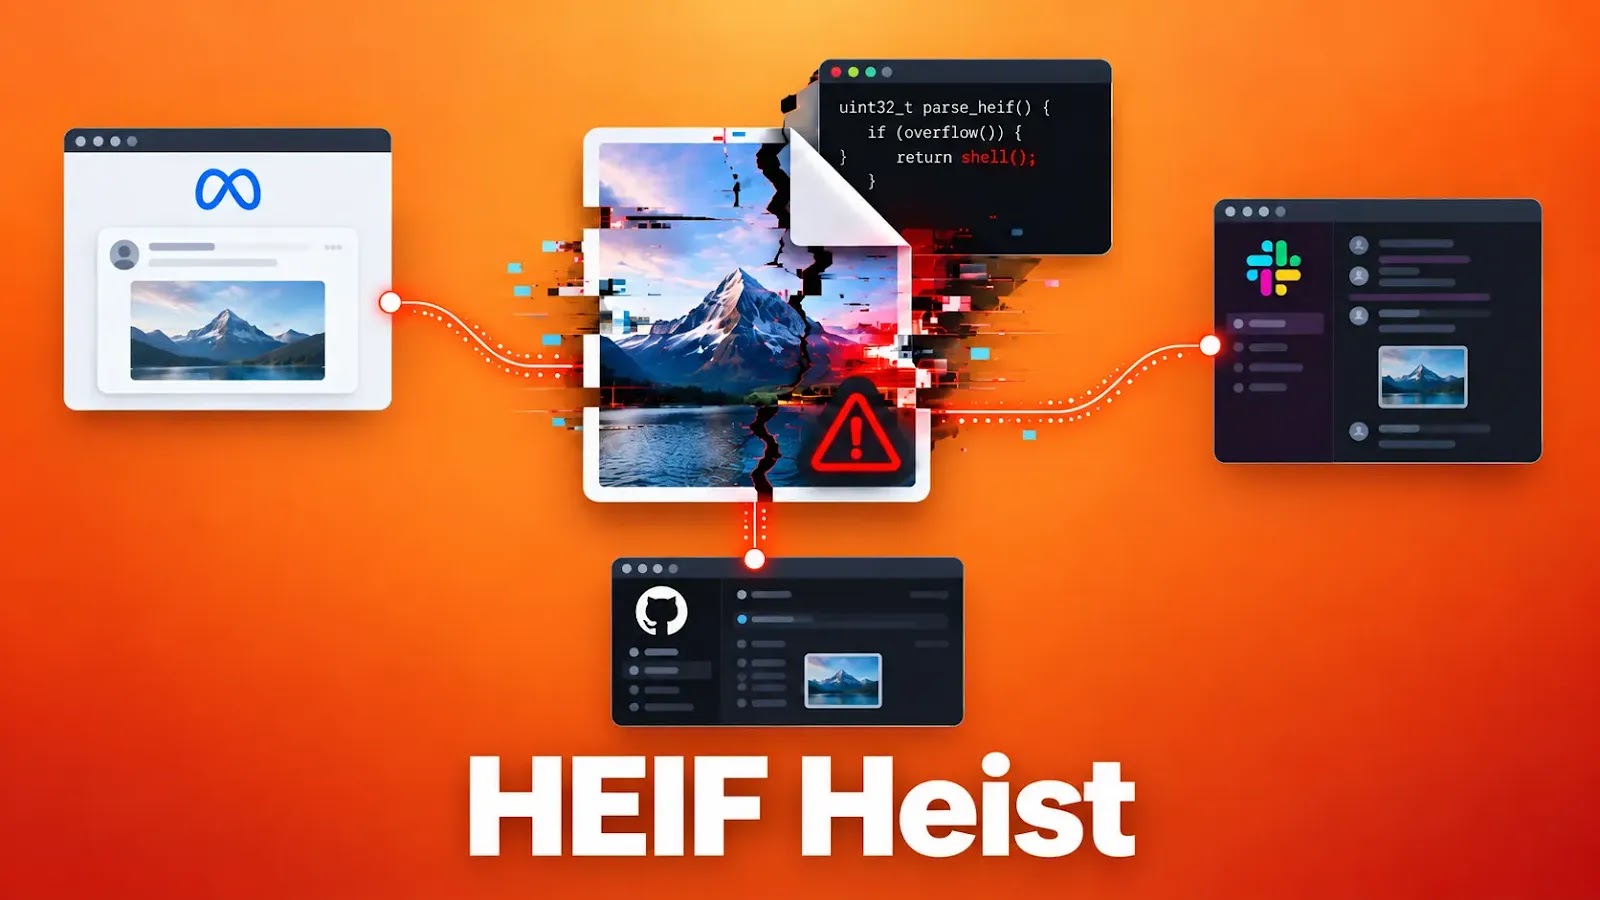
HEIF Heist Image Flaws Let Attackers Gain RCE Across Meta, Slack and GitHub Enterprise

“HEIF Heist,” a broad class of image-processing attack paths that could allow threat actors to turn malicious HEIF, HEIC, and AVIF uploads into remote code execution, sensitive-data exposure, and account compromise across major technology and enterprise platforms. The research, published by Hacktron, highlights a familiar but increasingly dangerous supply-chain weakness: applications often trust native image-decoding […]

The post HEIF Heist Image Flaws Let Attackers Gain RCE Across Meta, Slack and GitHub Enterprise appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌