As AI exposes flaws in IT systems and geopolitics plays out on the cyber frontline, some experts say the events of recent weeks could soon be a common occurrence
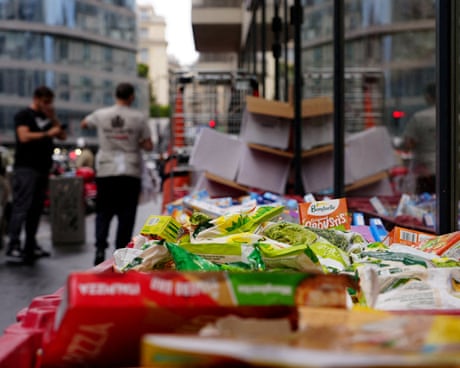
Alex Pearce was doing the morning rounds at his fruit and vegetable wholesale business in London on Monday last week when he noticed something odd.
The defrost light on refrigeration unit 2 was on, and the panel reading was 150C. Unit 4 was the same.
Separate actions also take place outside fence and across Europe in backlash against impact of AI boom
Activists have stormed the site of a Microsoft datacentre being built in Amsterdam, as the backlash to the social and environmental harms of the AI boom spreads across Europe.
Protesters from Geef Tegengas, a Dutch direct action group, clashed with police while breaking into a construction site at Westpoort, Amsterdam, where some members climbed a crane, lit flares and tied helium balloons to equipment.
Hackers altered refrigeration controls at three French blood service sites, but staff protected plasma supplies and prevented damage to blood products.
ASEC Blog publishes Ransom & Dark Web Issues Week 1, November 2026 FBI Seizes Domain of Bulletproof Hosting Service Virtualine Internal Data of a Saudi ERP and IT Solutions Company Offered for Sale Cyberattacks on Supermarket Refrigeration Systems Spread Across 12 European Countries OBSOFT Claims Data Extortion and Data Destruction […]
Supermarkets in Sweden, Belgium, Luxembourg, Ireland and Estonia were throwing out spoiled food on Monday after their fridges and freezers stopped doing their job. In at least two cases, temperatures had been pushed to 50 degrees Celsius (122 degrees Fahrenheit). The apparent supermarket cyberattack came only weeks after attackers took control of cooling equipment in hundreds of stores across France.
That raises an obvious question: why are supermarket freezers suddenly a target, and why now?
How the Supermarket Cyberattack Unfolded Across Europe
Sweden saw some of the clearest signs of tampering. ICA Group spokesperson Gustaf Nilsson told the TT news agency that "a limited number" of stores were affected overnight by an incident involving refrigeration systems. One ICA Kvantum store in Sjöbo, in southern Sweden, was more direct. In a Facebook post, it said its fridges and freezers had been hacked and set to 50 degrees Celsius, and that staff were discarding affected products. The Coop chain also reported problems with fridges and freezers at six stores in central Sweden, according to TT, though it did not immediately share details.
In Belgium, Delhaize said an "IT incident" had affected refrigeration in several dozen stores, mostly in Belgium and a few in neighbouring Luxembourg. "In the affected stores, the range of fresh and frozen products is temporarily somewhat limited. Our distribution centers are operating normally, and there has been no disruption to deliveries to our stores," spokesperson Sarah De Meester said. Carrefour said a cyberattack targeting refrigeration had affected 15 of its more than 700 Belgian stores, and described the impact as "extremely limited.
In Ireland, Musgrave Group said refrigeration systems in 13 SuperValu stores were affected by the "cyber incident." Chilled and frozen products were removed from sale as a precaution. By Monday afternoon, the company said the incident had been "fully resolved" and that restocking of chilled and frozen ranges was "well under way."
In Estonia, refrigeration technology company Kitman Coldtech said attackers had accessed a computer controlling a client's refrigeration system and raised the temperature to 50 degrees Celsius, public broadcaster ERR reported. Chief executive Jann Mutso declined to name the store but said the attack was addressed within minutes and caused no significant damage. The Selver supermarket chain confirmed that one of its outlets was affected.
Is This Supermarket Cyberattack Linked to France?
None of the companies has publicly linked Monday's incidents to France, but the pattern is hard to miss.
Last month, attackers remotely took control of refrigeration systems in hundreds of supermarkets and independent stores across France. They pushed fridge and freezer temperatures as high as 50 degrees Celsius. French TV channel BFM reported that the attackers appeared to trigger a forced defrost option, which kept units heating instead of cooling. By morning, tonnes of food had perished. Some equipment had melted, and in some stores the heat had sparked fires.
Five of France's major retail groups were hit: E.Leclerc, Intermarché, Carrefour, Monoprix and Coopérative U. At least 300 Intermarché and Netto stores were affected. Coopérative U reported more than 100 stores, Carrefour said 80, and Monoprix said about 5% of its roughly 490 stores were targeted.
Bruce Hallas, CEO at Re-thinking the Human Factor, who lives in France, noted on LinkedIn that current estimates sit around 400 stores. He added that some individual branches reported losses of about €250,000. Retailers say millions of euros' worth of food was spoiled, which makes food losses the most visible cost of the attack.
Why the Supermarket Cyberattack Targeted Fridges
The French case offers the strongest clue. The attack did not rely on a new exploit. It targeted ageing systems: internet-connected devices that were still online years after their manufacturer stopped supporting them. Experts say this weakness is common across retail and industry. The cyberattacks in France appeared to target old systems in particular.
Timing made the damage worse. In France, the attackers struck while shops were closed, so temperatures kept rising for hours with no one in the store to notice. Monday's incidents in Sweden also happened overnight.
Estonia shows the other side of the picture. There, the intrusion was caught within minutes and caused no significant damage. The difference between tonnes of ruined stock and almost no loss came down to how quickly someone noticed.
What We Still Don't Know
Key questions remain open. The reports do not say who is behind the attacks or what they want. The full scale is also unclear. Estimates for France range from around 400 to more than 500 stores, and ICA has not said how many of its Swedish stores were hit. The chains affected on Monday have not confirmed whether their equipment shares the ageing, unsupported setup seen in France.
What is clear is that the same tactic has now reached at least five European countries, with fridge temperatures set to 50 degrees Celsius each time.
A new wave of fridge cyberattacks hit supermarket refrigeration systems across five European countries, raising temperatures and causing food losses.
A new wave of fridge cyberattacks has affected supermarket refrigeration systems in several European countries. Fridges and freezers suddenly rose in temperature overnight, with some incidents suspected to be caused by hackers. On Monday, November 2, Ahold Delhaize and Colruyt reported an IT incident affecting dozens of stores in Belgium and Luxembourg. Swedish supermarket chains ICA and Coop also reported similar problems.
“Ahold Delhaize and Colruyt said on Monday that an IT incident overnight hit fridges and freezers in dozens of stores in Belgium and Luxembourg, while Swedish grocers ICA and Coop reported similar temperature spikes, with one store blaming a cyberattack.” Reuters states.
BREAKING: Swedish grocery giant ICA, one of Sweden's largest supermarket chains, says several of its stores have been hit by a cyberattack overnight, causing refrigerators and freezers to be remotely set to 50°C.
“Problems were discovered at several grocery stores in Sweden overnight Monday.” reported Sweden Herald.
“We are aware that a limited number of stores were affected by an incident overnight that affected their refrigeration and freezer systems. Ica is providing support in handling the incident, Ica Group press officer Gustaf Nilsson tells TT.”
The latest incidents follow a similar wave of fridge cyberattacks in France last month. In mid-October, a large cyberattack hit the refrigeration systems of hundreds of French supermarkets, BFMTV revealed. The attackers targeted equipment from the Danish maker Danfoss that many French stores use to regulate their cold. Fresh and frozen stock was destroyed, and the Paris prosecutor says there were also fires.
The method is simple and nasty. Refrigeration systems have a forced defrost function that clears ice buildup, and the attackers appear to have triggered it remotely in a continuous mode, with a temperature setting of 50 degrees. The equipment heated for several hours instead of keeping goods cold, and when staff opened the fridges and freezers in the morning, a sector source told BFM, “a wave of heat” came out.
The attack caused fires and food losses. However, cybersecurity consultant Emil Olofsson of Integrity 360 told Swedish news agency TT that temperatures reached 80°C in some cases and several units caught fire. This figure differs from the one reported by police.
ICA Kvantum in Sjöbo said on Facebook that a cyberattack caused the refrigeration problems. ICA Hägerstensåsen in Stockholm was also reportedly affected. According to the Sjöbo store, the temperature inside its fridges and freezers rose to 50°C.
In Belgium, Delhaize detected unusual temperature increases in its refrigeration systems on Monday. Spokesperson Sarah De Meester said the company is investigating the incident.
Stephan Moelans, CEO of Sabcobel, the company that manages Delhaize’s refrigeration systems, told news agency Belga that hackers had switched the units’ evaporators to defrost mode. His office declined to comment to Reuters. Colruyt Group, which operates Spar stores in Belgium through a franchise system, said five stores had suffered attacks on their refrigeration systems. Meanwhile, Belgian newspaper Le Soir reported that dozens of Delhaize and Carrefour stores were affected.
UPDATE: REFRIGERATION DISRUPTIONS SPREAD ACROSS EUROPE – SWEDEN AND BELGIUM AFFECTED
IN SWEDEN: • At least 6 ICA supermarkets affected by suspected refrigeration system hacks. • Coop has now CONFIRMED that 6 of its stores in central Sweden are also affected. • Freezer… https://t.co/a3oGMrGdmzpic.twitter.com/8Q3CFDDLhT
It follows a similar attack in France last month. Police said hackers seized control of the cooling units at hundreds of supermarkets and raised temperatures as high as 50 degrees Celsius (122 Fahrenheit), which caused fires and food losses. Cybersecurity consultant Emil Olofsson of Integrity 360 told TT, Sweden’s news agency, that temperatures there reached 80 degrees and some units caught fire, a figure that differs from the police number.
In Belgium, Delhaize noticed temperature increases in its cooling systems on Monday, spokesperson Sarah De Meester said, and the company is investigating. Stephan Moelans, CEO of the refrigeration firm Sabcobel, which runs Delhaize’s systems, told the news agency Belga it was a cyberattack that switched the units’ evaporators to defrost mode. His office declined to comment to Reuters. Colruyt Group, which runs Spar stores in Belgium under a franchise system, said five shops had their fridge systems attacked, and Le Soir reported that dozens of Delhaize and Carrefour stores were affected.
Ahold also reported a cybersecurity incident to Dutch police last month, after it detected suspicious activity in its infrastructure. Nothing in the reporting ties that report to Monday’s incident.
Fridges and freezers at dozens of supermarkets in Belgium and Sweden overheated overnight in a suspected cyberattack, similar to the one that hit French stores three weeks ago. Delhaize calls it an "IT incident."
In Sweden, John Billow, head of the national cybersecurity centre, told Reuters his team was working on several incidents involving refrigeration systems in grocery stores around the country. An ICA Kvantum store in Sjöbo said on Facebook that a cyberattack caused its problems, and an ICA store told its followers that its temperatures had been “hacked” overnight and set to 50 degrees. Fifty degrees is fine for a beach and poor for ice cream. That store later said it had opened.
At ICA Baronen in Stockholm, a notice said all the freezers were broken because of a cyberattack. The sales manager said the attack came at 2 a.m. and staff noticed it at 5:30 a.m. ICA Hägerstensåsen in Stockholm was reportedly hit too.
ICA said only a limited number of stores were affected and that it is helping them deal with the incident. However, press officer Gustaf Nilsson did not say how many stores were involved.
Coop told Swedish news agencies Aftonbladet and TT that six stores in central Sweden had similar problems. Press manager Carlos Cancino said it was still unclear whether any food would need to be thrown away or whether the refrigeration units had simply stopped working or had switched to heating mode. He also did not rule out further incidents affecting other stores.
An Estonian supermarket chain was also affected. Its refrigeration systems were reportedly set to 50°C, technology provider Kitman Coldtech told public broadcaster ERR. CEO Jann Mutso did not reveal the name of the supermarket chain, saying: “This is very recent. It happened this morning.”
How did the attackers get in? In France, Olofsson says they obtained login details for the control systems, which were exposed directly to the internet. He says the attack targeted a product that controls the cooling systems and that the hack isn’t very complicated, so amateurs may have carried it out.
Billow says Swedish authorities have noticed in recent weeks that quite a lot of exposed operational technology devices exist in Sweden, and they’ve been clear that these must be updated or patched.
Refrigerators and heating systems, security cameras and alarm networks were once largely mechanical, and now they can be monitored and controlled remotely. That gives cybercriminals new openings. Authorities haven’t said who was behind last month’s incidents, and nobody has claimed responsibility.
The Sweden Herald reported that the cause of the attacks on Swedish supermarkets remains unknown.
Update 20:00 Rome Time
The company at the center of the European supermarket refrigeration cyberattacks is Danfoss the same company whose refrigeration systems were targeted during the cyberattacks in France a few weeks ago.
Apparent attempt to hack Rade Bajić’s iPhone comes amid efforts to undermine landmark criminal case
A Serbian prosecutor who investigated the authorities’ allegedly illegal scheme to help the Trumps build a tower in Belgrade has been targeted with advanced spyware, expert analysis indicates.
The finding suggests a disturbing new element in the authoritarian Serbian regime’s campaign to undermine what is believed to be the first criminal case related to global moneymaking drive of the US president’s family, which critics describe as a “pay to play” scheme trading the Trump administration’s favour for business opportunities.
Whether it was youngsters proving their skills or state sabotage, Europe’s most hacked country was left with a mountain of waste after food began cooking in freezers
Shortly before midnight last Sunday, the digital thermostats controlling hundreds of supermarket cold aisles across France began to flicker and rise.
In a “bizarre and unprecedented” cyber-attack, hackers had remotely overridden the temperature settings on thousands of freezers, fridges and chiller cabinets pushing them from as low as -27C (-16.6F) to well over 50C (122F).
Dutch police arrested convicted hacker Pepijn van der Stap in the ShinyHunters probe into the Odido breach, which exposed data belonging to millions of customers.
This article is the result of a collaboration with The Sunday Times. You can find their corresponding piece here.
Sign up here to receive Bellingcat’s biggest investigations by email as soon as they are published.
Crime boss Christy Kinahan leads a $1.5 billion illicit network involved in drug trafficking, money laundering and arms smuggling from the cartel’s base in Dubai.
Christy Kinahan, the Irish founder of the Kinahan Organised Crime Group who is being pursued by authorities around the world from his bolthole in the United Arab Emirates (UAE), has had his residence permit cancelled.
The visa was cancelled at the end of last month, just weeks after the extradition of his eldest son Daniel Kinahan from Dubai to Ireland, where he is charged with directing the activities of a criminal organisation.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
It follows a review of public immigration records by Bellingcat and The Sunday Times, published in August, which revealed that Christopher Kinahan Jr, another of Christy Kinahan’s sons, was recently issued with a new two-year visa in the UAE.
This is despite his status as a sanctioned individual who, like his father and older brother, is the subject of a $5 million reward from the US government for information leading to his arrest or conviction.
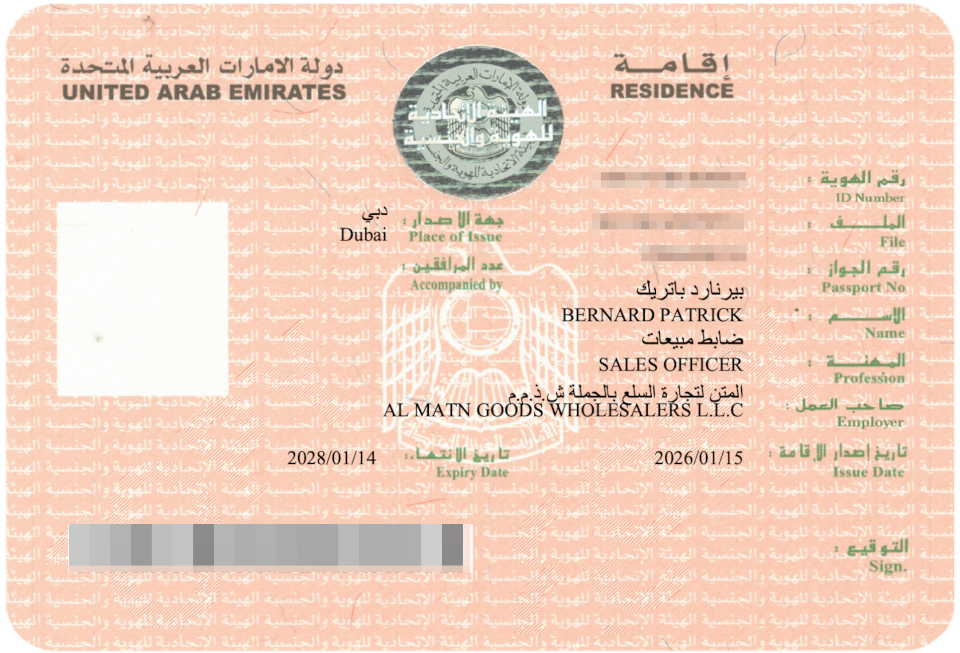
Last month, we also exposed the residence statuses of the crime gang’s other sanctioned leaders who remain at large in Dubai. These include cartel lieutenant Bernard Clancy, whose residence permit was renewed in January, as well as padel poster boy Ian Dixon and Christy Kinahan, who have been living in Dubai on expired permits.
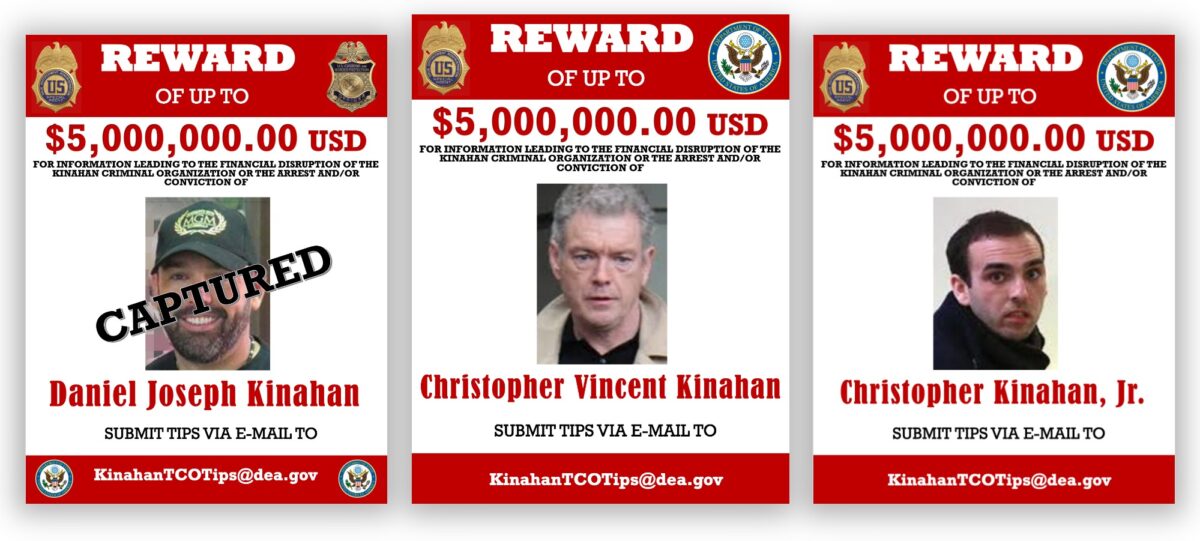
Wanted posters for Irish drug smugglers Daniel Kinahan, 49, Christy Kinahan, 69, and Christopher Kinahan Jr, 45. Senior cartel members Ian Dixon, 37, Sean McGovern, 40, Bernard Clancy, 49, and Johnny Morrissey, 66, were also sanctioned by the US government in 2022. Source: US Department of the Treasury
The cartel members had all obtained employment-based residence visas sponsored by Dubai companies, which are required to apply for employee work permits through the UAE’s Ministry of Human Resources and Emiratization.
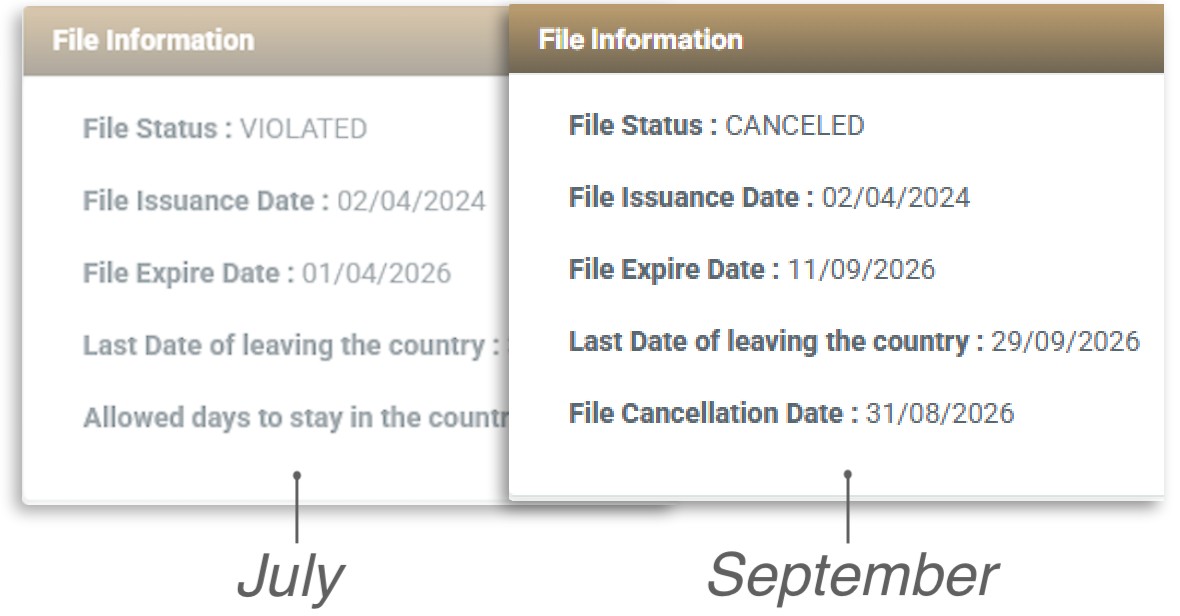
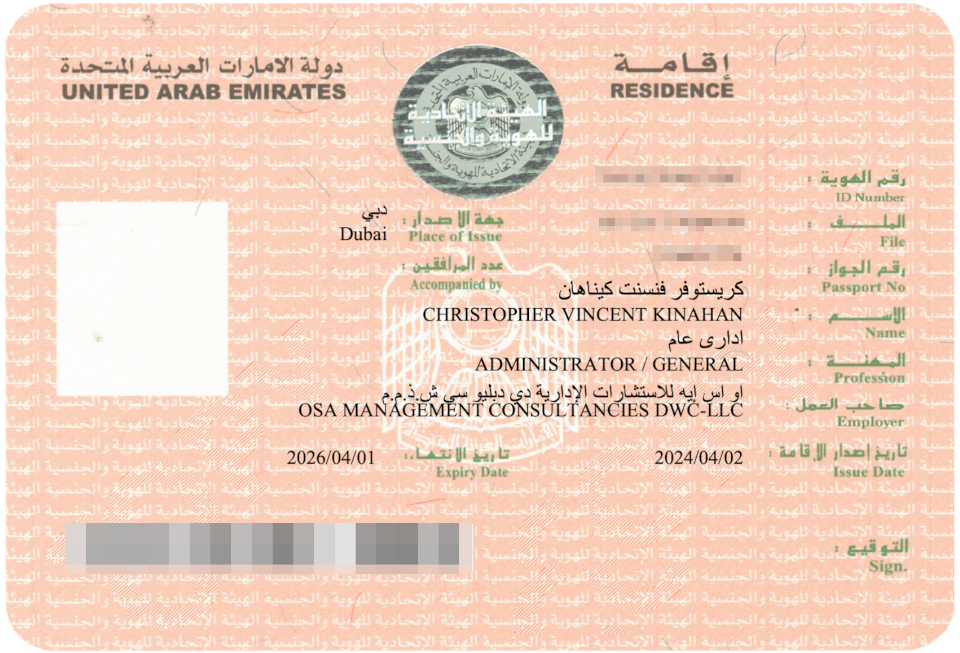
Christy Kinahan’s most recent visa listed his employer as OSA Management Consultancies DWC LLC, which is based at the same Dubai address as cartel-linked firm CV Aviation Consulting Services DWC LLC. The visa expired on April 1.
A new search of Emirate government portals shows the visa was subsequently cancelled on August 31.
According to information published by a UAE government-authorized service provider, visa cancellation applies to people who leave the country permanently, alter their visa category or change employer. For employment-based residence visas, the cancellation process must be initiated by the employer or an authorised representative.
In the case of Kinahan’s visa, the specific reason for the cancellation is unknown.However, his last date for leaving the country is listed as September 29 in the government immigration file. This is in line with the 30-day grace period granted to holders of standard employment visas after cancellation.
The Sunday Times reports today that Europe’s intelligence services believe Kinahan is still in Dubai, though rumours that he has moved to Africa have sparked speculation he has already fled the Gulf. It also reports that the cartel leader has moved assets out of the Emirates as the crime group breaks into rival factions.
The Kinahan Organised Crime Group is a $1.5 billion transnational network involved in drug trafficking, money laundering and arms smuggling. Investigators have connected it to Iran’s intelligence services and the Lebanon-based militant group Hezbollah.
The UAE foreign ministry has been contacted for comment.
Connor Plunkett, Peter Barth, Beau Donelly and John Mooney contributed to this article.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
Sign up here to receive Bellingcat’s biggest investigations by emailas soon as they are published.
A sanctioned vessel that was previously reported to have transported weapons destined for Russian mercenaries has been traversing ports on the west coast of Africa since March, exhibiting what experts told Bellingcat was an unusual set of movements and behaviours.
Patria (IMO: 9159921) has been sanctioned by the US, Ukraine and Canada.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
Radio France International (RFI) reported last year that it was one of two ships to deliver weapons to Conakry in Guinea that were intended for the Kremlin-controlled Africa Corps and their operations in Mali.
Satellite imagery and Automated Identification System (AIS) data from Lloyd’s List Intelligence shows Patria has shuttled between the Port of Douala in Cameroon and the Port of Owendo in Libreville, Gabon four times since March.
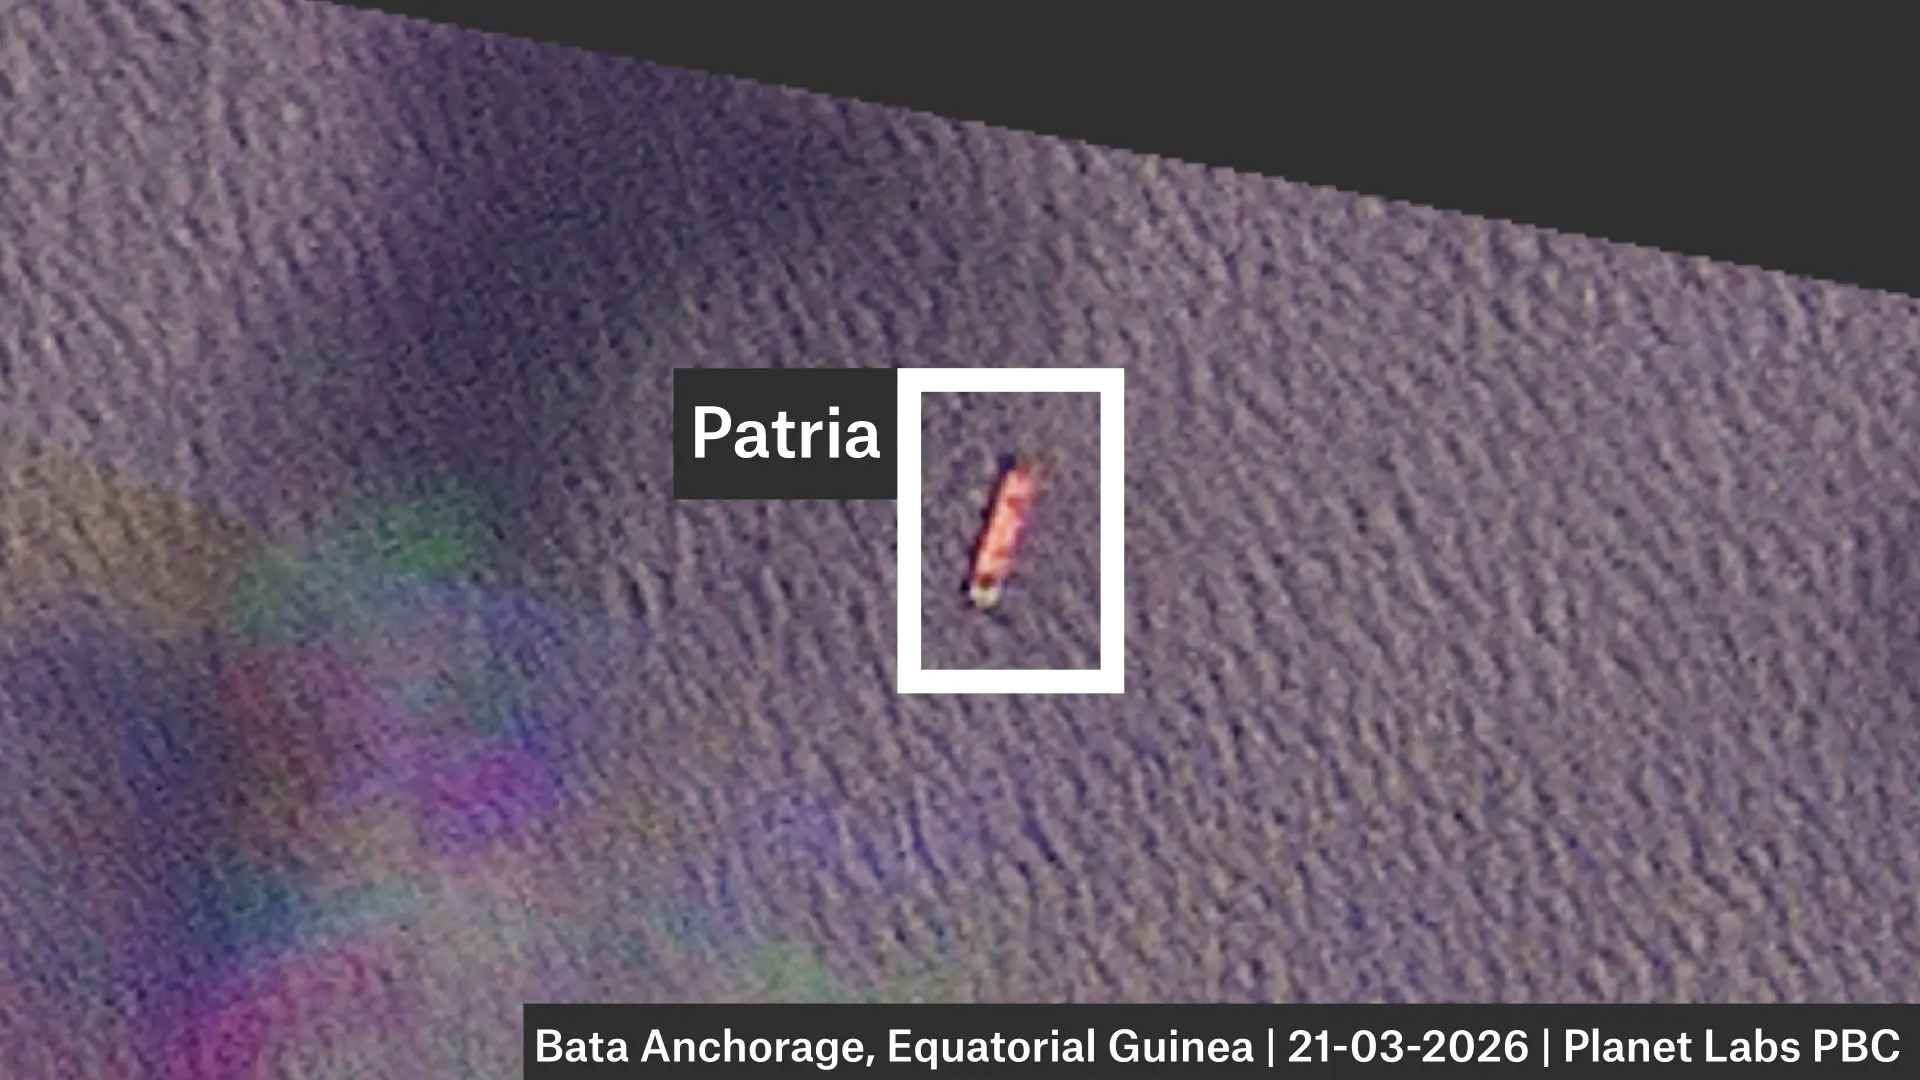
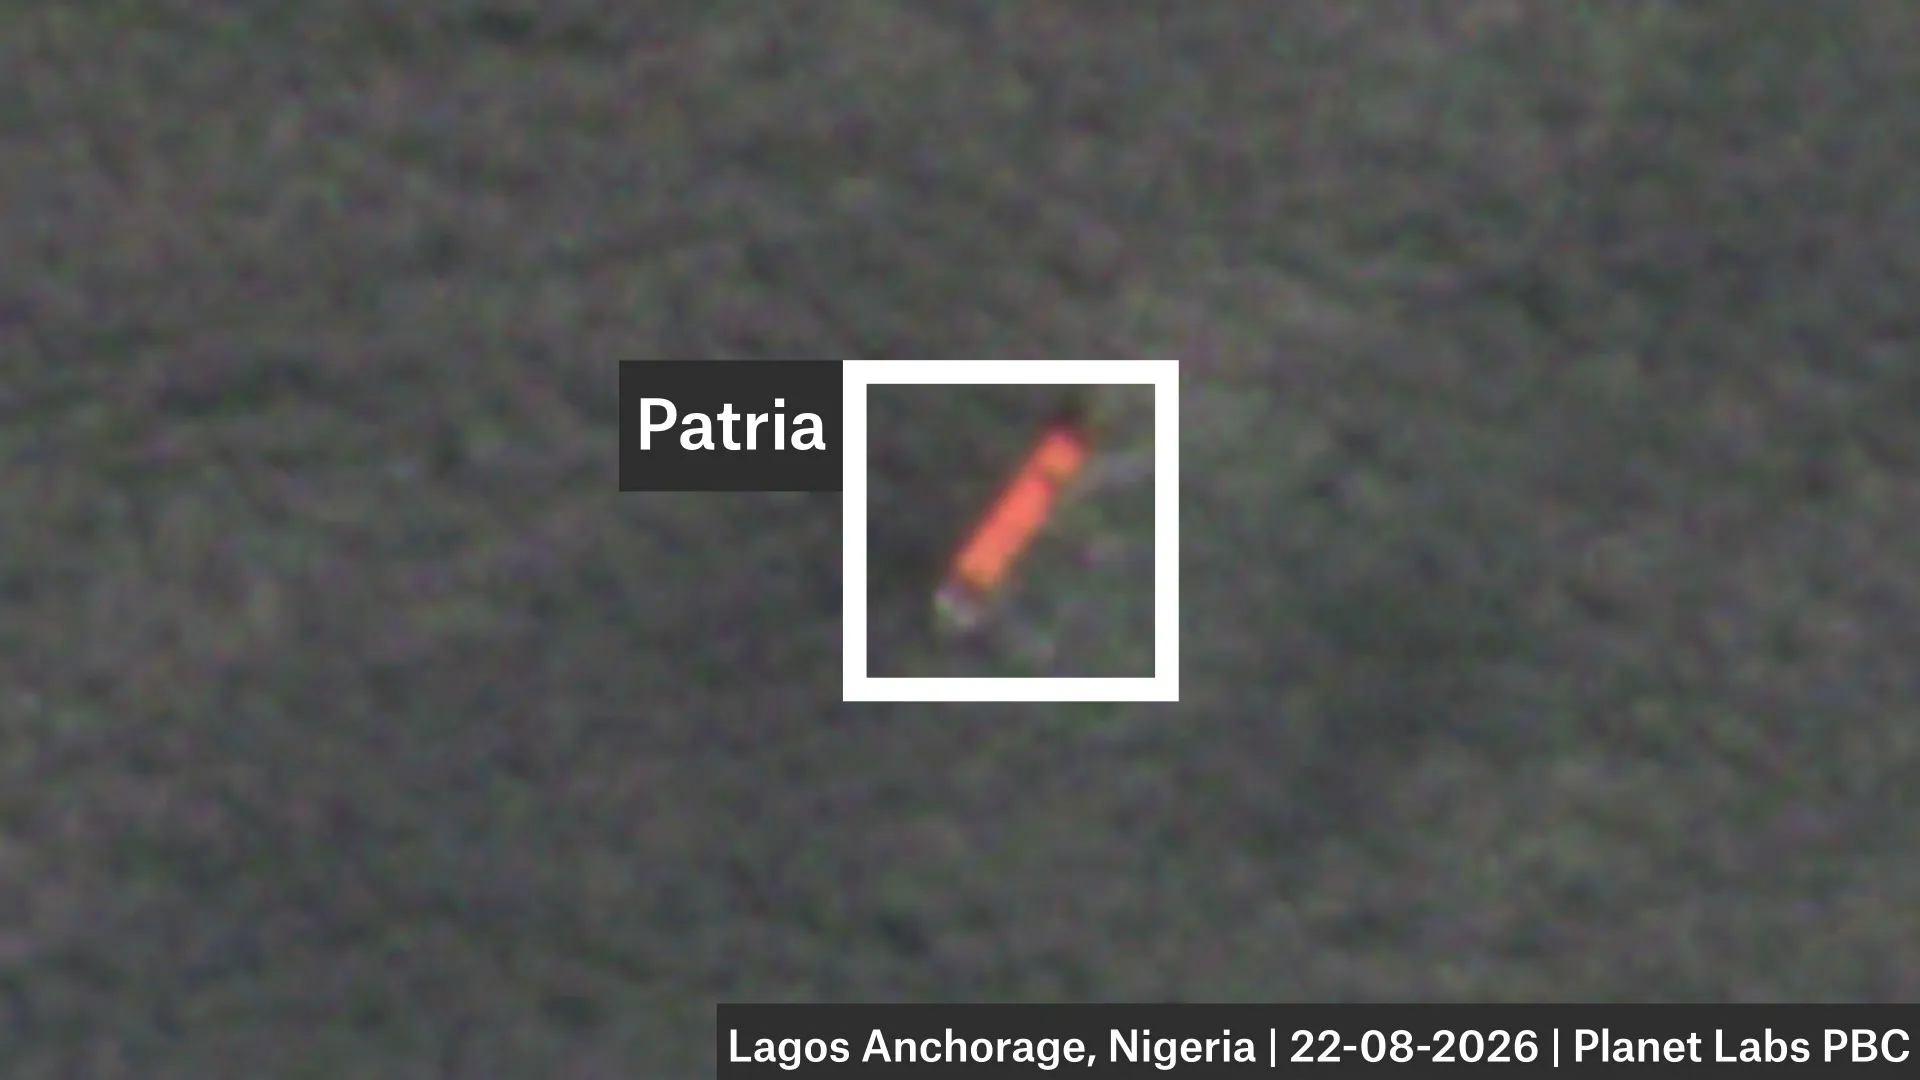
It has also twice stopped in anchorage off the coast of Lagos, Nigeria: first in March and then again at the time of publication. Analysis shows the vessel also spent time in anchorage off the coast of Equatorial Guinea.
The online news site, Modern Ghana, first reported Patria’s presence off the coast of Lagos in July after X-users @SONNAROW_OSINT and @RFNOSBlog picked up on Patria’s position.
It is not clear what Patria has delivered or picked up at these ports. Nor is it clear why it has spent so long going back and forth between them. But experts Bellingcat spoke to said the unusual patterns of behaviour raised numerous questions.
Charlie Brown, a former US Naval Officer and Senior Advisor at United Against Nuclear Iran said the combination of Patria’s repeated regional port calls, extended periods at anchor, and an apparent absence of a normal point-to-point trading cycle warranted scrutiny, especially as the ship is under sanction and is previously reported to have shipped arms.
Tracking the Patria
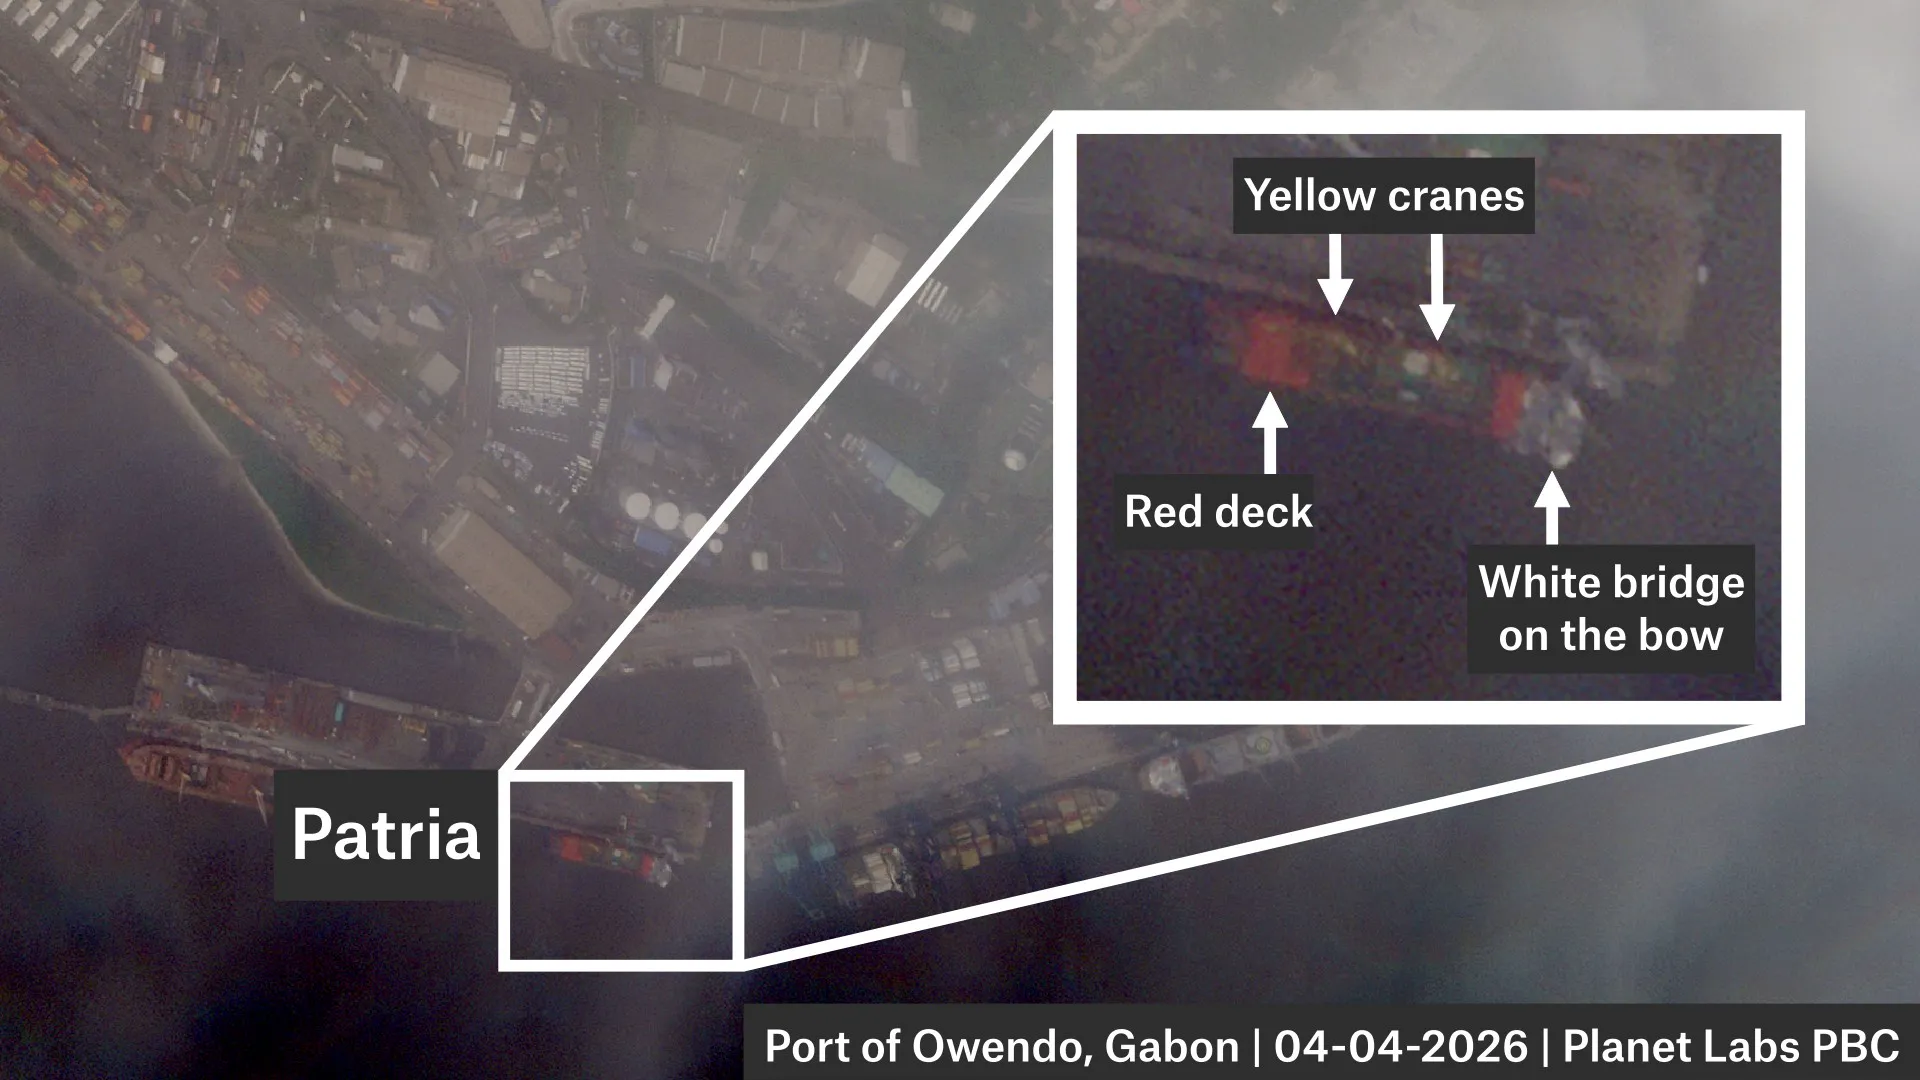
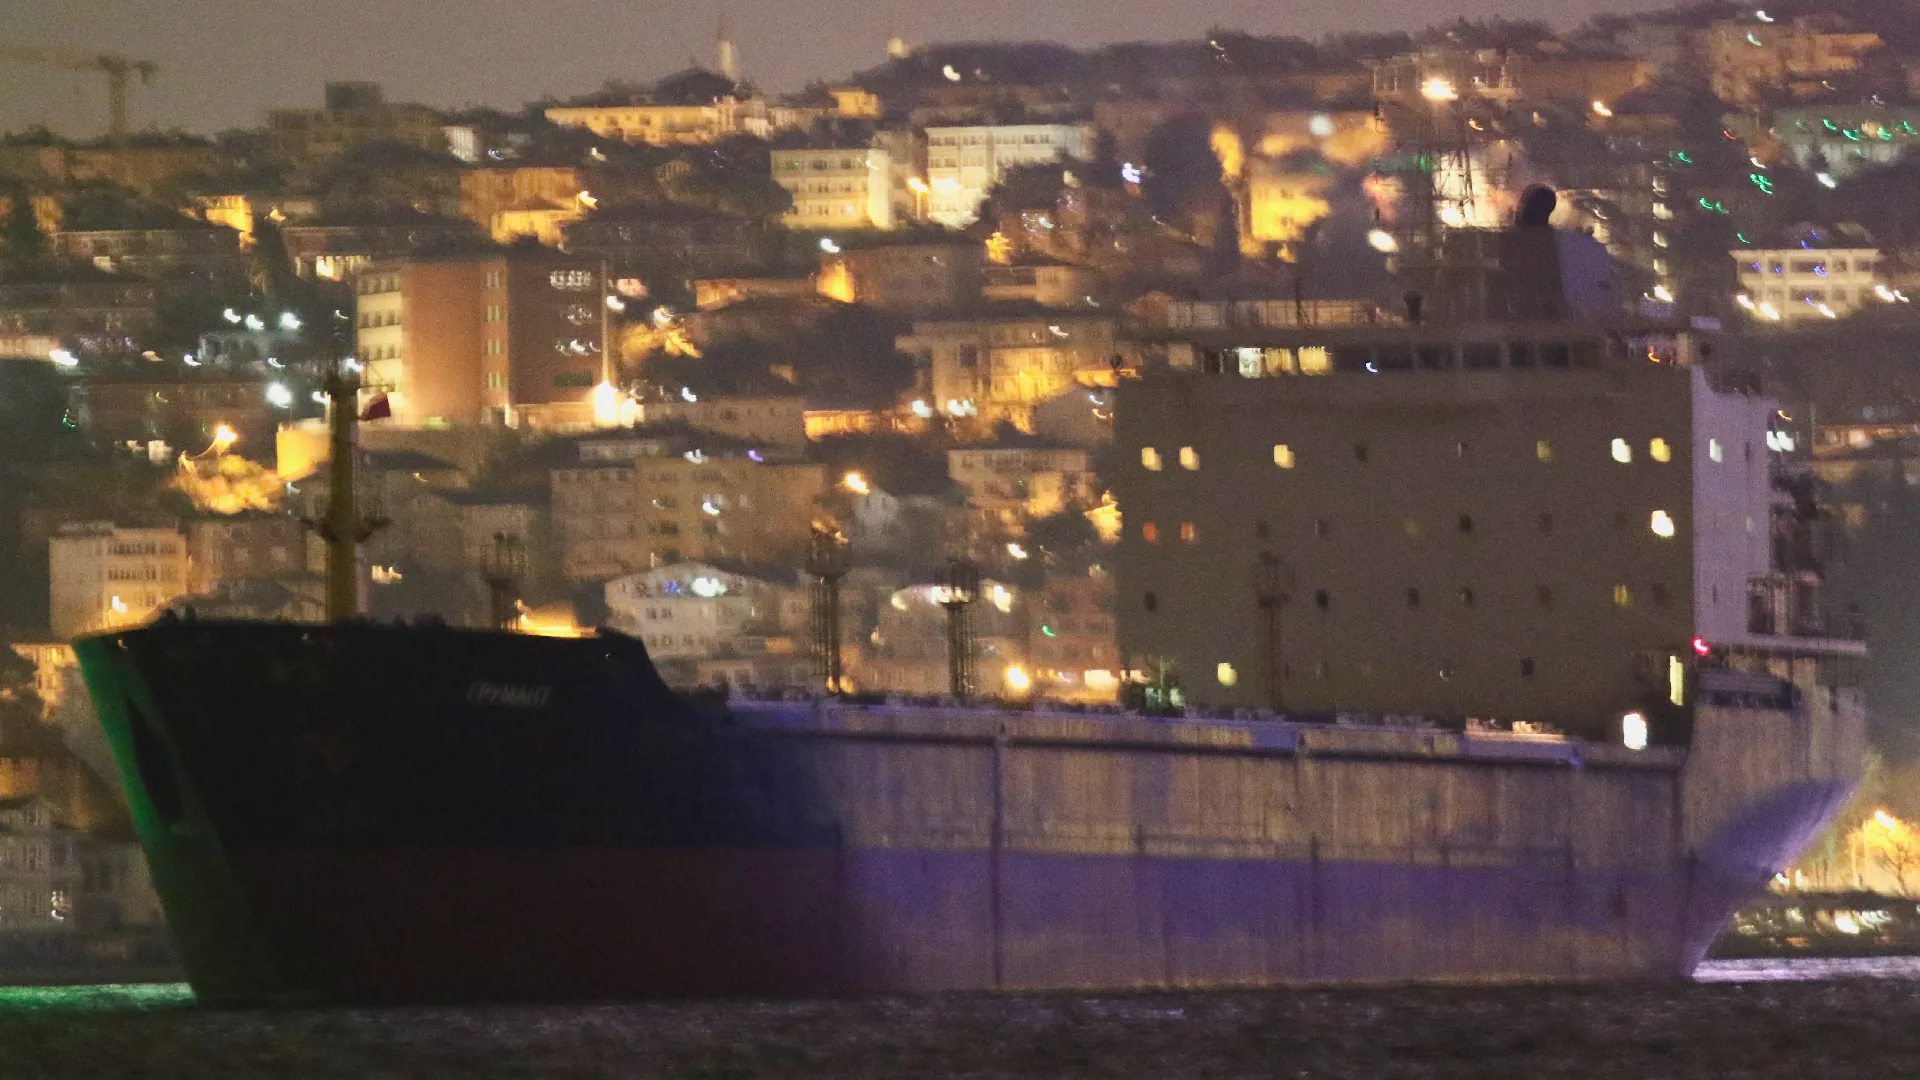
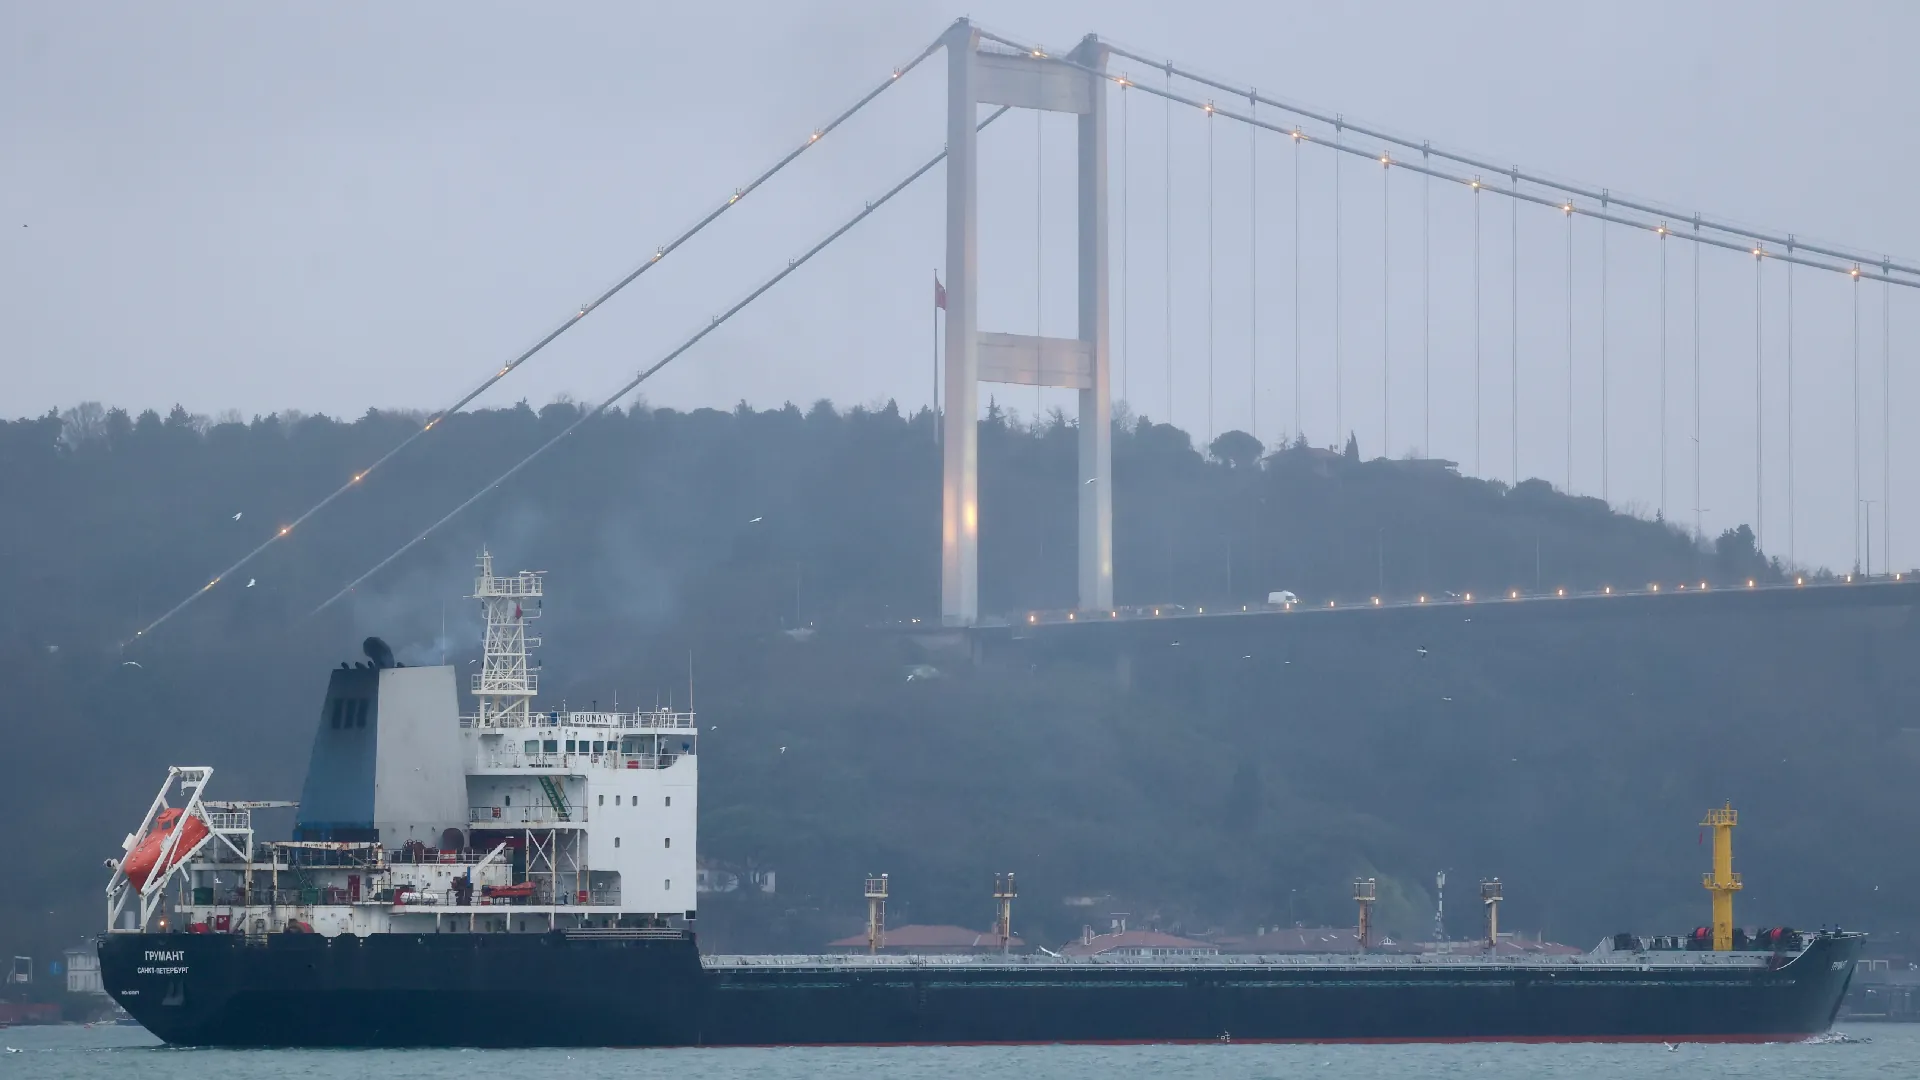
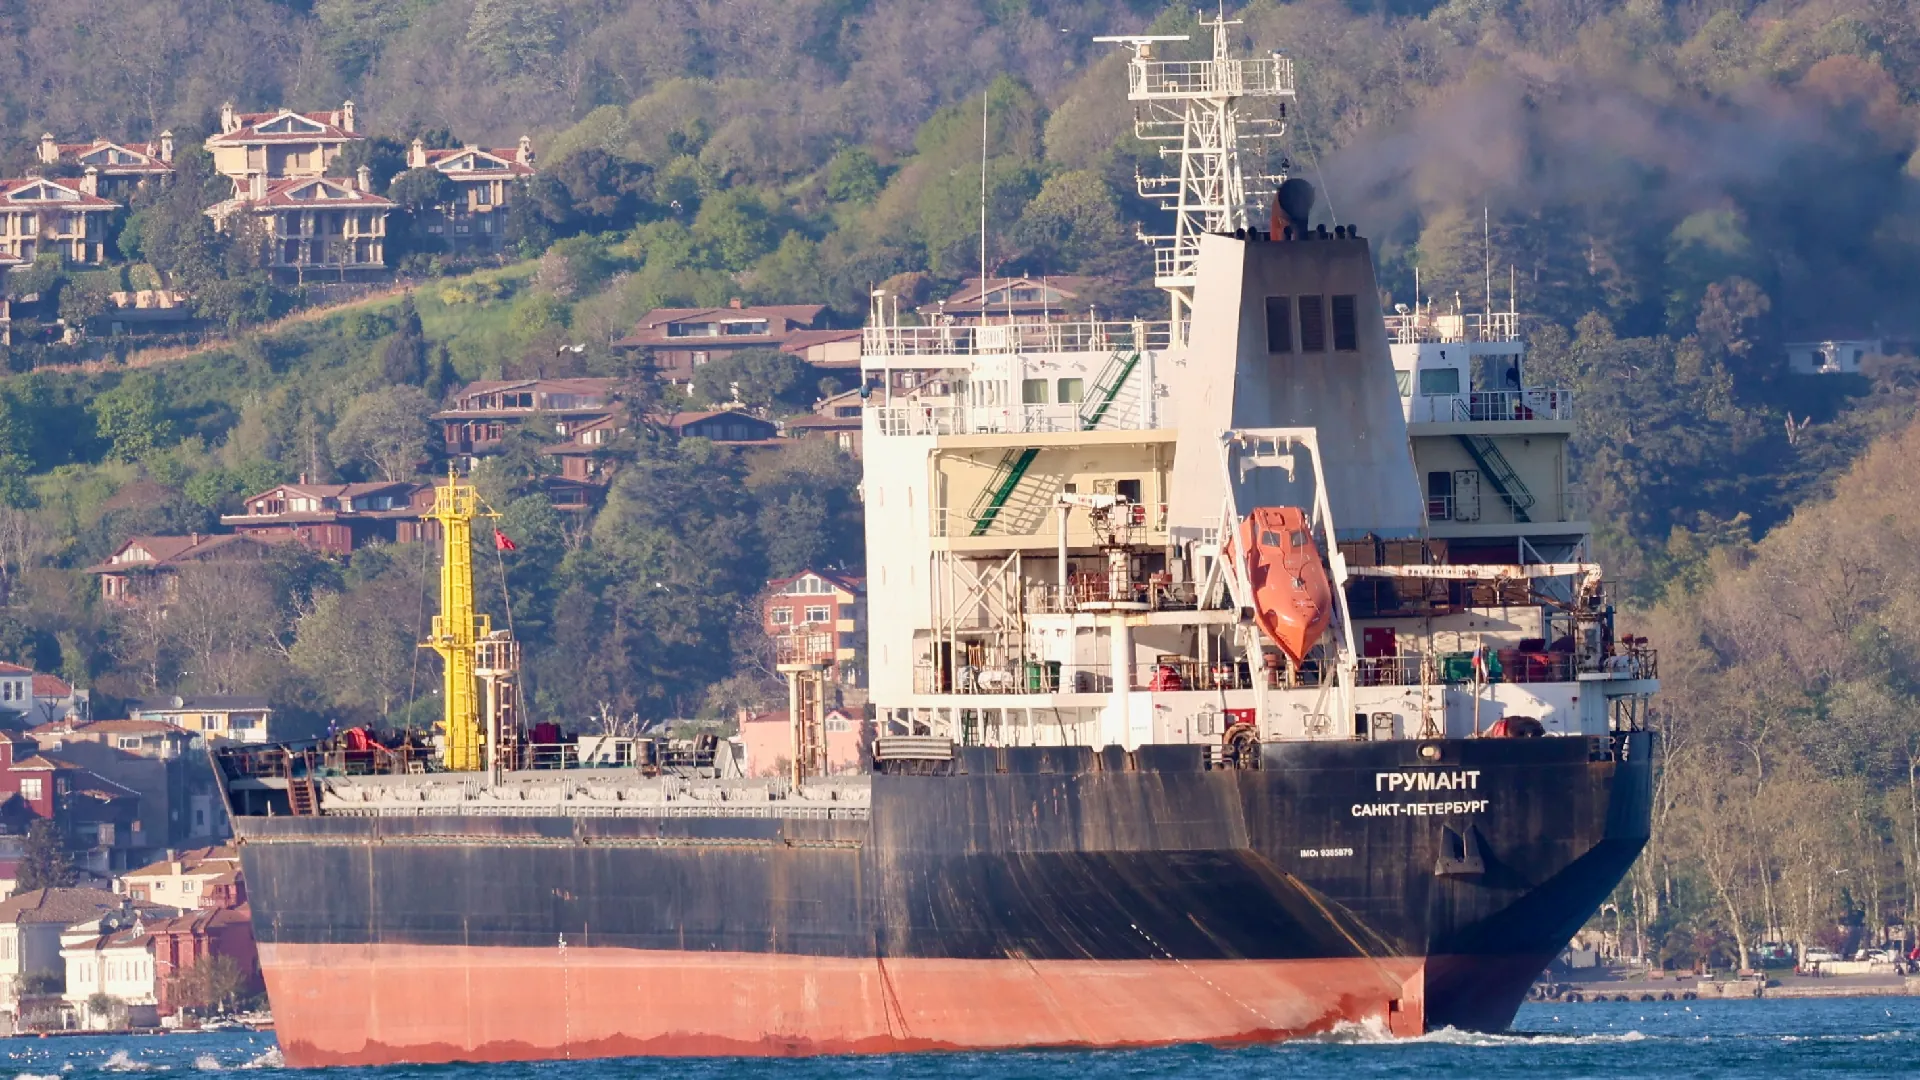
Patria is a cargo vessel that has a distinct shape and features. Its bridge is located on the bow and it has a bright red deck that contrasts with its blue hull and two yellow cranes.
At the end of the deck, the ship has a built-in ramp for vehicles (the Patria is a so-called roll on/roll off, or RoRo, vessel that is designed to transport wheeled vehicles). Its chimney is located next to the ramp.
Footage of the Patria, posted on Youtube on Jan 22, 2024. Credit: Hanro Shipping – Sakhalin Projects LLC / YouTube Channel @hanroship
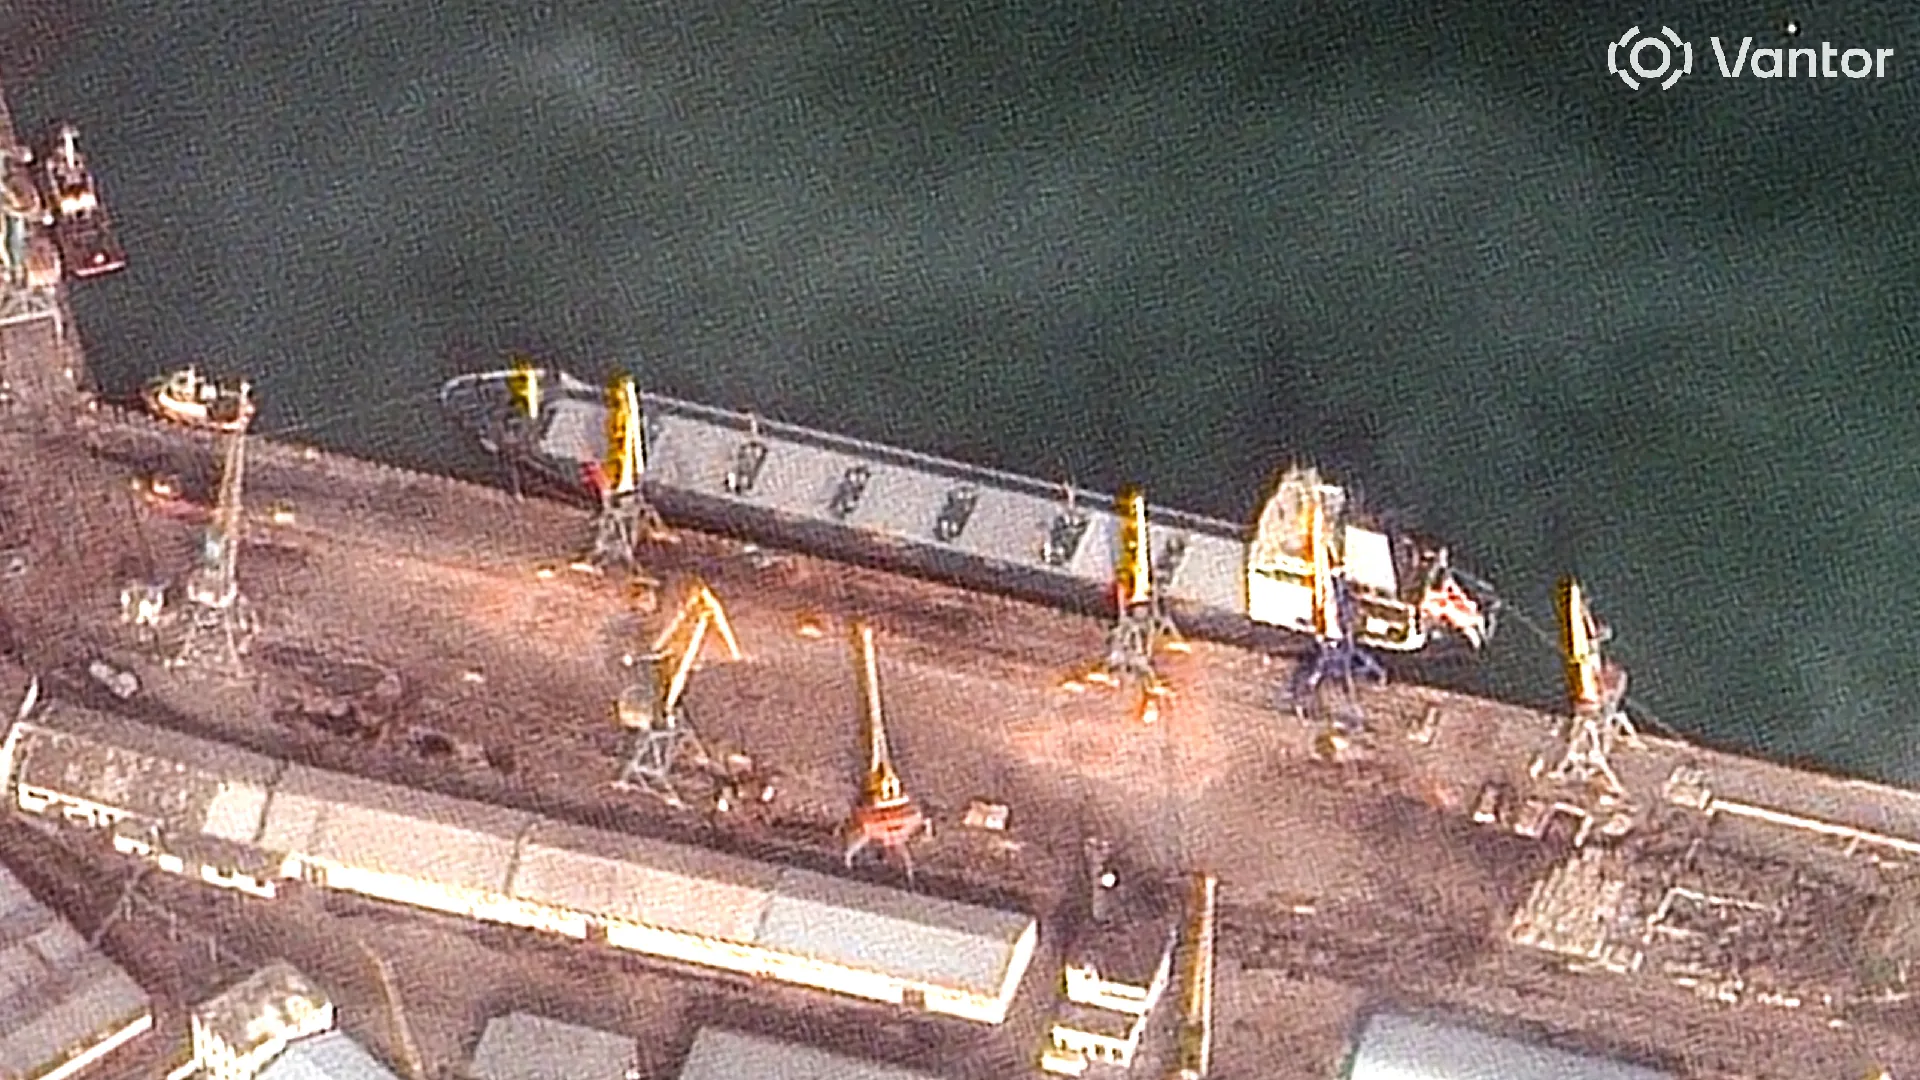
This, in combination with the length of the ship (101 m), allowed Bellingcat to pick the vessel out in satellite imagery. AIS data helped us further track its long journey which began in the Sea of Japan, in Russia’s far-east, in January.
For the most part, we were able to match Patria’s AIS position with corresponding satellite imagery. We found no evidence of obvious spoofing incidents (where a ship intentionally broadcasts misleading AIS data) by the vessel during its months-long voyage, however, there were some instances where satellite images were not available and thus spoofing by the vessel cannot be completely ruled out.
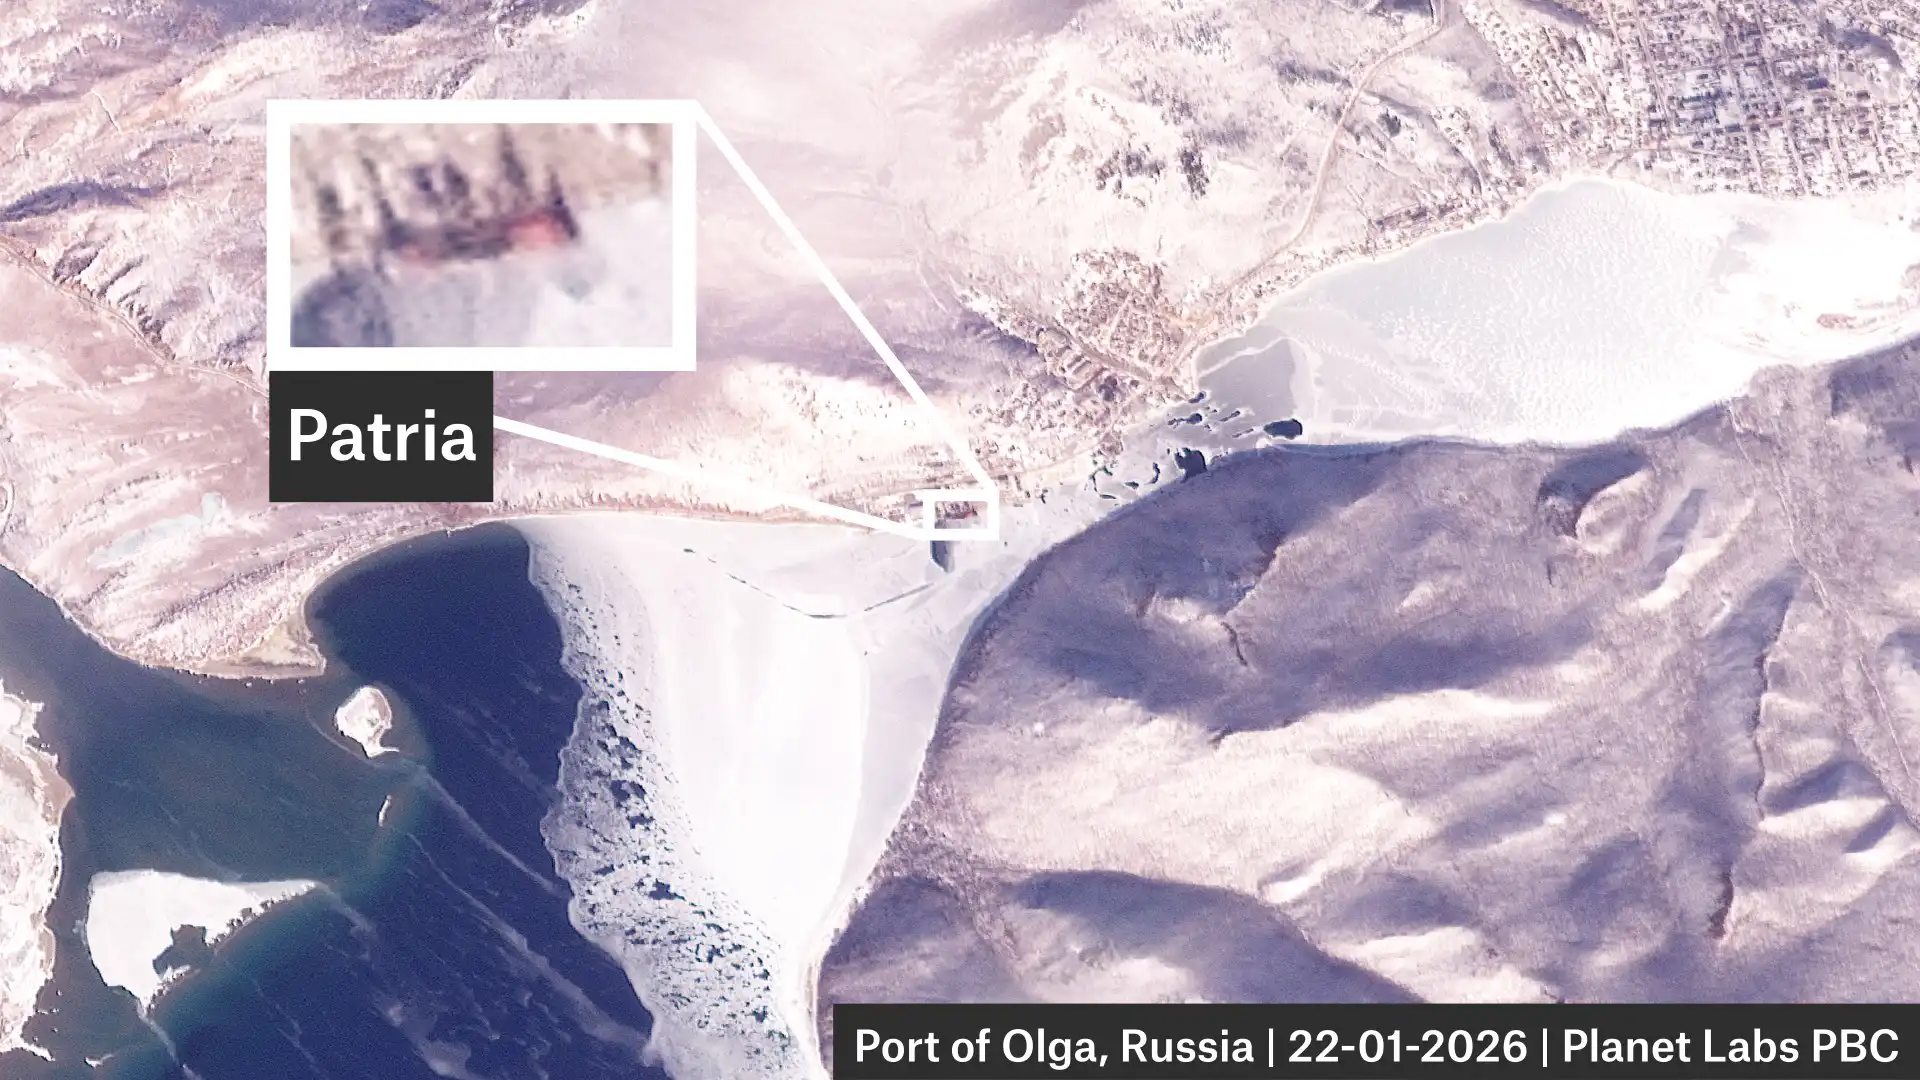
AIS data indicates that Patria loaded at the Port of Olga in the Sea of Japan between Jan. 21 and 23. Patria can also be seen on satellite imagery on these dates.
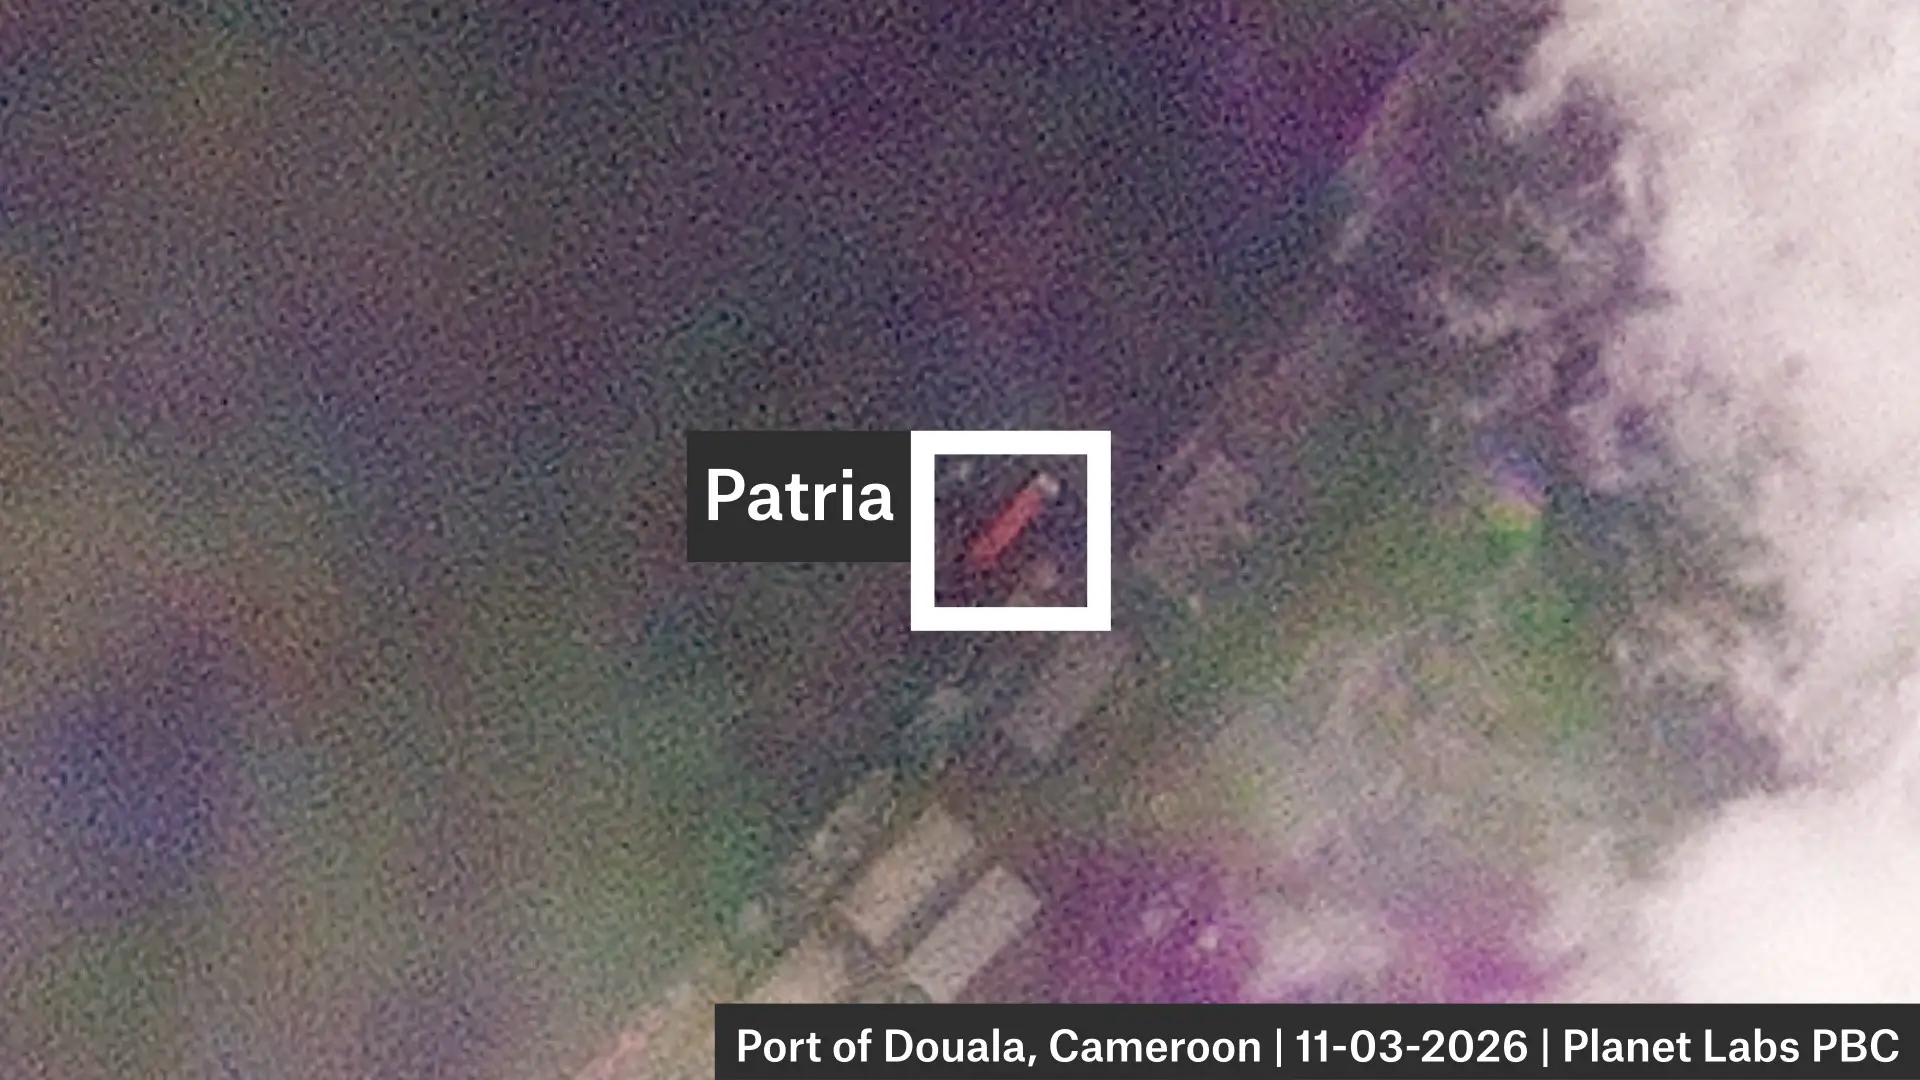
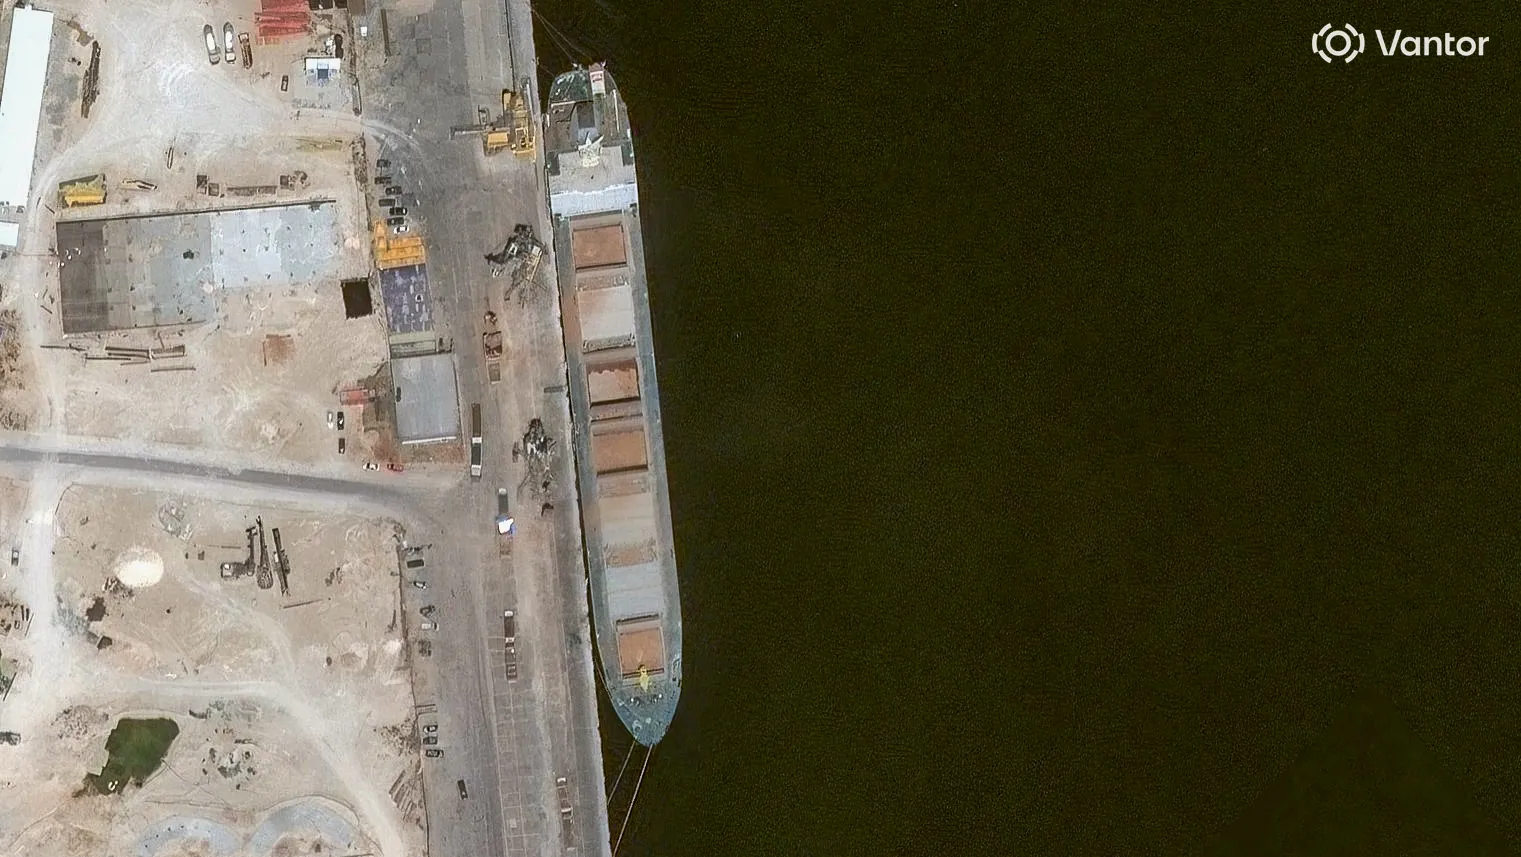
AIS data indicates that Patria unloaded some cargo in the Port of Douala between Mar. 11 and 12. Again, the ship can also be seen in satellite imagery on these dates.
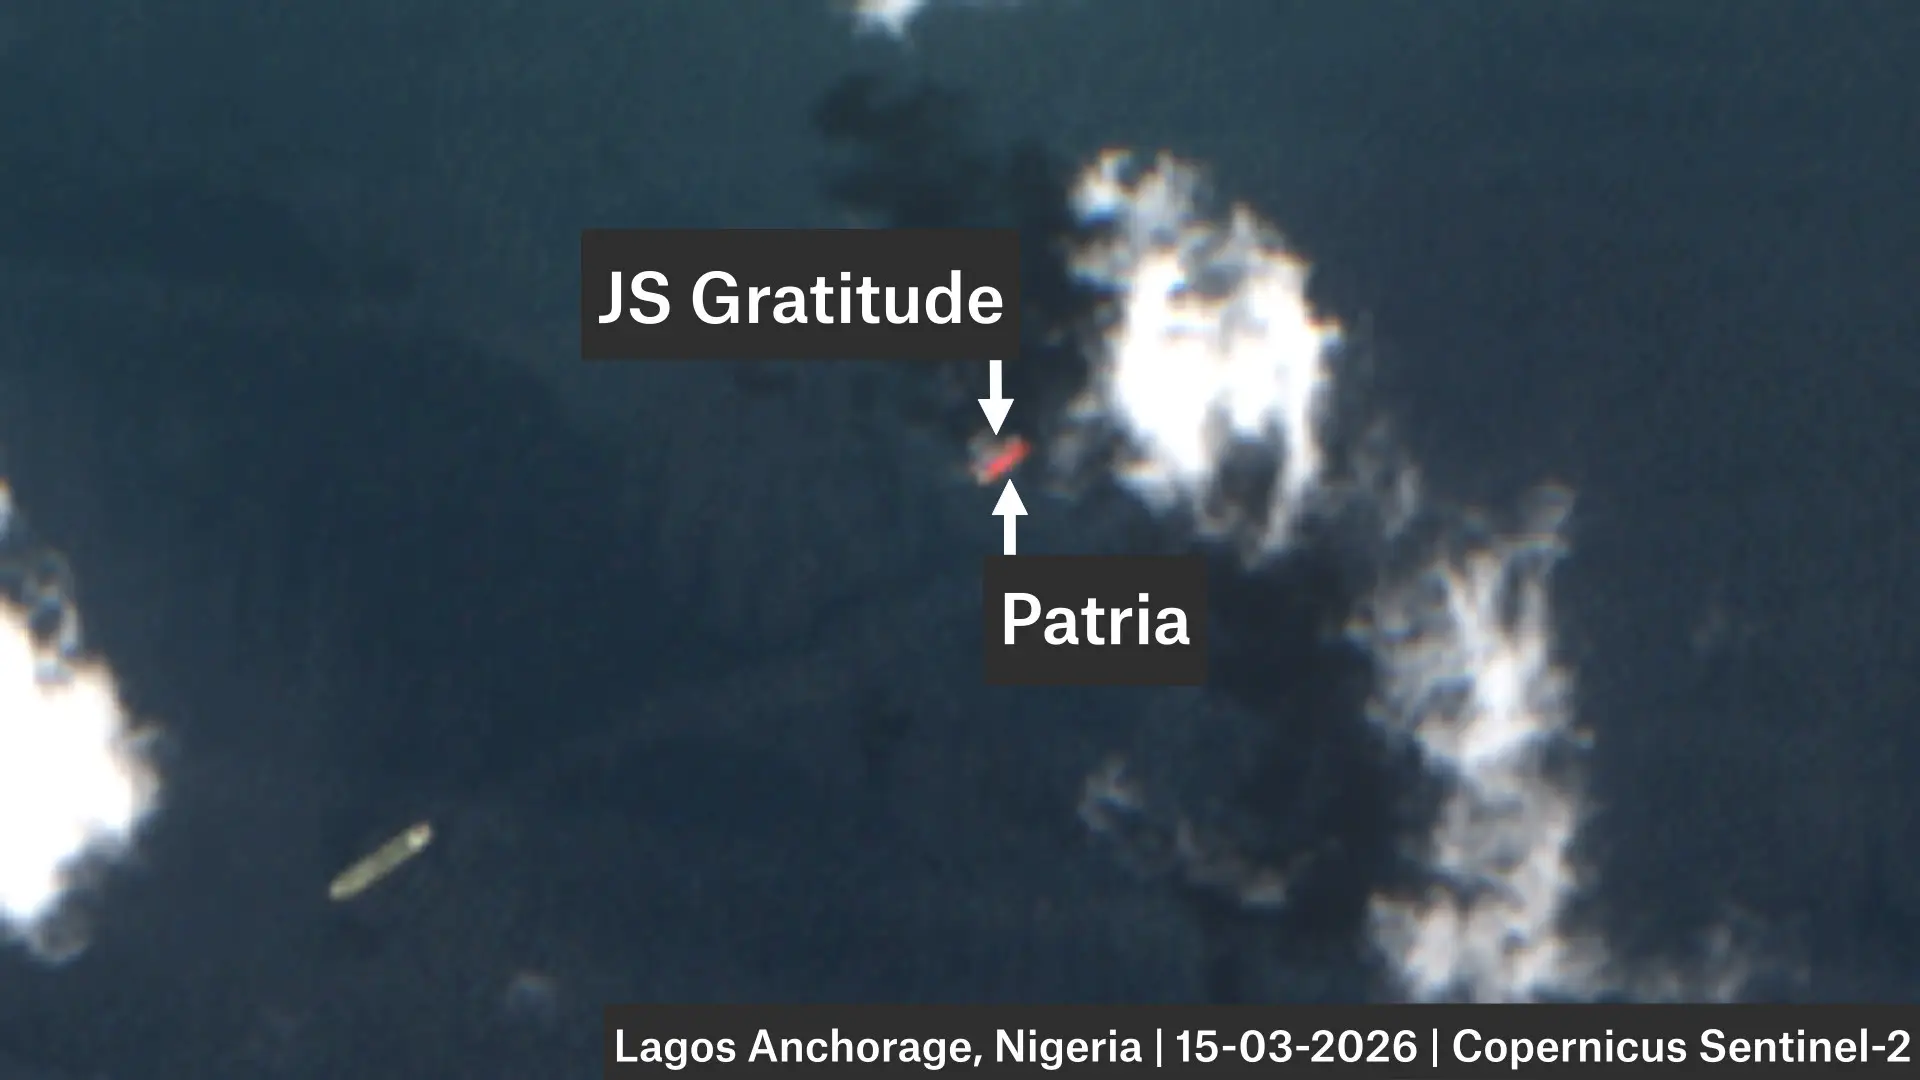
AIS data indicates Patria anchored off the coast of Lagos from Mar. 14 to 15.
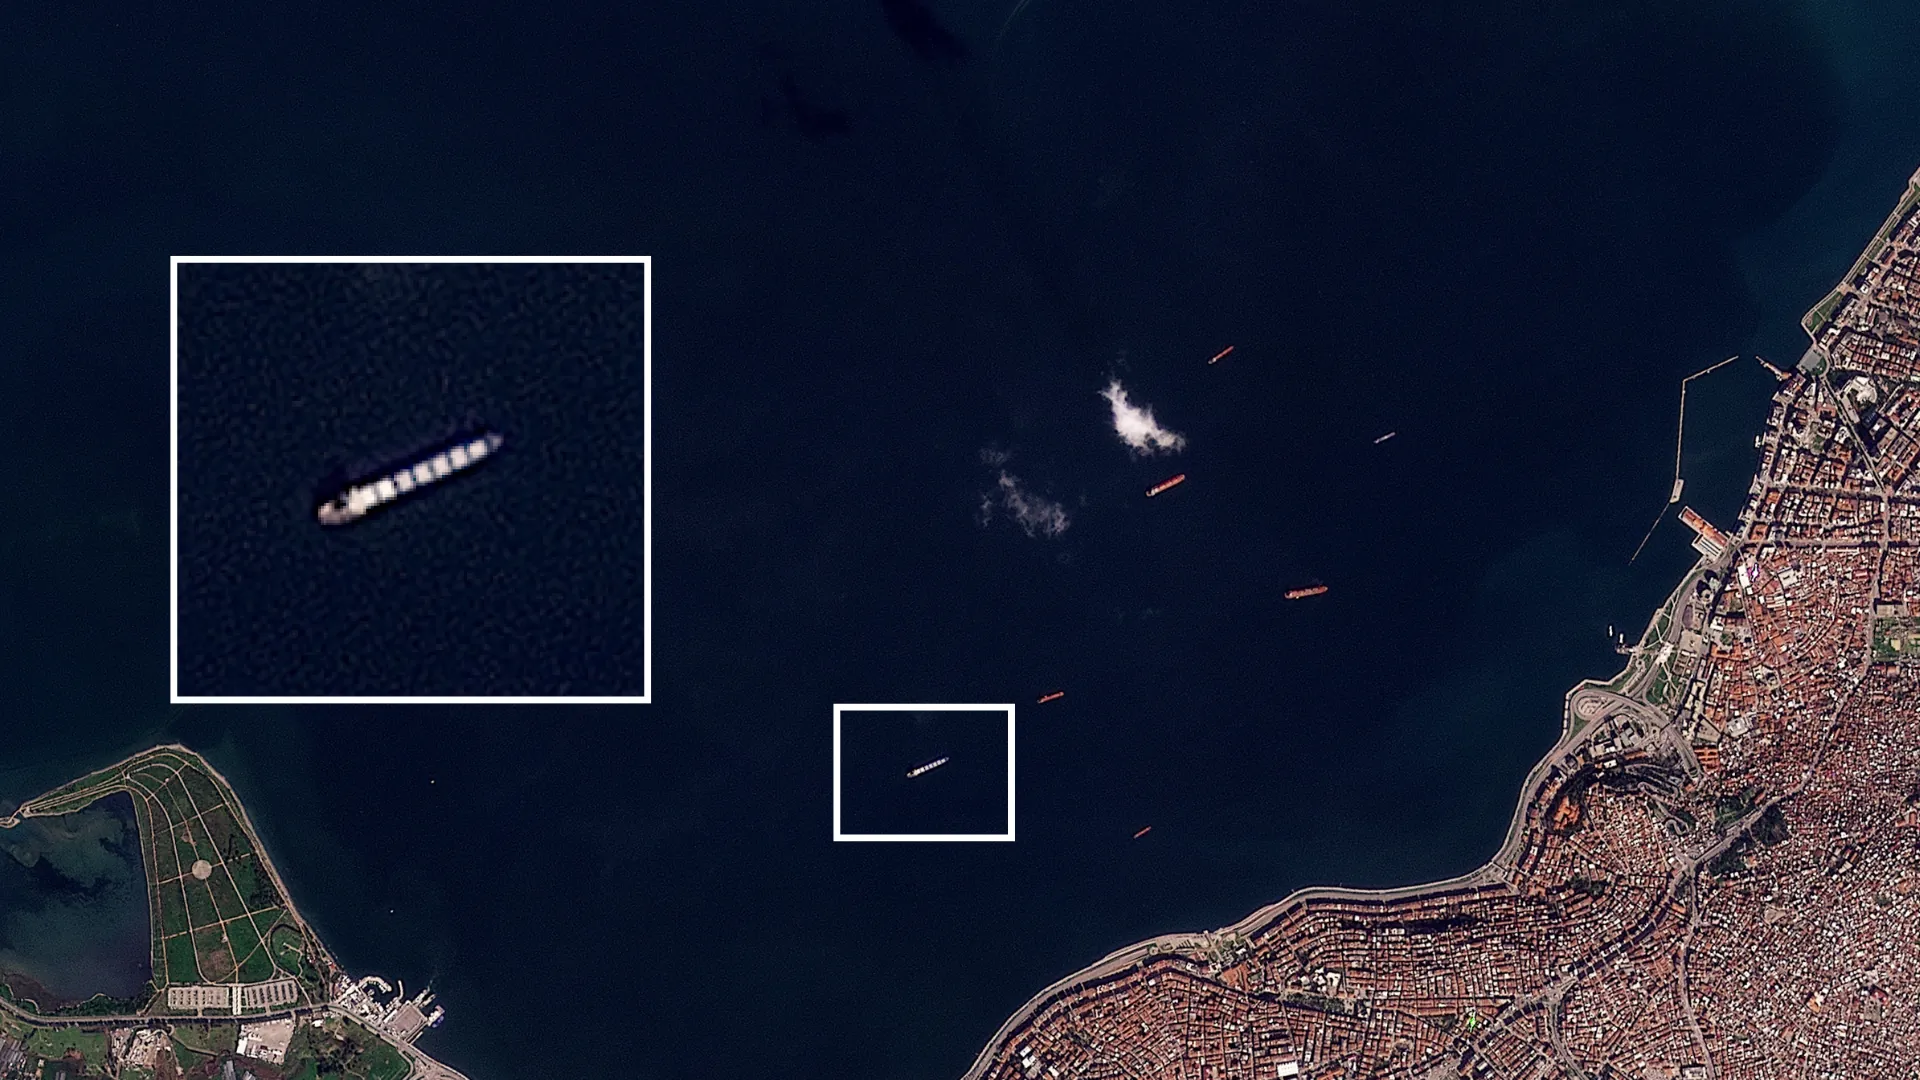
A Sentinel-2 image from the 15th appears to show another ship next to Patria. AIS data indicates that this is JS Gratitude, a bunkering tanker. This close proximity suggests that Patria was refuelling.
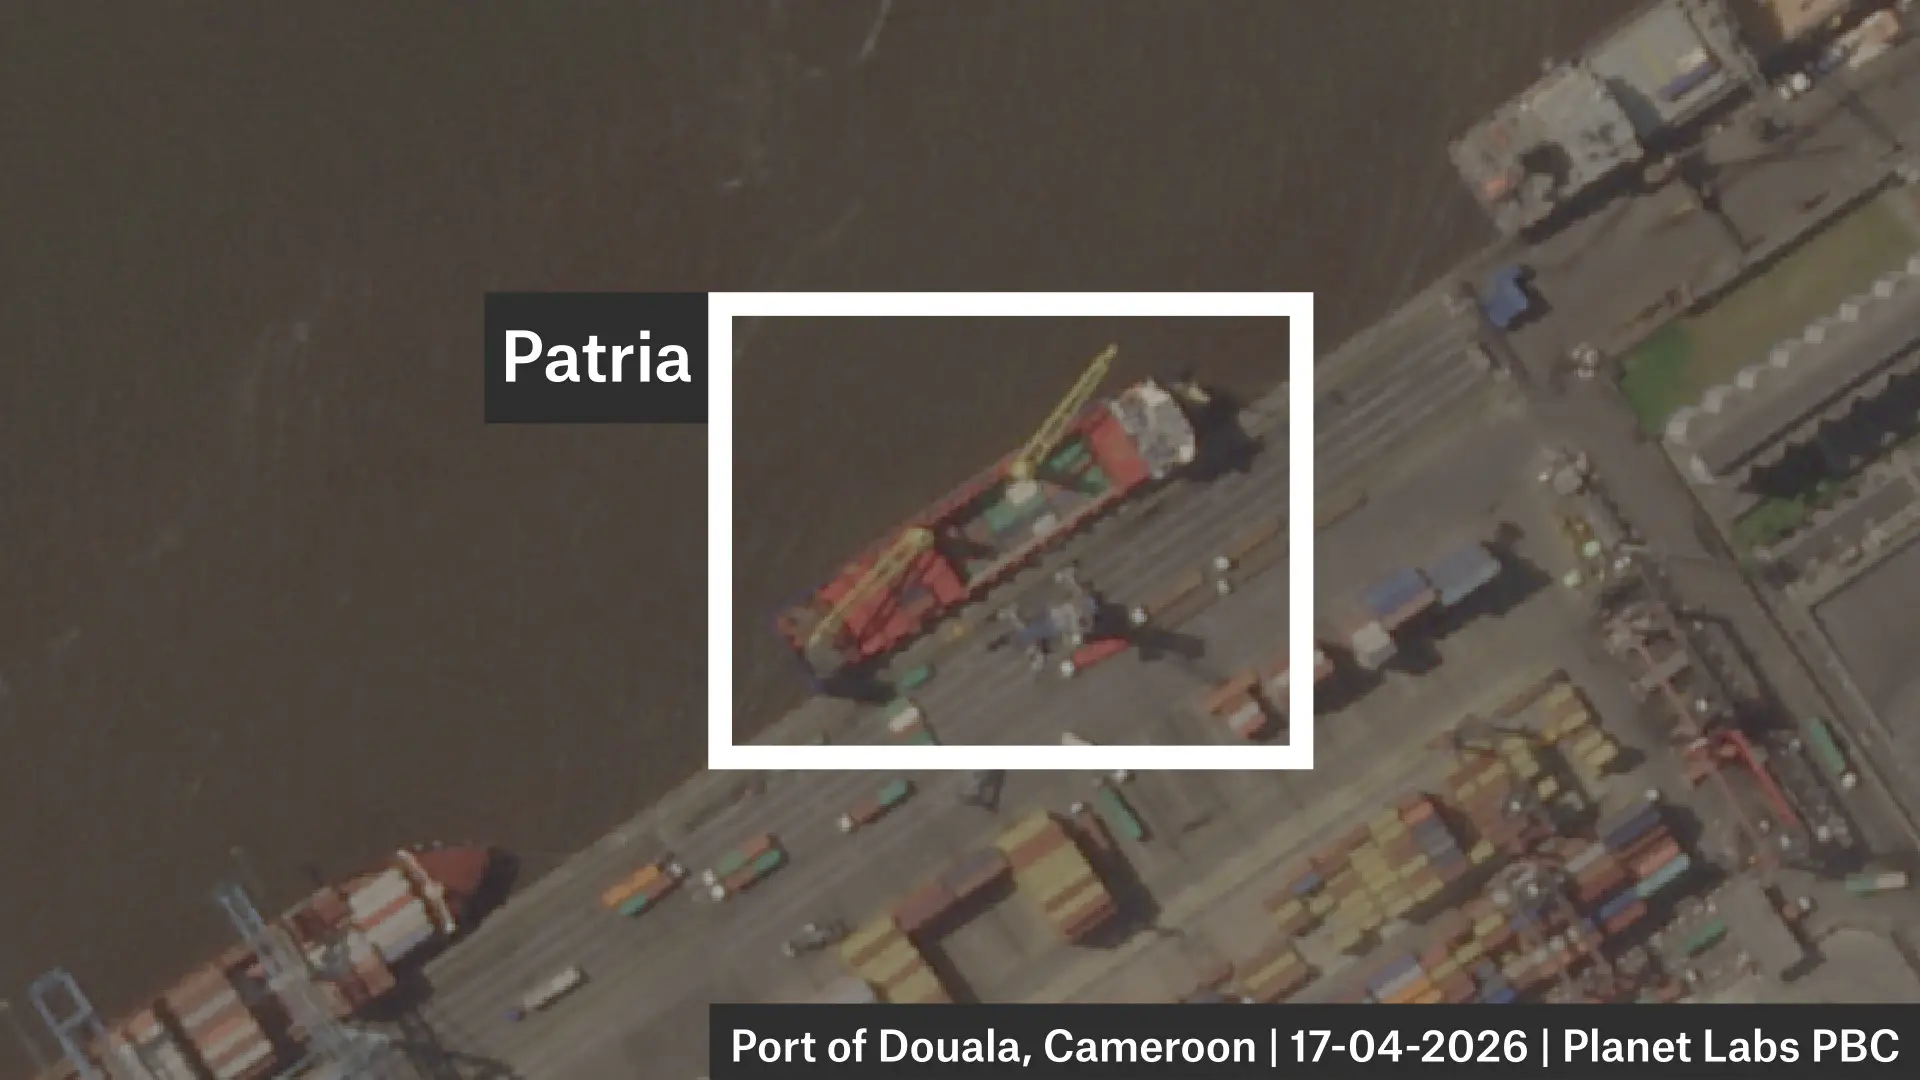
AIS data and satellite imagery indicate Patria stayed at the Douala Anchorage from Apr. 6 to 14, before unloading at the Port of Douala between Apr. 14 and 18.
AIS data suggests Patria loaded in Libreville again between Apr. 22 and 26.
Port of Douala, Cameroon
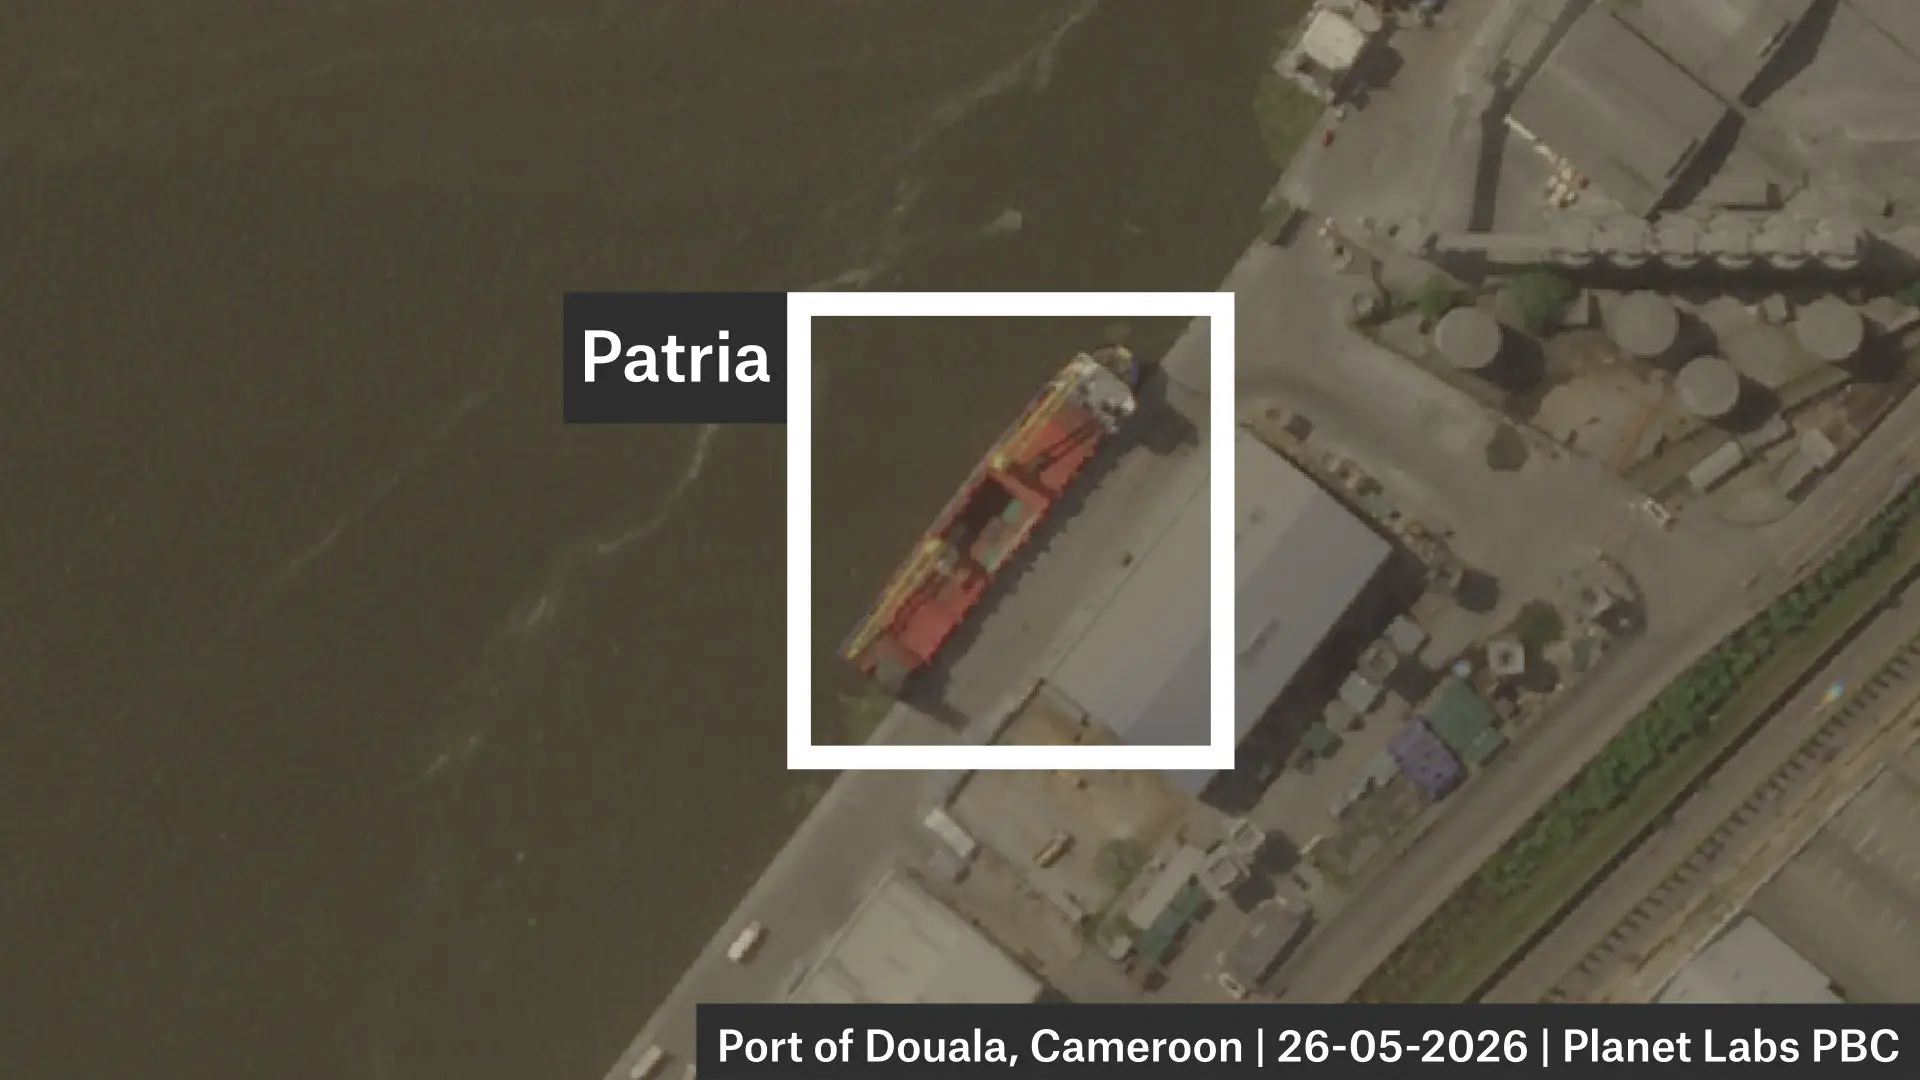
AIS data, supported by satellite imagery, indicates Patria stayed at the Douala Anchorage for nearly a month from Apr. 27 to May 21 before unloading in Douala from May 21 to 27.
A third trip between the Port of Owendo, Libreville to Douala, Cameroon
AIS data indicates, after nearly a month’s wait in Douala anchorage, Patria again loaded at Owendo before returning to Douala to unload.
A fourth trip between the Port of Owendo, Libreville to Douala, Cameroon
AIS data indicates Patria again loaded at Owendo before returning to Douala to unload.
Lagos Anchorage, Nigeria
AIS data indicates, after a short visit to the Libreville anchorage, Patria anchored off the coast of Lagos where it remained at the time of publication.
We reviewed the draught of the ship at each port visit and found that the ship’s draught always dropped after a stay at the Port of Douala, suggesting it was unloading there.
A ship’s “draught” is the distance from the bottom of the hull (the keel) to the waterline. When loaded, a ship is heavier and sits lower in the water (e.g. a draught of six metres) than when it is unloaded (e.g. a draught of four metres).
Draught is the depth of a ship below the waterline.
In the period from March to July, the Patria made five port calls to Douala and each time the draught decreased. Conversely, it called four times at the Port of Owendo in Libreville, each time the draught increased, meaning the ship became heavier, suggesting it was loading.
The draught is self-reported by ships but usually when it arrives at ports this kind of data is checked – reporting accurate draught is also a safety issue for ships arriving and departing at ports.
Bellingcat asked the ship’s owners, managers and both ports if items were being transferred from Libreville to Douala but did not receive a response at time of publication.
Brown, the former US Naval Officer and now a Senior Advisor at United Against Nuclear Iran, said Patria’s movements were unusual.
“A sanctioned vessel linked to a prior military logistics shipment spending nearly six months operating between a small cluster of West African ports, Douala, and Owendo, without returning to a clear commercial trading pattern warrants scrutiny,” Brown told us.
“While innocent explanations such as mechanical issues, commercial disputes, lack of cargo, chartering delays, or prolonged maintenance are possible, the combination of repeated regional port calls, extended periods at anchor, and an apparent absence of a normal point-to-point trading cycle is atypical for a merchant vessel.”
He added that the current period of more than 30 days at the Lagos Anchorage, in particular, is noteworthy.
David Soud, Head of Research and Analysis at I.R Consilium also told Bellingcat that Patria’s prolonged Lagos Anchorage could have innocent explanations such as its need for ongoing repairs, or that its operators were out of money, but added that there could also be more calculated reasons and it was laying low for a while.
Bellingcat analysed AIS data from Lagos Anchorage and found that while there has been high congestion, no other RoRo or container vessel waited longer than 10 days to enter the port in the period that Patria has been at Lagos Anchorage. At time of writing, Patria has been in anchorage for more than 30 days.
Regarding the Patria’s apparent deliveries of cargo between Libreville in Gabon, and Douala in Cameroon, Soud told Bellingcat:
“Given the vessel’s history of transporting military equipment to African seaports for overland delivery to Russian and allied forces in the Sahel, it’s not out of the question that some form of supplies for Russian or other forces could be picked up in Gabon, whose government has developed a closer relationship with Moscow, to be discharged in Douala, which is the main entry point for goods going to Central African Republic.”
Bellingcat asked the Nigerian Ports Authority why Patria had been in anchorage for so long, whether it had applied to dock and whether the port was aware of its sanctioned status but did not receive a response at time of publication.
The ports of Douala in Cameroon and Owendo in Libreville, Gabon did not respond to Bellingcat’s requests for comment about the Patria’s visits and the cargo it was carrying.
Bellingcat also contacted the two companies connected to the vessel – Hanro Shipping and Sakhalin Shipping Company which are listed as the vessel’s owner and manager respectively in sanctions documents. We also contacted the company connected to JS Gratitude. We did not receive a response at time of publication.
Youri van der Weide, Galen Reich, Yörük Işık contributed to this report.
Cover image: Planet Lab image shows the Patria at the Port of Douala, Cameroon, on April 17, 2026. Credit: Planet Labs PBC.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
Europe faced a ransomware onslaught in the first half of 2026 that sets a troubling precedent for the remainder of the year. According to Cyble Research and Intelligence Labs (CRIL), the region experienced 866 documented ransomware attacks, 51 confirmed data breach incidents, and 7 initial access sales between January and June 2026. These figures represent not just a volume problem, but a fundamental shift in how threat actors are organizing, targeting, and monetizing their operations within European territory.
What distinguishes the ransomware threats in Europe from other global regions is the concentration of power among a small number of highly sophisticated threat actors. While the threat ecosystem encompasses dozens of groups, five dominant ransomware operators account for approximately 55% of all documented activity. This concentration creates predictability—European security leaders can now identify, profile, and build specific defensive strategies against known adversaries.
The Five Dominant Ransomware Groups Targeting Europe
1. Qilin: The Biggest Ransomware Threat in Europe
Attack Volume: 158 documented incidents (18.2% of regional total)
Qilin stands as the dominant ransomware threat actor targeting Europe, commanding operational superiority through sophisticated affiliate management, rapid exploit weaponization, and industry-specific targeting intelligence.
Qilin's dominance stems from understanding European organizational economics. Construction projects operate under time-sensitive contracts with contractually-defined penalties for delay. A single day of downtime on a €50 million construction project can trigger cascading costs exceeding €100,000. This economic reality translates directly into ransom payment likelihood, making Qilin's targeting strategy rational and highly effective.
The group maintains an extensive affiliate network capable of concurrent operations across multiple European nations. Evidence suggests Qilin has compartmentalized its operations: initial access brokers handle reconnaissance and network compromise, mid-tier operators manage lateral movement and privilege escalation, and final-stage operators execute encryption and exfiltration. This division of labor enables rapid scaling and reduces attribution risk.
Why Qilin Dominates:
Industry Expertise: Deep understanding of construction project timelines and financial exposure
Exploit Library: Rapid weaponization of both known and zero-day vulnerabilities
Data Monetization: Established data brokerage partnerships ensure exfiltrated data reaches buyers
European Security Implications: Organizations in construction, professional services, and manufacturing should treat Qilin as their primary threat actor concern. Defensive strategies must prioritize data exfiltration prevention, network segmentation, and immutable backup infrastructure.
2. The Gentlemen: The Rising European Threat
Attack Volume: 144 documented incidents (16.6% of regional total)
The Gentlemen represent an emerging threat actor that has achieved remarkable scale in a relatively short operational window. Unlike established groups that evolved from other cybercriminal operations, The Gentlemen appear purpose-built for ransomware-as-a-service operations.
Geographic Concentration:
Europe: 144 attacks (primary focus)
United States: 100 attacks (secondary focus)
Thailand: 35 attacks (supply-chain targeting)
South Asia: 40 attacks
Worldwide Sectoral Targeting:
Construction: 45 incidents
Manufacturing: 56 incidents
Healthcare: 37 incidents
IT & ITES: 36 incidents
Professional Services: 29 incidents
Operational Characteristics:
The Gentlemen's rapid emergence and sustained growth suggest significant operational funding and technical sophistication. The group's geographic diversification—maintaining European dominance while aggressively expanding into Asia-Pacific—indicates either organizational scale or partnerships with regional threat actors.
Notably, The Gentlemen's Thailand targeting (35 incidents) suggests supply-chain attack sophistication. By compromising manufacturing and logistics operations in Thailand, the group can leverage these beachheads for downstream attacks against Western European organizations. This cross-continental supply-chain targeting represents a significant evolution in ransomware operational sophistication.
Key Distinction: While Qilin focuses on maximizing ransom payments from individual targets, The Gentlemen appear to prioritize operational scale and geographic expansion. This suggests the group may be building toward either:
A mega-RaaS platform rivaling LockBit's historical dominance
Preparation for potential acquisition or partnership with state-sponsored actors
Geographic arbitrage—leveraging lower prosecution risk in developing nations while maintaining European operations
European Security Implications: The Gentlemen's emergence signals market competition is intensifying. Organizations should monitor this group's operational evolution closely, as aggressive growth often precedes operational mistakes that create defensive opportunities.
3. LockBit: The Persistent Legacy Threat
Attack Volume: 61 documented incidents (7.0% of regional total)
LockBit's presence in European targeting represents a significant finding given sustained law enforcement pressure and multiple platform disruption attempts. Despite being targeted by coordinated international takedown operations, LockBit maintained operational capability throughout H1 2026.
Geographic Concentration:
Europe: 61 attacks (Primary operations)
North America: 47 attacks (Secondary operations)
Distributed: Global presence indicating resilient infrastructure
Worldwide Sectoral Targeting:
Construction: 22 incidents
Manufacturing: 22 incidents
Government & LEA: 12 incidents
Healthcare: 19 incidents
Professional Services: 13 incidents
Operational Resilience:
LockBit's continued operations despite international enforcement actions demonstrate several critical lessons:
Affiliate Compartmentalization: By maintaining separate operational cells, LockBit can continue operations even when core infrastructure is disrupted
Rapid Rebranding: The group has adopted multiple identities and platform variants, complicating attribution
Infrastructure Redundancy: Multiple command-and-control server locations across jurisdictions with varying law enforcement cooperation levels
Operator Recruitment: Continuous recruitment of new affiliates from emerging cybercriminal talent pools
The group's continued viability suggests that law enforcement actions, while disruptive, are insufficient to eliminate established RaaS operations. Organizations cannot rely on law enforcement intervention as a defensive strategy; they must assume LockBit and similar groups will remain operational threats indefinitely.
European Security Implications: LockBit should remain on European security teams' active threat monitoring lists. The group maintains technical sophistication, access to critical zero-day exploits, and demonstrated willingness to target European critical infrastructure.
4. Akira: The Opportunistic European Operator
Attack Volume: 59 documented incidents (6.8% of regional total)
Akira represents a secondary-tier ransomware group with focused European operations. The group demonstrates strong preference for Manufacturing and Construction sectors, suggesting industry-specific expertise or targeted affiliate recruitment.
Geographic Concentration:
Europe & UK: 59 attacks (Secondary focus)
North America: 268 attacks (Primary focus)
Secondary: Limited operations in other regions
Worldwide Sectoral Targeting:
Manufacturing: 54 incidents
Construction: 57 incidents
Professional Services: 47 incidents
Consumer Goods: 34 incidents
Healthcare: 13 incidents
Operational Profile:
Akira's disproportionate North American presence (268 attacks) with lower European activity (59 attacks) suggests the group may have established affiliate networks in North America with secondary capacity for European operations. The strong manufacturing and construction focus mirrors Qilin's strategy, indicating these sectors offer superior ransom payment likelihood across multiple geographic markets.
European Security Implications: While not as immediately threatening as Qilin or The Gentlemen, Akira's persistent operations warrant inclusion in threat modeling exercises. European manufacturing and construction organizations should monitor Akira's affiliate recruitment channels and tactical innovations.
5. Dragonforce: The Supply-Chain Specialist
Attack Volume: 54 documented incidents (6.2% of regional total)
Dragonforce rounds out the top-five European threat actors with apparent specialization in Manufacturing and Technology sectors, suggesting possible supply-chain attack capabilities.
Geographic Concentration:
North America: 135 attacks (Primary focus)
Europe & UK: 54 attacks (Secondary focus)
Secondary: Limited global operations
Worldwide Sectoral Targeting:
Manufacturing: 31 incidents
Construction: 48 incidents
Professional Services: 28 incidents
Food & Beverages: 9 incidents
Healthcare: 9 incidents
Operational Pattern:
Dragonforce's heavy US focus with secondary European operations suggests the group may be leveraging North American-based supply chains to gain access to European targets. Manufacturing supply chains are deeply interconnected across transatlantic partners; compromising US manufacturers could provide lateral access into European operations.
European Security Implications: European manufacturing organizations should implement aggressive third-party risk management programs, particularly for US-based suppliers. Dragonforce's supply-chain sophistication suggests the group may bypass direct targeting in favor of compromising upstream vendors.
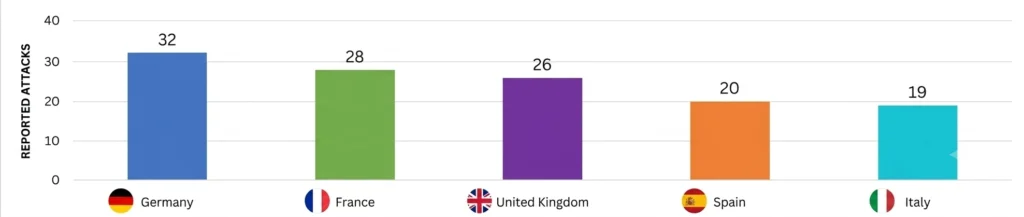
Top five European Nations Attacked by Ransomware Actors in 2026 H1 (Source: Cyble Research)
Germany: The Manufacturing Battleground
Attack Volume: 155 ransomware attacks (17.9% of regional total)
Germany's position as Europe's manufacturing powerhouse places it at the center of ransomware targeting campaigns. The nation's industrial sector—encompassing automotive, machinery, chemicals, and precision manufacturing—represents the most valuable ransomware target set in Europe.
German organizations represent an optimal target combination: high asset value, supply-chain criticality, strong operational technology integration, and proven willingness to pay ransoms to maintain production schedules. Additionally, Germany's federal structure creates jurisdictional complexity that may slow law enforcement response.
The nation's Mittelstand (mid-market manufacturing firms) are particularly vulnerable—large enough to justify ransom payments, but sometimes lacking enterprise-grade security infrastructure.
Defensive Priority: German manufacturing organizations should assume Qilin, The Gentlemen, Akira, and Dragonforce all maintain active operations targeting their sector. Network segmentation between IT and operational technology (OT) environments should be elevated to critical priority.
United Kingdom: The Financial Services Crosshairs
Attack Volume: 138 ransomware attacks (15.9% of regional total)
The UK faces a different threat profile than Germany, driven primarily by London's position as a global financial services hub. While manufacturing is targeted, Banking, Financial Services, and Insurance (BFSI) organizations command disproportionate attention.
Threat Actor Concentration:
Qilin: 26 attacks
The Gentlemen: 26 attacks
LockBit: 18 attacks
Akira: 13 attacks
Dragonforce: 11 attacks
Sectoral Breakdown:
BFSI: 38 incidents (concentrated targeting)
Technology: 32 incidents
Retail: 26 incidents
Professional Services: 24 incidents
Government & LEA: 16 incidents
Why the UK Is Targeted
London's financial services ecosystem manages trillions in assets, making it extraordinarily valuable to data-exfiltrating threat actors. BFSI organizations hold customer financial data, internal financial records, and strategic information that commands premium prices on dark web marketplaces.
Additionally, regulatory requirements (FCA, PRA, etc.) create pressure for rapid ransom payment to avoid breach notification delays that could trigger regulatory sanctions.
Data Exfiltration Risk: The UK's status as a financial services hub makes it particularly vulnerable to data-centric attack strategies. Organizations should assume that successful breach attempts will include aggressive data exfiltration alongside encryption deployment.
Defensive Priority: UK BFSI organizations must implement robust data loss prevention (DLP), encryption for data in transit and at rest, and aggressive monitoring for unauthorized data access or exfiltration attempts.
France: The Balanced Threat
Attack Volume: 119 ransomware attacks (13.7% of regional total)
France experiences balanced threat distribution across multiple sectors, reflecting both its manufacturing capacity and significant professional services sector.
Threat Actor Concentration:
Qilin: 28 attacks
The Gentlemen: 28 attacks
LockBit: 15 attacks
Akira: 14 attacks
Dragonforce: 8 attacks
Sectoral Breakdown:
Professional Services: 26 incidents
Manufacturing: 24 incidents
Construction: 19 incidents
Technology: 14 incidents
Healthcare: 10 incidents
Why France Faces Distributed Threat
As Europe's second-largest economy, France is attractive to ransomware operators across multiple sectors. The nation's professional services sector (legal, accounting, consulting) is particularly valuable for data exfiltration, while manufacturing remains a consistent target.
Defensive Priority: French organizations should implement sector-specific defensive strategies: professional services firms should prioritize client data protection and DLP, while manufacturing organizations should focus on OT segmentation and operational resilience.
Italy: The Construction and Manufacturing Hub
Attack Volume: 115 ransomware attacks (13.3% of regional total)
Italy faces concentrated targeting in construction and manufacturing sectors, with particular pressure on small-to-medium enterprises in industrial regions.
Threat Actor Concentration:
Qilin: 19 attacks
The Gentlemen: 18 attacks
LockBit: 12 attacks
Akira: 16 attacks
Dragonforce: 8 attacks
Sectoral Breakdown:
Construction: 48 incidents (concentrated)
Manufacturing: 38 incidents
Professional Services: 18 incidents
Retail: 14 incidents
Why Italy Faces Sector-Specific Pressure
Italy's construction industry is particularly vulnerable to ransom attacks due to tight project timelines and significant financial exposure. The nation's manufacturing sector, while sophisticated, sometimes operates with legacy infrastructure that creates exploitation opportunities.
Defensive Priority: Italian construction and manufacturing organizations should prioritize incident response readiness, backup infrastructure resilience, and supply-chain risk management.
Spain: The Emerging Risk
Attack Volume: 87 ransomware attacks (10.0% of regional total)
Spain experiences lower absolute attack volume than Germany, UK, France, or Italy, but faces concentrated pressure in manufacturing and professional services sectors.
Threat Actor Concentration:
Qilin: 20 attacks
The Gentlemen: 18 attacks
LockBit: 8 attacks
Akira: 12 attacks
Dragonforce: 7 attacks
Sectoral Breakdown:
Manufacturing: 28 incidents
Professional Services: 19 incidents
Construction: 16 incidents
Technology: 10 incidents
Regional Observation: Spain's lower attack volume may reflect either lower overall ransomware targeting or more effective defensive implementations. Spanish security teams should not interpret lower numbers as reduced threat but rather as a baseline for future comparison.
Where European Organizations Face Maximum Risk: A Sectoral Analysis
Construction: The Ransomware Goldmine
Attack Volume: 107 documented incidents (58% of all sector targeting across regions – not just in Europe – analyzed)
Construction organizations face disproportionate ransomware targeting across the entire European region. This concentration reflects understood economic vulnerabilities that threat actors exploit with precision.
Why Construction Is Targeted
Time-Sensitive Financial Exposure: Construction projects operate under contractually-defined timelines. Each day of delay triggers cascading costs, financial penalties, and potential contract termination. Organizations facing potential loss of €50-100 million contracts will prioritize rapid recovery over law enforcement involvement.
Operational Technology Integration: Modern construction increasingly relies on Building Information Modeling (BIM), cloud-based project management, and real-time equipment tracking. This IT/OT convergence creates exploitation pathways unavailable in purely IT-based industries.
Supply-Chain Complexity: Construction projects depend on dozens of subcontractors and suppliers. Compromising a single upstream supplier can provide lateral access into prime contractors.
Financial Pressure: Construction firms often operate with tight cash flow, making ransom negotiation essential to preserve solvency.
Accessibility: Many construction firms, particularly smaller regional players, operate with basic security infrastructure, creating easy exploitation opportunities.
European Construction Risk Mapping:
Germany (14 attacks): Heavy machinery and precision manufacturing integration
Supply-Chain Due Diligence: Implement security requirements for subcontractors and equipment suppliers
Professional Services: The Data Exfiltration Target
Attack Volume: 86 documented incidents
Professional services firms (law, accounting, consulting) face sophisticated targeting driven by data exfiltration opportunities rather than operational disruption pressure.
Why Professional Services Are Targeted
Client Confidentiality Risk: Legal privilege and client confidentiality create existential regulatory and reputational exposure. Threat actors leverage this to demand premium ransoms.
Sensitive Data Concentration: Professional services firms accumulate client financial records, litigation strategies, tax information, and corporate secrets—all commanding premium dark web prices.
Regulatory Exposure: GDPR breach notification requirements create pressure for rapid response and ransom payment to avoid regulatory sanctions.
Supply-Chain Position: Professional services firms advise major corporations; compromising advisors provides indirect access to clients.
Trust-Based Business Model: Client relationships depend on confidentiality. A single breach can destroy long-term client relationships and firm reputation.
European Professional Services Risk:
France (16 attacks): Concentrated targeting of Paris-based firms
Germany (16 attacks): Heavy focus on Frankfurt financial advisory firms
UK (17 attacks): London-based legal and accounting partnerships
Italy (6 attacks): Milan and Rome-based advisory firms
Spain (7 attacks): Barcelona and Madrid professional services sector
Key Finding: Professional services firms experience disproportionate data breach incidents (exfiltration with confirmed leak activity) compared to other sectors. Of the 51 total data breach incidents across Europe and UK, professional services represents a concentrated target.
Defensive Recommendations:
Client Data Segregation: Isolate client data on separate network segments with distinct access controls
Data Loss Prevention (DLP): Deploy DLP solutions with aggressive egress controls monitoring client data exfiltration
Encryption Standards: Implement client-facing encryption for all sensitive communications
Access Auditing: Maintain comprehensive logs of all access to sensitive client data
Ransomware-Specific Insurance: Consider cyber insurance with specific ransomware coverage addressing confidentiality exposure
Manufacturing: The Supply-Chain Critical Target
Attack Volume: 123 documented incidents
European manufacturing organizations face sophisticated, supply-chain-aware threat actors who understand production dependencies and downtime economics.
Why Manufacturing Is Targeted
Operational Technology Integration: Modern factories integrate IT and OT systems. Ransomware deployment can halt production lines, creating catastrophic financial exposure.
Supply-Chain Criticality: Manufacturing downtime cascades through dependent enterprises. A single organization's compromise can impact dozens of downstream customers.
Export Dependency: European manufacturers serve global markets. Production delays translate directly into lost revenue and market share.
Legacy Infrastructure: Many manufacturing facilities operate aging, unpatched systems integrated with newer IT infrastructure, creating exploitation bridges.
Financial Pressure: Manufacturing organizations face razor-thin margins; production downtime can drive solvency crises.
UK (14attacks): Aerospace, automotive, precision manufacturing
Critical Vulnerability Pattern: Manufacturing organizations are disproportionately targeting known, exploitable vulnerabilities in critical infrastructure appliances (network appliances, security tools, identity systems). Rather than deploying zero-days, threat actors exploit patched vulnerabilities that organizations have not implemented.
Defensive Recommendations:
OT/IT Segmentation: Implement airgapped network separation between operational technology and corporate IT
Vulnerability Management Prioritization: Focus patching efforts on network appliances, security tools, and identity systems
Industrial Control System (ICS) Monitoring: Deploy behavioral monitoring for unusual activity on manufacturing control systems
Healthcare organizations face a unique threat dynamic where ransomware directly endangers patient safety, creating existential operational pressure distinct from financial threats.
Why Healthcare Is Targeted
Patient Safety Risk: Ransomware disables critical medical systems (diagnostic equipment, pharmaceutical dispensing, patient records). Unlike other industries, downtime directly threatens life.
Regulatory Pressure: GDPR, HIPAA-equivalent regulations, and national privacy laws create breach notification requirements that incentivize ransom payment.
Data Value: Patient medical records, pharmaceutical research data, and clinical trial information command premium dark web prices.
Continuous Operation Requirement: Unlike manufacturing or services, healthcare cannot delay critical procedures. The operational pressure to pay ransoms is existential.
System Complexity: Healthcare IT environments integrate numerous legacy systems (PACS, EHR, medical devices) with varying security architectures.
European Healthcare Risk Distribution:
Germany (14 attacks): Concentrated in Berlin, Munich, and Frankfurt urban medical centers
Austria (2 attacks): private healthcare sector
France (5 attacks): Concentrated in Paris and Lyon region hospitals
Switzerland (3 attacks): medical centers
Spain (3 attacks): Barcelona and Madrid hospital networks
Critical Finding: Healthcare organizations experience disproportionately high data breach incident rates, suggesting organized threat actors specifically target health information exfiltration.
Defensive Recommendations:
Clinical System Isolation: Implement complete network separation between clinical systems and corporate IT
Redundant Critical Systems: Deploy redundant diagnostic and pharmaceutical systems capable of manual operation
Patient Data Encryption: Implement end-to-end encryption for all patient medical records
Breach Response Planning: Develop healthcare-specific incident response plans addressing patient notification and continuity of care
Medical Device Security: Implement inventory and monitoring for all connected medical devices
Supply-Chain Assessment: Assess security of medical device manufacturers and pharmaceutical distributors
The Data Exfiltration Reality: Beyond Encryption
Confirmed Data Breaches: 51 Incidents Across Europe and UK
While ransomware attacks total 866, only 51 incidents resulted in confirmed data breaches and leaks (5.9% confirmation rate). This apparent low percentage masks a critical operational truth: organizations cannot distinguish between encryption-only attacks and data exfiltration scenarios until exfiltration attempts or threats emerge.
Data Breach Distribution by Sector:
Sector
Confirmed Breaches
Percentage
BFSI
9
17.6%
Telecom
9
17.6%
Retail
8
15.7%
Government & LEA
6
11.8%
Media & Entertainment
5
9.8%
Technology
4
7.8%
Healthcare
4
7.8%
Automotive
3
5.9%
Construction
2
3.9%
Education
1
2.0%
Others
6
11.8%
Critical Observation: BFSI and Telecom sectors experience disproportionate data breach incidents, suggesting these industries are specifically targeted for data exfiltration rather than operational disruption. The strategic implication is clear: threat actors targeting financial and telecommunications organizations prioritize data monetization over ransom payment.
Most Active Threat Actors in Data Exfiltration: The Leak Economy
Primary Exfiltration Actors:
Actor
Confirmed Leak Posts
Targeting Pattern
tanaka
6
Industry-agnostic, global operations
kazutlg
4
BFSI and Professional Services focus
aslan1
2
Government and Technology sectors
darkcybervault
2
Retail and Professional Services
breach3d
2
Technology focus
frog
2
Diverse sector targeting
ken6k
2
BFSI concentration
max9898
2
Retail and Technology
worldrdp
2
Technology sector
zyad2drkwb
2
Government targeting
zoozkooz
2
Diverse sector
mr_x1
1
Retail focus
ventuuas
1
Professional Services
Others
18
Distributed diverse targeting
Strategic Finding: While Qilin, The Gentlemen, and LockBit dominate ransomware attack volume, data exfiltration is fragmented across numerous smaller actors, including tanaka (6 posts), kazutlg (4 posts), and dozens of single-incident operators. This suggests a mature data brokerage ecosystem where extracted data is resold to specialized exfiltration actors.
Dark Web Data Marketplace Activity:
916 unique domains impacted by data leaks
Approximately 86 distinct leak posts across dark web channels
Data types: Financial records, customer PII, medical records, intellectual property, trade secrets
Implication: Organizations can no longer assume encrypted data is "lost forever" if backups are restored. Exfiltrated data will be monetized regardless of whether organizations pay ransoms. Data loss prevention becomes as critical as ransomware detection.
Geopolitical and Ideological Dimensions: The Activism-Cybercrime Convergence
Pro-Russian Hacktivism: Blurred Lines Between Ideology and Profit
H1 2026 witnessed increasing overlap between geopolitically motivated hacktivism and financially motivated cybercrime, particularly among pro-Russian collectives targeting NATO-aligned European nations.
Key Threat Actors to Monitor
NoName057(16) - The Pro-Russian DDoS Coalition
Primary Activity: Large-scale DDoS attacks against NATO-aligned governments and Ukrainian supporters
Secondary Activity: Data exfiltration for monetization
Geographic Targets: Estonia, UK, Ukraine, Italy, Spain, France, Poland, Norway, Denmark, Lithuania, Latvia, Czech Republic, Germany, Moldova
Operational Pattern: Coordinated DDoS campaigns often accompanied by data theft and subsequent leak activity
Operational Evolution: NoName057(16) began as a purely activist collective claiming ideological motivation (anti-NATO, pro-Russia). By H1 2026, the group had evolved to include data exfiltration and monetization—suggesting either organizational evolution or infiltration by financially motivated threat actors.
Strategic Implication: European organizations cannot compartmentalize threat modeling. A geopolitically motivated attack that begins as a DDoS campaign can transition into ransomware deployment when exfiltration opportunities present themselves.
Strategic Defense Recommendations for European Organizations
Prioritized Defensive Roadmap
Based on CRIL's H1 2026 regional data, European security leaders should prioritize defensive investments in the following sequence:
Defensive Focus: Data encryption, DLP with aggressive egress controls, cyber insurance
If You're in Healthcare:
Primary Threat: Qilin, The Gentlemen, LockBit
Secondary Threat: Data exfiltration operators
Vulnerability: Patient safety risk, critical operational pressure, medical device security
Defensive Focus: Clinical system isolation, redundant critical systems, incident response for operational continuity
Conclusion: The European Ransomware Reality
Europe and the UK face a mature, organized ransomware ecosystem dominated by five sophisticated threat actors who have developed deep understanding of regional economic vulnerabilities. The threat is not random or opportunistic—it is strategic, targeted, and evolved.
Key Takeaways:
Five groups dominate: Qilin (158 attacks), The Gentlemen (144), LockBit (61), Akira (59), and Dragonforce (54) collectively account for 476 of 866 documented attacks (55%). European security leaders can build specific defensive strategies against known adversaries.
Geography matters: Germany, UK, France, Italy, and Spain face distinct threat profiles. Security strategies must be regionally and sector-specific, not generic.
Sectors are targeted deliberately: Construction, Professional Services, and Manufacturing are not randomly selected—they face extraordinary pressure due to economic vulnerabilities that threat actors systematically exploit.
Data exfiltration is the primary leverage: Of 866 attacks, only 51 resulted in confirmed breaches—but this understates the risk. Organizations must assume all breaches involve data exfiltration and cannot rely on backup restoration alone.
Patch management is the primary defense: Nearly 90% of exploited vulnerabilities had patches available. Disciplined patch management, particularly for network appliances, would prevent the vast majority of successful attacks.
Known vulnerabilities are the current threat: Despite awareness of zero-day sophistication, threat actors continue exploiting known vulnerabilities because patches lag adoption. This creates a predictable exploitation window that defensive teams can close.
For European security leaders, the path forward is to understand your regional threat actors, prioritize critical infrastructure protection, implement robust data protection measures, and establish resilient backup and recovery infrastructure. The threat is severe, but it is also understood and defensible. The question is not whether European organizations will face ransomware attacks in the remainder of 2026 and beyond—the data confirms they will. The question is whether they will be prepared.
This article is the result of a collaboration with The Sunday Times. You can find their corresponding piece here.
The Kinahan cartel, led by Christy Kinahan (centre) and his sons Christopher Jr (left) and Daniel (right), controls one of the most powerful transnational crime groups in the world from the Emirates. Source: Supplied
A key leader of the Kinahan cartel who is wanted by authorities around the world and has been living in hiding in Dubai for a decade has just had his Emirates residence permit renewed.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
A Bellingcat and The Sunday Times review of public immigration records from the United Arab Emirates (UAE) has revealed that Christopher Kinahan Jr, the son of cartel founder Christy Kinahan, was issued with a new visa less than two weeks ago.
This is despite his status as a sanctioned individual who is the subject of a $5 million reward from the US government for information leading to his arrest.
Our analysis has also exposed the residence statuses of the crime gang’s other sanctioned leaders who remain at large in Dubai. The records include previously unknown companies where the cartel members are purportedly employed.
The US government has offered a $5 million reward for information leading to the arrest or conviction of Christopher Kinahan Jr for participating in transnational organised crime, namely narcotics trafficking and money laundering.
It comes after Christopher Jr’s older brother Daniel Kinahan lost his final appeal in Dubai last week to prevent being extradited back to Ireland. He is the second key figure of the crime group to be apprehended in the Emirates following his high-profile arrest in April.
The Kinahan Organised Crime Group is a $1.5 billion transnational network involved in drug trafficking, money laundering and arms smuggling. Investigators have connected it to Iran’s intelligence services and the Lebanon-based militant group Hezbollah.
The cartel’s senior leadership – Christy Kinahan, 69, and his sons Daniel, 49, and Christopher Jr, 45, their cousin Ian Dixon, 36, along with associates Sean McGovern, 40, Bernard Clancy, 48, and Johnny Morrissey, 66 – was sanctioned by the US government in 2022.
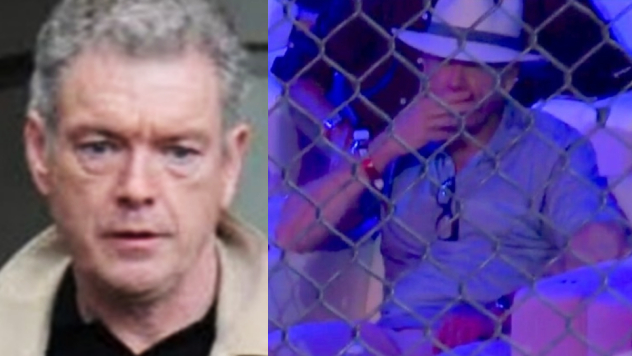
Christopher Kinahan Jr and his father Christy Kinahan, seen in the background of a photo posted to a Dubai restaurant’s social media in 2023.
The UAE reportedly banned the Kinahans from doing business in the wake of the sanctions and the Emiratis also claim to have frozen €200 million in Kinahan assets. However, our findings suggest the cartel is still doing business in the Emirates and its leadership has repeatedly engaged with immigration authorities in the years following the sanctions.
The visa records were accessed through publicly available UAE government websites. We entered data contained in the US government’s sanctions notice, including the gang members’ ID or passport number, birth date and nationality, to view their immigration files.
Action
in Dubai
Six of the seven key cartel figures who were sanctioned by
the US in 2022 lived in Dubai. Cartel lieutenant Sean McGovern was extradited
to Ireland in 2025 and jailed in June.
Daniel Kinahan awaits
extradition from Dubai.
Online
Immigration Records
Our open source review of immigration records shows two members
have active residence
permits. The other two have expired permits.
Chris Kinahan Jr
Active
Permit
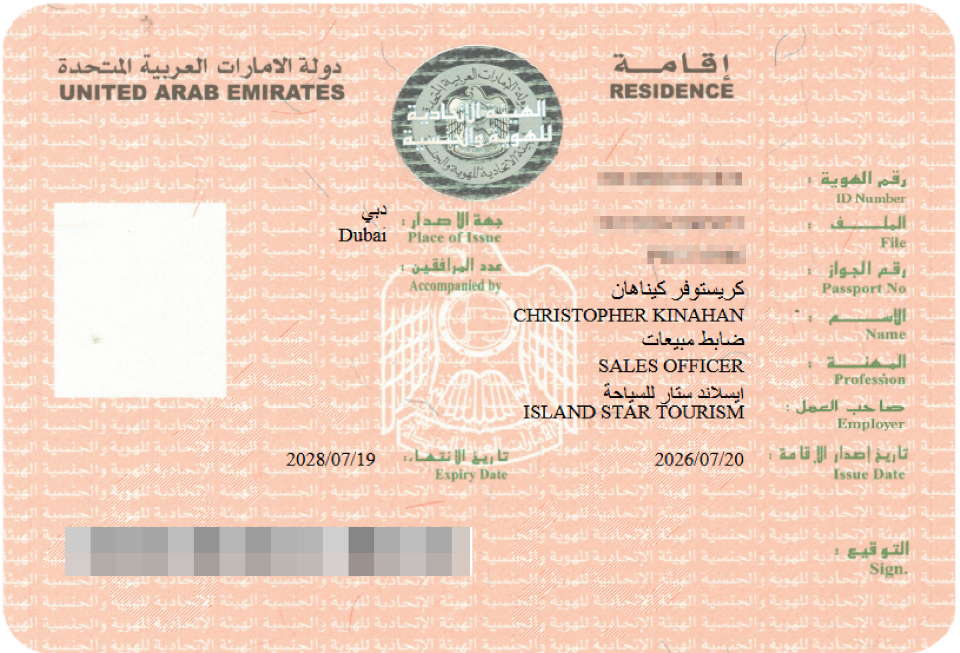
Christopher Kinahan Jr’s residence permit was renewed on July 20
for a two-year period. His previous visa had expired in December
2024. The new residence card lists his employment as “sales
officer” at a company named Island Star Tourism.
Bernard Clancy
Active
Permit
Bernard Clancy’s most recent two-year residence permit was
renewed in January. Like Christopher Jr, Clancy’s stated
profession is “sales officer”, but for a company named Al Matn
Goods Wholesalers LLC.
Christy Kinahan
Expired
Permit
Ian
Dixon
Expired
Permit
Records for Christy Kinahan and Ian Dixon show the residence
permits associated with their available passport numbers have
expired.
Christy Kinahan
Expired
Permit
On his most recent visa, which expired on April 1, Christy
Kinahan’s listed employer is OSA Management Consultancies DWC
LLC. This firm is based at the same Dubai
address as CV Aviation Consulting Services DWC LLC,
another company reportedly
linked to the cartel.
Ian Dixon
Expired
Permit
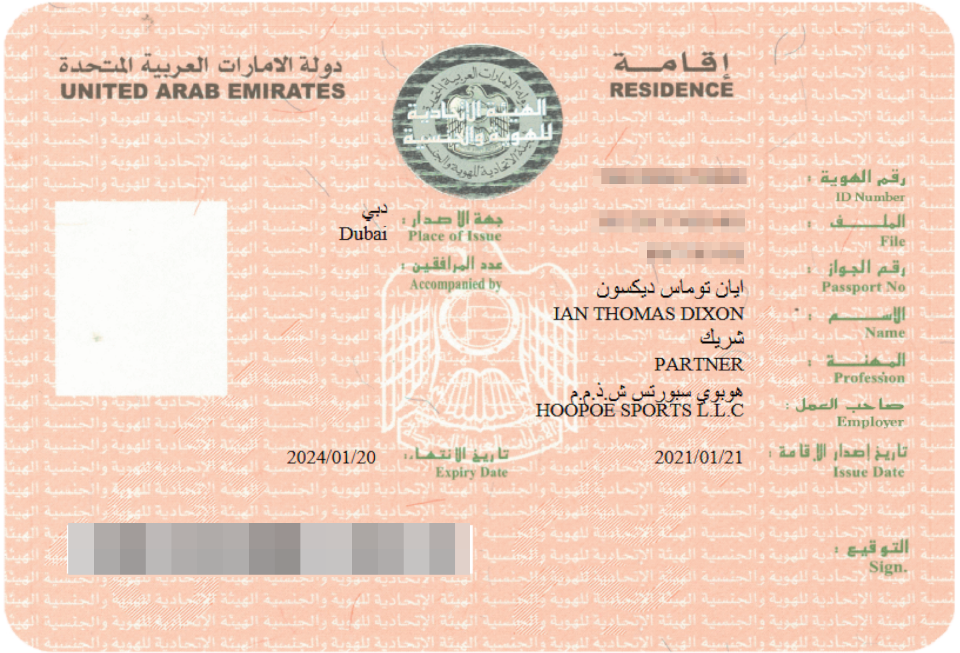
Dixon’s employer listed on his most recent visa was Hoopoe
Sports LLC, one of the firms sanctioned by the US for being
“owned or controlled” by Dixon.
Christy
Kinahan
The UAE imposes a
fine for each day a person stays in the country after
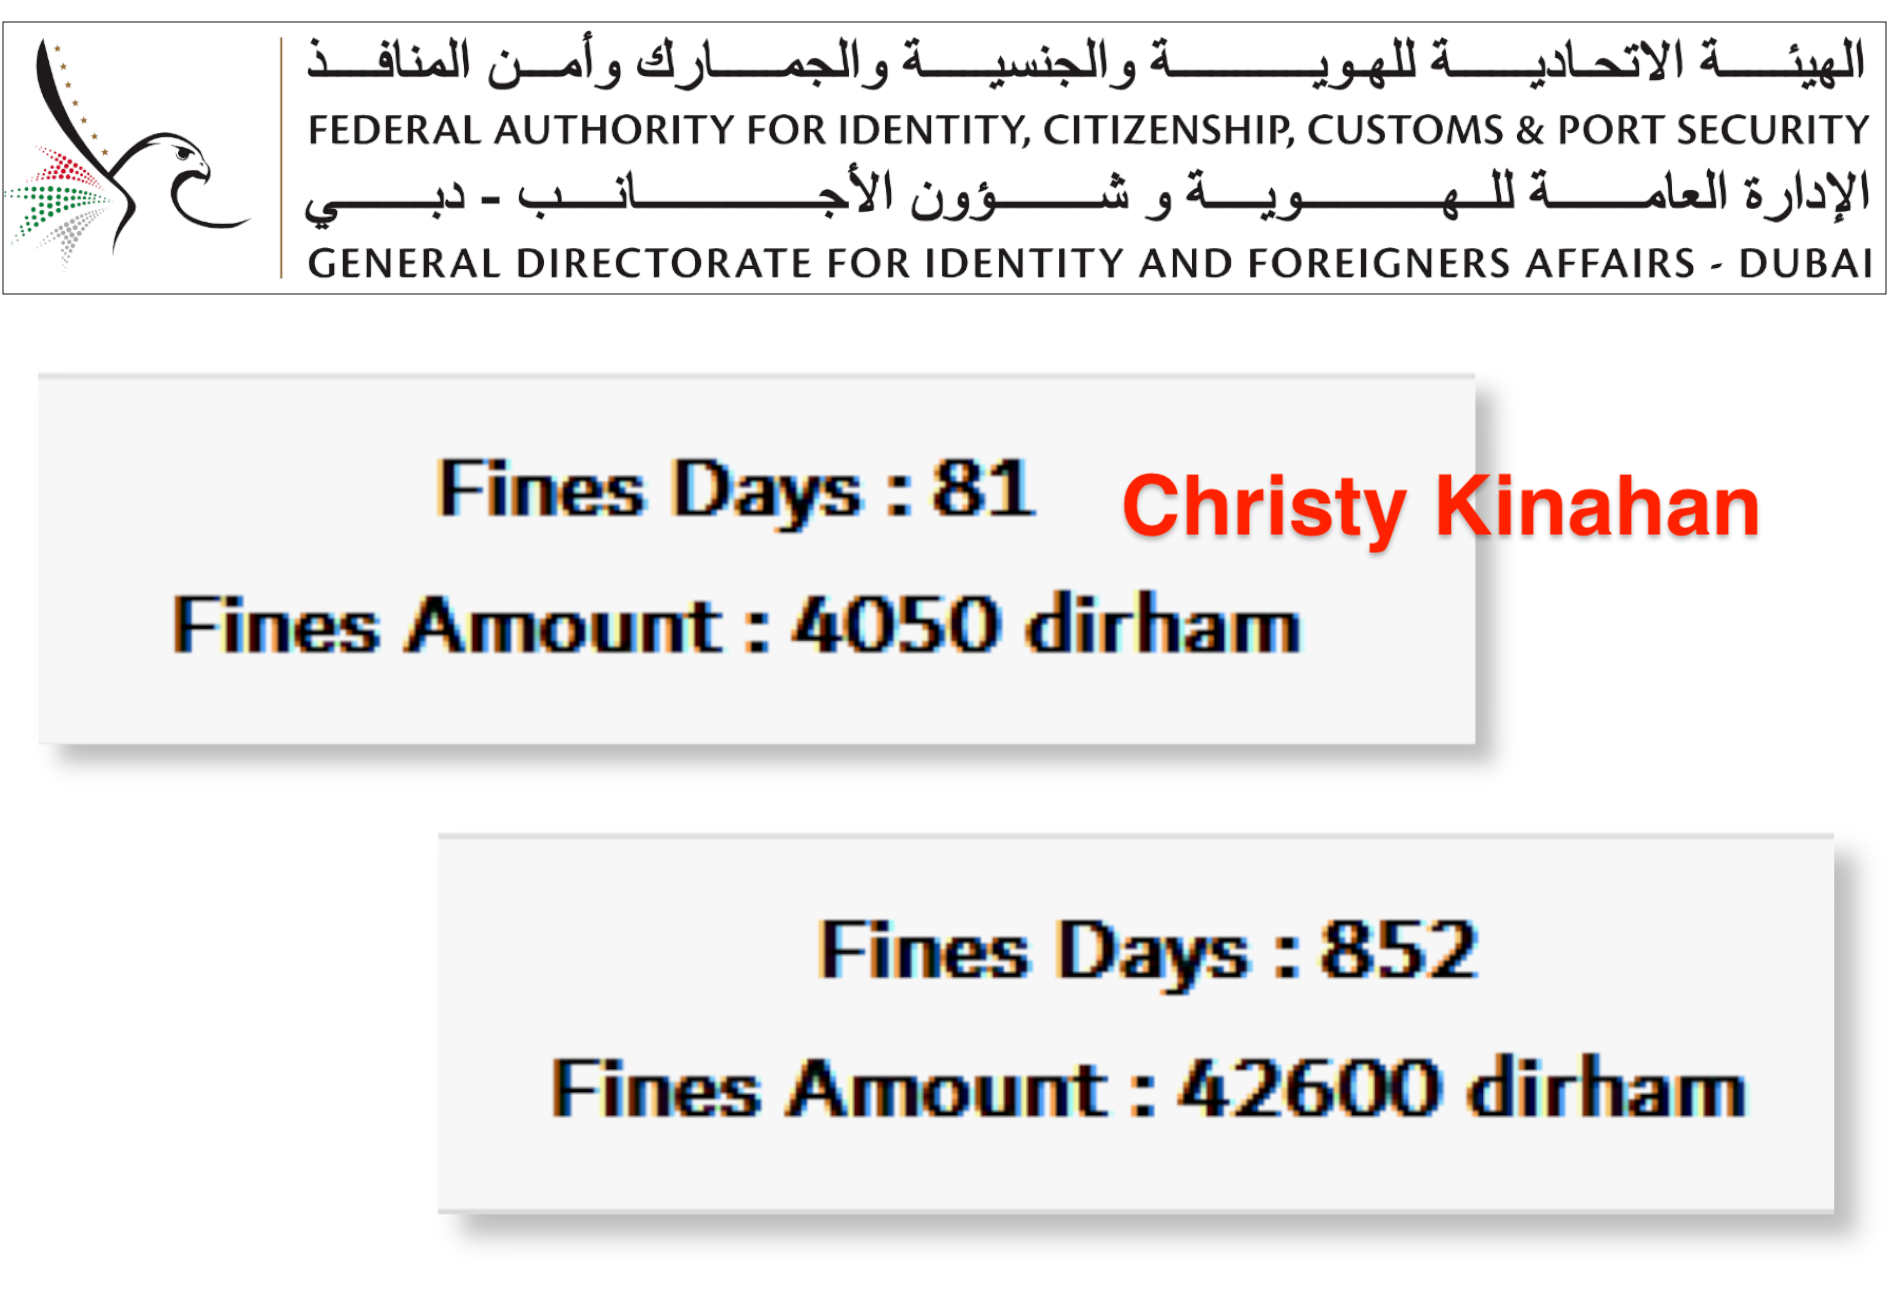
their visa expires. A Dubai government portal shows Christy
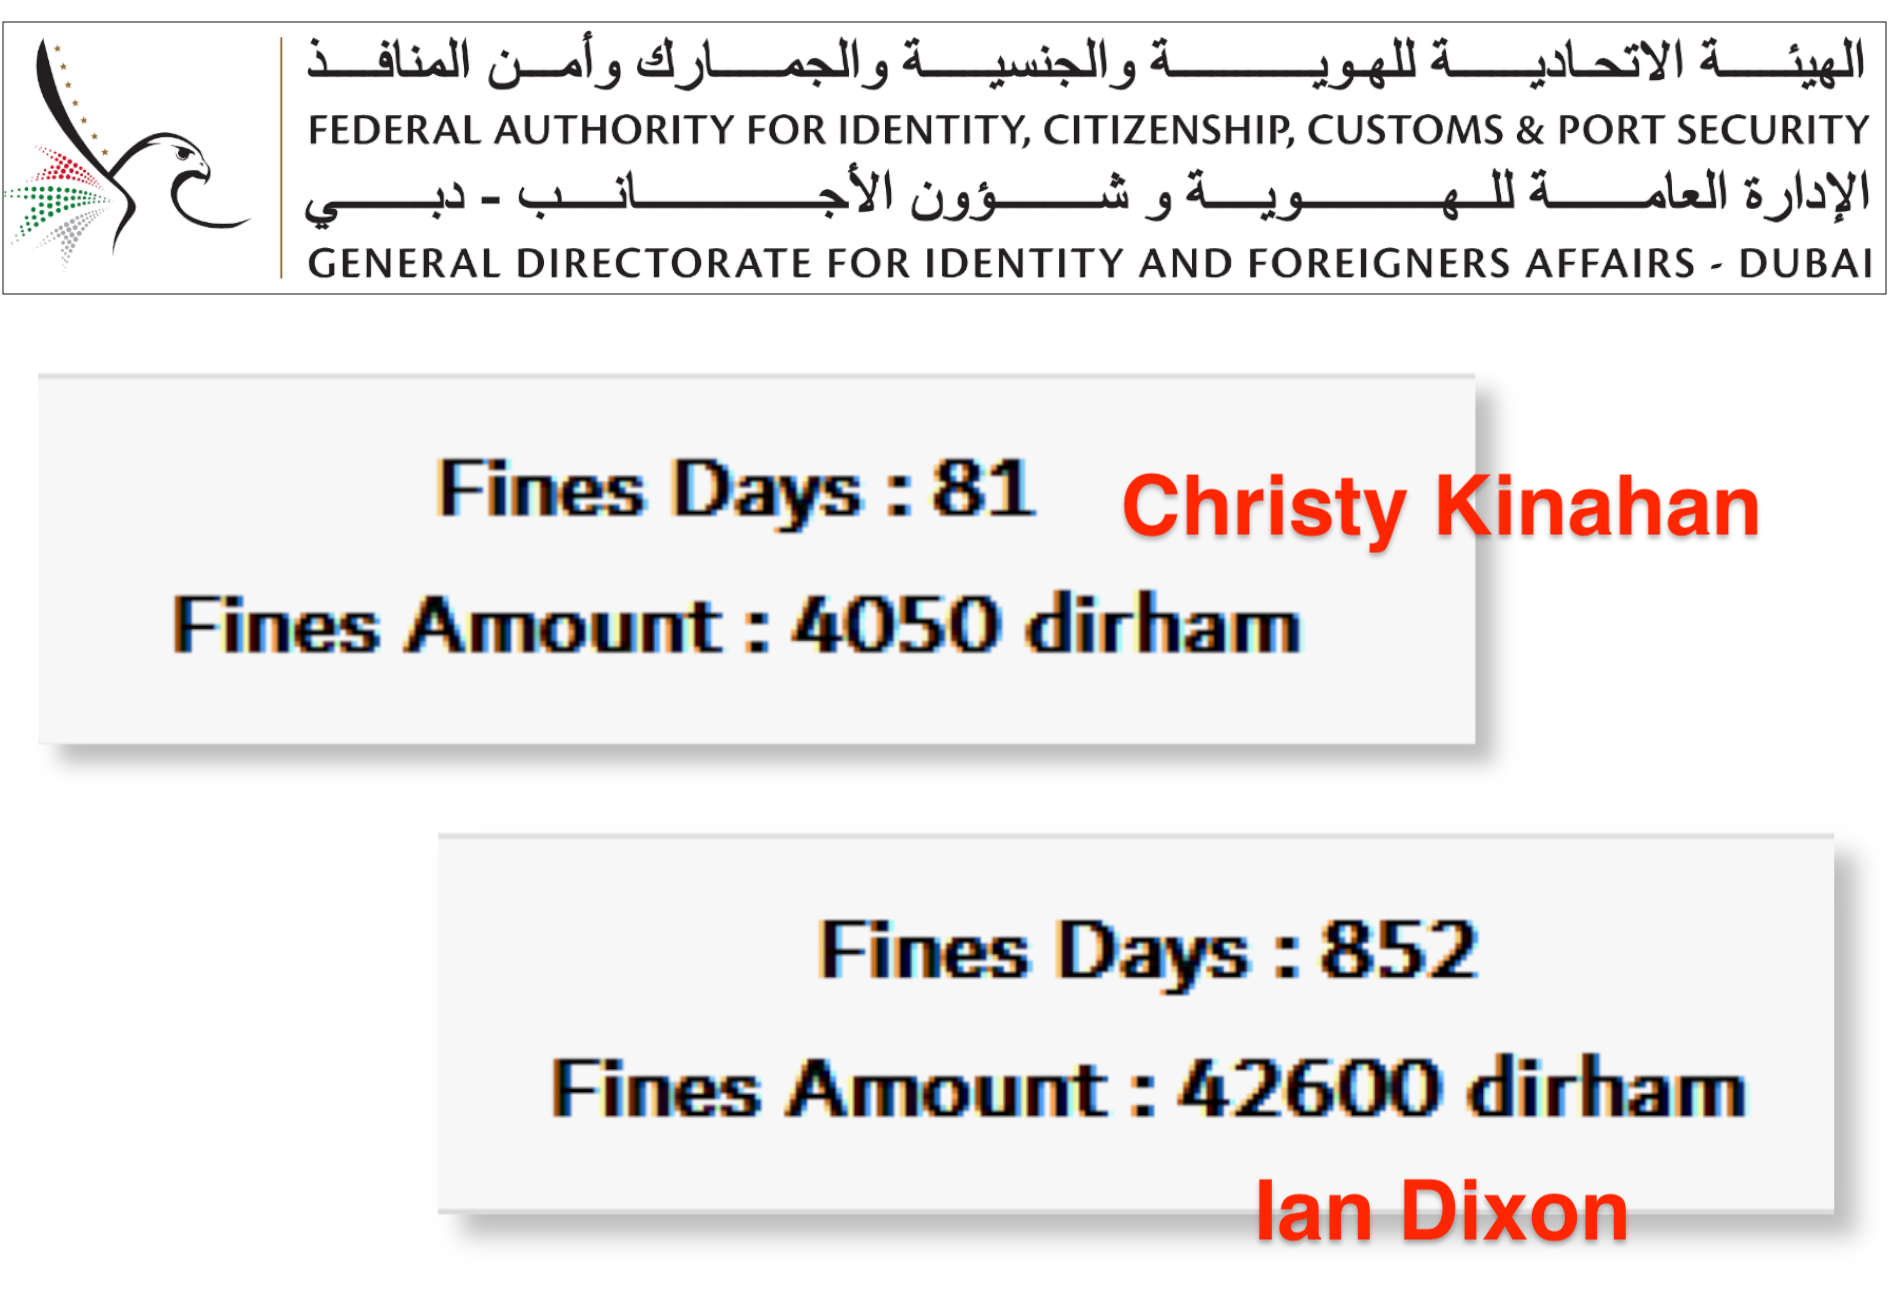
Kinahan owes the equivalent of more than USD $1,000 for an 81
day overstay.
Ian Dixon
Dixon, whose residency expired in 2024, owes more than USD
$11,000 for an 852-day overstay.
Sanctioned
Christy
Kinahan
Dubai
Expired Permit
81 days overstay
Fine: ~$1,000
Chris
Kinahan Jr
Dubai
Active Permit
Renewed: Jul 2026
Island Star Tourism
Bernard
Clancy
Dubai
Active Permit
Renewed: Jan 2026
Al Matn Goods Wholesalers LLC
Ian Dixon
Dubai
Expired Permit
852 days overstay
Fine: ~$11,000
Daniel
Kinahan
Dubai
Sean
McGovern
Dubai > IRE
Johnny
Morrissey
Spain
Chris Kinahan Jr
Dubai
Active Permit
Residence permit for Christopher Kinahan Jr. Source: GDRFA Dubai
Bernard Clancy
Dubai
Active Permit
Residence permit for Bernard Patrick Clancy under the name
“Bernard Patrick”. Source: GDRFA Dubai
Christy Kinahan
Dubai
Expired Permit
Ian Dixon
Dubai
Expired Permit
Expired residence permits for Christy Kinahan and Ian Dixon.
Source: GDRFA Dubai
Christy Kinahan
Dubai
Expired Permit
Expired residence permit for Christy Kinahan. Source: GDRFA
Dubai
Ian Dixon
Dubai
Expired Permit
Expired residence permit for Ian Dixon. Source: GDRFA Dubai
Screenshots of fine records for Christy Kinahan and Ian Dixon.
Source: GDRFA Dubai
Screenshots of fine records for Christy Kinahan and Ian Dixon.
Source: GDRFA Dubai
*Bellingcat searched the Dubai government’s identity and foreign affairs portal by inputting data about the
cartel’s leadership that was contained in the US government’s sanctions notice. Searching the gang
members’ ID or passport number, birth date and nationality returned a
“Unified Number”, a unique identifier assigned to every UAE visa holder.
This number, when entered with the other identity information on a UAE federal government portal, returned
the visa holder’s current status, history and file number.
Roy McComb, a former deputy director of the UK’s National Crime Agency, told The Sunday Times it was preposterous to suggest that the UAE did not know the visa status of the cartel members in Dubai.
“How is Christy Kinahan in the UAE unlawfully and the authorities there are unwilling to take appropriate action? The Kinahans are not an unknown entity, they are at the very apex of organised crime,” he said. “For the UAE not to know their residency status beggars belief.”
David Haigh, a British solicitor who was imprisoned on fraud charges in Dubai and now assists victims of abuse in the region, said it was clear the cartel must be paying off officials. “If someone is living openly there for a long period of time with that level of heat, that to me shows there’s been corruption involved,” he said. “If they were using false passports to enter Dubai, that’s a serious federal offence.”
Daniel and Christy Kinahan – nicknamed “The Dapper Don” – at a Dubai sports arena last June. Source: WeCaptureYou, TrillerTV
The passport details publicly listed in the US sanctions provide an unprecedented glimpse into the timeline of the cartel leadership’s visa history, giving an overview of their initial entry and exit to the Emirates.
The records show that four of the six key gang members had entered the UAE long before the 2016 attempt on Daniel Kinahan’s life in Dublin and the ensuing deadly feud that led to the cartel’s full relocation to the UAE.
A passport number for Christopher Kinahan Jr is linked to short-term UAE visas issued as early as September 2013. A passport number listed for Daniel Kinahan, searched in combination with an alternative sanctions-listed date of birth that is not his real one, returned seven short-term UAE visas between 2013 and 2015. It is not known what name this passport was under, but Daniel Kinahan has reportedly held illegitimate passports in the past.
A short-term visa for details associated with Ian Dixon first appeared in 2015. Authorities allege that Dixon acted as a trusted lieutenant to Daniel Kinahan by helping move bulk cash across Europe, arranging payments and keeping tabs on money owed by a narco-trafficker. In June, we revealed that Dixon was the poster boy for a padel club in Dubai, where he has been captured playing the racquet sport on webcams.
Left: Ian Dixon has been sanctioned by the US Treasury as part of its action against the Kinahan cartel. Right: Dixon at a racquet sports event post-sanctions. Source: US Treasury, sanddune_padel_dxb / Instagram
The earliest visas found for details associated with Sean McGovern and Bernard Clancy were from March and April 2016 respectively, the months after the 2016 attack in Dublin.
All key members of the group, with the exception of crime boss Christy Kinahan, gained residency in the UAE using Irish passports. The cartel founder’s British passport number is linked to his immigration file; both to his latest residence permit and four previous temporary visas. Records show the first visa associated with this passport was issued in February 2007 – the earliest known instance of Christy Kinahan entering the UAE. Another was issued in November 2009, and then two more in 2017.
However, details for an Irish passport under one of Christy Kinahan’s aliases (“Christopher O’Brien”) return 31 separate records on the UAE’s visa inquiry portal between 2014 and 2017. Bellingcat confirmed this passport number was associated with the name Christopher O’Brien after discovering both in corporate documents for a now-defunct Hong Kong firm that was incorporated in February 2014. This suggests Kinahan may have been using a false passport to travel to and from the UAE in addition to traveling under his authentic document. A man was jailed in 2023 after admitting he supplied “fraudulently obtained genuine passports” to criminals, including Kinahan.
Details from sanctions against Christy Kinahan were found on publicly available corporate documents of a defunct Hong Kong firm (passport number blurred by Bellingcat). Source: US Treasury, Hong Kong Companies Registry
One short-term UAE visa issued for “Christopher O’Brien” ended on August 19, 2015. Posts on LinkedIn three days later showed Christy Kinahan – wearing black-framed glasses and named in the posts as “Christopher O’Brien” – surrounded by Iranian and Turkish businessmen in a high-rise company office in Ankara. These images, discovered by Bellingcat in posts under the name of the managing director of a now-defunct Turkish investment company, have since been deleted.
LinkedIn posts from August 2015 showing “Christopher O’Brien”, a.k.a Christy Kinahan, in an office in Turkey.
According to the Dubai government, employment-based residence visas are valid for two years and must be obtained by a company on its employee’s behalf. The employer is required to apply for a work permit through the UAE’s Ministry of Human Resources and Emiratization. The employee must pass a fitness test before their employer can apply for the residence permit.
The company names on Clancy and Kinahan Jr’s residence permits, Al Matn Goods Wholesalers and Island Star Tourism respectively, match existing firms in Dubai. However, Bellingcat was unable to confirm whether these entities are the same as the ones listed on the residence permits. It is also not known why Clancy’s residence permit only includes his first and middle names (“Bernard Patrick”) while the other cartel members’ visas used their full names.
Wanted posters for Irish drugs smugglers Daniel, Christy and Christopher Kinahan Jr, released after the cartel leaders were sanctioned in 2022. Source: US Department of the Treasury
The firm named on Christy Kinahan’s permit, OSA Management Consultancies, is listed as an aviation consultancy on a Dubai government registry. In addition to sharing an address with cartel-linked firm CV Aviation Consulting Services, UAE company data accessed on Horizons, a platform created by Washington DC-based nonprofit C4ADS that aggregates public records, shows that both firms also have the same business licence number and date of incorporation, suggesting OSA may be a newer name for the same entity.
The managing director of Island Star Tourism told Bellingcat on the phone that Christopher Kinahan Jr was working as “commission-based staff, not in-office staff”. He confirmed he recognised Christopher Kinahan Jr’s name but said he had never met him. Asked how the company name appeared on his visa, he said “I don’t know”. He said if the UAE had any problem with Christopher Kinahan Jr, it would “not give permission”.
Al Matn Goods Wholesalers and OSA Management Consultancies did not respond to questions from Bellingcat.
The UAE foreign ministry has been approached for comment.
Connor Plunkett, Peter Barth, Beau Donelly and John Mooney contributed to this article. Scroll-driven interactive by Connor Plunkett and Miguel Ramalho.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
Note The June 2026 Dark Web Breach Incident Trend Report is based on major data breach cases posted on the deep web and dark web forums. Due to the nature of some sources, it was difficult to fully verify the accuracy of certain information, so the report includes content that requires further verification. Major Issue […]
This article is the result of a collaboration with The Sunday Times. You can find their corresponding piece here.
Every Friday evening, the brochure says, players can compete to win cash prizes in one of the world’s fastest-growing racquet sports. The padel club in Dubai’s west is the picture of modern wellness culture: climate-controlled courts, a private sauna and ice bath, and one-on-one coaching. The promotional image shows a bearded man in mid-swing, eyes locked on the ball. He wears matching activewear and a golden tan. The poster boy for padel is a talented player who once finished runner-up at an international tournament. He has also spent the past decade living in the shadows.
Left: Ian Dixon has been sanctioned by the US Treasury as part of its action against the Kinahan cartel. Right: Dixon, who appears to live a carefree lifestyle in Dubai, at a racquet sports event post-sanctions. Source: US Treasury, sanddune_padel_dxb / Instagram, asiapacificpadeltour / Instagram
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
Ian Thomas Dixon is a key figure in the Kinahan cartel, the Irish organised crime group that authorities say has evolved into a US$1.5 billion transnational network involved in drug trafficking, money laundering and arms smuggling. Investigators have connected the cartel to Iran’s intelligence services and the Lebanon-based militant group Hezbollah. Its feuds with rival gangs have been linked to at least 18 murders across four countries.
Dixon, 36, along with the Kinahan Organised Crime Group’s senior leadership – Christy Kinahan, 69, and his sons Daniel, 49, and Christopher Jr, 45 – was sanctioned by the US government in 2022. Authorities allege the Irishman acted as a trusted lieutenant to Daniel Kinahan, who is said to manage the cartel’s vast drug trafficking operation by helping move bulk cash across Europe, arranging payments and keeping tabs on money owed by a narco-trafficker.
Wanted posters for Irish drugs smugglers Daniel, Christy and Christopher Kinahan Jr, released after the cartel leaders were sanctioned along with four key associates in 2022. Source: US Department of the Treasury
Bellingcat and The Sunday Times can today reveal how Dixon’s racquet sport hobby has left behind a digital trail that led to the most recent footage of him since those sanctions were imposed – the first time he has been pictured publicly in almost a decade. This investigation also uncovers the alias Dixon has used in Dubai and exposes the first open source links to an underworld associate who was recently extradited from the Gulf state and jailed in Scotland.
It comes as cartel leader Daniel Kinahan awaits extradition to Ireland after his arrest in Dubai on foot of a warrant issued by Irish authorities. The arrest, in April, followed an extensive policing and diplomatic effort from international law enforcement.
Bellingcat recently published images of ex-UFC fighter Mounir Lazzez with Daniel and Christy Kinahan at a 2025 MMA event in Dubai. Our investigation also linked Lazzez to multimillion-dollar transactions for crude oil tankers that were later sanctioned by the US. Source: WeCaptureYou, C4ADS Horizons
In March, investigations by Bellingcat and The Sunday Times exposed the first photographs of Daniel Kinahan and his father in years and also revealed that the cartel’s “friend”, former UFC fighter Mounir Lazzez, was connected to US sanctions against Iran.
The latest findings give an unprecedented glimpse into the recent activity of a key cartel associate who, until now, has largely flown under the radar.
Family Ties
When cartel founder Christy Kinahan moved to Spain after his release from an Irish prison in 2001, it wasn’t long before his new home became a hub for the gang. His sons, Daniel and Christopher Jr, soon followed him to the Costa del Sol – as did their younger cousin, Dublin native Ian Dixon.
From the late 2000s onward, Dixon worked for businesses linked to the crime family in the south of Spain. One of these was The Auld Dubliner, a pub in Estepona that reportedly served as a base of operations for the cartel. In 2010, the pub was raided and temporarily closed by authorities as part of Operation Shovel, a years-long multi-national police investigation into the cartel’s drugs and arms-trafficking activities.
Left: Dixon pictured in 2011 behind the bar at The Auld Dubliner in Estepona. Right: Exterior of the pub in 2012 (image highlighted by Bellingcat). Source: Facebook, Google Street View
Dixon would also work as a trainer at MGM Marbella, the boxing gym co-founded by Daniel Kinahan that would go on to represent some of the biggest pro boxers in the world. The company, which was renamed MTK Global, shut down after the US sanctions on the Kinahans were imposed in April 2022.
Top left: Ian Dixon at MGM Marbella in 2013. Top right: Dixon running a pads training session at the gym in January 2015. Bottom: Dixon pictured with Daniel Kinahan and others in Spain in 2013. Source: X, MGM Marbella / YouTube
In 2016, Dixon was arrested by Spanish police investigating the murder of Irish criminal Gary Hutch. The previous year, Hutch had been gunned down while out for a morning jog in a gated community on the Costa del Sol.
Dixon was released without charge, and another Kinahan cartel associate was later sentenced to 22 years for his role in the murder. The killing sparked a feud between the Kinahans and the rival Irish Hutch gang that resulted in at least 18 deaths.
Dixon and other key Kinahan members fled to Dubai in the wake of the deadly feud.
CCTV footage of Gary Hutch being pursued by a gunman in southern Spain, moments before Hutch was cornered and shot dead in September 2015. Source: BBC, The Irish Sun
Ian Dixon has no known convictions. But his alleged role in the Kinahan Organised Crime Group was laid bare when the US sanctioned him. Authorities said Dixon managed finances and moved bulk currency for Daniel Kinahan and also kept tabs on the debt owed by a narco-trafficker.
The sanctions notice also said Dixon controlled Hoopoe Sports LLC, a Dubai firm that listed a number of pro boxers among its clients and reportedly received more than $4 million for bouts involving former heavyweight champion Tyson Fury. Boxing promoter Bob Arum told Yahoo Sports the money was for consulting fees owed to Daniel Kinahan.
Screenshot from a 2022 archive of US-sanctioned Hoopoe Sports’ website, showing pro boxers Jamie Conlan, Billy Joe Saunders, Hughie Fury and Michael Conlan among its clients list. Dixon’s company email address is visible on the footer. Source: arejaywoof / X, archive.org
Dixon lived in an exclusive gated community in Dubai, according to the 2022 sanctions notice. Online listings show that properties like his Spanish-inspired villa are worth up to $2.7 million.
Passion for Padel
Padel is an increasingly popular racquet sport from Mexico best described as a combination of tennis and squash. According to the sport’s governing body, it has more than 17.5 million weekly players across 150 countries and the UAE, where Dixon lives, has the second-highest number of padel courts in Asia. It was on these courts in late 2024 that Dixon played in the master final of the Asia Pacific Padel Tour (APPT).
A pre-match group photo was captured on the APPT male amateur final live stream. The photo, posted to Facebook, shows Dixon was part of the lineup. Source: APPT / YouTube, Facebook, US Treasury
APPT rankings show Dixon registered for the tournament under the name “Ian Thomas”. Like his cartel leader relative Christy Kinahan, who used his first and middle names as an alias on his Google review profile, Dixon had dropped his surname.
Finding a Fugitive – How we Located Dixon
Bellingcat found the padel club promotion showing Ian Dixon after running images of the cartel associate through a publicly available facial recognition search engine. Among the results was a link to a graphic designer’s online portfolio, which included the advertisement for the padel competition. The original photo had been posted on the sports club’s Instagram page in late 2023, with the caption: “Elevating fun, one swing at a time!” Dixon was not named.
Left: The padel tournament ad discovered via a PimEyes search for Ian Dixon. Right: The original picture and caption from the sports club’s Instagram page, posted in October 2023. Source: sanddune_padel_dxb / Instagram
We searched for additional open source evidence and located online profiles for a 36-year-old Irish padel player named “Ian Thomas” who had taken part in a number of matches in Dubai in recent years. One profile shows he played 16 ranked matches between September 2024 and April 2026 – the most recent being the week after Daniel Kinahan’s arrest. But the accounts did not include profile pictures.
Left: Screenshots from an online profile for 36-year-old Irishman “Ian Thomas” & Christy Kinahan’s Google review profile under the name “Christopher Vincent”. Right: Dixon pictured at a padel centre in an Instagram post from August 2024. Source: Rankedin.com, Google Maps, Instagram
Bellingcat searched for footage showing the padel events and venues listed on the profiles. It returned multiple social media posts and live-streams clearly showing Ian Dixon at the same events where “Ian Thomas” was registered as playing. Dixon can also be heard speaking with a Dublin accent and at one point is seen with a close relative of Daniel Kinahan.
Dixon and his doubles partner played four games over the December 13-15 weekend, eventually placing second after losing in the final. The Irish cartel associate is captured on film after the match receiving a silver medal and commemorative racquet.
Clip showing “Ian Thomas” in the final position in the APPT Dubai 2024 male amateur rankings, followed by Dixon on court during the match and receiving a racquet after his silver-medal placement. Source: asiapacificpadeltour.com, asiapacificpadeltour / Instagram
The Asia Pacific Padel Tour was held a month after senior Kinahan cartel figure Sean McGovern was arrested in Dubai on foot of an Interpol red notice. McGovern was extradited to Ireland last year and earlier this month jailed for 24 years for directing the activities of a criminal organisation in relation to murder and attempted murder.
The tournament was live-streamed to YouTube via webcams set up on two courts. Dixon was captured throughout the three-day event, both playing on the court and mingling with others in the background. The hour-long male amateur final, which Dixon lost, is viewable in its entirety.
Clips from the tournament on December 15 showing Dixon before, during and after the amateur male final. Source: APPT / YouTube
Dixon also posed for photos during the tournament, but it appears he did have some reticence about appearing on social media. In two images from a different padel event hosted at the same venue a few months later, Dixon’s face had been covered. However, a third photo was not edited, confirming that it was Ian Dixon.
Top: Dixon posed for a photo before beginning the APPT amateur male final. Bottom: Dixon’s face was covered with a grey oval and an emoji in two social media posts from a different event. One of the pictures was not censored in another post. Source: APPT / Facebook, isdpadel / Instagram, ISD Dubai Sports City / LinkedIn
Kingpin in the Crowd
Among the people Dixon was seen with at padel events in Dubai was Stephen Jamieson, a Scottish criminal who was recently jailed for his role in a multimillion-dollar drug trafficking operation.
Dixon (left) and Jamieson (right) seen arriving and meeting on a live stream of a Dubai racquet sport event in December 2024. Jamieson was arrested by authorities in the Gulf state the following July. Source: Police Scotland, The Scottish Sun, asiapacificpadeltour / Instagram, APPT / YouTube
Dixon greeted Jamieson with a fist pump during the Dubai APPT tournament in December 2024 on the day the Irishman played in the amateur final.
Left: Jamieson watching padel games on days one and three of the APPT in 2024, when Dixon was also in attendance. Right: Police mugshot of Jamieson. Source: asiapacificpadeltour / Instagram, Police Scotland
Dixon was also pictured with Jamieson at a family day padel event just weeks before the Scottish criminal’s arrest. (Bellingcat is not publishing details of that event to protect the identity of family members.)
Clips from day three of the tournament showing Dixon meeting Jamieson. Both men arrived and left separately at different times. Source: APPT / YouTube, BBC, The Scottish Sun
Jamieson, who has multiple convictions, was extradited from Dubai last year and is serving a six-year prison sentence in Scotland on organised crime and drug charges. The case against him was built around intercepted messages he had sent via the defunct encrypted communication network EncroChat – a network the Kinahans have also used – to direct drug shipments.
The Sunday Times reports today on the Kinahan cartel’s deeply entrenched links to organised crime in the UK, where it is known to control much of the illicit drug market. It said the footage showing that Dixon and Jamieson know each other could indicate an underworld connection, since cartel cadres do not associate with rival operations.
Dixon is among the remaining cartel figures at large in Dubai, along with Christy Kinahan, Christopher Jr and gang lieutenant Bernard Clancy. Source: US Treasury
Three of the seven alleged key Kinahan cartel figures have been arrested since the US sanctions were imposed. Johnny Morrissey, arrested in Spain in 2022, was later bailed and subject to a travel ban. Sean McGovern was jailed earlier this month and Daniel Kinahan awaits extradition to Ireland after his recent arrest in Dubai. Garda Commissioner Justin Kelly, of Ireland’s police force, recently said the investigation into the Kinahan cartel was ongoing and that authorities were continuing to focus on the other members of the gang.
Ian Dixon did not respond to questions from Bellingcat.
Connor Plunkett, Peter Barth, Beau Donelly and John Mooney contributed to this article.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
ShinyHunters claims it stole 297GB of data from the Council of Europe, including payroll and medical records, but the organization has not confirmed a breach.
On February 15, 2026, the bulk carrier, Grumant (IMO: 9385879) was pictured at the occupied Ukrainian Port of Feodosia on the Crimean peninsula. Satellite imagery suggests it had already been there for several days. It appeared to stock up on grain before departing on a two-month-long journey eventually docking at the Port of Benghazi in Libya on April 18.
While there have been previous reports of grain shipments from occupied Ukraine arriving in Libya, this is only the second time a Russian ship has been observed delivering what the Ukrainian government describes as “stolen” grain to the country. The previous case involved the Damas Wave which travelled in January of last year to the port of Misrata which is under the control of the UN-recognised Government of National Unity (GNU). In addition to satellite imagery, Bellingcat deployed a new technique that analysed Grumant’s heading data which was contained in AIS information provided by Lloyd’s List Intelligence, to help confirm Grumant’s presence in Feodosia.
Grumant transits the Bosphorus Strait in the middle of the night.
Credit: Yörük Işık.
Black Sea
Grumant enters a region of the Black Sea known for GNSS interference, meaning that Grumant’s publicly reported Automated Identification System (AIS) position is unreliable.
Port of Feodosia
On February 15, a high resolution satellite image confirms the ship is docked at the port of Feodosia at berth No. 1 that is used for bulk and metal cargo. Matching features visible include Grumant’s grey decking, its seven hatches and bright yellow front mast. What appears to be leftover grain can be seen under the two port crates, immediately next to the ship.
Grumant exits the area of signal interference, meaning that its reported position on ship tracking services is now reliable again. Its AIS messages indicate it is travelling towards the Bosphorus.
Bosphorus Strait
Grumant transits the Bosphorus Strait towards the Sea of Marmara. Judging by the draft, with no visible red paint on its hull, the ship appears to be fully laden.
Credit: Yörük Işık.
Izmir Anchorage
Grumant arrives in Izmir, Turkey on February 23 and anchors off the coast until March 13.
Over the course of three weeks, Grumant never enters the Port of Izmir. It is not known if it was denied entry. Bellingcat asked the port operators but did not receive a response before publication.
Grumant then loiters off the coast of Aliağa, about 50 km from Izmir. It stays here until March 16, never entering the port. It again is not known if it was denied entry. Bellingcat asked the port operators but did not receive a response before publication.
Near Benghazi
Grumant arrives in Libyan waters and stays off the coast of Benghazi until April 1.
Libyan Waters
Grumant briefly leaves the coast of Benghazi, but returns a few days later.
Benghazi
Grumant leaves the anchorage on April 18 and docks at the port of Benghazi where it unloads the grain. The ship was captured in a Vantor satellite image on April 20.
It leaves port on April 23, and heads back towards the Bosphorus.
According to the Ukrainian activism, journalism and hacker group, Kiborg News, Grumant used deceptive shipping practices to deliver grain to Latakia, Syria in 2024. The report included several of Grumant’s shipping manifests, which showed it had repeatedly exported grain from Occupied Crimea to Syria.
Heading Data Helps Locate Grumant
It is standard maritime practice that ships broadcast Automatic Identification System (AIS) messages which include a ship’s position, heading, and draught (among other information).
Between February 7 and February 19, 2026, data from Lloyd’s List Intelligence shows the Grumant transmitted 29 AIS messages, with unreliable positions in the vicinity of Feodosia. We know these positions are unreliable as they are erratic and some of them report the ship as being positioned on land.
Unreliable AIS positions – Grumant’s reported positions between February 7-19, 2026, via Lloyd’s List Seasearcher.
However, according to the IMO, the heading data transmitted by a ship’s AIS system must come from an onboard compass. A compass is unaffected by GNSS interference, meaning it is a more reliable source of information in these conditions.
Over the same dates, all 29 AIS messages reported the ship’s heading as 267 degrees or 268 degrees. The Port of Feodosia has a heading of 267.5 degrees. The close agreement between the ship’s heading and port heading strongly suggests that Grumant was moored at the port between February 7 and February 19, 2026.
We conducted an extra check of the heading data by reviewing satellite imagery available of berth 1 at Feodosia Port, which suggests that the same vessel was present on several days between February 6 and February 18. Imagery on Feb. 6 shows the port was empty in the morning and occupied in the afternoon. Grumant exited the area of GNSS interference on February 21, and berth 1 at the port was captured on satellite image on February 22 and appeared empty. The low resolution satellite imagery is only used as an additional check to see if a vessel is at the berth.
Timeline of open source observations related to Grumant’s presence (tick) or absence (cross) at Feodosia port. Empty entries indicate a lack of available data.
Sentinel-1 timelapse of Feodosia Port, Copernicus Sentinel data 2026. Annotations by Bellingcat.
PlanetScope timelapse of Feodosia Port, Planet Labs PBC. Annotations by Bellingcat.
Bellingcat checked all vessels transmitting AIS in the vicinity of Feodosia Port and found that Grumant was the only one that consistently transmitted a heading matching the Port of Feodosia over the period of interest.
We shared our research with Charlie Brown, a former US Naval Officer and Senior Advisor at United Against Nuclear Iran where he focuses on maritime sanctions enforcement and the tracking of illicit shipping. Brown told Bellingcat that while satellite imagery of vessels remained key for identification, when looking for reliable data in a spoofing environment it made sense to look at the various elements of AIS data to try and find some accurate information, despite GNSS spoofing.
“It’s quite standard for the independent gyro compass to be providing the heading […] I think the majority would not [be subject to spoofing] so it’s a good methodology to parse out the particular data and then make some inferences from that.”
“It’s neat to think of what can be derived from data that would otherwise be dirty or wrong. So there’s still some elements of use in there.”
He added that in theory there are probably some compasses that are subject to spoofing as well.
He told Bellingcat that it was fair to say the heading data of the Grumant supported identification, but stressed the need to cross-reference with other data sources.
While in this instance it has been possible to use AIS data to help verify the location of Grumant, it is relatively unusual to have access to this information.
This activity, known as “dark port calls”, is a common tactic for those engaging in illicit or sanctioned trades.
Grumant does not transmit AIS messages from February 8 to 11, but this is the longest gap in data (see diagram above), with intermittent messages coming through after that point.
It is unclear why Grumant continued to transmit AIS during the period it was loading in Feodosia.
A review of Lloyd’s List Intelligence data from January 2025 shows that on a previous voyage to the Black Sea the Grumant operated “dark” for 59 days.
Visual Identification
On February 15, 2026, high resolution imagery showed Grumant docked in the Port of Feodosia. We compared it with other recent images of Grumant to confirm the match.
The ship in the satellite image has a grey-coloured deck, which is uncommon enough for it to stand out. Many bulk carriers have cranes (including the ships we previously covered such as Krasnodar, Zafar and Zaid), Grumant does not have any. It also has seven hatches (openings for the grain) and a bright yellow front mast that matches the mast of Grumant (see the image of it transiting the Bosphorus). We can match the Grumant in the Feodosia image, not only to pictures of the Grumant shot from the ground, but also to the satellite image from Benghazi.
The length and breadth of the ship also matches that of the Grumant; 180 metres by 22.90 metres.
Libya has complicated internal dynamics with essentially two administrations in charge of different parts of the country – the Government of National Unity (GNU) in the west and the Libyan National Army (LNA) in the east.
In recent years, Russia has backed the LNA’s General Khalifa Haftar, based out of Benghazi, in the east of the country. But Jalel Harchaoui, a political scientist specialising in Libya with the Royal United Services Institute (RUSI), stressed that the two sides of this conflict, the LNA and the UN-recognised GNU, are not currently fighting. Instead they are in a flawed, multi-year truce.
Therefore, the east-west divide isn’t as clear-cut as during the civil war. While all shipments going to Benghazi and Tobruk are overseen by the LNA, not all shipments going to the city of Misrata (which is run by the GNU) are meant for the GNU-dominated part of the country.
Harchaoui told Bellingcat: “the Tripoli government is in some regards pro-Ukraine, but if there’s business that can be done with Russia through the very opaque port of Misrata and all the right people get paid, the business is going to take place.”
That observation is potentially significant given at least one previously tracked vessel that went from occupied Ukraine to Libya docked in Misrata.
This was not the case of the Grumant, however, which arrived in an LNA-controlled part of the country. It is not known from open sources alone if the authorities in Libya or at the port in Benghazi knew the grain carried by Grumant had come from occupied Ukraine.
Bellingcat contacted the Benghazi-based LNA government and representatives of the Tripoli-based GNU government via the Libyan Embassy in The Netherlands. We also contacted the Port of Benghazi, Port of Imzir in Turkey as well as the Ukrainian and Russian authorities. Representatives of the LNA did not respond to requests for comment before publication, nor did the Port of Benghazi or Port of Izmir. The Libyan Embassy in The Netherlands replied to Bellingcat after publication, stating that Benghazi and eastern Libya are not under the authority or administrative control of the Government of National Unity and therefore they are not currently in a position to comment on Bellingcat’s findings.
Ukraine Continues to Pursue the “Shadow Grain Fleet”
“The port of Feodosia, located in the temporarily occupied Autonomous Republic of Crimea, is not under Ukrainian control, and any commercial activity conducted there is illegal,” the Ministry for Development of Communities and Territories of Ukraine and the Ministry of Foreign Affairs of Ukraine told Bellingcat in a joint response.
They told us the loading of grain exported from the temporarily occupied territories is an illegal act and Russia was using ports as logistics centers to export stolen Ukrainian agricultural products.
“The expansion of such routes to third countries, in particular to North Africa, demonstrates Russia’s ongoing efforts to circumvent international sanctions and monetize resources stolen from the occupied Ukrainian territories.”
The Ukrainian Ministry of Foreign Affairs sent information about Grumant’s (IMO: 9385879) “illegal activities” to the diplomatic missions in Great Britain, the Republic of Turkey and the Republic of Tunisia over the course of March to May this year, the ministries told Bellingcat.
Ukraine is continuing to pursue legal action against Russia’s “shadow grain fleet” they told us. For instance, earlier this month a Swedish court approved the transfer of the Russian “shadow grain fleet” vessel CAFFA to Ukraine for investigation after it was arrested in Swedish waters.
This case has set a new precedent, going beyond sanction and fines previously handed out to such vessels, and allowing for the detention and confiscation of a shadow fleet vessel in European jurisdictions, the ministries said.
Bellingcat attempted to contact Decision/Reshenie to ask about Grumant’s grain shipment from Feodisia Port to Benghazi Port, but they had not responded at time of publication.
Cover image: Planet Lab image shows Grumant anchored off Izmir, Turkey on February 27. Credit: Planet Labs PBC.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
“In the age of misinformation, the line between fact and fiction is blurrier than ever.”
“For those of us working in video news, verification isn’t a nice-to-have. It’s a necessity. It is how we protect the stories we help shape and how we earn and maintain trust in an increasingly chaotic information ecosystem,” Abu Dhabi-registered video news agency Viory posted on LinkedIn on April 9, 2026, offering training to help newsrooms and journalists sort fact from fiction.
The self-described “video news agency of the Global South” has delivered journalism training to multiple national press agencies across Africa, Asia and the Middle East.
However, when it comes to Viory itself, the line between fact and fiction is very blurry indeed.
Bellingcat has found multiple links between the digital infrastructure of Viory and Ruptly news agency, a branch of sanctioned Russian propaganda outlet Russia Today, including shared IP addresses, a Viory-linked site using a digital security certificate registered to Ruptly, and Ruptly sending site performance data to Viory. While there have been previousreports on suspected links between the two outlets, our investigation adds new evidence about Viory’s ties to Ruptly media.
When contacted for comment, both Viory and Ruptly denied any connection with each other.
Composite Image created by Bellingcat.
‘Video News Agency of the Global South’
Viory’s main offering is raw video footage of news events provided via subscription. According to Viory, its clients include “major international news outlets, local media organisations, and independent creatives in more than 170 countries”.
If its own figures are to be believed, Viory was strikingly well established at its launch in November 2023, by which time it claimed to have a “pre-assembled team of over 150 full-time staff, and an established network of over 3,000 video journalists across the world”.
The name “Viory” is a trade name. The company’s legal name is Darpo Vision FZ LLC, according to its website, which also states that it is registered in Abu Dhabi. In August 2024, Darpo Vision FZ LLC filed for a trademark in the US for the name Viory, which was approved in December of 2025.
As of May 2026, Bellingcat found press releases and news reports referencing at least 30 agreements between Viory and partners in more than 22 countries, as well as cooperation agreements with government agencies, training agreements with universities and regional journalism bodies.
Ruptly is a video news agency formerly based in Berlin and ultimately controlled by Russia Today (RT), which is owned by Russian state media company ANO TV-Novosti. ANO TV-Novosti has been on the EU sanctions list since December 2022 for spreading “pro-Kremlin propaganda and disinformation” and supporting Russia’s war against Ukraine.
RT launched Ruptly, which operated in Berlin via a German-registered subsidiary in 2013, with the goal of “becom[ing] the go-to alternative resource in a highly concentrated market of professional news video footage, and to deliver coverage of stories that other agencies miss.”
Sanctions imposed on RT following Russia’s 2022 invasion of Ukraine choked off Ruptly’s source of funds in Germany, leading the German company to begin insolvency proceedings in October 2024. Ruptly continues to operate from Moscow as of 2026.
As with Viory, Ruptly’s main offering is providing raw news footage to subscribers around the world. It relies on a large network of international freelancers and stringers. In 2016 RT claimed that Ruptly had “surpassed” newswire services AFP and Reuters on YouTube, and was serving more than 600 media organisations in 45 countries.
Felix Huesmann of the German outlet RedaktionsNetzwerk Deutschland (RND),was the first to outline links between Ruptly and Viory while covering the insolvency proceedings of Ruptly. He found that Darpo Vision’s original details on the Abu Dhabi Creative Media Authority’s site included an email address d.toktosunova@gmail.com. It has not been confirmed who this email address belongs to; however, the username matches the first name initial and surname of Dinara Toktosunova, the managing director of Ruptly. When asked about this email address by Huesmann in 2024, Ruptly “explained that Toktosunova is focused on securing the future of the Ruptly team [in Moscow] and is not working anywhere else as a managing director.”The activist group, OSINT For Ukraine, also outlined links between Ruptly and Viory, including the movement of multiple key staff between the two organisations and strong similarities between the two organisations’ platforms and content.
Darpo Vision’s Security Certificate
The legal entity behind Viory, Darpo Vision, was set up in one of Abu Dhabi’s free zones – special economic areas that have business-friendly incentives such as tax exemptions and that allow 100 percent foreign ownership. The free zones also offer what some describe as high levels of “corporate privacy,” which others assert has created a haven for shell companies and opaque corporate structures.
Darpo Vision initially had its own web domain, darpo.vision. The site has since been removed. Whois records show that the domain was registered by Darpo Vision FZ LLC in December 2022 to a PO Box in Abu Dhabi, using a Russian domain name registrar and a Moscow phone number.
Initially, Darpo.vision had its own Secure Sockets Layer (SSL) certificate – a digital certificate that authenticates a website’s identity, allowing it to secure and encrypt data. However, VirusTotal data shows that as of at least June 2024, darpo.vision was using a wildcard SSL certificate registered to ruptly.video. A Wildcard SSL certificate is a single certificate with a wildcard character (*) in the domain name field. This allows the certificate to secure a single domain and multiple subdomains. You can see historical SSL certificates for darpo.vision.
James Wilson, a software and networking engineer with 20 years of experience and currently Enterprise Technology editor at Risky Business Media, told Bellingcat that to prevent unauthorised use or forgery of SSL certificates, a private key is needed to create and use a wildcard certificate across multiple domains.
“The fact that darpo.vision was using a wildcard SSL certificate for ruptly.video indicates that whoever was running darpo.vision also had access to the private key for ruptly.video’s SSL certificate. Normally, only the people operating Ruptly’s web hosting infrastructure would be likely to have access to that,” Wilson explained.
When asked by Bellingcat about whether there were alternative possible explanations, Wilson suggested that it was theoretically possible that someone may have hacked Ruptly and stolen their private SSL key.
“However, using that wildcard SSL certificate on a domain that didn’t match the wildcard in the certificate defies explanation as the browser would alert the user to the certificate error,” he added.
Shared IP Addresses
Bellingcat also identified multiple shared IP addresses which appeared to be concurrently in use by both Ruptly and Viory between May 2025 and May 2026.
From 2025 onwards, the Russian IP address 158.160.132.25 has been used concurrently by viory.video, ruptly.video, ruptly.agency and ruptly.tv, according to VirusTotal. Similarly, since the beginning of 2026, IP address 84.252.135.88 has been used concurrently by viory.video, viory.team, ruptly.video, ruptly.agency and ruptly.tv, according to VirusTotal.
VirusTotal data shows that from 2025 onwards, IP address 158.160.166.22 has been used by ruptly.video and viory.video while from 2026 onwards, IP address 158.160.226.68 has been used by viory.video and ruptly.tv. The VirusTotal data appearsto show these IP addresses being used exclusively by Ruptly and Viory as of 2025 and 2026. However, VirusTotal does not necessarily capture all domains which resolve to an IP, and other domains may also have resolved to these IP addresses, which were not observed by VirusTotal’s passive DNS replication service. It is also important to note that in some cases, unrelated domains use the same IP addresses.
Ruptly Sends Site Performance Data to Viory
Viory’s and Ruptly’s site infrastructure was also linked through data sent via Sentry, an internal error tracking and performance monitoring platform.
An API scan of Ruptly’s main client login page, ruptly.agency, on March 26, 2026, shows that the page was sending data to a subdomain of viory.team. This domain appears to be used by Viory primarily for backend purposes, based on subdomains which appear to refer to common developer and site management tools such as Traefik and ArgoCD, in addition to Sentry.io. Notably, two subdomains also appear to refer to Ruptly.
The purpose of one domain sending data to another domain’s Sentry project is generally to consolidate all of the relevant performance and error data in one place for in-house developers to monitor.
The ruptly.agency page’s request to viory.team also includes an authentication key for Viory’s Sentry project. Ruptly.agency is not the only Ruptly domain sending Sentry data to viory.team. As of May 9, 2026 the login page for ruptly.video’s own Sentry project, sentry.ops.ruptly.video, automatically redirects to sentry.ops.ruptly.video/auth/login/viory/. Ruptly Video’s Sentry login page also features “Viory” as the title.
The ruptly.video Sentry login page is also sending data to the viory.team Sentry project, the ruptly.agency homepage and using a favicon hosted on viory.team.
A third Ruptly domain, ruptly.tv, also sends performance data to viory.team’s Sentry project via cms.dev.ruptly.tv.
James Wilson noted that in each case, the Ruptly domains sending data to Viory appeared to be using a different Sentry key.
“If you look at each of these snippets sending telemetry data [from the Ruptly domains], the specific Sentry keys for sentry.ops.viory.team are different for each. I presume that someone with access to Viory’s Sentry keys has generated and included fresh Sentry keys in each of these instances in order to differentiate between the telemetry from this site versus others using the same Sentry instance,” Wilson said.
“This cuts against the idea that this is, for example, a case of someone just lazily copy-pasting code on Ruptly’s domains. It suggests that each of these snippets was likely to have been deliberately included. The alternative explanation of changing these API keys to some arbitrary value seems much less plausible given the lack of diligence in ensuring other aspects of the content didn’t cross-reference the domains.”
‘Ruptly’ Page Title on Viory Test Page
Finally, Bellingcat found a page at frontend.dev.viory.video/en that appears likely to be a developer test page for the front page of Viory’s main domain viory.video.
Notably, however, the page title reads “Stream trending news | Ruptly.” The page description included in the source code also refers to Ruptly:
“Follow breaking world news in real-time and stream the latest developments in politics, sports, finance, science, tech, and more from one of the top online news sites. Download and share international news today with award-winning news agency Ruptl” [sic].
Screenshot of frontend.dev.viory.video/en page, captured May 10th 2026. Archived source.
Wilson said that the use of the Ruply page title and text on the Viory test page “looks like a case of lazy copy and pasting”.
“That could potentially be done by someone outside of Ruptly, although it would be strange.”
While this particular piece lies on the lower end of the spectrum of proof, Wilson said that together with the other stronger pieces of evidence, including multiple Ruptly domains appearing to send data to Viory using different API keys, and Ruptly’s wildcard SSL certificate on Darpo Vision’s site, the weight of evidence for a connection between Ruptly and Viory adds up.
“None of the pieces of evidence are watertight on their own, but when you add them together it’s difficult to think of other plausible explanations for all of them being true at the same time,” he added.
“None of the pieces of evidence are watertight on their own, but when you add them together it’s difficult to think of other plausible explanations for all of them being true at the same time,”
-James Wilson
Bellingcat also found that Ruptly appears to have connections to a company in Hong Kong. Company records from July 2022 indicate that this company was originally named Ruptly Limited, but in September of that year, the company’s name was changed to Lotus Production Limited.
The Hong Kong company remains registered as active and filed annual reports in September 2025.
Russian Slant in the ‘Global South’
Anna Hiller, a Bangkok-based Consultant Research Analyst for the Institute for Strategic Dialogue told Bellingcat that the resources provided by Viory can be an attractive pool of source material for smaller media outlets, governments and academic institutions with small budgets.
She told Bellingcat that Viory’s editorial choices are clear when looking at the site’s videos.
“When accessing Viory, the prominence of pro-Russian and pro-China content is immediately noticeable, including numerous articles focused on Vladimir Putin, Russia-China cooperation, and broader China-related narratives.”
Bellingcat contacted Viory, Darpo Vision and Lotus Production Limited to ask about the connections we found between the Viory website and Ruptly and between Lotus Production Limited and Ruptly.
Viory said that it had no connection with Ruptly. “Viory has no connection with Ruptly; any suggestion otherwise based on ordinary use of similar digital platforms, tools or cloud providers is poorly founded and inaccurate; Viory is a UAE-based, privately held, self-funded and 100% privately owned organisation, and receives no funding, direction or instructions from any state media,” the company said in an email response.
Ruptly also said it was not connected to Viory. It declined to respond to Bellingcat’s questions, including about specific findings such as Ruptly’s domains sending technical performance and error data to Viory, calling these questions “irrelevant”.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.

 Entrar

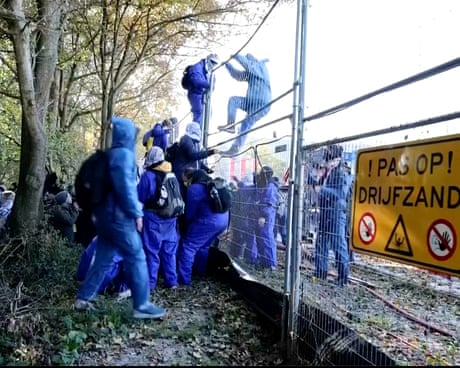
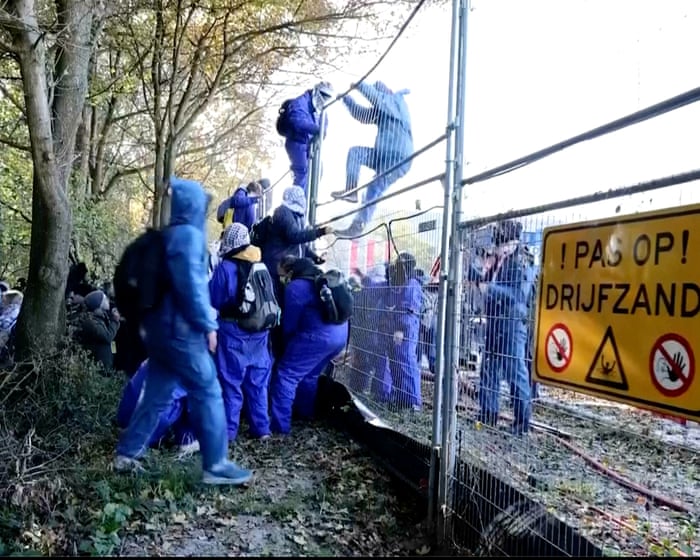

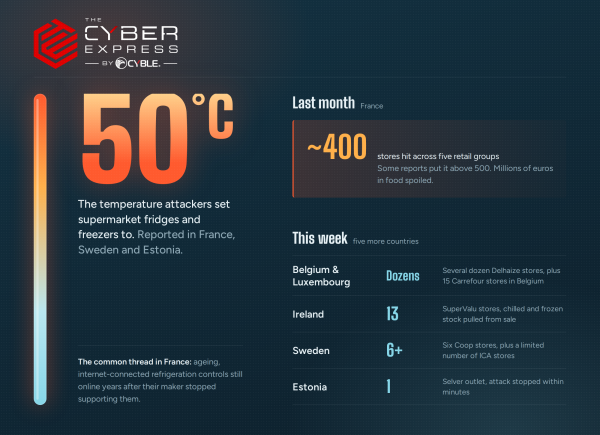 In Ireland, Musgrave Group said refrigeration systems in 13 SuperValu stores were affected by the "
 Swedish grocery giant ICA, one of Sweden's largest supermarket chains, says several of its stores have been hit by a cyberattack overnight, causing refrigerators and freezers to be remotely set to 50°C.


 The Informant (@theinformant_x)