Entrar

US Probes Suspected Hack Behind Military Base Freezer Failures
The Pentagon treats August freezer failures at US military bases as a suspected hack and is working with French investigators after a supermarket attack.
The Pentagon is investigating freezer failures that spoiled food at US military bases in August as a suspected cyberattack, according to four officials who spoke to Reuters. One official said US investigators are also in contact with French authorities about a similar attack on commercial freezers that disrupted supermarkets in France earlier this month. This is the first time Reuters has reported that the US incident is being treated as a suspected cyberattack.
“The Pentagon is treating the spate of mysterious freezer malfunctions that spoiled food at military bases across the United States in August as a suspected hack, according to four officials familiar with the matter.” Reuters reports.
“One of the officials said the military investigators were in touch with their French counterparts about a similar cyberattack on commercial freezers that disrupted supermarkets there earlier this month.”
It is still unclear who is behind the attacks. Reuters could not determine how far the investigation has progressed or whether investigators have identified the cause or those responsible. The Pentagon said a unit of US Cyber Command is working closely with other government agencies and law enforcement. The Army’s Criminal Investigation Division confirmed that its Cyber Field Office is involved and is working with French law enforcement to investigate the freezer outages in Europe.
The incidents hit commissaries, the on-base stores where military personnel buy food. At least six were affected in late August, according to Reuters’ review of the bases’ Facebook posts and website updates. Stars and Stripes named Fort Irwin, F.E. Warren, Naval Station Newport, Columbus and Travis among the confirmed stores, and some outlets count up to 14 sites in 11 states, though not all are confirmed.
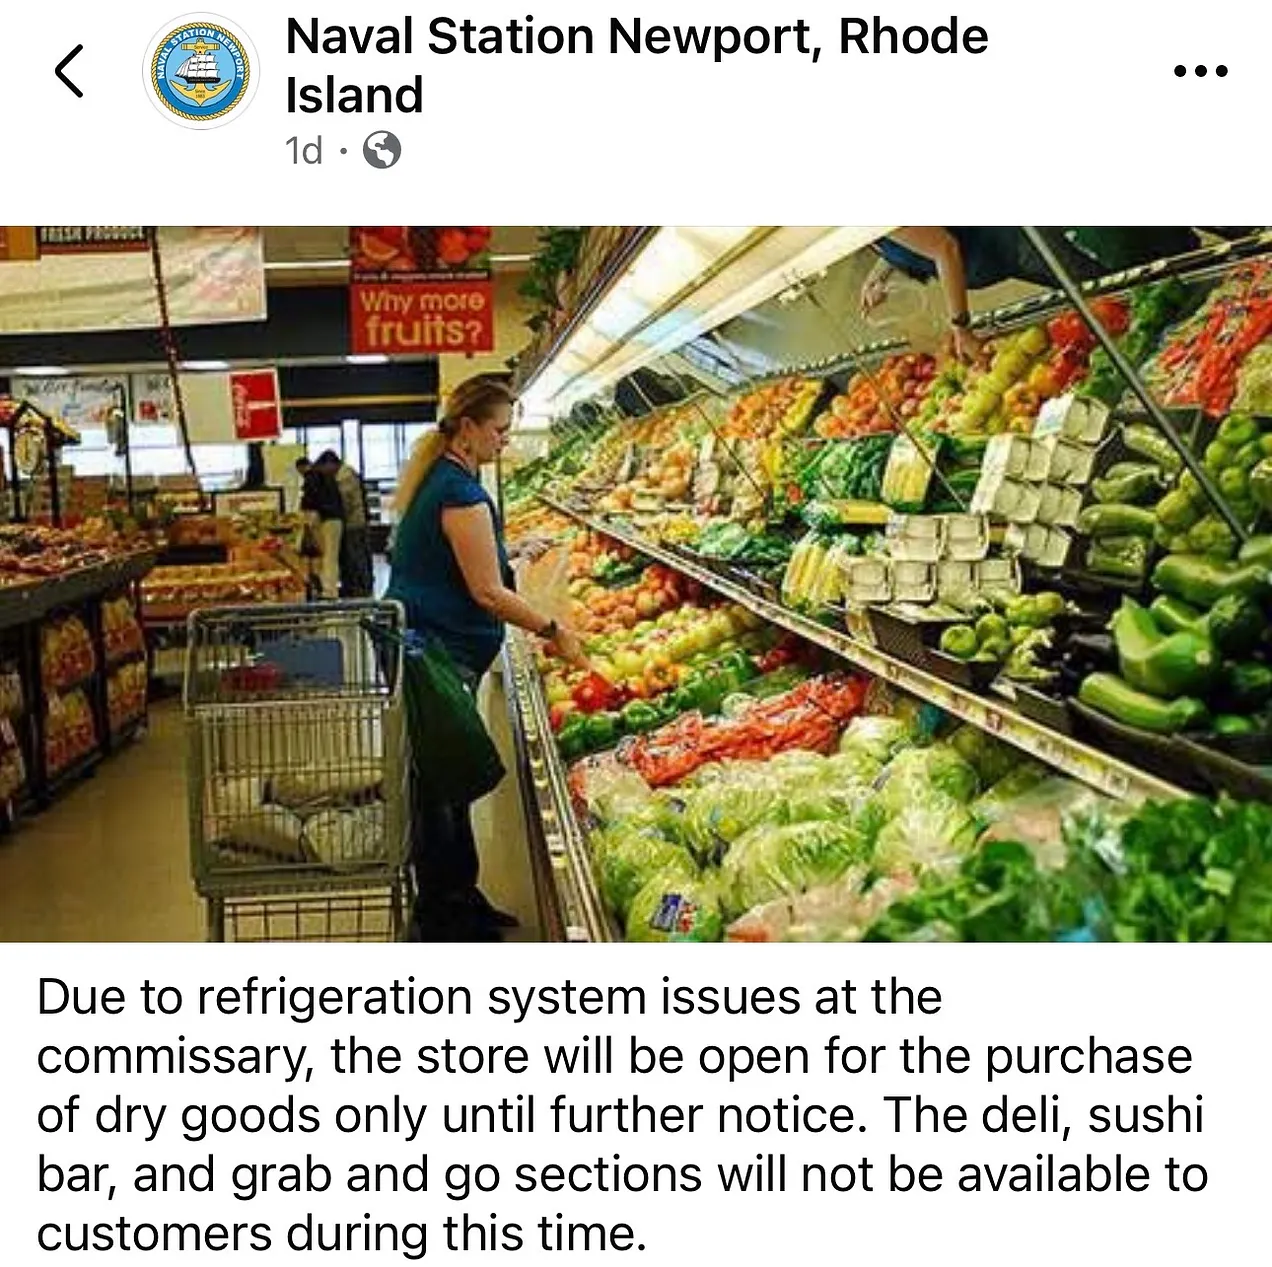
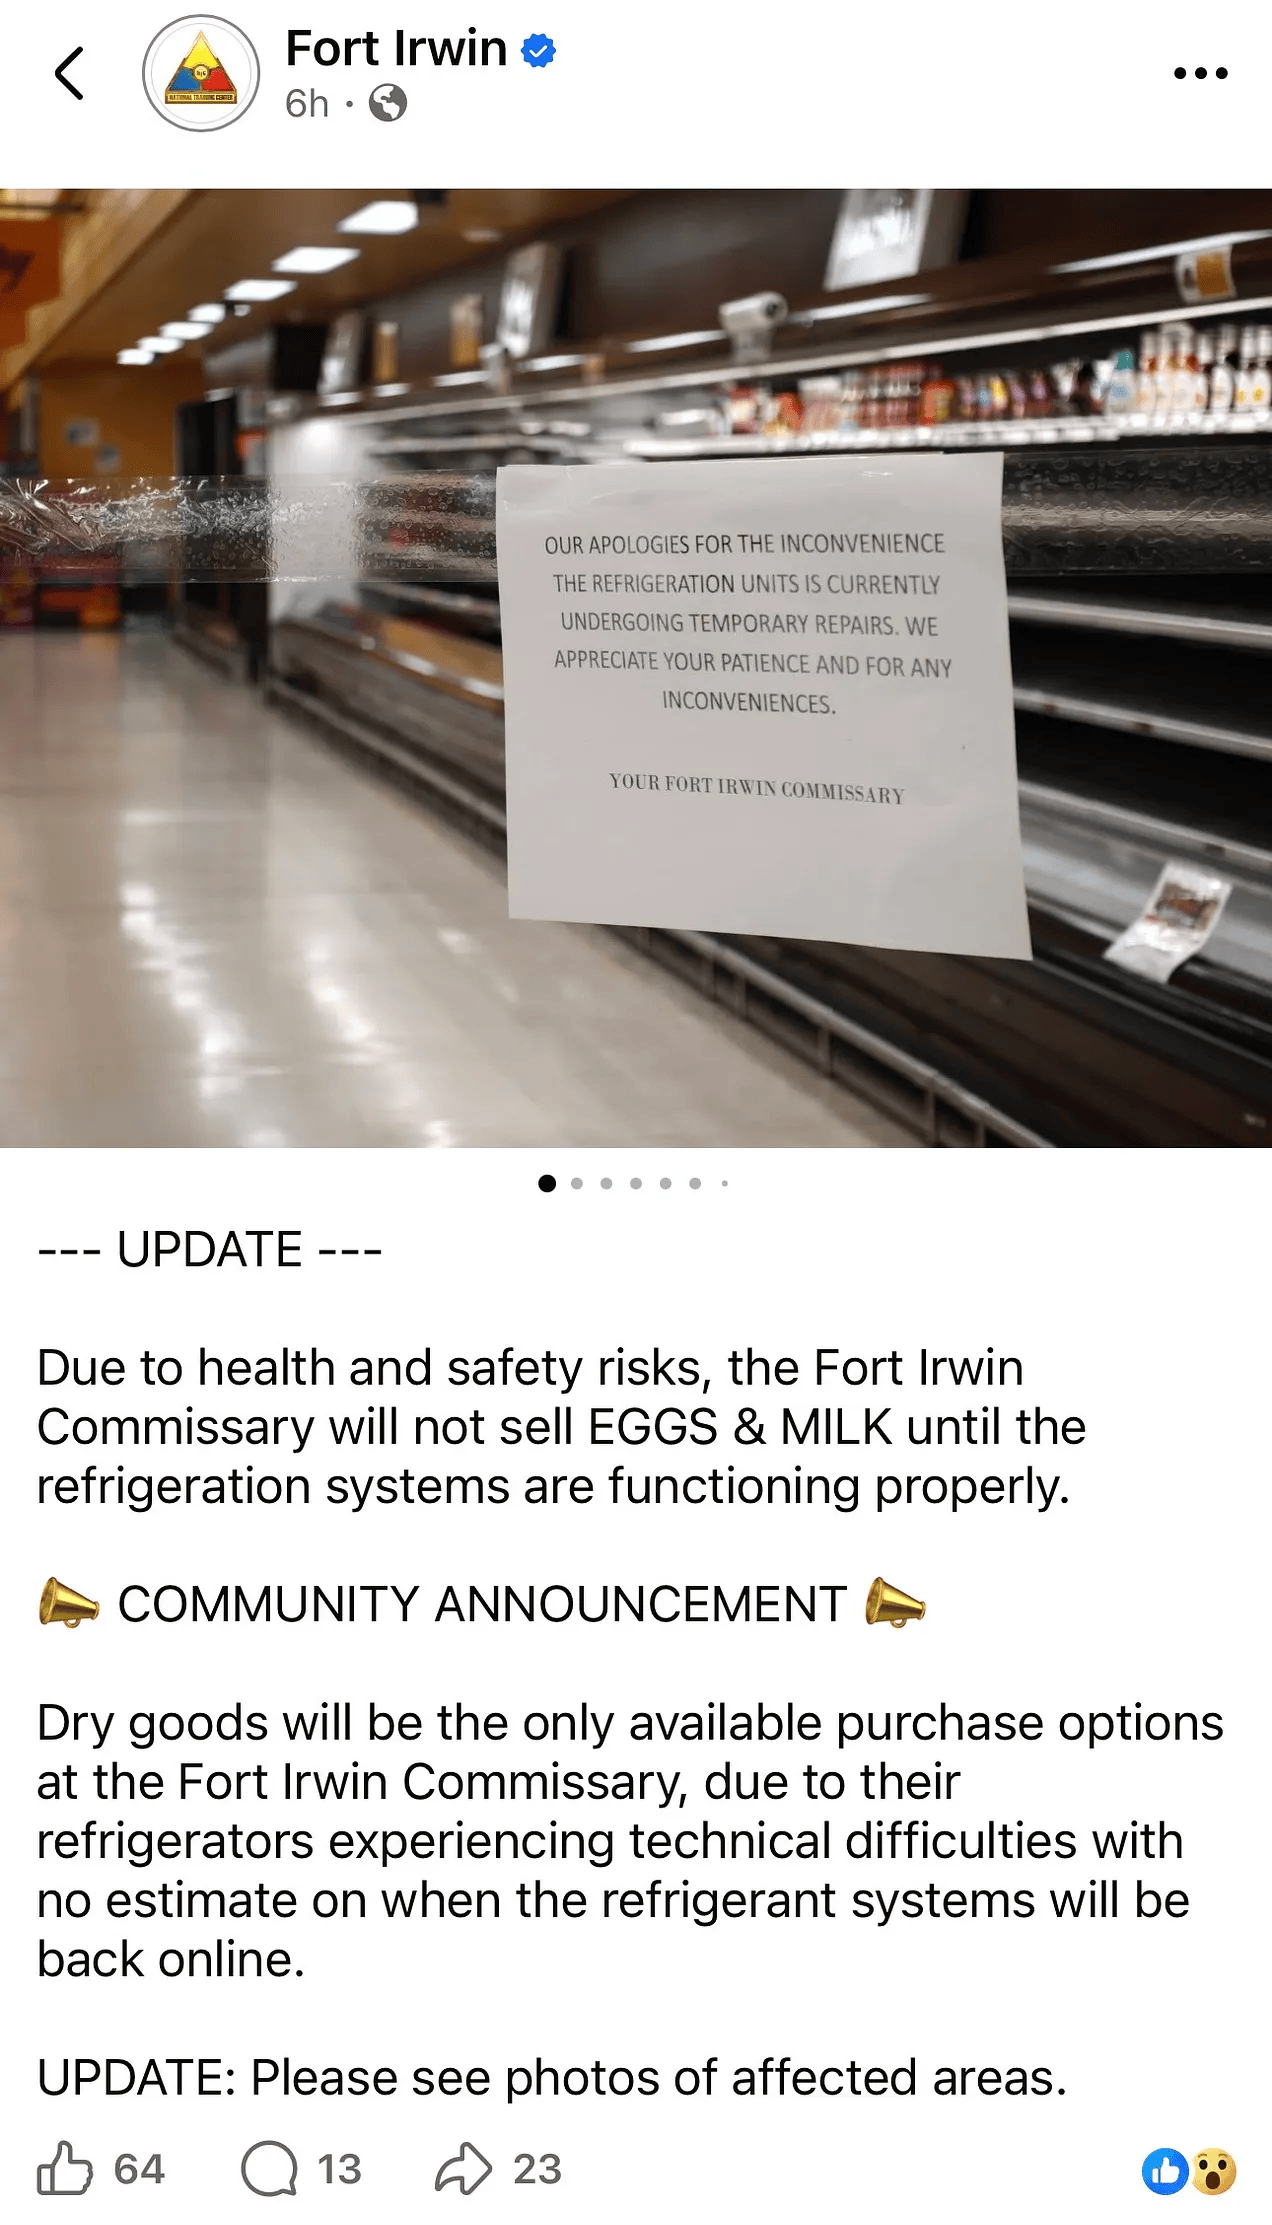
In at least one case the freezers didn’t just stop. Their temperatures were cranked up overnight, which left mounds of wilted or melted food in the morning. Fort Huachuca in Arizona said on August 26 that its freezer went into defrost mode and heated up all the food, adding that trust us when we say it was spoiled.
The Pentagon wasn’t the first to speak. A recently created blog called Signal and Silence reported the freezer failures and the possibility of sabotage on August 28, while Stars and Stripes reported the involvement of military investigators and Britain’s Daily Telegraph reported the contacts with the French. The French Embassy in Washington had no comment. Frozen food is the one asset where damage takes hours and evidence takes the form of puddles.
The French attack is the clearest example. Hackers took control of the cooling units in more than 350 stores and raised the temperatures. Frozen food aisles were emptied, and some units got so hot they caught fire. One supermarket owner said the total cost could reach tens of millions of euros.
The same thing happened in Arizona: attackers made the units hotter instead of just turning them off.
Reuters could not tell which brand was used at the US bases, and Danfoss, which is the manufacturer targeted in French supermarket attacks, did not reply. A public research report on Danfoss controllers came out before the incidents, but nothing shows a link to the bases.
There is a history of attacks on refrigeration systems. Danfoss reports that hackers targeted supermarkets in Russia and Israel in 2022 by exploiting outdated cooling controllers. In December 2025, US prosecutors accused a Ukrainian woman of belonging to a hacking group that disrupted refrigeration at a meat plant in 2024, ruining more than 2,000 pounds of meat.
Earlier this year, the Global Food Safety Initiative urged food safety experts and IT leaders to work together to protect refrigeration systems.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Military Base Freezer)