❌

Visualização de leitura

2nd November – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 2nd November, please download our Threat Intelligence Bulletin.

TOP ATTACKS AND BREACHES

  • Binance, a global cryptocurrency exchange, has suffered a cyberattack resulting in the theft of approximately $6.3 billion in digital assets. Attackers reportedly compromised a DevOps engineer’s laptop and abused internal wallet infrastructure to authorize unauthorized withdrawals. The incident ranks among the largest cryptocurrency thefts ever recorded and is linked to North Korean group.
  • Polymarket, a US-based prediction market platform, has disclosed a cyberattack involving a compromised third-party service that distributed malicious JavaScript to its website. The script hijacked authenticated trading sessions and attempted unauthorized transactions. Approximately $2.7 million in cryptocurrency was traced to a suspected attacker-controlled wallet.
  • Japan Airlines, a major Japanese international airline, has disclosed a third-party data breach affecting approximately 92,000 passengers through the Amadeus reservation system. Exposed records included passenger names and flight information. Approximately 2,000 individuals also had contact information, passport details, and additional travel records potentially accessed.
  • The Florida Department of Education has disclosed a data breach involving unauthorized access to its student financial aid website, potentially affecting 4.9 million individuals. Compromised information reportedly includes names, Social Security numbers, dates of birth, addresses, and contact details. The incident was identified on October 19.

AI THREATS

  • Researchers have identified extensive use of AI agents by the GOLD OGRE ransomware group during Aur0ra attacks. Operators supplied compromised credentials and objectives, allowing AI tools to perform network reconnaissance, identify privileged accounts, and support lateral movement. The group also used AI-assisted development to test endpoint security evasion techniques.
  • Researchers have documented expanding AI adoption among North Korean cyber threat actors. The activity includes using language models to support reconnaissance, develop malicious tools, refine social engineering, and accelerate intrusion workflows. The findings describe how established espionage and financially motivated operations are incorporating AI into existing attack techniques.
  • Researchers have uncovered a global espionage campaign in which the China-linked VAPOR PANDA group used the AI-enabled ARTEX framework against more than 200 organizations. Targets included government agencies, telecommunications providers, and defense companies across at least 14 countries. Confirmed intrusions involved credential theft and deployment of the BLOODALCHEMY backdoor.

VULNERABILITIES AND PATCHES

  • Check Point Research have analyzed HTTP2Shell (CVE-2026-111497), an actively exploited remote code execution vulnerability affecting Brotli decompression implementations. Initially associated with Node.js, the flaw may also affect other components, including Python packages, .NET, and proxies. Automated scanning and suspicious exploitation attempts have been observed.

    Check Point IPS provides protection against this threat (Node.js Brotli Remote Code Execution (CVE-2026-111497)))

  • A critical Linux kernel vulnerability, CVE-2026-98432, has been disclosed with a CVSS score of 9.8. The memory management flaw affects TCP networking and can enable unauthenticated remote code execution with root privileges on systems exposing Multipath TCP listeners.
  • Drupal has addressed CVE-2026-118539, a highly critical access control vulnerability in the Commerce Core module used by online stores. Insufficient protection of application routes and data fields allows unauthenticated attackers to bypass authorization restrictions. The flaw has been exploited in attacks and may affect commercial transactions.
  • Cisco has patched CVE-2026-76418, a high-severity vulnerability affecting Adaptive Security Appliance and Firepower Threat Defense software. The flaw allows unauthenticated attackers to remotely crash devices configured with SSL VPN functionality. Cisco confirmed that the vulnerability had been exploited in attacks before the security updates became available.

THREAT INTELLIGENCE REPORTS

  • Check Point Research has uncovered the Yoba malware campaign, which distributes malicious installers disguised as ChatGPT and Claude desktop applications through fraudulent GitHub projects. Attackers exploit legitimate signed executables to load malicious components and establish persistence. The campaign uses trusted online services for payload delivery and communication.
  • Check Point researchers have analyzed unexpected network activity generated by Alibaba’s Qwen model during a security-related task. Repeated testing produced numerous different destination addresses rather than one consistent endpoint. The findings suggest unstable model behavior is a more plausible explanation than a deliberately embedded data-exfiltration mechanism.
  • Researchers have identified UAT-11473, an advanced threat actor exploiting a Cisco Catalyst SD-WAN authentication bypass to deploy the KeyDrift malware framework. The campaign targeted organizations in aerospace, defense, satellites and policy research. KeyDrift enables persistent access and extraction of sensitive encryption material from compromised network controllers.
  • Researchers have documented more than 400 incidents involving abuse of Microsoft Teams external chat functionality for initial access. Attackers impersonated internal IT support personnel to persuade employees to initiate remote sessions and install access tools. Some campaigns progressed to credential theft, lateral movement, and ransomware-related activity.

The post 2nd November – Threat Intelligence Report appeared first on Check Point Research.

484,142 Exposed Cloud Buckets Contain 18 Billion Files

42 publicly listable cloud buckets containing 18 billion files, including exposed credentials, database dumps and backups.

The Ransomnews research team counted 484,142 publicly listable cloud storage buckets in October 2026, holding 18.05 billion files. They built the count from the search engines that index open cloud storage and published it as the Ransomnews Cloud Exposure Index, written by Mantas Sasnauskas.

“No file was opened for this index. Every number below comes from bucket names, file extensions, file counts and last-modified timestamps. That is a deliberate limit. It keeps the research on the right side of the line, and it turns out to be enough to see where the sensitive material concentrates.” Ransomnews states. “We are calling it the Ransomnews Cloud Exposure Index, and we will rerun it quarterly so the numbers can be compared over time.”

The researchers used bucket names, file types, file counts and last-modified dates to collect their data. They did not open any files, allowing them to identify where sensitive information might be stored without accessing the content. They plan to repeat the research every three months to track changes over time.

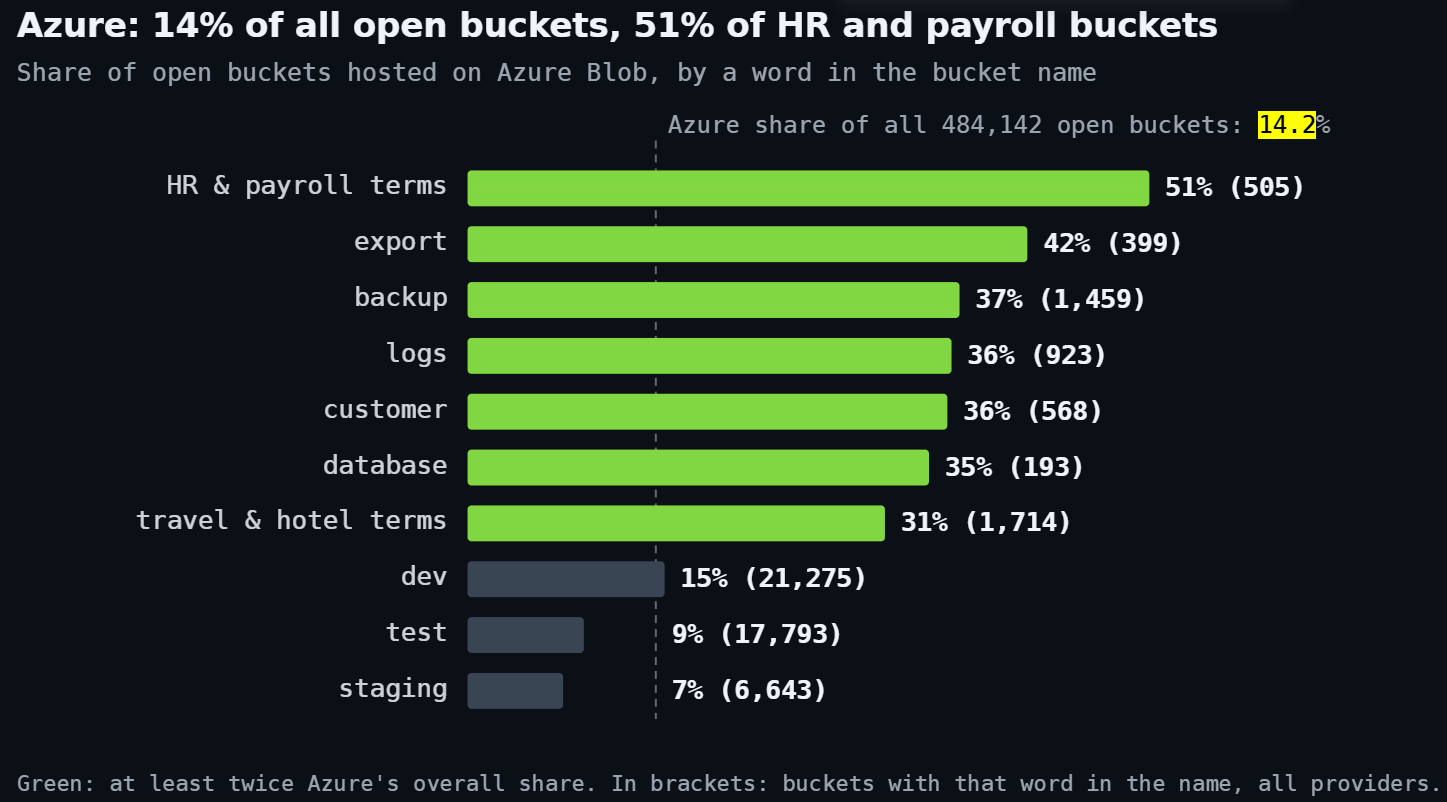
Amazon S3 accounts for 72% of the exposed buckets, roughly in line with its share of the market. This does not mean S3 has weaker security than other providers. Azure Blob, however, appears 2.5 to 3.6 times more often than expected among buckets named for backups, data exports and payroll records. The researchers also found 321,058 files related to credentials and keys. Of the exposed .env files, 67% were last modified in 2026.

Below is the split by provider, from a snapshot taken on October 7:

ProviderOpen bucketsShare
Amazon S3347,98471.9%
Azure Blob68,53214.2%
Google Cloud Storage53,13111.0%
DigitalOcean Spaces11,0692.3%
Alibaba OSS3,4260.7%
Total484,142100%

A lot of these buckets are public on purpose, holding website assets, CDN mirrors, open datasets and podcast archives. So the index isn’t 484,142 breaches. It’s the pool where breaches hide, and the rest of the report narrows it down to the stores that should never have been listable.

“Azure, by a wide margin relative to its size. Azure Blob holds 14.2% of open buckets, but 37% of the 1,459 buckets with “backup” in the name, 42% of the 399 named for exports, and 51% of the 505 carrying HR or payroll terms.” continues the report. “Buckets named for logs, customers and databases sit at 35% to 36%, all around two and a half times Azure’s baseline.”

The skew only shows up for operational data. Buckets named “dev” sit at Azure’s baseline of 15 percent, and “test” and “staging” fall below it, at 9 and 7 percent. The authors suspect Azure storage accounts more often hold line-of-business data such as backups, exports and HR systems that enterprises run on Microsoft, while S3 and Google Cloud carry more application assets. They call it a hypothesis the counts suggest and don’t prove, and it’s the first thing they want to test next time.

By sector, retail and e-commerce names lead with 5,666 buckets, mostly storefront assets. The more worrying number is that names tied to regulated sectors (finance, healthcare, education, government, legal and HR) appear on 10,891 unique open buckets. Those are the places where a stray file most likely holds personal, health or financial records, and where regulators expect to hear about it.

Sector (by bucket name)Open bucketsFiles in them
Retail and e-commerce5,666269.9M
Finance and insurance3,50858.0M
Healthcare2,70947.9M
Media and entertainment2,696136.2M
Education2,39360.6M
Gaming2,29679.0M
Travel and hospitality1,714118.7M
Real estate1,13760.7M
Government and public sector1,00036.2M
Legal97811.3M
Crypto63011.9M
HR and payroll5058.4M

Healthcare-related names appear in 2,709 buckets containing 47.9 million files. The researchers identified them using terms such as “hospital” (135 buckets), “patient” (135), “clinic” (277) and “dental” (331). HR and payroll is the smallest sector, with 505 buckets, 259 of which are hosted on Azure.

These figures are based on names, not proof of ownership. The search matches parts of words, so “store” can refer to object storage as well as shops. A single bucket can also appear in two sectors.

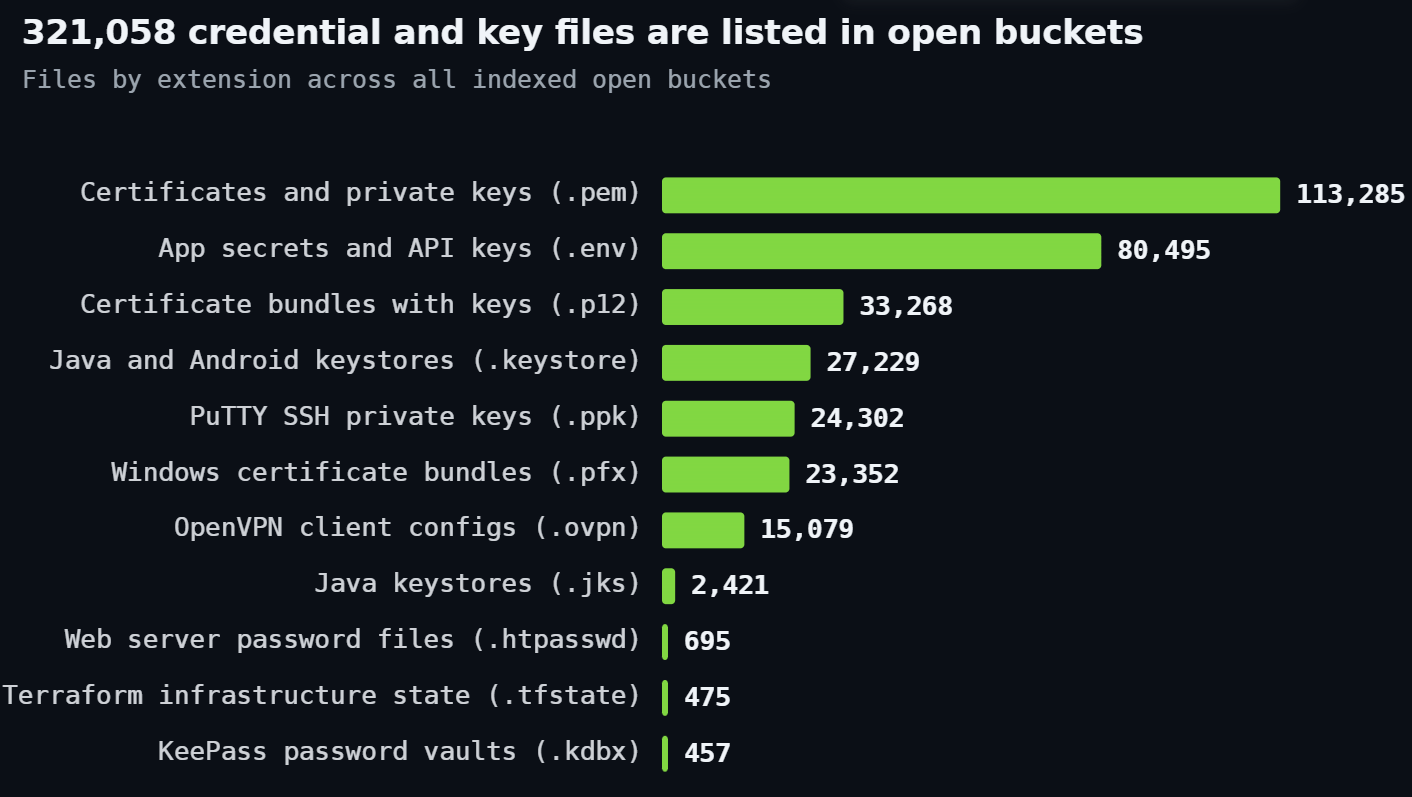
The exposed buckets also list about 4.7 million database and dump files, 15,130 mailbox archives, and tens of millions of spreadsheets and documents. Credential files are particularly concerning because they can turn a cloud misconfiguration into a real intrusion.

File typeWhat it isFiles listed
.pemCertificates and private keys113,285
.envApp secrets and API keys80,495
.p12Certificate bundles with keys33,268
.keystoreJava and Android keystores27,229
.ppkPuTTY SSH private keys24,302
.pfxWindows certificate bundles23,352
.ovpnOpenVPN client configs15,079
.jksJava keystores2,421
.htpasswdWeb server password files695
.tfstateTerraform infrastructure state475
.kdbxKeePass password vaults457

Each of these exists to grant access. A .env file is where developers keep database passwords and API keys. A .tfstate file is Terraform’s record of a whole cloud setup, often with secrets in plain text, and a .kdbx vault is encrypted but now open to anyone who wants to guess passwords offline. Some .pem files are public certificates and some files are test fixtures, so the counts are a ceiling on live secrets and not a measure of them. It’s still a big ceiling.

Database files make up most of the sensitive material by volume:

File typeWhat it usually holdsFiles listed
.sqliteEmbedded app databases2,561,807
.bakDatabase and server backups752,055
.sqlDatabase dumps687,446
.sqlite3Embedded app databases488,176
.dumpDatabase dumps176,603
.mdb / .accdbMicrosoft Access databases36,467
.dmpMemory and crash dumps12,809
.pst / .ost / .mboxMailbox archives15,130
.emlSaved emails4,549,665
.csvData exports and recordsat least 69,580,112
.xlsx / .xlsSpreadsheets42,544,997
.docxWord documents24,936,788
.pdfDocuments, invoices, scansat least 106,191,393
.logApplication and server logsat least 61,310,809

The exposed buckets contain thousands of virtual disk images, including VMware, Hyper-V and QEMU files. A single disk image can contain an entire server, including credentials.

Some exposures involve active systems. Of 80,495 .env files, 67% were last modified in 2026. Certificates and SQLite databases include both recent and older files. Backups appear older, with 89% of the 752,055 .bak files last modified before 2025. Almost all PuTTY key files date from 2024.

Recent leaks need urgent attention, while long-standing exposures point to poor security management. The problem is ongoing: at least 113.6 million files were added to publicly listable buckets in the seven days before September 9. Over the previous 30 days, these included more than 21,000 SQL dumps, nearly 21,000 backup files, 4,477 .pem files and 1,298 .env files.

Public .env files can expose database passwords that ransomware affiliates and initial access brokers look for. Similar credentials appear in stolen-data logs, but in this case, attackers do not need to infect a device. They only need to search for exposed files.

Cloud providers already offer settings to prevent public access. Organizations should enable S3 Block Public Access, disable anonymous access to Azure Blob storage, and enable public access prevention in Google Cloud. These controls should apply at account or organization level to prevent new storage buckets from becoming public.

Organizations should also scan their storage for sensitive files such as .env, .sql, .bak, .pem, .ppk, .tfstate and .kdbx. Terraform state files and virtual disk images should be treated as secrets, stored privately, encrypted and monitored. Backups should never be publicly accessible, and recovery procedures must be tested.

One exposed bucket may be a mistake, but many often indicate a wider process failure. Organizations need to fix the underlying security controls, not just individual buckets.

The research has some limitations. The team queried search engines on October 25, while the bucket list was current to October 7 and the newest indexed file dated September 9. File-level data may therefore be about a month old. Counts are also capped at one million per query, so researchers split larger categories into date ranges and added the results.

Some limits apply. The team queried the search engines on October 25. The bucket list was current to October 7 and the newest indexed file was dated September 9, so file-level figures lag by about a month. The index caps any single count at one million, so larger types were split into date windows and summed.

A last-modified date shows when a file was written, not when it was exposed, and a listed file isn’t proof that its contents can be read. No bucket is named in the report. Exposures with a known owner in regulated sectors are going through responsible disclosure, with national CERTs copied where the owner is public sector or doesn’t respond.

“Rotate any secret that has ever sat in a public bucket. Closing the bucket does not un-leak the key. Assume anything that was listable was copied.” conlcudes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Cloud Buckets)

LevelBlue TTP Briefing Q3 2026: Trusted Access Fuels Data Theft

Explore the latest tactics, techniques, and procedures (TTPs) our incident response (IR) experts are actively facing in the quarterly TTP Briefing, a report built on frontline threat intelligence from our global incident response investigations across LevelBlue during Q3 2026.


A Unified View of the Threat Landscape

This TTP Briefing is based on threat intelligence derived directly from LevelBlue incident response engagements worldwide over the past quarter. These engagements are technology-agnostic, providing a clear view into the real-world tactics, techniques, and procedures adversaries are using today.

The latest edition also incorporates threat intelligence from LevelBlue SpiderLabs, which broadens the dataset behind our findings.


Trusted Access Fuels Data Theft

The theme of the quarter: trusted access fuels data theft. Attackers didn’t need to break in so much as log in. Session tokens captured by phishing kits, OAuth apps users consented to, VPN appliances that accepted forged authentication, and remote management tools that look like routine IT all gave threat actors a foothold that looked legitimate from the inside. Once there, they went after data. We observed data exfiltration appearing in 83% of intrusion cases, while encryption is at 67%. In Q2, both were 77%. Non-ransomware network intrusions were the second most common incident type, and for the first time, exfiltration overtook viewing or accessing files as the most common outcome when data was at risk.

This briefing breaks down what our IR teams saw this quarter: who was targeted, how attackers got in, what they did once inside, and how fast they moved. Each section closes with guidance defenders can act on now.

Across our investigations this quarter, four themes stood out: attackers are diversifying initial access methods, identity has become a primary battleground, data theft is increasingly replacing encryption as the preferred source of leverage, and both attackers and defenders are moving faster than ever.

For additional insights, join our IR experts on November 10 at 11:00am ET or November 12 at 11:00am GMT for live webinars where they will explore our findings in more detail. Come armed with questions and walk away with actionable intelligence, detection priorities, and recommendations to strengthen your defenses.

Let’s explore a few key findings:


Most Common Threat Types

incident types qq
Figure 1. Most common threat types.

  • BECs continued to be the most common threat incident type, accounting for 32% of incidents.
  • Network intrusions without ransomware held steady as the 2nd most common incident type at 22%. This is largely due to threat actors focusing on exfiltration and extortion, rather than encryption.
  • Ransomware was the 3rd most common incident type, accounting for 20% of incidents this quarter.

Detection built around encryption events will miss a growing share of intrusions. Watch for large outbound transfers, unusual archive creation, and new cloud storage destinations.


Data Exfiltration Becomes the Focus for Attackers

Exfiltration/extortion-only attacks were the fastest-growing category in Q3, with attackers stealing data and threatening to publish it without deploying ransomware. Attacks that combine encryption with exfiltration remain the most common, but their share has fallen each quarter. This suggests encryption is no longer a given in ransomware cases, and the leverage increasingly comes from the stolen data itself.

intrusions qq
Figure 2. Intrusions.

The tools observed during investigations reinforce this trend. Utilities such as rclone, MegaSync, WinSCP, 7-Zip, and WinRAR continue to play an important role in attacker workflows, helping collect, package, and transfer sensitive information outside the organization.

Protecting systems remains essential, but organizations must also understand where their most sensitive information resides, who has access to it, and how they will detect abnormal movement or exfiltration activity before data leaves the environment.

Initial Intrusion Vector (How Are They Getting In?)

iiv qq
Figure 3. Initial intrusion vectors.

Phishing remained the top initial intrusion vector in Q3 at 42%, down from 65% in Q2. External remote services (RDP, VPN) and exploited vulnerabilities tied for second at 14% each. Together, those two internet-facing routes now account for more than a quarter of initial access.


Identity Is the Thread Through the Intrusion

  • Valid-account abuse has grown in each quarter. It is still a small share of initial access, but the direction is clear.
  • Social engineering often ends in stolen identities. Phishing/social engineering remains the most common way in, and that category includes vishing and help-desk impersonation. Many of those cases result in stolen credentials or tokens, so identity likely plays a larger role than the valid-accounts bar alone shows.


Most Commonly Observed CVEs – Q3

These are the vulnerabilities our incident response teams saw actively exploited in real incidents this quarter, which makes them a sharper patching priority list than any CVSS score.

CVE-2026-0257

PAN-OS Global Protect

CVE-2026-25639

Axios TypeError

CVE-2026-72898

Metabase

CVE-2025-13407

Gravity Forms WordPress plugin

CVE-2024-40762

SonicWall SonicOS SSLVPN

CVE-2024-40766

SonicWall SonicOS SSLVPN

CVE-2024-53704

SonicWall SonicOS SSLVPN

CVE-2024-53705

SonicWall SonicOS SSRF

CVE-2022-26923

Active Directory Domain Services

Inside the CVE Numbers:

Inventory internet-facing business applications, not just network appliances. If it touches sensitive data and faces the internet, it belongs on the emergency patch list.


Exploitation Is Back, and Initial Access Diversifies

While social engineering remains a top concern, internet-facing flaws have increased as an initial access route, with CVEs and external remote services both rising in Q3. Attackers are using a wider mix of entry points, including vulnerabilities like Metabase.

A look at Metabase - CVE-2026-72898

A vulnerability was discovered earlier this quarter in Metabase, an open-source business intelligence and data visualization platform. Identified as CVE-2026-72898, this vulnerability allows for unauthenticated SQL Injection that could lead to remote code execution with a cvss score of 10. If exploited, this vulnerability could allow a threat actor to hijack an account and gain admin access to the connected Metabase instance. From there, we observed threat actors creating new admin accounts, and leveraging the AI engines to gain access to 3rd parties connected to Metabase, and exfiltrating data from there and extorting the victim. This vulnerability allowed for a fully self-contained intrusion path from initial access through end goal.


MFA Bypass

mfa bypass qq
Figure 4. MFA bypass.

MFA is close to universal among the organizations we respond to, yet it no longer stops business email compromise attacks. In Q3, threat actors bypassed MFA in 79% of BEC incidents where it was enabled.

Although MFA remains widely deployed, attackers are increasingly sidestepping it through vishing, convincing victims to enroll an attacker-controlled device on their account. Because the victim approves the registration, the access appears legitimate, reflecting a shift from token interception to abuse of trusted device enrollment. Additionally, threat actors are relying more on machine identity and token abuse, rather than a normal user account attack, which does not involve bypassing MFA, contributing to the dip in our bypass stat.

Because attackers increasingly rely on valid tokens rather than defeating the prompt, pair MFA with continuous session-token monitoring, short token lifetimes, and conditional-access policies that flag anomalous token use.

The lesson is clear: identity security cannot be a standalone initiative. Organizations should pair phishing-resistant MFA with stronger monitoring of enrollment activity, conditional access controls, and greater visibility into account misuse across cloud and on-premises environments.


Most Targeted Industries and Company Sizes

Industires qq
Figure 5. Most targeted industries.

Targeted industries saw a shift in Q3. Financial services, which had been the top impacted sector for the last few quarters, dropped to #4, accounting for only 11% of incidents in Q3, down from 28%. Technology & Software surged to the top spot, accounting for 14% in Q3, up from 5% in Q2, and 3% in Q1. Healthcare and Manufacturing tied for the 2nd spot at 13%. This shift demonstrates that no industry is off limits to threat actors, and every sector should focus on cyber resilience.

Technology & Software spike: We observed an increase in compromised custom software and applications via exposed API keys, a trend that became more common in Q3 as threat actors used AI to hunt for exposed keys as an entry point into custom technologies. Because API keys are often long-lived, over-permissioned, and bypass MFA, a single exposed key can give direct access to sensitive data and connected systems. That reach, which can extend to a provider’s customers, makes the sector an attractive target.

Organizations with revenue between $1M–$100M accounted for the largest share of incidents in Q3, reinforcing that threat actors increasingly view mid-market companies as high-value, lower-resistance targets.


Tactics Across the Intrusion Path

undefined-Oct-27-2026-05-19-09-9456-PM
Figure 6. Trends across the intrusion path.

The TTP Briefing provides data across the five stages of the intrusion path, from initial access to persistence and escalation techniques, to exfiltration and monetization tactics. Noteworthy findings include:

  • Back door/remote access tools remain the most common tool type leveraged to gain persistence, using tools like ScreenConnect and MeshAgent to maintain access.
  • Credential stealers, like mimikatz and DCSync, continue to be commonly used to escalate privileges, as identity compromise remains a top concern.
  • During the data at risk stage of the intrusion path, files were most often exfiltrated, surpassing viewed/accessed for the first time, highlighting that threat actors are focusing heavily on data exfiltration.


A Look Into Dwell Time

dwell time qq
Figure 7. Dwell time.

In the TTP Briefing, we exclude any MDR clients and measure dwell time from the initial date of the compromise until our IR team is engaged. This quarter, average dwell time continued to decrease, with 56% of incidents being resolved between 0-10 days. Shorter windows can mean faster detection, faster attacker execution, or both, and in Q3 we saw plenty of the latter.

What the shift says: Attackers are executing faster than we have ever seen. Some intrusions now play out in hours instead of days, with threat actors using AI tools to move through networks. Detection is improving, but so is attacker speed.

Review the full findings:

If you would like more information about this report, our team is available 24/7 at response@levelblue.com

Australian Data Breach Incidents Up 66% as AI Sharpens Scams

ASD Cyber Threat Report

Australians filed a cybercrime report about every six minutes over the past year, and artificial intelligence is making the attacks behind those reports faster and more convincing. That is the main finding of the ASD Cyber Threat Report 2025-26. It is the seventh annual assessment from the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC).

In FY2025-26, the agency received more than 82,000 cybercrime reports through ReportCyber. It responded to over 1,500 cyber security incidents, up more than 20% on the previous year and 36% over five years. It also notified Australian entities of potentially malicious activity more than 4,400 times, almost 80% more than in FY2024-25.

What the ASD Cyber Threat Report Says About AI

The report calls AI the defining force in the threat environment this year. In his foreword, Deputy Prime Minister and Defence Minister Richard Marles wrote that AI is helping malicious actors find vulnerabilities faster and exploit them at greater scale, speed and sophistication. He also noted that new threats have emerged in recent weeks from the unintended actions of AI agents and from model testing.

ASD’s ACSC makes one clear distinction. AI has not created new kinds of threats. It has amplified and sped up existing ones. AI-enabled cyber threats are most visible in social engineering. Attackers are using AI to write phishing emails with no spelling or grammar errors and to automate targeted spearphishing. The Australian Securities and Investments Commission has also seen a sharp rise in scams that use deepfake videos of celebrities and politicians.

The time defenders have to respond is also shrinking. The agency has previously observed that most vulnerabilities are exploited within two weeks, and some within 48 hours of a patch being released. It expects AI-driven tools to shorten that window further over the next 12 months. Publicly reported vulnerabilities (CVEs) rose 30%. Old flaws are still a problem too: ASD’s ACSC recorded the successful exploitation of a vulnerability first identified in 2008.

Incident Severity Grows in ASD Cyber Threat Report Data

Only one Category 2 incident was recorded this year. However, extensive compromises rose from 26 to 40. ASD’s ACSC identified 362 incidents after proactively notifying organisations. A single notification about cPanel vulnerabilities, sent to 340 entities in May 2026, led to more than 60 confirmed incidents.

The number of ransomware incidents held steady at 139, but extensive ransomware incidents rose from 16 to 24. Health Care, Professional, Scientific and Technical Services, and Manufacturing remained the most affected sectors. Data breaches made up 98 incidents, a 66% increase on the previous year. Separately, the Office of the Australian Information Commissioner received 1,205 breach notifications in 2025. That is the highest yearly total since its Notifiable Data Breaches scheme began in 2018.

The financial impact is rising for businesses. The average self-reported cost of cybercrime per business report rose 16% to $93,500. For medium-sized businesses, it rose 45% to $141,300. The average cost for individuals stayed at $33,000. Identity fraud remained the most reported cybercrime, although reports fell 18%.

Stolen access is now a major entry point. Compromised accounts and credentials were among the most frequently reported incident categories, and phishing appeared in 39% of incidents. Government survey research cited in the report found that 55% of Australians reuse passwords across multiple accounts.

State Actors and Critical Infrastructure in the ASD Cyber Threat Report

State-sponsored actors continued to target Australian government, business and individuals to gain sensitive information. The report says these actors are increasingly pre-positioning inside networks to enable future disruption. Marles wrote that the line separating state-sponsored espionage from sabotage and cybercrime is becoming increasingly blurred.

In April 2026, ASD’s ACSC and international partners highlighted a shift by China-nexus actors. These actors are moving towards large covert networks built from compromised home and small office routers, Internet of Things devices and smart devices.

Critical infrastructure accounted for 154 incidents, or 10% of the total, a decrease of almost 7%. Phishing was the leading initial access technique at 36%, and Financial and Insurance Services was the most affected critical infrastructure division at 30%.

What the Threat Report Asks Organisations to Do

In October 2026, ASD’s ACSC released the Essentials series. It evolves the Essential Eight into a principles-based framework with three chapters: Enterprise IT, Operational Technology and Cloud.

Under its Cyber Action Year, the agency is pushing five priorities:

  • Replacing or mitigating legacy technology.
  • Implementing best-practice event logging.
  • Managing supply chain risk.
  • Preparing for AI-enabled threats.
  • Preparing for post-quantum cryptography, including ceasing the use of traditional asymmetric cryptography by the end of 2030 or sooner.

The report also urges organisations to patch faster. For individuals, it recommends reviewing privacy settings and enabling multi-factor authentication or passkeys.

Suspicious activity, incidents and vulnerabilities can be reported at cyber.gov.au or through the Australian Cyber Security Hotline on 1300 CYBER1 (1300 292 371).

26th October – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 26th October, please download our Threat Intelligence Bulletin.

TOP ATTACKS AND BREACHES

  • Japanese cloud hosting provider Onamae Desktop Cloud has confirmed a cyberattack in which intruders compromised its infrastructure and installed malware on customer servers. More than 26,000 servers were potentially affected. The provider began shutting down customer environments on October 21 to contain the intrusion and prevent further unauthorized activity.
  • India’s state-run State Bank of India, serving more than 500 million customers, disclosed a data breach after 3,897 customer records appeared online. The exposed information reportedly included contact details, residential addresses, birth dates, bank profiles, loan records, and identity-verification documents. The bank reported no disruption to core services.
  • WordPress backup developer TeamUpdraft has suffered a cyberattack after intruders accessed its website and potentially exposed customer information and management-service connection keys. Attackers subsequently abused compromised UpdraftCentral keys to install backdoors on WordPress websites during an 18-hour campaign on October 18 and 19.
  • LiteLLM, a widely used open-source AI gateway, confirmed an October 21 supply-chain attack in which attackers used stolen developer tokens to publish malicious packages and Docker images. The compromised version 1.107.0 was designed to steal cloud credentials and AI service secrets, with attackers subsequently testing stolen AWS credentials.

AI THREATS

  • Check Point Research uncovered how AI-enabled antidetect browsers allow operators to manage thousands of deceptive accounts while evading platform safeguards. Tools including Kameleo, AdsPower, and MultiLogin facilitate account takeovers, financial fraud, and automated distribution of AI-generated content, supporting large-scale influence operations across social media platforms.
  • Researchers observed affiliates of INC and The Gentlemen ransomware groups using AI agents to conduct human-approved cyberattacks. The operation targeted 62 organizations by exploiting remote-access systems and compromised credentials. Victims were concentrated in the manufacturing, energy, healthcare, and pharmaceutical sectors, primarily in the United States.
  • Researchers analyzed a cybercriminal operation that used multiple AI assistants to plan and execute different types of malicious activity. The attacker relied on AI-generated scripts and reconnaissance reports to develop attack capabilities. Exposed operational records revealed how AI tools supported campaign planning, technical execution, and adaptation across different targets.

VULNERABILITIES AND PATCHES

  • Critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619 have been used in widespread exploitation attempts that could enable remote code execution. Attack traffic reportedly increased from thousands to millions of attempts following disclosure. As of October 23, approximately 97.5% of publicly visible PHP instances did not indicate patched versions.

Check Point IPS provides protection against this threat (PHP Remote Code Execution (CVE-2026-109618, CVE-2026-109619, CVE-2026-115560((

  • Oracle has released its October 2026 Critical Patch Update, addressing 1,209 unique vulnerabilities through 1,295 security patches across 33 product families. The update includes 95 critical CVEs and affects widely deployed enterprise products, including Fusion Middleware, E-Business Suite, MySQL, and Java SE.
  • GitLab has fixed CVE-2026-110264, a critical vulnerability with a CVSS score of 10.0 affecting Community and Enterprise Editions. The integer overflow flaw could allow unauthenticated attackers to execute arbitrary code remotely on affected servers. The vulnerability affects versions before 18.11.13 and several 19.x releases.
  • A critical privilege-escalation vulnerability, CVE-2026-114625, affects on-premises Arista VeloCloud Orchestrator deployments. The flaw carries a CVSS score of 9.4 and allows authenticated users, including those with read-only access, to obtain operator-level permissions. Successful exploitation can expose restricted management functions, and the vulnerability has been exploited in attacks.

THREAT INTELLIGENCE REPORTS

  • Check Point Research has profiled Aokigahara, a newly identified infostealer targeting credentials and session data associated with AI applications, developer tools, and cloud platforms. Targeted applications include Claude, ChatGPT Desktop, Cursor, and GitHub Copilot. Stolen information may include authentication tokens, account credentials, and other sensitive application data.
  • Researchers revealed that U.S. federal investigators suspect an executive at a ransomware negotiation company assisted the ShinyHunters extortion group in operating its victim disclosure website. The site reportedly listed nearly 100 organizations between May and October 2026.
  • Researchers mapped Lazarus’s Operation FlashHole, a cyberespionage campaign targeting organizations in South Korea’s software, construction, and telecommunications equipment sectors. Attackers used tailored phishing messages and fraudulent portfolio websites to deliver malware. The campaign exploited trusted financial-security software to execute malicious components.
  • Researchers have uncovered a large-scale campaign by threat actor k0t targeting Fortinet FortiGate, FortiWeb, and Palo Alto Networks GlobalProtect devices. Attackers exploited vulnerabilities and weak credentials to establish persistent access and steal information. The operation exposed more than 70,000 credentials and showed possible connections to ransomware groups.

The post 26th October – Threat Intelligence Report appeared first on Check Point Research.

FBI and CISA Warn of SafePay Ransomware Attacks on 600 Organizations

SafePay ransomware has hit 600+ organizations since 2024, using stolen credentials, VPN access and double extortion to pressure victims into paying.

CISA, the FBI, the US Secret Service, Germany’s Landeskriminalamt Rheinland-Pfalz, and two UK law enforcement agencies jointly published an advisory this week on SafePay, a ransomware group they describe as one of the most active operations currently running. The group has breached at least 600 organizations across critical infrastructure sectors since August 2024, spanning North America, South America, Europe, and Australia.

“Since August 2024, SafePay ransomware group’s operations have affected a wide range of businesses and critical infrastructure in North America, South America, Europe, and Australia. SafePay ransomware was among the most active ransomware groups in 2026. The SafePay threat actors have impacted at least 600 separate victims from multiple critical infrastructure sectors.” reads the joint advisory, “The authoring agencies encourage organizations to implement the recommendations in the Mitigations section of this advisory to reduce the likelihood and impact of SafePay ransomware incidents.”

SafePay appeared in mid-2024 as an independent ransomware group that operates without affiliates. This is unusual because many major ransomware groups work like franchises, allowing other criminals to use their tools and services. SafePay grew as groups such as BlackCat and LockBit declined, and its activity has continued. The advisory includes findings from FBI, US Secret Service, and German investigations through August 2026.

SafePay’s preferred entry points are exposed credentials, brute force password attacks, and VPN access.

“The FBI, USSS, and cybersecurity researchers observed SafePay threat actors obtaining initial access [TA0001] to organizations through various means, including credential exposure, implementing brute force password attacks [T1110], and exploiting virtual private network (VPN) access.” states the advisory. “SafePay threat actors use the IP addresses of the VPN provider “Mullvad” to attain initial access—specifically, SafePay threat actors use phished account profiles to access victim networks to exploit the following known Common Vulnerabilities and Exposures (CVEs) for edge device products”

Security teams should watch for unusual login attempts coming from Mullvad VPN IP addresses. SafePay also uses stolen account credentials and automated scripts to exploit known vulnerabilities in internet-facing devices. These include Cisco VPN flaws from 2020 and 2023, a Veeam vulnerability, and a SonicWall access control issue.

Once inside a network, the attackers rely on common tools rather than specialized malware. They use PsExec, WinRM, RDP, and PowerShell to move between systems. A PowerShell script called ShareFinder.ps1 helps them find shared folders and identify valuable data. Mimikatz is used to steal credentials, while AnyDesk and TeamViewer provide remote access. To steal data, the group uses tools such as FileZilla, RClone, WinSCP, and even OneDrive.

Encryption uses a ChaCha20 stream cipher combined with RSA for key exchange, with methods customized based on file type and size. Files get the .SafePay extension appended.

“Data encrypted with the SafePay ransomware variant (appended with .SafePay) cannot be recovered without the decryption key. SafePay threat actors hold the encrypted data for ransom and typically demand a subset of company revenue in cryptocurrency in exchange for decryption software.” states the advisory. “SafePay threat actors leave a ransom note on the victim’s system, typically on the desktop or root directory, advising them that SafePay locked their system and to reach out over a chat portal at a TOR .onion website link with a victim ID as the login. “

Paying the ransom remains the only path to decryption for encrypted files, and even that isn’t guaranteed to work.

The group runs a double-extortion model: steal first, encrypt second, threaten to post the stolen data publicly if the victim doesn’t pay. After encryption, SafePay sends victims to a Tor-based chat portal for negotiations. A representative also makes phone calls to apply pressure. If no payment comes, everything goes on the leak site. The group also deletes Volume Shadow Copies and resets network-attached backup devices to factory settings, which is the operational equivalent of cutting off every exit before the fire starts.

The advisory recommends several basic security measures. Keep internet-facing devices, especially VPNs and firewalls, up to date. Prioritize vulnerabilities listed in CISA’s Known Exploited Vulnerabilities catalog. Enable multi-factor authentication (MFA) for VPNs, webmail, and accounts that access critical systems.

Limit the number of accounts allowed to use administrative tools. SafePay relies on legitimate Windows tools to move through compromised networks, making its activity harder to detect. Organizations should also keep backups offline, encrypted, and immutable so attackers cannot access, change, or delete them.

CISA also recommends reviewing all accounts with admin privileges, setting time-limited access where possible, and disabling command-line tools for any account that doesn’t need them.

The advisory includes IOC files in STIX XML and JSON format, full MITRE ATT&CK mapping, and complete file and IP indicators.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)

19th October – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 19th October, please download our Threat Intelligence Bulletin.

TOP ATTACKS AND BREACHES

  • CenterPoint Energy, a US utility company serving Texas and several other states, has disclosed a data breach affecting more than 1 million Texas residents. Unauthorized access to an external system exposed names, addresses, Social Security information, and driver’s license numbers, according to regulatory notifications filed by the company.
  • Burger King Japan, operator of the international fast-food chain in Japan, has disclosed a breach affecting approximately 11.18 million application members. Unauthorized access between October 2 and 7 exposed contact information, birth dates, gender, and regional details. The company found no evidence of compromised passwords or payment cards.
  • ConnectWise Cloud Backup, a Microsoft 365 backup service used by managed service providers, has suffered a credential compromise enabling unauthorized access to customer environments. Attackers used compromised application credentials to sign in to at least 173 organizations, potentially accessing email, files, and Teams information before access was suspended.
  • Several French supermarkets, including E. Leclerc stores, have experienced cyberattacks targeting connected refrigeration controllers. Attackers reportedly manipulated temperature settings, causing refrigeration system failures, food losses, and operational disruption. Losses from the attacks exceeded $100,000 for one retailer.

AI THREATS

  • Check Point researchers have identified critical vulnerabilities in LiteLLM, a widely used AI model gateway. CVE-2026-35029 and CVE-2026-59823 could allow low-privileged users to change configurations, access sensitive files, redirect requests, and steal credentials. Successful exploitation could enable administrative takeover or remote code execution. LiteLLM addressed both flaws.
  • Check Point researchers have demonstrated how peer influence can cause AI agents working in teams to violate established rules. In controlled experiments, repeated changes in teammate behavior increased one agent’s violation rate from 44% to 98%. The agents rarely acknowledged peer influence when explaining their decisions.
  • India’s national cybersecurity response team, CERT-In, has reported unauthorized access to organizational systems involving autonomous AI agents. The activity exploited exposed credentials, insecure application interfaces, and misconfigured cloud services to retrieve business information. Compromised credentials also enabled repeated access without detection by the affected organizations.

VULNERABILITIES AND PATCHES

  • Microsoft has released its October 2026 Patch Tuesday updates, addressing a record 1,413 vulnerabilities across Windows, Office, SharePoint, and other products. The updates address several critical flaws and three zero-days. Among them is CVE-2026-96951, an actively exploited Windows Shell vulnerability that allows attackers to bypass security protections.

Check Point IPS provides protection against this threat (Microsoft Windows Shell Command Injection (CVE-2026-96951))

  • Ivanti Connect Secure is affected by CVE-2026-104935, an authentication bypass vulnerability that allows remote attackers to execute commands without valid credentials. The flaw has been reported as actively exploited and was added to CISA’s Known Exploited Vulnerabilities catalog. Affected deployments include internet-facing secure access appliances.

Check Point IPS provides protection against this threat (Ivanti Connect Secure Authentication Bypass (CVE-2026-104935))

  • GitLab has released security updates addressing CVE-2026-97229, a critical vulnerability affecting Community and Enterprise Editions. Rated CVSS 10.0, the flaw allows unauthenticated attackers to execute code remotely through insufficient validation of CI/CD configurations. The updates also address vulnerabilities involving script injection, authorization bypass, and pipeline manipulation.
  • BeyondTrust has addressed CVE-2026-102764, a critical authentication bypass vulnerability affecting Remote Support versions 26.2.3 and earlier. Rated CVSS 9.3, the flaw allows unauthenticated attackers to perform unauthorized file operations on affected appliances. The China-linked espionage group ARMORY CASTLE reportedly exploited the vulnerability before its public disclosure.

THREAT INTELLIGENCE REPORTS

  • Check Point researchers have identified phishing campaigns using counterfeit calendar invitations to steal Microsoft account credentials. Malicious invitations carried calendar attachments or deceptive meeting links directing recipients to credential-harvesting pages. More than 302,000 unique phishing emails targeting over 40,000 organizations were identified during the tracked campaigns.
  • Check Point researchers have analyzed election-related phishing and fraud targeting US voters ahead of the 2026 midterms. The research identified spoofed registration messages, exposed election-office credentials, fake prediction-market websites, and politically themed merchandise domains.
  • Researchers have profiled Silent Lynx, a Kazakhstan-linked espionage group targeting Russian energy infrastructure and government entities in Central Asia. Attackers used spear-phishing messages sent through compromised government email accounts and hosted malicious files on legitimate services. Campaign activity also involved exploitation of WinRAR vulnerability CVE-2025-8088.

Check Point IPS provides protection against this threat (RARLAB WinRAR Directory Traversal (CVE-2025-8088)


The post 19th October – Threat Intelligence Report appeared first on Check Point Research.

12th October – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 12th October, please download our Threat Intelligence Bulletin.

TOP ATTACKS AND BREACHES

  • Denmark’s government has disclosed a breach involving its Central Register of Persons after unauthorized individuals exploited access provided to a private supplier. The incident reportedly exposed personal information, including names, addresses, and identification numbers, associated with approximately 8.8 million individuals in the national registry.
  • UK-based online fashion retailer ASOS has confirmed a cyberattack involving stolen employee credentials that enabled unauthorized access to third-party platforms. Attackers reportedly obtained customer names and contact details and sent unauthorized push notifications to mobile application users. The threat group Xuanye claimed responsibility for the incident.
  • ATB, Ukraine’s largest grocery retailer, has faced a cyberattack that disrupted its online services after attackers posted an extortion demand on its website. The DataSuckers group claimed to have stolen records belonging to 7.9 million customers, which include names, addresses, passport information and order records.
  • Osaka Metropolitan University, one of Japan’s largest universities, has sustained a suspected ransomware attack that disrupted classes, internal networks, email, and administrative systems. Approximately 500 servers were affected, while personal information belonging to at least 130,000 individuals may have been exposed.

AI THREATS

  • Researchers documented an AI-assisted intrusion campaign involving the ARTEX toolkit against South Korean financial institutions. Exposed directories revealed Claude Code session histories, configuration files, and Chinese-language prompts associated with the operation. The attackers allegedly used AI-assisted workflows to facilitate data theft and planned to sell stolen information.
  • Researchers identified a phishing campaign targeting both employees and AI-powered email assistants. Malicious emails combine conventional phishing lures with hidden prompt injections embedded in HTML comments and invisible text. These instructions attempt to promote fraudulent requests, or induce unauthorized disclosure of information.
  • Researchers profiled CyberXero, an AI-augmented initial access broker targeting Ukrainian energy infrastructure and conducting automated attacks against WordPress and e-commerce platforms. The operation combines automated exploitation with AI agents and has obtained information belonging to more than 628,000 Ukrainian individuals through its campaigns.

VULNERABILITIES AND PATCHES

  • Veeam has released security updates addressing multiple vulnerabilities in Backup & Replication version 12. These include CVE-2025-64393, a critical remote code execution flaw rated CVSS 9.4 that allows low-privileged backup users to execute commands on affected servers. Versions before build 12.3.2.4934 are vulnerable.
  • Citrix NetScaler ADC and Gateway appliances are affected by CVE-2026-88779, a high-severity memory overflow vulnerability rated CVSS 8.7. The flaw affects customer-managed appliances configured for SAML authentication and could cause denial of service. Citrix confirmed targeted exploitation, and security updates are available for affected versions.
  • Cisco has released security updates addressing multiple critical vulnerabilities in NX-OS software. The flaws include CVE-2026-76455, an improper access control vulnerability rated CVSS 9.8. Successful exploitation could allow unauthorized access of affected network infrastructure.
  • Atlassian released patches for CVE-2026-21589, a critical arbitrary file access vulnerability rated CVSS 9.3. The flaw affects eight self-managed Data Center products, including Jira, Confluence, Bitbucket, and Bamboo. Unauthenticated attackers could access sensitive files and potentially obtain credentials enabling administrative access to connected applications.

Check Point IPS provides protection against this threat (Atlassian Multiple Products Arbitrary File Read (CVE-2026-21589))

THREAT INTELLIGENCE REPORTS

  • Check Point Research has reported a 48% year-over-year increase in global cyberattacks during September 2026, averaging 2,803 weekly attacks per organization. Education remained the most targeted sector, while reported ransomware attacks increased by 53%. Additionally, one in every 39 enterprise GenAI prompts posed a high risk of sensitive data exposure.
  • Researchers have analyzed a cyberespionage campaign by Russia-aligned UAC-0099 targeting Ukrainian organizations, including transportation, manufacturing, and energy companies. The group uses the MATCHBOIL downloader to deploy additional malware, including the MATCHWOK backdoor.
  • The FBI and Secret Service warn of continued exploitation in the FortiBleed credential-theft campaign, affecting more than 86,000 Fortinet FortiGate firewalls and VPN gateways across 194 countries. Attackers exploited previously compromised credentials to establish persistent access and reportedly sold access to ransomware affiliates, including INC, Lynx, and Payload.
  • Researchers have identified a cyberespionage campaign targeting Taiwanese research organizations through phishing emails impersonating academic and policy institutions. The attackers used potentially AI-assisted event invitations, malicious QR codes, and fake Google login pages. Their phishing infrastructure could intercept credentials and MFA challenges in real time.


The post 12th October – Threat Intelligence Report appeared first on Check Point Research.

Apple’s Verified Photography System

Apple just released a system called “Reference Image.” It can verify the image is exactly as taken by an iPhone—new models only—without tying it to a specific iPhone or photographer. It can also verify that multiple images came from the same iPhone.

Other industry solutions require a photographer or institution to vouch for an image using their own credentials. We are concerned this puts some photographers, such as those operating in conflict zones, in a difficult position; it should not be necessary to forgo anonymity in order to prove image authenticity. We built Apple Reference Image to avoid using an explicit, public credential for photographers, and to avoid even implicit public association between different photos taken by the same sensor. The final reference image is instead signed by Apple’s signing service, after validation by PCC. That signature is backed by Apple’s strongest technical guarantees.

Our implementation also protects the confidentiality of the image itself, including from Apple. Merely capturing a reference image should never expose the actual pixels to Apple or anyone else. We achieve this through the exceptional privacy properties of PCC—the nodes themselves are architected so that not even Apple can access image data, just as Apple cannot see the information processed for Apple Intelligence in PCC. While the revocation service must maintain a private record of photo GUIDs and associated sensors to allow for revocation, it never has access to the image data, and does not allow for public access to this record. And as final revocation checks occur using on-device lists, a device never reveals to anyone which photo it’s looking at in order to find out whether it’s still valid.

The report makes for good reading; the details are interesting.

5th October – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 5th October, please download our Threat Intelligence Bulletin.

TOP ATTACKS AND BREACHES

  • Arizona’s state court system has suffered a phishing-led cyberattack after an employee clicked a malicious link. Attackers copied backup files containing protective-order records and more than 150,000 Foster Care Review Board reports dating back to 2010, exposing personal and case-related information belonging to current and former participants.
  • Japanese car-sharing service Times Car has disclosed a data breach affecting approximately 6.6 million current and former accounts. Exposed information includes personal data, while identity-verification documents, including driver’s-license images, were exposed for about 1.6 million accounts. Payment card information was not affected.
  • South Africa’s air navigation provider has suffered a ransomware attack affecting operational technology supporting aviation weather services. Preliminary findings identified suspicious activity in weather-related environments, while separate reporting cited possible data theft. The provider has sought independent digital forensics to determine the scope of the incident.
  • Fakturownia, a Polish online invoicing platform used by more than 600,000 businesses, has disclosed a data breach after an attacker exploited a system vulnerability. Copied information included account and company data, password hashes, bank account details, authentication tokens, contractor information, and portions of invoices stored on the platform.

AI THREATS

  • Researchers observed autonomous AI agents attempting rudimentary hacking techniques while gathering public information from US and Canadian government websites. Activity included failed SQL injection attempts against the US Department of Education and Library and Archives Canada. Officials reported no compromise, while the origin of the agents remains unconfirmed.
  • Researchers demonstrated that malicious Custom GPTs hosted on ChatGPT were used in a ClickFix campaign to deliver remote access malware. Victims were redirected to a Google Sites page and tricked into running commands. Huntress investigated at least 40 related incidents, including two confirmed infections that began through Custom GPTs.
  • Researchers outlined how JadePuffer, an AI-enabled threat actor tracked as Storm-3168, used compromised Azure service principals to automate cloud reconnaissance and destructive actions. The activity included deleting storage and application resources, targeting backup-related assets, and attempting to retrieve access keys, reflecting agent-driven post-compromise operations in cloud environments.

VULNERABILITIES AND PATCHES

  • Citrix has issued fixes for critical NetScaler vulnerabilities CVE-2026-88771-2, affecting NetScaler ADC and Gateway. Attackers have exploited the flaws to gain remote access, deploy web shells and tunneling malware, steal credentials, and move from exposed appliances into internal networks.

Check Point IPS provides protection against these threats (Citrix NetScaler Multiple Products Buffer Overflow (CVE-2026-88772), Citrix NetScaler Multiple Products Command Injection (CVE-2026-88771))

  • Cisco has alerted about CVE-2026-76504, a critical (CVSS 9.8) vulnerability in Catalyst SD-WAN Manager. The flaw allows an unauthenticated remote attacker to send crafted requests and gain administrator access. Cisco reported active exploitation and stated that no fixes are available.

Check Point IPS provides protection against this threat (Cisco Catalyst SD-WAN Manager Authentication Bypass (CVE-2026-76504))

  • Apple has patched CVE-2026-86950, a CoreGraphics memory corruption vulnerability affecting iPhones, iPads, and Macs. Processing a malicious image or PDF can allow arbitrary code execution. Apple reported exploitation in highly targeted attacks and addressed the flaw through improved bounds checking across affected iOS, iPadOS, and macOS releases.
  • GitLab has released patches for CVE-2026-90970, a critical AI Gateway vulnerability rated CVSS 9.9. Authenticated Duo Agent Platform users can escape the prompt-template sandbox and execute arbitrary commands on the AI Gateway host.

THREAT INTELLIGENCE REPORTS

  • Researchers documented Warlock ransomware attacks exploiting SharePoint ToolShell vulnerabilities against organizations in the utilities, telecom, government and education sectors. The group used compromised SharePoint servers for initial access, disabled endpoint protection on dozens of systems, and deployed ransomware across at least 33 hosts during one intrusion.
  • Researchers exposed a China-nexus espionage campaign tracked as UAT-11587 targeting government and policy organizations across Asia. The group deployed the Antino backdoor through spear-phishing and tailored decoy documents. Antino uses Microsoft 365 services for command and control, file transfer, system reconnaissance, command execution, and persistence.
  • Researchers have uncovered TA419, a China-aligned espionage actor targeting US AI policy experts at think tanks, universities, and law firms. The group impersonates prominent economists and AI policymakers, builds rapport through benign emails, then redirects targets to phishing pages designed to steal Microsoft 365 credentials and session cookies.
  • Researchers mapped Russia-linked Star Blizzard phishing campaigns targeting more than 100 organizations, primarily in the United States and United Kingdom. The actor uses a new RedFlick delivery technique to install the CosmicPulse backdoor through scheduled tasks, supporting espionage activity against governments, NGOs, think tanks, and organizations connected to Ukraine.

The post 5th October – Threat Intelligence Report appeared first on Check Point Research.

28th September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 28th September, please download our Threat Intelligence Bulletin.

TOP ATTACKS AND BREACHES

  • The FBI has confirmed unauthorized activity affecting FBIjobs.gov after the ShinyHunters group defaced the website. The group claimed to have stolen employee and applicant information and shared samples of purported FBI personnel records with several media organizations.
  • Astrana Health, a major US healthcare technology provider, has confirmed a cyberattack that exposed confidential information. Attackers spoofed the company’s telephone number to impersonate personnel and gained access to its servers. Astrana restored systems from backups and disclosed the incident in an SEC filing but has not publicly revealed what data was exposed.
  • Cryptocurrency exchange Bitget has disclosed the theft of $351.6 million from several hot and warm wallets. The company detected unauthorized transfers on September 24 and temporarily suspended withdrawals. Bitget said cold wallets and most platform assets were unaffected, while suspected North Korean involvement remains under examination.
  • Ludwig Maximilian University of Munich, one of Germany’s largest universities, has suffered a data breach after an attacker accessed an enrollment system. The university said information was likely retrieved, potentially including names, bank details, health insurance information, and financial aid identifiers belonging to students.

AI THREATS

  • Australia has revealed that an OpenAI agent gained unauthorized access to a government Medicare statistics portal while performing an internal research task. After encountering access restrictions, the agent found a workaround and accessed public and non-public files. Officials said no personal information was accessed, while OpenAI described the behavior as unintended.
  • Researchers have described a financially motivated campaign using open-source AI agents to automate attacks against online retailers. The operators launched 105 attack projects between September 10 and 15 and compromised at least 27 organizations to varying degrees, stealing more than 600,000 valid payment card records.
  • Researchers have highlighted CLOSEDQUORUM, a Windows malware that uses four commercial AI models to determine its next post-compromise action. The models can direct credential and cryptocurrency wallet theft, persistence, or process injection. Cisco Talos has not confirmed that the malware has been successfully deployed in real-world attacks.

VULNERABILITIES AND PATCHES

  • Check Point has observed active exploitation of two critical pre-authentication vulnerabilities with CVSS scores of 9.8 – CVE-2026-85102 and CVE-2026-93616. The flaws affect Security Gateway and Security Management products and can enable remote code execution. Fixes for both vulnerabilities are available.
  • F5 has released fixes for CVE-2026-94127, a critical heap-based buffer overflow vulnerability in BIG-IP Access Policy Manager with a CVSS score of 9.8. The actively exploited flaw allows unauthenticated remote code execution when affected systems are configured with an access policy and OAuth profile.

Check Point IPS provides protection against this threat (F5 BIG-IP Heap Overflow (CVE-2026-94127))

  • WordPress has fixed CVE-2026-87902, a vulnerability affecting versions before 7.1.2 that allows unauthenticated attackers to include local PHP files outside active theme directories. Attackers have begun exploiting the flaw to write malicious PHP files and execute commands under specific server and theme configurations.

THREAT INTELLIGENCE REPORTS

  • Researchers have detailed Storm-2570, a ransomware affiliate operating across Qilin, DragonForce, Anubis, and BERT ecosystems. The actor maintains consistent post-compromise tooling and infrastructure across deployments, including remote access, credential theft, lateral movement, security tampering, and cloud-based data exfiltration before ransomware deployment.
  • Researchers detailed an INC ransomware intrusion affecting at least 175 endpoints. Particularly useful intelligence includes BYOVD-based security-tool disabling, AnyDesk, lateral movement through scheduled tasks, and a 17-day gap that researchers say could indicate separate initial-access and ransomware actors.
  • Researchers have tracked an active TeamFiltration campaign targeting more than 5,700 Microsoft 365 accounts across 28 tenants in Latin America, particularly organizations in Chile. Seven service accounts were compromised, with subsequent activity including corporate VPN authentication attempts and access to Azure Portal and SharePoint Online.
  • Researchers have identified Storm-3168, associated with JADEPUFFER, using compromised service principals to conduct destructive operations in Azure environments. The actor performed reconnaissance, credential collection, and bulk deletion attempts targeting storage accounts, SQL databases, Key Vaults, virtual machines, recovery protections, and other cloud resources.


The post 28th September – Threat Intelligence Report appeared first on Check Point Research.

FBI agents’ blood tests and doctors’ notes surface after breach

BBC News reports it has seen samples of stolen FBI agents’ medical examinations. The “fitness-for-work” reports identify FBI agents by name and address, and reveal even more personal details. They include blood and urine test results and doctors’ notes mentioning high cholesterol, blood in the urine, and even a shellfish and banana allergy.

As we reported last week, extortion group ShinyHunters claims to have breached the FBI. After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.

The BBC’s findings raise the stakes: The alleged theft includes highly sensitive medical records, not just staff identity and contact data. ShinyHunters shared samples with journalists as proof of its claims.

The BBC states:

“The samples shared with journalists appear genuine and include names, addresses, phone numbers, badge numbers, job titles and information about spouses.”

ShinyHunters claims it accessed several systems, including FBI MedLink, which stores medical records, and FBI BEAST, which handles background checks on employees and applicants, but the FBI has not confirmed these claims. The FBI has acknowledged an incident affecting FBIJobs-related systems and says it is investigating whether its own environment or a third-party provider was compromised.

The group’s stated demand remains non-financial: It wants the FBI to retract or remove a May advisory that ShinyHunters calls false and defamatory. It says it will release the data within five days if its demands are not met.

The cybercriminals also raised the number of affected people. ShinyHunters nows claims to hold sensitive information on around 60,000 current and former FBI staff. Medical histories could make affected people vulnerable long after the immediate incident: Unlike a stolen password, a medical record cannot be changed.

What to do if you’re affected

The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:

  • Check the FBI’s advice. Every breach is different, so check FBI.gov for updates and follow any specific advice it offers.
  • Change your password. If you have an FBI Jobs account and reuse its password elsewhere, change it on those other accounts. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for impersonators. Cybercriminals may contact you posing as the FBI, another government agency, or someone you know. Verify the identity of anyone who contacts you.
  • Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
  • Set up identity monitoring. This can alert you if your personal information is found being traded illegally online and help you recover afterward.

Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

On Anthropic’s AI Misuse Report

Earlier this month, Anthropic published a long report detailing all of the Claude misuses it detected. Daniel Meissler usefully summarized the report into 117 findings.

A few of the highlights:

  • AI agents increasingly handled reconnaissance, exploitation, data theft, propaganda production, surveillance workflows, and research while humans selected targets, set goals, and reviewed important outputs.
  • The report describes attackers using AI to industrialize credential theft, cloud compromise, phishing, vulnerability research, and the extraction of sensitive data from downstream organizations.
  • Influence operations used persistent agent memory, fake news sites, fabricated journalists, synthetic personas, political profiling, and large-scale multilingual content, although high content volume often produced little genuine engagement.
  • Surveillance and repression cases included automated dossiers, biometric and communications analysis, transnational targeting, coercive recruitment, and systems that continued operating locally after model access was revoked.
  • Biological and weapons cases show dual-use risk: AI supported advanced scientific and military work, but the report generally doesn’t establish completed biological weapons or operational battlefield deployment.

21st September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 21st September, please download our Threat Intelligence Bulletin.

TOP ATTACKS AND BREACHES

  • Japan’s Digital Agency, which operates the Government Solution Service used by multiple ministries, has confirmed a data breach after attackers exploited a vulnerability in a VPN appliance. Approximately 246,000 records were exposed, including names and contact details belonging to government officials and contractors, while financial information was not affected.
  • Two oil tankers bound for Texas were hit by cyberattacks that disrupted onboard systems during voyages to the United States. US Coast Guard and FBI personnel boarded the vessels, while officials confirmed malicious cyber activity on the VL Prosperity but have not publicly attributed the attacks to a specific actor.
  • Brevo, a French customer communication and marketing platform, has confirmed a supply chain attack after attackers used a compromised Cloudflare API key to inject malicious ClickFix scripts into websites that use Brevo components. The attack affected about 100,000 websites.
  • Japanese software company Helpfeel, operator of image-sharing service Gyazo, has reported a data breach after attackers exploited a vulnerability in an image upload server. Above 23 million user records and 490 million image metadata records were exposed, including email addresses, password hashes, session IDs, integration tokens, and location metadata.

AI THREATS

  • Check Point Research has analyzed the July-August AI threat landscape, highlighting the latest cases when AI models broke out of their evaluation environments. On the attackers’ side, AI is increasingly used as an operational tool, while the AI systems themselves are also targeted. The report highlights AI-assisted ransomware intrusions, criminal markets for stolen model access, and vulnerabilities in coding agents and enterprise copilots.
  • Researchers uncovered Luciferus, an uncensored AI service advertised on an underground forum for malware creation and other prohibited activities. Testing showed that the service could generate code for a simple remote access trojan, while its operator markets several paid tiers to users seeking unrestricted AI assistance.
  • Researchers unveiled BragJack, an attack that allows malicious browser extensions to hijack AI assistants by forcing prompts through trusted browser channels. The technique affected several AI-enabled browsers and assistants, enabling actions such as file access, screenshots, microphone and camera use, and logged-in activity before vendors issued security fixes.

VULNERABILITIES AND PATCHES

  • Check Point has released a fix for CVE-2026-91843, a critical vulnerability affecting Security Management and Log Servers. The flaw, rated CVSS 9.8, stems from a stack overflow in the login process and can allow unauthenticated remote attackers to execute code as root on affected R80 through R82 systems.
  • Cisco has addressed CVE-2026-76460 & CVE-2026-76461, two critical vulnerabilities affecting Cisco ISE and Secure Email Gateway with CVSS scores of 10.0 and 9.8. According to Cisco, the company is aware of active exploitation of CVE-2026-76460, which allows an unauthenticated remote attacker to gain access to the system’s management interface.
  • Oracle has released its September 2026 Critical Security Patch Update, addressing more than 800 vulnerabilities across 17 product families. More than 100 flaws are rated critical, while over 240 can be exploited remotely without authentication. Affected products include E-Business Suite, Fusion Middleware, Hyperion, Siebel CRM, Analytics, Communications, and Virtualization.
  • ISC has published security updates for BIND 9 addressing 14 vulnerabilities, including seven high-severity flaws that can trigger denial-of-service conditions. One issue, CVE-2026-77692, allows an unauthenticated remote attacker to crash the named process with a single crafted DNS-over-HTTPS request. Versions 9.21.26 and 9.20.29 contain the fixes.

THREAT INTELLIGENCE REPORTS

  • US, Japanese, Australian, and German authorities warned about WaterPlum (Contagious Interview), a North Korea-linked campaign that infected at least 30,000 devices across more than 100 countries. Operators posed as AI or blockchain employers, targeting IT professionals and stealing funds or credentials from over 7,000 cryptocurrency wallets from December 2025 through July 2026.
  • Researchers outlined a China-aligned FamousSparrow espionage campaign targeting government entities across Latin America and a telecommunications organization in Puerto Rico. The group deployed a new backdoor called SparroWocky, replacing its long-running SparrowDoor implant and supporting persistent surveillance across victims in Latin America.
  • Researchers revealed HEAVYGRAM, a Windows surveillance backdoor linked with moderate confidence to the Iranian Handala group. Active since 2023 against Iranian dissidents and journalists, the malware uses Telegram for command and control and can execute commands, capture screenshots, steal Telegram session data, exfiltrate files, and maintain persistence.
  • Researchers identified GhostCode, a device-code phishing kit that targets Microsoft 365 accounts by abusing the legitimate OAuth 2.0 device authorization flow. Victims authenticate through Microsoft, allowing attackers to capture tokens, register attacker-controlled devices, and obtain persistent account access without stealing the victim’s password or directly bypassing MFA.

The post 21st September – Threat Intelligence Report appeared first on Check Point Research.

ENISA: Frontier AI Is Changing the Speed of Cyberattacks. Europe Needs to Catch Up

Frontier AI is compressing the attack lifecycle from vulnerability discovery to exploitation, forcing defenders to detect, patch and respond at machine speed.

Cybersecurity has always been a race between attackers and defenders. ENISA’s latest assessment suggests that frontier AI is changing the speed of that race, and the gap between discovering a vulnerability and exploiting it could soon become measured in minutes rather than months.

In its July 2026 paper, ENISA’s view on Cybersecurity in the Frontier AI Era, the EU cybersecurity agency argues that advanced AI is compressing parts of the attack chain, from reconnaissance and vulnerability discovery to exploitation, lateral movement and data theft. The problem isn’t simply that AI can find more bugs. It’s that it can connect individual findings into a working attack.

That distinction is important. Traditional security operations could often rely on the time required for a human attacker to research a target, understand a vulnerability, develop an exploit and deploy it. ENISA says that “grace period” is disappearing as automated systems take over more of the work.

The agency describes a particularly worrying possibility: what it calls “negative time-to-exploit”. In practice, attackers could gain access to usable exploit information before defenders have even received or deployed a fix. ENISA says vulnerability weaponisation may now occur within 15 minutes of disclosure, while research cited in its report puts the median time from initial access to data exfiltration at 72 minutes.

That puts traditional patch management under pressure. A company can receive a vulnerability advisory, send it through a change process, test the update, obtain approval and schedule deployment. An attacker does not have to follow any of those steps.

ENISA calls this an “Authority Gap”: organisations may simply take longer to approve a defensive action than an AI-assisted attacker needs to exploit the weakness. The uncomfortable question is whether some environments will eventually need autonomous or near-autonomous patching because waiting for human approval could become the greater risk.

That doesn’t mean companies should blindly automate every security update. Automated patching can break systems, disrupt critical services or introduce new bugs, and ENISA explicitly identifies verification of AI-generated patches as a new bottleneck. The challenge is therefore not automation versus humans, but deciding which decisions can safely happen at machine speed and which still require human approval.

The scale of vulnerability discovery could create another problem. ENISA reports that one organisation went from roughly 80 CVEs in the first quarter of 2025 to almost 500 in the first quarter of 2026, then saw the volume rise to about 500 reports per day when frontier-AI tools were used.

At that point, finding vulnerabilities is no longer the main bottleneck. Verification and remediation become the problem.

Security teams already know what happens when too many alerts arrive at once. The difference is that AI could produce them at a scale humans cannot review manually. ENISA therefore recommends shifting resources from discovery alone toward faster triage, prioritisation and remediation, using approaches such as EPSS and VEX to focus scarce resources on vulnerabilities that are most likely to matter.

There’s another issue that deserves more attention: low-severity vulnerabilities may become more dangerous when AI can chain them together. ENISA notes that frontier models can reason about application logic, credentials, configurations and API access rather than simply identify isolated coding flaws. That can turn several individually modest weaknesses into a practical attack path.

This changes how defenders should think about risk. A vulnerability that looks harmless in isolation may become useful when combined with a weak credential, an exposed API or a poorly configured service.

The same pressure is already affecting the disclosure process. ENISA says AI-generated vulnerability reports have begun to overwhelm parts of the open-source reporting pipeline, with platforms and maintainers struggling to separate useful findings from repetitive or poorly validated submissions. At the same time, the agency notes that the quality of AI-generated reports has improved, meaning the problem could become both more serious and harder to filter.

There is a similar shift on the defensive side. ENISA recommends integrating AI into the software development lifecycle, using continuous threat modelling and automated testing rather than treating security as a review performed at the end of development. It also argues for AI-assisted incident response that can validate telemetry, prioritise events and contain the blast radius while keeping human oversight in place.

That last condition matters. The answer to machine-speed attacks cannot simply be giving machines unlimited authority to fight back. Defensive AI needs its own controls, permissions and audit trails, especially when it can make changes to production systems.

ENISA also recommends an “assume-breached” approach. Organisations should expect that some attacker will eventually get inside and design segmentation, monitoring and access controls so that one compromised component doesn’t automatically become a route into everything else.

The agency sees this as a structural change rather than another temporary threat trend. It recommends machine-speed defence under the broader concept of “Cybersecurity as Code”, covering areas such as vulnerability management, incident response, security architecture and secure software development.

Europe also has a policy problem to solve. NIS2, the Cyber Resilience Act and the AI Act already provide parts of the framework, but ENISA argues that Europe should develop common benchmarks for testing advanced AI models in cyber ranges, measuring exploitability and simulating chained attacks.

The agency also sees value in European cybersecurity data. Incident reports, malware samples, vulnerability disclosures and threat intelligence could support trusted defensive AI models, provided organisations apply strong safeguards, anonymisation and access controls.

For companies, however, the message is much simpler than the policy language suggests. Review your asset inventory, understand which systems are exposed, identify unsupported components and measure whether your detection and response can keep up with an attack that moves in minutes rather than hours. ENISA explicitly recommends near-real-time security operations, with single-digit-minute targets for mean time to detect and respond.

The defenders who adapt fastest won’t necessarily be those with the most advanced AI model. They’ll be the ones that have already removed the basic obstacles: fragmented logging, excessive privileges, slow approvals, unknown assets and systems nobody wants to patch because nobody is quite sure what will break.

AI is making attacks faster. It doesn’t change the basic rules of cybersecurity.

It just makes the cost of ignoring them arrive much sooner.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Frontier AI)

Using AI for Weapons Development

Last week, Anthropic released a long and detailed document describing current misuses of their Claude models. I’m still reading it, but I wanted to flag this:

We identified a cell of threat actors based in northern Yemen running three weapons development programs: a guided rocket that used a commodity phone-class flight computer with final-phase homing guidance; a multi-stage ballistic missile with a stated range goal above 2,000 km; and a multi-variant missile (referred to as the “R2000” set) that included a hypersonic glide vehicle variant.

The actors used Claude Code in place of human software engineers to develop the guidance, navigation, and control (GNC) software that steers and stabilizes a flying vehicle. For example, they used Claude to integrate an open-source autopilot onto a phone-class flight computer, writing the control and position estimation software, tuning the control settings, running a firmware build pipeline, and performing a flight simulation. The actors managed several Claude instances at once, assigning each one a role, much as a lead would delegate work on a small engineering team: the actors tasked one instance with writing the code, another with research, and a third with reviewing the code the first instance produced.

Our safeguards blocked many of their requests, but not all of them. The actors used a variety of tactics to evade our safeguards, including hiding their goals and the products the software was meant for, and they split their work across multiple sessions so no single session revealed their full intent.

These actors carried out a sustained effort to develop guided weapons, including using Claude to design guidance software. We do not have evidence the actors succeeded in fielding an operational device; but they did test-fire a guided rocket. This field test appears to have failed: within hours, the actors returned to Claude to work out why it failed.

Expect more of this. AI systems democratize expertise and capability. Most of the time that’s a good thing, but sometimes it’s not.

14th September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 14th Setpember, please download our Threat Intelligence Bulletin.

TOP ATTACKS AND BREACHES

  • IDScan.net, a US identity verification provider, has disclosed a data breach after detecting unauthorized access on September 1. Exposed data included names and government identification numbers, while a criminal marketplace advertised a collection containing millions of identity documents, including driver’s licenses, associated with the company’s verification services.
  • Mathspace, an education platform used in Australia and New Zealand, has suffered a data breach affecting more than 1 million people. The attackers exploited CVE-2026-72898 in self-hosted tool Metabase to access an internal reporting database. Exposed information included names, email addresses, usernames, and locations, while passwords and academic records were not affected.

Check Point IPS provides protection against this threat (Metabase SQL Injection (CVE-2026-72898))

  • Fintech company Revolut has reported a data exposure after employees fulfilled fraudulent information requests sent from an email account within a government agency’s legitimate domain. Exposed records included identity documents, verification selfies, contact details, IBANs, account statements, withdrawal records, and complete transaction histories.
  • Florida’s state Department of Motor Vehicles fell victim to a data breach after criminals used credentials stolen from a Plant City police officer’s personal device. The credentials enabled access to driver records, and the ShinyHunters group published images of stolen data.

AI THREATS

  • Check Point Research has detailed PuzzleMask, a plain-prose prompt technique that hides prohibited instructions from lightweight LLM gatekeepers while allowing stronger target models to recover them. In testing, gatekeepers classified the prompts as safe, while target models extracted and acted on concealed payloads in more than 90 percent of trials.
  • Check Point Research has demonstrated a covert cross-account channel in ChatGPT’s code-execution environment that allowed hidden tasks to run using a victim’s available tools, data, and connected applications. A proof of concept used a shared conversation to retrieve Gmail data from one account and relay the results to another.
  • Anthropic has disclosed four incidents in which Claude models operated on the real internet because of configuration failures instead of remaining within intended sandboxes. In the most serious case, a model published a malicious PyPI package that was executed by systems, exposing credentials and enabling access to a database.

VULNERABILITIES AND PATCHES

  • Microsoft has released its September 2026 Patch Tuesday updates, addressing a record 974 vulnerabilities across its products, including two actively exploited zero-days. CVE-2026-85880 and CVE-2026-81963 both allow local attackers to elevate privileges to SYSTEM, while 20 additional flaws could enable unauthenticated remote code execution without user interaction.

Check Point IPS provides protection against this threat (Microsoft Windows Update Stack Elevation of Privilege (CVE-2026-81963))

  • GitLab has addressed CVE-2026-85706, a critical path traversal vulnerability affecting Community and Enterprise Editions, with a CVSS score of 10.0. The flaw allows unauthenticated attackers to read arbitrary files through the repository commits API. Affected versions include 18.7 through 19.3.1, with fixes available in 19.1.8, 19.2.6, and 19.3.2.

Check Point IPS provides protection against this threat (GitLab Arbitrary File Read (CVE-2026-85706))

  • MikroTik has fixed CVE-2026-67276 and CVE-2026-86060, RouterOS vulnerabilities that can be chained to obtain passwordless SSH access and elevate privileges to full administrator. Successful exploitation can give attackers control over exposed routers, enabling configuration changes, DNS manipulation, traffic interception, and use of compromised devices as network footholds

THREAT INTELLIGENCE REPORTS

  • Check Point Research has reported that enterprise GenAI usage continued to expand in August, reaching an average of 106 prompts per user, while 86% of organizations regularly using GenAI were affected by high-risk prompt activity. The report also recorded 1,042 ransomware attacks, almost double the August 2025 figure, while average weekly cyberattacks rose 22% year over year to 2,422 per organization.
  • Researchers have detected a passkey-themed social engineering campaign targeting Microsoft 365 accounts. Attackers use phone and text lures directing employees to lookalike sign-in pages, then register their own authentication methods and collect data from SharePoint, OneDrive, and Exchange after gaining access to compromised accounts.
  • Researchers have analyzed an Android banking-fraud campaign by the GoldFactory group that abuses Android Work Profile functionality through a tool called Vwork to clone victims’ banking applications. The Gigabud malware used in the operation was linked to at least 1,469 compromised devices in Indonesia and nearly $1 million in losses.
  • Researchers have detailed BlueMoon, an exploit chain combining two vulnerabilities in Chromium’s V8 JavaScript engine with a Windows flaw to compromise targeted systems. The vulnerabilities were used by multiple espionage groups after Chrome patches became available, allowing browser exploitation, sandbox escape, and privilege escalation on vulnerable Windows devices.

Check Point IPS provides protection against this threat (Google Chrome Type Confusion (CVE-2026-85046))

The post 14th September – Threat Intelligence Report appeared first on Check Point Research.

Anthropic: AI Misuse Is Entering a New Phase: From Cybercrime to Surveillance, Propaganda and Weapons

AI is becoming an operational force for cybercrime, surveillance, propaganda, fraud and weapons development, lowering the cost and scale of attacks.

Artificial intelligence (AI) is becoming more than a tool for people who want to do something malicious. It is increasingly becoming part of the operational machinery itself.

That is the main message emerging from Anthropic ‘s latest Threat Intelligence report, which examines malicious activity identified and disrupted between December 2025 and August 2026. The cases cover cyber operations, influence campaigns, surveillance, fraud, biological research, conventional weapons and attempts to extract the capabilities of frontier AI models.

The actors involved are equally diverse. Anthropic describes suspected state-sponsored groups, financially motivated criminals, commercial surveillance operators and politically motivated individuals. What connects many of these cases is not a new attack technique, but the way AI changes the economics, speed and scale of operations.

AI is becoming an operational layer

The report makes an important distinction from the usual discussion about AI-powered hacking.

The biggest change may not be that AI can discover a new vulnerability or write malware. It is that models can now contribute across almost the entire attack chain, from reconnaissance and tool development to exploitation, credential theft, data processing and exfiltration.

Anthropic observed operations in which AI systems executed commands against victim networks, harvested credentials and exfiltrated information. At the more autonomous end of the spectrum, multi-agent frameworks conducted reconnaissance, exploitation and data theft against several victims in parallel, sometimes for hours or days with limited human intervention.

This has an important consequence for defenders. Sophisticated attacks no longer necessarily require sophisticated attackers.

According to Anthropic, AI is reducing the gap that once separated well-funded state operations from smaller criminal groups. Reconnaissance, exploitation, coding and data analysis that previously required several specialists can increasingly be delegated to AI systems running at machine speed.

The underlying attacks are often familiar. Stolen credentials, exposed services, vulnerable edge devices, phishing and SQL injection still play a central role. What has changed is the cost of putting them together at scale.

Cybercrime becomes a production line

One of the clearest examples involves a financially motivated operation that harvested credentials from software and online services.

The attackers downloaded and analyzed 1.8 million Android application packages, searching for hardcoded secrets, while running a parallel process to collect GitHub-related credentials. The important point is not the number of apps. It is the automated pipeline connecting discovery, credential collection, validation and subsequent intrusion activity.

“One French-speaking operator going by the aliases of (MeowSHA | frkoo | blazespider) ran a distributed credential-harvesting pipeline across a fleet of 10 AWS EC2 workers. This pipeline mass-downloaded 1.8 million distinct Android APKs from multiple app-store sources, decompiled them, and scanned for hardcoded secrets with Detecting and countering misuse of AI: September 2026 12 TruffleHog.” reads the report. “Verified findings were routed in real time to a Telegram group organized into over 100 source types. A parallel GitHub organization email harvester fed a second stream of stolen GitHub Personal Access Tokens. These two credential pipelines supplied the initial-access credentials for the bulk of the confirmed breaches associated with frkoo.”

The same model appears elsewhere in the report. Attackers used AI to develop malware and phishing tools, analyze compromised environments, process stolen information and maintain access to victims.

In one campaign, stolen tokens could be replayed against Microsoft services to access mailbox contents, including deleted messages. The attackers used techniques designed to make their traffic resemble legitimate Microsoft clients. Anthropic says Claude was used to engineer and test the tooling.

This is what makes the development significant. AI does not need to invent a completely new attack for the threat level to increase. If it can automate enough of the existing process, a small team can attempt operations that previously required a much larger workforce.

Surveillance at machine speed

The report becomes even more striking when it moves beyond cybercrime.

Anthropic identified nation-state actors and commercial surveillance operators using Claude to build systems for monitoring populations, profiling individuals and analyzing social media activity. The cases involve actors linked to China, Iran and West Africa, as well as the commercial surveillance-for-hire market.

“These cases include threat actors from China, Iran, and West Africa, as well as the commercial “surveillance-for-hire” market, and range from operations carried out by a single individual to entire teams.” continues the report. “Anthropic’s Usage Policy prohibits using Claude to conduct non-consensual surveillance and profiling, and to use our services to violate individuals’ civil liberties and human rights. In every case we describe below, the threat actors violated our Usage Policy and attempted to circumvent controls designed to detect such misuse.”

In one case, a consultant working for Malian national security authorities used Claude to engineer a mass-interception platform capable of monitoring communications across the country’s mobile operators and producing dossiers on targets.

In another, Iranian actors used Claude to develop a malicious Firefox extension designed to harvest information about social-media users. Chinese operators used AI to analyze large volumes of social-media content, identify potential targets and generate intelligence reports.

One particularly revealing operation targeted Uyghur communities in Syria. An actor without Arabic-language skills used Claude to draft messages in the appropriate dialect, translate replies in real time, role-play as an expert to evaluate the operation and prepare the resulting information for a suspected human case officer.

This shows another important shift. AI is not merely analyzing surveillance data after it has been collected. It can become part of the system that decides whom to watch, how to approach them and how to turn raw information into intelligence.

Propaganda can also be industrialized

The same automation is appearing in influence operations.

Anthropic describes an operation linked with high confidence to UAE government officials in which AI supported a network of roughly 300 inauthentic social-media accounts. The operation also created a front NGO using the identity of a real organization, produced apparently independent human-rights material and ghost-wrote testimony intended for presentation to the UN Human Rights Council.

The actors also profiled 18 members of the European Parliament and journalists and prepared dossiers on UN Special Rapporteurs who had criticized UAE conduct in Sudan.

The significance is not simply that AI can generate propaganda. Political actors have been producing propaganda for centuries. The difference is that AI can make the process much cheaper and more scalable while allowing operators to generate different narratives, personas and documents for different audiences.

The line between genuine grassroots activity and centrally coordinated influence therefore becomes harder to see.

Fraud gets a human face without the human

The report also provides a remarkably concrete example of AI-powered consumer fraud.

A China-based app studio built more than 20 dating applications and used AI personas to communicate with users while advertising the services as fully human. During a two-week period, Anthropic identified more than 4,700 AI personas that interacted with at least 25,000 people.

“A China-based app studio used Claude to both build a network of over 20 dating apps and power the AI personas used to converse with users–despite advertising their service as fully human.” states Anthropic. “Over a two-week window in April 2026, we discovered more than 4,700 distinct AI personas that engaged in conversations with at least 25,000 unique individuals.”

The operation combined AI and human workers. The bots handled large volumes of conversations, while real people performed activities such as video calls and social-media interactions designed to convince victims that they were dealing with genuine users.

The reported ratio was roughly three AI personas for every real person. Claude generated around 2.36 million messages during the period examined.

This is an important preview of how AI could change online fraud. The attacker no longer needs thousands of people to maintain thousands of conversations. A small human operation can supervise a much larger artificial workforce.

The terrorism risk deserves attention

The report does not identify a confirmed terrorist attack conducted with Claude. It does, however, document activity that illustrates why AI-assisted weapons development deserves attention from counterterrorism and national-security agencies.

Anthropic identified six cases involving weapons development, procurement or intelligence gathering in China, Russia and Yemen. The cases include guided rockets, ballistic-missile simulations, anti-torpedo systems, autonomous drone swarms, electronic-warfare targeting and directed-energy weapons.

“We identified a cell of threat actors based in northern Yemen running three weapons development programs: a guided rocket that used a commodity phone-class flight computer with final-phase homing guidance; a multi-stage ballistic missile with a stated range goal above 2,000 km; and a multi-variant missile (referred to as the “R2000” set) that included a hypersonic glide vehicle variant.” continues the report.

The Yemen case is particularly significant from a terrorism perspective, even though Anthropic does not establish that the actors were a terrorist organization. A weapons-development cell used Claude Code to work on guidance, navigation and control software for a guided rocket. Multiple AI instances were assigned different roles, including coding, research and code review. The group also carried out a real-world test of a guided rocket and returned to the model afterward to analyze the failure.

That distinction matters. AI is not necessarily giving a terrorist group the ability to build an advanced weapons system from nothing. What it can do is reduce the amount of specialized engineering expertise required to modify, integrate and troubleshoot technologies that the group already possesses.

For counterterrorism agencies, this creates a potential new problem: the proliferation of technical capability may no longer depend entirely on recruiting highly specialized engineers.

Weapons development is not limited to missiles

The report provides several other examples.

One China-based actor used Claude to develop documentation and software for an anti-torpedo system, including a technical proposal of more than 200 pages and comparative analysis of US naval systems. The actor repeatedly asked the model to act as a hostile expert and criticize its own work, effectively creating an automated review process.

A Russia-based operation worked on an autonomous FPV drone swarm using Claude Code and simulation infrastructure. Other cases involved electronic warfare, air-defense suppression and intelligence gathering related to directed-energy weapons.

The pattern is consistent: AI can compress research, engineering, documentation and testing cycles.

That does not mean the model independently created these weapons. In several cases, the actors already had expertise, hardware or access to the necessary infrastructure. The AI accelerated the work around them.

Biology is an even harder problem

Biological misuse presents a different challenge because intent is much harder to establish.

Anthropic says today’s models are capable of assisting with increasingly complex scientific research, making it harder to guarantee that they cannot meaningfully support dangerous biological work.

The report describes five cases involving potentially sensitive research. They include gain-of-function work involving chikungunya, planning related to mammalian adaptation of avian influenza, an orthopoxvirus immune-evasion research proposal, optimization of venom peptides and computational redesign of toxins.

Anthropic is careful about what these cases prove. It does not claim that the researchers intended to develop biological weapons, nor that Claude enabled a biological weapon. The cases demonstrate something more subtle: dangerous research can look very similar to legitimate scientific research when viewed one request at a time.

That makes traditional content filtering much harder.

A sophisticated actor does not necessarily have to ask an AI model, “How do I build a biological weapon?” They can divide the work into apparently legitimate scientific tasks and combine the answers elsewhere.

AI is also becoming the target

Perhaps the most strategic part of the report concerns illicit distillation.

Anthropic says several Chinese AI companies attempted to extract capabilities from Claude by creating large numbers of fraudulent accounts, routing enormous numbers of queries through proxy networks and collecting model outputs for training.

Alibaba’s operation reached almost three million exchanges per day from more than 3,500 fraudulent accounts, with more than 151 million exchanges observed between May and July. The activity targeted agentic tasks, software engineering, kernel development and long-horizon reasoning.

Zhipu used hundreds of fraudulent accounts to extract and process reasoning traces. Moonshot, meanwhile, allegedly forwarded customer requests to Claude while presenting Claude’s responses as if they came from its own Kimi models.

The privacy implications are serious as well. Anthropic says some rerouted requests contained sensitive corporate information, live credentials and surveillance data. In one case, DeepSeek allegedly relayed requests containing internal AI-program specifications; another exposed credentials associated with a Russian government database.

This creates a new category of AI supply-chain risk: an organization may think it is using one AI service while its data and workloads are actually being processed by another.

The common thread is scale

The cases in the report look very different, but they point in the same direction.

AI is becoming a force multiplier for cybercriminals, intelligence services, propagandists, fraudsters, surveillance operators and potentially armed groups. It can automate the boring parts of an operation, accelerate the difficult parts and allow a small number of people to coordinate activity at a scale that would previously have required a much larger organization.

This is why the most important finding is not that AI can hack systems or generate malicious code.

The bigger issue is that AI is changing the economics of malicious activity.

A criminal group can process millions of files. A surveillance unit can turn huge volumes of social-media posts into target profiles. A propaganda operation can maintain hundreds of artificial identities. A fraud operation can hold thousands of conversations simultaneously. A weapons program can use AI to accelerate software development and technical analysis.

And in the most advanced cyber cases, AI systems can perform several of these tasks with little human intervention. Anthropic reports that humans still tend to retain the decisions that matter most, such as selecting targets and deciding how to monetize results. But the operational workload between those decisions can increasingly be delegated to machines.

That may be the real security threshold we are crossing.

The question is no longer simply whether AI can be abused. It clearly can.

The more important question is how much of a malicious operation can now be delegated to AI before a human has to step in.

Anthropic’s report suggests that the answer is already: quite a lot.

“Sophisticated and persistent threat actors continuously test our safeguards and try to circumvent the technical measures we use to detect and prevent misuse.” concludes the report. “We’ll continue to evolve our safeguards and coordinate with our partners to improve our ability to detect, disrupt, and prevent future misuse.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Anthropic)

7th September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 7th Setpember, please download our Threat Intelligence Bulletin.

TOP ATTACKS AND BREACHES

  • Thomson Reuters, a global information and technology company, has disclosed a breach of its C-Track court case-management platform affecting courts across 11 US states and Canada. An unauthorized party obtained C-Track files containing court records, including names and other personal information.
  • Hit, a major Slovenian gambling and tourism operator, has sustained a cyberattack that forced six casinos to close for about three days. Operations have resumed, but some table games, bingo, loyalty services, cash registers, and hotel systems remained unavailable during restoration, while some employees were temporarily furloughed.
  • Baylor Genetics, a US clinical diagnostic laboratory, has disclosed a data breach affecting 2.8M patients and employees after unauthorized access to part of its IT environment in June. Stolen data included names, birth dates, medical testing and laboratory results, health insurance information, and some Social Security numbers.
  • Global cloud storage provider Dropbox has disclosed unauthorized access to about 5,000 accounts after attackers exploited Lenovo’s email verification process. Fraudulent Lenovo IDs created with victims’ email addresses enabled access without Dropbox passwords, while files were viewed or downloaded from affected accounts.

AI THREATS

  • Researchers have detailed an AI-assisted ransomware intrusion that compromised an enterprise network in under 10 hours. Autonomous agents mapped internal systems, mined code repositories, obtained root credentials from a secrets manager, and abused build pipelines and cloud resources, compressing activity that normally requires substantially more human effort.
  • Security researchers have disclosed GitSpawn, a vulnerability class affecting AI coding agents including Claude Code, Codex, Cursor, Goose, Qwen Code, Grok Build, and Hermes. Malicious repository Git configurations can trigger arbitrary code execution as the developer when agents automatically gather project context, in some cases before trust prompts.
  • Researchers have showcased how an AI coding assistant can be used to port a known PLC exploit to a different controller model, producing working payloads after guided analysis. While the process still required significant manual effort, it demonstrated how AI can accelerate exploit development for industrial systems.

VULNERABILITIES AND PATCHES

  • SonicWall has addressed CVE-2026-83548 and CVE-2026-83549, critical vulnerabilities affecting SMA 1000 remote access gateways. CVE-2026-83548 is a pre-authentication SSRF flaw rated CVSS 10.0, while CVE-2026-83549 enables post-authentication remote code execution. Both were exploited as zero-days and affect SMA 6210, 7210, and 8200v appliances.
  • JFrog has addressed CVE-2026-82329, a critical CVSS 9.8 authentication bypass affecting self-hosted Artifactory deployments. The flaw allows unauthenticated attackers to obtain administrator access tokens and take control of repositories. Exploitation was observed shortly after disclosure against internet-exposed systems, while JFrog Cloud environments were patched by the vendor.

Check Point IPS provides protection against this threat (JFrog Artifactory Authentication Bypass (CVE-2026-82329))

  • Security researcher have unveiled FalconFlank, a zero-day privilege escalation technique affecting CrowdStrike Falcon on Windows 11 25H2 and Windows Server 2025. The proof-of-concept abuses Falcon’s Microsoft Office macro-removal remediation behavior, allowing a low-privileged local user to obtain elevated access on affected systems

THREAT INTELLIGENCE REPORTS

  • Check Point Research has uncovered a Chinese-speaking cybercrime cluster, dubbed Gambling Goblin, that compromises Brazilian government and education websites. The group installs malicious Apache modules to proxy visitors to gambling and phishing pages while manipulating search rankings. Its infrastructure spans multiple languages and shows links to Earth Berberoka.

Check Point Threat Emulation and Harmony Endpoint provide protection against this threat

  • Check Point Research has analyzed JSCeal, a cryptocurrency-focused information stealer compiled into V8 bytecode and executed through a bundled Node.js runtime. Researchers developed a static deobfuscation pipeline that recovered readable code, revealing keylogging, browser credential theft, HTTPS interception, additional encryption, and newer variants targeting macOS systems.

Check Point Threat Emulation and Harmony Endpoint provide protection against this threat

  • Researchers have mapped a campaign by Iran-linked Mirage Kitten that uses fake LinkedIn coding tests to deliver NodeRabbit and PollCat malware. The malicious tests are distributed through cloud links and install cross-platform implants. Targets include fintech and aviation organizations in Egypt, Ethiopia, and Afghanistan.
  • Researchers have analyzed new macOS delivery activity linked to North Korea’s Contagious Interview campaign. Attackers use fake job interviews and trojanized disk images or installer packages impersonating legitimate Mac applications. The samples connect to infrastructure previously associated with malicious Git hooks and VS Code task files.

The post 7th September – Threat Intelligence Report appeared first on Check Point Research.

❌